
Menace détectée.

Bonjour,
Veuillez regarder ma photo en pointant votre souris de profil pour regarder ce que détecte AVG sur mon Pc Vista!
Merci
Veuillez regarder ma photo en pointant votre souris de profil pour regarder ce que détecte AVG sur mon Pc Vista!
Merci
Configuration: Windows Vista / Firefox 3.5.8
22 réponses
-
ModérateurSalut,
Pour commencer, il serait plus efficace et pratique que tu envois ta capture d'écran ici :
http://cijoint.fr/
Et que tu nous communiques l'URL pour qu'on y ait accès plus facilement que par ton profil.
********
Ce fichier est normalement légitime :
https://www.systemlookup.com/accessverify.php?redirect=Drivers%2F828-iaStor_sys.html
Mais il semble patché (modifié par une infection).
*******On va vérifier******
Affiche les fichiers et dossiers cachés :
Dans Mes documents, Outils, Options des dossiers, Onglet Affichage, coche Afficher les fichiers et dossiers cachés.
**********
Analyse ce fichier :C:\Windows\System32\drivers\iaStor.sys
Sur le site de Virustotal :
https://www.virustotal.com/gui/
Parcourir > Sélectionne ton fichier > Analyser, patiente que l’analyse soit terminée.
Poste bien le rapport.
(Si VirusTotal indique que le fichier a déjà été analysé, clique sur le bouton Ré-analyse le fichier maintenant).
-
Contributeur sécuritébonjour , édité !!
-
Fichier iaStor.sys reçu le 2010.03.04 20:34:39 (UTC)
Situation actuelle: en cours de chargement ... mis en file d'attente en attente en cours d'analyse terminé NON TROUVE ARRETE
Résultat: 32/42 (76.2%)
en train de charger les informations du serveur...
Votre fichier est dans la file d'attente, en position: ___.
L'heure estimée de démarrage est entre ___ et ___ .
Ne fermez pas la fenêtre avant la fin de l'analyse.
L'analyseur qui traitait votre fichier est actuellement stoppé, nous allons attendre quelques secondes pour tenter de récupérer vos résultats.
Si vous attendez depuis plus de cinq minutes, vous devez renvoyer votre fichier.
Votre fichier est, en ce moment, en cours d'analyse par VirusTotal,
les résultats seront affichés au fur et à mesure de leur génération.
Formaté Formaté
Impression des résultats Impression des résultats
Votre fichier a expiré ou n'existe pas.
Le service est en ce moment, stoppé, votre fichier attend d'être analysé (position : ) depuis une durée indéfinie.
Vous pouvez attendre une réponse du Web (re-chargement automatique) ou taper votre e-mail dans le formulaire ci-dessous et cliquer "Demande" pour que le système vous envoie une notification quand l'analyse sera terminée.
Email:
Antivirus Version Dernière mise à jour Résultat
a-squared 4.5.0.50 2010.03.04 Rootkit.Win32.TDSS!IK
AhnLab-V3 5.0.0.2 2010.03.04 -
AntiVir 8.2.1.180 2010.03.04 TR/Patched.Gen
Antiy-AVL 2.0.3.7 2010.03.04 -
Authentium 5.2.0.5 2010.03.04 W32/SYStroj.AB.gen!Eldorado
Avast 4.8.1351.0 2010.03.04 Win32:Alureon-EU
Avast5 5.0.332.0 2010.03.04 Win32:Alureon-EU
AVG 9.0.0.730 2010.03.04 Win32/Patched.CJ
BitDefender 7.2 2010.03.04 Rootkit.Patched.TDSS.Gen
CAT-QuickHeal 10.00 2010.03.04 Rootkit.TDSS.y
ClamAV 0.96.0.0-git 2010.03.04 -
Comodo 4091 2010.02.28 Virus.Win32.Olmarik.RF0
DrWeb 5.0.1.12222 2010.03.04 BackDoor.Tdss.1365
eSafe 7.0.17.0 2010.03.04 -
eTrust-Vet 35.2.7340 2010.03.04 Win32/Alureon.AQH
F-Prot 4.5.1.85 2010.03.04 W32/SYStroj.AB.gen!Eldorado
F-Secure 9.0.15370.0 2010.03.04 Rootkit:W32/TDSS.gen!D
Fortinet 4.0.14.0 2010.03.04 -
GData 19 2010.03.04 Rootkit.Patched.TDSS.Gen
Ikarus T3.1.1.80.0 2010.03.04 Rootkit.Win32.TDSS
Jiangmin 13.0.900 2010.03.04 Rootkit.TDSS.cwp
K7AntiVirus 7.10.990 2010.03.04 -
Kaspersky 7.0.0.125 2010.03.04 Rootkit.Win32.TDSS.y
McAfee 5910 2010.03.04 Patched-SYSFile.a
McAfee+Artemis 5910 2010.03.04 Patched-SYSFile.a
McAfee-GW-Edition 6.8.5 2010.03.04 Heuristic.LooksLike.Trojan.Patched.H
Microsoft 1.5502 2010.03.04 Virus:Win32/Alureon.F
NOD32 4916 2010.03.04 Win32/Olmarik.RF
Norman 6.04.08 2010.03.04 W32/tdss.drv.gen6
nProtect 2009.1.8.0 2010.03.04 -
Panda 10.0.2.2 2010.03.04 -
PCTools 7.0.3.5 2010.03.04 Backdoor.Tidserv
Prevx 3.0 2010.03.04 Medium Risk Malware
Rising 22.37.03.04 2010.03.04 -
Sophos 4.51.0 2010.03.04 Mal/TDSSRt-A
Sunbelt 5751 2010.03.04 Rootkit.Win32.TDSS.y (v)
Symantec 20091.2.0.41 2010.03.04 Backdoor.Tidserv!inf
TheHacker 6.5.1.7.221 2010.03.04 -
TrendMicro 9.120.0.1004 2010.03.04 PE_TDSS.MTR
VBA32 3.12.12.2 2010.03.04 Rootkit.Win32.TDSL
ViRobot 2010.3.4.2212 2010.03.04 Trojan.Win32.R-Alureon.246784
VirusBuster 5.0.27.0 2010.03.04 Rootkit.Alureon.Gen!Pac.7
Information additionnelle
File size: 250368 bytes
MD5...: 0e15f66ae9e9a3d04f78e914517cdf3f
SHA1..: d96f0fd51730121b59605bf887b831537443aa90
SHA256: 0e9e34d50bd71e2c4935882662dd66fe8b86caf87d61eed6f723d553b9a3e32b
ssdeep: 3072:5jcE8Rt9Dh27TSpmHoEFdjuwguSq1yi/wVrIDDA5xEF8nctzHsajAgC25wQ
RWh:5jPm+9T/S0H7IVisrjnctzHsajAv9
PEiD..: -
PEInfo: PE Structure information
( base data )
entrypointaddress.: 0xb5024
timedatestamp.....: 0x4547c439 (Tue Oct 31 21:46:33 2006)
machinetype.......: 0x14c (I386)
( 6 sections )
name viradd virsiz rawdsiz ntrpy md5
.text 0x1000 0x37f92 0x38000 6.57 cbeb06606464fddf970079dc92eaa4d3
.rdata 0x39000 0xa94 0xc00 5.17 f7b7d774c7ae843a753396ee18a3ffda
.data 0x3a000 0x7964c 0x1000 4.70 b775edc23209eb4e86c7af721f886479
INIT 0xb4000 0xc74 0xe00 5.16 ffc9ccb7a2b69b7bb2dffdf27579316b
.rsrc 0xb5000 0x440 0x600 4.84 1c36fba45ae5a98eebe4a7c14fe131e9
.reloc 0xb6000 0x1dc4 0x1e00 5.55 f034c57c7164ae4c6301d102d9d819a1
( 2 imports )
> ntoskrnl.exe: ZwClose, ZwQueryValueKey, DbgPrint, ZwOpenKey, RtlCreateRegistryKey, RtlCopyUnicodeString, memmove, KeInsertQueueDpc, MmGetPhysicalAddress, KeInitializeSpinLock, KefAcquireSpinLockAtDpcLevel, KefReleaseSpinLockFromDpcLevel, IoInvalidateDeviceRelations, IoFreeWorkItem, IoRequestDeviceEject, IoQueueWorkItem, IoAllocateWorkItem, ExInterlockedPopEntrySList, ExInterlockedPushEntrySList, IofCompleteRequest, IofCallDriver, IoGetDmaAdapter, RtlWriteRegistryValue, RtlAnsiStringToUnicodeString, RtlInitAnsiString, ZwCreateKey, swprintf, KeWaitForSingleObject, KeInitializeEvent, IoDisconnectInterrupt, IoGetConfigurationInformation, IoDeleteDevice, ExDeleteNPagedLookasideList, KeCancelTimer, IoFreeIrp, KeLeaveCriticalRegion, KeEnterCriticalRegion, IoDetachDevice, IoDeleteSymbolicLink, IoConnectInterrupt, IoReleaseRemoveLockAndWaitEx, strstr, strncat, sprintf, IoBuildDeviceIoControlRequest, PoSetPowerState, PoRegisterDeviceForIdleDetection, RtlCompareMemory, KeClearEvent, IoInitializeRemoveLockEx, ObfReferenceObject, KeSetTimer, IoWriteErrorLogEntry, IoAllocateErrorLogEntry, IoAcquireRemoveLockEx, RtlInitUnicodeString, KeSetEvent, _allmul, KeInitializeDpc, KeInitializeTimer, ObfDereferenceObject, IoGetAttachedDeviceReference, IoAllocateIrp, IoInvalidateDeviceState, strncpy, strncmp, IoFreeMdl, MmProbeAndLockPages, IoAllocateMdl, _except_handler3, PoRequestPowerIrp, MmMapLockedPagesSpecifyCache, KeBugCheck, KeRemoveQueueDpc, KeQuerySystemTime, KeQueryTimeIncrement, KeTickCount, PsTerminateSystemThread, KeWaitForMultipleObjects, KeSetPriorityThread, ObReferenceObjectByHandle, PsCreateSystemThread, ExInitializeNPagedLookasideList, MmMapIoSpace, ExRegisterCallback, ExCreateCallback, IoReportResourceForDetection, ExUnregisterCallback, MmUnmapIoSpace, RtlCheckRegistryKey, IoAttachDeviceToDeviceStack, IoCreateSymbolicLink, IoCreateDevice, RtlUnicodeStringToInteger, wcsncpy, wcsstr, _wcsupr, IoGetDeviceProperty, ZwCreateDirectoryObject, WRITE_REGISTER_ULONG, READ_REGISTER_ULONG, _alldiv, PoStartNextPowerIrp, PoCallDriver, _purecall, ExSystemTimeToLocalTime, KeDelayExecutionThread, KeSetTimerEx, KeInitializeTimerEx, wcslen, ExAllocatePoolWithTag, RtlAppendUnicodeToString, RtlAppendUnicodeStringToString, RtlQueryRegistryValues, IoReleaseRemoveLockEx, ExFreePoolWithTag, KeBugCheckEx
> HAL.dll: ExAcquireFastMutex, ExReleaseFastMutex, KfReleaseSpinLock, KfAcquireSpinLock, KeGetCurrentIrql, KeStallExecutionProcessor
( 0 exports )
RDS...: NSRL Reference Data Set
-
pdfid.: -
trid..: Win32 Executable Generic (68.0%)
Generic Win/DOS Executable (15.9%)
DOS Executable Generic (15.9%)
Autodesk FLIC Image File (extensions: flc, fli, cel) (0.0%)
sigcheck:
publisher....: n/a
copyright....: n/a
product......: n/a
description..: n/a
original name: n/a
internal name: n/a
file version.: n/a
comments.....: n/a
signers......: -
signing date.: -
verified.....: Unsigned
<a href='http://info.prevx.com/aboutprogramtext.asp?PX5=B060887100486723D2A30304A75660005BCB9786' target='_blank'>http://info.prevx.com/aboutprogramtext.asp?PX5=B060887100486723D2A30304A75660005BCB9786</a> -
ModérateurEh bien... ça commence très mal !
Un beau rootkit !
Télécharge Combofix :
= = = = >>> En cliquant ici <<< = = = =
* On va enregistrer ce fichier sur le Bureau : pour cela, sur le panneau de gauche, clique sur le Bureau.
* Clique enfin sur le bouton Enregistrer en bas de page à droite.
* Assure toi que tous les programmes sont fermés avant de lancer le fix ! Ne lance pas le fix tout de suite !
* Fais un clic droit sur combofix.exe et sélectionne "Exécuter en mode administrateur".
* Clique sur Oui au message de Limitation de Garantie qui s’affiche.
* Il est possible que ton pare-feu te demande si tu acceptes ou non l’accès de nircmd.cfexe à la zone sure : accepte !
Note :
Ne ferme pas la fenêtre qui vient de s’ouvrir , tu te retrouverais avec un bureau vide !
* Lorsque le scan est terminé, un rapport sera généré : poste en le contenu dans ton prochain message.
* Note : Le rapport se trouve également là : C:\ComboFix.txt
-
ComboFix 10-03-04.02 - hourfane 05/03/2010 2:07.1.2 - x86
Microsoft® Windows Vista™ Édition Familiale Premium 6.0.6002.2.1252.41.1036.18.2046.1319 [GMT 1:00]
Eseguito da: c:\users\hourfane\Desktop\ComboFix.exe
SP: Windows Defender *enabled* (Updated) {D68DDC3A-831F-4FAE-9E44-DA132C1ACF46}
.
((((((((((((((((((((((((((((((((((((( Altre eliminazioni )))))))))))))))))))))))))))))))))))))))))))))))))))
.
c:\$recycle.bin\S-1-5-21-1467351081-4176806283-3864117359-500
c:\$recycle.bin\S-1-5-21-2152478756-3922319563-605102323-500
c:\$recycle.bin\S-1-5-21-409706545-1180766039-109059347-1003
c:\$recycle.bin\S-1-5-21-409706545-1180766039-109059347-500
C:\confin.sys
c:\program files\Dealio Toolbar
c:\program files\Dealio Toolbar\config.ini
c:\program files\Dealio Toolbar\DealioToolbarIE.dll
c:\program files\Dealio Toolbar\Res\amazon.gif
c:\program files\Dealio Toolbar\Res\apple.gif
c:\program files\Dealio Toolbar\Res\barnes.gif
c:\program files\Dealio Toolbar\Res\bestbuy.gif
c:\program files\Dealio Toolbar\Res\dealio_logo.gif
c:\program files\Dealio Toolbar\Res\dealio_logo_hover.gif
c:\program files\Dealio Toolbar\Res\ebay.gif
c:\program files\Dealio Toolbar\Res\icon_settings.gif
c:\program files\Dealio Toolbar\Res\macys.gif
c:\program files\Dealio Toolbar\Res\newegg.gif
c:\program files\Dealio Toolbar\Res\overstock.gif
c:\program files\Dealio Toolbar\Res\search-button-hover.gif
c:\program files\Dealio Toolbar\Res\search-button.gif
c:\program files\Dealio Toolbar\Res\search-chevron-hover.gif
c:\program files\Dealio Toolbar\Res\search-chevron.gif
c:\program files\Dealio Toolbar\Res\search_amazon.gif
c:\program files\Dealio Toolbar\Res\search_dealio.gif
c:\program files\Dealio Toolbar\Res\search_ebay.gif
c:\program files\Dealio Toolbar\Res\search_yahoo.gif
c:\program files\Dealio Toolbar\Res\separator.gif
c:\program files\Dealio Toolbar\Res\target.gif
c:\program files\Dealio Toolbar\Res\walmart.gif
c:\program files\Dealio Toolbar\Res\widgets.xml
c:\program files\Dealio Toolbar\SearchSettingsKit.exe
c:\program files\Dealio Toolbar\WidgiHelper.exe
c:\program files\FlashGet Network
c:\program files\FlashGet Network\FlashGet universal\dbtrans_verbose.log
c:\program files\FlashGet Network\FlashGet universal\fgoption.ini
c:\program files\FlashGet Network\FlashGet universal\P2PCfg.ini
c:\program files\FlashGet Network\FlashGet universal\p2spmgr.ini
c:\program files\FlashGet Network\FlashGet universal\p4spmgr.ini
c:\program files\FlashGet Network\FlashGet universal\Profiles\config.dat
c:\program files\FlashGet Network\FlashGet universal\Profiles\tasks.dat
c:\program files\FlashGet Network\FlashGet universal\transaction.log
c:\program files\Mozilla Firefox\extensions\{8CE11043-9A15-4207-A565-0C94C42D590D}
c:\program files\Mozilla Firefox\extensions\{8CE11043-9A15-4207-A565-0C94C42D590D}\chrome.manifest
c:\program files\Mozilla Firefox\extensions\{8CE11043-9A15-4207-A565-0C94C42D590D}\chrome\content\timer.xul
c:\program files\Mozilla Firefox\extensions\{8CE11043-9A15-4207-A565-0C94C42D590D}\install.rdf
c:\program files\Search Settings
c:\program files\Search Settings\kb128\SearchSettings.dll
c:\program files\Search Settings\kb128\SearchSettingsRes409.dll
c:\program files\Search Settings\SearchSettings.exe
c:\program files\temp
c:\users\hourfane\AppData\Roaming\BITS
c:\users\hourfane\AppData\Roaming\BITS\BITS.ini
c:\users\hourfane\AppData\Roaming\BITS\DHTTable.dat
c:\users\hourfane\AppData\Roaming\SystemProc
c:\users\hourfane\Documents\cc_20081013_1957.reg
c:\windows\system32\.. ArabLionz ...URL
.
((((((((((((((((((((((((( Files Creati Da 2010-02-05 al 2010-03-05 )))))))))))))))))))))))))))))))))))
.
2010-03-05 01:18 . 2010-03-05 01:18 -------- d-----w- c:\users\hourfane\AppData\Local\temp
2010-02-27 11:10 . 2010-02-12 10:32 293376 ----a-w- c:\windows\system32\browserchoice.exe
2010-02-25 09:51 . 2010-01-23 09:26 2048 ----a-w- c:\windows\system32\tzres.dll
2010-02-25 09:50 . 2010-01-25 12:00 471552 ----a-w- c:\windows\system32\secproc_isv.dll
2010-02-25 09:50 . 2010-01-25 12:00 471552 ----a-w- c:\windows\system32\secproc.dll
2010-02-25 09:50 . 2010-01-25 08:21 526336 ----a-w- c:\windows\system32\RMActivate_isv.exe
2010-02-25 09:50 . 2010-01-25 12:00 152576 ----a-w- c:\windows\system32\secproc_ssp_isv.dll
2010-02-25 09:50 . 2010-01-25 12:00 152064 ----a-w- c:\windows\system32\secproc_ssp.dll
2010-02-25 09:50 . 2010-01-25 11:58 332288 ----a-w- c:\windows\system32\msdrm.dll
2010-02-25 09:50 . 2010-01-25 08:21 346624 ----a-w- c:\windows\system32\RMActivate_ssp_isv.exe
2010-02-25 09:50 . 2010-01-25 08:21 518144 ----a-w- c:\windows\system32\RMActivate.exe
2010-02-25 09:50 . 2010-01-25 08:21 347136 ----a-w- c:\windows\system32\RMActivate_ssp.exe
2010-02-25 09:48 . 2010-01-06 15:39 1696256 ----a-w- c:\windows\system32\gameux.dll
2010-02-25 09:48 . 2010-01-06 15:38 28672 ----a-w- c:\windows\system32\Apphlpdm.dll
2010-02-25 09:48 . 2010-01-06 13:30 4240384 ----a-w- c:\windows\system32\GameUXLegacyGDFs.dll
2010-02-24 23:37 . 2010-02-24 23:37 -------- d-----w- c:\program files\NVIDIA Corporation
2010-02-12 19:47 . 2009-12-11 11:43 302080 ----a-w- c:\windows\system32\drivers\srv.sys
2010-02-12 19:47 . 2009-12-11 11:43 98816 ----a-w- c:\windows\system32\drivers\srvnet.sys
2010-02-12 19:47 . 2009-12-08 20:01 904776 ----a-w- c:\windows\system32\drivers\tcpip.sys
2010-02-12 19:46 . 2009-12-08 17:26 30720 ----a-w- c:\windows\system32\drivers\tcpipreg.sys
2010-02-12 19:46 . 2009-12-04 18:29 1314816 ----a-w- c:\windows\system32\quartz.dll
2010-02-12 19:46 . 2009-12-04 18:28 31744 ----a-w- c:\windows\system32\msvidc32.dll
2010-02-12 19:46 . 2009-12-04 18:30 12288 ----a-w- c:\windows\system32\tsbyuv.dll
2010-02-12 19:46 . 2009-12-04 18:28 22528 ----a-w- c:\windows\system32\msyuv.dll
2010-02-12 19:46 . 2009-12-04 18:28 123904 ----a-w- c:\windows\system32\msvfw32.dll
2010-02-12 19:46 . 2009-12-04 18:28 13312 ----a-w- c:\windows\system32\msrle32.dll
2010-02-12 19:46 . 2009-12-04 18:28 82944 ----a-w- c:\windows\system32\mciavi32.dll
2010-02-12 19:46 . 2009-12-04 18:28 50176 ----a-w- c:\windows\system32\iyuv_32.dll
2010-02-12 19:46 . 2009-12-04 18:27 91136 ----a-w- c:\windows\system32\avifil32.dll
2010-02-12 19:45 . 2009-12-04 15:56 212992 ----a-w- c:\windows\system32\drivers\mrxsmb10.sys
2010-02-12 19:45 . 2009-12-04 15:56 105984 ----a-w- c:\windows\system32\drivers\mrxsmb.sys
2010-02-09 18:56 . 2010-02-09 18:56 -------- d-----w- c:\users\hourfane\AppData\Roaming\EuroTalk
2010-02-09 18:56 . 2010-02-09 18:56 -------- d-----w- c:\program files\EuroTalk
.
(((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))
.
2010-03-05 00:52 . 2007-09-29 21:26 -------- d-----w- c:\programdata\Google Updater
2010-02-27 19:42 . 2009-03-28 21:33 -------- d-----w- c:\users\hourfane\AppData\Roaming\vlc
2010-02-27 19:42 . 2007-11-21 18:32 -------- d-----w- c:\users\hourfane\AppData\Roaming\dvdcss
2010-02-26 07:02 . 2008-10-04 15:18 -------- d-----w- c:\users\hourfane\AppData\Roaming\OpenOffice.org2
2010-02-25 18:30 . 2008-10-04 15:20 1 ----a-w- c:\users\hourfane\AppData\Roaming\OpenOffice.org2\user\uno_packages\cache\stamp.sys
2010-02-25 15:23 . 2007-09-21 17:16 101632 ----a-w- c:\users\hourfane\AppData\Local\GDIPFONTCACHEV1.DAT
2010-02-24 08:16 . 2009-10-02 23:50 181632 ------w- c:\windows\system32\MpSigStub.exe
2010-02-22 16:08 . 2009-11-20 12:23 -------- d-----w- c:\program files\JDownloader
2010-02-21 19:53 . 2009-12-28 23:11 50354 ----a-w- c:\users\hourfane\AppData\Roaming\Facebook\uninstall.exe
2010-02-21 19:53 . 2009-12-28 23:11 -------- d-----w- c:\users\hourfane\AppData\Roaming\Facebook
2010-02-13 20:40 . 2006-11-02 11:18 -------- d-----w- c:\program files\Windows Mail
2010-02-13 11:38 . 2009-05-23 17:19 -------- d-----w- c:\program files\Everest Poker
2010-02-12 19:50 . 2008-05-14 19:24 -------- d-----w- c:\programdata\Messenger Plus!
2010-02-12 19:36 . 2008-05-14 19:15 -------- d-----w- c:\program files\Messenger Plus! Live
2010-02-09 00:50 . 2007-09-22 14:00 -------- d-----w- c:\programdata\eMule
2010-02-06 19:29 . 2007-12-14 18:47 -------- d-----w- c:\program files\Java
2010-02-01 22:04 . 2010-02-01 22:04 847040 ----a-w- c:\users\hourfane\AppData\Roaming\Facebook\axfbootloader.dll
2010-02-01 22:04 . 2010-02-01 22:04 5578752 ----a-w- c:\users\hourfane\AppData\Roaming\Facebook\npfbplugin_1_0_1.dll
2010-02-01 19:20 . 2010-02-01 19:20 8704 ----a-w- c:\windows\system32\SpOrder.dll
2010-02-01 19:20 . 2010-02-01 19:20 73728 ----a-w- c:\windows\system32\VistaInfo32.dll
2010-01-28 11:00 . 2010-01-28 11:00 -------- d-----w- c:\users\hourfane\AppData\Roaming\Nitro PDF
2010-01-28 10:55 . 2010-01-28 10:55 -------- d-----w- c:\programdata\Nitro PDF
2010-01-28 10:55 . 2010-01-28 10:55 -------- d-----w- c:\program files\Common Files\Nitro PDF
2010-01-28 10:55 . 2010-01-28 10:55 -------- d-----w- c:\program files\Nitro PDF
2010-01-28 10:51 . 2010-01-28 10:51 -------- d-----w- c:\users\hourfane\AppData\Roaming\Downloaded Installations
2010-01-22 19:08 . 2009-03-30 12:02 -------- d-----w- c:\program files\Microsoft Silverlight
2010-01-13 18:56 . 2010-01-13 18:56 -------- d-----w- c:\users\hourfane\AppData\Roaming\Sony Creative Software
2010-01-12 22:32 . 2009-03-30 11:31 38888 ----a-w- c:\windows\system32\perfh00C.dat
2010-01-12 22:32 . 2009-03-30 11:31 10942 ----a-w- c:\windows\system32\perfc00C.dat
2010-01-11 21:17 . 2006-11-02 12:37 -------- d-----w- c:\program files\Microsoft Games
2010-01-11 20:46 . 2010-01-11 19:47 -------- d-----w- c:\users\hourfane\AppData\Roaming\Sony
2010-01-11 19:51 . 2010-01-11 19:51 -------- d-----w- c:\users\hourfane\AppData\Roaming\Publish Providers
2010-01-11 19:41 . 2010-01-11 19:41 -------- d-----w- c:\programdata\Sony
2010-01-11 19:40 . 2008-12-22 11:22 -------- d-----w- c:\program files\Sony
2010-01-06 15:38 . 2010-02-25 09:48 173056 ----a-w- c:\windows\AppPatch\AcXtrnal.dll
2010-01-06 15:38 . 2010-02-25 09:48 542720 ----a-w- c:\windows\AppPatch\AcLayers.dll
2010-01-06 15:38 . 2010-02-25 09:48 458752 ----a-w- c:\windows\AppPatch\AcSpecfc.dll
2010-01-06 15:38 . 2010-02-25 09:48 2159616 ----a-w- c:\windows\AppPatch\AcGenral.dll
2010-01-03 00:56 . 2010-01-03 00:56 10134 ----a-r- c:\users\hourfane\AppData\Roaming\Microsoft\Installer\{E3E71D07-CD27-46CB-8448-16D4FB29AA13}\ARPPRODUCTICON.exe
2010-01-02 06:38 . 2010-01-22 02:42 916480 ----a-w- c:\windows\system32\wininet.dll
2010-01-02 06:32 . 2010-01-22 02:41 71680 ----a-w- c:\windows\system32\iesetup.dll
2010-01-02 06:32 . 2010-01-22 02:41 109056 ----a-w- c:\windows\system32\iesysprep.dll
2010-01-02 04:57 . 2010-01-22 02:41 133632 ----a-w- c:\windows\system32\ieUnatt.exe
2009-12-28 19:52 . 2009-12-28 19:52 233472 ----a-w- c:\users\hourfane\AppData\Roaming\REX Shared Library.dll
2009-12-28 19:52 . 2009-12-28 19:52 233472 ----a-w- c:\users\hourfane\AppData\Roaming\REX Shared Library.dll
2009-12-28 19:52 . 2009-12-28 19:52 225280 ----a-w- c:\users\hourfane\AppData\Roaming\Rewire.dll
2009-12-28 19:52 . 2009-12-28 19:52 225280 ----a-w- c:\users\hourfane\AppData\Roaming\Rewire.dll
2009-12-17 06:49 . 2009-12-17 06:49 5562368 ----a-w- c:\users\hourfane\AppData\Roaming\Facebook\npfbplugin_1_0_0.dll
2009-12-16 09:11 . 2009-12-16 09:11 65856 ----a-w- c:\windows\system32\NLSSRV32.EXE
2009-12-16 08:50 . 2010-01-28 10:55 17728 ----a-w- c:\windows\system32\nitrolocalui.dll
2009-12-16 08:50 . 2010-01-28 10:55 26432 ----a-w- c:\windows\system32\nitrolocalmon.dll
2007-11-09 15:25 . 2007-12-24 18:23 57344 ----a-w- c:\program files\mozilla firefox\components\MGSHelper.dll
.
((((((((((((((((((((((((((((((((((((( Punti Reg Caricati ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Nota* i valori vuoti & legittimi/default non sono visualizzati.
REGEDIT4
[HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\URLSearchHooks]
"{A3BC75A2-1F87-4686-AA43-5347D756017C}"= "c:\program files\AVG\AVG8\Toolbar\IEToolbar.dll" [2009-11-25 1230080]
[HKEY_CLASSES_ROOT\clsid\{a3bc75a2-1f87-4686-aa43-5347d756017c}]
[HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{A3BC75A2-1F87-4686-AA43-5347D756017C}]
2009-11-25 12:01 1230080 ----a-w- c:\program files\AVG\AVG8\Toolbar\IEToolbar.dll
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Internet Explorer\Toolbar]
"{CCC7A320-B3CA-4199-B1A6-9F516DD69829}"= "c:\program files\AVG\AVG8\Toolbar\IEToolbar.dll" [2009-11-25 1230080]
[HKEY_CLASSES_ROOT\clsid\{ccc7a320-b3ca-4199-b1a6-9f516dd69829}]
[HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Toolbar\Webbrowser]
"{CCC7A320-B3CA-4199-B1A6-9F516DD69829}"= "c:\program files\AVG\AVG8\Toolbar\IEToolbar.dll" [2009-11-25 1230080]
[HKEY_CLASSES_ROOT\clsid\{ccc7a320-b3ca-4199-b1a6-9f516dd69829}]
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"MsnMsgr"="c:\program files\Windows Live\Messenger\MsnMsgr.Exe" [2009-07-26 3883856]
"swg"="c:\program files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe" [2007-09-29 68856]
"WMPNSCFG"="c:\program files\Windows Media Player\WMPNSCFG.exe" [2008-01-19 202240]
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"AVG8_TRAY"="c:\progra~1\AVG\AVG8\avgtray.exe" [2009-12-12 2043160]
"SunJavaUpdateSched"="c:\program files\Java\jre6\bin\jusched.exe" [2009-10-11 149280]
c:\users\hourfane\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\
Sommaire de OneNote.onetoc2 [2009-3-11 3656]
[HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system]
"EnableLUA"= 0 (0x0)
"FilterAdministratorToken"= 1 (0x1)
"EnableUIADesktopToggle"= 0 (0x0)
[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\windows]
"AppInit_DLLs"=c:\windows\System32\avgrsstx.dll
[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\drivers32]
"aux4"=wdmaud.drv
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\WinDefend]
@="Service"
[HKLM\~\startupfolder\C:^Users^hourfane^AppData^Roaming^Microsoft^Windows^Start Menu^Programs^Startup^OneNote 2007 - Capture d'écran et lancement.lnk]
path=c:\users\hourfane\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\OneNote 2007 - Capture d'écran et lancement.lnk
backup=c:\windows\pss\OneNote 2007 - Capture d'écran et lancement.lnk.Startup
backupExtension=.Startup
[HKLM\~\startupfolder\C:^Users^hourfane^AppData^Roaming^Microsoft^Windows^Start Menu^Programs^Startup^OpenOffice.org 2.4.lnk]
path=c:\users\hourfane\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\OpenOffice.org 2.4.lnk
backup=c:\windows\pss\OpenOffice.org 2.4.lnk.Startup
backupExtension=.Startup
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\CCUTRAYICON]
FactoryMode [X]
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher]
2009-02-27 15:10 35696 ----a-w- c:\program files\Adobe\Reader 9.0\Reader\reader_sl.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Athan]
2009-08-23 00:14 1114112 ----a-w- c:\program files\Athan\Athan.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\DAEMON Tools Lite]
2009-04-23 13:51 691656 ----a-w- c:\program files\DAEMON Tools Lite\daemon.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\ehTray.exe]
2008-01-19 07:33 125952 ----a-w- c:\windows\ehome\ehtray.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\HP Software Update]
2007-05-08 14:24 54840 ----a-w- c:\program files\HP\HP Software Update\hpwuSchd2.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\hpsysdrv]
2006-09-28 13:42 65536 ----a-w- c:\hp\support\hpsysdrv.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\IAAnotif]
2007-04-19 16:11 151552 ----a-w- c:\program files\Intel\Intel Matrix Storage Manager\IAAnotif.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\iTunesHelper]
2009-04-02 14:11 342312 ----a-w- c:\program files\iTunes\iTunesHelper.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\KBD]
2006-12-08 16:16 65536 ----a-w- c:\hp\KBD\KbdStub.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Launcher]
2007-03-07 09:09 44168 ----a-w- c:\windows\SMINST\Launcher.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\LDM]
2007-09-21 21:40 20480 ----a-w- c:\program files\Logitech\Desktop Messenger\8876480\Program\backWeb-8876480.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\OsdMaestro]
2007-02-15 10:59 118784 ----a-w- c:\program files\Hewlett-Packard\On-Screen OSD Indicator\OSD.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\QuickTime Task]
2009-01-05 14:18 413696 ----a-w- c:\program files\QuickTime\QTTask.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Sidebar]
2009-04-11 06:28 1233920 ----a-w- c:\program files\Windows Sidebar\sidebar.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\SunJavaUpdateSched]
2009-10-11 03:17 149280 ----a-w- c:\program files\Java\jre6\bin\jusched.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\swg]
2007-09-29 21:26 68856 ----a-w- c:\program files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Windows Defender]
2008-01-19 07:38 1008184 ----a-w- c:\program files\Windows Defender\MSASCui.exe
[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\WMPNSCFG]
2008-01-19 07:33 202240 ----a-w- c:\program files\Windows Media Player\wmpnscfg.exe
[HKEY_LOCAL_MACHINE\software\microsoft\security center\Monitoring]
"DisableMonitoring"=dword:00000001
[HKEY_LOCAL_MACHINE\software\microsoft\security center\Monitoring\SymantecAntiVirus]
"DisableMonitoring"=dword:00000001
[HKEY_LOCAL_MACHINE\software\microsoft\security center\Monitoring\SymantecFirewall]
"DisableMonitoring"=dword:00000001
R0 sptd;sptd;c:\windows\System32\Drivers\sptd.sys [2009-05-02 721904]
R2 DQLWinService;DQLWinService;c:\program files\Common Files\Intel\IntelDH\NMS\AdpPlugins\DQLWinService.exe [2006-09-03 208896]
R2 gupdate1ca2bf9ef43a62b;Service Google Update (gupdate1ca2bf9ef43a62b);c:\program files\Google\Update\GoogleUpdate.exe [2009-09-02 133104]
R2 IntelDHSvcConf;Intel DH Service;c:\program files\Intel\IntelDH\Intel Media Server\Tools\IntelDHSvcConf.exe [2006-05-10 29696]
R3 fbxusb;Carte réseau virtuelle FreeBox USB;c:\windows\system32\DRIVERS\fbxusb32.sys [2004-10-20 21344]
R3 netr73;RT73 USB Wireless LAN Card Driver for Vista;c:\windows\system32\DRIVERS\netr73.sys [2007-01-04 255488]
R3 UsbSagCom;Mobile Device Full USB Driver;c:\windows\system32\DRIVERS\UsbSagCom.sys [2007-06-29 51712]
S1 AvgLdx86;AVG Free AVI Loader Driver x86;c:\windows\System32\Drivers\avgldx86.sys [2009-08-29 335240]
S1 AvgTdiX;AVG Free8 Network Redirector;c:\windows\System32\Drivers\avgtdix.sys [2009-05-17 108552]
S1 FNETDEVI;FNETDEVI;c:\windows\system32\drivers\FNETDEVI.SYS [2008-10-18 19572]
S2 avg8emc;AVG Free8 E-mail Scanner;c:\progra~1\AVG\AVG8\avgemc.exe [2009-08-29 908056]
S2 avg8wd;AVG Free8 WatchDog;c:\progra~1\AVG\AVG8\avgwdsvc.exe [2009-08-29 297752]
S2 NitroDriverReadSpool;NitroPDFDriverCreatorReadSpool;c:\program files\Nitro PDF\Professional\NitroPDFDriverService.exe [2009-12-16 188736]
S2 nlsX86cc;NLS Service;c:\windows\system32\NLSSRV32.EXE [2009-12-16 65856]
[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
HPZ12 REG_MULTI_SZ Pml Driver HPZ12 Net Driver HPZ12
hpdevmgmt REG_MULTI_SZ hpqcxs08
LocalServiceAndNoImpersonation REG_MULTI_SZ FontCache
.
Contenuto della cartella 'Scheduled Tasks'
2010-03-05 c:\windows\Tasks\Google Software Updater.job
- c:\program files\Google\Common\Google Updater\GoogleUpdaterService.exe [2007-09-29 19:16]
2010-03-05 c:\windows\Tasks\GoogleUpdateTaskMachineCore.job
- c:\program files\Google\Update\GoogleUpdate.exe [2009-09-02 18:19]
2010-03-05 c:\windows\Tasks\GoogleUpdateTaskMachineUA.job
- c:\program files\Google\Update\GoogleUpdate.exe [2009-09-02 18:19]
2010-03-04 c:\windows\Tasks\User_Feed_Synchronization-{05EAAE1A-3231-43CB-BE4B-BDD6362824EF}.job
- c:\windows\system32\msfeedssync.exe [2010-01-22 04:56]
.
.
------- Scansione supplementare -------
.
uStart Page = hxxp://search.babylon.com/home
mWindow Title =
uInternet Settings,ProxyServer = 127.0.0.1:8080
uInternet Settings,ProxyOverride = local
IE: &Tout télécharger avec FlashGet - c:\program files\FlashGet\jc_all.htm
IE: &Télécharger avec FlashGet - c:\program files\FlashGet\jc_link.htm
IE: E&xporter vers Microsoft Excel - c:\progra~1\MICROS~3\Office12\EXCEL.EXE/3000
IE: Translate this web page with Babylon - c:\program files\Babylon\Babylon-Pro\Utils\BabylonIEPI.dll/ActionTU.htm
IE: Translate with Babylon - c:\program files\Babylon\Babylon-Pro\Utils\BabylonIEPI.dll/Action.htm
IE: {{F72841F0-4EF1-4df5-BCE5-B3AC8ACF5478} - res://c:\program files\Babylon\Babylon-Pro\Utils\BabylonIEPI.dll/ActionTU.htm
DPF: {5D86DDB5-BDF9-441B-9E9E-D4730F4EE499} - hxxp://www.bitdefender.fr/scan_fr/scan8/oscan8.cab
DPF: {FF3BA0DA-79B5-4110-8FAC-C402D85AAEDA}
FF - ProfilePath - c:\users\hourfane\AppData\Roaming\Mozilla\Firefox\Profiles\my4998sp.default\
FF - prefs.js: browser.search.defaulturl - hxxp://search.conduit.com/ResultsExt.aspx?ctid=CT2233703&SearchSource=3&q={searchTerms}
FF - prefs.js: browser.search.selectedEngine - Google
FF - prefs.js: browser.startup.homepage - Fast dial
FF - component: c:\program files\AVG\AVG8\Firefox\components\avgssff.dll
FF - component: c:\program files\AVG\AVG8\Toolbar\Firefox\avg@igeared\components\IGeared_tavgp_xputils2.dll
FF - component: c:\program files\AVG\AVG8\Toolbar\Firefox\avg@igeared\components\IGeared_tavgp_xputils3.dll
FF - component: c:\program files\AVG\AVG8\Toolbar\Firefox\avg@igeared\components\IGeared_tavgp_xputils35.dll
FF - component: c:\program files\AVG\AVG8\Toolbar\Firefox\avg@igeared\components\xpavgtbapi.dll
FF - component: c:\program files\Mozilla Firefox\components\MGSHelper.dll
FF - plugin: c:\program files\Google\Google Earth\plugin\npgeplugin.dll
FF - plugin: c:\program files\Google\Google Updater\2.4.1536.6592\npCIDetect13.dll
FF - plugin: c:\program files\Google\Update\1.2.183.17\npGoogleOneClick8.dll
FF - plugin: c:\program files\Microsoft\Office Live\npOLW.dll
FF - plugin: c:\program files\Windows Live\Photo Gallery\NPWLPG.dll
FF - plugin: c:\users\hourfane\AppData\Roaming\Facebook\npfbplugin_1_0_0.dll
FF - plugin: c:\users\hourfane\AppData\Roaming\Facebook\npfbplugin_1_0_1.dll
FF - HiddenExtension: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\windows\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension\
.
- - - - CHIAVI ORFANE RIMOSSE - - - -
URLSearchHooks-*{b2e293ee-fd7e-4c71-a714-5f4750d8d7b7} - (no file)
BHO-{01398B87-61AF-4FFB-9AB5-1A1C5FB39A9C} - c:\program files\Dealio Toolbar\DealioToolbarIE.dll
Toolbar-{01398B87-61AF-4FFB-9AB5-1A1C5FB39A9C} - c:\program files\Dealio Toolbar\DealioToolbarIE.dll
HKCU-Run-fsm - (no file)
MSConfigStartUp-RtHDVCpl - RtHDVCpl.exe
MSConfigStartUp-SearchSettings - c:\program files\Search Settings\SearchSettings.exe
AddRemove-{6AF49698-949A-4C89-9B31-041D2CCB5FBD} - c:\program files\InstallShield Installation Information\{6AF49698-949A-4C89-9B31-041D2CCB5FBD}\setup.exe
**************************************************************************
catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2010-03-05 02:18
Windows 6.0.6002 Service Pack 2 NTFS
scansione processi nascosti ...
scansione entrate autostart nascoste ...
Scansione files nascosti ...
Scansione completata con successo
Files nascosti: 0
**************************************************************************
[HKEY_LOCAL_MACHINE\system\ControlSet001\Services\istkptowiperxqf]
"imagepath"="\??\c:\windows\TEMP\DAB5.tmp"
.
--------------------- CHIAVI DI REGISTRO BLOCCATE ---------------------
[HKEY_USERS\S-1-5-21-409706545-1180766039-109059347-1001\Software\SecuROM\!CAUTION! NEVER A OR CHANGE ANY KEY*]
@Allowed: (Read) (RestrictedCode)
[HKEY_LOCAL_MACHINE\system\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0000\AllUserSettings]
@Denied: (A) (Users)
@Denied: (A) (Everyone)
@Allowed: (B 1 2 3 4 5) (S-1-5-20)
"BlindDial"=dword:00000000
[HKEY_LOCAL_MACHINE\system\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0001\AllUserSettings]
@Denied: (A) (Users)
@Denied: (A) (Everyone)
@Allowed: (B 1 2 3 4 5) (S-1-5-20)
"BlindDial"=dword:00000000
[HKEY_LOCAL_MACHINE\system\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0002\AllUserSettings]
@Denied: (A) (Users)
@Denied: (A) (Everyone)
@Allowed: (B 1 2 3 4 5) (S-1-5-20)
"BlindDial"=dword:00000000
.
Ora fine scansione: 2010-03-05 02:21:26
ComboFix-quarantined-files.txt 2010-03-05 01:21
Pre-Run: 53 679 210 496 octets libres
Post-Run: 61 480 308 736 octets libres
- - End Of File - - 4BDA001F9513C116F21EB2A763A104E1 -
ModérateurTrès bien, on a fait du ménage. Le souci de ton fichier .sys n'est pas encore résolu.
ADR.
Télécharge LopS&D (de eric_71)
= = = = >>> En cliquant ici <<< = = = =
Enregistre le fichier sur ton bureau.
Clique droit sur le fichier téléchargé (LopSD.exe) puis sélectionne 'Exécuter en tant qu'administrateur'.
Une fois le programme lancé tape F pour être en Français.
Réponds OK au message d'alerte qui s'affiche.
Puis exécute l'option 1, Recherche.
Un rapport sera généré.
Poste son intégralité ici.
Note :
Le rapport se trouve ici : C:\LopR.txt
Petit tutorial si besoin ICI. -
--------------------\\ Lop S&D 4.2.5-0 XP/Vista
Microsoft® Windows Vista™ Édition Familiale Premium ( v6.0.6002 ) Service Pack 2
X86-based PC ( Multiprocessor Free : Intel(R) Core(TM)2 CPU 4400 @ 2.00GHz )
BIOS : Phoenix - AwardBIOS v6.00PG
USER : hourfane ( Administrator )
BOOT : Normal boot
C:\ (Local Disk) - NTFS - Total:290 Go (Free:57 Go)
D:\ (Local Disk) - NTFS - Total:8 Go (Free:1 Go)
E:\ (CD or DVD)
F:\ (CD or DVD)
G:\ (CD or DVD)
H:\ (CD or DVD)
I:\ (USB)
J:\ (USB)
K:\ (USB)
L:\ (USB)
"C:\Lop SD" ( MAJ : 19-12-2008|23:40 )
Option : [1] ( 05/03/2010|12:38 )
[ UAC => 0 ]
--------------------\\ Listing des dossiers dans Local
[03/05/2009|00:59] C:\Users\hourfane\AppData\Local\Adobe
[24/12/2007|17:51] C:\Users\hourfane\AppData\Local\Apple
[24/12/2007|23:26] C:\Users\hourfane\AppData\Local\Apple Computer
[21/09/2007|18:05] C:\Users\hourfane\AppData\Local\Application Data
[15/03/2008|20:32] C:\Users\hourfane\AppData\Local\Apps
[27/06/2009|11:01] C:\Users\hourfane\AppData\Local\AVG Security Toolbar
[01/07/2009|21:30] C:\Users\hourfane\AppData\Local\Babylon
[18/09/2009|11:59] C:\Users\hourfane\AppData\Local\d3d9caps.dat
[03/03/2010|22:13] C:\Users\hourfane\AppData\Local\DCBC2A71-70D8-4DAN-EHR8-E0D61DEA3FDF.ini
[09/02/2010|01:50] C:\Users\hourfane\AppData\Local\eMule
[25/02/2010|16:23] C:\Users\hourfane\AppData\Local\GDIPFONTCACHEV1.DAT
[01/12/2009|20:33] C:\Users\hourfane\AppData\Local\Google
[21/09/2007|18:05] C:\Users\hourfane\AppData\Local\Historique
[05/03/2010|02:25] C:\Users\hourfane\AppData\Local\IconCache.db
[21/09/2007|22:24] C:\Users\hourfane\AppData\Local\Logitech-LS
[28/01/2010|14:12] C:\Users\hourfane\AppData\Local\Microsoft
[03/09/2008|19:20] C:\Users\hourfane\AppData\Local\Microsoft Games
[14/07/2008|21:37] C:\Users\hourfane\AppData\Local\Microsoft Help
[04/10/2007|20:54] C:\Users\hourfane\AppData\Local\MicroVision Applications
[05/10/2007|19:52] C:\Users\hourfane\AppData\Local\Mozilla
[01/02/2010|20:19] C:\Users\hourfane\AppData\Local\NetScop
[18/03/2009|20:00] C:\Users\hourfane\AppData\Local\PokerLauncher
[08/03/2008|16:05] C:\Users\hourfane\AppData\Local\PunkBuster
[11/01/2010|20:47] C:\Users\hourfane\AppData\Local\Sony
[05/03/2010|12:37] C:\Users\hourfane\AppData\Local\temp
[21/09/2007|18:05] C:\Users\hourfane\AppData\Local\Temporary Internet Files
[02/05/2009|09:46] C:\Users\hourfane\AppData\Local\uykyk.bat
[09/10/2007|19:35] C:\Users\hourfane\AppData\Local\VirtualStore
--------------------\\ Tâches planifiées dans C:\Windows\tasks
[05/03/2010 01:44][--a------] C:\Windows\tasks\GoogleUpdateTaskMachineUA.job
[05/03/2010 12:34][--a------] C:\Windows\tasks\GoogleUpdateTaskMachineCore.job
[05/03/2010 12:36][--a------] C:\Windows\tasks\Google Software Updater.job
[04/03/2010 18:32][--ah-----] C:\Windows\tasks\User_Feed_Synchronization-{05EAAE1A-3231-43CB-BE4B-BDD6362824EF}.job
[05/03/2010 12:34][--ah-----] C:\Windows\tasks\SA.DAT
[05/03/2010 02:25][--a------] C:\Windows\tasks\SCHEDLGU.TXT
--------------------\\ Listing des dossiers dans C:\ProgramData
[01/06/2007|21:58] C:\ProgramData\{623D32E9-0C62-4453-AD44-98B31F52A5E1}
[10/05/2009|14:17] C:\ProgramData\{8CD7F5AF-ECFA-4793-BF40-D8F42DBFF906}
[02/05/2009|23:46] C:\ProgramData\Adobe
[09/11/2007|21:30] C:\ProgramData\Age of Empires 3
[24/12/2007|17:48] C:\ProgramData\Apple
[10/05/2009|14:15] C:\ProgramData\Apple Computer
[02/11/2006|14:02] C:\ProgramData\Application Data
[29/11/2009|18:08] C:\ProgramData\AVG Security Toolbar
[17/05/2009|01:07] C:\ProgramData\avg8
[02/03/2008|18:38] C:\ProgramData\AVS4YOU
[01/07/2009|21:30] C:\ProgramData\Babylon
[21/09/2007|18:02] C:\ProgramData\Bureau
[22/12/2008|12:40] C:\ProgramData\BVRP Software
[02/05/2009|23:58] C:\ProgramData\DAEMON Tools Lite
[02/11/2006|14:02] C:\ProgramData\Desktop
[02/11/2006|14:02] C:\ProgramData\Documents
[09/02/2010|01:50] C:\ProgramData\eMule
[21/09/2007|18:02] C:\ProgramData\Favoris
[02/11/2006|14:02] C:\ProgramData\Favorites
[02/05/2009|17:25] C:\ProgramData\Google
[05/03/2010|01:52] C:\ProgramData\Google Updater
[30/04/2009|00:27] C:\ProgramData\Hewlett-Packard
[01/06/2007|21:44] C:\ProgramData\HP
[30/04/2009|00:25] C:\ProgramData\hpzinstall.log
[01/06/2007|21:41] C:\ProgramData\Intel
[03/03/2009|15:02] C:\ProgramData\KONAMI
[10/07/2009|00:08] C:\ProgramData\LauncherAccess.dt
[08/07/2009|21:48] C:\ProgramData\ma-config.com
[02/05/2009|12:26] C:\ProgramData\Malwarebytes
[21/09/2007|18:02] C:\ProgramData\Menu D‚marrer
[12/02/2010|20:50] C:\ProgramData\Messenger Plus!
[06/11/2009|13:31] C:\ProgramData\Microsoft
[09/12/2009|20:05] C:\ProgramData\Microsoft Help
[21/09/2007|18:02] C:\ProgramData\ModŠles
[05/10/2007|19:52] C:\ProgramData\Mozilla
[01/06/2007|21:53] C:\ProgramData\muvee Technologies
[28/01/2010|11:55] C:\ProgramData\Nitro PDF
[02/05/2009|17:32] C:\ProgramData\NortonInstaller
[03/05/2009|01:02] C:\ProgramData\ntuser.pol
[18/09/2009|11:59] C:\ProgramData\NVIDIA
[02/09/2009|19:47] C:\ProgramData\nvModes.001
[02/09/2009|19:47] C:\ProgramData\nvModes.dat
[01/06/2007|21:59] C:\ProgramData\PC-Doctor
[06/01/2009|13:43] C:\ProgramData\POPWWPROFILES
[28/12/2009|20:52] C:\ProgramData\Propellerhead Software
[04/10/2007|20:53] C:\ProgramData\Roxio
[10/03/2009|22:08] C:\ProgramData\Skype
[28/09/2007|17:27] C:\ProgramData\Sonic
[11/01/2010|20:41] C:\ProgramData\Sony
[22/12/2008|12:16] C:\ProgramData\Sony Ericsson
[12/05/2009|17:33] C:\ProgramData\Spybot - Search & Destroy
[02/11/2006|14:02] C:\ProgramData\Start Menu
[29/01/2010|13:12] C:\ProgramData\TEMP
[02/11/2006|14:02] C:\ProgramData\Templates
[25/04/2008|23:49] C:\ProgramData\Ubisoft
[26/02/2008|18:20] C:\ProgramData\WLInstaller
--------------------\\ Listing des dossiers dans C:\Program Files
[01/06/2007|21:58] C:\Program Files\Activation Assistant for the 2007 Microsoft Office suites
[02/05/2009|23:46] C:\Program Files\Adobe
[18/09/2009|11:59] C:\Program Files\AGEIA Technologies
[09/11/2007|15:31] C:\Program Files\Alwil Software
[19/11/2009|20:41] C:\Program Files\AnalogX
[10/05/2009|14:03] C:\Program Files\Apple Software Update
[23/11/2009|21:33] C:\Program Files\Athan
[22/12/2008|12:40] C:\Program Files\Avanquest update
[17/05/2009|01:07] C:\Program Files\AVG
[21/09/2009|11:57] C:\Program Files\AVS4YOU
[22/03/2009|23:56] C:\Program Files\Betsson
[02/05/2009|23:49] C:\Program Files\CCleaner
[25/12/2007|23:32] C:\Program Files\CDex_150
[05/03/2010|02:14] C:\Program Files\Common Files
[02/05/2009|23:58] C:\Program Files\DAEMON Tools Lite
[14/02/2008|18:23] C:\Program Files\DivX
[02/06/2007|07:07] C:\Program Files\EasyBits
[03/01/2010|01:45] C:\Program Files\Electronic Arts
[09/02/2010|19:56] C:\Program Files\EuroTalk
[13/02/2010|12:38] C:\Program Files\Everest Poker
[18/10/2008|17:05] C:\Program Files\FAT32 Format
[21/09/2007|18:02] C:\Program Files\Fichiers communs [C:\Program Files\Common Files]
[12/04/2009|11:10] C:\Program Files\FlashGet
[18/09/2009|17:57] C:\Program Files\Free Audio Pack
[21/09/2009|18:47] C:\Program Files\Free FLV Converter
[02/09/2009|19:19] C:\Program Files\Google
[09/10/2009|16:55] C:\Program Files\Guitar Pro 5
[10/12/2009|18:39] C:\Program Files\Happy Note
[29/04/2009|23:35] C:\Program Files\Hewlett-Packard
[08/06/2009|16:28] C:\Program Files\HP
[11/09/2008|20:11] C:\Program Files\Illustrate
[10/07/2009|17:22] C:\Program Files\InfraRecorder
[03/01/2010|01:45] C:\Program Files\InstallShield Installation Information
[01/06/2007|21:41] C:\Program Files\Intel
[27/01/2010|16:56] C:\Program Files\Internet Explorer
[10/05/2009|14:16] C:\Program Files\iPod
[10/05/2009|14:17] C:\Program Files\iTunes
[21/01/2009|16:08] C:\Program Files\iVideoMAX
[06/02/2010|20:29] C:\Program Files\Java
[22/02/2010|17:08] C:\Program Files\JDownloader
[09/05/2009|10:59] C:\Program Files\JkDefrag
[02/03/2009|12:27] C:\Program Files\KONAMI
[21/09/2007|22:47] C:\Program Files\Logitech
[08/07/2009|21:48] C:\Program Files\ma-config.com
[20/03/2009|17:53] C:\Program Files\Magicbit
[02/05/2009|12:26] C:\Program Files\Malwarebytes' Anti-Malware
[12/02/2010|20:36] C:\Program Files\Messenger Plus! Live
[24/12/2007|19:24] C:\Program Files\MGS FF Helper
[06/11/2009|13:32] C:\Program Files\Microsoft
[11/01/2010|22:17] C:\Program Files\Microsoft Games
[01/06/2007|21:57] C:\Program Files\Microsoft Office
[22/01/2010|20:08] C:\Program Files\Microsoft Silverlight
[06/11/2009|13:30] C:\Program Files\Microsoft SQL Server Compact Edition
[06/11/2009|13:31] C:\Program Files\Microsoft Sync Framework
[15/10/2009|19:52] C:\Program Files\Microsoft Works
[03/01/2010|01:56] C:\Program Files\Microsoft WSE
[01/06/2007|21:57] C:\Program Files\Microsoft.NET
[31/08/2009|18:29] C:\Program Files\Movie Maker
[05/03/2010|12:35] C:\Program Files\Mozilla Firefox
[09/10/2007|19:46] C:\Program Files\MP3 WAV Converter
[02/11/2006|13:37] C:\Program Files\MSBuild
[12/04/2009|17:56] C:\Program Files\MSXML 4.0
[01/06/2007|21:53] C:\Program Files\muvee Technologies
[28/01/2010|11:55] C:\Program Files\Nitro PDF
[25/02/2010|00:37] C:\Program Files\NVIDIA Corporation
[04/02/2008|20:00] C:\Program Files\OpenOffice.org 2.3
[04/10/2008|16:15] C:\Program Files\OpenOffice.org 2.4
[29/08/2009|18:30] C:\Program Files\PacificPoker
[01/06/2007|22:10] C:\Program Files\PC-Doctor 5 for Windows
[27/10/2008|12:28] C:\Program Files\PDFCreator
[27/10/2008|12:28] C:\Program Files\PDFCreator Toolbar
[25/08/2008|23:24] C:\Program Files\PeerTV
[10/04/2008|22:20] C:\Program Files\PhotoFiltre
[02/05/2008|09:12] C:\Program Files\Playlogic
[28/12/2009|20:52] C:\Program Files\Propellerhead
[10/05/2009|14:16] C:\Program Files\QuickTime
[01/06/2007|21:52] C:\Program Files\Real
[30/03/2009|11:48] C:\Program Files\Realtek
[02/11/2006|13:37] C:\Program Files\Reference Assemblies
[28/12/2007|01:58] C:\Program Files\SAGEM
[10/06/2009|11:29] C:\Program Files\Samsung
[06/09/2008|15:13] C:\Program Files\Sega
[01/06/2007|22:02] C:\Program Files\Services en ligne
[31/10/2009|01:45] C:\Program Files\SodeaSoft
[11/01/2010|20:40] C:\Program Files\Sony
[22/12/2008|12:22] C:\Program Files\Sony Ericsson
[19/10/2007|11:32] C:\Program Files\Sony Setup
[12/05/2009|17:33] C:\Program Files\Spybot - Search & Destroy
[24/06/2009|23:35] C:\Program Files\SpywareBlaster
[10/05/2009|16:23] C:\Program Files\SystemRequirementsLab
[16/05/2009|15:22] C:\Program Files\trend micro
[18/04/2008|19:28] C:\Program Files\Ubi Soft
[12/12/2008|23:45] C:\Program Files\Ubisoft
[02/11/2006|14:01] C:\Program Files\Uninstall Information
[28/03/2009|22:32] C:\Program Files\VideoLAN
[17/10/2007|13:38] C:\Program Files\VirtualDJ
[31/08/2009|18:29] C:\Program Files\Windows Calendar
[31/08/2009|18:29] C:\Program Files\Windows Collaboration
[31/08/2009|18:29] C:\Program Files\Windows Defender
[31/08/2009|18:29] C:\Program Files\Windows Journal
[06/11/2009|13:32] C:\Program Files\Windows Live
[13/06/2009|10:31] C:\Program Files\Windows Live Safety Center
[06/11/2009|13:28] C:\Program Files\Windows Live SkyDrive
[13/02/2010|21:40] C:\Program Files\Windows Mail
[28/10/2009|18:11] C:\Program Files\Windows Media Player
[21/09/2007|18:02] C:\Program Files\Windows NT
[31/08/2009|18:29] C:\Program Files\Windows Photo Gallery
[28/10/2009|22:27] C:\Program Files\Windows Portable Devices
[05/09/2009|23:01] C:\Program Files\Windows Sidebar
[26/10/2007|12:34] C:\Program Files\WinRAR
[03/02/2009|12:20] C:\Program Files\WorkoutLogger
[02/05/2009|17:24] C:\Program Files\Yahoo!
--------------------\\ Listing des dossiers dans C:\Program Files\Common Files
[02/05/2009|23:46] C:\Program Files\Common Files\Adobe
[10/05/2009|14:16] C:\Program Files\Common Files\Apple
[21/09/2009|11:57] C:\Program Files\Common Files\AVSMedia
[01/06/2007|21:57] C:\Program Files\Common Files\DESIGNER
[29/04/2009|23:30] C:\Program Files\Common Files\Hewlett-Packard
[01/06/2007|21:44] C:\Program Files\Common Files\HP
[21/09/2007|22:11] C:\Program Files\Common Files\InstallShield
[01/06/2007|21:41] C:\Program Files\Common Files\Intel
[01/06/2007|21:52] C:\Program Files\Common Files\LightScribe
[01/06/2007|21:51] C:\Program Files\Common Files\LS Getting Started
[14/10/2007|17:45] C:\Program Files\Common Files\MAGIX Shared
[27/02/2010|20:42] C:\Program Files\Common Files\microsoft shared
[01/06/2007|21:53] C:\Program Files\Common Files\muvee Technologies
[28/01/2010|11:55] C:\Program Files\Common Files\Nitro PDF
[14/02/2008|18:23] C:\Program Files\Common Files\PX Storage Engine
[27/09/2007|18:32] C:\Program Files\Common Files\Real
[04/10/2007|20:53] C:\Program Files\Common Files\Roxio Shared
[07/04/2009|22:10] C:\Program Files\Common Files\Scanner
[02/11/2006|12:18] C:\Program Files\Common Files\Services
[22/12/2008|12:23] C:\Program Files\Common Files\Sony Shared
[02/11/2006|12:18] C:\Program Files\Common Files\SpeechEngines
[06/05/2009|10:30] C:\Program Files\Common Files\Symantec Shared
[05/09/2009|23:00] C:\Program Files\Common Files\System
[08/02/2009|22:35] C:\Program Files\Common Files\Windows Live
[26/02/2008|18:25] C:\Program Files\Common Files\WindowsLiveInstaller
[10/05/2009|16:53] C:\Program Files\Common Files\Wise Installation Wizard
--------------------\\ Process
( 63 Processes )
... OK !
--------------------\\ Recherche avec S_Lop
Aucun fichier / dossier Lop trouvé !
--------------------\\ Recherche de Fichiers / Dossiers Lop
Aucun fichier / dossier Lop trouvé !
--------------------\\ Verification du Registre
..... OK !
--------------------\\ Verification du fichier Hosts
Fichier Hosts PROPRE
--------------------\\ Recherche de fichiers avec Catchme
catchme 0.3.1353 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2010-03-05 12:39:00
Windows 6.0.6002 Service Pack 2 NTFS
scanning hidden processes ...
scanning hidden files ...
scan completed successfully
hidden processes: 0
hidden files: 157
--------------------\\ Recherche d'autres infections
--------------------\\ Cracks & Keygens ..
C:\Users\hourfane\Desktop\bordel de music buro\Thisis50.com-Crack A Bottle - Eminem Feat Dr Dre And 50 Cent.lnk
C:\Users\hourfane\Desktop\MP3 ISMAIL\all dossier haf doc cours.. mp4\Thisis50.com-Crack A Bottle - Eminem Feat Dr Dre And 50 Cent.lnk
C:\Users\hourfane\Documents\HAFID\all dossier haf doc cours.. mp4\Thisis50.com-Crack A Bottle - Eminem Feat Dr Dre And 50 Cent.lnk
C:\Users\hourfane\Music\Crack A Bottle - Eminem Feat Dr Dre And 50 Cent.mp3
C:\Users\hourfane\Music\mp4 hafid\rik1 dossier 7\D-Rich - Whats Cracking (Produced By Scott Storch) (Newest Member Of G-Unit).mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\01-kochece-im_in_da_hood.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\02-lil_wayne-lollipop_remix_feat._kanye_west.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\03-blood_raw-chevy_boys_feat._rick_ross_and_young_jeezy.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\04-lil_wayne-got_money_feat._t-pain.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\05-lil_wayne-stacks_on_deck_feat._tyga.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\06-lil_wayne-thinkin_of_you_feat._tyga.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\07-lil_wayne-me_and_my_drink_feat._short_dawg.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\09-young_jeezy-put_on_feat._kanye_west.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\12-2_pistals-closed_eyes_feat._young_jeezy.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\13-lil_wayne-let_us_pray_feat._juelz_santana.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\15-lil_wayne-single.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\Lil Wayne ft. Static - Lollipop (Remix 2oo8)-NgT- (FULL).mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\Macy Gray feat. The Game - Only in the dark.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\Mr_ Criminal _amp_amp_ DJ AK _amp_quot_Bump_ Bump_ Bump_amp_quot_.mp3
C:\Users\hourfane\Music\Music\VA-Kochece_Lil_Wayne_Young_Jeezy_DJ_Mino-Crack_Phenomenon-Bootleg-2008\Roger Troutman - California Love.mp3
C:\Users\hourfane\Music\rapp\Alpha_5.20-Vivre_Et_Mourir_A_Dakar-FR-\16-alpha_5.20-mon_crack_feat_iron_sy_and_lino.mp3
C:\Users\hourfane\Music\Rockin'Squat - 2007 - Too Hot For TV\05 - Rockin' Squat - Too Hot For Tv - Crack Game.mp3
[F:17][D:11]-> C:\Users\hourfane\AppData\Local\Temp
[F:2][D:1]-> C:\Users\hourfane\AppData\Roaming\MICROS~1\Windows\Cookies
[F:3][D:1]-> C:\$Recycle.Bin
1 - "C:\Lop SD\LopR_1.txt" - 05/03/2010|12:41 - Option : [1]
--------------------\\ Fin du rapport a 12:41:27
[ UAC => 1 ] -
ModérateurTélécharge SEAF.exe de C_XX sur ton bureau :
= = = = =>>> En cliquant ici <<<= = = = =
* Clique droit sur SEAF.exe et sélectionne "Exécuter en tant qu'administrateur" pour le lancer.
* Une fenêtre va s'ouvrir.
* Copie-colle ceci dans la barre de recherche blanche iaStor.sys
* Coche sur la droite : "Chercher également dans le registre"
* Coche en bas "Afficher les ADS" et "Informations supplémentaires" tape sur [Entrée]
* Clique ensuite sur "Lancer la recherche".
* Patiente pendant la recherche.
* Une fenêtre avec un rapport au format ".txt" va s'afficher.
* Copie/colle ce rapport dans ta prochaine réponse.
******
Recherche avec Ad-Remover :
Télécharge Ad-Remover ( de Cyrildu17 / C_XX ) sur ton bureau :
= = = =>>> En cliquant ici <<<= = = =
/!\ Déconnectes toi et fermes toutes applications en cours, désactive ton antivirus le temps de la manipulation/!\
* Double clique sur le programme d'installation, et installe le dans son emplacement par défaut. (C:\Program files)
* Clique droit sur l'icône Ad-remover située sur ton bureau puis sélectionne "Exécuter en tant qu'administrateur".
* Réponds `Oui` au message d'alerte automatique.
* Au menu principal choisi l'option `S` et tape ensuite [Entrée]
* Poste le rapport qui apparaît à la fin.
(Le rapport est sauvegardé aussi sous C:\Ad-report(date).log)
(CTRL+A Pour tout sélectionner, CTRL+C pour copier et CTRL+V pour coller)
Note :
"Process.exe", une composante de l'outil, est détecté par certains antivirus (AntiVir, Dr.Web, Kaspersky Anti-Virus) comme étant un RiskTool.
Il ne s'agit pas d'un virus, mais d'un utilitaire destiné à mettre fin à des processus. -
1. ========================= SEAF 1.0.0.7 - C_XX
2.
3. Commencé à: 18:29:07 le 05/03/2010
4.
5. Valeur(s) recherchée(s):
6.
7. iaStor.sys
8.
9. (!) --- Affichage des ADS
10. (!) --- Informations supplémentaires
11. (!) --- Recherche registre
12.
13. ====== Fichier(s) (TC: Date de création, TM: Date de modification, DA, Dernier accès) ======
14.
15. "c:\Windows\System32\DriverStore\FileRepository\iastor.inf_ee67416f\iaStor.sys" [ ----A---- | 250368 ]
16. TC: 02/06/2007,07:20:30 | TM: 31/10/2006,14:46:36 | DA: 02/06/2007,07:20:30
17.
18. CompagnyName: Intel Corporation
19. ProductName: Intel Matrix Storage Manager driver
20. InternalName: iaStor.sys
21. OriginalFilename: iaStor.sys
22. LegalCopyright: Copyright(C) Intel Corporation 1994-2006
23. ProductVersion: 6.2.1.1002
24. FileVersion: 6.2.1.1002
25.
26. =========================
27.
28. "c:\Windows\System32\DriverStore\FileRepository\iaahci.inf_3bb7bc45\iaStor.sys" [ ----A---- | 250368 ]
29. TC: 02/06/2007,07:20:29 | TM: 31/10/2006,14:46:36 | DA: 02/06/2007,07:20:29
30.
31. CompagnyName: Intel Corporation
32. ProductName: Intel Matrix Storage Manager driver
33. InternalName: iaStor.sys
34. OriginalFilename: iaStor.sys
35. LegalCopyright: Copyright(C) Intel Corporation 1994-2006
36. ProductVersion: 6.2.1.1002
37. FileVersion: 6.2.1.1002
38.
39. =========================
40.
41. "c:\Windows\System32\drivers\iaStor.sys" [ ----A---- | 250368 ]
42. TC: 02/06/2007,07:20:30 | TM: 31/10/2006,14:46:36 | DA: 02/06/2007,07:20:30
43.
44.
45. =========================
46.
47. "c:\Program Files\Intel\Intel Matrix Storage Manager\Driver64\IaStor.sys" [ ----A---- | 495896 ]
48. TC: 01/06/2007,21:38:28 | TM: 31/10/2006,14:13:46 | DA: 01/06/2007,21:38:28
49.
50. CompagnyName: Intel Corporation
51. ProductName: Intel Matrix Storage Manager driver
52. InternalName: iaStor.sys
53. OriginalFilename: iaStor.sys
54. LegalCopyright: Copyright(C) Intel Corporation 1994-2006
55. ProductVersion: 6.2.1.1002
56. FileVersion: 6.2.1.1002
57.
58. =========================
59.
60. "c:\Program Files\Intel\Intel Matrix Storage Manager\Driver\iaStor.sys" [ ----A---- | 250368 ]
61. TC: 01/06/2007,21:38:28 | TM: 31/10/2006,13:46:36 | DA: 01/06/2007,21:38:28
62.
63. CompagnyName: Intel Corporation
64. ProductName: Intel Matrix Storage Manager driver
65. InternalName: iaStor.sys
66. OriginalFilename: iaStor.sys
67. LegalCopyright: Copyright(C) Intel Corporation 1994-2006
68. ProductVersion: 6.2.1.1002
69. FileVersion: 6.2.1.1002
70.
71. =========================
72.
73. "c:\hp\DRIVERS\Intel_raid\iastor.sys" [ ----A---- | 250368 ]
74. TC: 01/06/2007,21:38:19 | TM: 31/10/2006,14:46:36 | DA: 01/06/2007,21:38:19
75.
76. CompagnyName: Intel Corporation
77. ProductName: Intel Matrix Storage Manager driver
78. InternalName: iaStor.sys
79. OriginalFilename: iaStor.sys
80. LegalCopyright: Copyright(C) Intel Corporation 1994-2006
81. ProductVersion: 6.2.1.1002
82. FileVersion: 6.2.1.1002
83.
84. =========================
85.
86. "d:\hp\Drv\APP18096\offline_driver\iastor.sys" [ ----A---- | 250368 ]
87. TC: 02/06/2007,08:39:33 | TM: 31/10/2006,14:46:36 | DA: 02/06/2007,08:39:33
88.
89. CompagnyName: Intel Corporation
90. ProductName: Intel Matrix Storage Manager driver
91. InternalName: iaStor.sys
92. OriginalFilename: iaStor.sys
93. LegalCopyright: Copyright(C) Intel Corporation 1994-2006
94. ProductVersion: 6.2.1.1002
95. FileVersion: 6.2.1.1002
96.
97. =========================
98.
99. ====== Dossier(s) (TC: Date de création, TM: Date de modification, DA, Dernier accès) ======
100.
101. Aucun dossier trouvé
102.
103.
104. ====== Entrée(s) du registre ======
105.
106.
107.
108. [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Setup\PnpLockdownFiles]
109. "C:\Windows\system32\DRIVERS\iaStor.sys"=""
110.
111. [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\Eventlog\System\iaStor]
112. "EventMessageFile"="%SystemRoot%\System32\IoLogMsg.dll;%SystemRoot%\System32\drivers\iaStor.sys"
113.
114. [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\iaStor]
115. "ImagePath"="system32\drivers\iastor.sys"
116.
117. [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet002\Services\Eventlog\System\iaStor]
118. "EventMessageFile"="%SystemRoot%\System32\IoLogMsg.dll;%SystemRoot%\System32\drivers\iaStor.sys"
119.
120. [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet002\Services\iaStor]
121. "ImagePath"="system32\drivers\iastor.sys"
122.
123. [HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Eventlog\System\iaStor]
124. "EventMessageFile"="%SystemRoot%\System32\IoLogMsg.dll;%SystemRoot%\System32\drivers\iaStor.sys"
125.
126. [HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\iaStor]
127. "ImagePath"="system32\drivers\iastor.sys"
128.
129. =========================
130.
131. Fin à: 18:32:40 le 05/03/2010 ( E.O.F ) -
.
======= RAPPORT D'AD-REMOVER 1.1.4.6_J | UNIQUEMENT XP/VISTA/7 =======
.
Mis à jour par C_XX le 05.02.2010 à 17:34
Contact: AdRemover.contact@gmail.com
Site web: http://pagesperso-orange.fr/NosTools/ad_remover.html
.
Lancé à: 19:09:44, 05/03/2010 | Mode Normal | Option: SCAN
Exécuté de: C:\Ad-Remover\
Système d'exploitation: Microsoft® Windows Vista™ HomePremium Service Pack 2 v6.0.6002
Nom du PC: PC-DE-HOURFANE | Utilisateur actuel: hourfane
.
============== ÉLÉMENT(S) TROUVÉ(S) ==============
.
C:\Users\hourfane\DOCUME~1\PacificPoker
C:\Users\hourfane\AppData\Roaming\Microsoft\Internet Explorer\Quick Launch\Pacific Poker.lnk
C:\Users\hourfane\AppData\Roaming\MICROS~1\Windows\STARTM~1\Pacific Poker.lnk
C:\Users\hourfane\AppData\Roaming\MICROS~1\Windows\STARTM~1\Programs\Pacific Poker
C:\PROGRA~2\MICROS~1\Windows\STARTM~1\Programs\Everest Poker
C:\PROGRA~2\MICROS~1\Windows\STARTM~1\Programs\Pacific Poker
C:\Program Files\Everest Poker
C:\Program Files\PacificPoker
C:\Users\hourfane\AppData\Roaming\PacificPoker
C:\Users\hourfane\AppData\LocalLow\Dealio
C:\Users\hourfane\AppData\LocalLow\Search Settings
C:\Windows\Installer\1741eb4.msi
C:\Windows\Installer\1741ebc.msi
C:\Users\IUSR_NMPR\Desktop\Pacific Poker.lnk
C:\Users\Public\Desktop\Everest Poker.lnk
C:\Users\hourfane\AppData\Local\uykyk.bat
.
HKCU\software\appdatalow\software\Dealio
HKCU\software\Grand Virtual
HKCU\Software\Microsoft\Internet Explorer\LowRegistry\Search Settings
HKCU\software\microsoft\internet explorer\searchscopes\{0ECDF796-C2DC-4d79-A620-CCE0C0A66CC9}
HKCU\software\pacificpoker
HKCU\software\pokerinstaller
HKLM\software\classes\installer\Features\A3BB3C491A65ED342A24B8144FE679FE
HKLM\software\classes\installer\Products\79CAA1B036589D14EA74856E2A220F1E
HKLM\software\classes\installer\Products\A3BB3C491A65ED342A24B8144FE679FE
HKLM\Software\Classes\Interface\{D5A1EF9A-7948-435D-8B87-D6A598317288}
HKLM\software\Dealio
HKLM\Software\Microsoft\Internet Explorer\Low Rights\ElevationPolicy\{01398B87-61AF-4FFB-9AB5-1A1C5FB39A9C}
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\0292226F570267D459357AF78015E534
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\03285961954D5824C85975D955031EE8
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\23A03A6765D10864EB278629A2DF32C3
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\323D2420527EA994FB326F15D333660E
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\3A4FCCE032CA50340A6975C92410AE30
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\588DFA161592E9747948BFFE475476F4
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\6AC3985F4D64C2245A96D31569D1BF40
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\6E00D9B24354FBA44AE2CA0FA86EF2E2
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\7C13F41728A69EF41AA1A3372FB86FA6
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\855847FA0E25FBA46B8516389DFDD4B3
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\8ED411B7A244E0E4C82C46284CA65B81
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\94E65EF7E080DDA4AA2F1DEDCE74AC5B
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\9DC2844D0E3E8924C8973C3B3BAE1F58
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\AFEB575AA30ACB243B748619F62F0782
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\B072F84D5AF1BB34C980E01F5689D864
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\B92A2929968AED344BD6B34AD60E6604
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\BB1E992117B1B0B42BD2CDAEB8E749C4
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\C7D9132F42224AC49BD8C06A0F8E39C4
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\DA6F069968D91A540A1363E997581959
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\DBC7F2B5594E08A4C87EF4C22971C615
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\F461B8DD96FF5AA41A52D14E1D7B69C7
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Products\79CAA1B036589D14EA74856E2A220F1E
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Products\A3BB3C491A65ED342A24B8144FE679FE
HKLM\software\microsoft\windows\currentversion\uninstall\{0B1AAC97-8563-41D9-AE47-58E6A222F0E1}
HKLM\software\microsoft\windows\currentversion\uninstall\{94C3BB3A-56A1-43DE-A242-8B41F46E97EF}
HKLM\software\microsoft\windows\currentversion\uninstall\Everest Poker
HKLM\software\microsoft\windows\currentversion\uninstall\Pacific Poker
HKLM\software\Search Settings
HKU\s-1-5-21-409706545-1180766039-109059347-1001\software\appdatalow\software\Dealio
HKU\s-1-5-21-409706545-1180766039-109059347-1001\software\Grand Virtual
HKU\s-1-5-21-409706545-1180766039-109059347-1001\software\pacificpoker
HKU\s-1-5-21-409706545-1180766039-109059347-1001\software\pokerinstaller
.
============== Scan additionnel ==============
.
.
* Mozilla FireFox Version 3.5.8 [fr] *
.
Nom du profil: my4998sp.default (hourfane)
.
(hourfane, prefs.js) Browser.download.dir, C:\Users\hourfane\Desktop
(hourfane, prefs.js) Browser.download.lastDir, C:\Users\hourfane\Desktop
(hourfane, prefs.js) Browser.search.defaultenginename, Fast Browser Search
(hourfane, prefs.js) Browser.search.defaulturl, hxxp://search.conduit.com/ResultsExt.aspx?ctid=CT2233703&SearchSource=3&q={searchTerms}
(hourfane, prefs.js) Browser.search.selectedEngine, Google
(hourfane, prefs.js) Browser.startup.homepage, Fast dial
(hourfane, prefs.js) Extensions.enabledItems, {3f963a5b-e555-4543-90e2-c3908898db71}:8.5.0.429,avg@igeared:2.506.026.001,fastdial@telega.phpnet.us:2.23b1,{19503e42-ca3c-4c27-b1e2-9cdb2170ee34}:1.2.1.15,{CAFEEFAC-0016-0000-0013-ABCDEFFEDCBA}:6.0.13,{CAFEEFAC-0016-0000-0016-ABCDEFFEDCBA}:6.0.16,{CAFEEFAC-0016-0000-0017-ABCDEFFEDCBA}:6.0.17,{BD4B37E6-7AE7-48d7-A2D7-6FF5775924AB}:1.3.2.10,{d33c2f7c-b1e6-4d46-ab0e-be1f6d05c904}:2.0.2,{972ce4c6-7e08-4474-a285-3208198ce6fd}:3.5.8,nasanightlaunch@example.com:0.6.20100207
(hourfane, prefs.js) Privacy.popups.showBrowserMessage, false
.
(hourfane, prefs.js) TROUVE - Browser.search.defaultenginename, Fast Browser Search
(hourfane, prefs.js) TROUVE - Browser.search.defaultthis.engineName, 4shared Web Search
(hourfane, prefs.js) TROUVE - Browser.search.order.1, Fast Browser Search
.
.
* Internet Explorer Version 8.0.6001.18882 *
.
[HKEY_CURRENT_USER\..\Internet Explorer\Main]
.
Do404Search: 01000000
Local Page: C:\Windows\system32\blank.htm
Show_ToolBar: yes
Enable Browser Extensions: yes
Start Page: hxxp://search.babylon.com/home
Search Page: hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar=iesearch
Default_search_url: hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar=iesearch
.
[HKEY_LOCAL_MACHINE\..\Internet Explorer\Main]
.
Start Page: hxxp://fr.msn.com/
Default_Page_URL: hxxp://go.microsoft.com/fwlink/?LinkId=69157
Default_Search_URL: hxxp://go.microsoft.com/fwlink/?LinkId=54896
Search Page: hxxp://go.microsoft.com/fwlink/?LinkId=54896
Delete_Temp_Files_On_Exit: yes
Local Page: C:\Windows\System32\blank.htm
Search bar: hxxp://search.msn.com/spbasic.htm
.
[HKEY_LOCAL_MACHINE\..\Internet Explorer\ABOUTURLS]
.
Tabs: res://ieframe.dll/tabswelcome.htm
.
============== Suspect (Cracks, Serials, ...) ==============
.
C:\Users\hourfane\Downloads\PES2009Patch140.zip
.
===================================
.
3846 Octet(s) - C:\Ad-Report-Clean-12.05.2009.log
3099 Octet(s) - C:\Ad-Report-Scan-12.05.2009.log
8163 Octet(s) - C:\Ad-Report-SCAN[1].log
.
29 Fichier(s) - C:\Users\hourfane\AppData\Local\Temp
2 Fichier(s) - C:\Windows\Temp
129 Fichier(s) - C:\Windows\Prefetch
.
4 Fichier(s) - C:\Ad-Remover\BACKUP
0 Fichier(s) - C:\Ad-Remover\QUARANTINE
.
Fin à: 19:15:51 | 05/03/2010 - SCAN[1]
.
============== E.O.F ==============
. -
ModérateurAnalyse ce fichier sur Virustotal comme tu l'avais fait pour l'autre fichier :
c:\Program Files\Intel\Intel Matrix Storage Manager\Driver64\IaStor.sys
********
Suppression avec Ad-Remover :
/!\ Déconnectes toi et fermes toutes applications en cours, désactive ton antivirus le temps de la manipulation/!\
* Clique droit sur l'icône Ad-Remover située sur ton bureau puis sélectionne "Exécuter en tant qu'administrateur".
* Au menu principal choisi l'option "L" et tape ensuite [Entrée]
* Poste le rapport qui apparaît à la fin.
(Le rapport est sauvegardé aussi sous C:\Ad-report(date).log)
(CTRL+A Pour tout sélectionner, CTRL+C pour copier et CTRL+V pour coller)
Note :
"Process.exe", une composante de l'outil, est détecté par certains antivirus (AntiVir, Dr.Web, Kaspersky Anti-Virus) comme étant un RiskTool.
Il ne s'agit pas d'un virus, mais d'un utilitaire destiné à mettre fin à des processus.
**********
Tu as une infection Navipromo / Magic control.
Télécharge sur le bureau Navilog1 (Merci à IL-MAFIOSO)
= = = = >>> En cliquant ici <<< = = = =
* Désactive tes logiciels de sécurité (antivirus, pare-feu, antispyware,...)
* Clique droit sur "Navilog1" sur ton bureau que tu viens de télécharger et sélectionne "Exécuter en tant qu'administrateur"
* Appuie sur le chiffre 1 de ton clavier puis sur la touche Entrée pour sélectionner la langue française.
* Appuie sur une touche de ton clavier pour continuer... (Il te le sera demandé plusieurs fois).
* Tape 1, puis appuie sur la touche Entrée de ton clavier pour sélectionner l'option "Recherche / Désinfection automatique"
* Sois patient, cela peut prendre une dizaine de minutes voire plus.
* Navilog1 t'informe que la recherche est terminée
* Appuie sur une touche de ton clavier pour afficher le rapport qu'il a généré
* Le rapport sera sauvegardé dans le fichier suivant : "cleannavi.txt" à la racine de ton disque dur (C:\cleannavi.txt). -
Fichier IaStor.sys reçu le 2010.03.06 01:09:53 (UTC)
Situation actuelle: en cours de chargement ... mis en file d'attente en attente en cours d'analyse terminé NON TROUVE ARRETE
Résultat: 0/42 (0%)
en train de charger les informations du serveur...
Votre fichier est dans la file d'attente, en position: 1.
L'heure estimée de démarrage est entre 42 et 60 secondes.
Ne fermez pas la fenêtre avant la fin de l'analyse.
L'analyseur qui traitait votre fichier est actuellement stoppé, nous allons attendre quelques secondes pour tenter de récupérer vos résultats.
Si vous attendez depuis plus de cinq minutes, vous devez renvoyer votre fichier.
Votre fichier est, en ce moment, en cours d'analyse par VirusTotal,
les résultats seront affichés au fur et à mesure de leur génération.
Formaté Formaté
Impression des résultats Impression des résultats
Votre fichier a expiré ou n'existe pas.
Le service est en ce moment, stoppé, votre fichier attend d'être analysé (position : ) depuis une durée indéfinie.
Vous pouvez attendre une réponse du Web (re-chargement automatique) ou taper votre e-mail dans le formulaire ci-dessous et cliquer "Demande" pour que le système vous envoie une notification quand l'analyse sera terminée.
Email:
Antivirus Version Dernière mise à jour Résultat
a-squared 4.5.0.50 2010.03.05 -
AhnLab-V3 5.0.0.2 2010.03.05 -
AntiVir 8.2.1.180 2010.03.05 -
Antiy-AVL 2.0.3.7 2010.03.05 -
Authentium 5.2.0.5 2010.03.05 -
Avast 4.8.1351.0 2010.03.05 -
Avast5 5.0.332.0 2010.03.05 -
AVG 9.0.0.787 2010.03.05 -
BitDefender 7.2 2010.03.05 -
CAT-QuickHeal 10.00 2010.03.05 -
ClamAV 0.96.0.0-git 2010.03.05 -
Comodo 4091 2010.02.28 -
DrWeb 5.0.1.12222 2010.03.06 -
eSafe 7.0.17.0 2010.03.04 -
eTrust-Vet 35.2.7342 2010.03.05 -
F-Prot 4.5.1.85 2010.03.05 -
F-Secure 9.0.15370.0 2010.03.05 -
Fortinet 4.0.14.0 2010.03.04 -
GData 19 2010.03.06 -
Ikarus T3.1.1.80.0 2010.03.05 -
Jiangmin 13.0.900 2010.03.05 -
K7AntiVirus 7.10.990 2010.03.04 -
Kaspersky 7.0.0.125 2010.03.06 -
McAfee 5911 2010.03.05 -
McAfee+Artemis 5911 2010.03.05 -
McAfee-GW-Edition 6.8.5 2010.03.05 -
Microsoft 1.5502 2010.03.06 -
NOD32 4919 2010.03.05 -
Norman 6.04.08 2010.03.05 -
nProtect 2009.1.8.0 2010.03.05 -
Panda 10.0.2.2 2010.03.04 -
PCTools 7.0.3.5 2010.03.04 -
Prevx 3.0 2010.03.06 -
Rising 22.37.04.04 2010.03.05 -
Sophos 4.51.0 2010.03.06 -
Sunbelt 5765 2010.03.06 -
Symantec 20091.2.0.41 2010.03.06 -
TheHacker 6.5.1.8.222 2010.03.06 -
TrendMicro 9.120.0.1004 2010.03.05 -
VBA32 3.12.12.2 2010.03.05 -
ViRobot 2010.3.5.2214 2010.03.05 -
VirusBuster 5.0.27.0 2010.03.05 -
Information additionnelle
File size: 495896 bytes
MD5...: 81ec16afd70e3432b8c573782ccfee6d
SHA1..: 48d89969745186a847ab47cff48211cc554405cf
SHA256: 5169fb88710892493e4f9b5619e558cb53fcd23bce100d8f47894e0934ddaddb
ssdeep: 6144:t/oebmxnJyXn+t6xJvv+k8w5B++wpoS0G7slpBla9t9e+dix8mEyqNzd:tg
n5t6xRW0M0a5f0q3
PEiD..: -
PEInfo: PE Structure information
( base data )
entrypointaddress.: 0x1000
timedatestamp.....: 0x4547c735 (Tue Oct 31 21:59:17 2006)
machinetype.......: 0x8664 (AMD64)
( 7 sections )
name viradd virsiz rawdsiz ntrpy md5
.text 0x1000 0x6312b 0x63200 6.19 f2afcdca72847dc1ef541e2f1208dc2b
.rdata 0x65000 0xa028 0xa200 5.27 a1ae8d93533568f61c18dd3e1853f424
.data 0x70000 0xa1130 0x1000 2.90 3dbacd6069268390e7c49c1a4c1fe7cd
.pdata 0x112000 0x6888 0x6a00 5.78 ac41c0f0338b10a790db9de40c431741
INIT 0x119000 0xdbc 0xe00 5.07 76f5f9a90ea22fd18925e4b5a97429fd
.rsrc 0x11a000 0x440 0x600 2.54 b47a12837bfe2d963ff865f93f1c25a1
.reloc 0x11b000 0xef6 0x1000 1.76 73faaf93cc9614d79995b0333fbec394
( 2 imports )
> ntoskrnl.exe: RtlAppendUnicodeStringToString, RtlAppendUnicodeToString, ExAllocatePoolWithTag, RtlInitUnicodeString, ZwClose, ZwQueryValueKey, DbgPrint, ZwOpenKey, RtlCreateRegistryKey, RtlCopyUnicodeString, KeInsertQueueDpc, MmGetPhysicalAddress, KeAcquireSpinLockRaiseToDpc, KeReleaseSpinLock, KeAcquireSpinLockAtDpcLevel, KeReleaseSpinLockFromDpcLevel, IoInvalidateDeviceRelations, IoFreeWorkItem, IoRequestDeviceEject, IoQueueWorkItem, IoAllocateWorkItem, ExpInterlockedPopEntrySList, ExpInterlockedPushEntrySList, ExQueryDepthSList, IofCompleteRequest, IofCallDriver, IoGetDmaAdapter, ExReleaseFastMutex, ExAcquireFastMutex, RtlWriteRegistryValue, RtlAnsiStringToUnicodeString, RtlInitAnsiString, ZwCreateKey, swprintf, KeWaitForSingleObject, KeInitializeEvent, IoDisconnectInterrupt, IoGetConfigurationInformation, IoDeleteDevice, ExDeleteNPagedLookasideList, KeCancelTimer, IoFreeIrp, KeLeaveCriticalRegion, KeEnterCriticalRegion, IoDetachDevice, IoDeleteSymbolicLink, IoConnectInterrupt, IoReleaseRemoveLockAndWaitEx, strstr, strncat, sprintf, IoBuildDeviceIoControlRequest, PoSetPowerState, PoRegisterDeviceForIdleDetection, RtlCompareMemory, KeClearEvent, RtlQueryRegistryValues, ObfReferenceObject, KeSetTimer, IoIs32bitProcess, IoWriteErrorLogEntry, IoAllocateErrorLogEntry, IoAcquireRemoveLockEx, IoReleaseRemoveLockEx, KeSetEvent, KeInitializeDpc, KeInitializeTimer, ObfDereferenceObject, IoGetAttachedDeviceReference, IoAllocateIrp, IoInvalidateDeviceState, strncmp, __C_specific_handler, IoFreeMdl, MmProbeAndLockPages, IoAllocateMdl, PoRequestPowerIrp, MmMapLockedPagesSpecifyCache, KeBugCheck, KeRemoveQueueDpc, KeQueryTimeIncrement, PsTerminateSystemThread, KeWaitForMultipleObjects, KeSetPriorityThread, ObReferenceObjectByHandle, PsCreateSystemThread, ExInitializeNPagedLookasideList, MmMapIoSpace, ExRegisterCallback, ExCreateCallback, IoReportResourceForDetection, ExUnregisterCallback, MmUnmapIoSpace, RtlCheckRegistryKey, IoAttachDeviceToDeviceStack, IoCreateSymbolicLink, IoCreateDevice, RtlUnicodeStringToInteger, wcsncpy, wcsstr, _wcsupr, IoGetDeviceProperty, ZwCreateDirectoryObject, PoStartNextPowerIrp, PoCallDriver, strncpy, _purecall, ExSystemTimeToLocalTime, KeDelayExecutionThread, KeSetTimerEx, KeInitializeTimerEx, IoInitializeRemoveLockEx, ExFreePoolWithTag, KeBugCheckEx
> HAL.dll: KeStallExecutionProcessor
( 0 exports )
RDS...: NSRL Reference Data Set
-
pdfid.: -
sigcheck:
publisher....: Intel Corporation
copyright....: Copyright(C) Intel Corporation 1994-2006
product......: Intel Matrix Storage Manager driver
description..: Intel Matrix Storage Manager driver
original name: iaStor.sys
internal name: iaStor.sys
file version.: 6.2.1.1002
comments.....:
signers......: Intel Corporation
VeriSign Class 3 Code Signing 2004 CA
Class 3 Public Primary Certification Authority
signing date.: 11:13 PM 10/31/2006
verified.....: -
trid..: Win64 Executable Generic (95.5%)
Generic Win/DOS Executable (2.2%)
DOS Executable Generic (2.2%)
Autodesk FLIC Image File (extensions: flc, fli, cel) (0.0%) -
.
======= RAPPORT D'AD-REMOVER 1.1.4.6_J | UNIQUEMENT XP/VISTA/7 =======
.
Mis à jour par C_XX le 05.02.2010 à 17:34
Contact: AdRemover.contact@gmail.com
Site web: http://pagesperso-orange.fr/NosTools/ad_remover.html
.
Lancé à: 2:19:07, 06/03/2010 | Mode Normal | Option: CLEAN
Exécuté de: C:\Ad-Remover\
Système d'exploitation: Microsoft® Windows Vista™ HomePremium Service Pack 2 v6.0.6002
Nom du PC: PC-DE-HOURFANE | Utilisateur actuel: hourfane
.
============== ÉLÉMENT(S) NEUTRALISÉ(S) ==============
.
C:\Users\hourfane\DOCUME~1\PacificPoker
C:\Users\hourfane\AppData\Roaming\Microsoft\Internet Explorer\Quick Launch\Pacific Poker.lnk
C:\Users\hourfane\AppData\Roaming\MICROS~1\Windows\STARTM~1\Pacific Poker.lnk
C:\Users\hourfane\AppData\Roaming\MICROS~1\Windows\STARTM~1\Programs\Pacific Poker
C:\PROGRA~2\MICROS~1\Windows\STARTM~1\Programs\Everest Poker
C:\PROGRA~2\MICROS~1\Windows\STARTM~1\Programs\Pacific Poker
C:\Program Files\Everest Poker
C:\Program Files\PacificPoker
C:\Users\hourfane\AppData\Roaming\PacificPoker
C:\Users\hourfane\AppData\LocalLow\Dealio
C:\Users\hourfane\AppData\LocalLow\Search Settings
C:\Windows\Installer\1741eb4.msi
C:\Windows\Installer\1741ebc.msi
C:\Users\IUSR_NMPR\Desktop\Pacific Poker.lnk
C:\Users\Public\Desktop\Everest Poker.lnk
C:\Users\hourfane\AppData\Local\uykyk.bat
(!) -- Fichiers temporaires supprimés.
.
HKCU\software\appdatalow\software\Dealio
HKCU\software\Grand Virtual
HKCU\Software\Microsoft\Internet Explorer\LowRegistry\Search Settings
HKCU\software\microsoft\internet explorer\searchscopes\{0ECDF796-C2DC-4d79-A620-CCE0C0A66CC9}
HKCU\software\pacificpoker
HKCU\software\pokerinstaller
HKLM\software\classes\installer\Features\A3BB3C491A65ED342A24B8144FE679FE
HKLM\software\classes\installer\Products\79CAA1B036589D14EA74856E2A220F1E
HKLM\software\classes\installer\Products\A3BB3C491A65ED342A24B8144FE679FE
HKLM\Software\Classes\Interface\{D5A1EF9A-7948-435D-8B87-D6A598317288}
HKLM\software\Dealio
HKLM\Software\Microsoft\Internet Explorer\Low Rights\ElevationPolicy\{01398B87-61AF-4FFB-9AB5-1A1C5FB39A9C}
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\0292226F570267D459357AF78015E534
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\03285961954D5824C85975D955031EE8
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\23A03A6765D10864EB278629A2DF32C3
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\323D2420527EA994FB326F15D333660E
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\3A4FCCE032CA50340A6975C92410AE30
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\588DFA161592E9747948BFFE475476F4
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\6AC3985F4D64C2245A96D31569D1BF40
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\6E00D9B24354FBA44AE2CA0FA86EF2E2
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\7C13F41728A69EF41AA1A3372FB86FA6
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\855847FA0E25FBA46B8516389DFDD4B3
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\8ED411B7A244E0E4C82C46284CA65B81
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\94E65EF7E080DDA4AA2F1DEDCE74AC5B
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\9DC2844D0E3E8924C8973C3B3BAE1F58
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\AFEB575AA30ACB243B748619F62F0782
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\B072F84D5AF1BB34C980E01F5689D864
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\B92A2929968AED344BD6B34AD60E6604
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\BB1E992117B1B0B42BD2CDAEB8E749C4
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\C7D9132F42224AC49BD8C06A0F8E39C4
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\DA6F069968D91A540A1363E997581959
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\DBC7F2B5594E08A4C87EF4C22971C615
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Components\F461B8DD96FF5AA41A52D14E1D7B69C7
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Products\79CAA1B036589D14EA74856E2A220F1E
HKLM\software\microsoft\windows\currentversion\installer\userdata\S-1-5-18\Products\A3BB3C491A65ED342A24B8144FE679FE
HKLM\software\microsoft\windows\currentversion\uninstall\{0B1AAC97-8563-41D9-AE47-58E6A222F0E1}
HKLM\software\microsoft\windows\currentversion\uninstall\{94C3BB3A-56A1-43DE-A242-8B41F46E97EF}
HKLM\software\microsoft\windows\currentversion\uninstall\Everest Poker
HKLM\software\microsoft\windows\currentversion\uninstall\Pacific Poker
HKLM\software\Search Settings
.
============== Scan additionnel ==============
.
.
* Mozilla FireFox Version 3.5.8 [fr] *
.
Nom du profil: my4998sp.default (hourfane)
.
(hourfane, prefs.js) Browser.download.dir, C:\Users\hourfane\Desktop
(hourfane, prefs.js) Browser.download.lastDir, C:\Users\hourfane\Desktop
(hourfane, prefs.js) Browser.search.defaultenginename, Fast Browser Search
(hourfane, prefs.js) Browser.search.defaulturl, hxxp://search.conduit.com/ResultsExt.aspx?ctid=CT2233703&SearchSource=3&q={searchTerms}
(hourfane, prefs.js) Browser.search.selectedEngine, Google
(hourfane, prefs.js) Browser.startup.homepage, Fast dial
(hourfane, prefs.js) Extensions.enabledItems, {3f963a5b-e555-4543-90e2-c3908898db71}:8.5.0.429,avg@igeared:2.506.026.001,fastdial@telega.phpnet.us:2.23b1,{19503e42-ca3c-4c27-b1e2-9cdb2170ee34}:1.2.1.15,{CAFEEFAC-0016-0000-0013-ABCDEFFEDCBA}:6.0.13,{CAFEEFAC-0016-0000-0016-ABCDEFFEDCBA}:6.0.16,{CAFEEFAC-0016-0000-0017-ABCDEFFEDCBA}:6.0.17,{BD4B37E6-7AE7-48d7-A2D7-6FF5775924AB}:1.3.2.10,{d33c2f7c-b1e6-4d46-ab0e-be1f6d05c904}:2.0.2,{972ce4c6-7e08-4474-a285-3208198ce6fd}:3.5.8,nasanightlaunch@example.com:0.6.20100207
(hourfane, prefs.js) Privacy.popups.showBrowserMessage, false
.
(hourfane, prefs.js) EFFACE - Browser.search.defaultenginename, Fast Browser Search
(hourfane, prefs.js) EFFACE - Browser.search.defaultthis.engineName, 4shared Web Search
(hourfane, prefs.js) EFFACE - Browser.search.order.1, Fast Browser Search
.
.
* Internet Explorer Version 8.0.6001.18882 *
.
[HKEY_CURRENT_USER\..\Internet Explorer\Main]
.
Do404Search: 01000000
Local Page: C:\Windows\system32\blank.htm
Show_ToolBar: yes
Enable Browser Extensions: yes
Start Page: hxxp://fr.msn.com/
Default_search_url: hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar=iesearch
Default_page_url: hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&pver=6&ar=msnhome
Search bar: hxxp://go.microsoft.com/fwlink/?linkid=54896
.
[HKEY_LOCAL_MACHINE\..\Internet Explorer\Main]
.
Start Page: hxxp://fr.msn.com/
Default_Page_URL: hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&pver=6&ar=msnhome
Default_Search_URL: hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar=iesearch
Search Page: hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar=iesearch
Delete_Temp_Files_On_Exit: yes
Local Page: C:\Windows\System32\blank.htm
Search bar: hxxp://search.msn.com/spbasic.htm
.
[HKEY_LOCAL_MACHINE\..\Internet Explorer\ABOUTURLS]
.
Tabs: res://ieframe.dll/tabswelcome.htm
.
============== Suspect (Cracks, Serials, ...) ==============
.
C:\Users\hourfane\Downloads\PES2009Patch140.zip
.
===================================
.
3846 Octet(s) - C:\Ad-Report-Clean-12.05.2009.log
7965 Octet(s) - C:\Ad-Report-CLEAN[1].log
3099 Octet(s) - C:\Ad-Report-Scan-12.05.2009.log
8503 Octet(s) - C:\Ad-Report-SCAN[1].log
.
23 Fichier(s) - C:\Users\hourfane\AppData\Local\Temp
2 Fichier(s) - C:\Windows\Temp
10 Fichier(s) - C:\Windows\Prefetch
.
23 Fichier(s) - C:\Ad-Remover\BACKUP
2666 Fichier(s) - C:\Ad-Remover\QUARANTINE
.
Fin à: 2:28:29 | 06/03/2010 - CLEAN[1]
.
============== E.O.F ==============
. -
Fix Navipromo version 4.0.6 commencé le 06/03/2010 13:21:15,51
!!! Attention,ce rapport peut indiquer des fichiers/programmes légitimes!!!
!!! Postez ce rapport sur le forum pour le faire analyser !!!
Outil exécuté depuis C:\Program Files\navilog1
Mise à jour le 03.01.2010 à 11h00 par IL-MAFIOSO
Microsoft® Windows Vista™ Édition Familiale Premium ( v6.0.6002 ) Service Pack 2
X86-based PC ( Multiprocessor Free : Intel(R) Core(TM)2 CPU 4400 @ 2.00GHz )
BIOS : Phoenix - AwardBIOS v6.00PG
USER : hourfane ( Administrator )
BOOT : Normal boot
C:\ (Local Disk) - NTFS - Total:290 Go (Free:63 Go)
D:\ (Local Disk) - NTFS - Total:8 Go (Free:1 Go)
E:\ (CD or DVD)
F:\ (CD or DVD)
G:\ (CD or DVD)
H:\ (CD or DVD)
I:\ (USB)
J:\ (USB)
K:\ (USB)
L:\ (USB)
Recherche executée en mode normal
[b]Aucune Infection Navipromo/Egdaccess trouvée/b
*** Scan terminé 06/03/2010 13:21:42,85 *** -
ModérateurJe t'ai créé un fichier .bat contenant ceci :
COPY "C:\Program Files\Intel\Intel Matrix Storage Manager\Driver64\IaStor.sys" "C:\Windows\System32\drivers\iaStor.sys"
Télécharge-le ici :
http://sd-1.archive-host.com/membres/up/68979205412808752/test.bat
*******
Exécute le par clic droit > Exécuter en tant qu'administrateur.
Ensuite, redémarre et envoie ce fichier à nouveau sur VirusTotal (et réanalyse le bien) !!!
C:\Windows\System32\drivers\iaStor.sys
-
Fichier iaStor.sys reçu le 2010.03.08 17:45:09 (UTC)
Situation actuelle: en cours de chargement ... mis en file d'attente en attente en cours d'analyse terminé NON TROUVE ARRETE
Résultat: 1/42 (2.39%)
en train de charger les informations du serveur...
Votre fichier est dans la file d'attente, en position: 3.
L'heure estimée de démarrage est entre 56 et 80 secondes.
Ne fermez pas la fenêtre avant la fin de l'analyse.
L'analyseur qui traitait votre fichier est actuellement stoppé, nous allons attendre quelques secondes pour tenter de récupérer vos résultats.
Si vous attendez depuis plus de cinq minutes, vous devez renvoyer votre fichier.
Votre fichier est, en ce moment, en cours d'analyse par VirusTotal,
les résultats seront affichés au fur et à mesure de leur génération.
Formaté Formaté
Impression des résultats Impression des résultats
Votre fichier a expiré ou n'existe pas.
Le service est en ce moment, stoppé, votre fichier attend d'être analysé (position : ) depuis une durée indéfinie.
Vous pouvez attendre une réponse du Web (re-chargement automatique) ou taper votre e-mail dans le formulaire ci-dessous et cliquer "Demande" pour que le système vous envoie une notification quand l'analyse sera terminée.
Email:
Antivirus Version Dernière mise à jour Résultat
a-squared 4.5.0.50 2010.03.07 -
AhnLab-V3 5.0.0.2 2010.03.07 -
AntiVir 8.2.1.180 2010.03.05 -
Antiy-AVL 2.0.3.7 2010.03.05 -
Authentium 5.2.0.5 2010.03.06 -
Avast 4.8.1351.0 2010.03.07 -
Avast5 5.0.332.0 2010.03.07 -
AVG 9.0.0.787 2010.03.07 -
BitDefender 7.2 2010.03.07 -
CAT-QuickHeal 10.00 2010.03.06 -
ClamAV 0.96.0.0-git 2010.03.06 -
Comodo 4091 2010.02.28 -
DrWeb 5.0.1.12222 2010.03.07 -
eSafe 7.0.17.0 2010.03.04 -
eTrust-Vet 35.2.7342 2010.03.05 -
F-Prot 4.5.1.85 2010.03.06 -
F-Secure 9.0.15370.0 2010.03.07 -
Fortinet 4.0.14.0 2010.03.07 -
GData 19 2010.03.07 -
Ikarus T3.1.1.80.0 2010.03.07 -
Jiangmin 13.0.900 2010.03.07 -
K7AntiVirus 7.10.990 2010.03.04 -
Kaspersky 7.0.0.125 2010.03.07 -
McAfee 5912 2010.03.06 -
McAfee+Artemis 5912 2010.03.06 -
McAfee-GW-Edition 6.8.5 2010.03.07 Heuristic.LooksLike.Trojan.Patched.H
Microsoft 1.5502 2010.03.07 -
NOD32 4922 2010.03.07 -
Norman 6.04.08 2010.03.07 -
nProtect 2009.1.8.0 2010.03.07 -
Panda 10.0.2.2 2010.03.07 -
PCTools 7.0.3.5 2010.03.04 -
Prevx 3.0 2010.03.08 -
Rising 22.37.06.04 2010.03.07 -
Sophos 4.51.0 2010.03.07 -
Sunbelt 5780 2010.03.07 -
Symantec 20091.2.0.41 2010.03.07 -
TheHacker 6.5.1.9.223 2010.03.07 -
TrendMicro 9.120.0.1004 2010.03.07 -
VBA32 3.12.12.2 2010.03.05 -
ViRobot 2010.3.5.2214 2010.03.05 -
VirusBuster 5.0.27.0 2010.03.06 -
Information additionnelle
File size: 250368 bytes
MD5...: de01bf14ffb150c779fd561bd0e3c5c5
SHA1..: fc69088f44ef361837aff48c8f00296acaaf47fc
SHA256: d8c4f34195f9dec96eb25da2afd60ec9218aea8601a9deaea0fbb9121afd4ec4
ssdeep: 3072:/jcE8Rt9Dh27TSpmHoEFdjuwguSq1yi/wVrIDDA5xEF8nctzHsajAgC25wQ
RWiK:/jPm+9T/S0H7IVisrjnctzHsajAv9
PEiD..: -
PEInfo: PE Structure information
( base data )
entrypointaddress.: 0x1000
timedatestamp.....: 0x4547c439 (Tue Oct 31 21:46:33 2006)
machinetype.......: 0x14c (I386)
( 6 sections )
name viradd virsiz rawdsiz ntrpy md5
.text 0x1000 0x37f92 0x38000 6.57 cbeb06606464fddf970079dc92eaa4d3
.rdata 0x39000 0xa94 0xc00 5.17 f7b7d774c7ae843a753396ee18a3ffda
.data 0x3a000 0x7964c 0x1000 4.70 b775edc23209eb4e86c7af721f886479
INIT 0xb4000 0xc74 0xe00 5.16 ffc9ccb7a2b69b7bb2dffdf27579316b
.rsrc 0xb5000 0x440 0x600 2.54 e29997bb42ba3af1cef2f8955a15df0c
.reloc 0xb6000 0x1dc4 0x1e00 5.55 f034c57c7164ae4c6301d102d9d819a1
( 2 imports )
> ntoskrnl.exe: ZwClose, ZwQueryValueKey, DbgPrint, ZwOpenKey, RtlCreateRegistryKey, RtlCopyUnicodeString, memmove, KeInsertQueueDpc, MmGetPhysicalAddress, KeInitializeSpinLock, KefAcquireSpinLockAtDpcLevel, KefReleaseSpinLockFromDpcLevel, IoInvalidateDeviceRelations, IoFreeWorkItem, IoRequestDeviceEject, IoQueueWorkItem, IoAllocateWorkItem, ExInterlockedPopEntrySList, ExInterlockedPushEntrySList, IofCompleteRequest, IofCallDriver, IoGetDmaAdapter, RtlWriteRegistryValue, RtlAnsiStringToUnicodeString, RtlInitAnsiString, ZwCreateKey, swprintf, KeWaitForSingleObject, KeInitializeEvent, IoDisconnectInterrupt, IoGetConfigurationInformation, IoDeleteDevice, ExDeleteNPagedLookasideList, KeCancelTimer, IoFreeIrp, KeLeaveCriticalRegion, KeEnterCriticalRegion, IoDetachDevice, IoDeleteSymbolicLink, IoConnectInterrupt, IoReleaseRemoveLockAndWaitEx, strstr, strncat, sprintf, IoBuildDeviceIoControlRequest, PoSetPowerState, PoRegisterDeviceForIdleDetection, RtlCompareMemory, KeClearEvent, IoInitializeRemoveLockEx, ObfReferenceObject, KeSetTimer, IoWriteErrorLogEntry, IoAllocateErrorLogEntry, IoAcquireRemoveLockEx, RtlInitUnicodeString, KeSetEvent, _allmul, KeInitializeDpc, KeInitializeTimer, ObfDereferenceObject, IoGetAttachedDeviceReference, IoAllocateIrp, IoInvalidateDeviceState, strncpy, strncmp, IoFreeMdl, MmProbeAndLockPages, IoAllocateMdl, _except_handler3, PoRequestPowerIrp, MmMapLockedPagesSpecifyCache, KeBugCheck, KeRemoveQueueDpc, KeQuerySystemTime, KeQueryTimeIncrement, KeTickCount, PsTerminateSystemThread, KeWaitForMultipleObjects, KeSetPriorityThread, ObReferenceObjectByHandle, PsCreateSystemThread, ExInitializeNPagedLookasideList, MmMapIoSpace, ExRegisterCallback, ExCreateCallback, IoReportResourceForDetection, ExUnregisterCallback, MmUnmapIoSpace, RtlCheckRegistryKey, IoAttachDeviceToDeviceStack, IoCreateSymbolicLink, IoCreateDevice, RtlUnicodeStringToInteger, wcsncpy, wcsstr, _wcsupr, IoGetDeviceProperty, ZwCreateDirectoryObject, WRITE_REGISTER_ULONG, READ_REGISTER_ULONG, _alldiv, PoStartNextPowerIrp, PoCallDriver, _purecall, ExSystemTimeToLocalTime, KeDelayExecutionThread, KeSetTimerEx, KeInitializeTimerEx, wcslen, ExAllocatePoolWithTag, RtlAppendUnicodeToString, RtlAppendUnicodeStringToString, RtlQueryRegistryValues, IoReleaseRemoveLockEx, ExFreePoolWithTag, KeBugCheckEx
> HAL.dll: ExAcquireFastMutex, ExReleaseFastMutex, KfReleaseSpinLock, KfAcquireSpinLock, KeGetCurrentIrql, KeStallExecutionProcessor
( 0 exports )
RDS...: NSRL Reference Data Set
-
pdfid.: -
trid..: Win32 Executable Generic (68.0%)
Generic Win/DOS Executable (15.9%)
DOS Executable Generic (15.9%)
Autodesk FLIC Image File (extensions: flc, fli, cel) (0.0%)
sigcheck:
publisher....: Intel Corporation
copyright....: Copyright(C) Intel Corporation 1994-2006
product......: Intel Matrix Storage Manager driver
description..: Intel Matrix Storage Manager driver
original name: iaStor.sys
internal name: iaStor.sys
file version.: 6.2.1.1002
comments.....:
signers......: -
signing date.: -
verified.....: Unsigned -
ModérateurTrès bien.
Je vois que tu as Malwarebytes' Anti Malware (MBAM).
Mets-le à jour et fais une analyse complète du système stp. -
Malwarebytes' Anti-Malware 1.44
Version de la base de données: 3510
Windows 6.0.6002 Service Pack 2
Internet Explorer 8.0.6001.18882
09/03/2010 07:58:20
mbam-log-2010-03-09 (07-58-20).txt
Type de recherche: Examen complet (C:\|D:\|E:\|F:\|G:\|H:\|I:\|J:\|)
Eléments examinés: 312060
Temps écoulé: 1 hour(s), 59 minute(s), 28 second(s)
Processus mémoire infecté(s): 0
Module(s) mémoire infecté(s): 0
Clé(s) du Registre infectée(s): 0
Valeur(s) du Registre infectée(s): 0
Elément(s) de données du Registre infecté(s): 0
Dossier(s) infecté(s): 0
Fichier(s) infecté(s): 0
Processus mémoire infecté(s):
(Aucun élément nuisible détecté)
Module(s) mémoire infecté(s):
(Aucun élément nuisible détecté)
Clé(s) du Registre infectée(s):
(Aucun élément nuisible détecté)
Valeur(s) du Registre infectée(s):
(Aucun élément nuisible détecté)
Elément(s) de données du Registre infecté(s):
(Aucun élément nuisible détecté)
Dossier(s) infecté(s):
(Aucun élément nuisible détecté)
Fichier(s) infecté(s):
(Aucun élément nuisible détecté) -
ModérateurVersion de la base de données: 3510
MBAM n'est toujours pas à jour...
Si besoin.
A notre ami à tous, toptitbal. -
Malwarebytes' Anti-Malware 1.44
Version de la base de données: 3839
Windows 6.0.6002 Service Pack 2
Internet Explorer 8.0.6001.18882
09/03/2010 18:29:45
mbam-log-2010-03-09 (18-29-45).txt
Type de recherche: Examen complet (C:\|D:\|E:\|F:\|G:\|H:\|I:\|J:\|)
Eléments examinés: 320532
Temps écoulé: 2 hour(s), 1 minute(s), 44 second(s)
Processus mémoire infecté(s): 0
Module(s) mémoire infecté(s): 0
Clé(s) du Registre infectée(s): 0
Valeur(s) du Registre infectée(s): 0
Elément(s) de données du Registre infecté(s): 0
Dossier(s) infecté(s): 0
Fichier(s) infecté(s): 0
Processus mémoire infecté(s):
(Aucun élément nuisible détecté)
Module(s) mémoire infecté(s):
(Aucun élément nuisible détecté)
Clé(s) du Registre infectée(s):
(Aucun élément nuisible détecté)
Valeur(s) du Registre infectée(s):
(Aucun élément nuisible détecté)
Elément(s) de données du Registre infecté(s):
(Aucun élément nuisible détecté)
Dossier(s) infecté(s):
(Aucun élément nuisible détecté)
Fichier(s) infecté(s):
(Aucun élément nuisible détecté)


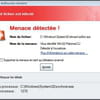
- 1
- 2
Suivant
