
Problème dossiers raccourcis port usb
Bonjour,
Bonjour,
Voilà, dès que je branche un périphérique USB à mon ordinateur, les documents contenus sur le support usb se transforment en raccourcis....
Quelqu'un aurait t-il une solution?!
Bien cordialement
Bonjour,
Voilà, dès que je branche un périphérique USB à mon ordinateur, les documents contenus sur le support usb se transforment en raccourcis....
Quelqu'un aurait t-il une solution?!
Bien cordialement
17 réponses
-
Contributeur sécuritéHello
###########| Canned Recherche
# Télécharge UsbFix par El Desaparecido sur ton Bureau.
# Si ton antivirus affiche une alerte, ignore-la et désactive l'antivirus temporairement.
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Recherche.

# Laisse travailler l'outil.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système ( C:\UsbFix [Scan ?] Nom de l'ordinateur.txt ).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# Tutoriel (aide) en images
-
Merci. Voici le rapport:
############################## | UsbFix V 7.166 | [Recherche]
Utilisateur: Jordy (Administrateur) # JORDY-PC
Mis à jour le 26/02/2014 par El Desaparecido - Team SosVirus
Lancé à 17:44:36 | 01/03/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://www.sosvirus.net/
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: ASUSTeK Computer INC. (1001PX)
CPU: Intel(R) Atom(TM) CPU N450 @ 1.66GHz
RAM -> [Total : 1014 Mo| Free : 323 Mo]
Bios: American Megatrends Inc.
Boot: Normal boot
OS: Microsoft Windows 7 Édition Starter (6.1.7601 32-Bit) Service Pack 1
WB: Windows Internet Explorer : 10.0.9200.16798
WB: Google Chrome : 26.0.1410.64
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AV: avast! Antivirus [Enabled | Updated]
AS: avast! Antivirus [Enabled | Updated]
AS: Windows Defender [Enabled | Updated]
FW: avast! Internet Security [(!) Disabled]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 100 Go (59 Go libre(s) - 59%) [] # NTFS
D:\ -> Disque fixe # 118 Go (84 Go libre(s) - 71%) [] # NTFS
E:\ -> Disque amovible # 4 Go (2 Go libre(s) - 55%) [K-Star] # FAT32
G:\ -> Disque amovible # 4 Go (2 Go libre(s) - 65%) [] # FAT32
H:\ -> Disque amovible # 1 Go (1002 Mo libre(s) - 93%) [WIKO] # FAT32
################## | Processus Actif |
C:\windows\system32\csrss.exe (ID: 464 |ParentID: 408)
C:\windows\system32\csrss.exe (ID: 516 |ParentID: 508)
C:\windows\system32\wininit.exe (ID: 524 |ParentID: 408)
C:\windows\system32\services.exe (ID: 572 |ParentID: 524)
C:\windows\system32\winlogon.exe (ID: 604 |ParentID: 508)
C:\windows\system32\lsass.exe (ID: 632 |ParentID: 524)
C:\windows\system32\lsm.exe (ID: 640 |ParentID: 524)
C:\windows\system32\svchost.exe (ID: 756 |ParentID: 572)
C:\windows\system32\svchost.exe (ID: 852 |ParentID: 572)
C:\windows\System32\svchost.exe (ID: 940 |ParentID: 572)
C:\windows\System32\svchost.exe (ID: 1000 |ParentID: 572)
C:\windows\system32\svchost.exe (ID: 1028 |ParentID: 572)
C:\windows\system32\svchost.exe (ID: 1060 |ParentID: 572)
C:\windows\system32\svchost.exe (ID: 1280 |ParentID: 572)
C:\Program Files\AVAST Software\Avast\AvastSvc.exe (ID: 1452 |ParentID: 572)
C:\windows\system32\taskeng.exe (ID: 1604 |ParentID: 1060)
C:\windows\System32\spoolsv.exe (ID: 1612 |ParentID: 572)
C:\windows\system32\svchost.exe (ID: 1644 |ParentID: 572)
C:\windows\system32\svchost.exe (ID: 1676 |ParentID: 572)
C:\Windows\System32\AsusService.exe (ID: 1852 |ParentID: 572)
C:\Program Files\Microsoft\BingBar\SeaPort.EXE (ID: 1892 |ParentID: 572)
C:\Program Files\WIDCOMM\Bluetooth Software\btwdins.exe (ID: 1936 |ParentID: 572)
C:\Program Files\Malwarebytes' Anti-Malware\mbamscheduler.exe (ID: 2008 |ParentID: 572)
C:\Program Files\Malwarebytes' Anti-Malware\mbamservice.exe (ID: 360 |ParentID: 572)
C:\Program Files\RealNetworks\RealDownloader\rndlresolversvc.exe (ID: 636 |ParentID: 572)
C:\Program Files\Microsoft Application Virtualization Client\sftvsa.exe (ID: 1792 |ParentID: 572)
C:\windows\system32\svchost.exe (ID: 2068 |ParentID: 572)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE (ID: 2112 |ParentID: 572)
C:\Program Files\Intel\Intel Matrix Storage Manager\IAANTMon.exe (ID: 2164 |ParentID: 572)
C:\Program Files\Microsoft Application Virtualization Client\sftlist.exe (ID: 2200 |ParentID: 572)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSvcM.exe (ID: 2336 |ParentID: 2112)
C:\windows\system32\taskhost.exe (ID: 2444 |ParentID: 572)
C:\windows\system32\Dwm.exe (ID: 2528 |ParentID: 1000)
C:\windows\Explorer.EXE (ID: 2548 |ParentID: 2520)
C:\Program Files\Malwarebytes' Anti-Malware\mbamgui.exe (ID: 2632 |ParentID: 360)
C:\Program Files\Google\Update\GoogleUpdate.exe (ID: 3004 |ParentID: 1604)
C:\Program Files\Common Files\Microsoft Shared\Virtualization Handler\CVHSVC.EXE (ID: 3040 |ParentID: 572)
C:\windows\system32\svchost.exe (ID: 3224 |ParentID: 572)
C:\windows\system32\svchost.exe (ID: 3360 |ParentID: 572)
C:\Program Files\EeePC\HotkeyService\HotKeyMon.exe (ID: 3812 |ParentID: 1852)
C:\Program Files\ASUS\Eee Docking\Eee Docking.exe (ID: 3912 |ParentID: 2548)
C:\Program Files\EeePC\HotkeyService\HotkeyService.exe (ID: 3888 |ParentID: 1852)
C:\Program Files\EeePC\SHE\SuperHybridEngine.exe (ID: 4004 |ParentID: 1852)
C:\Program Files\ASUS\ASUS WebStorage\SERVICE\AsusWSService.exe (ID: 3988 |ParentID: 2548)
C:\Program Files\EeePC\CapsHook\CapsHook.exe (ID: 1396 |ParentID: 1852)
C:\windows\system32\wbem\wmiprvse.exe (ID: 3516 |ParentID: 756)
C:\windows\system32\SearchIndexer.exe (ID: 364 |ParentID: 572)
C:\Windows\System32\igfxtray.exe (ID: 480 |ParentID: 2548)
C:\Program Files\Asus\LiveUpdate\LiveUpdate.exe (ID: 1716 |ParentID: 1852)
C:\Windows\System32\hkcmd.exe (ID: 352 |ParentID: 2548)
C:\Windows\System32\igfxpers.exe (ID: 2796 |ParentID: 2548)
C:\windows\system32\igfxsrvc.exe (ID: 1132 |ParentID: 756)
C:\Program Files\Realtek\Audio\HDA\RtHDVCpl.exe (ID: 2100 |ParentID: 2548)
C:\Program Files\Synaptics\SynTP\SynTPEnh.exe (ID: 3760 |ParentID: 2548)
C:\Program Files\Boingo\Boingo Wi-Fi\Boingo Wi-Fi.exe (ID: 3076 |ParentID: 2548)
C:\Program Files\Intel\Intel Matrix Storage Manager\IAAnotif.exe (ID: 3508 |ParentID: 2548)
C:\Program Files\Synaptics\SynTP\SynAsusAcpi.exe (ID: 744 |ParentID: 2548)
C:\Program Files\AVAST Software\Avast\AvastUI.exe (ID: 748 |ParentID: 2548)
C:\Program Files\Common Files\Java\Java Update\jusched.exe (ID: 3728 |ParentID: 2548)
C:\Program Files\Synaptics\SynTP\SynTPHelper.exe (ID: 3484 |ParentID: 3760)
C:\Users\Jordy\AppData\Roaming\Spotify\Data\SpotifyWebHelper.exe (ID: 4244 |ParentID: 2548)
C:\ProgramData\Badoo\Badoo Desktop\1.6.58.1220\Badoo.Desktop.exe (ID: 4608 |ParentID: 2548)
C:\Program Files\Skype\Phone\Skype.exe (ID: 4872 |ParentID: 2548)
C:\Users\Jordy\AppData\Local\Amazon Cloud Player\Amazon Music Helper.exe (ID: 4964 |ParentID: 2548)
C:\Program Files\WIDCOMM\Bluetooth Software\BTTray.exe (ID: 4980 |ParentID: 2548)
C:\Program Files\OpenOffice.org 3\program\soffice.exe (ID: 5212 |ParentID: 5068)
C:\Program Files\OpenOffice.org 3\program\soffice.bin (ID: 5440 |ParentID: 5212)
C:\Program Files\WIDCOMM\Bluetooth Software\BtStackServer.exe (ID: 5672 |ParentID: 756)
C:\windows\System32\svchost.exe (ID: 6052 |ParentID: 572)
C:\windows\system32\taskhost.exe (ID: 5868 |ParentID: 572)
C:\Program Files\Common Files\microsoft shared\virtualization handler\cvh.exe (ID: 5068 |ParentID: 2548)
C:\Program Files\Common Files\microsoft shared\virtualization handler\OfficeVirt.exe (ID: 6872 |ParentID: 5068)
C:\Program Files\Common Files\Microsoft Shared\OfficeSoftwareProtectionPlatform\OSPPSVC.EXE (ID: 6184 |ParentID: 572)
C:\windows\system32\wuauclt.exe (ID: 3900 |ParentID: 1060)
C:\Program Files\Real\RealPlayer\update\realsched.exe (ID: 5572 |ParentID: 7748)
C:\windows\system32\svchost.exe (ID: 7076 |ParentID: 572)
C:\Program Files\Google\Chrome\Application\chrome.exe (ID: 2224 |ParentID: 2548)
C:\Program Files\Google\Chrome\Application\chrome.exe (ID: 4444 |ParentID: 2224)
C:\Program Files\Google\Chrome\Application\chrome.exe (ID: 4320 |ParentID: 2224)
C:\windows\System32\WUDFHost.exe (ID: 8104 |ParentID: 1000)
C:\windows\system32\wbem\wmiprvse.exe (ID: 6584 |ParentID: 756)
################## | Regedit Run |
04 - HKCU\..\Run : [msnmsgr] "C:\Program Files\Windows Live\Messenger\msnmsgr.exe" /background
04 - HKCU\..\Run : [Spotify] "C:\Users\Jordy\AppData\Roaming\Spotify\Spotify.exe" /uri spotify:autostart
04 - HKCU\..\Run : [Spotify Web Helper] "C:\Users\Jordy\AppData\Roaming\Spotify\Data\SpotifyWebHelper.exe"
04 - HKCU\..\Run : [Badoo Desktop] C:\ProgramData\Badoo\Badoo Desktop\1.6.58.1220\Badoo.Desktop.exe
04 - HKCU\..\Run : [Facebook Update] "C:\Users\Jordy\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKCU\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKCU\..\Run : [Amazon Cloud Player] "C:\Users\Jordy\AppData\Local\Amazon Cloud Player\Amazon Music Helper.exe"
04 - HKLM\..\Run : [ASUS VIBE] C:\Program Files\ASUS\ASUS VIBE\ASUS VIBE.exe /S
04 - HKLM\..\Run : [EeeSplendidAgent] C:\Program Files\ASUS\EPC\EeeSplendid\AsAgent.exe
04 - HKLM\..\Run : [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe"
04 - HKLM\..\Run : [HotkeyMon] AsusSender.exe C:\Program Files\EeePC\HotkeyService\HotKeyMon.exe
04 - HKLM\..\Run : [HotkeyService] AsusSender.exe C:\Program Files\EeePC\HotkeyService\HotkeyService.exe
04 - HKLM\..\Run : [SuperHybridEngine] AsusSender.exe C:\Program Files\EeePC\SHE\SuperHybridEngine.exe
04 - HKLM\..\Run : [LiveUpdate] AsusSender.exe C:\Program Files\Asus\LiveUpdate\LiveUpdate.exe auto
04 - HKLM\..\Run : [CapsHook] AsusSender.exe C:\Program Files\EeePC\CapsHook\CapsHook.exe
04 - HKLM\..\Run : [Eee Docking] C:\Program Files\ASUS\Eee Docking\Eee Docking.exe autorun
04 - HKLM\..\Run : [ASUS WebStorage] C:\Program Files\ASUS\ASUS WebStorage\SERVICE\AsusWSService.exe
04 - HKLM\..\Run : [IgfxTray] C:\windows\system32\igfxtray.exe
04 - HKLM\..\Run : [HotKeysCmds] C:\windows\system32\hkcmd.exe
04 - HKLM\..\Run : [Persistence] C:\windows\system32\igfxpers.exe
04 - HKLM\..\Run : [RtHDVCpl] C:\Program Files\Realtek\Audio\HDA\RtHDVCpl.exe -s
04 - HKLM\..\Run : [SynTPEnh] %ProgramFiles%\Synaptics\SynTP\SynTPEnh.exe
04 - HKLM\..\Run : [Boingo Wi-Fi] "C:\Program Files\Boingo\Boingo Wi-Fi\Boingo.lnk"
04 - HKLM\..\Run : [IAAnotif] C:\Program Files\Intel\Intel Matrix Storage Manager\iaanotif.exe
04 - HKLM\..\Run : [ASUSPRP] C:\Program Files\ASUS\APRP\APRP.EXE
04 - HKLM\..\Run : [SynAsusAcpi] %ProgramFiles%\Synaptics\SynTP\SynAsusAcpi.exe
04 - HKLM\..\Run : [avast] "C:\Program Files\AVAST Software\Avast\avastUI.exe" /nogui
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [TkBellExe] "C:\Program Files\Real\RealPlayer\update\realsched.exe" -osboot
04 - HKLM\..\RunOnce : [20131224] C:\Program Files\AVAST Software\Avast\setup\emupdate\92701c62-48f8-493e-9421-b4daf6b84b8e.exe /check
04 - HKLM\..\RunOnce : []
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [msnmsgr] "C:\Program Files\Windows Live\Messenger\msnmsgr.exe" /background
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Spotify] "C:\Users\Jordy\AppData\Roaming\Spotify\Spotify.exe" /uri spotify:autostart
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Spotify Web Helper] "C:\Users\Jordy\AppData\Roaming\Spotify\Data\SpotifyWebHelper.exe"
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Badoo Desktop] C:\ProgramData\Badoo\Badoo Desktop\1.6.58.1220\Badoo.Desktop.exe
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Facebook Update] "C:\Users\Jordy\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Amazon Cloud Player] "C:\Users\Jordy\AppData\Local\Amazon Cloud Player\Amazon Music Helper.exe"
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Recherche générique |
Présent! G:\00001.lnk
Présent! G:\LOST.DIR.lnk
Présent! G:\download.lnk
Présent! G:\.android_secure.lnk
Présent! G:\DCIM.lnk
Présent! G:\SoundRecorder.lnk
Présent! G:\Android.lnk
Présent! G:\GOLauncherEXOS.lnk
Présent! G:\GOLauncherEX.lnk
Présent! G:\AppGame.lnk
Présent! G:\.ConvertedTo2D.lnk
Présent! G:\GOWeatherEX.lnk
Présent! G:\Pictures.lnk
Présent! G:\bluetooth.lnk
Présent! G:\Musiques.lnk
Présent! H:\.lnk
Présent! H:\LOST.DIR.lnk
Présent! H:\.android_secure.lnk
Présent! H:\Music.lnk
Présent! H:\Podcasts.lnk
Présent! H:\Ringtones.lnk
Présent! H:\Alarms.lnk
Présent! H:\Notifications.lnk
Présent! H:\Pictures.lnk
Présent! H:\Movies.lnk
Présent! H:\Download.lnk
Présent! H:\DCIM.lnk
Présent! H:\Android.lnk
Présent! H:\GOLauncherEXOS.lnk
Présent! H:\.ConvertedTo2D.lnk
Présent! H:\media.lnk
Présent! H:\mtklog.lnk
Présent! H:\.mblog.lnk
Présent! H:\AppGame.lnk
Présent! H:\GOWeatherEX.lnk
Présent! H:\GOLauncherEX.lnk
################## | Registre |
Présent! HKLM\Software\updat
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Contributeur sécurité# Si ton antivirus affiche une alerte, ignore-la et désactive l'antivirus temporairement.
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Suppression.

# Note : L'ordinateur va redémarrer automatiquement, au redémarrage, clique sur le message transmis par UsbFix et laisse le programme travailler.
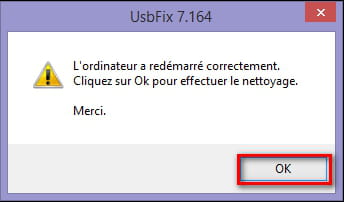
# Laisse travailler l'outil, ton bureau ne sera pas accessible durant la phase de nettoyage, c'est normal.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système ( C:\UsbFix [Clean ?] Nom de l'ordinateur.txt ).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# ->> Tutoriel (aide) en images sur le site de l'auteur.
-
Et voici:
############################## | UsbFix V 7.166 | [Suppression]
Utilisateur: Jordy (Administrateur) # JORDY-PC
Mis à jour le 26/02/2014 par El Desaparecido - Team SosVirus
Lancé à 09:42:20 | 02/03/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://www.sosvirus.net/
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: ASUSTeK Computer INC. (1001PX)
CPU: Intel(R) Atom(TM) CPU N450 @ 1.66GHz
RAM -> [Total : 1014 Mo| Free : 357 Mo]
Bios: American Megatrends Inc.
Boot: Normal boot
OS: Microsoft Windows 7 Édition Starter (6.1.7601 32-Bit) Service Pack 1
WB: Windows Internet Explorer : 10.0.9200.16798
WB: Google Chrome : 26.0.1410.64
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AV: avast! Antivirus [Enabled | Updated]
AS: avast! Antivirus [Enabled | Updated]
AS: Windows Defender [Enabled | Updated]
FW: avast! Internet Security [(!) Disabled]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 100 Go (60 Go libre(s) - 60%) [] # NTFS
D:\ -> Disque fixe # 118 Go (84 Go libre(s) - 71%) [] # NTFS
################## | Processus Actif |
C:\windows\system32\csrss.exe (ID: 468 |ParentID: 412)
C:\windows\system32\wininit.exe (ID: 520 |ParentID: 412)
C:\windows\system32\csrss.exe (ID: 528 |ParentID: 512)
C:\windows\system32\winlogon.exe (ID: 564 |ParentID: 512)
C:\windows\system32\services.exe (ID: 624 |ParentID: 520)
C:\windows\system32\lsass.exe (ID: 636 |ParentID: 520)
C:\windows\system32\lsm.exe (ID: 644 |ParentID: 520)
C:\windows\system32\svchost.exe (ID: 756 |ParentID: 624)
C:\windows\system32\svchost.exe (ID: 844 |ParentID: 624)
C:\windows\System32\svchost.exe (ID: 936 |ParentID: 624)
C:\windows\System32\svchost.exe (ID: 984 |ParentID: 624)
C:\windows\system32\svchost.exe (ID: 1032 |ParentID: 624)
C:\windows\system32\svchost.exe (ID: 1056 |ParentID: 624)
C:\windows\system32\svchost.exe (ID: 1296 |ParentID: 624)
C:\Program Files\AVAST Software\Avast\AvastSvc.exe (ID: 1456 |ParentID: 624)
C:\windows\system32\taskeng.exe (ID: 1600 |ParentID: 1056)
C:\windows\System32\spoolsv.exe (ID: 1608 |ParentID: 624)
C:\windows\system32\svchost.exe (ID: 1644 |ParentID: 624)
C:\windows\system32\svchost.exe (ID: 1684 |ParentID: 624)
C:\Windows\System32\AsusService.exe (ID: 1884 |ParentID: 624)
C:\Program Files\Microsoft\BingBar\BBSvc.EXE (ID: 1924 |ParentID: 624)
C:\Program Files\Microsoft\BingBar\SeaPort.EXE (ID: 1948 |ParentID: 624)
C:\Program Files\WIDCOMM\Bluetooth Software\btwdins.exe (ID: 1992 |ParentID: 624)
C:\Program Files\Malwarebytes' Anti-Malware\mbamscheduler.exe (ID: 264 |ParentID: 624)
C:\Program Files\Malwarebytes' Anti-Malware\mbamservice.exe (ID: 480 |ParentID: 624)
C:\windows\System32\svchost.exe (ID: 632 |ParentID: 624)
C:\windows\System32\svchost.exe (ID: 640 |ParentID: 624)
C:\Program Files\RealNetworks\RealDownloader\rndlresolversvc.exe (ID: 860 |ParentID: 624)
C:\Program Files\Microsoft Application Virtualization Client\sftvsa.exe (ID: 708 |ParentID: 624)
C:\Program Files\Skype\Updater\Updater.exe (ID: 2068 |ParentID: 624)
C:\windows\system32\svchost.exe (ID: 2092 |ParentID: 624)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE (ID: 2140 |ParentID: 624)
C:\Program Files\Intel\Intel Matrix Storage Manager\IAANTMon.exe (ID: 2184 |ParentID: 624)
C:\Program Files\Microsoft Application Virtualization Client\sftlist.exe (ID: 2232 |ParentID: 624)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSvcM.exe (ID: 2264 |ParentID: 2140)
C:\Program Files\Common Files\Microsoft Shared\Virtualization Handler\CVHSVC.EXE (ID: 2628 |ParentID: 624)
C:\windows\servicing\TrustedInstaller.exe (ID: 3076 |ParentID: 624)
C:\windows\system32\svchost.exe (ID: 3124 |ParentID: 624)
C:\windows\system32\svchost.exe (ID: 3192 |ParentID: 624)
C:\windows\system32\taskhost.exe (ID: 3448 |ParentID: 624)
C:\Program Files\Malwarebytes' Anti-Malware\mbamgui.exe (ID: 3472 |ParentID: 480)
C:\windows\system32\Dwm.exe (ID: 3612 |ParentID: 984)
C:\windows\Explorer.EXE (ID: 3620 |ParentID: 3588)
C:\windows\system32\runonce.exe (ID: 3740 |ParentID: 3620)
C:\windows\system32\taskeng.exe (ID: 3788 |ParentID: 1056)
C:\Program Files\Google\Update\GoogleUpdate.exe (ID: 3832 |ParentID: 1600)
C:\windows\system32\wbem\wmiprvse.exe (ID: 3300 |ParentID: 756)
################## | Regedit Run |
04 - HKCU\..\Run : [msnmsgr] "C:\Program Files\Windows Live\Messenger\msnmsgr.exe" /background
04 - HKCU\..\Run : [Spotify] "C:\Users\Jordy\AppData\Roaming\Spotify\Spotify.exe" /uri spotify:autostart
04 - HKCU\..\Run : [Spotify Web Helper] "C:\Users\Jordy\AppData\Roaming\Spotify\Data\SpotifyWebHelper.exe"
04 - HKCU\..\Run : [Badoo Desktop] C:\ProgramData\Badoo\Badoo Desktop\1.6.58.1220\Badoo.Desktop.exe
04 - HKCU\..\Run : [Facebook Update] "C:\Users\Jordy\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKCU\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKCU\..\Run : [Amazon Cloud Player] "C:\Users\Jordy\AppData\Local\Amazon Cloud Player\Amazon Music Helper.exe"
04 - HKLM\..\Run : [ASUS VIBE] C:\Program Files\ASUS\ASUS VIBE\ASUS VIBE.exe /S
04 - HKLM\..\Run : [EeeSplendidAgent] C:\Program Files\ASUS\EPC\EeeSplendid\AsAgent.exe
04 - HKLM\..\Run : [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe"
04 - HKLM\..\Run : [HotkeyMon] AsusSender.exe C:\Program Files\EeePC\HotkeyService\HotKeyMon.exe
04 - HKLM\..\Run : [HotkeyService] AsusSender.exe C:\Program Files\EeePC\HotkeyService\HotkeyService.exe
04 - HKLM\..\Run : [SuperHybridEngine] AsusSender.exe C:\Program Files\EeePC\SHE\SuperHybridEngine.exe
04 - HKLM\..\Run : [LiveUpdate] AsusSender.exe C:\Program Files\Asus\LiveUpdate\LiveUpdate.exe auto
04 - HKLM\..\Run : [CapsHook] AsusSender.exe C:\Program Files\EeePC\CapsHook\CapsHook.exe
04 - HKLM\..\Run : [Eee Docking] C:\Program Files\ASUS\Eee Docking\Eee Docking.exe autorun
04 - HKLM\..\Run : [ASUS WebStorage] C:\Program Files\ASUS\ASUS WebStorage\SERVICE\AsusWSService.exe
04 - HKLM\..\Run : [IgfxTray] C:\windows\system32\igfxtray.exe
04 - HKLM\..\Run : [HotKeysCmds] C:\windows\system32\hkcmd.exe
04 - HKLM\..\Run : [Persistence] C:\windows\system32\igfxpers.exe
04 - HKLM\..\Run : [RtHDVCpl] C:\Program Files\Realtek\Audio\HDA\RtHDVCpl.exe -s
04 - HKLM\..\Run : [SynTPEnh] %ProgramFiles%\Synaptics\SynTP\SynTPEnh.exe
04 - HKLM\..\Run : [Boingo Wi-Fi] "C:\Program Files\Boingo\Boingo Wi-Fi\Boingo.lnk"
04 - HKLM\..\Run : [IAAnotif] C:\Program Files\Intel\Intel Matrix Storage Manager\iaanotif.exe
04 - HKLM\..\Run : [ASUSPRP] C:\Program Files\ASUS\APRP\APRP.EXE
04 - HKLM\..\Run : [SynAsusAcpi] %ProgramFiles%\Synaptics\SynTP\SynAsusAcpi.exe
04 - HKLM\..\Run : [avast] "C:\Program Files\AVAST Software\Avast\avastUI.exe" /nogui
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [TkBellExe] "C:\Program Files\Real\RealPlayer\update\realsched.exe" -osboot
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [msnmsgr] "C:\Program Files\Windows Live\Messenger\msnmsgr.exe" /background
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Spotify] "C:\Users\Jordy\AppData\Roaming\Spotify\Spotify.exe" /uri spotify:autostart
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Spotify Web Helper] "C:\Users\Jordy\AppData\Roaming\Spotify\Data\SpotifyWebHelper.exe"
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Badoo Desktop] C:\ProgramData\Badoo\Badoo Desktop\1.6.58.1220\Badoo.Desktop.exe
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Facebook Update] "C:\Users\Jordy\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Amazon Cloud Player] "C:\Users\Jordy\AppData\Local\Amazon Cloud Player\Amazon Music Helper.exe"
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Recherche générique |
(!) Fichiers temporaires supprimés.
################## | Registre |
Supprimé! HKLM\Software\updat
Réparé ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|EnableLUA -> 1
Réparé ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|ConsentPromptBehaviorAdmin -> 5
################## | Listing |
[08/04/2012 - 13:16:05 | SHD] - C:\$Recycle.Bin
[10/06/2009 - 22:42:20 | N | 0 Ko] - C:\autoexec.bat
[17/04/2012 - 08:28:38 | SHD] - C:\Boot
[20/11/2010 - 13:40:07 | RASH | 375 Ko] - C:\bootmgr
[10/06/2009 - 22:42:20 | N | 0 Ko] - C:\config.sys
[01/12/2013 - 16:33:48 | N | 2 Ko | 46E5B02CE63433842E3E4084FA4FB0E0] - C:\DelFix.txt
[14/07/2009 - 05:53:55 | SHD] - C:\Documents and Settings
[28/12/2013 - 19:31:10 | D] - C:\found.000
[02/03/2014 - 09:40:24 | ASH | 778888 Ko] - C:\hiberfil.sys
[07/06/2010 - 19:06:04 | D] - C:\Intel
[11/04/2012 - 15:49:40 | RHD] - C:\MSOCache
[02/03/2014 - 09:40:29 | ASH | 1048576 Ko] - C:\pagefile.sys
[14/07/2009 - 03:37:05 | D] - C:\PerfLogs
[01/11/2013 - 10:36:41 | N | 1 Ko] - C:\PhysicalMBR.bin
[04/01/2014 - 10:25:00 | D] - C:\Program Files
[01/12/2013 - 16:32:46 | HD] - C:\ProgramData
[08/04/2012 - 12:56:56 | SHD] - C:\Recovery
[08/04/2012 - 13:02:07 | N | 2 Ko] - C:\RHDSetup.log
[02/03/2014 - 09:11:25 | SHD] - C:\System Volume Information
[01/03/2014 - 17:44:02 | D] - C:\UsbFix
[02/03/2014 - 09:44:50 | A | 10 Ko | 84CCBF96419095A7AFDF34F6C5451AD5] - C:\UsbFix [Clean 2] JORDY-PC.txt
[01/03/2014 - 17:49:43 | N | 13 Ko | F2740A4CDA6168EDC7AE80D396AE8233] - C:\UsbFix [Scan 1] JORDY-PC.txt
[08/04/2012 - 12:58:39 | D] - C:\Users
[02/03/2014 - 09:22:23 | D] - C:\Windows
[08/04/2012 - 13:16:05 | D] - D:\$RECYCLE.BIN
[09/09/2010 - 00:05:32 | D] - D:\603c355298a0fe3d86
[08/04/2012 - 15:29:47 | D] - D:\JORDY-PC
[08/04/2012 - 15:29:13 | N | 1 Ko] - D:\MediaID.bin
[26/04/2013 - 18:17:55 | D] - D:\msdownld.tmp
[22/04/2012 - 19:50:15 | SHD] - D:\System Volume Information
[08/04/2012 - 17:00:57 | D] - D:\WindowsImageBackup
################## | Vaccin |
D:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Contributeur sécuritéRecommence
Tu n'as pas connecté tes clés USB!
L'infection est présente sur la clé H -
Ah, bon j'ai retenté l'opération,
############################## | UsbFix V 7.166 | [Suppression]
Utilisateur: Jordy (Administrateur) # JORDY-PC
Mis à jour le 26/02/2014 par El Desaparecido - Team SosVirus
Lancé à 10:52:57 | 02/03/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://www.sosvirus.net/
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: ASUSTeK Computer INC. (1001PX)
CPU: Intel(R) Atom(TM) CPU N450 @ 1.66GHz
RAM -> [Total : 1014 Mo| Free : 352 Mo]
Bios: American Megatrends Inc.
Boot: Normal boot
OS: Microsoft Windows 7 Édition Starter (6.1.7601 32-Bit) Service Pack 1
WB: Windows Internet Explorer : 10.0.9200.16798
WB: Google Chrome : 26.0.1410.64
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AV: avast! Antivirus [Enabled | Updated]
AS: avast! Antivirus [Enabled | Updated]
AS: Windows Defender [Enabled | Updated]
FW: avast! Internet Security [(!) Disabled]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 100 Go (61 Go libre(s) - 61%) [] # NTFS
D:\ -> Disque fixe # 118 Go (84 Go libre(s) - 71%) [] # NTFS
E:\ -> Disque amovible # 4 Go (2 Go libre(s) - 55%) [K-Star] # FAT32
################## | Processus Actif |
C:\windows\system32\csrss.exe (ID: 468 |ParentID: 412)
C:\windows\system32\wininit.exe (ID: 536 |ParentID: 412)
C:\windows\system32\csrss.exe (ID: 544 |ParentID: 524)
C:\windows\system32\winlogon.exe (ID: 592 |ParentID: 524)
C:\windows\system32\services.exe (ID: 648 |ParentID: 536)
C:\windows\system32\lsass.exe (ID: 656 |ParentID: 536)
C:\windows\system32\lsm.exe (ID: 664 |ParentID: 536)
C:\windows\system32\svchost.exe (ID: 772 |ParentID: 648)
C:\windows\system32\svchost.exe (ID: 860 |ParentID: 648)
C:\windows\System32\svchost.exe (ID: 944 |ParentID: 648)
C:\windows\System32\svchost.exe (ID: 1000 |ParentID: 648)
C:\windows\system32\svchost.exe (ID: 1044 |ParentID: 648)
C:\windows\system32\svchost.exe (ID: 1072 |ParentID: 648)
C:\windows\system32\svchost.exe (ID: 1280 |ParentID: 648)
C:\Program Files\AVAST Software\Avast\AvastSvc.exe (ID: 1460 |ParentID: 648)
C:\windows\System32\spoolsv.exe (ID: 1616 |ParentID: 648)
C:\windows\system32\taskeng.exe (ID: 1624 |ParentID: 1072)
C:\windows\system32\svchost.exe (ID: 1664 |ParentID: 648)
C:\windows\system32\svchost.exe (ID: 1700 |ParentID: 648)
C:\Windows\System32\AsusService.exe (ID: 1852 |ParentID: 648)
C:\Program Files\Microsoft\BingBar\BBSvc.EXE (ID: 1884 |ParentID: 648)
C:\Program Files\Microsoft\BingBar\SeaPort.EXE (ID: 1904 |ParentID: 648)
C:\Program Files\WIDCOMM\Bluetooth Software\btwdins.exe (ID: 1964 |ParentID: 648)
C:\Program Files\Malwarebytes' Anti-Malware\mbamscheduler.exe (ID: 2040 |ParentID: 648)
C:\Program Files\Malwarebytes' Anti-Malware\mbamservice.exe (ID: 404 |ParentID: 648)
C:\windows\System32\svchost.exe (ID: 528 |ParentID: 648)
C:\windows\System32\svchost.exe (ID: 660 |ParentID: 648)
C:\Program Files\RealNetworks\RealDownloader\rndlresolversvc.exe (ID: 1068 |ParentID: 648)
C:\Program Files\Microsoft Application Virtualization Client\sftvsa.exe (ID: 2056 |ParentID: 648)
C:\Program Files\Skype\Updater\Updater.exe (ID: 2080 |ParentID: 648)
C:\windows\system32\svchost.exe (ID: 2108 |ParentID: 648)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE (ID: 2168 |ParentID: 648)
C:\Program Files\Intel\Intel Matrix Storage Manager\IAANTMon.exe (ID: 2188 |ParentID: 648)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSvcM.exe (ID: 2252 |ParentID: 2168)
C:\Program Files\Microsoft Application Virtualization Client\sftlist.exe (ID: 2268 |ParentID: 648)
C:\Program Files\Common Files\Microsoft Shared\Virtualization Handler\CVHSVC.EXE (ID: 2500 |ParentID: 648)
C:\windows\servicing\TrustedInstaller.exe (ID: 2652 |ParentID: 648)
C:\windows\system32\svchost.exe (ID: 2696 |ParentID: 648)
C:\windows\system32\svchost.exe (ID: 2744 |ParentID: 648)
C:\windows\system32\taskhost.exe (ID: 2984 |ParentID: 648)
C:\Program Files\Malwarebytes' Anti-Malware\mbamgui.exe (ID: 3128 |ParentID: 404)
C:\windows\system32\Dwm.exe (ID: 3136 |ParentID: 1000)
C:\windows\Explorer.EXE (ID: 3148 |ParentID: 3060)
C:\windows\system32\runonce.exe (ID: 3252 |ParentID: 3148)
C:\windows\system32\taskeng.exe (ID: 3544 |ParentID: 1072)
C:\windows\System32\rundll32.exe (ID: 3608 |ParentID: 772)
C:\Program Files\Google\Update\GoogleUpdate.exe (ID: 3704 |ParentID: 1624)
C:\windows\System32\svchost.exe (ID: 4080 |ParentID: 648)
C:\windows\system32\wbem\wmiprvse.exe (ID: 2948 |ParentID: 772)
################## | Regedit Run |
04 - HKCU\..\Run : [msnmsgr] "C:\Program Files\Windows Live\Messenger\msnmsgr.exe" /background
04 - HKCU\..\Run : [Spotify] "C:\Users\Jordy\AppData\Roaming\Spotify\Spotify.exe" /uri spotify:autostart
04 - HKCU\..\Run : [Spotify Web Helper] "C:\Users\Jordy\AppData\Roaming\Spotify\Data\SpotifyWebHelper.exe"
04 - HKCU\..\Run : [Badoo Desktop] C:\ProgramData\Badoo\Badoo Desktop\1.6.58.1220\Badoo.Desktop.exe
04 - HKCU\..\Run : [Facebook Update] "C:\Users\Jordy\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKCU\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKCU\..\Run : [Amazon Cloud Player] "C:\Users\Jordy\AppData\Local\Amazon Cloud Player\Amazon Music Helper.exe"
04 - HKLM\..\Run : [ASUS VIBE] C:\Program Files\ASUS\ASUS VIBE\ASUS VIBE.exe /S
04 - HKLM\..\Run : [EeeSplendidAgent] C:\Program Files\ASUS\EPC\EeeSplendid\AsAgent.exe
04 - HKLM\..\Run : [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe"
04 - HKLM\..\Run : [HotkeyMon] AsusSender.exe C:\Program Files\EeePC\HotkeyService\HotKeyMon.exe
04 - HKLM\..\Run : [HotkeyService] AsusSender.exe C:\Program Files\EeePC\HotkeyService\HotkeyService.exe
04 - HKLM\..\Run : [SuperHybridEngine] AsusSender.exe C:\Program Files\EeePC\SHE\SuperHybridEngine.exe
04 - HKLM\..\Run : [LiveUpdate] AsusSender.exe C:\Program Files\Asus\LiveUpdate\LiveUpdate.exe auto
04 - HKLM\..\Run : [CapsHook] AsusSender.exe C:\Program Files\EeePC\CapsHook\CapsHook.exe
04 - HKLM\..\Run : [Eee Docking] C:\Program Files\ASUS\Eee Docking\Eee Docking.exe autorun
04 - HKLM\..\Run : [ASUS WebStorage] C:\Program Files\ASUS\ASUS WebStorage\SERVICE\AsusWSService.exe
04 - HKLM\..\Run : [IgfxTray] C:\windows\system32\igfxtray.exe
04 - HKLM\..\Run : [HotKeysCmds] C:\windows\system32\hkcmd.exe
04 - HKLM\..\Run : [Persistence] C:\windows\system32\igfxpers.exe
04 - HKLM\..\Run : [RtHDVCpl] C:\Program Files\Realtek\Audio\HDA\RtHDVCpl.exe -s
04 - HKLM\..\Run : [SynTPEnh] %ProgramFiles%\Synaptics\SynTP\SynTPEnh.exe
04 - HKLM\..\Run : [Boingo Wi-Fi] "C:\Program Files\Boingo\Boingo Wi-Fi\Boingo.lnk"
04 - HKLM\..\Run : [IAAnotif] C:\Program Files\Intel\Intel Matrix Storage Manager\iaanotif.exe
04 - HKLM\..\Run : [ASUSPRP] C:\Program Files\ASUS\APRP\APRP.EXE
04 - HKLM\..\Run : [SynAsusAcpi] %ProgramFiles%\Synaptics\SynTP\SynAsusAcpi.exe
04 - HKLM\..\Run : [avast] "C:\Program Files\AVAST Software\Avast\avastUI.exe" /nogui
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [TkBellExe] "C:\Program Files\Real\RealPlayer\update\realsched.exe" -osboot
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [msnmsgr] "C:\Program Files\Windows Live\Messenger\msnmsgr.exe" /background
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Spotify] "C:\Users\Jordy\AppData\Roaming\Spotify\Spotify.exe" /uri spotify:autostart
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Spotify Web Helper] "C:\Users\Jordy\AppData\Roaming\Spotify\Data\SpotifyWebHelper.exe"
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Badoo Desktop] C:\ProgramData\Badoo\Badoo Desktop\1.6.58.1220\Badoo.Desktop.exe
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Facebook Update] "C:\Users\Jordy\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Amazon Cloud Player] "C:\Users\Jordy\AppData\Local\Amazon Cloud Player\Amazon Music Helper.exe"
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Recherche générique |
(!) Fichiers temporaires supprimés.
################## | Registre |
Réparé ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|EnableLUA -> 1
Réparé ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|ConsentPromptBehaviorAdmin -> 5
################## | Listing |
[08/04/2012 - 13:16:05 | SHD] - C:\$Recycle.Bin
[10/06/2009 - 22:42:20 | N | 0 Ko] - C:\autoexec.bat
[17/04/2012 - 08:28:38 | SHD] - C:\Boot
[20/11/2010 - 13:40:07 | RASH | 375 Ko] - C:\bootmgr
[10/06/2009 - 22:42:20 | N | 0 Ko] - C:\config.sys
[01/12/2013 - 16:33:48 | N | 2 Ko | 46E5B02CE63433842E3E4084FA4FB0E0] - C:\DelFix.txt
[14/07/2009 - 05:53:55 | SHD] - C:\Documents and Settings
[28/12/2013 - 19:31:10 | D] - C:\found.000
[02/03/2014 - 10:50:09 | ASH | 778888 Ko] - C:\hiberfil.sys
[07/06/2010 - 19:06:04 | D] - C:\Intel
[11/04/2012 - 15:49:40 | RHD] - C:\MSOCache
[02/03/2014 - 10:50:12 | ASH | 1048576 Ko] - C:\pagefile.sys
[14/07/2009 - 03:37:05 | D] - C:\PerfLogs
[01/11/2013 - 10:36:41 | N | 1 Ko] - C:\PhysicalMBR.bin
[04/01/2014 - 10:25:00 | D] - C:\Program Files
[01/12/2013 - 16:32:46 | HD] - C:\ProgramData
[08/04/2012 - 12:56:56 | SHD] - C:\Recovery
[08/04/2012 - 13:02:07 | N | 2 Ko] - C:\RHDSetup.log
[02/03/2014 - 09:11:25 | SHD] - C:\System Volume Information
[02/03/2014 - 10:47:50 | D] - C:\UsbFix
[02/03/2014 - 09:44:50 | N | 11 Ko | 4602BFC745E836DBBF749CB922257C0F] - C:\UsbFix [Clean 2] JORDY-PC.txt
[02/03/2014 - 10:54:45 | A | 10 Ko | FB7C5DC6E59AD1AA6F4F84F23944E26D] - C:\UsbFix [Clean 4] JORDY-PC.txt
[01/03/2014 - 17:49:43 | N | 13 Ko | F2740A4CDA6168EDC7AE80D396AE8233] - C:\UsbFix [Scan 1] JORDY-PC.txt
[08/04/2012 - 12:58:39 | D] - C:\Users
[02/03/2014 - 09:22:23 | D] - C:\Windows
[08/04/2012 - 13:16:05 | D] - D:\$RECYCLE.BIN
[09/09/2010 - 00:05:32 | D] - D:\603c355298a0fe3d86
[08/04/2012 - 15:29:47 | D] - D:\JORDY-PC
[08/04/2012 - 15:29:13 | N | 1 Ko] - D:\MediaID.bin
[26/04/2013 - 18:17:55 | D] - D:\msdownld.tmp
[22/04/2012 - 19:50:15 | SHD] - D:\System Volume Information
[08/04/2012 - 17:00:57 | D] - D:\WindowsImageBackup
################## | Vaccin |
D:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
E:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Contributeur sécuritéToujours pas
Où sont les clés G et H?
-
Ah.... Bon cette fois j'espère que c'est la bonne! :)
############################## | UsbFix V 7.166 | [Suppression]
Utilisateur: Jordy (Administrateur) # JORDY-PC
Mis à jour le 26/02/2014 par El Desaparecido - Team SosVirus
Lancé à 11:08:41 | 02/03/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://www.sosvirus.net/
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: ASUSTeK Computer INC. (1001PX)
CPU: Intel(R) Atom(TM) CPU N450 @ 1.66GHz
RAM -> [Total : 1014 Mo| Free : 393 Mo]
Bios: American Megatrends Inc.
Boot: Normal boot
OS: Microsoft Windows 7 Édition Starter (6.1.7601 32-Bit) Service Pack 1
WB: Windows Internet Explorer : 10.0.9200.16798
WB: Google Chrome : 26.0.1410.64
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AV: avast! Antivirus [Enabled | Updated]
AS: avast! Antivirus [Enabled | Updated]
AS: Windows Defender [Enabled | Updated]
FW: avast! Internet Security [(!) Disabled]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 100 Go (61 Go libre(s) - 61%) [] # NTFS
D:\ -> Disque fixe # 118 Go (84 Go libre(s) - 71%) [] # NTFS
E:\ -> Disque amovible # 4 Go (2 Go libre(s) - 55%) [K-Star] # FAT32
G:\ -> Disque amovible # 4 Go (2 Go libre(s) - 65%) [] # FAT32
H:\ -> Disque amovible # 1 Go (1002 Mo libre(s) - 93%) [WIKO] # FAT32
################## | Processus Actif |
C:\windows\system32\csrss.exe (ID: 468 |ParentID: 412)
C:\windows\system32\wininit.exe (ID: 520 |ParentID: 412)
C:\windows\system32\csrss.exe (ID: 528 |ParentID: 512)
C:\windows\system32\services.exe (ID: 576 |ParentID: 520)
C:\windows\system32\winlogon.exe (ID: 608 |ParentID: 512)
C:\windows\system32\lsass.exe (ID: 636 |ParentID: 520)
C:\windows\system32\lsm.exe (ID: 644 |ParentID: 520)
C:\windows\system32\svchost.exe (ID: 756 |ParentID: 576)
C:\windows\system32\svchost.exe (ID: 860 |ParentID: 576)
C:\windows\System32\svchost.exe (ID: 948 |ParentID: 576)
C:\windows\System32\svchost.exe (ID: 996 |ParentID: 576)
C:\windows\system32\svchost.exe (ID: 1028 |ParentID: 576)
C:\windows\system32\svchost.exe (ID: 1072 |ParentID: 576)
C:\windows\system32\svchost.exe (ID: 1312 |ParentID: 576)
C:\Program Files\AVAST Software\Avast\AvastSvc.exe (ID: 1464 |ParentID: 576)
C:\windows\system32\taskeng.exe (ID: 1616 |ParentID: 1072)
C:\windows\System32\spoolsv.exe (ID: 1624 |ParentID: 576)
C:\windows\system32\svchost.exe (ID: 1660 |ParentID: 576)
C:\windows\system32\svchost.exe (ID: 1700 |ParentID: 576)
C:\Windows\System32\AsusService.exe (ID: 1916 |ParentID: 576)
C:\Program Files\Microsoft\BingBar\BBSvc.EXE (ID: 1936 |ParentID: 576)
C:\Program Files\Microsoft\BingBar\SeaPort.EXE (ID: 1956 |ParentID: 576)
C:\Program Files\WIDCOMM\Bluetooth Software\btwdins.exe (ID: 2000 |ParentID: 576)
C:\Program Files\Malwarebytes' Anti-Malware\mbamscheduler.exe (ID: 356 |ParentID: 576)
C:\Program Files\Malwarebytes' Anti-Malware\mbamservice.exe (ID: 464 |ParentID: 576)
C:\windows\System32\svchost.exe (ID: 932 |ParentID: 576)
C:\windows\System32\svchost.exe (ID: 1264 |ParentID: 576)
C:\Program Files\RealNetworks\RealDownloader\rndlresolversvc.exe (ID: 1356 |ParentID: 576)
C:\windows\system32\taskhost.exe (ID: 1528 |ParentID: 576)
C:\Program Files\Microsoft Application Virtualization Client\sftvsa.exe (ID: 2152 |ParentID: 576)
C:\Program Files\Malwarebytes' Anti-Malware\mbamgui.exe (ID: 2176 |ParentID: 464)
C:\Program Files\Skype\Updater\Updater.exe (ID: 2208 |ParentID: 576)
C:\windows\system32\svchost.exe (ID: 2260 |ParentID: 576)
C:\windows\system32\Dwm.exe (ID: 2280 |ParentID: 996)
C:\windows\Explorer.EXE (ID: 2304 |ParentID: 2216)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE (ID: 2340 |ParentID: 576)
C:\Program Files\Intel\Intel Matrix Storage Manager\IAANTMon.exe (ID: 2408 |ParentID: 576)
C:\Program Files\Microsoft Application Virtualization Client\sftlist.exe (ID: 2484 |ParentID: 576)
C:\windows\system32\runonce.exe (ID: 2508 |ParentID: 2304)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSvcM.exe (ID: 2552 |ParentID: 2340)
C:\windows\system32\taskeng.exe (ID: 2728 |ParentID: 1072)
C:\Program Files\Google\Update\GoogleUpdate.exe (ID: 2844 |ParentID: 1616)
C:\Program Files\Common Files\Microsoft Shared\Virtualization Handler\CVHSVC.EXE (ID: 2872 |ParentID: 576)
C:\windows\system32\svchost.exe (ID: 3652 |ParentID: 576)
C:\windows\servicing\TrustedInstaller.exe (ID: 3708 |ParentID: 576)
C:\windows\system32\svchost.exe (ID: 3744 |ParentID: 576)
C:\windows\System32\WUDFHost.exe (ID: 4008 |ParentID: 996)
C:\windows\System32\rundll32.exe (ID: 4024 |ParentID: 756)
C:\windows\system32\wbem\wmiprvse.exe (ID: 2932 |ParentID: 756)
################## | Regedit Run |
04 - HKCU\..\Run : [msnmsgr] "C:\Program Files\Windows Live\Messenger\msnmsgr.exe" /background
04 - HKCU\..\Run : [Spotify] "C:\Users\Jordy\AppData\Roaming\Spotify\Spotify.exe" /uri spotify:autostart
04 - HKCU\..\Run : [Spotify Web Helper] "C:\Users\Jordy\AppData\Roaming\Spotify\Data\SpotifyWebHelper.exe"
04 - HKCU\..\Run : [Badoo Desktop] C:\ProgramData\Badoo\Badoo Desktop\1.6.58.1220\Badoo.Desktop.exe
04 - HKCU\..\Run : [Facebook Update] "C:\Users\Jordy\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKCU\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKCU\..\Run : [Amazon Cloud Player] "C:\Users\Jordy\AppData\Local\Amazon Cloud Player\Amazon Music Helper.exe"
04 - HKLM\..\Run : [ASUS VIBE] C:\Program Files\ASUS\ASUS VIBE\ASUS VIBE.exe /S
04 - HKLM\..\Run : [EeeSplendidAgent] C:\Program Files\ASUS\EPC\EeeSplendid\AsAgent.exe
04 - HKLM\..\Run : [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe"
04 - HKLM\..\Run : [HotkeyMon] AsusSender.exe C:\Program Files\EeePC\HotkeyService\HotKeyMon.exe
04 - HKLM\..\Run : [HotkeyService] AsusSender.exe C:\Program Files\EeePC\HotkeyService\HotkeyService.exe
04 - HKLM\..\Run : [SuperHybridEngine] AsusSender.exe C:\Program Files\EeePC\SHE\SuperHybridEngine.exe
04 - HKLM\..\Run : [LiveUpdate] AsusSender.exe C:\Program Files\Asus\LiveUpdate\LiveUpdate.exe auto
04 - HKLM\..\Run : [CapsHook] AsusSender.exe C:\Program Files\EeePC\CapsHook\CapsHook.exe
04 - HKLM\..\Run : [Eee Docking] C:\Program Files\ASUS\Eee Docking\Eee Docking.exe autorun
04 - HKLM\..\Run : [ASUS WebStorage] C:\Program Files\ASUS\ASUS WebStorage\SERVICE\AsusWSService.exe
04 - HKLM\..\Run : [IgfxTray] C:\windows\system32\igfxtray.exe
04 - HKLM\..\Run : [HotKeysCmds] C:\windows\system32\hkcmd.exe
04 - HKLM\..\Run : [Persistence] C:\windows\system32\igfxpers.exe
04 - HKLM\..\Run : [RtHDVCpl] C:\Program Files\Realtek\Audio\HDA\RtHDVCpl.exe -s
04 - HKLM\..\Run : [SynTPEnh] %ProgramFiles%\Synaptics\SynTP\SynTPEnh.exe
04 - HKLM\..\Run : [Boingo Wi-Fi] "C:\Program Files\Boingo\Boingo Wi-Fi\Boingo.lnk"
04 - HKLM\..\Run : [IAAnotif] C:\Program Files\Intel\Intel Matrix Storage Manager\iaanotif.exe
04 - HKLM\..\Run : [ASUSPRP] C:\Program Files\ASUS\APRP\APRP.EXE
04 - HKLM\..\Run : [SynAsusAcpi] %ProgramFiles%\Synaptics\SynTP\SynAsusAcpi.exe
04 - HKLM\..\Run : [avast] "C:\Program Files\AVAST Software\Avast\avastUI.exe" /nogui
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [TkBellExe] "C:\Program Files\Real\RealPlayer\update\realsched.exe" -osboot
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [msnmsgr] "C:\Program Files\Windows Live\Messenger\msnmsgr.exe" /background
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Spotify] "C:\Users\Jordy\AppData\Roaming\Spotify\Spotify.exe" /uri spotify:autostart
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Spotify Web Helper] "C:\Users\Jordy\AppData\Roaming\Spotify\Data\SpotifyWebHelper.exe"
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Badoo Desktop] C:\ProgramData\Badoo\Badoo Desktop\1.6.58.1220\Badoo.Desktop.exe
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Facebook Update] "C:\Users\Jordy\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKU\S-1-5-21-798286396-1796259554-2711769751-1000\..\Run : [Amazon Cloud Player] "C:\Users\Jordy\AppData\Local\Amazon Cloud Player\Amazon Music Helper.exe"
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Recherche générique |
Supprimé! G:\00001.lnk
Supprimé! G:\LOST.DIR.lnk
Supprimé! G:\download.lnk
Supprimé! G:\.android_secure.lnk
Supprimé! G:\DCIM.lnk
Supprimé! G:\SoundRecorder.lnk
Supprimé! G:\Android.lnk
Supprimé! G:\GOLauncherEXOS.lnk
Supprimé! G:\GOLauncherEX.lnk
Supprimé! G:\AppGame.lnk
Supprimé! G:\.ConvertedTo2D.lnk
Supprimé! G:\GOWeatherEX.lnk
Supprimé! G:\Pictures.lnk
Supprimé! G:\bluetooth.lnk
Supprimé! G:\Musiques.lnk
Supprimé! H:\.lnk
Supprimé! H:\LOST.DIR.lnk
Supprimé! H:\.android_secure.lnk
Supprimé! H:\Music.lnk
Supprimé! H:\Podcasts.lnk
Supprimé! H:\Ringtones.lnk
Supprimé! H:\Alarms.lnk
Supprimé! H:\Notifications.lnk
Supprimé! H:\Pictures.lnk
Supprimé! H:\Movies.lnk
Supprimé! H:\Download.lnk
Supprimé! H:\DCIM.lnk
Supprimé! H:\Android.lnk
Supprimé! H:\GOLauncherEXOS.lnk
Supprimé! H:\.ConvertedTo2D.lnk
Supprimé! H:\media.lnk
Supprimé! H:\mtklog.lnk
Supprimé! H:\.mblog.lnk
Supprimé! H:\AppGame.lnk
Supprimé! H:\GOWeatherEX.lnk
Supprimé! H:\GOLauncherEX.lnk
(!) Fichiers temporaires supprimés.
################## | Registre |
Réparé ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|EnableLUA -> 1
Réparé ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|ConsentPromptBehaviorAdmin -> 5
################## | Listing |
[08/04/2012 - 13:16:05 | SHD] - C:\$Recycle.Bin
[10/06/2009 - 22:42:20 | N | 0 Ko] - C:\autoexec.bat
[17/04/2012 - 08:28:38 | SHD] - C:\Boot
[20/11/2010 - 13:40:07 | RASH | 375 Ko] - C:\bootmgr
[10/06/2009 - 22:42:20 | N | 0 Ko] - C:\config.sys
[01/12/2013 - 16:33:48 | N | 2 Ko | 46E5B02CE63433842E3E4084FA4FB0E0] - C:\DelFix.txt
[14/07/2009 - 05:53:55 | SHD] - C:\Documents and Settings
[28/12/2013 - 19:31:10 | D] - C:\found.000
[02/03/2014 - 11:07:25 | ASH | 778888 Ko] - C:\hiberfil.sys
[07/06/2010 - 19:06:04 | D] - C:\Intel
[11/04/2012 - 15:49:40 | RHD] - C:\MSOCache
[02/03/2014 - 11:07:28 | ASH | 1048576 Ko] - C:\pagefile.sys
[14/07/2009 - 03:37:05 | D] - C:\PerfLogs
[01/11/2013 - 10:36:41 | N | 1 Ko] - C:\PhysicalMBR.bin
[04/01/2014 - 10:25:00 | D] - C:\Program Files
[01/12/2013 - 16:32:46 | HD] - C:\ProgramData
[08/04/2012 - 12:56:56 | SHD] - C:\Recovery
[08/04/2012 - 13:02:07 | N | 2 Ko] - C:\RHDSetup.log
[02/03/2014 - 09:11:25 | SHD] - C:\System Volume Information
[02/03/2014 - 11:06:21 | D] - C:\UsbFix
[02/03/2014 - 09:44:50 | N | 11 Ko | 4602BFC745E836DBBF749CB922257C0F] - C:\UsbFix [Clean 2] JORDY-PC.txt
[02/03/2014 - 10:54:48 | N | 11 Ko | A37517A82F89803A34C5400A9AFF7D52] - C:\UsbFix [Clean 4] JORDY-PC.txt
[02/03/2014 - 11:11:19 | A | 11 Ko | 555E7E3A3E300907EAE0044EC9FC14A4] - C:\UsbFix [Clean 6] JORDY-PC.txt
[01/03/2014 - 17:49:43 | N | 13 Ko | F2740A4CDA6168EDC7AE80D396AE8233] - C:\UsbFix [Scan 1] JORDY-PC.txt
[08/04/2012 - 12:58:39 | D] - C:\Users
[02/03/2014 - 09:22:23 | D] - C:\Windows
[08/04/2012 - 13:16:05 | D] - D:\$RECYCLE.BIN
[09/09/2010 - 00:05:32 | D] - D:\603c355298a0fe3d86
[08/04/2012 - 15:29:47 | D] - D:\JORDY-PC
[08/04/2012 - 15:29:13 | N | 1 Ko] - D:\MediaID.bin
[26/04/2013 - 18:17:55 | D] - D:\msdownld.tmp
[22/04/2012 - 19:50:15 | SHD] - D:\System Volume Information
[08/04/2012 - 17:00:57 | D] - D:\WindowsImageBackup
[06/02/2014 - 08:58:40 | D] - E:\FOUND.000
[20/04/2012 - 17:27:34 | D] - E:\Nelly Furtado
[28/09/2013 - 19:31:18 | D] - E:\Robin Stjernberg
[19/01/2014 - 16:45:04 | D] - E:\Lana Del Rey
[28/09/2013 - 19:23:40 | D] - E:\Cocorosie
[22/12/2013 - 06:33:26 | N | 8974 Ko] - E:\_9834_9829_9834_--Katy_Perry_-_Legendary_lovers.mp3
[04/03/2013 - 00:28:00 | D] - E:\Dido
[01/08/2013 - 06:11:06 | N | 6406 Ko] - E:\L_Amour_A_C_est_Raison_Que_La_Raison_Ignore--James_Arthur_-_Impossible.mp3
[29/01/2014 - 09:20:38 | N | 8099 Ko] - E:\01 - Into The Blue.mp3
[28/09/2013 - 19:25:18 | D] - E:\Flight Facilities feat_ Christine Hoberg
[02/02/2014 - 16:02:20 | N | 234262 Ko] - E:\DJ Skerdi - Romanian Electro (The Year Mix 2012).mp3
[07/09/2013 - 09:38:24 | D] - E:\Margaux Avril
[02/02/2014 - 15:47:50 | N | 150313 Ko] - E:\DJ Skerdi - Progressive House Yearmix 2013 (Top 100 Beatport).mp3
[22/07/2013 - 21:58:46 | N | 4213 Ko] - E:\Celeste-Party_Never_Ends_-INNA_Shining_Star_.mp3
[19/10/2013 - 12:45:48 | N | 3020 Ko] - E:\Bah_Traor_--INNA_feat._Yandel_-_In_Your_Eyes.mp3
[28/09/2013 - 10:40:22 | D] - E:\Multi Interprètes
[01/08/2013 - 06:00:58 | N | 4969 Ko] - E:\Dannii_Minogue-I_Begin_To_Wonder(mp3squid.com).mp3
[06/11/2013 - 12:01:36 | N | 1454 Ko] - E:\DJ-lil_gwada-AMG-45--DVBBS_Borgeous_-_Tsunami_Radio_Edit_le_carton_du_moment_new_2013.mp3
[06/11/2013 - 12:12:04 | N | 8228 Ko] - E:\Myl_ne_farmer-Bleu_Noir-Moi_je_veux.mp3
[06/11/2013 - 12:04:24 | N | 4818 Ko] - E:\Myl_ne_Farmer-Monkey_Me-Myl_ne_Farmer_-_Love_Dance.mp3
[06/11/2013 - 12:06:12 | N | 4093 Ko] - E:\Mylene_Farmer-Point_De_Suture-Je_M_Ennuie_MYLENE_FARMER_Web_Radio_FARMER-PointDeSouture.mp3
[06/11/2013 - 12:01:32 | N | 5330 Ko] - E:\Musiic_Don_t_Stop_9829_-Lady_Gaga-Do_What_U_Want_Ft_R_Kelly_.mp3
[06/11/2013 - 12:01:38 | N | 5491 Ko] - E:\Musiic_Don_t_Stop_9829_-Lady_Gaga-Venus.mp3
[06/11/2013 - 12:11:00 | N | 10099 Ko] - E:\Myl_ne_farmer-Bleu_Noir-Diabolique_mon_ange.mp3
[07/09/2013 - 17:54:56 | N | 4983 Ko] - E:\Madonna-I_m_Breathless-Vogue_-_Madonna_1990_.mp3
[16/08/2013 - 10:38:56 | N | 8105 Ko] - E:\Loreen - We Got The Power.mp3
[29/07/2013 - 06:18:58 | N | 3329 Ko] - E:\Les_cendres_se_dispercent-_9829_9829_-Showtek_-_Slow_Down.mp3
[23/08/2013 - 22:41:24 | N | 5366 Ko] - E:\_8594_._305_l_305_ll_305_.P_8467_945_y_8467_ist._305_l_305_ll_305_.--Madonna_ft._David_Guetta_Lil_Wayne_-_Revolver.mp3
[01/08/2013 - 06:11:46 | N | 5321 Ko] - E:\_9834_music_9829_--shontelle_-_impossible.mp3
[15/10/2013 - 06:18:10 | N | 3330 Ko] - E:\_associer_blog_que-du-bon-son-du-13009_T_l_charge_gratuitement_--Tara_McDonald_ft_Zaho_-_Shooting_Star_sortie_2013.mp3
[22/07/2013 - 22:34:58 | N | 9279 Ko] - E:\Beyonc_G._Knowles-B-REVOLUTION-Beyonce_-_Run_the_World_Girls_.mp3
[01/12/2013 - 23:02:50 | N | 8006 Ko] - E:\faithless_feat_dido_one_step_too_far_320.mp3
[01/12/2013 - 23:04:18 | N | 17192 Ko] - E:\feelin_good_faithless_feat_dido_320.mp3
[02/02/2014 - 12:29:02 | N | 152018 Ko] - E:\DJ Skerdi - Romanain Electronicast #1.mp3
[02/02/2014 - 12:06:10 | N | 69047 Ko] - E:\DJ Skerdi - Romanian Electronicast #04.mp3
[12/12/2013 - 10:51:48 | N | 3090 Ko] - E:\Britney_Spears-Britney_Jean-Don_t_Cry.mp3
[12/12/2013 - 10:51:10 | N | 2808 Ko] - E:\Britney_Spears-Britney_Jean-Tik_Tik_Boom_feat._T.I._.mp3
[12/12/2013 - 10:51:42 | N | 3521 Ko] - E:\Britney_Spears-Britney_Jean-Til_It_s_Gone.mp3
[12/12/2013 - 10:45:12 | N | 7267 Ko] - E:\BritishBoy-The_Wanted-I_Found_You.mp3
[12/12/2013 - 10:52:36 | N | 3698 Ko] - E:\Britney_Spears-Britney_Jean-Alien.mp3
[12/12/2013 - 10:51:16 | N | 3257 Ko] - E:\Britney_Spears-Britney_Jean-Body_Ache.mp3
[12/12/2013 - 10:58:56 | N | 8263 Ko] - E:\BelgiumMusic-Ceci_n_est_pas_un_clip-Stromae_-_B_tard.mp3
[08/12/2013 - 19:15:42 | N | 7871 Ko] - E:\B39-Sunny_Tales-Sunlounger_feat._Zara_-_Lost.mp3
[08/12/2013 - 19:15:36 | N | 8602 Ko] - E:\B39--Moonbeam_Tyler_Michaud_feat._Fisher_-_Love_Never_Dies.mp3
[17/12/2013 - 08:53:10 | N | 133649 Ko] - E:\onceforgo.mp3
[19/07/2013 - 07:06:34 | N | 8869 Ko] - E:\Lana_Del_Rey_9829_-Born_To_Die-Summertime_Sadness_9829_ (1).mp3
[19/07/2013 - 07:07:04 | N | 9502 Ko] - E:\Lana_Del_Rey_9829_-Born_To_Die-Dark_Paradise_9835_.mp3
[17/12/2013 - 08:35:36 | N | 145442 Ko] - E:\Echoes of Summer - Jan 2012.mp3
[17/12/2013 - 10:30:46 | N | 77742 Ko] - E:\DJ Skerdi - Romanian Electronicast #03.mp3
[22/12/2013 - 06:33:34 | N | 9087 Ko] - E:\_9834_9829_9834_--Katy_Perry_-_International_Smile.mp3
[30/05/2013 - 14:56:00 | D] - G:\LOST.DIR
[26/02/2014 - 02:19:50 | D] - G:\download
[30/05/2013 - 14:56:00 | D] - G:\.android_secure
[22/10/2013 - 21:13:44 | D] - G:\DCIM
[10/08/2013 - 21:24:04 | D] - G:\SoundRecorder
[22/09/2013 - 18:19:32 | D] - G:\Android
[22/09/2013 - 19:07:56 | D] - G:\GOLauncherEXOS
[22/09/2013 - 19:25:26 | D] - G:\GOLauncherEX
[22/09/2013 - 19:25:42 | D] - G:\AppGame
[23/09/2013 - 09:20:26 | D] - G:\.ConvertedTo2D
[28/09/2013 - 12:51:10 | D] - G:\GOWeatherEX
[28/09/2013 - 21:54:56 | D] - G:\Pictures
[20/02/2014 - 17:40:16 | D] - G:\bluetooth
[19/10/2013 - 18:58:02 | N | 0 Ko] - G:\00001.vcf
[25/01/2014 - 22:13:44 | D] - G:\badoo
[26/01/2014 - 11:00:06 | N | 59 Ko] - G:\00002.vcf
[12/10/2013 - 23:28:52 | D] - G:\Musiques
[26/02/2014 - 23:11:08 | D] - G:\burstlyVideoCache
[01/01/2013 - 00:00:04 | D] - H:\LOST.DIR
[01/01/2013 - 00:00:04 | D] - H:\.android_secure
[01/01/2013 - 00:00:04 | D] - H:\Music
[01/01/2013 - 00:00:04 | D] - H:\Podcasts
[18/09/2013 - 20:40:08 | D] - H:\Ringtones
[01/01/2013 - 00:00:04 | D] - H:\Alarms
[01/01/2013 - 00:00:14 | D] - H:\Notifications
[22/09/2013 - 13:16:02 | D] - H:\Pictures
[01/01/2013 - 00:00:06 | D] - H:\Movies
[20/09/2013 - 20:18:44 | D] - H:\Download
[15/09/2013 - 22:07:20 | D] - H:\DCIM
[01/01/2013 - 00:00:12 | D] - H:\Android
[01/01/2013 - 01:01:40 | D] - H:\GOLauncherEXOS
[01/01/2013 - 01:02:34 | D] - H:\.ConvertedTo2D
[14/09/2013 - 00:10:10 | N | 0 Ko] - H:\.config_p56
[14/09/2013 - 21:28:08 | D] - H:\media
[16/09/2013 - 09:17:18 | N | 0 Ko] - H:\.profig.os
[16/09/2013 - 14:12:14 | D] - H:\mtklog
[16/09/2013 - 14:12:14 | D] - H:\.mblog
[18/09/2013 - 21:45:38 | D] - H:\AppGame
[18/09/2013 - 23:54:56 | D] - H:\GOWeatherEX
[18/09/2013 - 21:49:12 | D] - H:\GOLauncherEX
################## | Vaccin |
D:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
E:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
G:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
H:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Contributeur sécurité:)
Plus de raccourci?
-
Non! :)
-
Contributeur sécurité:)
On vérifie quand même ou pas l'état de ton pc?
-
Volontiers!
-
Contributeur sécurité* Télécharge ZHPDiag (de Nicolas Coolman)
https://www.zebulon.fr/telechargements/securite/systeme/zhpdiag.html ou https://www.commentcamarche.net/telecharger/utilitaires/24803-zhpdiag/
* Au cas où le premier lien ne marcherai pas, clique sur celui de dessous
ftp://zebulon.fr/ZHPDiag2.exe
* Laisse toi guider lors de l'installation, il se lancera automatiquement à la fin.
* Surtout, n'oublie pas d'installer son icône sur le bureau l'icône est en forme de parchemin
https://www.cjoint.com/13sp/CIvuQfap3YY_zhpdiag.png
* A l'ouverture du logiciel il te sera proposé deux options "rechercher" et "configurer"
* Cliques sur configurer
* Tournevis puis tous
* Clique sur l'icône représentant une loupe + (« Lancer le diagnostic »)
* Enregistre le rapport sur ton Bureau à l'aide de l'icône représentant une disquette
* Pour héberger le rapport, rends toi sur cjoint.com
* Clique sur choisissez un fichier va chercher le rapport dans ton PC.
* Le rapport est hébergé:
- Pour XP : C:\Documents and Settings\username\Local Settings\Application Data\ZHP
- Depuis Vista : C:\Users\username\AppData\Roaming\ZHP
* Une fois le rapport trouvé, sélectionne le, et clique sur Ouvrir
* Choisis le type de diffusion(je te conseille privée 4 jours il sera détruit)
* Puis cliques sur créer le lien cjoint
* Une fois que tu auras obtenu le lien copies colle dans ta prochaine réponse
* Pour t'aider https://www.commentcamarche.net/faq/29493-utiliser-cjoint-pour-heberger-des-fichiers
-
-
Contributeur sécuritéPas grand chose :)
Avast pas à jour passe à la version 9 ;) -
OKk, je fais çà! Merci beaucoup!
-
Contributeur sécuritéIl y a juste des clés de registre inoffensives :)


