
Trojan.p2p worm
suite à un scan, malwarebytes me signale un trojan.p2p worm. Pouvez vous m'indiquer ce qu'il faut faire?
merci de me répondre.
54 réponses
Une alerte Malwarebytes signale un trojan.p2p worm après un scan et la problématique porte sur les mesures à prendre pour nettoyer et sécuriser le système. La meilleure réponse propose d’utiliser Delfix pour désinstaller les outils de désinfection et purger la restauration, puis de maintenir les logiciels à jour et de nettoyer les fichiers temporaires. Elle recommande des outils de mise à jour (Filehippo Update Checker, CCleaner) et des précautions de navigation (sécuriser les navigateurs, éviter le téléchargement via P2P et sites douteux). En dernier élément utile, la discussion rappelle de maintenir Windows Update et d’être vigilant lors des téléchargements, en évitant les sources douteuses et en surveillant les programmes indésirables.
-
Contributeur sécuritéHello
###########| Canned Recherche
# Télécharge UsbFix par El Desaparecido sur ton Bureau.
# Si ton antivirus affiche une alerte, ignore-la et désactive l'antivirus temporairement.
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Recherche.

# Laisse travailler l'outil.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système ( C:\UsbFix [Scan ?] Nom de l'ordinateur.txt ).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# Tutoriel (aide) en images
-
merci de m'aider, voici le rapport USBFIX
############################## | UsbFix V 7.167 | [Recherche]
Utilisateur: patrick (Administrateur) # PC-DE-PATRICK
Mis à jour le 13/03/2014 par El Desaparecido - Team SosVirus
Lancé à 12:02:54 | 16/03/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://depannageinformatique.org/acheter/reservation/?f=6
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: ASUSTeK Computer INC. (M2R-FVM)
CPU: AMD Athlon(tm) 64 Processor 3500+
RAM -> [Total : 2014 Mo| Free : 944 Mo]
Bios: Phoenix Technologies, LTD
Boot: Normal boot
OS: Microsoft® Windows Vista(TM) Édition Familiale Basique (6.0.6002 32-Bit) Service Pack 2
WB: Windows Internet Explorer : 9.0.8112.16421
WB: Mozilla Firefox : 27.0.1
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AV: avast! Antivirus [(!) Disabled | Updated]
AS: Windows Defender [Enabled | Updated]
AS: avast! Antivirus [(!) Disabled | Updated]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 108 Go (8 Go libre(s) - 7%) [SYSTEM] # NTFS
D:\ -> Disque fixe # 27 Go (1 Go libre(s) - 5%) [DATA] # NTFS
E:\ -> CD-ROM
F:\ -> Disque amovible # 7 Go (3 Go libre(s) - 35%) [STORE N GO] # FAT32
################## | Processus Actif |
C:\Windows\system32\csrss.exe (ID: 524 |ParentID: 512)
C:\Windows\system32\wininit.exe (ID: 576 |ParentID: 512)
C:\Windows\system32\csrss.exe (ID: 584 |ParentID: 568)
C:\Windows\system32\winlogon.exe (ID: 632 |ParentID: 568)
C:\Windows\system32\services.exe (ID: 660 |ParentID: 576)
C:\Windows\system32\lsass.exe (ID: 676 |ParentID: 576)
C:\Windows\system32\lsm.exe (ID: 684 |ParentID: 576)
C:\Windows\system32\svchost.exe (ID: 848 |ParentID: 660)
C:\Windows\system32\svchost.exe (ID: 928 |ParentID: 660)
C:\Windows\System32\svchost.exe (ID: 960 |ParentID: 660)
C:\Windows\system32\Ati2evxx.exe (ID: 1044 |ParentID: 660)
C:\Windows\System32\svchost.exe (ID: 1096 |ParentID: 660)
C:\Windows\System32\svchost.exe (ID: 1132 |ParentID: 660)
C:\Windows\system32\svchost.exe (ID: 1144 |ParentID: 660)
C:\Windows\system32\svchost.exe (ID: 1252 |ParentID: 660)
C:\Windows\system32\SLsvc.exe (ID: 1268 |ParentID: 660)
C:\Windows\system32\svchost.exe (ID: 1304 |ParentID: 660)
C:\Windows\system32\Ati2evxx.exe (ID: 1384 |ParentID: 1044)
C:\Windows\system32\svchost.exe (ID: 1512 |ParentID: 660)
C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (ID: 1664 |ParentID: 660)
C:\Windows\System32\spoolsv.exe (ID: 1820 |ParentID: 660)
C:\Windows\system32\svchost.exe (ID: 1852 |ParentID: 660)
C:\Program Files\Common Files\Adobe\ARM\1.0\armsvc.exe (ID: 856 |ParentID: 660)
C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe (ID: 1376 |ParentID: 660)
C:\PROGRA~1\COMMON~1\France Telecom\Shared Modules\FTRTSVC\0\FTRTSVC.exe (ID: 292 |ParentID: 660)
C:\Windows\system32\svchost.exe (ID: 1036 |ParentID: 660)
C:\Program Files\Malwarebytes' Anti-Malware\mbamscheduler.exe (ID: 2084 |ParentID: 660)
C:\Program Files\Common Files\Microsoft Shared\VS7DEBUG\MDM.EXE (ID: 2228 |ParentID: 660)
C:\Windows\System32\svchost.exe (ID: 2244 |ParentID: 660)
C:\Windows\System32\svchost.exe (ID: 2272 |ParentID: 660)
C:\Windows\system32\svchost.exe (ID: 2284 |ParentID: 660)
C:\Windows\system32\svchost.exe (ID: 2304 |ParentID: 660)
C:\Windows\System32\svchost.exe (ID: 2336 |ParentID: 660)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE (ID: 2376 |ParentID: 660)
C:\Windows\system32\SearchIndexer.exe (ID: 2484 |ParentID: 660)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSvcM.exe (ID: 2616 |ParentID: 2376)
C:\Windows\system32\taskeng.exe (ID: 3260 |ParentID: 1144)
C:\Windows\system32\svchost.exe (ID: 3780 |ParentID: 660)
C:\Windows\system32\Dwm.exe (ID: 3588 |ParentID: 1132)
C:\Windows\Explorer.EXE (ID: 3540 |ParentID: 3220)
C:\Windows\system32\taskeng.exe (ID: 2748 |ParentID: 1144)
C:\Windows\RtHDVCpl.exe (ID: 3108 |ParentID: 3540)
C:\Program Files\Alwil Software\Avast5\AvastUI.exe (ID: 2992 |ParentID: 3540)
C:\Program Files\Common Files\Java\Java Update\jusched.exe (ID: 2672 |ParentID: 3540)
C:\Program Files\Mozilla Firefox\firefox.exe (ID: 168 |ParentID: 3540)
C:\Windows\System32\WUDFHost.exe (ID: 3760 |ParentID: 1132)
C:\Windows\system32\conime.exe (ID: 680 |ParentID: 3848)
C:\Windows\system32\ctfmon.exe (ID: 3492 |ParentID: 2992)
C:\Windows\system32\SearchProtocolHost.exe (ID: 1072 |ParentID: 2484)
C:\Windows\system32\SearchFilterHost.exe (ID: 2520 |ParentID: 2484)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 736 |ParentID: 848)
################## | Regedit Run |
F2 - HKLM\..\Winlogon : [Shell] explorer.exe
F2 - [64bit] HKLM\..\Winlogon : [Shell] explorer.exe
F2 - HKLM\..\Winlogon : [Userinit] C:\Windows\system32\userinit.exe,
F2 - [64bit] HKLM\..\Winlogon : [Userinit] C:\Windows\system32\userinit.exe,
04 - HKCU\..\Run : [Google Update] "C:\Users\patrick\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKCU\..\Run : [MsgCenterExe] "C:\Program Files\Real\RealPlayer\update\RealOneMessageCenter.exe" -osboot
04 - HKLM\..\Run : [Windows Defender] %ProgramFiles%\Windows Defender\MSASCui.exe -hide
04 - HKLM\..\Run : [RtHDVCpl] RtHDVCpl.exe
04 - HKLM\..\Run : [ORAHSSSessionManager] "C:\Program Files\Orange\Connexion Internet Orange\SessionManager\SessionManager.exe"
04 - HKLM\..\Run : [Malwarebytes Anti-Malware (reboot)] "C:\Program Files\Malwarebytes' Anti-Malware\mbam.exe" /runcleanupscript
04 - HKLM\..\Run : [avast5] "C:\Program Files\Alwil Software\Avast5\avastUI.exe" /nogui
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [APSDaemon] "C:\Program Files\Common Files\Apple\Apple Application Support\APSDaemon.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [AvastUI.exe] "C:\Program Files\Alwil Software\Avast5\AvastUI.exe" /nogui
04 - HKLM\..\Run : [QuickTime Task] "C:\Program Files\VistaCodecPack\QT\QTTask.exe" -atboottime
04 - HKLM\..\RunOnce : []
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /detectMem
04 - HKU\S-1-5-19\..\Run : [WindowsWelcomeCenter] rundll32.exe oobefldr.dll,ShowWelcomeCenter
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /detectMem
04 - HKU\S-1-5-20\..\Run : [WindowsWelcomeCenter] rundll32.exe oobefldr.dll,ShowWelcomeCenter
04 - HKU\S-1-5-21-1848170651-1566554758-3786996702-1000\..\Run : [Google Update] "C:\Users\patrick\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKU\S-1-5-21-1848170651-1566554758-3786996702-1000\..\Run : [MsgCenterExe] "C:\Program Files\Real\RealPlayer\update\RealOneMessageCenter.exe" -osboot
################## | Recherche générique |
Présent! C:\Users\Public\sdelevURL.tmp
################## | Registre |
Présent! HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced|Start_ShowPrinters -> 0
Présent! HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced|Start_ShowRecentDocs -> 0
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Contributeur sécuritéPourrais tu poster le rapport de Mbam aussi ?
# Si ton antivirus affiche une alerte, ignore-la et désactive l'antivirus temporairement.
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Suppression.

# Note : L'ordinateur va redémarrer automatiquement, au redémarrage, clique sur le message transmis par UsbFix et laisse le programme travailler.
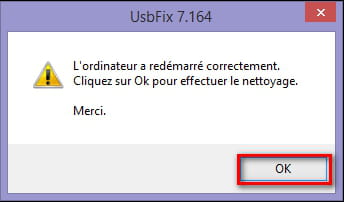
# Laisse travailler l'outil, ton bureau ne sera pas accessible durant la phase de nettoyage, c'est normal.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système ( C:\UsbFix [Clean ?] Nom de l'ordinateur.txt ).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# ->> Tutoriel (aide) en images sur le site de l'auteur.
-
J'ai fait suppression sur usbfix depuis4 heures, et il ne se passe rien, juste un tiret qui clignote enhaut a gauche de l'ecran. J'ai eteint l'ordi, pensant recommencer l'operation, mais depuis l'allumage, rien... juste le tiret qui clignote. Que dois je faire?
-
Contributeur sécuritéEssaie d'accéder au mode de démarrage avancé
-
Mode sans echec?
-
J'ai reussi a avoir l'ecran options de demarrage avancees, et maintenant je fait quoi?
-
Il n'y a plus personne pour me repondre?
-
Contributeur sécuritéTente une restauration d'avant la suppression avec usbfix
-
j'ai redémarré l'ordi en mode sans echec, lancé avast et usbfix s'est remis en route.
voici le rapport mais je ne sais pas si il est complet
############################## | UsbFix V 7.167 | [Suppression]
Utilisateur: patrick (Administrateur) # PC-DE-PATRICK
Mis à jour le 13/03/2014 par El Desaparecido - Team SosVirus
Lancé à 19:25:25 | 16/03/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://depannageinformatique.org/acheter/reservation/?f=6
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: ASUSTeK Computer INC. (M2R-FVM)
CPU: AMD Athlon(tm) 64 Processor 3500+
RAM -> [Total : 2014 Mo| Free : 1292 Mo]
Bios: Phoenix Technologies, LTD
Boot: Normal boot
OS: Microsoft® Windows Vista(TM) Édition Familiale Basique (6.0.6002 32-Bit) Service Pack 2
WB: Windows Internet Explorer : 9.0.8112.16421
WB: Mozilla Firefox : 27.0.1
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AV: avast! Antivirus [(!) Disabled | Updated]
AS: Windows Defender [(!) Disabled | Updated]
AS: avast! Antivirus [(!) Disabled | Updated]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 108 Go (8 Go libre(s) - 7%) [SYSTEM] # NTFS
D:\ -> Disque fixe # 27 Go (1 Go libre(s) - 5%) [DATA] # NTFS
E:\ -> CD-ROM
################## | Processus Actif |
C:\Windows\system32\csrss.exe (ID: 532 |ParentID: 520)
C:\Windows\system32\wininit.exe (ID: 584 |ParentID: 520)
C:\Windows\system32\csrss.exe (ID: 592 |ParentID: 576)
C:\Windows\system32\winlogon.exe (ID: 632 |ParentID: 576)
C:\Windows\system32\services.exe (ID: 668 |ParentID: 584)
C:\Windows\system32\lsass.exe (ID: 680 |ParentID: 584)
C:\Windows\system32\lsm.exe (ID: 688 |ParentID: 584)
C:\Windows\system32\svchost.exe (ID: 856 |ParentID: 668)
C:\Windows\system32\svchost.exe (ID: 932 |ParentID: 668)
C:\Windows\System32\svchost.exe (ID: 964 |ParentID: 668)
C:\Windows\system32\Ati2evxx.exe (ID: 1056 |ParentID: 668)
C:\Windows\System32\svchost.exe (ID: 1112 |ParentID: 668)
C:\Windows\System32\svchost.exe (ID: 1140 |ParentID: 668)
C:\Windows\system32\svchost.exe (ID: 1152 |ParentID: 668)
C:\Windows\system32\svchost.exe (ID: 1256 |ParentID: 668)
C:\Windows\system32\SLsvc.exe (ID: 1272 |ParentID: 668)
C:\Windows\system32\svchost.exe (ID: 1292 |ParentID: 668)
C:\Windows\system32\Ati2evxx.exe (ID: 1412 |ParentID: 1056)
C:\Windows\system32\svchost.exe (ID: 1540 |ParentID: 668)
C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (ID: 1712 |ParentID: 668)
C:\Windows\System32\spoolsv.exe (ID: 1840 |ParentID: 668)
C:\Windows\system32\svchost.exe (ID: 1864 |ParentID: 668)
C:\Windows\system32\taskeng.exe (ID: 500 |ParentID: 1152)
C:\Windows\system32\Dwm.exe (ID: 748 |ParentID: 1140)
C:\Windows\system32\taskeng.exe (ID: 844 |ParentID: 1152)
C:\Windows\Explorer.EXE (ID: 1380 |ParentID: 596)
C:\Program Files\Common Files\Adobe\ARM\1.0\armsvc.exe (ID: 1612 |ParentID: 668)
C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe (ID: 1740 |ParentID: 668)
C:\PROGRA~1\COMMON~1\France Telecom\Shared Modules\FTRTSVC\0\FTRTSVC.exe (ID: 1908 |ParentID: 668)
C:\Windows\system32\svchost.exe (ID: 240 |ParentID: 668)
C:\Program Files\Malwarebytes' Anti-Malware\mbamscheduler.exe (ID: 1420 |ParentID: 668)
C:\Program Files\Common Files\Microsoft Shared\VS7DEBUG\MDM.EXE (ID: 2232 |ParentID: 668)
C:\Windows\System32\svchost.exe (ID: 2260 |ParentID: 668)
C:\Windows\System32\svchost.exe (ID: 2300 |ParentID: 668)
C:\Windows\system32\svchost.exe (ID: 2312 |ParentID: 668)
C:\Windows\system32\svchost.exe (ID: 2348 |ParentID: 668)
C:\Windows\System32\svchost.exe (ID: 2376 |ParentID: 668)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE (ID: 2428 |ParentID: 668)
C:\Windows\system32\SearchIndexer.exe (ID: 2456 |ParentID: 668)
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSvcM.exe (ID: 2672 |ParentID: 2428)
C:\Windows\system32\runonce.exe (ID: 3204 |ParentID: 1380)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 3952 |ParentID: 856)
################## | Regedit Run |
F2 - HKLM\..\Winlogon : [Shell] explorer.exe
F2 - [64bit] HKLM\..\Winlogon : [Shell] explorer.exe
F2 - HKLM\..\Winlogon : [Userinit] C:\Windows\system32\userinit.exe,
F2 - [64bit] HKLM\..\Winlogon : [Userinit] C:\Windows\system32\userinit.exe,
04 - HKCU\..\Run : [Google Update] "C:\Users\patrick\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKCU\..\Run : [MsgCenterExe] "C:\Program Files\Real\RealPlayer\update\RealOneMessageCenter.exe" -osboot
04 - HKLM\..\Run : [Windows Defender] %ProgramFiles%\Windows Defender\MSASCui.exe -hide
04 - HKLM\..\Run : [RtHDVCpl] RtHDVCpl.exe
04 - HKLM\..\Run : [ORAHSSSessionManager] "C:\Program Files\Orange\Connexion Internet Orange\SessionManager\SessionManager.exe"
04 - HKLM\..\Run : [Malwarebytes Anti-Malware (reboot)] "C:\Program Files\Malwarebytes' Anti-Malware\mbam.exe" /runcleanupscript
04 - HKLM\..\Run : [avast5] "C:\Program Files\Alwil Software\Avast5\avastUI.exe" /nogui
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [APSDaemon] "C:\Program Files\Common Files\Apple\Apple Application Support\APSDaemon.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [AvastUI.exe] "C:\Program Files\Alwil Software\Avast5\AvastUI.exe" /nogui
04 - HKLM\..\Run : [QuickTime Task] "C:\Program Files\VistaCodecPack\QT\QTTask.exe" -atboottime
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /detectMem
04 - HKU\S-1-5-19\..\Run : [WindowsWelcomeCenter] rundll32.exe oobefldr.dll,ShowWelcomeCenter
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /detectMem
04 - HKU\S-1-5-20\..\Run : [WindowsWelcomeCenter] rundll32.exe oobefldr.dll,ShowWelcomeCenter
04 - HKU\S-1-5-21-1848170651-1566554758-3786996702-1000\..\Run : [Google Update] "C:\Users\patrick\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKU\S-1-5-21-1848170651-1566554758-3786996702-1000\..\Run : [MsgCenterExe] "C:\Program Files\Real\RealPlayer\update\RealOneMessageCenter.exe" -osboot
################## | Recherche générique |
Supprimé! C:\Users\Public\sdelevURL.tmp
(!) Fichiers temporaires supprimés.
################## | Registre |
Réparé ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|EnableLUA -> 1
Réparé ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|ConsentPromptBehaviorAdmin -> 5
Réparé ! HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced|Start_ShowPrinters -> 1
Réparé ! HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced|Start_ShowRecentDocs -> 1
Supprimé! HKU\S-1-5-21-1848170651-1566554758-3786996702-1000\Software\.\.\.\.\Mountpoints2\{20551f9c-4504-11dc-beaf-001a9243b0bf}
Supprimé! HKU\S-1-5-21-1848170651-1566554758-3786996702-1000\Software\.\.\.\.\Mountpoints2\{42fd037f-d408-11dd-81e2-f07d7d244276}
Supprimé! HKU\S-1-5-21-1848170651-1566554758-3786996702-1000\Software\.\.\.\.\Mountpoints2\{f781649e-521e-11dc-8e69-001a9243b0bf}
################## | Listing |
[28/07/2007 - 11:54:34 | SHD] - C:\$Recycle.Bin
[10/10/2013 - 08:35:55 | D] - C:\58d45bfec2179dfd03
[02/05/2009 - 17:57:05 | N | 3 Ko] - C:\Ad-Report-Clean-02.05.2009.log
[02/05/2009 - 11:29:36 | N | 3 Ko] - C:\Ad-Report-Scan-02.05.2009.log
[29/01/2014 - 10:24:47 | D] - C:\AdwCleaner
[06/12/2006 - 09:23:32 | N | 0 Ko] - C:\appinst.cmd
[18/09/2006 - 22:43:36 | A | 0 Ko] - C:\autoexec.bat
[24/09/2009 - 14:10:21 | SHD] - C:\Boot
[11/04/2009 - 07:36:36 | RASH | 325 Ko] - C:\bootmgr
[08/02/2007 - 08:38:36 | RAS | 8 Ko] - C:\BOOTSECT.BAK
[14/03/2014 - 12:23:36 | D] - C:\Config.Msi
[18/09/2006 - 22:43:37 | N | 0 Ko] - C:\config.sys
[02/11/2006 - 13:59:44 | SHD] - C:\Documents and Settings
[31/07/2007 - 17:58:46 | D] - C:\DRIVER
[07/02/2008 - 17:51:28 | D] - C:\Drivers
[13/12/2008 - 02:45:57 | N | 353 Ko | 20FD267C6F4A49C8D2E69BBF001B3F0F] - C:\ExtractLog.txt
[02/11/2012 - 13:41:53 | D] - C:\FirstSteps
[21/02/2014 - 12:24:00 | D] - C:\found.000
[16/03/2014 - 19:23:00 | ASH | 2062904 Ko] - C:\hiberfil.sys
[08/02/2007 - 09:42:58 | RASH | 0 Ko] - C:\IO.SYS
[10/01/2010 - 00:52:14 | N | 0 Ko] - C:\ioSpecial.ini
[08/02/2007 - 08:39:09 | D] - C:\ISP
[18/02/2008 - 00:00:49 | D] - C:\k3d
[05/02/2012 - 12:33:04 | D] - C:\leg
[31/07/2007 - 17:49:56 | D] - C:\MANUAL
[08/02/2007 - 09:42:58 | RASH | 0 Ko] - C:\MSDOS.SYS
[04/10/2007 - 18:05:46 | RHD] - C:\MSOCache
[08/02/2007 - 09:16:08 | D] - C:\nero
[16/03/2014 - 19:22:58 | ASH | 2048000 Ko] - C:\pagefile.sys
[21/05/2008 - 12:44:34 | D] - C:\PerfLogs
[08/02/2007 - 08:39:51 | N | 1 Ko | 021035FEFF2CE69DC955D6344DEAE6CA] - C:\Prodlog.txt
[13/03/2014 - 20:39:14 | D] - C:\Program Files
[13/03/2014 - 20:39:14 | D] - C:\ProgramData
[28/07/2007 - 21:14:24 | D] - C:\Securitoo
[18/01/2011 - 14:41:36 | N | 1 Ko | 24C366B93F6481D513FB0E0FBFB4A9B9] - C:\Setup Log.txt
[09/11/2006 - 15:05:25 | N | 0 Ko | 7D729CA2DF0B0DF5A2B08227574A74FE] - C:\sort-d.txt
[15/03/2014 - 15:58:51 | SHD] - C:\System Volume Information
[28/07/2007 - 11:52:48 | D] - C:\TMP
[26/09/2009 - 12:29:21 | N | 1 Ko] - C:\updatedatfix.log
[16/03/2014 - 12:02:35 | D] - C:\UsbFix
[16/03/2014 - 19:26:46 | A | 9 Ko | 55D76A24FBFB9C50CEF4E945A79F4EBD] - C:\UsbFix [Clean 2] PC-DE-PATRICK.txt
[16/03/2014 - 11:59:20 | N | 7 Ko | 5B4AD82CE4068444B89E53E61C3A2301] - C:\UsbFix [Scan 1] PC-DE-PATRICK.txt
[16/03/2014 - 12:03:20 | N | 7 Ko | 532D3F44EDCB9EA22AF5FF72170615E7] - C:\UsbFix [Scan 2] PC-DE-PATRICK.txt
[28/07/2007 - 11:53:54 | D] - C:\Users
[14/11/2006 - 08:42:32 | N | 0 Ko] - C:\vtype.cmd
[01/12/2007 - 13:00:56 | D] - C:\Winamp
[16/03/2014 - 19:12:21 | D] - C:\Windows
[08/02/2007 - 08:52:02 | D] - C:\x86
[28/07/2007 - 11:54:34 | SHD] - D:\$RECYCLE.BIN
[14/02/2011 - 01:18:04 | N | 718086 Ko] - D:\A.History.Of.Violence.avi
[31/12/2009 - 11:38:44 | N | 3 Ko] - D:\AlbumArtSmall.jpg
[21/03/2009 - 23:03:24 | N | 8 Ko] - D:\AlbumArt_{007F1ADC-5E1B-4C1A-AB53-DEED98FEC4C1}_Large.jpg
[21/03/2009 - 23:03:15 | N | 2 Ko] - D:\AlbumArt_{007F1ADC-5E1B-4C1A-AB53-DEED98FEC4C1}_Small.jpg
[28/12/2008 - 17:09:30 | N | 13 Ko] - D:\AlbumArt_{13E528B1-D1A6-4BB4-BB08-82D00919DDB6}_Large.jpg
[28/12/2008 - 17:09:27 | N | 3 Ko] - D:\AlbumArt_{13E528B1-D1A6-4BB4-BB08-82D00919DDB6}_Small.jpg
[25/03/2008 - 21:36:18 | N | 10 Ko] - D:\AlbumArt_{4158D985-A563-4DC5-976B-E257E0914584}_Large.jpg
[25/03/2008 - 21:36:17 | N | 3 Ko] - D:\AlbumArt_{4158D985-A563-4DC5-976B-E257E0914584}_Small.jpg
[28/12/2008 - 17:07:54 | N | 14 Ko] - D:\AlbumArt_{4EEB1242-7916-4361-A158-9C9C635312EA}_Large.jpg
[28/12/2008 - 17:07:51 | N | 3 Ko] - D:\AlbumArt_{4EEB1242-7916-4361-A158-9C9C635312EA}_Small.jpg
[31/12/2009 - 11:38:45 | N | 16 Ko] - D:\AlbumArt_{4F348092-364A-4952-851A-9A192C6732C5}_Large.jpg
[31/12/2009 - 11:38:44 | N | 3 Ko] - D:\AlbumArt_{4F348092-364A-4952-851A-9A192C6732C5}_Small.jpg
[21/03/2009 - 23:03:28 | N | 10 Ko] - D:\AlbumArt_{A1B72686-18A5-4171-B0CF-45D23C929193}_Large.jpg
[21/03/2009 - 23:03:25 | N | 2 Ko] - D:\AlbumArt_{A1B72686-18A5-4171-B0CF-45D23C929193}_Small.jpg
[21/03/2009 - 23:02:40 | N | 11 Ko] - D:\AlbumArt_{F809EF15-3242-4D31-9C17-0320EB386E52}_Large.jpg
[21/03/2009 - 23:02:33 | N | 3 Ko] - D:\AlbumArt_{F809EF15-3242-4D31-9C17-0320EB386E52}_Small.jpg
[03/01/2014 - 15:41:27 | N | 1436272 Ko] - D:\Apres.Mai.2012.zone-telechargement.com.avi
[04/01/2014 - 20:28:42 | N | 634239 Ko] - D:\camille.claudel.1915.2013.french.bdrip.x264-tickets.avi
[05/01/2014 - 14:34:36 | N | 602919 Ko] - D:\Chemins.D.Ecole.Chemins.De.Tous.Les.Dangers.E01.Nepal.DOC.FRENCH.HDTV.x264-ABiTBOL.www.zone-telechargement.com.mp4
[31/12/2009 - 11:38:45 | SH | 0 Ko] - D:\desktop.ini
[02/01/2011 - 03:49:28 | N | 717301 Ko] - D:\Et.Dieu.Crea.Lafesse.FRENCH.DVDRiP.XviD-SBX.avi
[31/12/2009 - 11:38:45 | N | 16 Ko] - D:\Folder.jpg
[11/08/2013 - 00:50:25 | N | 1433497 Ko] - D:\In.The.Fog.2013.VOSTFR.BRRiP.XViD.by-adrien95-wawa-mania.ec.AVI
[11/01/2011 - 01:03:50 | N | 717028 Ko] - D:\La.Famille.Wolberg.FRENCH.DVDRip.XviD-UNSKiLLED.avi
[04/01/2014 - 14:09:07 | N | 712831 Ko] - D:\La.Fille.De.Nulle.Part.2012.FRENCH.DVDRip.XviD-UTT.avi
[18/01/2014 - 14:13:21 | N | 752809 Ko] - D:\La.Playa.D.C.2012.VOSTFR.DVDRiP.XViD-LOLOTE.AVI
[07/01/2014 - 08:37:05 | N | 724304 Ko] - D:\Mobius.2013.avi
[16/03/2014 - 19:22:58 | ASH | 2369368 Ko] - D:\pagefile.sys
[27/01/2014 - 13:58:25 | N | 519401 Ko] - D:\PIERRE RABHI au nom de la terre dvdrip tchelss avi.avi
[15/03/2014 - 12:44:30 | SHD] - D:\System Volume Information
[24/02/2013 - 23:33:20 | D] - D:\toto
[13/03/2014 - 00:06:15 | D] - D:\United.Red.Army.FRENCH.SUBBED.DVDRip.XviD-COGiTO
################## | Vaccin |
D:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
pas moyen d'envoyer ma réponse en cliquant sur la case "répondre au sujet"
est ce qu je dois ouvrir un nouveau sujet? -
Contributeur sécuritéHéberge le rapport
Tu as pu démarrer normalement?
-
-
ModérateurBonsoir
Message restauré
https://forums.commentcamarche.net/forum/affich-29888568-trojan-p2p-worm#16
-
-
Contributeur sécuritéOui vu le bot a happé certains de tes messages
=> https://forums.commentcamarche.net/forum/affich-29892546-disparition-message#p29892764
mais réponds à ceci
=> Tu as pu démarrer normalement?
Si problème il y a il existe toujours une solution
~~~~~~ Cs ~~~~~~ -
Contributeur sécurité:)
Héberge sur cjoint
Redémarre en mode normal :)
-
Contributeur sécuritéSi si
Le rapport usbfix est trop long
-
Contributeur sécuritéLa clé F était pas branchée?
-
bonjour,
la clé n'était plus branchée quand j'ai redémarré l'ordi en mode sans échec. -
Contributeur sécuritéIl aurait fallu la brancher
-
Je recommence le tout?
-
Contributeur sécuritéFais juste recherche ;)


- 1
- 2
- 3


