Ordi qui rame
Résolu
Bonsoir,
Depuis 3 jours, mon ordi rame à tout les niveaux : démarrage des programmes, lire des vidéos, navigation sur le net.... je pense que j'ai chopé une cochonnerie
J'ai fait un scan ad-ware qui m'a trouvé des trucs et j'ai pu les supprimer. Mais le problème est toujours là
Pouvez-vous m'aider ?
Depuis 3 jours, mon ordi rame à tout les niveaux : démarrage des programmes, lire des vidéos, navigation sur le net.... je pense que j'ai chopé une cochonnerie
J'ai fait un scan ad-ware qui m'a trouvé des trucs et j'ai pu les supprimer. Mais le problème est toujours là
Pouvez-vous m'aider ?
7 réponses
Résumé de la discussion
Ralentissement généralisé d'un ordinateur depuis plusieurs jours, malgré un scan adware et la suppression apparente de menaces, conduit à une demande d'aide et à l'examen de plusieurs rapports de nettoyage. Les rapports détaillent des éléments PUP et extensions malveillantes, notamment des proxy et des modules Astromenda, avec une première tentative de réparation via ZHPCleaner qui n'élimine pas toutes les menaces, puis une seconde réparation partielle. Par ailleurs, des conseils recommandent Delfix et CCleaner, la désactivation puis création d'un point de restauration, et l'usage de Malwarebytes ou Secunia PSI, tout en évitant les téléchargements trompeurs et la conservation des outils.
-
ContributeurPour moi plus de problèmes :

voici quelques conseils :
c'est juste des conseils ......
C'est un canned, (discours déjà prêt) si il y a des liens qui ne fonctionnent pas il suffit de me le signaler .fin de désinfection
ensuite Quelques conseils
Pour terminer :
Les programmes que nous avons utilisés ne doivent pas être conservés.
Beaucoup d'entre eux peuvent être dangereux et entrainer des dommages irréversibles sur ton système s'ils sont utilisés sans l'aide d'une personne qualifiée, de plus, fréquemment modifiés et mis à jour par leurs auteurs ils deviennent très rapidement obsolètes, en plus d'encombrer inutilement ton bureau.
1/ Désinstallation des outils :
Delfix
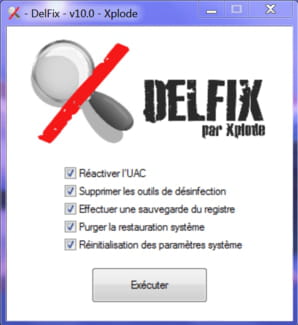
Delfix à changé et est devenu plus performant !
1 - Télécharges DelFix sur votre bureau ICI (grosse flèche verte)
2 - Vous pouvez cocher la case "réactiver l'UAC s'il a été désactivé !
la case "suprimer les outils de désinfection est cochée par défaut !
3 - vous pouvez cocher la case "éffectuer une sauvegarde du registre ! (au cas ou il y est un pbl )
4 - vous pouvez cocher la case "purger la restauration système" tous les anciens points seront supprimés et un nouveau "sain" sera créer !
5 - enfin cliquez sur : exécuter
ps : Pour usage simple si rien n'est indiqué le passer comme il est programmé !
Puis :
2/Télécharge et installe
Ccleaner
CCleaner (N'installe pas la Yahoo Toolbar) :
1 - Avec ce logiciel on va supprimer les fichiers temporaires et inutiles sur ton PC. Ce n'est pas un logiciel qui supprime les infections
2 - Avant toute chose commence par décocher la case activer la surveillance du système :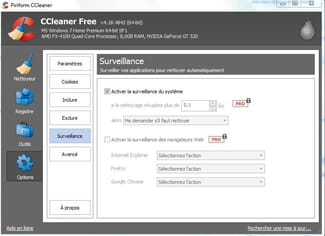
3- Lance-le. Va dans Options puis Avancé et décoche la case Effacer uniquement les fichiers etc....
4- Va dans Nettoyeur, choisis Analyse. Une fois terminé, lance le nettoyage.
5- Lance le nettoyage autant de fois qu'il faut pour que ce soit vide !
tu as aussi beaucoup de programmes au démarrage , (et qui reste actif tout le temps (évidement))
laisse Ccleaner comme il est paramétré , c'est plus léger mais c'est plus sur !!!
pour les désactiver (les programmes au démarrage) , moi j'utilise ccleaner
>> je l'ouvre >> onglet >> outil , puis >>démarrage et je désactive certains programmes
je te conseille de désactiver tout les programmes (surtout ceux que tu ne connais pas !) sinon >> recherche google !
sauf l'antivirus !
(sur les 3 ou 4 moteurs de recherche présent ! si..!)
(les programmes seront toujours là quand tu en auras besoin mais ne "tourneront" plus continuellement !)
puis à l'onglet Nettoyeur , Analyser , puis Nettoyer, !plusieurs fois , jusqu'a ce qu'il n'y ai plus rien
en suite la fin tu fermes et tu redemarres ton ordinateur pour que tes paramètrages soit pris en compte !
Enfin(si cela n'a pas été fait avec Delfix)
3/ Désactive la restauration système et crée un point de restauration
1 - Dans la barre des tâches de Windows, clique sur Démarrer.
2 - Clique avec le bouton droit de la souris sur Poste de travail puis clique sur Propriétés.
3 - Dans l'onglet Restauration du système, coche "Désactiver la Restauration du système"
4 - Clique sur Appliquer.
5 - Ensuite décoche "Désactiver la restauration du système"
6 - Clique sur appliquer puis ok
Crée un point de restauration en cliquant sur démarrer => tous les programmes => accessoires => outils système => restauration du système => créer un point de restauration => tu mets un nom (par exemple : PR après désinfection) puis tu valides .
OU : Logiciel de Lady >>(très simple d'utilisation) : oneclick-2-restore-point
-------------------------------------------------------------
IMPORTANT
Maintenir ses programmes à jourSécunia
téléchargement :
Sécunia
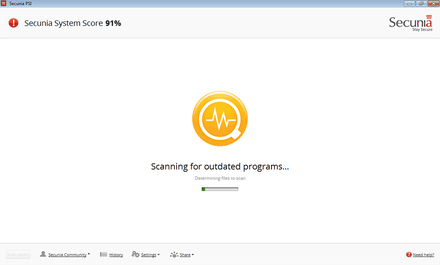
Une connexion internet active est nécessaire pendant le fonctionnement du logiciel.Secunia PSI scanne votre PC :
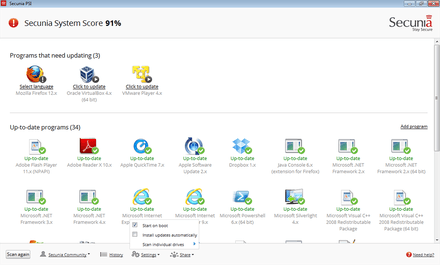
Plusieurs vieilles versions "dangereuses" à utiliser ont été détectées :
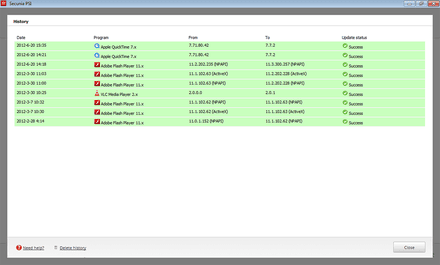
Historique
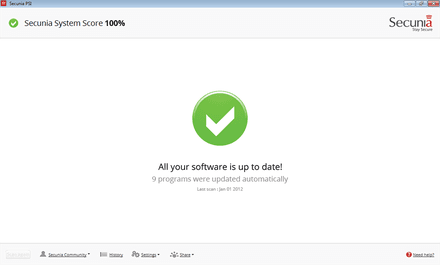
Résumé :
Tutoriel et site éditeur
____________________________________________________________
Malwarebytes
Nouvelle version
Toujours gratuite !
Toujours simple d'utilisation
Téléchargement >> Malwarebytes
ou bien mirroir
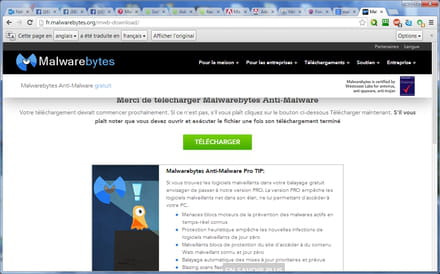
Il faut maintenant ouvrir le fichier , clic droit bien évidement :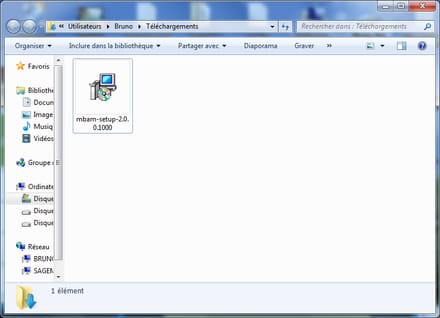
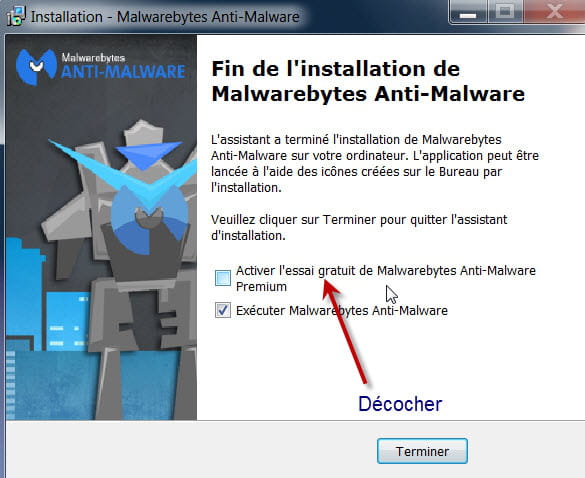
Instalation simple, choisir sa langue et se laisser guider ne pas oublier de décocher Activer l'essai gratuit de Malwarebytes Anti-Malware Premium
Au premier démarrage de Malwarebytes Anti-Malware, une popup en bas à droite vous informe que les définitions virales ne sont pas à jour.
- 1 Cliquez dessus
- 2 Puis cliquez sur Examen en haut.
- 3 Le scan se lance et les objets détectés sont énumérés, une fois le scan terminé, la liste des menaces apparaît.
- 4 Choisir mettre en quarantaine puis aller dans l'onglet quarantaine pour tout supprimer
Il est possible que Malwarebytes demande de redémarrer l'ordinateur, acceptez en cliquant sur Yes.
l'onglet Historique permet de retrouver les rapports afin de les poster sur le forum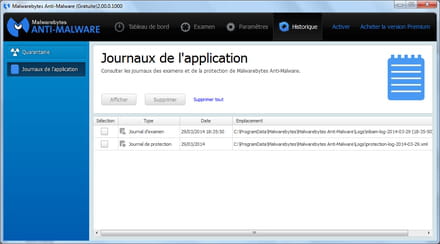
Á la deuxième utilisation (et les suivantes)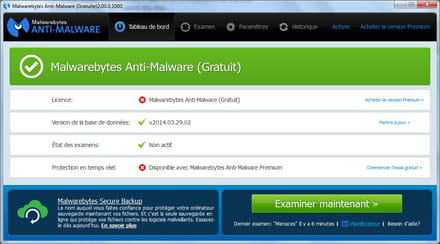
Cliquer sur l'onglet Examen , il faut que soit coché examen menaces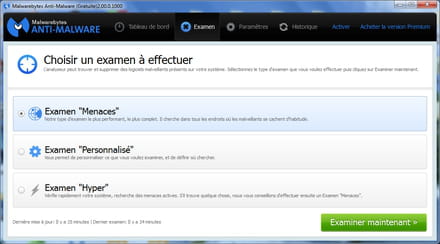
puis examiner maintenant
si rapport demandé , le poster sur le forum
_____________________________________________
SXGU de igor 51
Téléchargement
Compatible : Windows XP (32 / 64 bit), Vista (32 / 64 bit), 2008, Windows 7 (32 / 64 bit)
Utilisateur d'AVAST : Il vous faut désactiver les agents de protections le temps de l'exécution.
Désactiver l'Agent WEB pour que l'outil puisse correctement fonctionner.
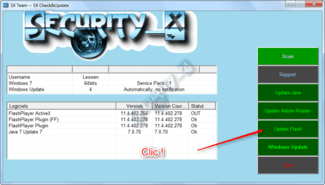
Au menu principal, choisir l'option Rapport.
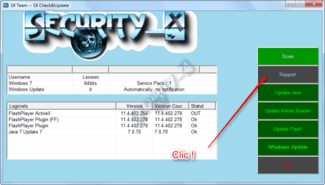
Le rapport indique que Flash player pour Internet Explorer (ActiveX) n'est pas à jour, il suffit de cliquer sur le bouton Update Flash pour lancer la mise à jour au travers du navigateur concerné.
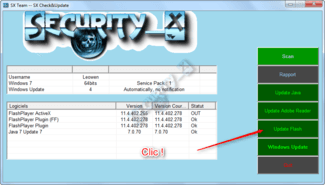
Le programme vous ouvre le navigateur concerné instantanément sur la page de téléchargement de la mise à jour qui fait défaut
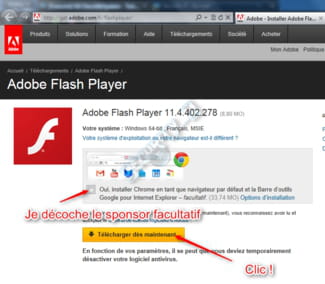
A noter que vous pouvez visualiser instantanément les mises à jour à faire sans lancer de rapport comme sur cette image:
ssouligne>Information complémentaire : </souligne>
Maintenir Java, Adobe Reader et Flash Player à jour :
https://www.malekal.com/maintenir-java-adobe-reader-et-le-player-flash-a-jour/
Et aussi :
Comment éviter les fausses mises à jour
_______________________________________________________________________________________________________________D'autre liens TRÈS utiles Pour les mises à jour :
Java
Adobe reader
Flash player
Update checker
Delfix
Ccleaner
Unchecky
Comodo
________________________________________________________________________________________________________________
4/ Maintenant je te propose un peu de lecture !
1 - Conserve MBAM. Il te servira à scanner les fichiers douteux en complément de l'antivirus et scanne le disque dur régulièrement. Mais n'oublie pas de faire la mise à jour avant de lancer le scan.
2 - Installe l'extension de sécurité adblock plus pour bloquer les publicités : AdBlock_Plus
3 - Extension pour ton navigateur internet : WOT
Voici une extension à télécharger qui te permettra, en faisant tes recherches sur google, de savoir si le site proposé lors de tes recherches est un site de confiance ou un site à éviter car il pourrait infecter ton PC :
Pour Firefox : WOT Firefox
Pour internet explorer: WOT_IE
4 - Ci-dessous un tutoriel pour t'aider à installer WOT:
tuto_WOT
Un lien utile et important : Mettre à jours son PC contre les failles de sécurité.
5/ - Tu peux lire ce sujet sur les logiciels recommandés :
logiciels_recommandés
6/- Et celui ci, sur les logiciels gratuits à éviter :
logiciels à éviter
7/- Et ce dossier sur la prévention et protection:
prévention_protection
8/ - Si tu utilise FireFox, vérifie que tes plugin sont à jour :
plugin
9/ Pourquoi les P2P sont nocifs :
Tout savoir sur les P2P , merci Malekal
et http://www.malwareteks.com/articles/MalwareSources.php
10/ - Reconnaitre les PUPS
PUPS
11/ Pour ne plus se faire avoir, A lire :
Programmes parasites / PUPs
12/ - Enfin les Toolbars c'est pas obligatoire
Toolbars
13/ - La sécurité de son PC c'est quoi ?
La sécurité de son PC
14/ - Ne pas avoir plusieurs anti-virus
https://www.commentcamarche.net/faq/8835-installer-plusieurs-antivirus-pour-augmenter-la-securite
15/ - Pour libérer un peu d'espace sur ton disque
http://www.malekal.com/2011/09/04/comment-liberer-de-lespace-disque/
16/ - Pense à marquer le fil comme résolu !
comme ceci
- Sois plus vigilant(e) sur Internet à l'avenir !
Voilà pour moi c'est terminé.
Si tu as des questions n'hésite pas.
-
Contributeurdeux nouveaux trucs donc tu vas repasser ce script et me refaire un ZHPDiag après ...Merci !
ZHPFix Script
ATTENTION !!! : Script personnalisé pour cette machine uniquement , ne pas reproduire !!
/!\ Double Avertissement /!\
.
Ce script est seulement valable pour ce pc, en cours de nettoyage, à ne pas utiliser sur un autre pc,
risque de plantage !
Ce script va cibler certains éléments à supprimer :- Copie les lignes suivantes (surligner et copier) :
Script ZHPFix
ShortcutFix
[MD5.E8B7FD67DA14A7BE57A5CB80E3139E60] - (.Google Inc. - Google Toolbar Broker.) -- C:\Program Files\Google\Google Toolbar\GoogleToolbarUser_32.exe [309704] [PID.10124]
R3 - URLSearchHook: (no name) - {5bcf818d-78c8-41b8-ba89-65c5fdac4fc4} . (.Adobe Systems Inc. - Adobe PDF Plug-In For Firefox and Netscape 11.0.10.) (No version) -- (.not file.) => Fichier absent
O2 - BHO: Google Toolbar Helper - {AA58ED58-01DD-4d91-8333-CF10577473F7} . (.Google Inc. - Google Toolbar.) -- C:\Program Files\Google\Google Toolbar\GoogleToolbar_32.dll
O3 - Toolbar: Google Toolbar - [HKLM]{2318C2B1-4965-11d4-9B18-009027A5CD4F} . (.Google Inc. - Google Toolbar.) -- C:\Program Files\Google\Google Toolbar\GoogleToolbar_32.dll
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{2318C2B1-4965-11D4-9B18-009027A5CD4F} Clé orpheline => Toolbar.Google
O42 - Logiciel: Google Toolbar for Internet Explorer - (.Google Inc..) [HKLM] -- {18455581-E099-4BA8-BC6B-F34B2F06600C} => Toolbar.Google
O42 - Logiciel: Google Toolbar for Internet Explorer - (.Google Inc..) [HKLM] -- {2318C2B1-4965-11d4-9B18-009027A5CD4F} => Toolbar.Google
[MD5.13706B903F8226B56C64BD7AC029AC74] [SPRF][27/09/2012] (...) -- C:\Users\remy\Desktop\WordBiz18.exe [7796392]
[HKLM\Software\Classes\protector_dll.protectorbho.1] =>PUP.BProtector
[HKLM\Software\Classes\protector_dll.protectorbho] =>PUP.BProtector
ProxyFix
EmptyPrefetch
EmptyFlash
SysRestore
FirewallRAZ
EmptyTemp
- Lance ZHPFix à partir du raccourci sur ton Bureau (si tu es sous Windows Vista ou Windows 7, fais le par un clic-droit --> Exécuter en temps qu'administrateur)
- Clique sur Importer, (vérifie) .Les lignes se collent automatiquement dans ZHPFix, sinon colle les lignes
- Avant toute opération, ZHPFix vide la corbeille cela peut durer jusqu'à plusieurs minutes (mais tu peux dire non )
- Clique sur le bouton « GO » pour lancer le nettoyage.
- Copie/colle la totalité du rapport dans ta prochaine réponse.
- Un redémarrage est nécessaire .....
Tutoriels Tutoriels officiels
-
Rapport de ZHPFix 2015.2.17.3 par Nicolas Coolman, Update du 17/02/2015
Fichier d'export Registre :
Run by remy at 28/02/2015 12:52:58
High Elevated Privileges : OK
Windows 7 Ultimate Edition, 32-bit Service Pack 1 (Build 7601)
Corbeille vidée (00mn 03s)
Dossier Prefetcher vidé
Réparation des raccourcis navigateur
========== Logiciels ==========
SUPPRIMÉ: Google Toolbar for Internet Explorer
========== Clés du Registre ==========
SUPPRIMÉ: [HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{18455581-E099-4BA8-BC6B-F34B2F06600C}]
========== Valeurs du Registre ==========
SUPPRIMÉ: URLSearchHook: {5bcf818d-78c8-41b8-ba89-65c5fdac4fc4}
SUPPRIMÉ: Toolbar: {2318C2B1-4965-11D4-9B18-009027A5CD4F}
ProxyFix : Configuration proxy supprimée avec succès
SUPPRIMÉ ProxyServer Value
SUPPRIMÉ ProxyEnable Value
SUPPRIMÉ EnableHttp1_1 Value
SUPPRIMÉ ProxyHttp1.1 Value
SUPPRIMÉ ProxyOverride Value
Aucune Valeur Standard Profile: FirewallRaz :
Aucune Valeur Domain Profile: FirewallRaz :
========== Dossiers ==========
SUPPRIMÉS Flash Cookies (0)
SUPPRIMÉS Temporaires Windows (4)
========== Fichiers ==========
SUPPRIMÉS Flash Cookies (0) (0 octets)
SUPPRIMÉS Temporaires Windows (8) (1 126 921 octets)
========== Restauration Système ==========
Point de restauration du système créé avec succès
========== Récapitulatif ==========
1 : Clés du Registre
10 : Valeurs du Registre
2 : Dossiers
2 : Fichiers
1 : Logiciels
1 : Restauration Système
End of clean in 00mn 40s
========== Chemin de fichier rapport ==========
C:\Users\remy\AppData\Roaming\ZHP\ZHPFix[R1].txt - 28/02/2015 07:10:40 [3705]
C:\Users\remy\AppData\Roaming\ZHP\ZHPFix[R2].txt - 28/02/2015 12:53:02 [1664] -
http://cjoint.com/?3BCnlTCkCfA
et voilà ! par contre lorsque je veux regarder une vidéo sur n'importe quel site, j'ai une petite fenêtre qui s'ouvre systématiquement et me met "Paramètres Adobe Flash Player - stockage local - le nom du site demande la permission d'enregistrer des informations sur votre ordinateurs - autoriser ou refuser" -
ContributeurRefuser !
Pour Flash Player :
- Flash Player (vérification)
- Instalation (choisir sa version)
IMPORTANT : Ne prendre des téléchargements QUE sur le site Editeur
Et aussi :
Comment éviter les fausses mises à jour
-
ContributeurBonjour,
Flash Player toujours pas à jour : Adobe Flash Player 11 Plugin => Adobe Systems
Mise à jour :Pour Flash Player :
- Flash Player (vérification)
- Instalation (choisir sa version)
IMPORTANT : Ne prendre des téléchargements QUE sur le site Editeur
Et aussi :
Comment éviter les fausses mises à jour
Nouveau script depuis hier :
ZHPFix Script
ATTENTION !!! : Script personnalisé pour cette machine uniquement , ne pas reproduire !!
/!\ Double Avertissement /!\
.
Ce script est seulement valable pour ce pc, en cours de nettoyage, à ne pas utiliser sur un autre pc,
risque de plantage !
Ce script va cibler certains éléments à supprimer :- Copie les lignes suivantes (surligner et copier) :
Script ZHPFix
ShortcutFix
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyHttp1.1 = 0 => Internet Explorer Proxy GET HTTP1.1 Disabled
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{71576546-354D-41C9-AAE8-31F2EC22BF0D} Clé orpheline => WOT Web Of Trust / PUP.BearShare
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{56444A2D-5637-006A-76A7-7A786E7484D7} Clé orpheline => Orphean Key not necessary
O23 - Service: SystemSafeguard (f6082713) . (...) - c:\Program Files\SystemSafeguard\SystemSafeguard.dll (.not file.) => Fichier absent
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderDownloaderScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (...) -- C:\Program Files\RealNetworks\RealDownloader\recordingmanager.exe (.not file.) [0] => RealNetworks Inc - RealDownloader
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderRealUpgradeLogonTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (...) -- C:\Program Files\RealNetworks\RealDownloader\realupgrade.exe (.not file.) [0] => RealNetworks Inc - RealDownloader
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderRealUpgradeScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (...) -- C:\Program Files\RealNetworks\RealDownloader\realupgrade.exe (.not file.) [0] => RealNetworks Inc - RealDownloader
O42 - Logiciel: Adobe Flash Player 11 Plugin - (.Adobe Systems Incorporated.) [HKLM] -- Adobe Flash Player Plugin => Adobe Systems
[HKCU\Software\Reg]
[HKLM\Software\Reg]
O43 - CFD: 07/12/2011 - 19:43:02 - [] ----D C:\ProgramData\XsRXTfiwSUdn
O43 - CFD: 26/02/2015 - 23:08:26 - [] ----D C:\ProgramData\{4896dc69-39e0-8578-4896-6dc6939e71a4}
O43 - CFD: 26/02/2015 - 23:10:00 - [] ----D C:\ProgramData\{89c85052-2a23-cc44-89c8-850522a24148}
O43 - CFD: 03/06/2013 - 05:55:23 - [] -SH-D C:\ProgramData\{C4ABDBC8-1C81-42C9-BFFC-4A68511E9E4F} => Toolbar.TuneUp
O43 - CFD: 07/12/2011 - 19:43:06 - [] ----D C:\Users\remy\AppData\Roaming\lJQXCOOdhkcB
O43 - CFD: 26/02/2015 - 22:17:50 - [] ----D C:\Users\remy\AppData\Roaming\uTorrent =>P2P.µTorrent
O43 - CFD: 03/01/2012 - 21:05:21 - [] ----D C:\Users\remy\AppData\Local\Apps => PUP.Mysoftpack
O45 - LFCP:[MD5.336CDEA0FA9807EBE880711EBDE8BBE4] - 26/02/2015 - 22:17:48 ---A- - C:\Windows\Prefetch\UTORRENT.EXE-46818A54.pf =>P2P.µTorrent
O51 - MPSK:{7acffa7f-1681-11e4-9979-001a4d804024}\AutoRun\command. (...) -- H:\HTC_Sync_Manager_PC.exe (.not file.) => Fichier absent
O51 - MPSK:{86c00077-82a2-11e4-85e8-001a4d804024}\AutoRun\command. (...) -- G:\HTC_Sync_Manager_PC.exe (.not file.) => Fichier absent
O51 - MPSK:{86c00086-82a2-11e4-85e8-001a4d804024}\AutoRun\command. (...) -- G:\HTC_Sync_Manager_PC.exe (.not file.) => Fichier absent
O51 - MPSK:{da063d2c-370a-11e4-840e-001a4d804024}\AutoRun\command. (...) -- I:\HTC_Sync_Manager_PC.exe (.not file.) => Fichier absent
O51 - MPSK:{f084c7e1-abc8-11e4-b648-001a4d804024}\AutoRun\command. (...) -- G:\HTC_Sync_Manager_PC.exe (.not file.) => Fichier absent
O68 - StartMenuInternet: <FIREFOX.EXE> <Mozilla Firefox>[HKLM\..\Shell\open\Command] (...) -- firefox.exe (.not file.) => Fichier absent
[MD5.13706B903F8226B56C64BD7AC029AC74] [SPRF][27/09/2012] (...) -- C:\Users\remy\Desktop\WordBiz18.exe [7796392]
SS - | Auto 22/07/1658 0 | (f6082713) . (...) - c:\Program Files\SystemSafeguard\SystemSafeguard.dll
C:\Users\remy\AppData\Roaming\uTorrent =>P2P.µTorrent^
ProxyFix
EmptyPrefetch
EmptyFlash
SysRestore
FirewallRAZ
EmptyTemp
- Lance ZHPFix à partir du raccourci sur ton Bureau (si tu es sous Windows Vista ou Windows 7, fais le par un clic-droit --> Exécuter en temps qu'administrateur)
- Clique sur Importer, (vérifie) .Les lignes se collent automatiquement dans ZHPFix, sinon colle les lignes
- Avant toute opération, ZHPFix vide la corbeille cela peut durer jusqu'à plusieurs minutes (mais tu peux dire non )
- Clique sur le bouton « GO » pour lancer le nettoyage.
- Copie/colle la totalité du rapport dans ta prochaine réponse.
- Un redémarrage est nécessaire .....
Tutoriels Tutoriels officiels
Et un nouveau ZHPDiag de vérification merci !-
Rapport de ZHPFix 2015.2.17.3 par Nicolas Coolman, Update du 17/02/2015
Fichier d'export Registre :
Run by remy at 28/02/2015 07:10:36
High Elevated Privileges : OK
Windows 7 Ultimate Edition, 32-bit Service Pack 1 (Build 7601)
Corbeille vidée (00mn 04s)
Dossier Prefetcher vidé
Réparation des raccourcis navigateur
========== Clés du Registre ==========
SUPPRIMÉ: [HKLM\SOFTWARE\Classes\CLSID\{71576546-354D-41C9-AAE8-31F2EC22BF0D}]
SUPPRIMÉ: Service: f6082713
SUPPRIMÉ: HKCU\Software\Reg
SUPPRIMÉ: HKLM\Software\Reg
SUPPRIMÉ CLSID MPSK: {7acffa7f-1681-11e4-9979-001a4d804024}
SUPPRIMÉ CLSID MPSK: {86c00077-82a2-11e4-85e8-001a4d804024}
SUPPRIMÉ CLSID MPSK: {86c00086-82a2-11e4-85e8-001a4d804024}
SUPPRIMÉ CLSID MPSK: {da063d2c-370a-11e4-840e-001a4d804024}
SUPPRIMÉ CLSID MPSK: {f084c7e1-abc8-11e4-b648-001a4d804024}
========== Valeurs du Registre ==========
SUPPRIMÉ: Toolbar: {71576546-354D-41C9-AAE8-31F2EC22BF0D}
SUPPRIMÉ: Toolbar: {56444A2D-5637-006A-76A7-7A786E7484D7}
ProxyFix : Configuration proxy supprimée avec succès
SUPPRIMÉ ProxyServer Value
SUPPRIMÉ ProxyEnable Value
SUPPRIMÉ EnableHttp1_1 Value
SUPPRIMÉ ProxyHttp1.1 Value
SUPPRIMÉ ProxyOverride Value
Aucune Valeur Standard Profile: FirewallRaz :
Aucune Valeur Domain Profile: FirewallRaz :
SUPPRIMÉ: FirewallRaz (Public) : TCP Query User{56B1897F-C3C7-49BF-96D3-BDE3B6DC1160}C:\program files\real\realplayer\realplay.exe
SUPPRIMÉ: FirewallRaz (Public) : UDP Query User{66DAB585-3576-427C-8E47-AC77BC997FF2}C:\program files\real\realplayer\realplay.exe
SUPPRIMÉ: FirewallRaz (Private) : TCP Query User{BD45DF53-2B7B-4496-AA2E-FF62F86AA19F}C:\users\remy\appdata\roaming\cacaoweb\cacaoweb.exe
SUPPRIMÉ: FirewallRaz (Private) : UDP Query User{F380DF53-098A-431F-8B82-552938853235}C:\users\remy\appdata\roaming\cacaoweb\cacaoweb.exe
SUPPRIMÉ: FirewallRaz (Public) : TCP Query User{628AA8C8-7F5E-45F2-B5AB-B31CA616DBCC}C:\users\remy\appdata\roaming\cacaoweb\cacaoweb.exe
SUPPRIMÉ: FirewallRaz (Public) : UDP Query User{87BE7248-5E94-4BFC-9B88-965420E14F4F}C:\users\remy\appdata\roaming\cacaoweb\cacaoweb.exe
========== Eléments de donnée du Registre ==========
SUPPRIMÉ: R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyHttp1.1
SUPPRIMÉ: StartMenuInternet: firefox.exe
========== Dossiers ==========
SUPPRIMÉ: C:\ProgramData\XsRXTfiwSUdn
SUPPRIMÉ: C:\ProgramData\{4896dc69-39e0-8578-4896-6dc6939e71a4}
SUPPRIMÉ: C:\ProgramData\{89c85052-2a23-cc44-89c8-850522a24148}
SUPPRIMÉ: C:\ProgramData\{C4ABDBC8-1C81-42C9-BFFC-4A68511E9E4F}
SUPPRIMÉ: C:\Users\remy\AppData\Roaming\lJQXCOOdhkcB
SUPPRIMÉ: C:\Users\remy\AppData\Roaming\uTorrent
SUPPRIMÉ: C:\Users\remy\AppData\Local\Apps
SUPPRIMÉS Flash Cookies (0)
SUPPRIMÉS Temporaires Windows (153)
========== Fichiers ==========
SUPPRIMÉS Flash Cookies (0) (0 octets)
SUPPRIMÉS Temporaires Windows (801) (1 937 512 901 octets)
========== Tache planifiée ==========
SUPPRIMÉ: RealDownloaderDownloaderScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000
SUPPRIMÉ: RealDownloaderRealUpgradeLogonTaskS-1-5-21-1214120938-4103684180-1072874238-1000
SUPPRIMÉ: RealDownloaderRealUpgradeScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000
========== Restauration Système ==========
Point de restauration du système créé avec succèsil -
-
ContributeurOK
Supprime : P2P.BitTorrent
Et tu passes Adwcleaner, JRT et Malwarebytes ensuite tu me refais un ZHPDiag s'il te plait !
AdwCleaner
: Logiciel très simple d'utilisation
1 - Téléchargez AdwCleaner et lance son exécution.
>>>ICI<<< Alternatif
2 - L'interface du programme va s'ouvrir.
Cliques sur le bouton Scanner afin de lancer la détection, celle-ci ne prendra que quelques secondes, patientes.
Le rapport est automatiquement enregistré à la racine de votre disque dur principal, en général C:
3 - Fermes le rapport puis cliques sur le bouton NettoyerSI
AdwCleaner a trouvé des choses dans les différents onglets
4 - Dès la suppression effective, le logiciel demande de redémarrer l'ordinateur, cliques sur Ok.
au redémarrage :
5 - Poste les deux rapports , recherche et suppression
(CTRL+A Pour tout sélectionner , CTRL+C pour copier et CTRL+V pour coller)
6 - Tu peux fermer AdwCleaner
___________________________________________JRT

Téléchargement : JRT
1 - Enregistre-le sur ton bureau.
2 - Fermes toutes les applications en cours.
3 - Fais un clic droit => Exécuter en tant qu'administrateur
4 - Une fois le logiciel ouvert, appuis sur la touche Entrée.
5 - Patientes le temps que l'outil travaille (cela peut être assez long)
6 - le bureau va disparaître quelques instants, c'est tout à fait normal.
À la fin de l'analyse, un rapport nommé JRT.txt va s'ouvrir
Il va falloir que tu patientes ne touche à rien même si tu as l'impression que cela n'avance pas !
Poste le rapport
ne t'inquiète pas si tu as l'impression qu'il ne "travaille" pas !!
patiente !
_________________________________________
Malwarebytes
Nouvelle version
Toujours gratuite !
Toujours simple d'utilisation
Téléchargement >> Malwarebytes
ou bien mirroir
Il faut maintenant ouvrir le fichier , clic droit bien évidement :
Instalation simple, choisir sa langue et se laisser guider
A la fin de l'installation, décoche l'option "Activer l'essai gratuit de Malwarebytes Anti-Malware Premium".
La case Exécuter Malwarebytes Anti-Malware reste cochée.
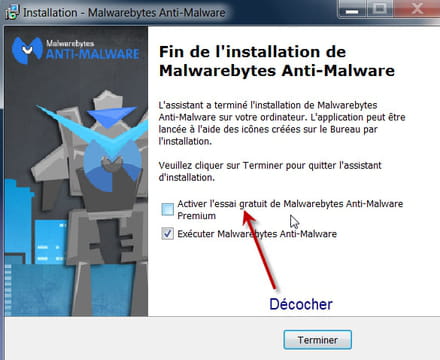
Au premier démarrage de Malwarebytes Anti-Malware, une popup en bas à droite vous informe que les définitions virales ne sont pas à jour.
- 1 Cliquez dessus mettre à jour maintenant
- 2 Puis cliquez sur Examen en haut.
- 3 Le scan se lance et les objets détectés sont énumérés, une fois le scan terminé, la liste des menaces apparaît.
- 4 Choisir mettre en quarantaine puis aller dans l'onglet quarantaine pour tout supprimer
Il est possible que Malwarebytes demande de redémarrer l'ordinateur, acceptez en cliquant sur Yes.
l'onglet Historique permet de retrouver les rapports afin de les poster sur le forum
Á la deuxième utilisation (et les suivantes)
Cliquer sur l'onglet Examen , il faut que soit coché examen menaces
puis examiner maintenant
si rapport demandé , le poster sur le forum
Après redémarrage me refaire un ZHPDiag s'il te plait !
-
-
# AdwCleaner v4.111 - Rapport créé le 26/02/2015 à 22:21:19
# Mis à jour le 18/02/2015 par Xplode
# Base de données : 2015-02-18.3 [Serveur]
# Système d'exploitation : Windows 7 Ultimate Service Pack 1 (x86)
# Nom d'utilisateur : remy - REMY-PC
# Exécuté depuis : C:\Users\remy\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\N4LWF4GH\adwcleaner_4.111.exe
# Option : Nettoyer- [ Services ] *****
- [ Fichiers / Dossiers ] *****
- [ Tâches planifiées ] *****
- [ Raccourcis ] *****
- [ Registre ] *****
Clé Supprimée : HKLM\SOFTWARE\{12A61307-94CD-4F8E-94BC-918E511FAA81}- [ Navigateurs ] *****
-\\ Internet Explorer v11.0.9600.17631
-\\ Mozilla Firefox v23.0 (fr)
-\\ Google Chrome v40.0.2214.115
AdwCleaner[R0].txt - [26330 octets] - [26/02/2015 18:53:53]
AdwCleaner[R1].txt - [1077 octets] - [26/02/2015 22:18:24]
AdwCleaner[S0].txt - [0 octets] - [26/02/2015 18:58:39]
AdwCleaner[S1].txt - [1004 octets] - [26/02/2015 22:21:19]
########## EOF - C:\AdwCleaner\AdwCleaner[S1].txt - [1064 octets] ########## -
2e rapport JKT :
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~
Junkware Removal Tool (JRT) by Thisisu
Version: 6.4.2 (02.02.2015:1)
OS: Windows 7 Ultimate x86
Ran by remy on 26/02/2015 at 22:30:17,5
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~
~~~ Services
~~~ Registry Values
~~~ Registry Keys
~~~ Files
~~~ Folders
~~~ FireFox
Successfully deleted: [Folder] C:\Users\remy\AppData\Roaming\mozilla\firefox\profiles\2tefea1k.default\extensions\staged
Successfully deleted the following from C:\Users\remy\AppData\Roaming\mozilla\firefox\profiles\2tefea1k.default\prefs.js
user_pref("valueApps.autoDisableScopes", -1);
~~~ Event Viewer Logs were cleared
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~
Scan was completed on 26/02/2015 at 22:32:42,57
End of JRT log
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~ -
-
@buckhulk~ Rapport de ZHPDiag v2015.2.23.23 - Nicolas Coolman (23/02/2015)
~ Lancé par remy (26/02/2015 23:13:13)
~ Facebook : https://www.facebook.com/nicolascoolman1
~ Adresse du Forum http://forum.nicolascoolman.fr
~ Traduit par Nicolas Coolman
~ Etat de la version : Version à jour.
~ Liste blanche : Désactivée par l'utilisateur
~ Elévation des Privilèges : OK
~ User Account Control (UAC): Activate by user
---\\ Navigateurs Internet
MSIE: Internet Explorer v11.0.9600.17633 (Defaut)
MFIE: Mozilla Firefox 23.0
GCIE: Google Chrome v40.0.2214.115
---\\ Informations sur les produits Windows
~ Langage: Français
Windows Server License Manager Script : OK
~ Windows Operating System - Windows(R) 7, OEM_SLP channel
System Locked Preinstallation (OEM_SLP) : OK
Windows ID Activation : OK
~ Windows Partial Key : HYRR2
Windows License : OK
~ Windows Remaining Initializations Number : 4
Software Protection Service (Protection logicielle) : OK
Windows Automatic Updates : OK
Windows Activation Technologies : OK
Windows 7 Ultimate, 32-bit Service Pack 1 (Build 7601)
---\\ Logiciels de protection du système
Malwarebytes Anti-Malware version 2.0.4.1028
Microsoft Security Client v4.7.0205.0
Windows Defender W7 (Deactivate)
---\\ Logiciels d'optimisation du système
CCleaner v4.02
---\\ Logiciels de partage PeerToPeer
---\\ Surveillance de Logiciels
Adobe Flash Player 11 Plugin
Adobe Reader XI
---\\ Informations sur le système
~ Processor: x86 Family 15 Model 75 Stepping 2, AuthenticAMD
~ Operating System: 32 Bits
Boot mode: Normal (Normal boot)
Total RAM: 1983 MB (58% free)
System Restore: Activé (Enable)
System drive C: has 69 GB (50%) free of 136 GB
---\\ Mode de connexion au système
~ Computer Name: REMY-PC
~ User Name: remy
~ All Users Names: UpdatusUser, remy, HomeGroupUser$, Administrateur,
~ Unselected Option: None
Logged in as Administrator
---\\ Variables d'environnement
~ System Unit : C:\
~ %AppZHP% : C:\Users\remy\AppData\Roaming\ZHP\
~ %AppData% : C:\Users\remy\AppData\Roaming\
~ %Desktop% : C:\Users\remy\Desktop\
~ %Favorites% : C:\Users\remy\Favorites\
~ %LocalAppData% : C:\Users\remy\AppData\Local\
~ %StartMenu% : C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\
~ %Windir% : C:\Windows\
~ %System% : C:\Windows\System32\
---\\ Enumération des unités disques
A: Floppy drive, Flash card reader, USB Key (Not Inserted)
B: Hard drive, Flash drive, Thumb drive (Free 70 Go of 98 Go)
C: Hard drive, Flash drive, Thumb drive (Free 69 Go of 136 Go)
D: CD-ROM drive (Not Inserted)
E: Hard drive, Flash drive, Thumb drive (Free 35 Go of 59 Go)
F: Hard drive, Flash drive, Thumb drive (Free 47 Go of 94 Go)
H: Hard drive, Flash drive, Thumb drive (Free 506 Go of 932 Go)
J: Floppy drive, Flash card reader, USB Key (Not Inserted)
K: Floppy drive, Flash card reader, USB Key (Not Inserted)
L: Floppy drive, Flash card reader, USB Key (Not Inserted)
M: Floppy drive, Flash card reader, USB Key (Not Inserted)
---\\ Etat du Centre de Sécurité Windows
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiSpywareOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiVirusOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] FirewallOverride: OK
[HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System] DisableTaskMgr: OK
[HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System] DisableRegistryTools: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\system] EnableLUA: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\NOHIDDEN] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\SHOWALL] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Associations] Application: OK
[HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon] Shell: OK
[HKCU\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows] Load: OK
[HKLM\SYSTEM\CurrentControlSet\Services\COMSysApp] Type: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install] LastSuccessTime : OK
~ Security Center: 41 Scanned in 00mn 00s
---\\ Recherche particulière de fichiers génériques
[MD5.8B88EBBB05A0E56B7DCC708498C02B3E] - (.Microsoft Corporation - Explorateur Windows.) (.25/02/2011 - 06:30:54.) -- C:\Windows\Explorer.exe [2616320]
[MD5.B5C5DCAD3899512020D135600129D665] - (.Microsoft Corporation - Application de démarrage de Windows.) (.14/07/2009 - 02:14:45.) -- C:\Windows\System32\Wininit.exe [96256]
[MD5.F285D499EC42969D963CA49EADA63218] - (.Microsoft Corporation - Extensions Internet pour Win32.) (.12/01/2015 - 02:00:17.) -- C:\Windows\System32\wininet.dll [1888256]
[MD5.52449FD429D6053B78AE564DEF303870] - (.Microsoft Corporation - Application d'ouverture de session Windows.) (.17/07/2014 - 02:39:27.) -- C:\Windows\System32\Winlogon.exe [304128]
[MD5.E3AE23569749DE12D45BA3B489A036AE] - (.Microsoft Corporation - Bibliothèque de licences.) (.20/11/2010 - 13:21:24.) -- C:\Windows\System32\sppcomapi.dll [193536]
[MD5.D0B388DA1D111A34366E04EB4A5DD156] - (.Microsoft Corporation - Ancillary Function Driver for WinSock.) (.30/05/2014 - 07:36:07.) -- C:\Windows\system32\Drivers\AFD.sys [338944]
[MD5.338C86357871C167A96AB976519BF59E] - (.Microsoft Corporation - ATAPI IDE Miniport Driver.) (.14/07/2009 - 02:26:15.) -- C:\Windows\system32\Drivers\atapi.sys [21584]
[MD5.77EA11B065E0A8AB902D78145CA51E10] - (.Microsoft Corporation - CD-ROM File System Driver.) (.14/07/2009 - 00:11:15.) -- C:\Windows\system32\Drivers\Cdfs.sys [70656]
[MD5.BE167ED0FDB9C1FA1133953C18D5A6C9] - (.Microsoft Corporation - SCSI CD-ROM Driver.) (.20/11/2010 - 09:38:10.) -- C:\Windows\system32\Drivers\Cdrom.sys [108544]
[MD5.F024449C97EC1E464AAFFDA18593DB88] - (.Microsoft Corporation - DFS Namespace Client Driver.) (.20/11/2010 - 09:42:32.) -- C:\Windows\system32\Drivers\DfsC.sys [78336]
[MD5.9036377B8A6C15DC2EEC53E489D159B5] - (.Microsoft Corporation - High Definition Audio Bus Driver.) (.20/11/2010 - 10:59:29.) -- C:\Windows\system32\Drivers\HDAudBus.sys [108544]
[MD5.F151F0BDC47F4A28B1B20A0818EA36D6] - (.Microsoft Corporation - Pilote de port i8042.) (.14/07/2009 - 00:11:24.) -- C:\Windows\system32\Drivers\i8042prt.sys [80896]
[MD5.A5FA468D67ABCDAA36264E463A7BB0CD] - (.Microsoft Corporation - IP Network Address Translator.) (.14/07/2009 - 00:54:29.) -- C:\Windows\system32\Drivers\IpNat.sys [101888]
[MD5.5D16C921E3671636C0EBA3BBAAC5FD25] - (.Microsoft Corporation - Windows NT SMB Minirdr.) (.27/04/2011 - 03:17:22.) -- C:\Windows\system32\Drivers\MRxSmb.sys [123904]
[MD5.280122DDCF04B378EDD1AD54D71C1E54] - (.Microsoft Corporation - MBT Transport driver.) (.20/11/2010 - 09:39:44.) -- C:\Windows\system32\Drivers\netBT.sys [187904]
[MD5.C8DFF8D07755A66C7A4A738930F0FEAC] - (.Microsoft Corporation - Pilote du système de fichiers NT.) (.24/01/2014 - 03:18:22.) -- C:\Windows\system32\Drivers\ntfs.sys [1212352]
[MD5.2EA877ED5DD9713C5AC74E8EA7348D14] - (.Microsoft Corporation - Pilote de port parallèle.) (.14/07/2009 - 00:45:35.) -- C:\Windows\system32\Drivers\Parport.sys [79360]
[MD5.D9F91EAFEC2815365CBE6D167E4E332A] - (.Microsoft Corporation - RAS L2TP mini-port/call-manager driver.) (.14/07/2009 - 00:54:34.) -- C:\Windows\system32\Drivers\Rasl2tp.sys [78848]
[MD5.B973FCFC50DC1434E1970A146F7E3885] - (.Microsoft Corporation - Microsoft RDP Device redirector.) (.20/11/2010 - 11:24:46.) -- C:\Windows\system32\Drivers\rdpdr.sys [133632]
[MD5.3E21C083B8A01CB70BA1F09303010FCE] - (.Microsoft Corporation - SMB Transport driver.) (.14/07/2009 - 00:53:41.) -- C:\Windows\system32\Drivers\smb.sys [71168]
[MD5.7FE680A3DFA421C4A8E4879AE4C5AAB0] - (.Microsoft Corporation - TDI Translation Driver.) (.11/11/2014 - 02:32:14.) -- C:\Windows\system32\Drivers\tdx.sys [74752]
[MD5.F497F67932C6FA693D7DE2780631CFE7] - (.Microsoft Corporation - Pilote de cliché instantané du volume.) (.20/11/2010 - 13:30:16.) -- C:\Windows\system32\Drivers\volsnap.sys [245632]
~ Generic Processes: Scanned in 00mn 00s
---\\ Etat des fichiers cachés (Caché/Total)
~ Mes images (My Pictures) : 3/15
~ Mes musiques (My Musics) : 8/18
~ Mes Videos (My Videos) : 1/2
~ Mes Favoris (My Favorites) : 1/64
~ Mes Documents (My Documents) : 1/358
~ Mon Bureau (My Desktop) : 1/6959
~ Menu demarrer (Programs) : 1/40
~ Hidden Files: Scanned in 00mn 05s
---\\ Processus lancés
[MD5.28F667911C25649637C0F5AADF660134] - (...) -- C:\Program Files\HTC\HTC Sync Manager\HTC Sync\adb.exe [169312] [PID.2320]
[MD5.B776DFE408E415AA901030C022EEB7DA] - (.NVIDIA Corporation - NVIDIA Settings.) -- C:\Program Files\NVIDIA Corporation\Display\nvtray.exe [1821472] [PID.2520]
[MD5.51138BEEA3E2C21EC44D0932C71762A8] - (...) -- ystem32\rundll32.exe [0] [PID.3068]
[MD5.A2418D3C557C0A0C634DA713A8AC3789] - (.Logitech Inc. - Logitech Webcam Software.) -- C:\Program Files\Logitech\LWS\Webcam Software\LWS.exe [205336] [PID.3180]
[MD5.6E70704C2568ED01CDDF6291F5043763] - (.CANON INC. - Canon My Printer.) -- C:\Program Files\Canon\MyPrinter\BJMYPRT.exe [2569616] [PID.3204]
[MD5.6521891B67EAD77CAFD877D8A24ED769] - (.CANON INC. - Canon Solution Menu EX.) -- C:\Program Files\Canon\Solution Menu EX\CNSEMAIN.exe [1213848] [PID.3220]
[MD5.D3570ACC178180AC0D7C24645461A9D3] - (.CANON INC. - Canon IJ Network Scanner Selector EX.) -- C:\Program Files\Canon\IJ Network Scanner Selector EX\CNMNSST.exe [452016] [PID.3240]
[MD5.550B8CB98A8FA1D7A1A7371055A38DDA] - (...) -- C:\Program Files\Logitech\LWS\Webcam Software\CameraHelperShell.exe [265240] [PID.3260]
[MD5.902054D6B4292329F9594FFF24EE02DB] - (...) -- C:\Program Files\Common Files\Logishrd\LQCVFX\COCIManager.exe [680984] [PID.3496]
[MD5.472D170E4E1FEED584616E08CFB0F1EF] - (.Nicolas Coolman - ZHPDiag.) -- C:\Program Files\ZHPDiag\ZHPDiag.exe [8179200] [PID.2612]
~ Processes Running: Scanned in 00mn 01s
---\\ Mozilla Firefox, Plugins,Demarrage,Recherche,Extensions (P2,M0,M1,M2,M3)
C:\Users\remy\AppData\Roaming\Mozilla\Firefox\Profiles\2tefea1k.default\prefs.js
P2 - FPN: [HKLM] [@adobe.com/FlashPlayer] - (...) -- C:\Windows\system32\Macromed\Flash\NPSWF32_11_4_402_278.dll
P2 - FPN: [HKLM] [@canon.com/EPPEX] - (.CANON INC. - CANON iMAGE GATEWAY Album Plugin Utility Module.) -- C:\Program Files\Canon\Easy-PhotoPrint EX\NPEZFFPI.dll
P2 - FPN: [HKLM] [@Google.com/GoogleEarthPlugin] - (.Google - GEPlugin.) -- C:\Program Files\Google\Google Earth\plugin\npgeplugin.dll =>.Google Inc
P2 - FPN: [HKLM] [@google.com/npPicasa3,version=3.0.0] - (.Google, Inc. - Picasa plugin.) -- C:\Program Files\Google\Picasa3\npPicasa3.dll
P2 - FPN: [HKLM] [@java.com/DTPlugin,version=11.31.2] - (.Oracle Corporation - NPRuntime Script Plug-in Library for Java(TM) Deploy.) -- C:\Program Files\Java\jre1.8.0_31\bin\dtplugin\npDeployJava1.dll
P2 - FPN: [HKLM] [@java.com/JavaPlugin,version=11.31.2] - (.Oracle Corporation - Next Generation Java Plug-in 11.31.2 for Mozilla browsers.) -- C:\Program Files\Java\jre1.8.0_31\bin\plugin2\npjp2.dll
P2 - FPN: [HKLM] [@Microsoft.com/NpCtrl,version=1.0] - (. Microsoft Corporation - 5.1.31211.0.) -- C:\Program Files\Microsoft Silverlight\5.1.31211.0\npctrl.dll
P2 - FPN: [HKLM] [@microsoft.com/WLPG,version=15.4.3502.0922] - (.Microsoft Corporation - NPWLPG.) -- C:\Program Files\Windows Live\Photo Gallery\NPWLPG.dll
P2 - FPN: [HKLM] [@microsoft.com/WLPG,version=15.4.3538.0513] - (.Microsoft Corporation - NPWLPG.) -- C:\Program Files\Windows Live\Photo Gallery\NPWLPG.dll
P2 - FPN: [HKLM] [@microsoft.com/WLPG,version=16.4.3505.0912] - (.Microsoft Corporation - NPWLPG.) -- C:\Program Files\Windows Live\Photo Gallery\NPWLPG.dll
P2 - FPN: [HKLM] [@real.com/nprpchromebrowserrecordext;version=15.0.6.14] - (.RealNetworks, Inc. - RealNetworks(tm) RealPlayer Chrome Background Extension Plug-In.) -- C:\ProgramData\Real\RealPlayer\BrowserRecordPlugin\MozillaPlugins\nprpchromebrowserrecordext.dll
P2 - FPN: [HKLM] [@real.com/nprphtml5videoshim;version=15.0.6.14] - (.RealNetworks, Inc. - RealPlayer(tm) HTML5VideoShim Plug-In.) -- C:\ProgramData\Real\RealPlayer\BrowserRecordPlugin\MozillaPlugins\nprphtml5videoshim.dll
P2 - FPN: [HKLM] [@tools.google.com/Google Update;version=3] - (.Google Inc. - Google Update.) -- C:\Program Files\Google\Update\1.3.26.9\npGoogleUpdate3.dll
P2 - FPN: [HKLM] [@tools.google.com/Google Update;version=9] - (.Google Inc. - Google Update.) -- C:\Program Files\Google\Update\1.3.26.9\npGoogleUpdate3.dll
P2 - FPN: [HKLM] [@videolan.org/vlc,version=2.0.7] - (.VideoLAN - VLC media player Web Plugin 2.1.3.) -- C:\Program Files\VideoLAN\VLC\npvlc.dll =>.VideoLAN
P2 - FPN: [HKLM] [@videolan.org/vlc,version=2.1.3] - (.VideoLAN - VLC media player Web Plugin 2.1.3.) -- C:\Program Files\VideoLAN\VLC\npvlc.dll =>.VideoLAN
P2 - FPN: [HKLM] [@videolan.org/vlc,version=2.1.5] - (.VideoLAN - VLC media player Web Plugin 2.1.3.) -- C:\Program Files\VideoLAN\VLC\npvlc.dll =>.VideoLAN
P2 - FPN: [HKLM] [Adobe Reader] - (.Adobe Systems Inc. - Adobe PDF Plug-In For Firefox and Netscape 11.0.10.) -- C:\Program Files\Adobe\Reader 11.0\Reader\AIR\nppdf32.dll
~ Firefox Browser: 18 Scanned in 00mn 00s
---\\ Internet Explorer, Démarrage,Recherche,URLSearchHook, Phishing (R0,R1,R3,R4)
R0 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://www.google.fr
R0 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://www.google.com
R1 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com
R1 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = http://www.google.com
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = http://www.google.com
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Extensions Off Page = about:noadd-ons
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Security Risk Page = about:securityrisk
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\AboutURLs,Tabs = http://www.google.com
R3 - URLSearchHook: (no name) - {5bcf818d-78c8-41b8-ba89-65c5fdac4fc4} . (.Adobe Systems Inc. - Adobe PDF Plug-In For Firefox and Netscape 11.0.10.) (No version) -- (.not file.)
R3 - URLSearchHook: Microsoft Url Search Hook - {CFBFAE00-17A6-11D0-99CB-00C04FD64497} . (.Adobe Systems Inc. - Adobe PDF Plug-In For Firefox and Netscape 11.0.10.) (No version) -- (.not file.)
R4 - HKLM\SOFTWARE\Microsoft\Internet Explorer\PhishingFilter,EnabledV8 = 1
~ IE Browser: 13 Scanned in 00mn 00s
---\\ Internet Explorer, Proxy Management (R5)
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = no key
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyEnable = 0
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,MigrateProxy = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,EnableHttp1_1 = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyHttp1.1 = 0
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,AutoConfigProxy = wininet.dll
~ Proxy management: Scanned in 00mn 00s
---\\ Analyse des lignes F0, F1, F2, F3 - IniFiles, Autoloading programs
F2 - REG:system.ini: USERINIT=C:\Windows\system32\userinit.exe,
F2 - REG:system.ini: Shell=C:\Windows\explorer.exe
F2 - REG:system.ini: VMApplet=C:\Windows\System32\SystemPropertiesPerformance.exe
~ Keys: Scanned in 00mn 00s
---\\ Hosts file redirection (O1)
~ Le fichier hôte est sain (The hosts file is clean) (21)
~ Hosts File: Scanned in 00mn 00s
---\\ Internet Explorer Toolbars (O3)
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{71576546-354D-41C9-AAE8-31F2EC22BF0D} Clé orpheline
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{56444A2D-5637-006A-76A7-7A786E7484D7} Clé orpheline
~ Toolbar: Scanned in 00mn 00s
---\\ Applications lancées au démarrage du système (O4)
O4 - HKLM\..\Run: [LWS] . (.Logitech Inc. - Logitech Webcam Software.) -- C:\Program Files\Logitech\LWS\Webcam Software\LWS.exe =>.Logitech Inc
O4 - HKLM\..\Run: [CanonMyPrinter] . (.CANON INC. - Canon My Printer.) -- C:\Program Files\Canon\MyPrinter\BJMyPrt.exe
O4 - HKLM\..\Run: [CanonSolutionMenuEx] . (.CANON INC. - Canon Solution Menu EX.) -- C:\Program Files\Canon\Solution Menu EX\CNSEMAIN.exe
O4 - HKLM\..\Run: [IJNetworkScannerSelectorEX] . (.CANON INC. - Canon IJ Network Scanner Selector EX.) -- C:\Program Files\Canon\IJ Network Scanner Selector EX\CNMNSST.exe
O4 - HKLM\..\Run: [MSC] . (.Microsoft Corporation - Microsoft Security Client User Interface.) -- C:\Program Files\Microsoft Security Client\msseces.exe
O4 - HKLM\..\Run: [APSDaemon] C:\Program Files\Common Files\Apple\Apple Application Support\APSDaemon.exe (.not file.)
O4 - HKCU\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files\Windows Sidebar\sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-19\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-19\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-21-1214120938-4103684180-1072874238-1000\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files\Windows Sidebar\sidebar.exe =>.Microsoft Corporation
~ Application: Scanned in 00mn 00s
---\\ Invisibilité de l'icône d'options IE dans le panneau de Configuration (O5)
O5 - control.ini: [HKLM\..\Control Panel] inetcpl.cpl=no
~ IE Control Panel: 1 Scanned in 00mn 00s
---\\ Boutons situés sur la barre d'outils principale d'Internet Explorer (O9)
O9 - Extra button: @C:\Program Files\Windows Live\Writer\WindowsLiveWriterShortcuts.dll,-1003 - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} . (.Microsoft Corporation - Windows Live Writer Blog This Extension.) -- C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} . (...) -- C:\Program Files\Microsoft Office\Office12\REFBARH.ICO
~ IE Extra Buttons: Scanned in 00mn 00s
---\\ Winsock hijacker (Layered Service Provider) (O10)
O10 - WLSP:\000000000001\Winsock LSP File . (.Microsoft Corporation - Network Location Awareness 2.) -- C:\Windows\system32\NLAapi.dll
O10 - WLSP:\000000000002\Winsock LSP File . (.Microsoft Corporation - Fournisseur Shim d'affectation de noms de messagerie.) -- C:\Windows\system32\napinsp.dll
O10 - WLSP:\000000000003\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000004\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000005\Winsock LSP File . (.Microsoft Corporation - Fournisseur de service Sockets 2.0 de Microsoft Windows.) -- C:\Windows\system32\mswsock.dll =>.Microsoft Corporation
O10 - WLSP:\000000000006\Winsock LSP File . (.Microsoft Corporation - LDAP RnR Provider DLL.) -- C:\Windows\system32\winrnr.dll
O10 - WLSP:\000000000007\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
O10 - WLSP:\000000000008\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
~ Winsock: 8 Scanned in 00mn 00s
---\\ Objets ActiveX (Downloaded Program Files)(O16)
O16 - DPF: Garmin Communicator Plug-In (Garmin Communicator Plug-In) - https://static.garmincdn.com/gcp/ie/4.0.3.0/GarminAxControl_32.CAB
O16 - DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} ((no name)) - http://fpdownload2.macromedia.com/get/shockwave/cabs/flash/swflash.cab
~ Objets ActiveX: Scanned in 00mn 00s
---\\ Modification Domaine/Adresses DNS (O17)
O17 - HKLM\System\CCS\Services\Tcpip\..\{AF98B48B-0BAC-418A-8237-AE0AD93B453A}: DhcpNameServer = 192.168.42.129
O17 - HKLM\System\CCS\Services\Tcpip\..\{B71CD3C7-0BF8-462F-8164-2BCFD1421D8E}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CCS\Services\Tcpip\..\{D5894A53-BF97-4ED2-8B89-319AF4A6BF7F}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CS1\Services\Tcpip\..\{AF98B48B-0BAC-418A-8237-AE0AD93B453A}: DhcpNameServer = 192.168.42.129
O17 - HKLM\System\CS1\Services\Tcpip\..\{B71CD3C7-0BF8-462F-8164-2BCFD1421D8E}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CS1\Services\Tcpip\..\{D5894A53-BF97-4ED2-8B89-319AF4A6BF7F}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CS2\Services\Tcpip\..\{AF98B48B-0BAC-418A-8237-AE0AD93B453A}: DhcpNameServer = 192.168.42.129
O17 - HKLM\System\CS2\Services\Tcpip\..\{B71CD3C7-0BF8-462F-8164-2BCFD1421D8E}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CS2\Services\Tcpip\..\{D5894A53-BF97-4ED2-8B89-319AF4A6BF7F}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = 89.2.0.1 89.2.0.2
~ Domain: Scanned in 00mn 00s
---\\ Protocole additionnel (O18)
O18 - Handler: wot - {C2A44D6B-CB9F-4663-88A6-DF2F26E4D952} . (...) -- C:\Program Files\WOT\WOT.dll
O18 - Filter: text/xml - {807563E5-5146-11D5-A672-00B0D022E945} . (.Microsoft Corporation - Microsoft Office XML MIME Filter.) -- C:\Program Files\Common Files\microsoft shared\OFFICE12\MSOXMLMF.dll =>.Microsoft Corporation
~ Protocole Additionnel: Scanned in 00mn 00s
---\\ Clé de Registre autorun ShellServiceObjectDelayLoad (SSO/SSODL) (O21)
O21 - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} - CLSID or File not found.
~ SSODL: 1 Scanned in 00mn 00s
---\\ Liste des services NT non Microsoft et non désactivés (O23)
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) . (.Adobe Systems Incorporated - Adobe Acrobat Update Service.) - C:\Program Files\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: SystemSafeguard (f6082713) . (...) - c:\Program Files\SystemSafeguard\SystemSafeguard.dll (.not file.)
O23 - Service: Service Google Update (gupdate) (gupdate) . (.Google Inc. - Programme d'installation de Google.) - C:\Program Files\Google\Update\GoogleUpdate.exe =>.Google Inc
O23 - Service: HTCMonitorService (HTCMonitorService) . (.Nero AG - NService Application.) - C:\Program Files\HTC\HTC Sync Manager\HSMServiceEntry.exe
O23 - Service: Canon Inkjet Printer/Scanner/Fax Extended Survey Program (IJPLMSVC) . (.Pas de propriétaire - Inkjet Printer/Scanner/Fax Extended Survey.) - C:\Program Files\Canon\IJPLM\IJPLMSVC.exe
O23 - Service: NVIDIA Display Driver Service (nvsvc) . (.NVIDIA Corporation - NVIDIA Driver Helper Service, Version 307.8.) - C:\Windows\system32\nvvsvc.exe
O23 - Service: NVIDIA Update Service Daemon (nvUpdatusService) . (.NVIDIA Corporation - NVIDIA Settings Update Manager.) - C:\Program Files\NVIDIA Corporation\NVIDIA Update Core\daemonu.exe
O23 - Service: Internet Pass-Through Service (PassThru Service) . (.Pas de propriétaire - PassThruSvr Application.) - C:\Program Files\HTC\Internet Pass-Through\PassThruSvr.exe
O23 - Service: Skype Updater (SkypeUpdate) . (.Skype Technologies - Skype Updater Service.) - C:\Program Files\Skype\Updater\Updater.exe
~ Services: 8 Scanned in 00mn 03s
---\\ Enumération Active Desktop & MHTML Editor (O24)
O24 - Default MHTML Editor: Last - .(...) - (.not file.)
~ Desktop Component: 4 Scanned in 00mn 00s
---\\ Enumère les données de BootExecute (BEX) (O34)
O34 - HKLM BootExecute: (autocheck autochk *) - File not found
~ BEX: 1 Scanned in 00mn 00s
---\\ Tâches planifiées en automatique (O39)
[MD5.3E04F1E482357B1FC8B088197C3D9FF8] [APT] [Adobe Acrobat Update Task] (.Adobe Systems Incorporated.) -- C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe [1022152]
[MD5.518545E8CBD79EBF42891A6066578118] [APT] [CCleanerSkipUAC] (.Piriform Ltd.) -- C:\Program Files\CCleaner\CCleaner.exe [3591960]
[MD5.506708142BC63DABA64F2D3AD1DCD5BF] [APT] [GoogleUpdateTaskMachineCore] (.Google Inc..) -- C:\Program Files\Google\Update\GoogleUpdate.exe [116648]
[MD5.506708142BC63DABA64F2D3AD1DCD5BF] [APT] [GoogleUpdateTaskMachineUA] (.Google Inc..) -- C:\Program Files\Google\Update\GoogleUpdate.exe [116648]
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderDownloaderScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (...) -- C:\Program Files\RealNetworks\RealDownloader\recordingmanager.exe (.not file.) [0]
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderRealUpgradeLogonTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (...) -- C:\Program Files\RealNetworks\RealDownloader\realupgrade.exe (.not file.) [0]
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderRealUpgradeScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (...) -- C:\Program Files\RealNetworks\RealDownloader\realupgrade.exe (.not file.) [0]
[MD5.A2530419BF7607A13698A6D07F89550B] [APT] [RealPlayerRealUpgradeLogonTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (.RealNetworks, Inc..) -- C:\Program Files\Real\RealUpgrade\RealUpgrade.exe [141312]
[MD5.A2530419BF7607A13698A6D07F89550B] [APT] [RealPlayerRealUpgradeScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (.RealNetworks, Inc..) -- C:\Program Files\Real\RealUpgrade\RealUpgrade.exe [141312]
[MD5.A2530419BF7607A13698A6D07F89550B] [APT] [RealUpgradeLogonTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (.RealNetworks, Inc..) -- C:\Program Files\Real\RealUpgrade\RealUpgrade.exe [141312]
[MD5.A2530419BF7607A13698A6D07F89550B] [APT] [RealUpgradeScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (.RealNetworks, Inc..) -- C:\Program Files\Real\RealUpgrade\RealUpgrade.exe [141312]
[MD5.8880B530B309F297EE99F3178E60DD5E] [APT] [{FBC97478-91E3-4C60-A558-EBA432C3062A}] (.Atomix Productions.) -- C:\Program Files\VirtualDJ\virtualdj_broadcaster.exe [14499328]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineCore.job [1054]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineCore [1054]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineUA.job [1058]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineUA [1058]
~ Scheduled Task: 15 Scanned in 00mn 05s
---\\ Composants installés (ActiveSetup Installed Components) (O40)
O40 - ASIC: Microsoft Windows Media Player - >{22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Microsoft Windows Media Player 12.0 - {22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Windows Media Player Extension.) -- C:\Windows\System32\wmpdxm.dll =>.Microsoft Corporation
O40 - ASIC: Themes Setup - {2C7339CF-2B09-4501-B3F3-F3508C9228ED} . (.Microsoft Corporation - API Windows Theme.) -- C:\Windows\System32\themeui.dll
O40 - ASIC: Internet Explorer - {2D46B6DC-2207-486B-B523-A557E6D54B47} . (.Microsoft Corporation - Interpréteur de commandes Windows.) -- C:\Windows\system32\cmd.exe =>.Microsoft Corporation
O40 - ASIC: Microsoft Windows - {44BBA840-CC51-11CF-AAFA-00AA00B6015C} . (.Microsoft Corporation - Windows Mail.) -- C:\Program Files\Windows Mail\WinMail.exe =>.Microsoft Corporation
O40 - ASIC: Browsing Enhancements - {630b1da0-b465-11d1-9948-00c04f98bbc9} . (.Microsoft Corporation - Extension Shell dossier FTP Microsoft Internet Explorer..) -- C:\Windows\System32\msieftp.dll
O40 - ASIC: Microsoft Windows Media Player - {6BF52A52-394A-11d3-B153-00C04F79FAA6} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Windows Desktop Update - {89820200-ECBD-11cf-8B85-00AA005B4340} . (.Microsoft Corporation - DLL commune du shell Windows.) -- C:\Windows\System32\shell32.dll
O40 - ASIC: Web Platform Customizations - {89820200-ECBD-11cf-8B85-00AA005B4383} . (.Microsoft Corporation - Utilitaire d'initialisation d'Internet Explorer par utilisateur.) -- C:\Windows\System32\ie4uinit.exe
O40 - ASIC: (no name) - {89B4C1CD-B018-4511-B0A1-5476DBF70820} . (.Microsoft Corporation - Microsoft .NET IE SECURITY REGISTRATION.) -- C:\Windows\system32\mscories.dll
O40 - ASIC: Google Chrome - {8A69D345-D564-463c-AFF1-A69D9E530F96} . (.Google Inc. - Google Chrome Installer.) -- C:\Program Files\Google\Chrome\Application\40.0.2214.115\Installer\chrmstp.exe
~ Active Setup: 11 Scanned in 00mn 00s
---\\ Pilotes lancés au démarrage du système (O41)
O41 - Driver: C:\Windows\System32\drivers\afd.sys (AFD) . (.Microsoft Corporation - Ancillary Function Driver for WinSock.) - C:\Windows\system32\drivers\afd.sys
O41 - Driver: (blbdrive) . (.Microsoft Corporation - BLB Drive Driver.) - C:\Windows\System32\DRIVERS\blbdrive.sys
O41 - Driver: (cdrom) . (.Microsoft Corporation - SCSI CD-ROM Driver.) - C:\Windows\System32\DRIVERS\cdrom.sys
O41 - Driver: C:\Windows\System32\cscsvc.dll (CSC) . (.Microsoft Corporation - Windows Client Side Caching Driver.) - C:\Windows\System32\drivers\csc.sys
O41 - Driver: C:\Windows\System32\drivers\dfsc.sys (DfsC) . (.Microsoft Corporation - DFS Namespace Client Driver.) - C:\Windows\System32\Drivers\dfsc.sys
O41 - Driver: C:\Windows\System32\drivers\discache.sys (discache) . (.Microsoft Corporation - System Indexer/Cache Driver.) - C:\Windows\System32\drivers\discache.sys
O41 - Driver: (MpKsl2593c2bc) . (. - .) - C:\ProgramData\Microsoft\Microsoft Antimalware\Definition Updates\{9184CDCB-D27A-421D-954B-69D88208652B}\MpKsl2593c2bc.sys (.not file.)
O41 - Driver: (mssmbios) . (.Microsoft Corporation - System Management BIOS Driver.) - C:\Windows\system32\drivers\mssmbios.sys
O41 - Driver: (NetBIOS) . (.Microsoft Corporation - NetBIOS interface driver.) - C:\Windows\System32\DRIVERS\netbios.sys
O41 - Driver: C:\Windows\System32\drivers\netbt.sys (NetBT) . (.Microsoft Corporation - MBT Transport driver.) - C:\Windows\System32\DRIVERS\netbt.sys
O41 - Driver: C:\Windows\System32\drivers\nsiproxy.sys (nsiproxy) . (.Microsoft Corporation - NSI Proxy.) - C:\Windows\System32\drivers\nsiproxy.sys
O41 - Driver: C:\Windows\System32\drivers\pacer.sys (Psched) . (.Microsoft Corporation - Planificateur de paquets QoS.) - C:\Windows\System32\DRIVERS\pacer.sys
O41 - Driver: C:\Windows\System32\wkssvc.dll (rdbss) . (.Microsoft Corporation - Pilote du sous-système de mise en mémoire t.) - C:\Windows\System32\DRIVERS\rdbss.sys
O41 - Driver: C:\Windows\System32\DRIVERS\RDPCDD.sys (RDPCDD) . (.Microsoft Corporation - RDP Miniport.) - C:\Windows\System32\DRIVERS\RDPCDD.sys
O41 - Driver: C:\Windows\System32\drivers\RDPENCDD.sys (RDPENCDD) . (.Microsoft Corporation - RDP Encoder Miniport.) - C:\Windows\System32\drivers\rdpencdd.sys
O41 - Driver: C:\Windows\System32\drivers\RdpRefMp.sys (RDPREFMP) . (.Microsoft Corporation - RDP Reflector Driver Miniport.) - C:\Windows\System32\drivers\rdprefmp.sys
O41 - Driver: (Serial) . (.Brother Industries Ltd. - Pilote Brother Série I/F (WDM).) - C:\Windows\System32\DRIVERS\serial.sys
O41 - Driver: C:\Windows\System32\tcpipcfg.dll (tdx) . (.Microsoft Corporation - TDI Translation Driver.) - C:\Windows\System32\DRIVERS\tdx.sys
O41 - Driver: (TermDD) . (.Microsoft Corporation - Remote Desktop Server Driver.) - C:\Windows\system32\drivers\termdd.sys
O41 - Driver: (VgaSave) . (.Microsoft Corporation - VGA/Super VGA Video Driver.) - C:\Windows\system32\drivers\vga.sys
O41 - Driver: (vpcnfltr) . (.Microsoft Corporation - Virtual PC Network Filter Driver.) - C:\Windows\System32\DRIVERS\vpcnfltr.sys
O41 - Driver: C:\Windows\System32\drivers\vpcvmm.sys (vpcvmm) . (.Microsoft Corporation - Moniteur d'ordinateur virtuel Virtual PC.) - C:\Windows\System32\drivers\vpcvmm.sys
O41 - Driver: C:\Windows\System32\rascfg.dll (Wanarpv6) . (.Microsoft Corporation - MS Remote Access and Routing ARP Driver.) - C:\Windows\System32\DRIVERS\wanarp.sys
O41 - Driver: (WfpLwf) . (.Microsoft Corporation - WFP NDIS 6.20 Lightweight Filter Driver.) - C:\Windows\System32\DRIVERS\wfplwf.sys
~ Drivers: 72 Scanned in 00mn 00s
---\\ Logiciels installés (O42)
O42 - Logiciel: Adobe Digital Editions - (...) [HKLM] -- Digital Editions
O42 - Logiciel: Adobe Flash Player 11 Plugin - (.Adobe Systems Incorporated.) [HKLM] -- Adobe Flash Player Plugin
O42 - Logiciel: Adobe Flash Player 16 ActiveX - (.Adobe Systems Incorporated.) [HKLM] -- Adobe Flash Player ActiveX
O42 - Logiciel: Adobe Reader XI (11.0.10) - Français - (.Adobe Systems Incorporated.) [HKLM] -- {AC76BA86-7AD7-1036-7B44-AB0000000001}
O42 - Logiciel: Adobe Refresh Manager - (.Adobe Systems Incorporated.) [HKLM] -- {AC76BA86-0804-1033-1959-001802114130}
O42 - Logiciel: AxCrypt 1.7.2976.0 - (.Axantum Software AB.) [HKLM] -- {38350E9E-D50E-454A-BAFC-58BBDDBE08C4}
O42 - Logiciel: CCleaner - (.Piriform.) [HKLM] -- CCleaner
O42 - Logiciel: CameraHelperMsi - (.Logitech.) [HKLM] -- {15634701-BACE-4449-8B25-1567DA8C9FD3}
O42 - Logiciel: Canon Easy-PhotoPrint EX - (...) [HKLM] -- Easy-PhotoPrint EX
O42 - Logiciel: Canon Easy-WebPrint EX - (...) [HKLM] -- Easy-WebPrint EX
O42 - Logiciel: Canon IJ Network Scanner Selector EX - (...) [HKLM] -- Canon_IJ_Network_Scanner_Selector_EX
O42 - Logiciel: Canon IJ Network Tool - (...) [HKLM] -- Canon_IJ_Network_UTILITY
O42 - Logiciel: Canon Inkjet Printer/Scanner/Fax Extended Survey Program - (...) [HKLM] -- CANONIJPLM100
O42 - Logiciel: Canon MP Navigator EX 4.1 - (...) [HKLM] -- MP Navigator EX 4.1
O42 - Logiciel: Canon MX420 series MP Drivers - (...) [HKLM] -- {1199FAD5-9546-44f3-81CF-FFDB8040B7BF}_Canon_MX420_series
O42 - Logiciel: Canon My Printer - (...) [HKLM] -- CanonMyPrinter
O42 - Logiciel: Canon Solution Menu EX - (...) [HKLM] -- CanonSolutionMenuEX
O42 - Logiciel: Canon Utilitaire de numérotation rapide - (...) [HKLM] -- Speed Dial Utility
O42 - Logiciel: D3DX10 - (.Microsoft.) [HKLM] -- {E09C4DB7-630C-4F06-A631-8EA7239923AF}
O42 - Logiciel: Enregistrement utilisateur de Canon MX420 series - (...) [HKLM] -- Enregistrement utilisateur de Canon MX420 series =>.Canon Inc
O42 - Logiciel: Galerie de photos - (.Microsoft Corporation.) [HKLM] -- {446CC8CE-0E90-44F7-ADD0-774B243EF090}
O42 - Logiciel: Google Chrome - (.Google Inc..) [HKLM] -- Google Chrome
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM] -- {60EC980A-BDA2-4CB6-A427-B07A5498B4CA}
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM] -- {A92DAB39-4E2C-4304-9AB6-BC44E68B55E2}
O42 - Logiciel: Google Earth - (.Google.) [HKLM] -- {4D2A6330-2F8B-11E3-9C40-B8AC6F97B88E}
O42 - Logiciel: HTC Sync Manager - (.HTC.) [HKLM] -- {5002C5B1-B688-474A-AB3A-9B65DBD38FF9}
O42 - Logiciel: IPTInstaller - (.HTC.) [HKLM] -- {08208143-777D-4A06-BB54-71BF0AD1BB70}
O42 - Logiciel: Java 8 Update 31 - (.Oracle Corporation.) [HKLM] -- {26A24AE4-039D-4CA4-87B4-2F83218031F0}
O42 - Logiciel: Junk Mail filter update - (.Microsoft Corporation.) [HKLM] -- {400C31E4-796F-4E86-8FDC-C3C4FACC6847}
O42 - Logiciel: LWS Facebook - (.Logitech.) [HKLM] -- {FF167195-9EE4-46C0-8CD7-FBA3457E88AB}
O42 - Logiciel: LWS Gallery - (.Logitech.) [HKLM] -- {6F76EC3C-34B1-436E-97FB-48C58D7BEDCD}
O42 - Logiciel: LWS Help_main - (.Logitech.) [HKLM] -- {1651216E-E7AD-4250-92A1-FB8ED61391C9}
O42 - Logiciel: LWS Launcher - (.Logitech.) [HKLM] -- {83C8FA3C-F4EA-46C4-8392-D3CE353738D6}
O42 - Logiciel: LWS Motion Detection - (.Logitech.) [HKLM] -- {71E66D3F-A009-44AB-8784-75E2819BA4BA}
O42 - Logiciel: LWS Pictures And Video - (.Logitech.) [HKLM] -- {08610298-29AE-445B-B37D-EFBE05802967}
O42 - Logiciel: LWS Twitter - (.Logitech.) [HKLM] -- {174A3B31-4C43-43DD-866F-73C9DB887B48}
O42 - Logiciel: LWS Video Mask Maker - (.Logitech.) [HKLM] -- {EED027B7-0DB6-404B-8F45-6DFEE34A0441}
O42 - Logiciel: LWS VideoEffects - (.Logitech.) [HKLM] -- {138A4072-9E64-46BD-B5F9-DB2BB395391F}
O42 - Logiciel: LWS WLM Plugin - (.Logitech.) [HKLM] -- {9DAEA76B-E50F-4272-A595-0124E826553D}
O42 - Logiciel: LWS Webcam Software - (.Logitech.) [HKLM] -- {8937D274-C281-42E4-8CDB-A0B2DF979189}
O42 - Logiciel: LWS YouTube Plugin - (.Logitech.) [HKLM] -- {21DF0294-6B9D-4741-AB6F-B2ABFBD2387E}
O42 - Logiciel: Logitech Webcam Software - (.Logitech Inc..) [HKLM] -- {D40EB009-0499-459c-A8AF-C9C110766215} =>.Logitech Inc
O42 - Logiciel: MSVCRT - (.Microsoft.) [HKLM] -- {8DD46C6A-0056-4FEC-B70A-28BB16A1F11F}
O42 - Logiciel: MSVCRT110 - (.Microsoft.) [HKLM] -- {8E14DDC8-EA60-4E18-B3E3-1937104D5BDA}
O42 - Logiciel: MSXML 4.0 SP2 (KB954430) - (.Microsoft Corporation.) [HKLM] -- {86493ADD-824D-4B8E-BD72-8C5DCDC52A71}
O42 - Logiciel: MSXML 4.0 SP2 (KB973688) - (.Microsoft Corporation.) [HKLM] -- {F662A8E6-F4DC-41A2-901E-8C11F044BDEC}
O42 - Logiciel: Malwarebytes Anti-Malware version 2.0.4.1028 - (.Malwarebytes Corporation.) [HKLM] -- Malwarebytes Anti-Malware_is1
O42 - Logiciel: Microsoft OneDrive - (.Microsoft Corporation.) [HKCU] -- OneDriveSetup.exe
O42 - Logiciel: Microsoft Security Client - (.Microsoft Corporation.) [HKLM] -- {D6F9CBDC-58B6-430A-8DD4-8F61CBC1ADF4}
O42 - Logiciel: Microsoft Security Essentials - (.Microsoft Corporation.) [HKLM] -- Microsoft Security Client
O42 - Logiciel: Microsoft Silverlight - (.Microsoft Corporation.) [HKLM] -- {89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}
O42 - Logiciel: Mises à jour NVIDIA 1.10.8 - (.NVIDIA Corporation.) [HKLM] -- {B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.Update
O42 - Logiciel: Mozilla Firefox 23.0 (x86 fr) - (.Mozilla.) [HKLM] -- Mozilla Firefox 23.0 (x86 fr)
O42 - Logiciel: Mozilla Maintenance Service - (.Mozilla.) [HKLM] -- MozillaMaintenanceService
O42 - Logiciel: NVIDIA Pilote graphique 307.83 - (.NVIDIA Corporation.) [HKLM] -- {B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.Driver
O42 - Logiciel: PDFCreator - (.Frank Heindörfer, Philip Chinery.) [HKLM] -- {0001B4FD-9EA3-4D90-A79E-FD14BA3AB01D}
O42 - Logiciel: Picasa 3 - (.Google, Inc..) [HKLM] -- Picasa 3
O42 - Logiciel: RealUpgrade 1.1 - (.RealNetworks, Inc..) [HKLM] -- {28C2DED6-325B-4CC7-983A-1777C8F7FBAB}
O42 - Logiciel: Security Update for CAPICOM (KB931906) - (.Microsoft Corporation.) [HKLM] -- KB931906
O42 - Logiciel: Security Update for CAPICOM (KB931906) - (.Microsoft Corporation.) [HKLM] -- {0EFDF2F9-836D-4EB7-A32D-038BD3F1FB2A}
O42 - Logiciel: Skype(TM) 7.1 - (.Skype Technologies S.A..) [HKLM] -- {24991BA0-F0EE-44AD-9CC8-5EC50AECF6B7}
O42 - Logiciel: VLC media player - (.VideoLAN.) [HKLM] -- VLC media player =>.VideoLAN
O42 - Logiciel: Virtual DJ Packages - (...) [HKCU] -- Virtual DJ Packages
O42 - Logiciel: VirtualDJ 8 - (.Atomix Productions.) [HKLM] -- {13E44DA9-FE06-4298-9179-BEF27214B47B}
O42 - Logiciel: VirtualDJ Broadcaster - (.Atomix Productions.) [HKLM] -- {3575B758-28E1-4AA8-AFC4-D597CC4C7B14}
O42 - Logiciel: VirtualDJ Home FREE - (.Atomix Productions.) [HKLM] -- {EE9E75F0-1FB8-440A-A34A-058F7456E113}
O42 - Logiciel: WOT for Internet Explorer - (.WOT Services Oy.) [HKLM] -- {DCAEC601-735C-41AE-B84F-D792F09FB7D1}
O42 - Logiciel: WinRAR 4.00 (32 bits) - (.win.rar GmbH.) [HKLM] -- WinRAR archiver
O42 - Logiciel: erLT - (.Logitech, Inc..) [HKLM] -- {3EE9BCAE-E9A9-45E5-9B1C-83A4D357E05C}
O42 - Logiciel: scrabbleproB 1.1.3 - (.scrabblepro.) [HKLM] -- scrabbleproB_is1
~ Logic: 41 Scanned in 00mn 00s
---\\ HKCU & HKLM Software Keys
[HKCU\Software\Adobe]
[HKCU\Software\AppDataLow\Software\Against Intuition]
[HKCU\Software\AppDataLow\Software\Canon]
[HKCU\Software\AppDataLow\Software\JavaSoft]
[HKCU\Software\AppDataLow\Software\RealNetworks]
[HKCU\Software\AppDataLow]
[HKCU\Software\Apple Computer, Inc.]
[HKCU\Software\Apple Inc.]
[HKCU\Software\Axantum]
[HKCU\Software\Canon]
[HKCU\Software\Classes]
[HKCU\Software\Clients]
[HKCU\Software\Convertir.co]
[HKCU\Software\Fast Folder Access]
[HKCU\Software\FreeTime]
[HKCU\Software\Freecom]
[HKCU\Software\Freemake]
[HKCU\Software\GNU]
[HKCU\Software\Gabest]
[HKCU\Software\Garmin]
[HKCU\Software\GlarySoft]
[HKCU\Software\Google]
[HKCU\Software\HTC]
[HKCU\Software\Haali]
[HKCU\Software\HookNetwork]
[HKCU\Software\IM Providers]
[HKCU\Software\JavaSoft]
[HKCU\Software\Leadertech]
[HKCU\Software\Licenses]
[HKCU\Software\LogiShrd]
[HKCU\Software\Logitech]
[HKCU\Software\Macromedia]
[HKCU\Software\Macrovision]
[HKCU\Software\MozillaPlugins]
[HKCU\Software\Mozilla]
[HKCU\Software\NVIDIA Corporation]
[HKCU\Software\Nero]
[HKCU\Software\Netscape]
[HKCU\Software\ODBC]
[HKCU\Software\Orange]
[HKCU\Software\PDFCreator]
[HKCU\Software\Piriform]
[HKCU\Software\Policies]
[HKCU\Software\RealNetworks]
[HKCU\Software\Reg]
[HKCU\Software\Sarbakan]
[HKCU\Software\Skype]
[HKCU\Software\TeleCharger]
[HKCU\Software\TeleCharger_v2]
[HKCU\Software\Trolltech]
[HKCU\Software\TuneUp]
[HKCU\Software\VB and VBA Program Settings]
[HKCU\Software\VirtualDJ]
[HKCU\Software\WebApp]
[HKCU\Software\WinRAR SFX]
[HKCU\Software\WinRAR]
[HKCU\Software\Wow6432Node]
[HKCU\Software\ZebHelpProcess Helper]
[HKCU\Software\redsn0w]
[HKLM\Software\ATI Technologies]
[HKLM\Software\Adobe]
[HKLM\Software\AdwCleaner]
[HKLM\Software\Apple Computer, Inc.]
[HKLM\Software\Apple Inc.]
[HKLM\Software\Axantum]
[HKLM\Software\CDDB]
[HKLM\Software\Canon]
[HKLM\Software\Classes]
[HKLM\Software\Clients]
[HKLM\Software\DivXNetworks]
[HKLM\Software\Electronic Arts]
[HKLM\Software\Freemake]
[HKLM\Software\GEAR Software]
[HKLM\Software\GNU]
[HKLM\Software\Garmin]
[HKLM\Software\GlarySoft]
[HKLM\Software\Google]
[HKLM\Software\HTC]
[HKLM\Software\HaaliMkx]
[HKLM\Software\IM Providers]
[HKLM\Software\Intel]
[HKLM\Software\JavaSoft]
[HKLM\Software\JreMetrics]
[HKLM\Software\Khronos]
[HKLM\Software\Logitech]
[HKLM\Software\Macromedia]
[HKLM\Software\Malwarebytes' Anti-Malware]
[HKLM\Software\MozillaPlugins]
[HKLM\Software\Mozilla]
[HKLM\Software\NVIDIA Corporation]
[HKLM\Software\Nero]
[HKLM\Software\ODBC]
[HKLM\Software\PDFCreator]
[HKLM\Software\Piriform]
[HKLM\Software\Policies]
[HKLM\Software\Promolettres]
[HKLM\Software\RealNetworks]
[HKLM\Software\Reg]
[HKLM\Software\RegisteredApplications]
[HKLM\Software\Skype]
[HKLM\Software\Sonic]
[HKLM\Software\Symantec]
[HKLM\Software\TuneUp]
[HKLM\Software\VideoLAN]
[HKLM\Software\VirtualDJ]
[HKLM\Software\WinRAR]
[HKLM\Software\Windows]
[HKLM\Software\Wow6432Node]
[HKLM\Software\Xing Technology Corp.]
[HKLM\Software\logishrd]
[HKLM\Software\mozilla.org]
~ Key Software: 224 Scanned in 00mn 00s
---\\ Contenu des dossiers Programs/ProgramFiles/ProgramData/AppData (O43)
O43 - CFD: 07/07/2014 - 22:02:59 - [] ----D C:\Program Files\Adobe
O43 - CFD: 30/12/2013 - 21:24:56 - [] ----D C:\Program Files\Axantum
O43 - CFD: 21/12/2011 - 12:43:29 - [] ----D C:\Program Files\Canon
O43 - CFD: 21/12/2011 - 12:31:39 - [] --H-D C:\Program Files\CanonBJ
O43 - CFD: 15/06/2013 - 10:33:22 - [] ----D C:\Program Files\CCleaner
O43 - CFD: 29/01/2015 - 21:21:25 - [] ----D C:\Program Files\Common Files
O43 - CFD: 12/07/2014 - 19:26:13 - [] ----D C:\Program Files\Convertisseur MP3
O43 - CFD: 16/10/2014 - 21:14:46 - [] ----D C:\Program Files\Convertisseur YouTube
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\DVD Maker
O43 - CFD: 29/07/2012 - 07:16:49 - [] ----D C:\Program Files\EA SPORTS
O43 - CFD: 30/12/2013 - 21:22:51 - [] ----D C:\Program Files\Fast Folder Access
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\Program Files\Fichiers communs
O43 - CFD: 12/07/2014 - 19:27:48 - [] ----D C:\Program Files\Freemake
O43 - CFD: 12/07/2014 - 19:28:04 - [0] ----D C:\Program Files\FreeTime
O43 - CFD: 12/12/2013 - 20:25:46 - [] ----D C:\Program Files\Google
O43 - CFD: 13/07/2013 - 08:34:26 - [] ----D C:\Program Files\HTC
O43 - CFD: 05/10/2014 - 14:18:23 - [] ----D C:\Program Files\Intelore
O43 - CFD: 12/02/2015 - 18:18:06 - [] ----D C:\Program Files\Internet Explorer
O43 - CFD: 29/01/2015 - 21:21:57 - [] ----D C:\Program Files\Java
O43 - CFD: 11/12/2011 - 11:18:35 - [] ----D C:\Program Files\Logitech
O43 - CFD: 26/02/2015 - 22:45:00 - [] ----D C:\Program Files\Malwarebytes Anti-Malware
O43 - CFD: 16/12/2011 - 08:22:28 - [] ----D C:\Program Files\Microsoft CAPICOM 2.1.0.2
O43 - CFD: 14/07/2009 - 08:50:24 - [] ----D C:\Program Files\Microsoft Games
O43 - CFD: 21/02/2012 - 23:46:04 - [] ----D C:\Program Files\Microsoft Office
O43 - CFD: 11/02/2015 - 23:27:43 - [] ----D C:\Program Files\Microsoft Security Client
O43 - CFD: 14/12/2014 - 10:43:20 - [] ----D C:\Program Files\Microsoft Silverlight
O43 - CFD: 18/02/2013 - 22:40:24 - [] ----D C:\Program Files\Microsoft SkyDrive =>.Microsoft Corporation
O43 - CFD: 07/12/2011 - 21:07:11 - [] ----D C:\Program Files\Microsoft SQL Server Compact Edition
O43 - CFD: 07/12/2011 - 19:55:15 - [] ----D C:\Program Files\Microsoft Visual Studio
O43 - CFD: 07/12/2011 - 19:51:23 - [] ----D C:\Program Files\Microsoft Visual Studio 8
O43 - CFD: 18/12/2011 - 03:03:15 - [] ----D C:\Program Files\Microsoft Works
O43 - CFD: 08/12/2011 - 00:58:34 - [] ----D C:\Program Files\Microsoft.NET
O43 - CFD: 03/01/2012 - 22:50:22 - [] ----D C:\Program Files\Movie Maker
O43 - CFD: 03/01/2012 - 22:55:30 - [] ----D C:\Program Files\Movie Maker 2.6
O43 - CFD: 07/08/2013 - 20:15:14 - [] ----D C:\Program Files\Mozilla Firefox
O43 - CFD: 05/01/2014 - 09:18:54 - [] ----D C:\Program Files\Mozilla Maintenance Service
O43 - CFD: 07/12/2011 - 19:55:33 - [] ----D C:\Program Files\MSBuild
O43 - CFD: 14/07/2013 - 00:49:39 - [0] ----D C:\Program Files\MSXML 4.0
O43 - CFD: 14/04/2013 - 21:07:27 - [] ----D C:\Program Files\NVIDIA Corporation
O43 - CFD: 15/06/2013 - 14:12:32 - [] ----D C:\Program Files\PDFCreator
O43 - CFD: 17/01/2015 - 13:34:03 - [] ----D C:\Program Files\Real
O43 - CFD: 17/10/2014 - 17:30:14 - [0] ----D C:\Program Files\Recuva
O43 - CFD: 14/07/2009 - 05:52:30 - [] ----D C:\Program Files\Reference Assemblies
O43 - CFD: 11/12/2011 - 12:06:37 - [] ----D C:\Program Files\scrabbleproB
O43 - CFD: 11/10/2012 - 19:17:05 - [] ----D C:\Program Files\scrabbleproB1.1
O43 - CFD: 21/02/2015 - 20:42:50 - [] R---D C:\Program Files\Skype
O43 - CFD: 14/07/2009 - 05:53:23 - [0] --H-D C:\Program Files\Uninstall Information
O43 - CFD: 21/12/2011 - 19:42:48 - [] ----D C:\Program Files\VideoLAN
O43 - CFD: 26/01/2015 - 21:25:37 - [] ----D C:\Program Files\VirtualDJ
O43 - CFD: 26/02/2015 - 23:08:26 - [] ----D C:\Program Files\Webplayer decompression
O43 - CFD: 10/07/2013 - 06:00:54 - [] ----D C:\Program Files\Windows Defender
O43 - CFD: 11/07/2014 - 10:17:12 - [] ----D C:\Program Files\Windows Journal
O43 - CFD: 01/05/2013 - 07:32:46 - [] ----D C:\Program Files\Windows Live
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\Windows Mail =>.Microsoft Corporation
O43 - CFD: 13/12/2013 - 06:13:27 - [] ----D C:\Program Files\Windows Media Player =>.Microsoft Corporation
O43 - CFD: 07/12/2011 - 19:35:47 - [] ----D C:\Program Files\Windows NT
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\Windows Photo Viewer
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\Windows Portable Devices
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\Windows Sidebar
O43 - CFD: 31/07/2009 - 15:53:45 - [] ----D C:\Program Files\Windows Virtual PC
O43 - CFD: 07/12/2011 - 19:42:33 - [] ----D C:\Program Files\WinRAR
O43 - CFD: 13/06/2013 - 21:05:31 - [] ----D C:\Program Files\WordBiz
O43 - CFD: 15/06/2013 - 14:24:15 - [] ----D C:\Program Files\WOT
O43 - CFD: 26/02/2015 - 21:33:31 - [] ----D C:\Program Files\ZHPDiag =>.Nicolas Coolman
O43 - CFD: 07/07/2014 - 22:03:25 - [] ----D C:\Program Files\Common Files\Adobe
O43 - CFD: 21/12/2011 - 12:37:13 - [] ----D C:\Program Files\Common Files\CANON
O43 - CFD: 15/05/2014 - 00:15:40 - [] ----D C:\Program Files\Common Files\DESIGNER
O43 - CFD: 29/01/2015 - 21:21:25 - [] ----D C:\Program Files\Common Files\Java
O43 - CFD: 15/02/2013 - 23:41:52 - [] ----D C:\Program Files\Common Files\logishrd
O43 - CFD: 11/12/2011 - 11:17:23 - [] ----D C:\Program Files\Common Files\LWS
O43 - CFD: 13/07/2013 - 08:32:43 - [] ----D C:\Program Files\Common Files\microsoft shared
O43 - CFD: 13/07/2013 - 08:35:03 - [] ----D C:\Program Files\Common Files\Nero
O43 - CFD: 02/12/2012 - 21:49:19 - [0] ----D C:\Program Files\Common Files\Promolettres
O43 - CFD: 12/12/2011 - 00:42:12 - [] ----D C:\Program Files\Common Files\Real
O43 - CFD: 14/07/2009 - 03:37:05 - [] ----D C:\Program Files\Common Files\Services
O43 - CFD: 17/01/2015 - 13:36:05 - [] ----D C:\Program Files\Common Files\Skype
O43 - CFD: 14/07/2009 - 03:37:05 - [] ----D C:\Program Files\Common Files\SpeechEngines
O43 - CFD: 11/07/2012 - 07:04:45 - [] ----D C:\Program Files\Common Files\System
O43 - CFD: 07/12/2011 - 20:57:21 - [] ----D C:\Program Files\Common Files\Windows Live
O43 - CFD: 12/07/2014 - 19:33:53 - [] ----D C:\ProgramData\188F1432-103A-4ffb-80F1-36B633C5C9E1
O43 - CFD: 07/07/2014 - 22:03:05 - [] ----D C:\ProgramData\Adobe
O43 - CFD: 12/07/2014 - 19:35:42 - [] ----D C:\ProgramData\Apple
O43 - CFD: 19/01/2012 - 08:35:51 - [] ----D C:\ProgramData\Apple Computer
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Application Data
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\ProgramData\Bureau
O43 - CFD: 21/12/2011 - 12:40:42 - [0] ----D C:\ProgramData\Canon IJ Network Tool
O43 - CFD: 21/12/2011 - 12:32:32 - [] --H-D C:\ProgramData\CanonBJ
O43 - CFD: 21/12/2011 - 12:43:30 - [0] --H-D C:\ProgramData\CanonEPP
O43 - CFD: 23/12/2011 - 10:25:24 - [] ----D C:\ProgramData\CanonIJ
O43 - CFD: 16/07/2012 - 20:59:55 - [] --H-D C:\ProgramData\CanonIJEGV
O43 - CFD: 04/09/2012 - 20:06:03 - [] --H-D C:\ProgramData\CanonIJEPPEX
O43 - CFD: 21/12/2011 - 12:43:30 - [0] --H-D C:\ProgramData\CanonIJEPPEX2
O43 - CFD: 21/12/2011 - 12:40:27 - [] --H-D C:\ProgramData\CanonIJFAX
O43 - CFD: 21/12/2011 - 12:43:29 - [] --H-D C:\ProgramData\CanonIJMyPrinter
O43 - CFD: 03/02/2015 - 18:24:01 - [] ----D C:\ProgramData\CanonIJPLM
O43 - CFD: 23/12/2011 - 10:23:57 - [] --H-D C:\ProgramData\CanonIJScan
O43 - CFD: 21/12/2011 - 12:43:31 - [] --H-D C:\ProgramData\CanonIJSolutionMenuEX
O43 - CFD: 21/12/2011 - 12:37:04 - [] ----D C:\ProgramData\CanonIJWSpt
O43 - CFD: 03/06/2013 - 05:55:23 - [] --H-D C:\ProgramData\Common Files
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Desktop
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Documents
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\ProgramData\Favoris
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Favorites
O43 - CFD: 12/07/2014 - 19:27:51 - [0] ----D C:\ProgramData\Freemake
O43 - CFD: 13/07/2013 - 08:44:16 - [] ----D C:\ProgramData\HTC
O43 - CFD: 11/12/2011 - 11:16:32 - [] ----D C:\ProgramData\LogiShrd
O43 - CFD: 11/12/2011 - 11:17:28 - [] ----D C:\ProgramData\Logitech
O43 - CFD: 26/02/2015 - 22:42:19 - [] ----D C:\ProgramData\Malwarebytes
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\ProgramData\Menu Démarrer
O43 - CFD: 10/12/2014 - 19:25:31 - [] -S--D C:\ProgramData\Microsoft
O43 - CFD: 11/02/2015 - 23:31:40 - [] ----D C:\ProgramData\Microsoft Help
O43 - CFD: 19/09/2014 - 13:18:45 - [] ----D C:\ProgramData\Microsoft OneDrive
O43 - CFD: 18/02/2013 - 22:40:01 - [] ----D C:\ProgramData\Microsoft SkyDrive =>.Microsoft Corporation
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\ProgramData\Modèles
O43 - CFD: 13/07/2013 - 08:35:22 - [] ----D C:\ProgramData\Motorola
O43 - CFD: 27/10/2012 - 18:33:29 - [] ----D C:\ProgramData\Mozilla
O43 - CFD: 14/04/2013 - 21:07:36 - [] ----D C:\ProgramData\NVIDIA
O43 - CFD: 14/04/2013 - 21:05:52 - [] ----D C:\ProgramData\NVIDIA Corporation
O43 - CFD: 29/01/2015 - 21:23:44 - [] ----D C:\ProgramData\Oracle
O43 - CFD: 17/01/2015 - 13:33:56 - [] ----D C:\ProgramData\Real
O43 - CFD: 21/02/2015 - 20:42:57 - [] ----D C:\ProgramData\Skype
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Start Menu
O43 - CFD: 07/12/2011 - 22:42:03 - [] ----D C:\ProgramData\Sun
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Templates
O43 - CFD: 03/06/2013 - 05:55:46 - [] ----D C:\ProgramData\TuneUp Software
O43 - CFD: 07/12/2011 - 19:43:02 - [] ----D C:\ProgramData\XsRXTfiwSUdn
O43 - CFD: 19/01/2012 - 08:36:24 - [] ----D C:\ProgramData\{429CAD59-35B1-4DBC-BB6D-1DB246563521}
O43 - CFD: 26/02/2015 - 23:08:26 - [] ----D C:\ProgramData\{4896dc69-39e0-8578-4896-6dc6939e71a4}
O43 - CFD: 26/02/2015 - 23:10:00 - [] ----D C:\ProgramData\{89c85052-2a23-cc44-89c8-850522a24148}
O43 - CFD: 03/06/2013 - 05:55:23 - [] -SH-D C:\ProgramData\{C4ABDBC8-1C81-42C9-BFFC-4A68511E9E4F}
O43 - CFD: 03/01/2012 - 22:49:47 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Accessoires
O43 - CFD: 12/12/2011 - 00:35:05 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Accessories
O43 - CFD: 07/12/2011 - 19:33:12 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Administrative Tools
O43 - CFD: 01/05/2012 - 13:46:11 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Adobe
O43 - CFD: 30/12/2013 - 21:25:00 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Axantum AxCrypt
O43 - CFD: 21/12/2011 - 12:32:29 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Canon MX420 series
O43 - CFD: 21/12/2011 - 12:33:15 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Canon MX420 series Manual
O43 - CFD: 21/12/2011 - 12:40:53 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Canon Utilities
O43 - CFD: 15/06/2013 - 10:33:22 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\CCleaner
O43 - CFD: 21/12/2011 - 12:38:59 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Enregistrement utilisateur de Canon MX420 series =>.Canon Inc
O43 - CFD: 30/12/2013 - 21:22:50 - [0] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Fast Folder Access
O43 - CFD: 07/12/2011 - 19:33:12 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Games
O43 - CFD: 14/06/2013 - 19:10:22 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Chrome
O43 - CFD: 12/12/2013 - 20:25:55 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Earth =>.Google Inc
O43 - CFD: 28/07/2014 - 20:16:45 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\HTC
O43 - CFD: 29/01/2015 - 21:20:26 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Java
O43 - CFD: 15/02/2013 - 23:41:54 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Logitech
O43 - CFD: 14/07/2009 - 05:42:30 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Maintenance
O43 - CFD: 26/02/2015 - 22:45:00 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Malwarebytes Anti-Malware
O43 - CFD: 19/12/2011 - 03:05:10 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Office
O43 - CFD: 14/12/2014 - 02:00:00 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Silverlight
O43 - CFD: 23/12/2011 - 10:43:15 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\PDFCreator
O43 - CFD: 10/09/2012 - 22:59:41 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Picasa 3
O43 - CFD: 05/10/2014 - 14:18:24 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\RAR Password Recovery
O43 - CFD: 11/12/2011 - 12:06:37 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\scrabbleproB
O43 - CFD: 11/10/2012 - 19:17:05 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\scrabbleproB1.1
O43 - CFD: 17/01/2015 - 13:36:06 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Skype
O43 - CFD: 17/01/2015 - 13:33:42 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup
O43 - CFD: 14/07/2009 - 08:48:45 - [0] R-H-D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Tablet PC
O43 - CFD: 25/06/2014 - 19:37:55 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\VideoLAN
O43 - CFD: 18/02/2013 - 23:07:44 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Windows Live
O43 - CFD: 07/12/2011 - 19:33:12 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Windows Virtual PC
O43 - CFD: 07/12/2011 - 19:42:33 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\WinRAR
O43 - CFD: 26/02/2015 - 21:31:30 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\ZHP =>.Nicolas Coolman
O43 - CFD: 13/06/2013 - 21:06:02 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Zylom
O43 - CFD: 01/05/2012 - 13:51:56 - [] ----D C:\Users\remy\AppData\Roaming\Adobe
O43 - CFD: 13/07/2013 - 08:35:30 - [] ----D C:\Users\remy\AppData\Roaming\Apple Computer
O43 - CFD: 11/09/2013 - 07:02:17 - [] ----D C:\Users\remy\AppData\Roaming\Canon
O43 - CFD: 24/07/2013 - 22:36:07 - [] ----D C:\Users\remy\AppData\Roaming\Convertisseur MP3
O43 - CFD: 25/07/2013 - 18:10:59 - [] ----D C:\Users\remy\AppData\Roaming\Convertisseur YouTube
O43 - CFD: 14/09/2012 - 09:51:42 - [] ----D C:\Users\remy\AppData\Roaming\Garmin
O43 - CFD: 11/02/2012 - 15:38:40 - [] ----D C:\Users\remy\AppData\Roaming\GlarySoft
O43 - CFD: 13/07/2013 - 08:44:32 - [] ----D C:\Users\remy\AppData\Roaming\HTC
O43 - CFD: 13/07/2013 - 08:44:23 - [] ----D C:\Users\remy\AppData\Roaming\HTC Sync
O43 - CFD: 07/12/2011 - 19:36:09 - [] ----D C:\Users\remy\AppData\Roaming\Identities
O43 - CFD: 11/12/2011 - 11:18:37 - [] ----D C:\Users\remy\AppData\Roaming\Leadertech
O43 - CFD: 07/12/2011 - 19:43:06 - [] ----D C:\Users\remy\AppData\Roaming\lJQXCOOdhkcB
O43 - CFD: 07/12/2011 - 19:49:55 - [] ----D C:\Users\remy\AppData\Roaming\Macromedia
O43 - CFD: 14/07/2009 - 08:48:45 - [0] ----D C:\Users\remy\AppData\Roaming\Media Center Programs
O43 - CFD: 02/11/2013 - 09:39:01 - [] -S--D C:\Users\remy\AppData\Roaming\Microsoft
O43 - CFD: 15/06/2013 - 14:30:11 - [] ----D C:\Users\remy\AppData\Roaming\Mozilla
O43 - CFD: 19/10/2014 - 09:30:26 - [] ----D C:\Users\remy\AppData\Roaming\Oracle
O43 - CFD: 17/01/2015 - 13:33:39 - [] ----D C:\Users\remy\AppData\Roaming\Real
O43 - CFD: 08/08/2013 - 19:13:05 - [0] ----D C:\Users\remy\AppData\Roaming\redsn0w
O43 - CFD: 21/02/2015 - 20:44:07 - [] ----D C:\Users\remy\AppData\Roaming\Skype
O43 - CFD: 03/06/2013 - 05:55:46 - [] ----D C:\Users\remy\AppData\Roaming\TuneUp Software
O43 - CFD: 26/02/2015 - 22:17:50 - [] ----D C:\Users\remy\AppData\Roaming\uTorrent =>P2P.µTorrent
O43 - CFD: 22/02/2015 - 14:52:25 - [] ----D C:\Users\remy\AppData\Roaming\vlc
O43 - CFD: 07/12/2011 - 19:42:52 - [] ----D C:\Users\remy\AppData\Roaming\WinRAR
O43 - CFD: 26/02/2015 - 23:14:21 - [] ----D C:\Users\remy\AppData\Roaming\ZHP =>.Nicolas Coolman
O43 - CFD: 30/12/2014 - 19:43:48 - [] ----D C:\Users\remy\AppData\Local\Adobe
O43 - CFD: 19/01/2012 - 08:35:11 - [] ----D C:\Users\remy\AppData\Local\Apple
O43 - CFD: 13/07/2013 - 08:35:30 - [] ----D C:\Users\remy\AppData\Local\Apple Computer
O43 - CFD: 07/12/2011 - 19:35:54 - [] -SH-D C:\Users\remy\AppData\Local\Application Data
O43 - CFD: 03/01/2012 - 21:05:21 - [] ----D C:\Users\remy\AppData\Local\Apps
O43 - CFD: 02/03/2014 - 18:17:20 - [] ----D C:\Users\remy\AppData\Local\Canon Easy-PhotoPrint EX
O43 - CFD: 03/01/2012 - 21:05:32 - [0] ----D C:\Users\remy\AppData\Local\Deployment
O43 - CFD: 10/02/2015 - 20:41:57 - [] ----D C:\Users\remy\AppData\Local\Diagnostics
O43 - CFD: 13/07/2013 - 08:31:54 - [] ----D C:\Users\remy\AppData\Local\Downloaded Installations
O43 - CFD: 14/11/2014 - 18:24:02 - [] -SH-D C:\Users\remy\AppData\Local\EmieBrowserModeList
O43 - CFD: 10/04/2014 - 08:14:22 - [] -SH-D C:\Users\remy\AppData\Local\EmieSiteList
O43 - CFD: 10/04/2014 - 08:14:22 - [] -SH-D C:\Users\remy\AppData\Local\EmieUserList
O43 - CFD: 17/04/2014 - 10:39:50 - [] ----D C:\Users\remy\AppData\Local\FreemakeVideoDownloader
O43 - CFD: 14/06/2013 - 19:10:24 - [] ----D C:\Users\remy\AppData\Local\Google
O43 - CFD: 07/12/2011 - 19:35:54 - [] -SH-D C:\Users\remy\AppData\Local\Historique
O43 - CFD: 26/02/2015 - 23:11:07 - [] ----D C:\Users\remy\AppData\Local\HTC MediaHub
O43 - CFD: 11/12/2011 - 11:23:25 - [] ----D C:\Users\remy\AppData\Local\Logitech® Webcam Software
O43 - CFD: 27/10/2012 - 12:47:07 - [] ----D C:\Users\remy\AppData\Local\Macromedia
O43 - CFD: 17/07/2014 - 22:46:18 - [] ----D C:\Users\remy\AppData\Local\Microsoft
O43 - CFD: 18/08/2014 - 14:02:45 - [] ----D C:\Users\remy\AppData\Local\Microsoft Games
O43 - CFD: 07/12/2011 - 19:50:34 - [0] ----D C:\Users\remy\AppData\Local\Microsoft Help
O43 - CFD: 11/02/2012 - 19:36:21 - [] ----D C:\Users\remy\AppData\Local\Mozilla
O43 - CFD: 01/11/2012 - 22:53:42 - [] ----D C:\Users\remy\AppData\Local\Programs
O43 - CFD: 06/03/2014 - 07:55:44 - [] ----D C:\Users\remy\AppData\Local\Skype
O43 - CFD: 26/02/2015 - 23:11:17 - [] ----D C:\Users\remy\AppData\Local\Temp
O43 - CFD: 07/12/2011 - 19:35:54 - [] -SH-D C:\Users\remy\AppData\Local\Temporary Internet Files
O43 - CFD: 30/12/2013 - 21:21:00 - [] ----D C:\Users\remy\AppData\Local\VirtualStore
O43 - CFD: 01/05/2013 - 06:43:55 - [] ----D C:\Users\remy\AppData\Local\Windows Live
O43 - CFD: 08/01/2012 - 17:39:45 - [] ----D C:\Users\remy\AppData\Local\WMTools Downloaded Files
O43 - CFD: 12/12/2011 - 00:42:10 - [] R---D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories
O43 - CFD: 15/08/2014 - 10:16:03 - [] R---D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Administrative Tools
O43 - CFD: 14/07/2009 - 05:37:42 - [] R---D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Maintenance
O43 - CFD: 22/02/2015 - 16:36:05 - [] R---D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup
O43 - CFD: 26/01/2015 - 21:25:42 - [] ----D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\VirtualDJ
O43 - CFD: 07/12/2011 - 19:42:33 - [] ----D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\WinRAR
~ Program Folder: 225 Scanned in 00mn 00s
---\\ Derniers fichiers modifiés ou crées sous Windows et System32 (O44)
O44 - LFC:[MD5.E185BDA84E5F03F4E1D8DCA30E209277] - 11/02/2015 - 23:28:23 ---A- . (...) -- C:\Windows\epplauncher.mif [1912]
O44 - LFC:[MD5.79CD788F17C0D836180BD89730DB8F87] - 11/02/2015 - 23:33:56 ---A- . (.Microsoft Corporation - Outil de suppression de logiciels malveilla.) -- C:\Windows\System32\MRT.exe [113756392]
O44 - LFC:[MD5.4FD3763F3917201856B0CBCE310003EA] - 12/02/2015 - 18:32:12 ---A- . (.Microsoft Corporation - Microsoft (R) JScript.) -- C:\Windows\System32\jscript9.dll [4300800]
O44 - LFC:[MD5.01BD2653F2185218837CF4A175617F8A] - 12/02/2015 - 18:32:13 ---A- . (.Microsoft Corporation - Microsoft ® JScript Diagnostics.) -- C:\Windows\System32\jscript9diag.dll [620032]
O44 - LFC:[MD5.86FFF55A58999971CF8D6C0310C70ABB] - 12/02/2015 - 18:44:37 ---A- . (...) -- C:\Windows\System32\FNTCACHE.DAT [414664]
O44 - LFC:[MD5.864AA60174B5D8C86CA5A77E05B8ADF0] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\PerfStringBackup.INI [1669656]
O44 - LFC:[MD5.26B3FEB8BE950E0C381FF9F2CFF95F29] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\perfc009.dat [122700]
O44 - LFC:[MD5.AEE57061B6CE9943F90E9530E8B7D787] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\perfc00C.dat [150838]
O44 - LFC:[MD5.F70E11D738E3B145DBCE0F7DBC3A48CF] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\perfh009.dat [654828]
O44 - LFC:[MD5.F925A407FCDC1827E3BAC9ACAF270071] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\perfh00C.dat [749526]
O44 - LFC:[MD5.3B9E2AB1F3ABC53D4A423E699EB625C8] - 25/02/2015 - 19:54:28 ---A- . (...) -- C:\Windows\System32\locale.nls [419936]
O44 - LFC:[MD5.D41D8CD98F00B204E9800998ECF8427E] - 26/02/2015 - 19:42:27 ---A- . (...) -- C:\essai.txt [0]
O44 - LFC:[MD5.7D9CCE95A49F1A477FF66597D8982486] - 26/02/2015 - 21:33:34 ---A- . (...) -- C:\PhysicalDisk0_MBR.bin [512]
O44 - LFC:[MD5.A3F4391DFDF2F9E9FE4EAD193265A5AD] - 26/02/2015 - 22:42:20 ---A- . (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) -- C:\Windows\System32\Drivers\mbam.sys [23256]
O44 - LFC:[MD5.9BD41E40039098BF5F8FE878A9A6989E] - 26/02/2015 - 22:42:20 ---A- . (.Malwarebytes Corporation - Malwarebytes Chameleon Protection Driver.) -- C:\Windows\System32\Drivers\mbamchameleon.sys [75480]
O44 - LFC:[MD5.312CD3307F600E7CD340B79B3DCB3A01] - 26/02/2015 - 22:42:20 ---A- . (.Malwarebytes Corporation - Malwarebytes Web Access Control.) -- C:\Windows\System32\Drivers\mwac.sys [51928]
O44 - LFC:[MD5.8E2E9CCD873ABF180F48BCAEEEBE347D] - 26/02/2015 - 22:45:22 ---A- . (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) -- C:\Windows\System32\Drivers\MBAMSwissArmy.sys [114904]
O44 - LFC:[MD5.B21C914A3C8B930E9E703E3E49399A96] - 26/02/2015 -
-
-
Contributeuril est pas complet le rapport tu as oublié de l'héberger !
Merci !
Hebergement
Les rapports sont trop long ils dépassent la taille autorisée par les éditeurs de forums de sécurité
A Héberge le rapport ZHPDiag.txt sur : cjoint
B Cliques sur >> Parcourir (ou choisissez un fichier)
Cherche le rapport de ZHPDiag que tu viens de faire qui est sur ton bureau
C Cliques sur >> envoyer le fichier (ou créer le lien)
D Un lien sera généré, Un lien de cette forme: https://www.cjoint.com/index.php?file=cjge368/cijSKAP5fU.txt
E Il te suffit de le poster ici et uniquement ce lien
F Tutoriel explicatif de cjoint !
-
Contributeurdésinstalle le et retélécharge le !
-
-
-
C'est bon
3e ra~ Rapport de ZHPDiag v2015.2.23.23 - Nicolas Coolman (23/02/2015)
~ Lancé par remy (26/02/2015 21:32:25)
~ Facebook : https://www.facebook.com/nicolascoolman1
~ Adresse du Forum http://forum.nicolascoolman.fr
~ Traduit par Nicolas Coolman
~ Etat de la version : Version à jour.
~ Liste blanche : Désactivée par l'utilisateur
~ Elévation des Privilèges : OK
~ User Account Control (UAC): Deactivate by program
---\\ Navigateurs Internet
MSIE: Internet Explorer v11.0.9600.17633 (Defaut)
MFIE: Mozilla Firefox 23.0
GCIE: Google Chrome v40.0.2214.115
---\\ Informations sur les produits Windows
~ Langage: Français
Windows Server License Manager Script : OK
~ Windows Operating System - Windows(R) 7, OEM_SLP channel
System Locked Preinstallation (OEM_SLP) : OK
Windows ID Activation : OK
~ Windows Partial Key : HYRR2
Windows License : OK
~ Windows Remaining Initializations Number : 4
Software Protection Service (Protection logicielle) : OK
Windows Automatic Updates : OK
Windows Activation Technologies : OK
Windows 7 Ultimate, 32-bit Service Pack 1 (Build 7601)
---\\ Logiciels de protection du système
Microsoft Security Client v4.7.0205.0
Windows Defender W7 (Deactivate)
---\\ Logiciels d'optimisation du système
CCleaner v4.02
---\\ Logiciels de partage PeerToPeer
---\\ Surveillance de Logiciels
Adobe Flash Player 11 Plugin
Adobe Reader XI
---\\ Informations sur le système
~ Processor: x86 Family 15 Model 75 Stepping 2, AuthenticAMD
~ Operating System: 32 Bits
Boot mode: Normal (Normal boot)
Total RAM: 1983 MB (38% free)
System Restore: Activé (Enable)
System drive C: has 69 GB (51%) free of 136 GB
---\\ Mode de connexion au système
~ Computer Name: REMY-PC
~ User Name: remy
~ All Users Names: UpdatusUser, remy, HomeGroupUser$, Administrateur,
~ Unselected Option: None
Logged in as Administrator
---\\ Variables d'environnement
~ System Unit : C:\
~ %AppZHP% : C:\Users\remy\AppData\Roaming\ZHP\
~ %AppData% : C:\Users\remy\AppData\Roaming\
~ %Desktop% : C:\Users\remy\Desktop\
~ %Favorites% : C:\Users\remy\Favorites\
~ %LocalAppData% : C:\Users\remy\AppData\Local\
~ %StartMenu% : C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\
~ %Windir% : C:\Windows\
~ %System% : C:\Windows\System32\
---\\ Enumération des unités disques
A: Floppy drive, Flash card reader, USB Key (Not Inserted)
B: Hard drive, Flash drive, Thumb drive (Free 70 Go of 98 Go)
C: Hard drive, Flash drive, Thumb drive (Free 69 Go of 136 Go)
D: CD-ROM drive (Not Inserted)
E: Hard drive, Flash drive, Thumb drive (Free 35 Go of 59 Go)
F: Hard drive, Flash drive, Thumb drive (Free 47 Go of 94 Go)
H: Hard drive, Flash drive, Thumb drive (Free 506 Go of 932 Go)
J: Floppy drive, Flash card reader, USB Key (Not Inserted)
K: Floppy drive, Flash card reader, USB Key (Not Inserted)
L: Floppy drive, Flash card reader, USB Key (Not Inserted)
M: Floppy drive, Flash card reader, USB Key (Not Inserted)
---\\ Etat du Centre de Sécurité Windows
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiSpywareOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiVirusOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] FirewallOverride: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\system] EnableLUA: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\NOHIDDEN] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\SHOWALL] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Associations] Application: OK
[HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon] Shell: OK
[HKCU\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows] Load: OK
[HKLM\SYSTEM\CurrentControlSet\Services\COMSysApp] Type: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install] LastSuccessTime : OK
~ Security Center: 38 Scanned in 00mn 00s
---\\ Recherche particulière de fichiers génériques
[MD5.8B88EBBB05A0E56B7DCC708498C02B3E] - (.Microsoft Corporation - Explorateur Windows.) (.25/02/2011 - 06:30:54.) -- C:\Windows\Explorer.exe [2616320]
[MD5.B5C5DCAD3899512020D135600129D665] - (.Microsoft Corporation - Application de démarrage de Windows.) (.14/07/2009 - 02:14:45.) -- C:\Windows\System32\Wininit.exe [96256]
[MD5.F285D499EC42969D963CA49EADA63218] - (.Microsoft Corporation - Extensions Internet pour Win32.) (.12/01/2015 - 02:00:17.) -- C:\Windows\System32\wininet.dll [1888256]
[MD5.52449FD429D6053B78AE564DEF303870] - (.Microsoft Corporation - Application d'ouverture de session Windows.) (.17/07/2014 - 02:39:27.) -- C:\Windows\System32\Winlogon.exe [304128]
[MD5.E3AE23569749DE12D45BA3B489A036AE] - (.Microsoft Corporation - Bibliothèque de licences.) (.20/11/2010 - 13:21:24.) -- C:\Windows\System32\sppcomapi.dll [193536]
[MD5.D0B388DA1D111A34366E04EB4A5DD156] - (.Microsoft Corporation - Ancillary Function Driver for WinSock.) (.30/05/2014 - 07:36:07.) -- C:\Windows\system32\Drivers\AFD.sys [338944]
[MD5.338C86357871C167A96AB976519BF59E] - (.Microsoft Corporation - ATAPI IDE Miniport Driver.) (.14/07/2009 - 02:26:15.) -- C:\Windows\system32\Drivers\atapi.sys [21584]
[MD5.77EA11B065E0A8AB902D78145CA51E10] - (.Microsoft Corporation - CD-ROM File System Driver.) (.14/07/2009 - 00:11:15.) -- C:\Windows\system32\Drivers\Cdfs.sys [70656]
[MD5.BE167ED0FDB9C1FA1133953C18D5A6C9] - (.Microsoft Corporation - SCSI CD-ROM Driver.) (.20/11/2010 - 09:38:10.) -- C:\Windows\system32\Drivers\Cdrom.sys [108544]
[MD5.F024449C97EC1E464AAFFDA18593DB88] - (.Microsoft Corporation - DFS Namespace Client Driver.) (.20/11/2010 - 09:42:32.) -- C:\Windows\system32\Drivers\DfsC.sys [78336]
[MD5.9036377B8A6C15DC2EEC53E489D159B5] - (.Microsoft Corporation - High Definition Audio Bus Driver.) (.20/11/2010 - 10:59:29.) -- C:\Windows\system32\Drivers\HDAudBus.sys [108544]
[MD5.F151F0BDC47F4A28B1B20A0818EA36D6] - (.Microsoft Corporation - Pilote de port i8042.) (.14/07/2009 - 00:11:24.) -- C:\Windows\system32\Drivers\i8042prt.sys [80896]
[MD5.A5FA468D67ABCDAA36264E463A7BB0CD] - (.Microsoft Corporation - IP Network Address Translator.) (.14/07/2009 - 00:54:29.) -- C:\Windows\system32\Drivers\IpNat.sys [101888]
[MD5.5D16C921E3671636C0EBA3BBAAC5FD25] - (.Microsoft Corporation - Windows NT SMB Minirdr.) (.27/04/2011 - 03:17:22.) -- C:\Windows\system32\Drivers\MRxSmb.sys [123904]
[MD5.280122DDCF04B378EDD1AD54D71C1E54] - (.Microsoft Corporation - MBT Transport driver.) (.20/11/2010 - 09:39:44.) -- C:\Windows\system32\Drivers\netBT.sys [187904]
[MD5.C8DFF8D07755A66C7A4A738930F0FEAC] - (.Microsoft Corporation - Pilote du système de fichiers NT.) (.24/01/2014 - 03:18:22.) -- C:\Windows\system32\Drivers\ntfs.sys [1212352]
[MD5.2EA877ED5DD9713C5AC74E8EA7348D14] - (.Microsoft Corporation - Pilote de port parallèle.) (.14/07/2009 - 00:45:35.) -- C:\Windows\system32\Drivers\Parport.sys [79360]
[MD5.D9F91EAFEC2815365CBE6D167E4E332A] - (.Microsoft Corporation - RAS L2TP mini-port/call-manager driver.) (.14/07/2009 - 00:54:34.) -- C:\Windows\system32\Drivers\Rasl2tp.sys [78848]
[MD5.B973FCFC50DC1434E1970A146F7E3885] - (.Microsoft Corporation - Microsoft RDP Device redirector.) (.20/11/2010 - 11:24:46.) -- C:\Windows\system32\Drivers\rdpdr.sys [133632]
[MD5.3E21C083B8A01CB70BA1F09303010FCE] - (.Microsoft Corporation - SMB Transport driver.) (.14/07/2009 - 00:53:41.) -- C:\Windows\system32\Drivers\smb.sys [71168]
[MD5.7FE680A3DFA421C4A8E4879AE4C5AAB0] - (.Microsoft Corporation - TDI Translation Driver.) (.11/11/2014 - 02:32:14.) -- C:\Windows\system32\Drivers\tdx.sys [74752]
[MD5.F497F67932C6FA693D7DE2780631CFE7] - (.Microsoft Corporation - Pilote de cliché instantané du volume.) (.20/11/2010 - 13:30:16.) -- C:\Windows\system32\Drivers\volsnap.sys [245632]
~ Generic Processes: Scanned in 00mn 00s
---\\ Etat des fichiers cachés (Caché/Total)
~ Mes images (My Pictures) : 3/15
~ Mes musiques (My Musics) : 8/18
~ Mes Videos (My Videos) : 1/2
~ Mes Favoris (My Favorites) : 1/64
~ Mes Documents (My Documents) : 1/358
~ Mon Bureau (My Desktop) : 1/6957
~ Menu demarrer (Programs) : 1/40
~ Hidden Files: Scanned in 00mn 00s
---\\ Processus lancés
[MD5.A2418D3C557C0A0C634DA713A8AC3789] - (.Logitech Inc. - Logitech Webcam Software.) -- C:\Program Files\Logitech\LWS\Webcam Software\LWS.exe [205336] [PID.1992]
[MD5.6E70704C2568ED01CDDF6291F5043763] - (.CANON INC. - Canon My Printer.) -- C:\Program Files\Canon\MyPrinter\BJMYPRT.exe [2569616] [PID.2028]
[MD5.6521891B67EAD77CAFD877D8A24ED769] - (.CANON INC. - Canon Solution Menu EX.) -- C:\Program Files\Canon\Solution Menu EX\CNSEMAIN.exe [1213848] [PID.2040]
[MD5.D3570ACC178180AC0D7C24645461A9D3] - (.CANON INC. - Canon IJ Network Scanner Selector EX.) -- C:\Program Files\Canon\IJ Network Scanner Selector EX\CNMNSST.exe [452016] [PID.308]
[MD5.550B8CB98A8FA1D7A1A7371055A38DDA] - (...) -- C:\Program Files\Logitech\LWS\Webcam Software\CameraHelperShell.exe [265240] [PID.328]
[MD5.B776DFE408E415AA901030C022EEB7DA] - (.NVIDIA Corporation - NVIDIA Settings.) -- C:\Program Files\NVIDIA Corporation\Display\nvtray.exe [1821472] [PID.2192]
[MD5.902054D6B4292329F9594FFF24EE02DB] - (...) -- C:\Program Files\Common Files\Logishrd\LQCVFX\COCIManager.exe [680984] [PID.2208]
[MD5.591C3AD6C5A54FDB90D3B406C945EE28] - (...) -- C:\ProgramData\{89c85052-2a23-cc44-89c8-850522a24148}\L Equipe Magazine N 1701 du 21 fevrier 2015.pdf.exe [1069256] [PID.2532]
[MD5.28F667911C25649637C0F5AADF660134] - (...) -- C:\Program Files\HTC\HTC Sync Manager\HTC Sync\adb.exe [169312] [PID.2828]
[MD5.363BC25BACB34E9D40441968B1B3D5BE] - (.Microsoft Corporation - Internet Explorer.) -- C:\Program Files\Internet Explorer\iexplore.exe [815288] [PID.5992]
[MD5.7B29C3CE3B2CB870C7B29FFBBFE61E60] - (.Adobe Systems Incorporated - Adobe® Flash® Player Installer/Uninstaller.) -- C:\Windows\system32\Macromed\Flash\FlashUtil32_16_0_0_296_ActiveX.exe [960688] [PID.2684]
[MD5.C4F2424A0671907FD3AC44EBE43C3C66] - (.Microsoft Corporation - Microsoft Spell Checking Facility.) -- C:\Windows\System32\MsSpellCheckingFacility.exe [667648] [PID.4904]
[MD5.472D170E4E1FEED584616E08CFB0F1EF] - (.Nicolas Coolman - ZHPDiag.) -- C:\Program Files\ZHPDiag\ZHPDiag.exe [8179200] [PID.8892]
~ Processes Running: Scanned in 00mn 00s
---\\ Mozilla Firefox, Plugins,Demarrage,Recherche,Extensions (P2,M0,M1,M2,M3)
C:\Users\remy\AppData\Roaming\Mozilla\Firefox\Profiles\2tefea1k.default\prefs.js
P2 - FPN: [HKLM] [@adobe.com/FlashPlayer] - (...) -- C:\Windows\system32\Macromed\Flash\NPSWF32_11_4_402_278.dll
P2 - FPN: [HKLM] [@canon.com/EPPEX] - (.CANON INC. - CANON iMAGE GATEWAY Album Plugin Utility Module.) -- C:\Program Files\Canon\Easy-PhotoPrint EX\NPEZFFPI.dll
P2 - FPN: [HKLM] [@Google.com/GoogleEarthPlugin] - (.Google - GEPlugin.) -- C:\Program Files\Google\Google Earth\plugin\npgeplugin.dll =>.Google Inc
P2 - FPN: [HKLM] [@google.com/npPicasa3,version=3.0.0] - (.Google, Inc. - Picasa plugin.) -- C:\Program Files\Google\Picasa3\npPicasa3.dll
P2 - FPN: [HKLM] [@java.com/DTPlugin,version=11.31.2] - (.Oracle Corporation - NPRuntime Script Plug-in Library for Java(TM) Deploy.) -- C:\Program Files\Java\jre1.8.0_31\bin\dtplugin\npDeployJava1.dll
P2 - FPN: [HKLM] [@java.com/JavaPlugin,version=11.31.2] - (.Oracle Corporation - Next Generation Java Plug-in 11.31.2 for Mozilla browsers.) -- C:\Program Files\Java\jre1.8.0_31\bin\plugin2\npjp2.dll
P2 - FPN: [HKLM] [@Microsoft.com/NpCtrl,version=1.0] - (. Microsoft Corporation - 5.1.31211.0.) -- C:\Program Files\Microsoft Silverlight\5.1.31211.0\npctrl.dll
P2 - FPN: [HKLM] [@microsoft.com/WLPG,version=15.4.3502.0922] - (.Microsoft Corporation - NPWLPG.) -- C:\Program Files\Windows Live\Photo Gallery\NPWLPG.dll
P2 - FPN: [HKLM] [@microsoft.com/WLPG,version=15.4.3538.0513] - (.Microsoft Corporation - NPWLPG.) -- C:\Program Files\Windows Live\Photo Gallery\NPWLPG.dll
P2 - FPN: [HKLM] [@microsoft.com/WLPG,version=16.4.3505.0912] - (.Microsoft Corporation - NPWLPG.) -- C:\Program Files\Windows Live\Photo Gallery\NPWLPG.dll
P2 - FPN: [HKLM] [@real.com/nprpchromebrowserrecordext;version=15.0.6.14] - (.RealNetworks, Inc. - RealNetworks(tm) RealPlayer Chrome Background Extension Plug-In.) -- C:\ProgramData\Real\RealPlayer\BrowserRecordPlugin\MozillaPlugins\nprpchromebrowserrecordext.dll
P2 - FPN: [HKLM] [@real.com/nprphtml5videoshim;version=15.0.6.14] - (.RealNetworks, Inc. - RealPlayer(tm) HTML5VideoShim Plug-In.) -- C:\ProgramData\Real\RealPlayer\BrowserRecordPlugin\MozillaPlugins\nprphtml5videoshim.dll
P2 - FPN: [HKLM] [@tools.google.com/Google Update;version=3] - (.Google Inc. - Google Update.) -- C:\Program Files\Google\Update\1.3.26.9\npGoogleUpdate3.dll
P2 - FPN: [HKLM] [@tools.google.com/Google Update;version=9] - (.Google Inc. - Google Update.) -- C:\Program Files\Google\Update\1.3.26.9\npGoogleUpdate3.dll
P2 - FPN: [HKLM] [@videolan.org/vlc,version=2.0.7] - (.VideoLAN - VLC media player Web Plugin 2.1.3.) -- C:\Program Files\VideoLAN\VLC\npvlc.dll =>.VideoLAN
P2 - FPN: [HKLM] [@videolan.org/vlc,version=2.1.3] - (.VideoLAN - VLC media player Web Plugin 2.1.3.) -- C:\Program Files\VideoLAN\VLC\npvlc.dll =>.VideoLAN
P2 - FPN: [HKLM] [@videolan.org/vlc,version=2.1.5] - (.VideoLAN - VLC media player Web Plugin 2.1.3.) -- C:\Program Files\VideoLAN\VLC\npvlc.dll =>.VideoLAN
P2 - FPN: [HKLM] [Adobe Reader] - (.Adobe Systems Inc. - Adobe PDF Plug-In For Firefox and Netscape 11.0.10.) -- C:\Program Files\Adobe\Reader 11.0\Reader\AIR\nppdf32.dll
~ Firefox Browser: 18 Scanned in 00mn 00s
---\\ Internet Explorer, Démarrage,Recherche,URLSearchHook, Phishing (R0,R1,R3,R4)
R0 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://www.google.fr
R0 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://www.google.com
R1 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com
R1 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = http://www.google.com
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = http://www.google.com
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Extensions Off Page = about:noadd-ons
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Security Risk Page = about:securityrisk
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\AboutURLs,Tabs = http://www.google.com
R3 - URLSearchHook: (no name) - {5bcf818d-78c8-41b8-ba89-65c5fdac4fc4} . (.Adobe Systems Inc. - Adobe PDF Plug-In For Firefox and Netscape 11.0.10.) (No version) -- (.not file.)
R3 - URLSearchHook: Microsoft Url Search Hook - {CFBFAE00-17A6-11D0-99CB-00C04FD64497} . (.Adobe Systems Inc. - Adobe PDF Plug-In For Firefox and Netscape 11.0.10.) (No version) -- (.not file.)
R4 - HKLM\SOFTWARE\Microsoft\Internet Explorer\PhishingFilter,EnabledV8 = 1
~ IE Browser: 13 Scanned in 00mn 00s
---\\ Internet Explorer, Proxy Management (R5)
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = no key
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyEnable = 0
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,MigrateProxy = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,EnableHttp1_1 = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyHttp1.1 = 0
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,AutoConfigProxy = wininet.dll
~ Proxy management: Scanned in 00mn 00s
---\\ Analyse des lignes F0, F1, F2, F3 - IniFiles, Autoloading programs
F2 - REG:system.ini: USERINIT=C:\Windows\system32\userinit.exe,
F2 - REG:system.ini: Shell=C:\Windows\explorer.exe
F2 - REG:system.ini: VMApplet=C:\Windows\System32\SystemPropertiesPerformance.exe
~ Keys: Scanned in 00mn 00s
---\\ Hosts file redirection (O1)
~ Le fichier hôte est sain (The hosts file is clean) (21)
~ Hosts File: Scanned in 00mn 00s
---\\ Internet Explorer Toolbars (O3)
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{71576546-354D-41C9-AAE8-31F2EC22BF0D} Clé orpheline
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{56444A2D-5637-006A-76A7-7A786E7484D7} Clé orpheline
~ Toolbar: Scanned in 00mn 00s
---\\ Autres liens utilisateurs (O4)
O4 - GS\Desktop [remy]: µTorrent.lnk . (.BitTorrent Inc. - µTorrent.) -- C:\Users\remy\AppData\Roaming\uTorrent\uTorrent.exe =>P2P.BitTorrent
~ Global Startup: 1 Scanned in 00mn 01s
---\\ Applications lancées au démarrage du système (O4)
O4 - HKLM\..\Run: [LWS] . (.Logitech Inc. - Logitech Webcam Software.) -- C:\Program Files\Logitech\LWS\Webcam Software\LWS.exe =>.Logitech Inc
O4 - HKLM\..\Run: [CanonMyPrinter] . (.CANON INC. - Canon My Printer.) -- C:\Program Files\Canon\MyPrinter\BJMyPrt.exe
O4 - HKLM\..\Run: [CanonSolutionMenuEx] . (.CANON INC. - Canon Solution Menu EX.) -- C:\Program Files\Canon\Solution Menu EX\CNSEMAIN.exe
O4 - HKLM\..\Run: [IJNetworkScannerSelectorEX] . (.CANON INC. - Canon IJ Network Scanner Selector EX.) -- C:\Program Files\Canon\IJ Network Scanner Selector EX\CNMNSST.exe
O4 - HKLM\..\Run: [MSC] . (.Microsoft Corporation - Microsoft Security Client User Interface.) -- C:\Program Files\Microsoft Security Client\msseces.exe
O4 - HKLM\..\Run: [APSDaemon] C:\Program Files\Common Files\Apple\Apple Application Support\APSDaemon.exe (.not file.)
O4 - HKLM\..\Run: [Allin1Convert EPM Support] C:\Program Files\ALLIN1~2\bar\1.bin\8hmedint.exe (.not file.) =>Adware.Allin1Convert
O4 - HKLM\..\Run: [Allin1Convert AppIntegrator 32-bit] C:\Program Files\ALLIN1~2\bar\1.bin\AppIntegrator.exe (.not file.) =>Adware.Allin1Convert
O4 - HKCU\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files\Windows Sidebar\sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-19\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-19\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-21-1214120938-4103684180-1072874238-1000\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files\Windows Sidebar\sidebar.exe =>.Microsoft Corporation
~ Application: Scanned in 00mn 00s
---\\ Invisibilité de l'icône d'options IE dans le panneau de Configuration (O5)
O5 - control.ini: [HKLM\..\Control Panel] inetcpl.cpl=no
~ IE Control Panel: 1 Scanned in 00mn 00s
---\\ Boutons situés sur la barre d'outils principale d'Internet Explorer (O9)
O9 - Extra button: @C:\Program Files\Windows Live\Writer\WindowsLiveWriterShortcuts.dll,-1003 - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} . (.Microsoft Corporation - Windows Live Writer Blog This Extension.) -- C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} . (...) -- C:\Program Files\Microsoft Office\Office12\REFBARH.ICO
~ IE Extra Buttons: Scanned in 00mn 00s
---\\ Winsock hijacker (Layered Service Provider) (O10)
O10 - WLSP:\000000000001\Winsock LSP File . (.Microsoft Corporation - Network Location Awareness 2.) -- C:\Windows\system32\NLAapi.dll
O10 - WLSP:\000000000002\Winsock LSP File . (.Microsoft Corporation - Fournisseur Shim d'affectation de noms de messagerie.) -- C:\Windows\system32\napinsp.dll
O10 - WLSP:\000000000003\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000004\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000005\Winsock LSP File . (.Microsoft Corporation - Fournisseur de service Sockets 2.0 de Microsoft Windows.) -- C:\Windows\system32\mswsock.dll =>.Microsoft Corporation
O10 - WLSP:\000000000006\Winsock LSP File . (.Microsoft Corporation - LDAP RnR Provider DLL.) -- C:\Windows\system32\winrnr.dll
O10 - WLSP:\000000000007\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
O10 - WLSP:\000000000008\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
~ Winsock: 8 Scanned in 00mn 00s
---\\ Objets ActiveX (Downloaded Program Files)(O16)
O16 - DPF: Garmin Communicator Plug-In (Garmin Communicator Plug-In) - https://static.garmincdn.com/gcp/ie/4.0.3.0/GarminAxControl_32.CAB
O16 - DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} ((no name)) - http://fpdownload2.macromedia.com/get/shockwave/cabs/flash/swflash.cab
~ Objets ActiveX: Scanned in 00mn 00s
---\\ Modification Domaine/Adresses DNS (O17)
O17 - HKLM\System\CCS\Services\Tcpip\..\{AF98B48B-0BAC-418A-8237-AE0AD93B453A}: DhcpNameServer = 192.168.42.129
O17 - HKLM\System\CCS\Services\Tcpip\..\{B71CD3C7-0BF8-462F-8164-2BCFD1421D8E}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CCS\Services\Tcpip\..\{D5894A53-BF97-4ED2-8B89-319AF4A6BF7F}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CS1\Services\Tcpip\..\{AF98B48B-0BAC-418A-8237-AE0AD93B453A}: DhcpNameServer = 192.168.42.129
O17 - HKLM\System\CS1\Services\Tcpip\..\{B71CD3C7-0BF8-462F-8164-2BCFD1421D8E}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CS1\Services\Tcpip\..\{D5894A53-BF97-4ED2-8B89-319AF4A6BF7F}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CS2\Services\Tcpip\..\{AF98B48B-0BAC-418A-8237-AE0AD93B453A}: DhcpNameServer = 192.168.42.129
O17 - HKLM\System\CS2\Services\Tcpip\..\{B71CD3C7-0BF8-462F-8164-2BCFD1421D8E}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CS2\Services\Tcpip\..\{D5894A53-BF97-4ED2-8B89-319AF4A6BF7F}: DhcpNameServer = 89.2.0.1 89.2.0.2
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = 89.2.0.1 89.2.0.2
~ Domain: Scanned in 00mn 00s
---\\ Protocole additionnel (O18)
O18 - Handler: wot - {C2A44D6B-CB9F-4663-88A6-DF2F26E4D952} . (...) -- C:\Program Files\WOT\WOT.dll
O18 - Filter: text/xml - {807563E5-5146-11D5-A672-00B0D022E945} . (.Microsoft Corporation - Microsoft Office XML MIME Filter.) -- C:\Program Files\Common Files\microsoft shared\OFFICE12\MSOXMLMF.dll =>.Microsoft Corporation
~ Protocole Additionnel: Scanned in 00mn 00s
---\\ Clé de Registre autorun ShellServiceObjectDelayLoad (SSO/SSODL) (O21)
O21 - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} - CLSID or File not found.
~ SSODL: 1 Scanned in 00mn 00s
---\\ Liste des services NT non Microsoft et non désactivés (O23)
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) . (.Adobe Systems Incorporated - Adobe Acrobat Update Service.) - C:\Program Files\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: SystemSafeguard (f6082713) . (...) - c:\Program Files\SystemSafeguard\SystemSafeguard.dll
O23 - Service: Service Google Update (gupdate) (gupdate) . (.Google Inc. - Programme d'installation de Google.) - C:\Program Files\Google\Update\GoogleUpdate.exe =>.Google Inc
O23 - Service: HTCMonitorService (HTCMonitorService) . (.Nero AG - NService Application.) - C:\Program Files\HTC\HTC Sync Manager\HSMServiceEntry.exe
O23 - Service: Canon Inkjet Printer/Scanner/Fax Extended Survey Program (IJPLMSVC) . (.Pas de propriétaire - Inkjet Printer/Scanner/Fax Extended Survey.) - C:\Program Files\Canon\IJPLM\IJPLMSVC.exe
O23 - Service: NVIDIA Display Driver Service (nvsvc) . (.NVIDIA Corporation - NVIDIA Driver Helper Service, Version 307.8.) - C:\Windows\system32\nvvsvc.exe
O23 - Service: NVIDIA Update Service Daemon (nvUpdatusService) . (.NVIDIA Corporation - NVIDIA Settings Update Manager.) - C:\Program Files\NVIDIA Corporation\NVIDIA Update Core\daemonu.exe
O23 - Service: Internet Pass-Through Service (PassThru Service) . (.Pas de propriétaire - PassThruSvr Application.) - C:\Program Files\HTC\Internet Pass-Through\PassThruSvr.exe
O23 - Service: Skype Updater (SkypeUpdate) . (.Skype Technologies - Skype Updater Service.) - C:\Program Files\Skype\Updater\Updater.exe
~ Services: 9 Scanned in 00mn 03s
---\\ Enumération Active Desktop & MHTML Editor (O24)
O24 - Default MHTML Editor: Last - .(...) - (.not file.)
~ Desktop Component: 4 Scanned in 00mn 00s
---\\ Enumère les données de BootExecute (BEX) (O34)
O34 - HKLM BootExecute: (autocheck autochk *) - File not found
~ BEX: 1 Scanned in 00mn 00s
---\\ Tâches planifiées en automatique (O39)
[MD5.3E04F1E482357B1FC8B088197C3D9FF8] [APT] [Adobe Acrobat Update Task] (.Adobe Systems Incorporated.) -- C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe [1022152]
[MD5.518545E8CBD79EBF42891A6066578118] [APT] [CCleanerSkipUAC] (.Piriform Ltd.) -- C:\Program Files\CCleaner\CCleaner.exe [3591960]
[MD5.506708142BC63DABA64F2D3AD1DCD5BF] [APT] [GoogleUpdateTaskMachineCore] (.Google Inc..) -- C:\Program Files\Google\Update\GoogleUpdate.exe [116648]
[MD5.506708142BC63DABA64F2D3AD1DCD5BF] [APT] [GoogleUpdateTaskMachineUA] (.Google Inc..) -- C:\Program Files\Google\Update\GoogleUpdate.exe [116648]
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderDownloaderScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (...) -- C:\Program Files\RealNetworks\RealDownloader\recordingmanager.exe (.not file.) [0]
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderRealUpgradeLogonTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (...) -- C:\Program Files\RealNetworks\RealDownloader\realupgrade.exe (.not file.) [0]
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderRealUpgradeScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (...) -- C:\Program Files\RealNetworks\RealDownloader\realupgrade.exe (.not file.) [0]
[MD5.A2530419BF7607A13698A6D07F89550B] [APT] [RealPlayerRealUpgradeLogonTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (.RealNetworks, Inc..) -- C:\Program Files\Real\RealUpgrade\RealUpgrade.exe [141312]
[MD5.A2530419BF7607A13698A6D07F89550B] [APT] [RealPlayerRealUpgradeScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (.RealNetworks, Inc..) -- C:\Program Files\Real\RealUpgrade\RealUpgrade.exe [141312]
[MD5.A2530419BF7607A13698A6D07F89550B] [APT] [RealUpgradeLogonTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (.RealNetworks, Inc..) -- C:\Program Files\Real\RealUpgrade\RealUpgrade.exe [141312]
[MD5.A2530419BF7607A13698A6D07F89550B] [APT] [RealUpgradeScheduledTaskS-1-5-21-1214120938-4103684180-1072874238-1000] (.RealNetworks, Inc..) -- C:\Program Files\Real\RealUpgrade\RealUpgrade.exe [141312]
[MD5.8880B530B309F297EE99F3178E60DD5E] [APT] [{FBC97478-91E3-4C60-A558-EBA432C3062A}] (.Atomix Productions.) -- C:\Program Files\VirtualDJ\virtualdj_broadcaster.exe [14499328]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineCore.job [1054]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineCore [1054]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineUA.job [1058]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineUA [1058]
~ Scheduled Task: 15 Scanned in 00mn 02s
---\\ Composants installés (ActiveSetup Installed Components) (O40)
O40 - ASIC: Microsoft Windows Media Player - >{22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Microsoft Windows Media Player 12.0 - {22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Windows Media Player Extension.) -- C:\Windows\System32\wmpdxm.dll =>.Microsoft Corporation
O40 - ASIC: Themes Setup - {2C7339CF-2B09-4501-B3F3-F3508C9228ED} . (.Microsoft Corporation - API Windows Theme.) -- C:\Windows\System32\themeui.dll
O40 - ASIC: Internet Explorer - {2D46B6DC-2207-486B-B523-A557E6D54B47} . (.Microsoft Corporation - Interpréteur de commandes Windows.) -- C:\Windows\system32\cmd.exe =>.Microsoft Corporation
O40 - ASIC: Microsoft Windows - {44BBA840-CC51-11CF-AAFA-00AA00B6015C} . (.Microsoft Corporation - Windows Mail.) -- C:\Program Files\Windows Mail\WinMail.exe =>.Microsoft Corporation
O40 - ASIC: Browsing Enhancements - {630b1da0-b465-11d1-9948-00c04f98bbc9} . (.Microsoft Corporation - Extension Shell dossier FTP Microsoft Internet Explorer..) -- C:\Windows\System32\msieftp.dll
O40 - ASIC: Microsoft Windows Media Player - {6BF52A52-394A-11d3-B153-00C04F79FAA6} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Windows Desktop Update - {89820200-ECBD-11cf-8B85-00AA005B4340} . (.Microsoft Corporation - DLL commune du shell Windows.) -- C:\Windows\System32\shell32.dll
O40 - ASIC: Web Platform Customizations - {89820200-ECBD-11cf-8B85-00AA005B4383} . (.Microsoft Corporation - Utilitaire d'initialisation d'Internet Explorer par utilisateur.) -- C:\Windows\System32\ie4uinit.exe
O40 - ASIC: (no name) - {89B4C1CD-B018-4511-B0A1-5476DBF70820} . (.Microsoft Corporation - Microsoft .NET IE SECURITY REGISTRATION.) -- C:\Windows\system32\mscories.dll
O40 - ASIC: Google Chrome - {8A69D345-D564-463c-AFF1-A69D9E530F96} . (.Google Inc. - Google Chrome Installer.) -- C:\Program Files\Google\Chrome\Application\40.0.2214.115\Installer\chrmstp.exe
~ Active Setup: 11 Scanned in 00mn 00s
---\\ Pilotes lancés au démarrage du système (O41)
O41 - Driver: C:\Windows\System32\drivers\afd.sys (AFD) . (.Microsoft Corporation - Ancillary Function Driver for WinSock.) - C:\Windows\system32\drivers\afd.sys
O41 - Driver: (blbdrive) . (.Microsoft Corporation - BLB Drive Driver.) - C:\Windows\System32\DRIVERS\blbdrive.sys
O41 - Driver: (cdrom) . (.Microsoft Corporation - SCSI CD-ROM Driver.) - C:\Windows\System32\DRIVERS\cdrom.sys
O41 - Driver: C:\Windows\System32\cscsvc.dll (CSC) . (.Microsoft Corporation - Windows Client Side Caching Driver.) - C:\Windows\System32\drivers\csc.sys
O41 - Driver: C:\Windows\System32\drivers\dfsc.sys (DfsC) . (.Microsoft Corporation - DFS Namespace Client Driver.) - C:\Windows\System32\Drivers\dfsc.sys
O41 - Driver: C:\Windows\System32\drivers\discache.sys (discache) . (.Microsoft Corporation - System Indexer/Cache Driver.) - C:\Windows\System32\drivers\discache.sys
O41 - Driver: (MpKsl2593c2bc) . (.Microsoft Corporation - KSLDriver.) - C:\ProgramData\Microsoft\Microsoft Antimalware\Definition Updates\{9184CDCB-D27A-421D-954B-69D88208652B}\MpKsl2593c2bc.sys
O41 - Driver: (mssmbios) . (.Microsoft Corporation - System Management BIOS Driver.) - C:\Windows\system32\drivers\mssmbios.sys
O41 - Driver: (NetBIOS) . (.Microsoft Corporation - NetBIOS interface driver.) - C:\Windows\System32\DRIVERS\netbios.sys
O41 - Driver: C:\Windows\System32\drivers\netbt.sys (NetBT) . (.Microsoft Corporation - MBT Transport driver.) - C:\Windows\System32\DRIVERS\netbt.sys
O41 - Driver: C:\Windows\System32\drivers\nsiproxy.sys (nsiproxy) . (.Microsoft Corporation - NSI Proxy.) - C:\Windows\System32\drivers\nsiproxy.sys
O41 - Driver: C:\Windows\System32\drivers\pacer.sys (Psched) . (.Microsoft Corporation - Planificateur de paquets QoS.) - C:\Windows\System32\DRIVERS\pacer.sys
O41 - Driver: C:\Windows\System32\wkssvc.dll (rdbss) . (.Microsoft Corporation - Pilote du sous-système de mise en mémoire t.) - C:\Windows\System32\DRIVERS\rdbss.sys
O41 - Driver: C:\Windows\System32\DRIVERS\RDPCDD.sys (RDPCDD) . (.Microsoft Corporation - RDP Miniport.) - C:\Windows\System32\DRIVERS\RDPCDD.sys
O41 - Driver: C:\Windows\System32\drivers\RDPENCDD.sys (RDPENCDD) . (.Microsoft Corporation - RDP Encoder Miniport.) - C:\Windows\System32\drivers\rdpencdd.sys
O41 - Driver: C:\Windows\System32\drivers\RdpRefMp.sys (RDPREFMP) . (.Microsoft Corporation - RDP Reflector Driver Miniport.) - C:\Windows\System32\drivers\rdprefmp.sys
O41 - Driver: (Serial) . (.Brother Industries Ltd. - Pilote Brother Série I/F (WDM).) - C:\Windows\System32\DRIVERS\serial.sys
O41 - Driver: C:\Windows\System32\tcpipcfg.dll (tdx) . (.Microsoft Corporation - TDI Translation Driver.) - C:\Windows\System32\DRIVERS\tdx.sys
O41 - Driver: (TermDD) . (.Microsoft Corporation - Remote Desktop Server Driver.) - C:\Windows\system32\drivers\termdd.sys
O41 - Driver: (VgaSave) . (.Microsoft Corporation - VGA/Super VGA Video Driver.) - C:\Windows\system32\drivers\vga.sys
O41 - Driver: (vpcnfltr) . (.Microsoft Corporation - Virtual PC Network Filter Driver.) - C:\Windows\System32\DRIVERS\vpcnfltr.sys
O41 - Driver: C:\Windows\System32\drivers\vpcvmm.sys (vpcvmm) . (.Microsoft Corporation - Moniteur d'ordinateur virtuel Virtual PC.) - C:\Windows\System32\drivers\vpcvmm.sys
O41 - Driver: C:\Windows\System32\rascfg.dll (Wanarpv6) . (.Microsoft Corporation - MS Remote Access and Routing ARP Driver.) - C:\Windows\System32\DRIVERS\wanarp.sys
O41 - Driver: (WfpLwf) . (.Microsoft Corporation - WFP NDIS 6.20 Lightweight Filter Driver.) - C:\Windows\System32\DRIVERS\wfplwf.sys
~ Drivers: 71 Scanned in 00mn 00s
---\\ Logiciels installés (O42)
O42 - Logiciel: Adobe Digital Editions - (...) [HKLM] -- Digital Editions
O42 - Logiciel: Adobe Flash Player 11 Plugin - (.Adobe Systems Incorporated.) [HKLM] -- Adobe Flash Player Plugin
O42 - Logiciel: Adobe Flash Player 16 ActiveX - (.Adobe Systems Incorporated.) [HKLM] -- Adobe Flash Player ActiveX
O42 - Logiciel: Adobe Reader XI (11.0.10) - Français - (.Adobe Systems Incorporated.) [HKLM] -- {AC76BA86-7AD7-1036-7B44-AB0000000001}
O42 - Logiciel: Adobe Refresh Manager - (.Adobe Systems Incorporated.) [HKLM] -- {AC76BA86-0804-1033-1959-001802114130}
O42 - Logiciel: AxCrypt 1.7.2976.0 - (.Axantum Software AB.) [HKLM] -- {38350E9E-D50E-454A-BAFC-58BBDDBE08C4}
O42 - Logiciel: CCleaner - (.Piriform.) [HKLM] -- CCleaner
O42 - Logiciel: CameraHelperMsi - (.Logitech.) [HKLM] -- {15634701-BACE-4449-8B25-1567DA8C9FD3}
O42 - Logiciel: Canon Easy-PhotoPrint EX - (...) [HKLM] -- Easy-PhotoPrint EX
O42 - Logiciel: Canon Easy-WebPrint EX - (...) [HKLM] -- Easy-WebPrint EX
O42 - Logiciel: Canon IJ Network Scanner Selector EX - (...) [HKLM] -- Canon_IJ_Network_Scanner_Selector_EX
O42 - Logiciel: Canon IJ Network Tool - (...) [HKLM] -- Canon_IJ_Network_UTILITY
O42 - Logiciel: Canon Inkjet Printer/Scanner/Fax Extended Survey Program - (...) [HKLM] -- CANONIJPLM100
O42 - Logiciel: Canon MP Navigator EX 4.1 - (...) [HKLM] -- MP Navigator EX 4.1
O42 - Logiciel: Canon MX420 series MP Drivers - (...) [HKLM] -- {1199FAD5-9546-44f3-81CF-FFDB8040B7BF}_Canon_MX420_series
O42 - Logiciel: Canon My Printer - (...) [HKLM] -- CanonMyPrinter
O42 - Logiciel: Canon Solution Menu EX - (...) [HKLM] -- CanonSolutionMenuEX
O42 - Logiciel: Canon Utilitaire de numérotation rapide - (...) [HKLM] -- Speed Dial Utility
O42 - Logiciel: D3DX10 - (.Microsoft.) [HKLM] -- {E09C4DB7-630C-4F06-A631-8EA7239923AF}
O42 - Logiciel: Enregistrement utilisateur de Canon MX420 series - (...) [HKLM] -- Enregistrement utilisateur de Canon MX420 series =>.Canon Inc
O42 - Logiciel: Galerie de photos - (.Microsoft Corporation.) [HKLM] -- {446CC8CE-0E90-44F7-ADD0-774B243EF090}
O42 - Logiciel: Google Chrome - (.Google Inc..) [HKLM] -- Google Chrome
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM] -- {60EC980A-BDA2-4CB6-A427-B07A5498B4CA}
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM] -- {A92DAB39-4E2C-4304-9AB6-BC44E68B55E2}
O42 - Logiciel: Google Earth - (.Google.) [HKLM] -- {4D2A6330-2F8B-11E3-9C40-B8AC6F97B88E}
O42 - Logiciel: HTC Sync Manager - (.HTC.) [HKLM] -- {5002C5B1-B688-474A-AB3A-9B65DBD38FF9}
O42 - Logiciel: IPTInstaller - (.HTC.) [HKLM] -- {08208143-777D-4A06-BB54-71BF0AD1BB70}
O42 - Logiciel: Java 8 Update 31 - (.Oracle Corporation.) [HKLM] -- {26A24AE4-039D-4CA4-87B4-2F83218031F0}
O42 - Logiciel: Junk Mail filter update - (.Microsoft Corporation.) [HKLM] -- {400C31E4-796F-4E86-8FDC-C3C4FACC6847}
O42 - Logiciel: LWS Facebook - (.Logitech.) [HKLM] -- {FF167195-9EE4-46C0-8CD7-FBA3457E88AB}
O42 - Logiciel: LWS Gallery - (.Logitech.) [HKLM] -- {6F76EC3C-34B1-436E-97FB-48C58D7BEDCD}
O42 - Logiciel: LWS Help_main - (.Logitech.) [HKLM] -- {1651216E-E7AD-4250-92A1-FB8ED61391C9}
O42 - Logiciel: LWS Launcher - (.Logitech.) [HKLM] -- {83C8FA3C-F4EA-46C4-8392-D3CE353738D6}
O42 - Logiciel: LWS Motion Detection - (.Logitech.) [HKLM] -- {71E66D3F-A009-44AB-8784-75E2819BA4BA}
O42 - Logiciel: LWS Pictures And Video - (.Logitech.) [HKLM] -- {08610298-29AE-445B-B37D-EFBE05802967}
O42 - Logiciel: LWS Twitter - (.Logitech.) [HKLM] -- {174A3B31-4C43-43DD-866F-73C9DB887B48}
O42 - Logiciel: LWS Video Mask Maker - (.Logitech.) [HKLM] -- {EED027B7-0DB6-404B-8F45-6DFEE34A0441}
O42 - Logiciel: LWS VideoEffects - (.Logitech.) [HKLM] -- {138A4072-9E64-46BD-B5F9-DB2BB395391F}
O42 - Logiciel: LWS WLM Plugin - (.Logitech.) [HKLM] -- {9DAEA76B-E50F-4272-A595-0124E826553D}
O42 - Logiciel: LWS Webcam Software - (.Logitech.) [HKLM] -- {8937D274-C281-42E4-8CDB-A0B2DF979189}
O42 - Logiciel: LWS YouTube Plugin - (.Logitech.) [HKLM] -- {21DF0294-6B9D-4741-AB6F-B2ABFBD2387E}
O42 - Logiciel: Logitech Webcam Software - (.Logitech Inc..) [HKLM] -- {D40EB009-0499-459c-A8AF-C9C110766215} =>.Logitech Inc
O42 - Logiciel: MSVCRT - (.Microsoft.) [HKLM] -- {8DD46C6A-0056-4FEC-B70A-28BB16A1F11F}
O42 - Logiciel: MSVCRT110 - (.Microsoft.) [HKLM] -- {8E14DDC8-EA60-4E18-B3E3-1937104D5BDA}
O42 - Logiciel: MSXML 4.0 SP2 (KB954430) - (.Microsoft Corporation.) [HKLM] -- {86493ADD-824D-4B8E-BD72-8C5DCDC52A71}
O42 - Logiciel: MSXML 4.0 SP2 (KB973688) - (.Microsoft Corporation.) [HKLM] -- {F662A8E6-F4DC-41A2-901E-8C11F044BDEC}
O42 - Logiciel: Microsoft OneDrive - (.Microsoft Corporation.) [HKCU] -- OneDriveSetup.exe
O42 - Logiciel: Microsoft Security Client - (.Microsoft Corporation.) [HKLM] -- {D6F9CBDC-58B6-430A-8DD4-8F61CBC1ADF4}
O42 - Logiciel: Microsoft Security Essentials - (.Microsoft Corporation.) [HKLM] -- Microsoft Security Client
O42 - Logiciel: Microsoft Silverlight - (.Microsoft Corporation.) [HKLM] -- {89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}
O42 - Logiciel: Mises à jour NVIDIA 1.10.8 - (.NVIDIA Corporation.) [HKLM] -- {B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.Update
O42 - Logiciel: Mozilla Firefox 23.0 (x86 fr) - (.Mozilla.) [HKLM] -- Mozilla Firefox 23.0 (x86 fr)
O42 - Logiciel: Mozilla Maintenance Service - (.Mozilla.) [HKLM] -- MozillaMaintenanceService
O42 - Logiciel: NVIDIA Pilote graphique 307.83 - (.NVIDIA Corporation.) [HKLM] -- {B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.Driver
O42 - Logiciel: PDFCreator - (.Frank Heindörfer, Philip Chinery.) [HKLM] -- {0001B4FD-9EA3-4D90-A79E-FD14BA3AB01D}
O42 - Logiciel: Picasa 3 - (.Google, Inc..) [HKLM] -- Picasa 3
O42 - Logiciel: RealUpgrade 1.1 - (.RealNetworks, Inc..) [HKLM] -- {28C2DED6-325B-4CC7-983A-1777C8F7FBAB}
O42 - Logiciel: Security Update for CAPICOM (KB931906) - (.Microsoft Corporation.) [HKLM] -- KB931906
O42 - Logiciel: Security Update for CAPICOM (KB931906) - (.Microsoft Corporation.) [HKLM] -- {0EFDF2F9-836D-4EB7-A32D-038BD3F1FB2A}
O42 - Logiciel: Skype(TM) 7.1 - (.Skype Technologies S.A..) [HKLM] -- {24991BA0-F0EE-44AD-9CC8-5EC50AECF6B7}
O42 - Logiciel: VLC media player - (.VideoLAN.) [HKLM] -- VLC media player =>.VideoLAN
O42 - Logiciel: Virtual DJ Packages - (...) [HKCU] -- Virtual DJ Packages
O42 - Logiciel: VirtualDJ 8 - (.Atomix Productions.) [HKLM] -- {13E44DA9-FE06-4298-9179-BEF27214B47B}
O42 - Logiciel: VirtualDJ Broadcaster - (.Atomix Productions.) [HKLM] -- {3575B758-28E1-4AA8-AFC4-D597CC4C7B14}
O42 - Logiciel: VirtualDJ Home FREE - (.Atomix Productions.) [HKLM] -- {EE9E75F0-1FB8-440A-A34A-058F7456E113}
O42 - Logiciel: WOT for Internet Explorer - (.WOT Services Oy.) [HKLM] -- {DCAEC601-735C-41AE-B84F-D792F09FB7D1}
O42 - Logiciel: WinRAR 4.00 (32 bits) - (.win.rar GmbH.) [HKLM] -- WinRAR archiver
O42 - Logiciel: erLT - (.Logitech, Inc..) [HKLM] -- {3EE9BCAE-E9A9-45E5-9B1C-83A4D357E05C}
O42 - Logiciel: scrabbleproB 1.1.3 - (.scrabblepro.) [HKLM] -- scrabbleproB_is1
O42 - Logiciel: µTorrent - (.BitTorrent Inc..) [HKCU] -- uTorrent =>P2P.BitTorrent
~ Logic: 41 Scanned in 00mn 00s
---\\ HKCU & HKLM Software Keys
[HKCU\Software\Adobe]
[HKCU\Software\AppDataLow\Software\Against Intuition]
[HKCU\Software\AppDataLow\Software\Canon]
[HKCU\Software\AppDataLow\Software\JavaSoft]
[HKCU\Software\AppDataLow\Software\RealNetworks]
[HKCU\Software\AppDataLow]
[HKCU\Software\Apple Computer, Inc.]
[HKCU\Software\Apple Inc.]
[HKCU\Software\Axantum]
[HKCU\Software\BitTorrent] =>P2P.BitTorrent
[HKCU\Software\Canon]
[HKCU\Software\Classes]
[HKCU\Software\Clients]
[HKCU\Software\Convertir.co]
[HKCU\Software\Fast Folder Access]
[HKCU\Software\FreeTime]
[HKCU\Software\Freecom]
[HKCU\Software\Freemake]
[HKCU\Software\GNU]
[HKCU\Software\Gabest]
[HKCU\Software\Garmin]
[HKCU\Software\GlarySoft]
[HKCU\Software\Google]
[HKCU\Software\HTC]
[HKCU\Software\Haali]
[HKCU\Software\HookNetwork]
[HKCU\Software\IM Providers]
[HKCU\Software\JavaSoft]
[HKCU\Software\Leadertech]
[HKCU\Software\Licenses]
[HKCU\Software\LogiShrd]
[HKCU\Software\Logitech]
[HKCU\Software\Macromedia]
[HKCU\Software\Macrovision]
[HKCU\Software\MozillaPlugins]
[HKCU\Software\Mozilla]
[HKCU\Software\NVIDIA Corporation]
[HKCU\Software\Nero]
[HKCU\Software\Netscape]
[HKCU\Software\ODBC]
[HKCU\Software\Orange]
[HKCU\Software\PDFCreator]
[HKCU\Software\Piriform]
[HKCU\Software\Policies]
[HKCU\Software\RealNetworks]
[HKCU\Software\Reg]
[HKCU\Software\Sarbakan]
[HKCU\Software\Skype]
[HKCU\Software\TeleCharger]
[HKCU\Software\TeleCharger_v2]
[HKCU\Software\Trolltech]
[HKCU\Software\TuneUp]
[HKCU\Software\VB and VBA Program Settings]
[HKCU\Software\VirtualDJ]
[HKCU\Software\WebApp]
[HKCU\Software\WinRAR SFX]
[HKCU\Software\WinRAR]
[HKCU\Software\Wow6432Node]
[HKCU\Software\ZebHelpProcess Helper]
[HKCU\Software\redsn0w]
[HKLM\Software\ATI Technologies]
[HKLM\Software\Adobe]
[HKLM\Software\AdwCleaner]
[HKLM\Software\Apple Computer, Inc.]
[HKLM\Software\Apple Inc.]
[HKLM\Software\Axantum]
[HKLM\Software\CDDB]
[HKLM\Software\Canon]
[HKLM\Software\Classes]
[HKLM\Software\Clients]
[HKLM\Software\DivXNetworks]
[HKLM\Software\Electronic Arts]
[HKLM\Software\Freemake]
[HKLM\Software\GEAR Software]
[HKLM\Software\GNU]
[HKLM\Software\Garmin]
[HKLM\Software\GlarySoft]
[HKLM\Software\Google]
[HKLM\Software\HTC]
[HKLM\Software\HaaliMkx]
[HKLM\Software\IM Providers]
[HKLM\Software\Intel]
[HKLM\Software\JavaSoft]
[HKLM\Software\JreMetrics]
[HKLM\Software\Khronos]
[HKLM\Software\Logitech]
[HKLM\Software\Macromedia]
[HKLM\Software\MozillaPlugins]
[HKLM\Software\Mozilla]
[HKLM\Software\NVIDIA Corporation]
[HKLM\Software\Nero]
[HKLM\Software\ODBC]
[HKLM\Software\PDFCreator]
[HKLM\Software\Piriform]
[HKLM\Software\Policies]
[HKLM\Software\Promolettres]
[HKLM\Software\RealNetworks]
[HKLM\Software\Reg]
[HKLM\Software\RegisteredApplications]
[HKLM\Software\Skype]
[HKLM\Software\Sonic]
[HKLM\Software\Symantec]
[HKLM\Software\TuneUp]
[HKLM\Software\VideoLAN]
[HKLM\Software\VirtualDJ]
[HKLM\Software\WinRAR]
[HKLM\Software\Windows]
[HKLM\Software\Wow6432Node]
[HKLM\Software\Xing Technology Corp.]
[HKLM\Software\logishrd]
[HKLM\Software\mozilla.org]
~ Key Software: 224 Scanned in 00mn 00s
---\\ Contenu des dossiers Programs/ProgramFiles/ProgramData/AppData (O43)
O43 - CFD: 07/07/2014 - 22:02:59 - [] ----D C:\Program Files\Adobe
O43 - CFD: 30/12/2013 - 21:24:56 - [] ----D C:\Program Files\Axantum
O43 - CFD: 21/12/2011 - 12:43:29 - [] ----D C:\Program Files\Canon
O43 - CFD: 21/12/2011 - 12:31:39 - [] --H-D C:\Program Files\CanonBJ
O43 - CFD: 15/06/2013 - 10:33:22 - [] ----D C:\Program Files\CCleaner
O43 - CFD: 29/01/2015 - 21:21:25 - [] ----D C:\Program Files\Common Files
O43 - CFD: 12/07/2014 - 19:26:13 - [] ----D C:\Program Files\Convertisseur MP3
O43 - CFD: 16/10/2014 - 21:14:46 - [] ----D C:\Program Files\Convertisseur YouTube
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\DVD Maker
O43 - CFD: 29/07/2012 - 07:16:49 - [] ----D C:\Program Files\EA SPORTS
O43 - CFD: 30/12/2013 - 21:22:51 - [] ----D C:\Program Files\Fast Folder Access
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\Program Files\Fichiers communs
O43 - CFD: 12/07/2014 - 19:27:48 - [] ----D C:\Program Files\Freemake
O43 - CFD: 12/07/2014 - 19:28:04 - [0] ----D C:\Program Files\FreeTime
O43 - CFD: 12/12/2013 - 20:25:46 - [] ----D C:\Program Files\Google
O43 - CFD: 13/07/2013 - 08:34:26 - [] ----D C:\Program Files\HTC
O43 - CFD: 05/10/2014 - 14:18:23 - [] ----D C:\Program Files\Intelore
O43 - CFD: 12/02/2015 - 18:18:06 - [] ----D C:\Program Files\Internet Explorer
O43 - CFD: 29/01/2015 - 21:21:57 - [] ----D C:\Program Files\Java
O43 - CFD: 11/12/2011 - 11:18:35 - [] ----D C:\Program Files\Logitech
O43 - CFD: 16/12/2011 - 08:22:28 - [] ----D C:\Program Files\Microsoft CAPICOM 2.1.0.2
O43 - CFD: 14/07/2009 - 08:50:24 - [] ----D C:\Program Files\Microsoft Games
O43 - CFD: 21/02/2012 - 23:46:04 - [] ----D C:\Program Files\Microsoft Office
O43 - CFD: 11/02/2015 - 23:27:43 - [] ----D C:\Program Files\Microsoft Security Client
O43 - CFD: 14/12/2014 - 10:43:20 - [] ----D C:\Program Files\Microsoft Silverlight
O43 - CFD: 18/02/2013 - 22:40:24 - [] ----D C:\Program Files\Microsoft SkyDrive =>.Microsoft Corporation
O43 - CFD: 07/12/2011 - 21:07:11 - [] ----D C:\Program Files\Microsoft SQL Server Compact Edition
O43 - CFD: 07/12/2011 - 19:55:15 - [] ----D C:\Program Files\Microsoft Visual Studio
O43 - CFD: 07/12/2011 - 19:51:23 - [] ----D C:\Program Files\Microsoft Visual Studio 8
O43 - CFD: 18/12/2011 - 03:03:15 - [] ----D C:\Program Files\Microsoft Works
O43 - CFD: 08/12/2011 - 00:58:34 - [] ----D C:\Program Files\Microsoft.NET
O43 - CFD: 03/01/2012 - 22:50:22 - [] ----D C:\Program Files\Movie Maker
O43 - CFD: 03/01/2012 - 22:55:30 - [] ----D C:\Program Files\Movie Maker 2.6
O43 - CFD: 07/08/2013 - 20:15:14 - [] ----D C:\Program Files\Mozilla Firefox
O43 - CFD: 05/01/2014 - 09:18:54 - [] ----D C:\Program Files\Mozilla Maintenance Service
O43 - CFD: 07/12/2011 - 19:55:33 - [] ----D C:\Program Files\MSBuild
O43 - CFD: 14/07/2013 - 00:49:39 - [0] ----D C:\Program Files\MSXML 4.0
O43 - CFD: 14/04/2013 - 21:07:27 - [] ----D C:\Program Files\NVIDIA Corporation
O43 - CFD: 15/06/2013 - 14:12:32 - [] ----D C:\Program Files\PDFCreator
O43 - CFD: 17/01/2015 - 13:34:03 - [] ----D C:\Program Files\Real
O43 - CFD: 17/10/2014 - 17:30:14 - [0] ----D C:\Program Files\Recuva
O43 - CFD: 14/07/2009 - 05:52:30 - [] ----D C:\Program Files\Reference Assemblies
O43 - CFD: 11/12/2011 - 12:06:37 - [] ----D C:\Program Files\scrabbleproB
O43 - CFD: 11/10/2012 - 19:17:05 - [] ----D C:\Program Files\scrabbleproB1.1
O43 - CFD: 21/02/2015 - 20:42:50 - [] R---D C:\Program Files\Skype
O43 - CFD: 22/02/2015 - 16:37:43 - [] ----D C:\Program Files\SystemSafeguard
O43 - CFD: 14/07/2009 - 05:53:23 - [0] --H-D C:\Program Files\Uninstall Information
O43 - CFD: 21/12/2011 - 19:42:48 - [] ----D C:\Program Files\VideoLAN
O43 - CFD: 26/01/2015 - 21:25:37 - [] ----D C:\Program Files\VirtualDJ
O43 - CFD: 13/06/2013 - 21:09:12 - [] ----D C:\Program Files\Webplayer decompression
O43 - CFD: 10/07/2013 - 06:00:54 - [] ----D C:\Program Files\Windows Defender
O43 - CFD: 11/07/2014 - 10:17:12 - [] ----D C:\Program Files\Windows Journal
O43 - CFD: 01/05/2013 - 07:32:46 - [] ----D C:\Program Files\Windows Live
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\Windows Mail =>.Microsoft Corporation
O43 - CFD: 13/12/2013 - 06:13:27 - [] ----D C:\Program Files\Windows Media Player =>.Microsoft Corporation
O43 - CFD: 07/12/2011 - 19:35:47 - [] ----D C:\Program Files\Windows NT
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\Windows Photo Viewer
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\Windows Portable Devices
O43 - CFD: 18/12/2011 - 08:49:35 - [] ----D C:\Program Files\Windows Sidebar
O43 - CFD: 31/07/2009 - 15:53:45 - [] ----D C:\Program Files\Windows Virtual PC
O43 - CFD: 07/12/2011 - 19:42:33 - [] ----D C:\Program Files\WinRAR
O43 - CFD: 13/06/2013 - 21:05:31 - [] ----D C:\Program Files\WordBiz
O43 - CFD: 15/06/2013 - 14:24:15 - [] ----D C:\Program Files\WOT
O43 - CFD: 26/02/2015 - 21:31:30 - [] ----D C:\Program Files\ZHPDiag =>.Nicolas Coolman
O43 - CFD: 07/07/2014 - 22:03:25 - [] ----D C:\Program Files\Common Files\Adobe
O43 - CFD: 21/12/2011 - 12:37:13 - [] ----D C:\Program Files\Common Files\CANON
O43 - CFD: 15/05/2014 - 00:15:40 - [] ----D C:\Program Files\Common Files\DESIGNER
O43 - CFD: 29/01/2015 - 21:21:25 - [] ----D C:\Program Files\Common Files\Java
O43 - CFD: 15/02/2013 - 23:41:52 - [] ----D C:\Program Files\Common Files\logishrd
O43 - CFD: 11/12/2011 - 11:17:23 - [] ----D C:\Program Files\Common Files\LWS
O43 - CFD: 13/07/2013 - 08:32:43 - [] ----D C:\Program Files\Common Files\microsoft shared
O43 - CFD: 13/07/2013 - 08:35:03 - [] ----D C:\Program Files\Common Files\Nero
O43 - CFD: 02/12/2012 - 21:49:19 - [0] ----D C:\Program Files\Common Files\Promolettres
O43 - CFD: 12/12/2011 - 00:42:12 - [] ----D C:\Program Files\Common Files\Real
O43 - CFD: 14/07/2009 - 03:37:05 - [] ----D C:\Program Files\Common Files\Services
O43 - CFD: 17/01/2015 - 13:36:05 - [] ----D C:\Program Files\Common Files\Skype
O43 - CFD: 14/07/2009 - 03:37:05 - [] ----D C:\Program Files\Common Files\SpeechEngines
O43 - CFD: 11/07/2012 - 07:04:45 - [] ----D C:\Program Files\Common Files\System
O43 - CFD: 07/12/2011 - 20:57:21 - [] ----D C:\Program Files\Common Files\Windows Live
O43 - CFD: 12/07/2014 - 19:33:53 - [] ----D C:\ProgramData\188F1432-103A-4ffb-80F1-36B633C5C9E1
O43 - CFD: 07/07/2014 - 22:03:05 - [] ----D C:\ProgramData\Adobe
O43 - CFD: 12/07/2014 - 19:35:42 - [] ----D C:\ProgramData\Apple
O43 - CFD: 19/01/2012 - 08:35:51 - [] ----D C:\ProgramData\Apple Computer
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Application Data
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\ProgramData\Bureau
O43 - CFD: 21/12/2011 - 12:40:42 - [0] ----D C:\ProgramData\Canon IJ Network Tool
O43 - CFD: 21/12/2011 - 12:32:32 - [] --H-D C:\ProgramData\CanonBJ
O43 - CFD: 21/12/2011 - 12:43:30 - [0] --H-D C:\ProgramData\CanonEPP
O43 - CFD: 23/12/2011 - 10:25:24 - [] ----D C:\ProgramData\CanonIJ
O43 - CFD: 16/07/2012 - 20:59:55 - [] --H-D C:\ProgramData\CanonIJEGV
O43 - CFD: 04/09/2012 - 20:06:03 - [] --H-D C:\ProgramData\CanonIJEPPEX
O43 - CFD: 21/12/2011 - 12:43:30 - [0] --H-D C:\ProgramData\CanonIJEPPEX2
O43 - CFD: 21/12/2011 - 12:40:27 - [] --H-D C:\ProgramData\CanonIJFAX
O43 - CFD: 21/12/2011 - 12:43:29 - [] --H-D C:\ProgramData\CanonIJMyPrinter
O43 - CFD: 03/02/2015 - 18:24:01 - [] ----D C:\ProgramData\CanonIJPLM
O43 - CFD: 23/12/2011 - 10:23:57 - [] --H-D C:\ProgramData\CanonIJScan
O43 - CFD: 21/12/2011 - 12:43:31 - [] --H-D C:\ProgramData\CanonIJSolutionMenuEX
O43 - CFD: 21/12/2011 - 12:37:04 - [] ----D C:\ProgramData\CanonIJWSpt
O43 - CFD: 03/06/2013 - 05:55:23 - [] --H-D C:\ProgramData\Common Files
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Desktop
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Documents
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\ProgramData\Favoris
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Favorites
O43 - CFD: 12/07/2014 - 19:27:51 - [0] ----D C:\ProgramData\Freemake
O43 - CFD: 13/07/2013 - 08:44:16 - [] ----D C:\ProgramData\HTC
O43 - CFD: 11/12/2011 - 11:16:32 - [] ----D C:\ProgramData\LogiShrd
O43 - CFD: 11/12/2011 - 11:17:28 - [] ----D C:\ProgramData\Logitech
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\ProgramData\Menu Démarrer
O43 - CFD: 10/12/2014 - 19:25:31 - [] -S--D C:\ProgramData\Microsoft
O43 - CFD: 11/02/2015 - 23:31:40 - [] ----D C:\ProgramData\Microsoft Help
O43 - CFD: 19/09/2014 - 13:18:45 - [] ----D C:\ProgramData\Microsoft OneDrive
O43 - CFD: 18/02/2013 - 22:40:01 - [] ----D C:\ProgramData\Microsoft SkyDrive =>.Microsoft Corporation
O43 - CFD: 07/12/2011 - 19:35:47 - [] -SH-D C:\ProgramData\Modèles
O43 - CFD: 13/07/2013 - 08:35:22 - [] ----D C:\ProgramData\Motorola
O43 - CFD: 27/10/2012 - 18:33:29 - [] ----D C:\ProgramData\Mozilla
O43 - CFD: 14/04/2013 - 21:07:36 - [] ----D C:\ProgramData\NVIDIA
O43 - CFD: 14/04/2013 - 21:05:52 - [] ----D C:\ProgramData\NVIDIA Corporation
O43 - CFD: 29/01/2015 - 21:23:44 - [] ----D C:\ProgramData\Oracle
O43 - CFD: 17/01/2015 - 13:33:56 - [] ----D C:\ProgramData\Real
O43 - CFD: 21/02/2015 - 20:42:57 - [] ----D C:\ProgramData\Skype
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Start Menu
O43 - CFD: 07/12/2011 - 22:42:03 - [] ----D C:\ProgramData\Sun
O43 - CFD: 14/07/2009 - 05:53:55 - [] -SH-D C:\ProgramData\Templates
O43 - CFD: 03/06/2013 - 05:55:46 - [] ----D C:\ProgramData\TuneUp Software
O43 - CFD: 07/12/2011 - 19:43:02 - [] ----D C:\ProgramData\XsRXTfiwSUdn
O43 - CFD: 19/01/2012 - 08:36:24 - [] ----D C:\ProgramData\{429CAD59-35B1-4DBC-BB6D-1DB246563521}
O43 - CFD: 22/02/2015 - 16:22:26 - [] ----D C:\ProgramData\{4896dc69-39e0-8578-4896-6dc6939e71a4}
O43 - CFD: 24/02/2015 - 19:42:34 - [] ----D C:\ProgramData\{89c85052-2a23-cc44-89c8-850522a24148}
O43 - CFD: 03/06/2013 - 05:55:23 - [] -SH-D C:\ProgramData\{C4ABDBC8-1C81-42C9-BFFC-4A68511E9E4F}
O43 - CFD: 03/01/2012 - 22:49:47 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Accessoires
O43 - CFD: 12/12/2011 - 00:35:05 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Accessories
O43 - CFD: 07/12/2011 - 19:33:12 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Administrative Tools
O43 - CFD: 01/05/2012 - 13:46:11 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Adobe
O43 - CFD: 30/12/2013 - 21:25:00 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Axantum AxCrypt
O43 - CFD: 21/12/2011 - 12:32:29 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Canon MX420 series
O43 - CFD: 21/12/2011 - 12:33:15 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Canon MX420 series Manual
O43 - CFD: 21/12/2011 - 12:40:53 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Canon Utilities
O43 - CFD: 15/06/2013 - 10:33:22 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\CCleaner
O43 - CFD: 21/12/2011 - 12:38:59 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Enregistrement utilisateur de Canon MX420 series =>.Canon Inc
O43 - CFD: 30/12/2013 - 21:22:50 - [0] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Fast Folder Access
O43 - CFD: 07/12/2011 - 19:33:12 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Games
O43 - CFD: 14/06/2013 - 19:10:22 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Chrome
O43 - CFD: 12/12/2013 - 20:25:55 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Earth =>.Google Inc
O43 - CFD: 28/07/2014 - 20:16:45 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\HTC
O43 - CFD: 29/01/2015 - 21:20:26 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Java
O43 - CFD: 15/02/2013 - 23:41:54 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Logitech
O43 - CFD: 14/07/2009 - 05:42:30 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Maintenance
O43 - CFD: 19/12/2011 - 03:05:10 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Office
O43 - CFD: 14/12/2014 - 02:00:00 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Silverlight
O43 - CFD: 23/12/2011 - 10:43:15 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\PDFCreator
O43 - CFD: 10/09/2012 - 22:59:41 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Picasa 3
O43 - CFD: 05/10/2014 - 14:18:24 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\RAR Password Recovery
O43 - CFD: 11/12/2011 - 12:06:37 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\scrabbleproB
O43 - CFD: 11/10/2012 - 19:17:05 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\scrabbleproB1.1
O43 - CFD: 17/01/2015 - 13:36:06 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Skype
O43 - CFD: 17/01/2015 - 13:33:42 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup
O43 - CFD: 14/07/2009 - 08:48:45 - [0] R-H-D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Tablet PC
O43 - CFD: 25/06/2014 - 19:37:55 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\VideoLAN
O43 - CFD: 18/02/2013 - 23:07:44 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Windows Live
O43 - CFD: 07/12/2011 - 19:33:12 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Windows Virtual PC
O43 - CFD: 07/12/2011 - 19:42:33 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\WinRAR
O43 - CFD: 26/02/2015 - 21:31:30 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\ZHP =>.Nicolas Coolman
O43 - CFD: 13/06/2013 - 21:06:02 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Zylom
O43 - CFD: 01/05/2012 - 13:51:56 - [] ----D C:\Users\remy\AppData\Roaming\Adobe
O43 - CFD: 13/07/2013 - 08:35:30 - [] ----D C:\Users\remy\AppData\Roaming\Apple Computer
O43 - CFD: 11/09/2013 - 07:02:17 - [] ----D C:\Users\remy\AppData\Roaming\Canon
O43 - CFD: 24/07/2013 - 22:36:07 - [] ----D C:\Users\remy\AppData\Roaming\Convertisseur MP3
O43 - CFD: 25/07/2013 - 18:10:59 - [] ----D C:\Users\remy\AppData\Roaming\Convertisseur YouTube
O43 - CFD: 14/09/2012 - 09:51:42 - [] ----D C:\Users\remy\AppData\Roaming\Garmin
O43 - CFD: 11/02/2012 - 15:38:40 - [] ----D C:\Users\remy\AppData\Roaming\GlarySoft
O43 - CFD: 13/07/2013 - 08:44:32 - [] ----D C:\Users\remy\AppData\Roaming\HTC
O43 - CFD: 13/07/2013 - 08:44:23 - [] ----D C:\Users\remy\AppData\Roaming\HTC Sync
O43 - CFD: 07/12/2011 - 19:36:09 - [] ----D C:\Users\remy\AppData\Roaming\Identities
O43 - CFD: 11/12/2011 - 11:18:37 - [] ----D C:\Users\remy\AppData\Roaming\Leadertech
O43 - CFD: 07/12/2011 - 19:43:06 - [] ----D C:\Users\remy\AppData\Roaming\lJQXCOOdhkcB
O43 - CFD: 07/12/2011 - 19:49:55 - [] ----D C:\Users\remy\AppData\Roaming\Macromedia
O43 - CFD: 14/07/2009 - 08:48:45 - [0] ----D C:\Users\remy\AppData\Roaming\Media Center Programs
O43 - CFD: 02/11/2013 - 09:39:01 - [] -S--D C:\Users\remy\AppData\Roaming\Microsoft
O43 - CFD: 15/06/2013 - 14:30:11 - [] ----D C:\Users\remy\AppData\Roaming\Mozilla
O43 - CFD: 19/10/2014 - 09:30:26 - [] ----D C:\Users\remy\AppData\Roaming\Oracle
O43 - CFD: 17/01/2015 - 13:33:39 - [] ----D C:\Users\remy\AppData\Roaming\Real
O43 - CFD: 08/08/2013 - 19:13:05 - [0] ----D C:\Users\remy\AppData\Roaming\redsn0w
O43 - CFD: 21/02/2015 - 20:44:07 - [] ----D C:\Users\remy\AppData\Roaming\Skype
O43 - CFD: 03/06/2013 - 05:55:46 - [] ----D C:\Users\remy\AppData\Roaming\TuneUp Software
O43 - CFD: 22/02/2015 - 14:15:28 - [] ----D C:\Users\remy\AppData\Roaming\uTorrent =>P2P.µTorrent
O43 - CFD: 22/02/2015 - 14:52:25 - [] ----D C:\Users\remy\AppData\Roaming\vlc
O43 - CFD: 07/12/2011 - 19:42:52 - [] ----D C:\Users\remy\AppData\Roaming\WinRAR
O43 - CFD: 26/02/2015 - 21:32:46 - [] ----D C:\Users\remy\AppData\Roaming\ZHP =>.Nicolas Coolman
O43 - CFD: 30/12/2014 - 19:43:48 - [] ----D C:\Users\remy\AppData\Local\Adobe
O43 - CFD: 19/01/2012 - 08:35:11 - [] ----D C:\Users\remy\AppData\Local\Apple
O43 - CFD: 13/07/2013 - 08:35:30 - [] ----D C:\Users\remy\AppData\Local\Apple Computer
O43 - CFD: 07/12/2011 - 19:35:54 - [] -SH-D C:\Users\remy\AppData\Local\Application Data
O43 - CFD: 03/01/2012 - 21:05:21 - [] ----D C:\Users\remy\AppData\Local\Apps
O43 - CFD: 02/03/2014 - 18:17:20 - [] ----D C:\Users\remy\AppData\Local\Canon Easy-PhotoPrint EX
O43 - CFD: 03/01/2012 - 21:05:32 - [0] ----D C:\Users\remy\AppData\Local\Deployment
O43 - CFD: 10/02/2015 - 20:41:57 - [] ----D C:\Users\remy\AppData\Local\Diagnostics
O43 - CFD: 13/07/2013 - 08:31:54 - [] ----D C:\Users\remy\AppData\Local\Downloaded Installations
O43 - CFD: 14/11/2014 - 18:24:02 - [] -SH-D C:\Users\remy\AppData\Local\EmieBrowserModeList
O43 - CFD: 10/04/2014 - 08:14:22 - [] -SH-D C:\Users\remy\AppData\Local\EmieSiteList
O43 - CFD: 10/04/2014 - 08:14:22 - [] -SH-D C:\Users\remy\AppData\Local\EmieUserList
O43 - CFD: 17/04/2014 - 10:39:50 - [] ----D C:\Users\remy\AppData\Local\FreemakeVideoDownloader
O43 - CFD: 14/06/2013 - 19:10:24 - [] ----D C:\Users\remy\AppData\Local\Google
O43 - CFD: 07/12/2011 - 19:35:54 - [] -SH-D C:\Users\remy\AppData\Local\Historique
O43 - CFD: 26/02/2015 - 19:01:30 - [] ----D C:\Users\remy\AppData\Local\HTC MediaHub
O43 - CFD: 11/12/2011 - 11:23:25 - [] ----D C:\Users\remy\AppData\Local\Logitech® Webcam Software
O43 - CFD: 27/10/2012 - 12:47:07 - [] ----D C:\Users\remy\AppData\Local\Macromedia
O43 - CFD: 17/07/2014 - 22:46:18 - [] ----D C:\Users\remy\AppData\Local\Microsoft
O43 - CFD: 18/08/2014 - 14:02:45 - [] ----D C:\Users\remy\AppData\Local\Microsoft Games
O43 - CFD: 07/12/2011 - 19:50:34 - [0] ----D C:\Users\remy\AppData\Local\Microsoft Help
O43 - CFD: 11/02/2012 - 19:36:21 - [] ----D C:\Users\remy\AppData\Local\Mozilla
O43 - CFD: 01/11/2012 - 22:53:42 - [] ----D C:\Users\remy\AppData\Local\Programs
O43 - CFD: 06/03/2014 - 07:55:44 - [] ----D C:\Users\remy\AppData\Local\Skype
O43 - CFD: 26/02/2015 - 21:32:14 - [] ----D C:\Users\remy\AppData\Local\Temp
O43 - CFD: 07/12/2011 - 19:35:54 - [] -SH-D C:\Users\remy\AppData\Local\Temporary Internet Files
O43 - CFD: 30/12/2013 - 21:21:00 - [] ----D C:\Users\remy\AppData\Local\VirtualStore
O43 - CFD: 01/05/2013 - 06:43:55 - [] ----D C:\Users\remy\AppData\Local\Windows Live
O43 - CFD: 08/01/2012 - 17:39:45 - [] ----D C:\Users\remy\AppData\Local\WMTools Downloaded Files
O43 - CFD: 12/12/2011 - 00:42:10 - [] R---D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories
O43 - CFD: 15/08/2014 - 10:16:03 - [] R---D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Administrative Tools
O43 - CFD: 14/07/2009 - 05:37:42 - [] R---D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Maintenance
O43 - CFD: 22/02/2015 - 16:36:05 - [] R---D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup
O43 - CFD: 26/01/2015 - 21:25:42 - [] ----D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\VirtualDJ
O43 - CFD: 07/12/2011 - 19:42:33 - [] ----D C:\Users\remy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\WinRAR
~ Program Folder: 223 Scanned in 00mn 00s
---\\ Derniers fichiers modifiés ou crées sous Windows et System32 (O44)
O44 - LFC:[MD5.E185BDA84E5F03F4E1D8DCA30E209277] - 11/02/2015 - 23:28:23 ---A- . (...) -- C:\Windows\epplauncher.mif [1912]
O44 - LFC:[MD5.79CD788F17C0D836180BD89730DB8F87] - 11/02/2015 - 23:33:56 ---A- . (.Microsoft Corporation - Outil de suppression de logiciels malveilla.) -- C:\Windows\System32\MRT.exe [113756392]
O44 - LFC:[MD5.29EB6A5ACB708A293DA959D3A2E9C322] - 12/02/2015 - 18:17:58 ---A- . (...) -- C:\Windows\PFRO.log [71320]
O44 - LFC:[MD5.4FD3763F3917201856B0CBCE310003EA] - 12/02/2015 - 18:32:12 ---A- . (.Microsoft Corporation - Microsoft (R) JScript.) -- C:\Windows\System32\jscript9.dll [4300800]
O44 - LFC:[MD5.01BD2653F2185218837CF4A175617F8A] - 12/02/2015 - 18:32:13 ---A- . (.Microsoft Corporation - Microsoft ® JScript Diagnostics.) -- C:\Windows\System32\jscript9diag.dll [620032]
O44 - LFC:[MD5.86FFF55A58999971CF8D6C0310C70ABB] - 12/02/2015 - 18:44:37 ---A- . (...) -- C:\Windows\System32\FNTCACHE.DAT [414664]
O44 - LFC:[MD5.864AA60174B5D8C86CA5A77E05B8ADF0] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\PerfStringBackup.INI [1669656]
O44 - LFC:[MD5.26B3FEB8BE950E0C381FF9F2CFF95F29] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\perfc009.dat [122700]
O44 - LFC:[MD5.AEE57061B6CE9943F90E9530E8B7D787] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\perfc00C.dat [150838]
O44 - LFC:[MD5.F70E11D738E3B145DBCE0F7DBC3A48CF] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\perfh009.dat [654828]
O44 - LFC:[MD5.F925A407FCDC1827E3BAC9ACAF270071] - 22/02/2015 - 14:18:12 ---A- . (...) -- C:\Windows\System32\perfh00C.dat [749526]
O44 - LFC:[MD5.3B9E2AB1F3ABC53D4A423E699EB625C8] - 25/02/2015 - 19:54:28 ---A- . (...) -- C:\Windows\System32\locale.nls [419936]
O44 - LFC:[MD5.B15B67A896A8975DD908269949682F2A] - 26/02/2015 - 19:00:50 -S-A- . (...) -- C:\Windows\bootstat.dat [67584]
O44 - LFC:[MD5.A5551690E3A5D1DDE1844674023888AB] - 26/02/2015 - 19:01:09 ---A- . (...) -- C:\Windows\setupact.log [69590]
O44 - LFC:[MD5.D41D8C
-
-
ContributeurBonjour,
je m'appelle buckhulk et nous allons essayer de régler ton soucis.
si tu as un problème avec un outil ou autre , parles-en ....
Commence par faire ce qui est indiqué dessous en suivant bien les tutos :
ZHPcleaner
Désactiver ton Antivirus
-
Ton moteur de recherche va se fermer il faudra le réouvir pour poster les rapports
téléchargement : ZHPcleaner de Nicolas Cooleman
- Cliquer sur le Bouton Bleu
- cet outil ne nécessite aucune installation, il est très rapide car basé sur l'éxécution de scripts.
- Accepte "les conditions d'utilisation"
- Il restaure les paramètres Proxy par défaut,
- Il supprime les redirections des raccourcis de navigateurs (Infection par argument),
- Il restaure les pages de démarrage et de recherche dun navigateur Internet Explorer (Base de Registres),
- Il restaure la page de démarrage du navigateur Mozilla Firefox (Fichier de préférences),
- Il restaure la page de démarrage du navigateur Google Chrome (Fichier de préférences),
- Il restaure la page de démarrage du navigateur Opera (Fichier de préférences),
- Il supprime certains Browser Helper Object (BHO) nuisibles de navigateurs,
- Il supprime certaines Barres d'outil (Toolbar) nuisibles de navigateurs,
- Il répare le fournisseur de recherche par défaut (SearchScope),
- En cas de présence d'un proxy, un message apparaît avec la question suivante
"Avez-vous installé ce proxy ?" suivi de l'adresse IP du proxy.
Si vous n'avez pas installé de Proxy, cliquer sur "NON" pour accepter la réparation du proxy.
- les cases sont cochées suivant le ou les navigateurs présents
- Cliquer sur le popup qui apparait
- Puis sur scanner
- Laisser la barre de progression arriver jusqu'à la fin.
- A la fin du traitement, un rapport de nettoyage s'affiche dans le bloc-notes le "baisser" sinon celui de réparer va l'effacer :
- Cliquer sur réparer
- Fournir les deux rapports
- Fermeture des navigateurs pour le nettoyage
- Si tu veux réparer le fichier hote, il faut désactiver ton antivirus.
Tutoriel officiel
___________________________________________
Ensuite :
___________________________________________
ZHPDiag
suis bien les instructions
1) * Télécharge ZHPDiag (de Nicolas coolman) sur ton bureau !!
>> ZHPDiag officiel
- cliquer sur le Bouton Bleu + Nicolas Coolman :
ZHPDiag (de Nicolas coolman)
Si ton système d'exploitation est Vista ou Win7/8, lance les logiciels par simple clic droit et choisis "exécuter en tant qu'administrateur"
a) * Une fois le téléchargement achevé,
b) * double clique (ou clic droit pour seven , vista et 8 <ital>exécuter en tant qu'administrateur<:ital>) sur ZHPDiag2.exe et suis les instructions.
c) * L'outil va créer 2 icônes de racourcis : ZHPDiag >> ZHPFix
d) * Clique Droit sur l'icone en forme de parchemin
e) *A l'ouverture le programme te proposes "Rechercher" , "Configurer" , "Complet" -
<ital>Clique sur "Complet" le scan démarre ....le rapport s'affiche
Deuxième solution :
- Si tu cliques sur configurer- Des icônes apparaissent en bas de la fenêtre.
- Clique sur le tournevis en bas à droite et choisis "Tous" puis "OK"
2 ) * si tu as choisi configurer, maintenant clique sur "Rechercher".
* Important >> Pendant l analyse de ton PC par ZHPDIag ne touche à plus rien !!- Laisse l'outil travailler, il peut être assez long
une fenêtre peut s'ouvrir à la fin de la recherche :
Il suffit de cliquer sur :
le programme s'est installé correctement
3) * Le rapport s'affiche sur ton Bureau une fois terminé !Tu peux fermer ZHPDiag
IMPORTANT
les rapports étant trop long, les héberger :
Rappel des dépôts
1 cjoint >>>> Explication
2 SoSVirus Upload >>>>explication
-
le 1er rapport
~ ZHPCleaner v2015.2.26.93 by Nicolas Coolman (26/02/2015)
~ Run by remy (Administrator) (26/02/2015 19:20:13)
~ Forum : http://forum.nicolascoolman.fr
~ Facebook : https://www.facebook.com/nicolascoolman1
~ State version : Version OK
~ Type : Scanner
~ Report : C:\Users\remy\Desktop\ZHPCleaner.txt
~ Quarantine : C:\Users\remy\AppData\Roaming\ZHP\ZHPCleaner_Quarantine.txt
~ UAC : Activate
~ Boot Mode : Normal (Normal boot)
~ Windows 7, 32-bit Service Pack 1 (Build 7601)
---\\ Service. (0)
~ Aucun élément malicieux trouvé.
---\\ Navigateur internet. (22)
TROUVÉ Proxy: HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\\ProxyHttp1.1 ( 1 )
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.AL", 4); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.aflt", "ast_ggfc_14_42_ie"); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.appId", "{9CB2CD61-FFA0-406C-9D2D-8FDE6F4A4D8A}"); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.cd", "2XzuyEtN2Y1L1QzutDtDtC0AyE0DzztDyEtDtByE0FtD0A0AtN0D0Tzu0StCt[...] (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.cr", "1845549647"); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.dfltLng", ""); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.dfltSrch", true); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.dnsErr", true); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.excTlbr", false); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.hmpg", true); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.id", "001A4D804024F0AA"); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.instlDay", "16359"); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.instlRef", "142905_b"); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.prdct", "astrmndasr"); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.tlbrId", ""); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.vrsn", ""); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.vrsni", ""); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr_i.newTab", true); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr_i.smplGrp", "none"); (PUP.Astromenda)
TROUVÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr_i.vrsnTs", "21:47:9"); (PUP.Astromenda)
TROUVÉ Chrome URL: hxxp://astromenda.com/?f=7&a=ast_ggfc_14_42_ie&cd=2XzuyEtN2Y1L1QzutDtDtC0AyE0DzztDyEtDtByE0FtD0A0AtN[...]
---\\ Fichier hôte. (1)
~ Le fichier hôte est légitime. (21)
---\\ Tâche planifiée. (0)
~ Aucun élément malicieux trouvé.
---\\ Explorateur ( Dossiers, Fichiers ). (16)
TROUVÉ fichier: C:\Users\remy\AppData\Roaming\Mozilla\Firefox\Profiles\2tefea1k.default\searchplugins\Lasaoren.xml [] (PUP.Lasaoren)
TROUVÉ fichier: C:\Users\remy\Downloads\FileOpenerSetup.exe [ - ](Adware.InstallCore)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\air760A.exe [AirInstaller Inc. - Adobe Flash Player](Adware.AirInstaller)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\setup.exe [AirInstaller Inc. - Adobe Flash Player](Adware.AirInstaller)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\RarSFX0\Binaries\IExploreInstaller.exe [Iminent - Installer](Adware.IMBooster)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\is1242154493\6850765_stp.EXE [Smart PC Solutions - PC Speed Maximizer](PUP.SmartPCSolutions)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\is1242154493\6923905_stp.EXE [Smart PC Solutions - PC Speed Maximizer](PUP.SmartPCSolutions)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\is1242154493\6955425_stp.EXE [Smart PC Solutions - PC Speed Maximizer](PUP.SmartPCSolutions)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\is1242154493\7023000_stp.EXE [Smart PC Solutions - PC Speed Maximizer](PUP.SmartPCSolutions)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\hxxps_static.re-markit00.re-markit.co_0.localstorage [ - ](PUP.ReMarkIt)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\hxxps_static.re-markit00.re-markit.co_0.localstorage-journal [ - ](PUP.ReMarkIt)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\hxxp_static.re-markit00.re-markit.co_0.localstorage [ - ](PUP.ReMarkIt)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\hxxp_static.re-markit00.re-markit.co_0.localstorage-journal [ - ](PUP.ReMarkIt)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\Bubble Dock.txt [ - ](PUP.BubbleDock)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\LBubble Dock.txt [ - ](PUP.BubbleDock)
TROUVÉ fichier: C:\Users\remy\AppData\Local\Temp\SearchProtectINT.exe [Conduit - Search Protect by conduit](PUP.SearchProtect)
---\\ Base de Registres ( Clés, Valeurs, Données ). (7)
TROUVÉ clé: HKLM\SOFTWARE\eedf452f-ea02-5f45-cd87-c4a5a3cb4a68 [] (PUP.CrossRider)
TROUVÉ clé: HKCU\Software\ForumerIT [] (Toolbar.Forumer)
TROUVÉ clé: HKLM\SYSTEM\CurrentControlSet\Services\Eventlog\Application\WebCakeUpdaterService [] (PUP.WebCake)
TROUVÉ clé: HKLM\SOFTWARE\mamverifier [] (Toolbar.Mamverifier)
TROUVÉ clé: HKLM\SOFTWARE\{12DA0E6F-5543-440C-BAA2-28BF01070AFA} [] (Adware.Graftor)
TROUVÉ clé: HKLM\SOFTWARE\Microsoft\Internet Explorer\Low Rights\ElevationPolicy\{6874fade-02c8-4181-831a-fc7486cf1d74} [C:\Program Files\Allin1Convert_8h\bar\1.bin] (PUP.MindSpark)
TROUVÉ clé: HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\DuuquUpdate.exe [] (PUP.FrameFox)
---\\ Bilan de la réparation
~ Aucune réparation effectuée.
~ Ce navigateur est absent (Opera Software)
---\\ Statistiques
~ Items scannés : 60954
~ Items trouvés : 45
~ Items réparés : 0
End of clean at 19:33:37 -
2e rapport
~ Run by remy (Administrator) (26/02/2015 19:34:06)
~ Forum : http://forum.nicolascoolman.fr
~ Facebook : https://www.facebook.com/nicolascoolman1
~ State version : Version OK
~ Type : Réparer
~ Report : C:\Users\remy\Desktop\ZHPCleaner.txt
~ Quarantine : C:\Users\remy\AppData\Roaming\ZHP\ZHPCleaner_Quarantine.txt
~ UAC : Activate
~ Boot Mode : Normal (Normal boot)
~ Windows 7, 32-bit Service Pack 1 (Build 7601)
---\\ Service. (0)
~ Aucun élément malicieux trouvé.
---\\ Navigateur internet. (22)
REMPLACÉ Proxy: HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\\ProxyHttp1.1 ( 1 )
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.AL", 4); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.aflt", "ast_ggfc_14_42_ie"); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.appId", "{9CB2CD61-FFA0-406C-9D2D-8FDE6F4A4D8A}"); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.cd", "2XzuyEtN2Y1L1QzutDtDtC0AyE0DzztDyEtDtByE0FtD0A0AtN0D0Tzu0StCt[...] (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.cr", "1845549647"); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.dfltLng", ""); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.dfltSrch", true); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.dnsErr", true); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.excTlbr", false); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.hmpg", true); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.id", "001A4D804024F0AA"); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.instlDay", "16359"); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.instlRef", "142905_b"); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.prdct", "astrmndasr"); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.tlbrId", ""); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.vrsn", ""); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr.vrsni", ""); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr_i.newTab", true); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr_i.smplGrp", "none"); (PUP.Astromenda)
REMPLACÉ: [2tefea1k.default] - user_pref("extensions.astrmndasr_i.vrsnTs", "21:47:9"); (PUP.Astromenda)
REMPLACÉ Chrome URL: hxxp://astromenda.com/?f=7&a=ast_ggfc_14_42_ie&cd=2XzuyEtN2Y1L1QzutDtDtC0AyE0DzztDyEtDtByE0FtD0A0AtN[...]
---\\ Fichier hôte. (1)
~ Le fichier hôte est légitime. (21)
---\\ Tâche planifiée. (0)
~ Aucun élément malicieux trouvé.
---\\ Explorateur ( Dossiers, Fichiers ). (16)
DEPLACÉ fichier: C:\Users\remy\AppData\Roaming\Mozilla\Firefox\Profiles\2tefea1k.default\searchplugins\Lasaoren.xml [] (PUP.Lasaoren)
DEPLACÉ fichier: C:\Users\remy\Downloads\FileOpenerSetup.exe [ - ] (Adware.InstallCore)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\air760A.exe [AirInstaller Inc. - Adobe Flash Player] (Adware.AirInstaller)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\setup.exe [AirInstaller Inc. - Adobe Flash Player] (Adware.AirInstaller)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\RarSFX0\Binaries\IExploreInstaller.exe [Iminent - Installer] (Adware.IMBooster)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\is1242154493\6850765_stp.EXE [Smart PC Solutions - PC Speed Maximizer] (PUP.SmartPCSolutions)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\is1242154493\6923905_stp.EXE [Smart PC Solutions - PC Speed Maximizer] (PUP.SmartPCSolutions)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\is1242154493\6955425_stp.EXE [Smart PC Solutions - PC Speed Maximizer] (PUP.SmartPCSolutions)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\is1242154493\7023000_stp.EXE [Smart PC Solutions - PC Speed Maximizer] (PUP.SmartPCSolutions)
DEPLACÉ fichier*: C:\Users\remy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\hxxps_static.re-markit00.re-markit.co_0.localstorage [ - ] (PUP.ReMarkIt)
DEPLACÉ fichier*: C:\Users\remy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\hxxps_static.re-markit00.re-markit.co_0.localstorage-journal [ - ] (PUP.ReMarkIt)
DEPLACÉ fichier*: C:\Users\remy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\hxxp_static.re-markit00.re-markit.co_0.localstorage [ - ] (PUP.ReMarkIt)
DEPLACÉ fichier*: C:\Users\remy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\hxxp_static.re-markit00.re-markit.co_0.localstorage-journal [ - ] (PUP.ReMarkIt)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\Bubble Dock.txt [ - ] (PUP.BubbleDock)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\LBubble Dock.txt [ - ] (PUP.BubbleDock)
DEPLACÉ fichier: C:\Users\remy\AppData\Local\Temp\SearchProtectINT.exe [Conduit - Search Protect by conduit] (PUP.SearchProtect)
---\\ Base de Registres ( Clés, Valeurs, Données ). (7)
SUPPRIMÉ clé*: HKLM\SOFTWARE\eedf452f-ea02-5f45-cd87-c4a5a3cb4a68 [] (PUP.CrossRider)
SUPPRIMÉ clé*: HKCU\Software\ForumerIT [] (Toolbar.Forumer)
SUPPRIMÉ clé*: HKLM\SYSTEM\CurrentControlSet\Services\Eventlog\Application\WebCakeUpdaterService [] (PUP.WebCake)
SUPPRIMÉ clé*: HKLM\SOFTWARE\mamverifier [] (Toolbar.Mamverifier)
SUPPRIMÉ clé*: HKLM\SOFTWARE\{12DA0E6F-5543-440C-BAA2-28BF01070AFA} [] (Adware.Graftor)
SUPPRIMÉ clé*: HKLM\SOFTWARE\Microsoft\Internet Explorer\Low Rights\ElevationPolicy\{6874fade-02c8-4181-831a-fc7486cf1d74} [C:\Program Files\Allin1Convert_8h\bar\1.bin] (PUP.MindSpark)
SUPPRIMÉ clé*: HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\DuuquUpdate.exe [] (PUP.FrameFox)
---\\ Bilan de la réparation
~ Réparation réalisée avec succès.
~ Ce navigateur est absent (Opera Software)
---\\ Statistiques
~ Items scannés : 60951
~ Items trouvés : 0
~ Items réparés : 39 -
-
@buckhulkil a "buggué" à 39 %
-