Virus + que redondant
Résolu
Bonjour,
voivi la situation, J'avais c virus avant qu je formate mon pc hier,j'ai tout tenter pour les supprimer,rien n'y fait :( Adwcleaner les supprime (supposer mais ils revienne a la seconde : AVG anti..virus ne détecte rien toutefois Malwarebytes anti malware jui détecte ceci:hxxp://jamenize.com je vous poste le rapprt adwcleaner ainsi que Hi-Jack le rapport de malwarebyte mais commementionner sous-haut c toujours la mëme chose un tres Grand Merci a L,avance:
# AdwCleaner v4.203 - Rapport créé le 05/05/2015 à 13:34:30
# Mis à jour le 30/04/2015 par Xplode
# Base de données : 2015-05-02.1 [Serveur]
# Système d'exploitation : Windows 7 Ultimate Service Pack 1 (x64)
# Nom d'utilisateur : Claude - CLAUDE-PC
# Exécuté depuis : C:\Users\Claude\Downloads\adwcleaner_4.203.exe
# Option : Nettoyer
-\\ Internet Explorer v11.0.9600.17728
-\\ Google Chrome v42.0.2311.135
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Web Data] - Supprimée [Search Provider] : hxxp://www.ask.com/web?q={searchTerms}
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Web Data] - Supprimée [Search Provider] : hxxp://jamenize.com/results.php?f=4&q={searchTerms}&a=jmz_forstw01_15_13&cd=2XzuyEtN2Y1L1Qzu0DtDyDtDzyzytByCtBtCzzyCtC0E0DyCtN0D0Tzu0StCtCyBzztN1L2XzutAtFzztFyEtFtDtN1L1CzutCyEtBzytDyD1V1BtBtN1L1G1B1V1N2Y1L1Qzu2StC0EyCyC0F0C0A0AtG0DyBtA0CtG0Ezy0AtAtG0FyCtD0AtGyB0AyDtBtCtDzz0FyBzyyDtC2QtN1M1F1B2Z1V1N2Y1L1Qzu2S0CzzyC0D0AtAyEzztGzztC0DyCtGyEyDtD0EtGzytB0E0DtGtDyBtC0AtD0D0A0BtAyDyC0E2QtN1B1L1H1Ezu1O2U1M1B&cr=287188896&ir=
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Web Data] - Supprimée [Search Provider] : hxxp://websearch.coolsearches.info/?l=1&q={searchTerms}&pid=22890&r=2015/03/27&hid=16105866817757014254&lg=EN&cc=CA&unqvl=85
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Web Data] - Supprimée [Search Provider] : hxxp://www.softonic.fr/s/{searchTerms}
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Secure Preferences] - Supprimée [Homepage] : hxxp://jamenize.com/?f=1&a=jmz_forstw01_15_13&cd=2XzuyEtN2Y1L1Qzu0DtDyDtDzyzytByCtBtCzzyCtC0E0DyCtN0D0Tzu0StCtCyBzztN1L2XzutAtFzztFyEtFtDtN1L1CzutCyEtBzytDyD1V1BtBtN1L1G1B1V1N2Y1L1Qzu2StC0EyCyC0F0C0A0AtG0DyBtA0CtG0Ezy0AtAtG0FyCtD0AtGyB0AyDtBtCtDzz0FyBzyyDtC2QtN1M1F1B2Z1V1N2Y1L1Qzu2S0CzzyC0D0AtAyEzztGzztC0DyCtGyEyDtD0EtGzytB0E0DtGtDyBtC0AtD0D0A0BtAyDyC0E2QtN1B1L1H1Ezu1O2U1M1B&cr=287188896&ir=
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Secure Preferences] - Supprimée [Startup_URLs] : hxxp://jamenize.com/?f=7&a=jmz_forstw01_15_13&cd=2XzuyEtN2Y1L1Qzu0DtDyDtDzyzytByCtBtCzzyCtC0E0DyCtN0D0Tzu0StCtCyBzztN1L2XzutAtFzztFyEtFtDtN1L1CzutCyEtBzytDyD1V1BtBtN1L1G1B1V1N2Y1L1Qzu2StC0EyCyC0F0C0A0AtG0DyBtA0CtG0Ezy0AtAtG0FyCtD0AtGyB0AyDtBtCtDzz0FyBzyyDtC2QtN1M1F1B2Z1V1N2Y1L1Qzu2S0CzzyC0D0AtAyEzztGzztC0DyCtGyEyDtD0EtGzytB0E0DtGtDyBtC0AtD0D0A0BtAyDyC0E2QtN1B1L1H1Ezu1O2U1M1B&cr=287188896&ir=
AdwCleaner[R0].txt - [5668 octets] - [05/05/2015 12:25:11]
AdwCleaner[R1].txt - [2966 octets] - [05/05/2015 13:32:17]
AdwCleaner[S0].txt - [5818 octets] - [05/05/2015 12:27:03]
AdwCleaner[S1].txt - [2899 octets] - [05/05/2015 13:34:30]
########## EOF - C:\AdwCleaner\AdwCleaner[S1].txt - [2959 octets] ##########
et le rapport HI-Jack:
Logfile of Trend Micro HijackThis v2.0.5
Scan saved at 13:38:49, on 2015-05-05
Platform: Windows 7 SP1 (WinNT 6.00.3505)
MSIE: Internet Explorer v11.0 (11.00.9600.17728)
Boot mode: Normal
Running processes:
C:\Program Files (x86)\AVG\AVG2015\avgui.exe
C:\Program Files (x86)\Intel\Intel(R) USB 3.0 eXtensible Host Controller Driver\Application\iusb3mon.exe
C:\Program Files (x86)\Logitech\LWS\Webcam Software\LWS.exe
C:\Windows\SysWOW64\ctfmon.exe
C:\Program Files (x86)\Logitech\LWS\Webcam Software\CameraHelperShell.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Users\Claude\Downloads\HijackThis-2.0.5 beta.exe
R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Page = https://www.bing.com/?toHttps=1&redig=5FC791212101479BAFBE1A679848B1AF
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = https://www.google.ca/
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = https://www.msn.com/fr-fr/?ocid=iehp
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = https://www.bing.com/?toHttps=1&redig=5FC791212101479BAFBE1A679848B1AF
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = https://www.bing.com/?toHttps=1&redig=5FC791212101479BAFBE1A679848B1AF
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = https://www.msn.com/fr-fr/?ocid=iehp
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Local Page = C:\Windows\SysWOW64\blank.htm
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
F2 - REG:system.ini: UserInit=userinit.exe,
O2 - BHO: Programme d'aide de l'Assistant de connexion au compte Microsoft - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: Google Toolbar Helper - {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O2 - BHO: SkypeIEPluginBHO - {AE805869-2E5C-4ED4-8F7B-F1F7851A4497} - C:\Program Files (x86)\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O2 - BHO: Google Toolbar Notifier BHO - {AF69DE43-7D58-4638-B6FA-CE66B5AD205D} - C:\Program Files (x86)\Google\GoogleToolbarNotifier\5.10.11023.1534\swg.dll
O3 - Toolbar: Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O4 - HKLM\..\Run: [AVG_UI] "C:\Program Files (x86)\AVG\AVG2015\avgui.exe" /TRAYONLY
O4 - HKLM\..\Run: [USB3MON] "C:\Program Files (x86)\Intel\Intel(R) USB 3.0 eXtensible Host Controller Driver\Application\iusb3mon.exe"
O4 - HKLM\..\Run: [LWS] C:\Program Files (x86)\Logitech\LWS\Webcam Software\LWS.exe -hide
O4 - HKCU\..\Run: [Web Companion] C:\Program Files (x86)\Lavasoft\Web Companion\Application\WebCompanion.exe --minimize
O4 - HKCU\..\Run: [CCleaner Monitoring] "C:\Program Files\CCleaner\CCleaner64.exe" /MONITOR
O4 - Startup: Logitech . Enregistrement du produit.lnk = C:\Program Files (x86)\Logitech\Ereg\eReg.exe
O9 - Extra button: Skype Click to Call settings - {898EA8C8-E7FF-479B-8935-AEC46303B9E5} - C:\Program Files (x86)\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O10 - Unknown file in Winsock LSP: c:\program files (x86)\common files\microsoft shared\windows live\wlidnsp.dll
O10 - Unknown file in Winsock LSP: c:\program files (x86)\common files\microsoft shared\windows live\wlidnsp.dll
O11 - Options group: [ACCELERATED_GRAPHICS] Accelerated graphics
O18 - Protocol: skypec2c - {91774881-D725-4E58-B298-07617B9B86A8} - C:\Program Files (x86)\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O18 - Protocol: wlpg - {E43EF6CD-A37A-4A9B-9E6F-83F89B8E6324} - C:\Program Files (x86)\Windows Live\Photo Gallery\AlbumDownloadProtocolHandler.dll
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) - Adobe Systems Incorporated - C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: Adobe Flash Player Update Service (AdobeFlashPlayerUpdateSvc) - Adobe Systems Incorporated - C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe
O23 - Service: @%SystemRoot%\system32\aelupsvc.dll,-1 (AeLookupSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\Alg.exe,-112 (ALG) - Unknown owner - C:\Windows\System32\alg.exe (file missing)
O23 - Service: @%systemroot%\system32\appidsvc.dll,-100 (AppIDSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\appinfo.dll,-100 (Appinfo) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @appmgmts.dll,-3250 (AppMgmt) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\audiosrv.dll,-204 (AudioEndpointBuilder) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\audiosrv.dll,-200 (AudioSrv) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: Pare-feu AVG (avgfws) - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\AVG2015\avgfws.exe
O23 - Service: AVGIDSAgent - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\AVG2015\avgidsagent.exe
O23 - Service: AVG WatchDog (avgwd) - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\AVG2015\avgwdsvc.exe
O23 - Service: @%SystemRoot%\system32\AxInstSV.dll,-103 (AxInstSV) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\bdesvc.dll,-100 (BDESVC) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\bfe.dll,-1001 (BFE) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\qmgr.dll,-1000 (BITS) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\browser.dll,-100 (Browser) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\bthserv.dll,-101 (bthserv) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\certprop.dll,-11 (CertPropSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: Intel(R) Content Protection HECI Service (cphs) - Intel Corporation - C:\Windows\SysWow64\IntelCpHeciSvc.exe
O23 - Service: @%SystemRoot%\system32\cryptsvc.dll,-1001 (CryptSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\cscsvc.dll,-200 (CscService) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @oleres.dll,-5012 (DcomLaunch) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\defragsvc.dll,-101 (defragsvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\dhcpcore.dll,-100 (Dhcp) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\UtcResources.dll,-3001 (DiagTrack) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\dnsapi.dll,-101 (Dnscache) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\dot3svc.dll,-1102 (dot3svc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\dps.dll,-500 (DPS) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\eapsvc.dll,-1 (EapHost) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\efssvc.dll,-100 (EFS) - Unknown owner - C:\Windows\System32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\ehome\ehrecvr.exe,-101 (ehRecvr) - Unknown owner - C:\Windows\ehome\ehRecvr.exe
O23 - Service: @%SystemRoot%\ehome\ehsched.exe,-101 (ehSched) - Unknown owner - C:\Windows\ehome\ehsched.exe
O23 - Service: @%SystemRoot%\system32\wevtsvc.dll,-200 (eventlog) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @comres.dll,-2450 (EventSystem) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\fxsresm.dll,-118 (Fax) - Unknown owner - C:\Windows\system32\fxssvc.exe (file missing)
O23 - Service: @%systemroot%\system32\fdPHost.dll,-100 (fdPHost) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\fdrespub.dll,-100 (FDResPub) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\FntCache.dll,-100 (FontCache) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @gpapi.dll,-112 (gpsvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: Service Google Update (gupdate) (gupdate) - Unknown owner - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Service Google Update (gupdatem) (gupdatem) - Unknown owner - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Google Software Updater (gusvc) - Google - C:\Program Files (x86)\Google\Common\Google Updater\GoogleUpdaterService.exe
O23 - Service: @%SystemRoot%\System32\hidserv.dll,-101 (hidserv) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\kmsvc.dll,-6 (hkmsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\ListSvc.dll,-100 (HomeGroupListener) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\provsvc.dll,-100 (HomeGroupProvider) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: Intel(R) Integrated Clock Controller Service - Intel(R) ICCS (ICCS) - Intel Corporation - C:\Program Files (x86)\Intel\Intel(R) Integrated Clock Controller Service\ICCProxy.exe
O23 - Service: @%SystemRoot%\system32\ieetwcollectorres.dll,-1000 (IEEtwCollectorService) - Unknown owner - C:\Windows\system32\IEEtwCollector.exe (file missing)
O23 - Service: Intel(R) HD Graphics Control Panel Service (igfxCUIService1.0.0.0) - Unknown owner - C:\Windows\system32\igfxCUIService.exe (file missing)
O23 - Service: @%SystemRoot%\system32\ikeext.dll,-501 (IKEEXT) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\IPBusEnum.dll,-102 (IPBusEnum) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\iphlpsvc.dll,-500 (iphlpsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @keyiso.dll,-100 (KeyIso) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @comres.dll,-2946 (KtmRm) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\srvsvc.dll,-100 (LanmanServer) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\wkssvc.dll,-100 (LanmanWorkstation) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\lltdres.dll,-1 (lltdsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\lmhsvc.dll,-101 (lmhosts) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: Ma-Config Agent (MaConfigAgent) - Unknown owner - C:\Program Files\ma-config.com\MaConfigAgent.exe
O23 - Service: MBAMScheduler - Malwarebytes Corporation - C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamscheduler.exe
O23 - Service: MBAMService - Malwarebytes Corporation - C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamservice.exe
O23 - Service: @%systemroot%\system32\mmcss.dll,-100 (MMCSS) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\FirewallAPI.dll,-23090 (MpsSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @comres.dll,-2797 (MSDTC) - Unknown owner - C:\Windows\System32\msdtc.exe (file missing)
O23 - Service: @%SystemRoot%\system32\iscsidsc.dll,-5000 (MSiSCSI) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\msimsg.dll,-27 (msiserver) - Unknown owner - C:\Windows\system32\msiexec.exe
O23 - Service: @%SystemRoot%\system32\qagentrt.dll,-6 (napagent) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\netlogon.dll,-102 (Netlogon) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\netman.dll,-109 (Netman) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\netprofm.dll,-202 (netprofm) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\nlasvc.dll,-1 (NlaSvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\nsisvc.dll,-200 (nsi) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\pnrpsvc.dll,-8004 (p2pimsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\p2psvc.dll,-8006 (p2psvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\pcasvc.dll,-1 (PcaSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\peerdistsvc.dll,-9000 (PeerDistSvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\sysWow64\perfhost.exe,-2 (PerfHost) - Unknown owner - C:\Windows\SysWow64\perfhost.exe
O23 - Service: @%systemroot%\system32\pla.dll,-500 (pla) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\umpnpmgr.dll,-100 (PlugPlay) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\pnrpauto.dll,-8002 (PNRPAutoReg) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\pnrpsvc.dll,-8000 (PNRPsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\polstore.dll,-5010 (PolicyAgent) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\umpo.dll,-100 (Power) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\profsvc.dll,-300 (ProfSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\psbase.dll,-300 (ProtectedStorage) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\qwave.dll,-1 (QWAVE) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%Systemroot%\system32\rasauto.dll,-200 (RasAuto) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%Systemroot%\system32\rasmans.dll,-200 (RasMan) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @regsvc.dll,-1 (RemoteRegistry) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%windir%\system32\RpcEpMap.dll,-1001 (RpcEptMapper) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\Locator.exe,-2 (RpcLocator) - Unknown owner - C:\Windows\system32\locator.exe (file missing)
O23 - Service: @oleres.dll,-5010 (RpcSs) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\samsrv.dll,-1 (SamSs) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\System32\SCardSvr.dll,-1 (SCardSvr) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\schedsvc.dll,-100 (Schedule) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\certprop.dll,-13 (SCPolicySvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\sdrsvc.dll,-107 (SDRSVC) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\seclogon.dll,-7001 (seclogon) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\Sens.dll,-200 (SENS) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\sensrsvc.dll,-1000 (SensrSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\SessEnv.dll,-1026 (SessionEnv) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\shsvcs.dll,-12288 (ShellHWDetection) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: Skype Updater (SkypeUpdate) - Skype Technologies - C:\Program Files (x86)\Skype\Updater\Updater.exe
O23 - Service: @%SystemRoot%\system32\snmptrap.exe,-3 (SNMPTRAP) - Unknown owner - C:\Windows\System32\snmptrap.exe (file missing)
O23 - Service: @%systemroot%\system32\spoolsv.exe,-1 (Spooler) - Unknown owner - C:\Windows\System32\spoolsv.exe (file missing)
O23 - Service: @%SystemRoot%\system32\sppsvc.exe,-101 (sppsvc) - Unknown owner - C:\Windows\system32\sppsvc.exe (file missing)
O23 - Service: @%SystemRoot%\system32\sppuinotify.dll,-103 (sppuinotify) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\ssdpsrv.dll,-100 (SSDPSRV) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\sstpsvc.dll,-200 (SstpSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wiaservc.dll,-9 (stisvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\swprv.dll,-103 (swprv) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\sysmain.dll,-1000 (SysMain) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\TabSvc.dll,-100 (TabletInputService) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\tapisrv.dll,-10100 (TapiSrv) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\tbssvc.dll,-100 (TBS) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\termsrv.dll,-268 (TermService) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\themeservice.dll,-8192 (Themes) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\mmcss.dll,-102 (THREADORDER) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\trkwks.dll,-1 (TrkWks) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\servicing\TrustedInstaller.exe,-100 (TrustedInstaller) - Unknown owner - C:\Windows\servicing\TrustedInstaller.exe
O23 - Service: @%SystemRoot%\system32\ui0detect.exe,-101 (UI0Detect) - Unknown owner - C:\Windows\system32\UI0Detect.exe (file missing)
O23 - Service: @%SystemRoot%\system32\umrdp.dll,-1000 (UmRdpService) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\upnphost.dll,-213 (upnphost) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\dwm.exe,-2000 (UxSms) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\vaultsvc.dll,-1003 (VaultSvc) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\vds.exe,-100 (vds) - Unknown owner - C:\Windows\System32\vds.exe (file missing)
O23 - Service: @%systemroot%\system32\vssvc.exe,-102 (VSS) - Unknown owner - C:\Windows\system32\vssvc.exe (file missing)
O23 - Service: vToolbarUpdater18.4.0 - Unknown owner - C:\Program Files (x86)\Common Files\AVG Secure Search\vToolbarUpdater\18.4.0\ToolbarUpdater.exe (file missing)
O23 - Service: @%SystemRoot%\system32\w32time.dll,-200 (W32Time) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\Wat\WatUX.exe,-601 (WatAdminSvc) - Unknown owner - C:\Windows\system32\Wat\WatAdminSvc.exe (file missing)
O23 - Service: @%systemroot%\system32\wbengine.exe,-104 (wbengine) - Unknown owner - C:\Windows\system32\wbengine.exe (file missing)
O23 - Service: @%systemroot%\system32\wbiosrvc.dll,-100 (WbioSrvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wcncsvc.dll,-3 (wcncsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\WcsPlugInService.dll,-200 (WcsPlugInService) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\wdi.dll,-502 (WdiServiceHost) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\wdi.dll,-500 (WdiSystemHost) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\webclnt.dll,-100 (WebClient) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wecsvc.dll,-200 (Wecsvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wercplsupport.dll,-101 (wercplsupport) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wersvc.dll,-100 (WerSvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%ProgramFiles%\Windows Defender\MsMpRes.dll,-103 (WinDefend) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\winhttp.dll,-100 (WinHttpAutoProxySvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%Systemroot%\system32\wbem\wmisvc.dll,-205 (Winmgmt) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%Systemroot%\system32\wsmsvc.dll,-101 (WinRM) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wlansvc.dll,-257 (Wlansvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%Systemroot%\system32\wbem\wmiapsrv.exe,-110 (wmiApSrv) - Unknown owner - C:\Windows\system32\wbem\WmiApSrv.exe (file missing)
O23 - Service: @%PROGRAMFILES%\Windows Media Player\wmpnetwk.exe,-101 (WMPNetworkSvc) - Unknown owner - C:\Program Files (x86)\Windows Media Player\wmpnetwk.exe (file missing)
O23 - Service: @%SystemRoot%\system32\wpcsvc.dll,-100 (WPCSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wpdbusenum.dll,-100 (WPDBusEnum) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wscsvc.dll,-200 (wscsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\SearchIndexer.exe,-103 (WSearch) - Unknown owner - C:\Windows\system32\SearchIndexer.exe
O23 - Service: WtuSystemSupport - Unknown owner - C:\Program Files (x86)\AVG Web TuneUp\WtuSystemSupport.exe
O23 - Service: @%systemroot%\system32\wuaueng.dll,-105 (wuauserv) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wudfsvc.dll,-1000 (wudfsvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wwansvc.dll,-257 (WwanSvc) - Unknown owner - C:\Windows\system32\svchost.exe
--
End of file - 23097 bytes
voivi la situation, J'avais c virus avant qu je formate mon pc hier,j'ai tout tenter pour les supprimer,rien n'y fait :( Adwcleaner les supprime (supposer mais ils revienne a la seconde : AVG anti..virus ne détecte rien toutefois Malwarebytes anti malware jui détecte ceci:hxxp://jamenize.com je vous poste le rapprt adwcleaner ainsi que Hi-Jack le rapport de malwarebyte mais commementionner sous-haut c toujours la mëme chose un tres Grand Merci a L,avance:
# AdwCleaner v4.203 - Rapport créé le 05/05/2015 à 13:34:30
# Mis à jour le 30/04/2015 par Xplode
# Base de données : 2015-05-02.1 [Serveur]
# Système d'exploitation : Windows 7 Ultimate Service Pack 1 (x64)
# Nom d'utilisateur : Claude - CLAUDE-PC
# Exécuté depuis : C:\Users\Claude\Downloads\adwcleaner_4.203.exe
# Option : Nettoyer
- [ Services ] *****
- [ Fichiers / Dossiers ] *****
- [ Tâches planifiées ] *****
- [ Raccourcis ] *****
- [ Registre ] *****
- [ Navigateurs ] *****
-\\ Internet Explorer v11.0.9600.17728
-\\ Google Chrome v42.0.2311.135
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Web Data] - Supprimée [Search Provider] : hxxp://www.ask.com/web?q={searchTerms}
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Web Data] - Supprimée [Search Provider] : hxxp://jamenize.com/results.php?f=4&q={searchTerms}&a=jmz_forstw01_15_13&cd=2XzuyEtN2Y1L1Qzu0DtDyDtDzyzytByCtBtCzzyCtC0E0DyCtN0D0Tzu0StCtCyBzztN1L2XzutAtFzztFyEtFtDtN1L1CzutCyEtBzytDyD1V1BtBtN1L1G1B1V1N2Y1L1Qzu2StC0EyCyC0F0C0A0AtG0DyBtA0CtG0Ezy0AtAtG0FyCtD0AtGyB0AyDtBtCtDzz0FyBzyyDtC2QtN1M1F1B2Z1V1N2Y1L1Qzu2S0CzzyC0D0AtAyEzztGzztC0DyCtGyEyDtD0EtGzytB0E0DtGtDyBtC0AtD0D0A0BtAyDyC0E2QtN1B1L1H1Ezu1O2U1M1B&cr=287188896&ir=
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Web Data] - Supprimée [Search Provider] : hxxp://websearch.coolsearches.info/?l=1&q={searchTerms}&pid=22890&r=2015/03/27&hid=16105866817757014254&lg=EN&cc=CA&unqvl=85
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Web Data] - Supprimée [Search Provider] : hxxp://www.softonic.fr/s/{searchTerms}
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Secure Preferences] - Supprimée [Homepage] : hxxp://jamenize.com/?f=1&a=jmz_forstw01_15_13&cd=2XzuyEtN2Y1L1Qzu0DtDyDtDzyzytByCtBtCzzyCtC0E0DyCtN0D0Tzu0StCtCyBzztN1L2XzutAtFzztFyEtFtDtN1L1CzutCyEtBzytDyD1V1BtBtN1L1G1B1V1N2Y1L1Qzu2StC0EyCyC0F0C0A0AtG0DyBtA0CtG0Ezy0AtAtG0FyCtD0AtGyB0AyDtBtCtDzz0FyBzyyDtC2QtN1M1F1B2Z1V1N2Y1L1Qzu2S0CzzyC0D0AtAyEzztGzztC0DyCtGyEyDtD0EtGzytB0E0DtGtDyBtC0AtD0D0A0BtAyDyC0E2QtN1B1L1H1Ezu1O2U1M1B&cr=287188896&ir=
[C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Secure Preferences] - Supprimée [Startup_URLs] : hxxp://jamenize.com/?f=7&a=jmz_forstw01_15_13&cd=2XzuyEtN2Y1L1Qzu0DtDyDtDzyzytByCtBtCzzyCtC0E0DyCtN0D0Tzu0StCtCyBzztN1L2XzutAtFzztFyEtFtDtN1L1CzutCyEtBzytDyD1V1BtBtN1L1G1B1V1N2Y1L1Qzu2StC0EyCyC0F0C0A0AtG0DyBtA0CtG0Ezy0AtAtG0FyCtD0AtGyB0AyDtBtCtDzz0FyBzyyDtC2QtN1M1F1B2Z1V1N2Y1L1Qzu2S0CzzyC0D0AtAyEzztGzztC0DyCtGyEyDtD0EtGzytB0E0DtGtDyBtC0AtD0D0A0BtAyDyC0E2QtN1B1L1H1Ezu1O2U1M1B&cr=287188896&ir=
AdwCleaner[R0].txt - [5668 octets] - [05/05/2015 12:25:11]
AdwCleaner[R1].txt - [2966 octets] - [05/05/2015 13:32:17]
AdwCleaner[S0].txt - [5818 octets] - [05/05/2015 12:27:03]
AdwCleaner[S1].txt - [2899 octets] - [05/05/2015 13:34:30]
########## EOF - C:\AdwCleaner\AdwCleaner[S1].txt - [2959 octets] ##########
et le rapport HI-Jack:
Logfile of Trend Micro HijackThis v2.0.5
Scan saved at 13:38:49, on 2015-05-05
Platform: Windows 7 SP1 (WinNT 6.00.3505)
MSIE: Internet Explorer v11.0 (11.00.9600.17728)
Boot mode: Normal
Running processes:
C:\Program Files (x86)\AVG\AVG2015\avgui.exe
C:\Program Files (x86)\Intel\Intel(R) USB 3.0 eXtensible Host Controller Driver\Application\iusb3mon.exe
C:\Program Files (x86)\Logitech\LWS\Webcam Software\LWS.exe
C:\Windows\SysWOW64\ctfmon.exe
C:\Program Files (x86)\Logitech\LWS\Webcam Software\CameraHelperShell.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Users\Claude\Downloads\HijackThis-2.0.5 beta.exe
R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Page = https://www.bing.com/?toHttps=1&redig=5FC791212101479BAFBE1A679848B1AF
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = https://www.google.ca/
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = https://www.msn.com/fr-fr/?ocid=iehp
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = https://www.bing.com/?toHttps=1&redig=5FC791212101479BAFBE1A679848B1AF
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = https://www.bing.com/?toHttps=1&redig=5FC791212101479BAFBE1A679848B1AF
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = https://www.msn.com/fr-fr/?ocid=iehp
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Local Page = C:\Windows\SysWOW64\blank.htm
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
F2 - REG:system.ini: UserInit=userinit.exe,
O2 - BHO: Programme d'aide de l'Assistant de connexion au compte Microsoft - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: Google Toolbar Helper - {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O2 - BHO: SkypeIEPluginBHO - {AE805869-2E5C-4ED4-8F7B-F1F7851A4497} - C:\Program Files (x86)\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O2 - BHO: Google Toolbar Notifier BHO - {AF69DE43-7D58-4638-B6FA-CE66B5AD205D} - C:\Program Files (x86)\Google\GoogleToolbarNotifier\5.10.11023.1534\swg.dll
O3 - Toolbar: Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O4 - HKLM\..\Run: [AVG_UI] "C:\Program Files (x86)\AVG\AVG2015\avgui.exe" /TRAYONLY
O4 - HKLM\..\Run: [USB3MON] "C:\Program Files (x86)\Intel\Intel(R) USB 3.0 eXtensible Host Controller Driver\Application\iusb3mon.exe"
O4 - HKLM\..\Run: [LWS] C:\Program Files (x86)\Logitech\LWS\Webcam Software\LWS.exe -hide
O4 - HKCU\..\Run: [Web Companion] C:\Program Files (x86)\Lavasoft\Web Companion\Application\WebCompanion.exe --minimize
O4 - HKCU\..\Run: [CCleaner Monitoring] "C:\Program Files\CCleaner\CCleaner64.exe" /MONITOR
O4 - Startup: Logitech . Enregistrement du produit.lnk = C:\Program Files (x86)\Logitech\Ereg\eReg.exe
O9 - Extra button: Skype Click to Call settings - {898EA8C8-E7FF-479B-8935-AEC46303B9E5} - C:\Program Files (x86)\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O10 - Unknown file in Winsock LSP: c:\program files (x86)\common files\microsoft shared\windows live\wlidnsp.dll
O10 - Unknown file in Winsock LSP: c:\program files (x86)\common files\microsoft shared\windows live\wlidnsp.dll
O11 - Options group: [ACCELERATED_GRAPHICS] Accelerated graphics
O18 - Protocol: skypec2c - {91774881-D725-4E58-B298-07617B9B86A8} - C:\Program Files (x86)\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O18 - Protocol: wlpg - {E43EF6CD-A37A-4A9B-9E6F-83F89B8E6324} - C:\Program Files (x86)\Windows Live\Photo Gallery\AlbumDownloadProtocolHandler.dll
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) - Adobe Systems Incorporated - C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: Adobe Flash Player Update Service (AdobeFlashPlayerUpdateSvc) - Adobe Systems Incorporated - C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe
O23 - Service: @%SystemRoot%\system32\aelupsvc.dll,-1 (AeLookupSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\Alg.exe,-112 (ALG) - Unknown owner - C:\Windows\System32\alg.exe (file missing)
O23 - Service: @%systemroot%\system32\appidsvc.dll,-100 (AppIDSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\appinfo.dll,-100 (Appinfo) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @appmgmts.dll,-3250 (AppMgmt) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\audiosrv.dll,-204 (AudioEndpointBuilder) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\audiosrv.dll,-200 (AudioSrv) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: Pare-feu AVG (avgfws) - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\AVG2015\avgfws.exe
O23 - Service: AVGIDSAgent - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\AVG2015\avgidsagent.exe
O23 - Service: AVG WatchDog (avgwd) - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\AVG2015\avgwdsvc.exe
O23 - Service: @%SystemRoot%\system32\AxInstSV.dll,-103 (AxInstSV) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\bdesvc.dll,-100 (BDESVC) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\bfe.dll,-1001 (BFE) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\qmgr.dll,-1000 (BITS) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\browser.dll,-100 (Browser) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\bthserv.dll,-101 (bthserv) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\certprop.dll,-11 (CertPropSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: Intel(R) Content Protection HECI Service (cphs) - Intel Corporation - C:\Windows\SysWow64\IntelCpHeciSvc.exe
O23 - Service: @%SystemRoot%\system32\cryptsvc.dll,-1001 (CryptSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\cscsvc.dll,-200 (CscService) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @oleres.dll,-5012 (DcomLaunch) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\defragsvc.dll,-101 (defragsvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\dhcpcore.dll,-100 (Dhcp) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\UtcResources.dll,-3001 (DiagTrack) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\dnsapi.dll,-101 (Dnscache) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\dot3svc.dll,-1102 (dot3svc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\dps.dll,-500 (DPS) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\eapsvc.dll,-1 (EapHost) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\efssvc.dll,-100 (EFS) - Unknown owner - C:\Windows\System32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\ehome\ehrecvr.exe,-101 (ehRecvr) - Unknown owner - C:\Windows\ehome\ehRecvr.exe
O23 - Service: @%SystemRoot%\ehome\ehsched.exe,-101 (ehSched) - Unknown owner - C:\Windows\ehome\ehsched.exe
O23 - Service: @%SystemRoot%\system32\wevtsvc.dll,-200 (eventlog) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @comres.dll,-2450 (EventSystem) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\fxsresm.dll,-118 (Fax) - Unknown owner - C:\Windows\system32\fxssvc.exe (file missing)
O23 - Service: @%systemroot%\system32\fdPHost.dll,-100 (fdPHost) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\fdrespub.dll,-100 (FDResPub) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\FntCache.dll,-100 (FontCache) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @gpapi.dll,-112 (gpsvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: Service Google Update (gupdate) (gupdate) - Unknown owner - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Service Google Update (gupdatem) (gupdatem) - Unknown owner - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Google Software Updater (gusvc) - Google - C:\Program Files (x86)\Google\Common\Google Updater\GoogleUpdaterService.exe
O23 - Service: @%SystemRoot%\System32\hidserv.dll,-101 (hidserv) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\kmsvc.dll,-6 (hkmsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\ListSvc.dll,-100 (HomeGroupListener) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\provsvc.dll,-100 (HomeGroupProvider) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: Intel(R) Integrated Clock Controller Service - Intel(R) ICCS (ICCS) - Intel Corporation - C:\Program Files (x86)\Intel\Intel(R) Integrated Clock Controller Service\ICCProxy.exe
O23 - Service: @%SystemRoot%\system32\ieetwcollectorres.dll,-1000 (IEEtwCollectorService) - Unknown owner - C:\Windows\system32\IEEtwCollector.exe (file missing)
O23 - Service: Intel(R) HD Graphics Control Panel Service (igfxCUIService1.0.0.0) - Unknown owner - C:\Windows\system32\igfxCUIService.exe (file missing)
O23 - Service: @%SystemRoot%\system32\ikeext.dll,-501 (IKEEXT) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\IPBusEnum.dll,-102 (IPBusEnum) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\iphlpsvc.dll,-500 (iphlpsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @keyiso.dll,-100 (KeyIso) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @comres.dll,-2946 (KtmRm) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\srvsvc.dll,-100 (LanmanServer) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\wkssvc.dll,-100 (LanmanWorkstation) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\lltdres.dll,-1 (lltdsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\lmhsvc.dll,-101 (lmhosts) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: Ma-Config Agent (MaConfigAgent) - Unknown owner - C:\Program Files\ma-config.com\MaConfigAgent.exe
O23 - Service: MBAMScheduler - Malwarebytes Corporation - C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamscheduler.exe
O23 - Service: MBAMService - Malwarebytes Corporation - C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamservice.exe
O23 - Service: @%systemroot%\system32\mmcss.dll,-100 (MMCSS) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\FirewallAPI.dll,-23090 (MpsSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @comres.dll,-2797 (MSDTC) - Unknown owner - C:\Windows\System32\msdtc.exe (file missing)
O23 - Service: @%SystemRoot%\system32\iscsidsc.dll,-5000 (MSiSCSI) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\msimsg.dll,-27 (msiserver) - Unknown owner - C:\Windows\system32\msiexec.exe
O23 - Service: @%SystemRoot%\system32\qagentrt.dll,-6 (napagent) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\netlogon.dll,-102 (Netlogon) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\netman.dll,-109 (Netman) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\netprofm.dll,-202 (netprofm) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\nlasvc.dll,-1 (NlaSvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\nsisvc.dll,-200 (nsi) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\pnrpsvc.dll,-8004 (p2pimsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\p2psvc.dll,-8006 (p2psvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\pcasvc.dll,-1 (PcaSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\peerdistsvc.dll,-9000 (PeerDistSvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\sysWow64\perfhost.exe,-2 (PerfHost) - Unknown owner - C:\Windows\SysWow64\perfhost.exe
O23 - Service: @%systemroot%\system32\pla.dll,-500 (pla) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\umpnpmgr.dll,-100 (PlugPlay) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\pnrpauto.dll,-8002 (PNRPAutoReg) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\pnrpsvc.dll,-8000 (PNRPsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\polstore.dll,-5010 (PolicyAgent) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\umpo.dll,-100 (Power) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\profsvc.dll,-300 (ProfSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\psbase.dll,-300 (ProtectedStorage) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\qwave.dll,-1 (QWAVE) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%Systemroot%\system32\rasauto.dll,-200 (RasAuto) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%Systemroot%\system32\rasmans.dll,-200 (RasMan) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @regsvc.dll,-1 (RemoteRegistry) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%windir%\system32\RpcEpMap.dll,-1001 (RpcEptMapper) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\Locator.exe,-2 (RpcLocator) - Unknown owner - C:\Windows\system32\locator.exe (file missing)
O23 - Service: @oleres.dll,-5010 (RpcSs) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\samsrv.dll,-1 (SamSs) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\System32\SCardSvr.dll,-1 (SCardSvr) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\schedsvc.dll,-100 (Schedule) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\certprop.dll,-13 (SCPolicySvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\sdrsvc.dll,-107 (SDRSVC) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\seclogon.dll,-7001 (seclogon) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\Sens.dll,-200 (SENS) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\sensrsvc.dll,-1000 (SensrSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\SessEnv.dll,-1026 (SessionEnv) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\shsvcs.dll,-12288 (ShellHWDetection) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: Skype Updater (SkypeUpdate) - Skype Technologies - C:\Program Files (x86)\Skype\Updater\Updater.exe
O23 - Service: @%SystemRoot%\system32\snmptrap.exe,-3 (SNMPTRAP) - Unknown owner - C:\Windows\System32\snmptrap.exe (file missing)
O23 - Service: @%systemroot%\system32\spoolsv.exe,-1 (Spooler) - Unknown owner - C:\Windows\System32\spoolsv.exe (file missing)
O23 - Service: @%SystemRoot%\system32\sppsvc.exe,-101 (sppsvc) - Unknown owner - C:\Windows\system32\sppsvc.exe (file missing)
O23 - Service: @%SystemRoot%\system32\sppuinotify.dll,-103 (sppuinotify) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\ssdpsrv.dll,-100 (SSDPSRV) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\sstpsvc.dll,-200 (SstpSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wiaservc.dll,-9 (stisvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\swprv.dll,-103 (swprv) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\sysmain.dll,-1000 (SysMain) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\TabSvc.dll,-100 (TabletInputService) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\tapisrv.dll,-10100 (TapiSrv) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\tbssvc.dll,-100 (TBS) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\termsrv.dll,-268 (TermService) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\themeservice.dll,-8192 (Themes) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\mmcss.dll,-102 (THREADORDER) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\trkwks.dll,-1 (TrkWks) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\servicing\TrustedInstaller.exe,-100 (TrustedInstaller) - Unknown owner - C:\Windows\servicing\TrustedInstaller.exe
O23 - Service: @%SystemRoot%\system32\ui0detect.exe,-101 (UI0Detect) - Unknown owner - C:\Windows\system32\UI0Detect.exe (file missing)
O23 - Service: @%SystemRoot%\system32\umrdp.dll,-1000 (UmRdpService) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\upnphost.dll,-213 (upnphost) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\dwm.exe,-2000 (UxSms) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\vaultsvc.dll,-1003 (VaultSvc) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\vds.exe,-100 (vds) - Unknown owner - C:\Windows\System32\vds.exe (file missing)
O23 - Service: @%systemroot%\system32\vssvc.exe,-102 (VSS) - Unknown owner - C:\Windows\system32\vssvc.exe (file missing)
O23 - Service: vToolbarUpdater18.4.0 - Unknown owner - C:\Program Files (x86)\Common Files\AVG Secure Search\vToolbarUpdater\18.4.0\ToolbarUpdater.exe (file missing)
O23 - Service: @%SystemRoot%\system32\w32time.dll,-200 (W32Time) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\Wat\WatUX.exe,-601 (WatAdminSvc) - Unknown owner - C:\Windows\system32\Wat\WatAdminSvc.exe (file missing)
O23 - Service: @%systemroot%\system32\wbengine.exe,-104 (wbengine) - Unknown owner - C:\Windows\system32\wbengine.exe (file missing)
O23 - Service: @%systemroot%\system32\wbiosrvc.dll,-100 (WbioSrvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wcncsvc.dll,-3 (wcncsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\WcsPlugInService.dll,-200 (WcsPlugInService) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%systemroot%\system32\wdi.dll,-502 (WdiServiceHost) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\wdi.dll,-500 (WdiSystemHost) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\webclnt.dll,-100 (WebClient) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wecsvc.dll,-200 (Wecsvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wercplsupport.dll,-101 (wercplsupport) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wersvc.dll,-100 (WerSvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%ProgramFiles%\Windows Defender\MsMpRes.dll,-103 (WinDefend) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\system32\winhttp.dll,-100 (WinHttpAutoProxySvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%Systemroot%\system32\wbem\wmisvc.dll,-205 (Winmgmt) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%Systemroot%\system32\wsmsvc.dll,-101 (WinRM) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wlansvc.dll,-257 (Wlansvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%Systemroot%\system32\wbem\wmiapsrv.exe,-110 (wmiApSrv) - Unknown owner - C:\Windows\system32\wbem\WmiApSrv.exe (file missing)
O23 - Service: @%PROGRAMFILES%\Windows Media Player\wmpnetwk.exe,-101 (WMPNetworkSvc) - Unknown owner - C:\Program Files (x86)\Windows Media Player\wmpnetwk.exe (file missing)
O23 - Service: @%SystemRoot%\system32\wpcsvc.dll,-100 (WPCSvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wpdbusenum.dll,-100 (WPDBusEnum) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wscsvc.dll,-200 (wscsvc) - Unknown owner - C:\Windows\System32\svchost.exe
O23 - Service: @%systemroot%\system32\SearchIndexer.exe,-103 (WSearch) - Unknown owner - C:\Windows\system32\SearchIndexer.exe
O23 - Service: WtuSystemSupport - Unknown owner - C:\Program Files (x86)\AVG Web TuneUp\WtuSystemSupport.exe
O23 - Service: @%systemroot%\system32\wuaueng.dll,-105 (wuauserv) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\system32\wudfsvc.dll,-1000 (wudfsvc) - Unknown owner - C:\Windows\system32\svchost.exe
O23 - Service: @%SystemRoot%\System32\wwansvc.dll,-257 (WwanSvc) - Unknown owner - C:\Windows\system32\svchost.exe
--
End of file - 23097 bytes
7 réponses
-
Bonjour,
HijackThis n'est pas assez complet !
On peut commencer par vérifier ton PC.
Pourcela :- Télécharge ZHPDiag
- Sur la page de téléchargement de ZHPDiag, puis clique sur le bouton bleu "Nicolas Coolman - Télécharger".

- Lance le (si tu es sous Windows Vista, 7 ou 8, fais le par un clic-droit -> Exécuter en temps qu'administrateur
- Laisse toi guider lors de l'installation, puis clique sur "Terminer" à la fin.
- Deux raccourcis vont être créés sur le Bureau (ZHPDiag et ZHPFix) :
- lance ZHPDiag (si tu es sous Windows Vista, 7 ou 8, fais le par un clic-droit -> Exécuter en temps qu'administrateur

- Clique sur l'icône "Complet" pour faire une analyse complète puis patiente, ça peut durer quelques minutes.
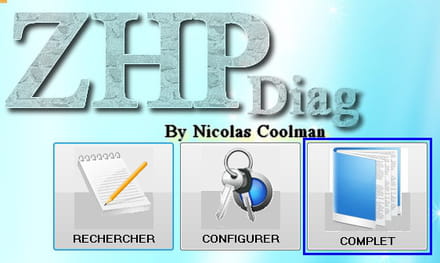
- A la fin de l'analyse, un rapport va s'ouvrir, enregistre le sur ton Bureau (Fichier -> Enregistrer sous).
- Rends toi sur pjjoint clique sur "Parcourir", sélectionne le rapport de ZHPDiag et clique sur Envoyer le fichier. Patiente pendant l'envoi du fichier, puis copie/colle le lien fourni dans ta prochaine réponse sur le forum.
-
Merci de m'aider voici le rapport:
~ Rapport de ZHPDiag v2015.5.5.46 - Nicolas Coolman (2015-05-05)
~ Lancé par Claude (2015-05-05 14:47:06)
~ Facebook : https://www.facebook.com/nicolascoolman1
~ Adresse du Forum https://nicolascoolman.eu
~ Traduit par Nicolas Coolman
~ Etat de la version : Version à jour.
~ Liste blanche : Désactivée par l'utilisateur
~ Elévation des Privilèges : OK
~ User Account Control (UAC): Deactivate by program
---\\ Navigateurs Internet
MSIE: Internet Explorer v11.0.9600.17728
GCIE: Google Chrome v42.0.2311.135 (Defaut)
---\\ Informations sur les produits Windows
~ Langage: Français
Windows Server License Manager Script : OK
~ Windows Operating System - Windows(R) 7, OEM_COA_NSLP channel
Windows ID Activation : OK
~ Windows Partial Key : MW72B
Windows License : OK
~ Windows Remaining Initializations Number : 3
Software Protection Service (Protection logicielle) : OK
Windows Automatic Updates : OK
Windows Activation Technologies : OK
Windows 7 Ultimate, 64-bit Service Pack 1 (Build 7601)
---\\ Logiciels de protection du système
AVG 2015 v15.0.5941
Malwarebytes Anti-Malware version 2.1.6.1022
Windows Defender W7 (Deactivate)
---\\ Logiciels d'optimisation du système
CCleaner v5.05
---\\ Logiciels de partage PeerToPeer
---\\ Surveillance de Logiciels
Adobe Flash Player 17 NPAPI
Adobe Acrobat Reader DC - Français
---\\ Informations sur le système
~ Processor: Intel64 Family 6 Model 55 Stepping 3, GenuineIntel
~ Operating System: 64 Bits
Boot mode: Normal (Normal boot)
Total RAM: 3797 MB (46% free)
System Restore: Activé (Enable)
System drive C: has 431 GB (92%) free of 466 GB
---\\ Mode de connexion au système
~ Computer Name: CLAUDE-PC
~ User Name: Claude
~ All Users Names: HomeGroupUser$, Claude, Administrateur,
~ Unselected Option: None
Logged in as Administrator
---\\ Variables d'environnement
~ System Unit : C:\
~ %AppZHP% : C:\Users\Claude\AppData\Roaming\ZHP\
~ %AppData% : C:\Users\Claude\AppData\Roaming\
~ %Desktop% : C:\Users\Claude\Desktop\
~ %Favorites% : C:\Users\Claude\Favorites\
~ %LocalAppData% : C:\Users\Claude\AppData\Local\
~ %StartMenu% : C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\
~ %Windir% : C:\Windows\
~ %System% : C:\Windows\System32\
---\\ Enumération des unités disques
C: Hard drive, Flash drive, Thumb drive (Free 431 Go of 466 Go)
D: CD-ROM drive (Not Inserted)
---\\ Etat du Centre de Sécurité Windows
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiSpywareOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiVirusOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] FirewallOverride: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\Explorer] NoActiveDesktopChanges: Modified
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\system] EnableLUA: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\NOHIDDEN] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\SHOWALL] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Associations] Application: OK
[HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon] Shell: OK
[HKLM\SYSTEM\CurrentControlSet\Services\COMSysApp] Type: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install] LastSuccessTime : OK
~ Security Center: 41 Scanned in 00mn 00s
---\\ Recherche particulière de fichiers génériques
[MD5.332FEAB1435662FC6C672E25BEB37BE3] - (.Microsoft Corporation - Explorateur Windows.) (.2011-02-25 - 01:19:30.) -- C:\Windows\Explorer.exe [2871808]
[MD5.94355C28C1970635A31B3FE52EB7CEBA] - (.Microsoft Corporation - Application de démarrage de Windows.) (.2009-07-13 - 20:39:52.) -- C:\Windows\System32\Wininit.exe [129024]
[MD5.77B35D0FC22A2D2EAC8D07C3F9784DBF] - (.Microsoft Corporation - Extensions Internet pour Win32.) (.2015-03-12 - 21:45:57.) -- C:\Windows\System32\wininet.dll [2358784]
[MD5.8CEBD9D0A0A879CDE9F36F4383B7CAEA] - (.Microsoft Corporation - Application d'ouverture de session Windows.) (.2014-07-16 - 21:07:24.) -- C:\Windows\System32\Winlogon.exe [455168]
[MD5.067FA52BFB59A56110A12312EF9AF243] - (.Microsoft Corporation - Bibliothèque de licences.) (.2010-11-20 - 22:24:16.) -- C:\Windows\System32\sppcomapi.dll [232448]
[MD5.FA886682CFC5D36718D3E436AACF10B9] - (.Microsoft Corporation - Ancillary Function Driver for WinSock.) (.2014-05-30 - 01:45:52.) -- C:\Windows\system32\Drivers\AFD.sys [497152]
[MD5.02062C0B390B7729EDC9E69C680A6F3C] - (.Microsoft Corporation - ATAPI IDE Miniport Driver.) (.2009-07-13 - 20:52:21.) -- C:\Windows\system32\Drivers\atapi.sys [24128]
[MD5.B8BD2BB284668C84865658C77574381A] - (.Microsoft Corporation - CD-ROM File System Driver.) (.2009-07-13 - 18:19:47.) -- C:\Windows\system32\Drivers\Cdfs.sys [92160]
[MD5.F036CE71586E93D94DAB220D7BDF4416] - (.Microsoft Corporation - SCSI CD-ROM Driver.) (.2010-11-20 - 22:23:47.) -- C:\Windows\system32\Drivers\Cdrom.sys [147456]
[MD5.9BB2EF44EAA163B29C4A4587887A0FE4] - (.Microsoft Corporation - DFS Namespace Client Driver.) (.2010-11-20 - 22:24:32.) -- C:\Windows\system32\Drivers\DfsC.sys [102400]
[MD5.97BFED39B6B79EB12CDDBFEED51F56BB] - (.Microsoft Corporation - High Definition Audio Bus Driver.) (.2010-11-20 - 22:23:47.) -- C:\Windows\system32\Drivers\HDAudBus.sys [122368]
[MD5.FA55C73D4AFFA7EE23AC4BE53B4592D3] - (.Microsoft Corporation - Pilote de port i8042.) (.2009-07-13 - 18:19:57.) -- C:\Windows\system32\Drivers\i8042prt.sys [105472]
[MD5.AF9B39A7E7B6CAA203B3862582E9F2D0] - (.Microsoft Corporation - IP Network Address Translator.) (.2009-07-13 - 19:10:03.) -- C:\Windows\system32\Drivers\IpNat.sys [116224]
[MD5.A5D9106A73DC88564C825D317CAC68AC] - (.Microsoft Corporation - Windows NT SMB Minirdr.) (.2011-04-26 - 21:40:40.) -- C:\Windows\system32\Drivers\MRxSmb.sys [158208]
[MD5.09594D1089C523423B32A4229263F068] - (.Microsoft Corporation - MBT Transport driver.) (.2010-11-20 - 22:23:51.) -- C:\Windows\system32\Drivers\netBT.sys [261632]
[MD5.1A29A59A4C5BA6F8C85062A613B7E2B2] - (.Microsoft Corporation - Pilote du système de fichiers NT.) (.2014-01-23 - 21:37:55.) -- C:\Windows\system32\Drivers\ntfs.sys [1684928]
[MD5.0086431C29C35BE1DBC43F52CC273887] - (.Microsoft Corporation - Pilote de port parallèle.) (.2009-07-13 - 19:00:41.) -- C:\Windows\system32\Drivers\Parport.sys [97280]
[MD5.471815800AE33E6F1C32FB1B97C490CA] - (.Microsoft Corporation - RAS L2TP mini-port/call-manager driver.) (.2010-11-20 - 22:24:33.) -- C:\Windows\system32\Drivers\Rasl2tp.sys [129536]
[MD5.1B6163C503398B23FF8B939C67747683] - (.Microsoft Corporation - Microsoft RDP Device redirector.) (.2010-11-20 - 22:25:07.) -- C:\Windows\system32\Drivers\rdpdr.sys [165888]
[MD5.548260A7B8654E024DC30BF8A7C5BAA4] - (.Microsoft Corporation - SMB Transport driver.) (.2009-07-13 - 19:09:09.) -- C:\Windows\system32\Drivers\smb.sys [93184]
[MD5.70988118145F5F10EF24720B97F35F65] - (.Microsoft Corporation - TDI Translation Driver.) (.2014-11-10 - 20:46:26.) -- C:\Windows\system32\Drivers\tdx.sys [119296]
[MD5.0D08D2F3B3FF84E433346669B5E0F639] - (.Microsoft Corporation - Pilote de cliché instantané du volume.) (.2010-11-20 - 22:23:47.) -- C:\Windows\system32\Drivers\volsnap.sys [295808]
~ Generic Processes: Scanned in 00mn 00s
---\\ Etat des fichiers cachés (Caché/Total)
~ Mes images (My Pictures) : 1/4
~ Mes Favoris (My Favorites) : 0/62
~ Mon Bureau (My Desktop) : 1/127
~ Menu demarrer (Programs) : 1/36
~ Hidden Files: Scanned in 00mn 00s
---\\ Processus lancés
[MD5.7E212E742BF06BF678AE35E9C1B74B8F] - (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) -- C:\Program Files (x86)\Malwarebytes Anti-Malware\mbam.exe [6212920] [PID.2720]
[MD5.BEE793728636C7E729937D317B5D1F6D] - (.AVG Technologies CZ, s.r.o. - AVG User Interface.) -- C:\Program Files (x86)\AVG\AVG2015\avgui.exe [3745232] [PID.3944]
[MD5.2555A094409BD20DAB7A97A5A539F21C] - (.Intel Corporation - iusb3mon.) -- C:\Program Files (x86)\Intel\Intel(R) USB 3.0 eXtensible Host Controller Driver\Application\iusb3mon.exe [296216] [PID.3992]
[MD5.8FFDB89A0FB7C8ABC3A8825E38047341] - (.Logitech Inc. - Logitech Webcam Software.) -- C:\Program Files (x86)\Logitech\LWS\Webcam Software\LWS.exe [204136] [PID.4000]
[MD5.E4C53CE8409DCFF708C790A0AC76398D] - (...) -- C:\Program Files (x86)\Logitech\LWS\Webcam Software\CameraHelperShell.exe [264040] [PID.2980]
[MD5.0ED961A25AC5C8EB29219513B7A7DEA5] - (.Almico Software (almico.com) - Pas de description.) -- C:\Program Files (x86)\SpeedFan\speedfan.exe [4841120] [PID.6136]
[MD5.7EDA1D46618C2F5801E4A47D80AE89ED] - (.Google Inc. - Google Chrome.) -- C:\Program Files (x86)\Google\Chrome\Application\chrome.exe [812872] [PID.5548]
[MD5.A299EA000386A57EBAA2699A95FB91E0] - (.Nicolas Coolman - ZHPDiag.) -- C:\Program Files (x86)\ZHPDiag\ZHPDiag.exe [8207360] [PID.4140]
[MD5.FFD80DC0CDA145C3376A5076360162C8] - (...) -- C:\Program Files (x86)\AVG Web TuneUp\WtuSystemSupport.exe [620056] [PID.1032] =>Toolbar.AVGSafeGuard
[MD5.929593D76589294BA3F74540298D1B3E] - (.Adobe Systems Incorporated - Adobe Acrobat Update Service.) -- C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [81088] [PID.1864]
[MD5.ABCDD4260B6AF7631322ED71D6379779] - (.AVG Technologies CZ, s.r.o. - AVG Firewall Service.) -- C:\Program Files (x86)\AVG\AVG2015\avgfws.exe [1517480] [PID.1916]
[MD5.ADDD8FF660E3758A4D3C6B47EE71356E] - (.AVG Technologies CZ, s.r.o. - AVG Identity Protection Service.) -- C:\Program Files (x86)\AVG\AVG2015\avgidsagent.exe [3438032] [PID.2108]
[MD5.95A260961EB2401BE0FAB69B7A8A049C] - (.AVG Technologies CZ, s.r.o. - AVG Watchdog Service.) -- C:\Program Files (x86)\AVG\AVG2015\avgwdsvc.exe [311792] [PID.2152]
[MD5.1F79342D9EB530A48742F651E570983A] - (.Microsoft Corporation - Updates Skype Click to Call.) -- C:\Program Files (x86)\Skype\Toolbars\AutoUpdate\SkypeC2CAutoUpdateSvc.exe [1390176] [PID.2180]
[MD5.E4938E0A376CF0B9D989EE5C0A146891] - (.Microsoft Corporation - Phone Number Recognition (PNR) module.) -- C:\Program Files (x86)\Skype\Toolbars\PNRSvc\SkypeC2CPNRSvc.exe [1767520] [PID.2304]
[MD5.516E29AD03BDF610CC36A95AE692FE42] - (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) -- C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamscheduler.exe [1871160] [PID.2560]
[MD5.2B983F067AEE3F9EB4DF5E97F45D21D1] - (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) -- C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamservice.exe [1080120] [PID.2984]
~ Processes Running: Scanned in 00mn 01s
---\\ Google Chrome, Démarrage,Recherche,Extensions (G0,G1,G2)
C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Preferences
---\\ Liste des dossiers d'extension Google Chrome
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\aapbdbdomjkkjkaonfhkkikfgjllcleb [__MSG_8969005060131950570__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\aohghmighlieiainnegkcijnfilokake [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\apdfllckaahabafndbhieahigkjlhalf [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\bgnkhhnnamicmpeenaelnjfhikgbkllg [__MSG_name__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\blpcfgokakmgnkcojhhkbfbldkacnbeo [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\coobgpohoikkiipiblmjeljniedjpjpf [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\felcaaldnbdncclmgdcncolpebgiejap [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\gighmmpiobklfepjocnamgkkbiglidom [AdBlock]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\gmlllbghnfkpflemihljekbapjopfjik [Bookmark Manager]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\habdflddkbkcmiglihdemgpijopehham [Currency Converter]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\lccekmodgklaepjeofjdjpbminllajkg [Chrome Hotword Shared Module]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\mlomiejdfkolichcflejclcbmpeaniij [Ghostery]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\nmmhkkegccagdldgiimedpiccmgmieda [__MSG_APP_NAME__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\pjkljhegncpnkpknbcohdijeoejaedia [__MSG_appName__]
~ Google Lines Browser: 28 Scanned in 00mn 01s
---\\ Mozilla Firefox, Plugins,Demarrage,Recherche,Extensions (P2,M0,M1,M2,M3)
P2 - FPN: [HKLM] [@adobe.com/FlashPlayer] - (...) -- C:\Windows\system32\Macromed\Flash\NPSWF64_17_0_0_169.dll
P2 - FPN: [HKLM] [@Microsoft.com/NpCtrl,version=1.0] - (. Microsoft Corporation - 5.1.30514.0.) -- C:\Program Files\Microsoft Silverlight\5.1.30514.0\npctrl.dll
~ Firefox Browser: 2 Scanned in 00mn 00s
---\\ Internet Explorer, Démarrage,Recherche,URLSearchHook, Phishing (R0,R1,R3,R4)
R0 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = https://www.google.ca/?gws_rd=ssl
R0 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = https://www.microsoft.com/fr-fr/
R0 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Start Page = https://www.microsoft.com/fr-fr/
R1 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Extensions Off Page = about:noadd-ons
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Security Risk Page = about:securityrisk
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Search_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Search Page = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Default_Page_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Default_Search_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Extensions Off Page = about:noadd-ons
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Security Risk Page = about:securityrisk
R3 - URLSearchHook: Microsoft Url Search Hook [64Bits] - {CFBFAE00-17A6-11D0-99CB-00C04FD64497} . (.Microsoft Corporation - Navigateur Internet.) (11.00.9600.17631 (winblue_r7.150111-1500)) -- C:\Windows\SysWOW64\ieframe.dll
R4 - HKLM\SOFTWARE\Microsoft\Internet Explorer\PhishingFilter,EnabledV8 = 1
R4 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\PhishingFilter,EnabledV8 = 1
~ IE Browser: 17 Scanned in 00mn 00s
---\\ Internet Explorer, Proxy Management (R5)
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = no key
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyEnable = 0
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,MigrateProxy = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,EnableHttp1_1 = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,AutoConfigProxy = wininet.dll
~ Proxy management: Scanned in 00mn 00s
---\\ Analyse des lignes F0, F1, F2, F3 - IniFiles, Autoloading programs
F2 - REG:system.ini: USERINIT=C:\Windows\system32\userinit.exe,
F2 - REG:system.ini: Shell=C:\Windows\explorer.exe
F2 - REG:system.ini: VMApplet=C:\Windows\System32\SystemPropertiesPerformance.exe
~ Keys: Scanned in 00mn 00s
---\\ Hosts file redirection (O1)
~ Le fichier hôte est sain (The hosts file is clean) (21)
~ Hosts File: Scanned in 00mn 00s
---\\ Browser Helper Objects de navigateur (O2)
O2 - BHO: Programme d'aide de l'Assistant de connexion au compte Microsoft [64Bits] - {9030D464-4C02-4ABF-8ECC-5164760863C6} . (.Microsoft Corp. - Microsoft® Windows Live ID Login Helper.) -- C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: Google Toolbar Helper [64Bits] - {AA58ED58-01DD-4d91-8333-CF10577473F7} . (.Google Inc. - Google Toolbar.) -- C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O2 - BHO: SkypeIEPluginBHO [64Bits] - {AE805869-2E5C-4ED4-8F7B-F1F7851A4497} . (.Microsoft Corporation - Skype Click to Call IE Add-on.) -- C:\Program Files (x86)\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O2 - BHO: Google Toolbar Notifier BHO [64Bits] - {AF69DE43-7D58-4638-B6FA-CE66B5AD205D} . (.Google Inc. - GoogleToolbarNotifier.) -- C:\Program Files (x86)\Google\GoogleToolbarNotifier\5.10.11023.1534\swg.dll
~ BHO: 8 Scanned in 00mn 00s
---\\ Internet Explorer Toolbars (O3)
O3 - Toolbar: Google Toolbar - [HKLM]{2318C2B1-4965-11d4-9B18-009027A5CD4F} . (.Google Inc. - Google Toolbar.) -- C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{2318C2B1-4965-11D4-9B18-009027A5CD4F} Clé orpheline
~ Toolbar: Scanned in 00mn 00s
---\\ Applications lancées au démarrage du système (O4)
O4 - HKLM\..\Run: [RTHDVCPL] . (.Realtek Semiconductor - Gestionnaire audio HD Realtek.) -- C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe =>.Realtek Semiconductor Corp
O4 - HKCU\..\Run: [Web Companion] C:\Program Files (x86)\Lavasoft\Web Companion\Application\WebCompanion.exe (.not file.)
O4 - HKCU\..\Run: [CCleaner Monitoring] . (.Piriform Ltd - CCleaner.) -- C:\Program Files\CCleaner\CCleaner64.exe =>.Piriform Ltd
O4 - HKLM\..\Wow6432Node\Run: [AVG_UI] . (.AVG Technologies CZ, s.r.o. - AVG User Interface.) -- C:\Program Files (x86)\AVG\AVG2015\avgui.exe
O4 - HKLM\..\Wow6432Node\Run: [USB3MON] . (.Intel Corporation - iusb3mon.) -- C:\Program Files (x86)\Intel\Intel(R) USB 3.0 eXtensible Host Controller Driver\Application\iusb3mon.exe
O4 - HKLM\..\Wow6432Node\Run: [LWS] . (.Logitech Inc. - Logitech Webcam Software.) -- C:\Program Files (x86)\Logitech\LWS\Webcam Software\LWS.exe =>.Logitech Inc
O4 - HKUS\S-1-5-19\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files (x86)\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files (x86)\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-19\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-21-2664199691-3854510578-2085819547-1000\..\Run: [Web Companion] C:\Program Files (x86)\Lavasoft\Web Companion\Application\WebCompanion.exe (.not file.)
O4 - HKUS\S-1-5-21-2664199691-3854510578-2085819547-1000\..\Run: [CCleaner Monitoring] . (.Piriform Ltd - CCleaner.) -- C:\Program Files\CCleaner\CCleaner64.exe =>.Piriform Ltd
~ Application: Scanned in 00mn 00s
---\\ Invisibilité de l'icône d'options IE dans le panneau de Configuration (O5)
O5 - control.ini: [HKLM\..\Control Panel] inetcpl.cpl=no
~ IE Control Panel: 1 Scanned in 00mn 00s
---\\ Boutons situés sur la barre d'outils principale d'Internet Explorer (O9)
O9 - Extra button: Skype Click to Call settings [64Bits] - {898EA8C8-E7FF-479B-8935-AEC46303B9E5} . (...) -- c:\program files (x86)\skype\toolbars\internet explorer x64\icon.ico
~ IE Extra Buttons: Scanned in 00mn 00s
---\\ Winsock hijacker (Layered Service Provider) (O10)
O10 - WLSP:\000000000001\Winsock LSP File . (.Microsoft Corporation - Network Location Awareness 2.) -- C:\Windows\system32\NLAapi.dll
O10 - WLSP:\000000000002\Winsock LSP File . (.Microsoft Corporation - Fournisseur Shim d'affectation de noms de messagerie.) -- C:\Windows\system32\napinsp.dll
O10 - WLSP:\000000000003\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000004\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000005\Winsock LSP File . (.Microsoft Corporation - Fournisseur de service Sockets 2.0 de Microsoft Windows.) -- C:\Windows\system32\mswsock.dll =>.Microsoft Corporation
O10 - WLSP:\000000000006\Winsock LSP File . (.Microsoft Corporation - LDAP RnR Provider DLL.) -- C:\Windows\system32\winrnr.dll
O10 - WLSP:\000000000007\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
O10 - WLSP:\000000000008\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
~ Winsock: 8 Scanned in 00mn 00s
---\\ Modification Domaine/Adresses DNS (O17)
O17 - HKLM\System\CCS\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpNameServer = 192.168.2.1
O17 - HKLM\System\CCS\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpDomain = gateway.2wire.net
O17 - HKLM\System\CS1\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpNameServer = 192.168.2.1
O17 - HKLM\System\CS1\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpDomain = gateway.2wire.net
O17 - HKLM\System\CS2\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpNameServer = 192.168.2.1
O17 - HKLM\System\CS2\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpDomain = gateway.2wire.net
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = 192.168.2.1
~ Domain: Scanned in 00mn 00s
---\\ Protocole additionnel (O18)
O18 - Handler: wlpg [64Bits] - {E43EF6CD-A37A-4A9B-9E6F-83F89B8E6324} . (...) --
O18 - Filter: application/x-msdownload [64Bits] - {1E66F26B-79EE-11D2-8710-00C04F79ED0D} . (.Microsoft Corporation - Microsoft .NET Runtime Execution Engine.) -- C:\Windows\System32\mscoree.dll =>.Microsoft Corporation
~ Protocole Additionnel: Scanned in 00mn 00s
---\\ Clé de Registre autorun ShellServiceObjectDelayLoad (SSO/SSODL) (O21)
O21 - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} - CLSID or File not found.
~ SSODL: 1 Scanned in 00mn 00s
---\\ Liste des services NT non Microsoft et non désactivés (O23)
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) . (.Adobe Systems Incorporated - Adobe Acrobat Update Service.) - C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: Pare-feu AVG (avgfws) . (.AVG Technologies CZ, s.r.o. - AVG Firewall Service.) - C:\Program Files (x86)\AVG\AVG2015\avgfws.exe
O23 - Service: AVGIDSAgent (AVGIDSAgent) . (.AVG Technologies CZ, s.r.o. - AVG Identity Protection Service.) - C:\Program Files (x86)\AVG\AVG2015\avgidsagent.exe
O23 - Service: AVG WatchDog (avgwd) . (.AVG Technologies CZ, s.r.o. - AVG Watchdog Service.) - C:\Program Files (x86)\AVG\AVG2015\avgwdsvc.exe
O23 - Service: Service Google Update (gupdate) (gupdate) . (.Google Inc. - Programme d'installation de Google.) - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe =>.Google Inc
O23 - Service: Intel(R) HD Graphics Control Panel Service (igfxCUIService1.0.0.0) . (.Intel Corporation - igfxCUIService Module.) - C:\Windows\System32\igfxCUIService.exe
O23 - Service: Ma-Config Agent (MaConfigAgent) . (.CybelSoft - Service de détection matériel.) - C:\Program Files\ma-config.com\MaConfigAgent.exe
O23 - Service: (MBAMScheduler) . (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) - C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamscheduler.exe
O23 - Service: (MBAMService) . (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) - C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamservice.exe
O23 - Service: Skype Updater (SkypeUpdate) . (.Skype Technologies - Skype Updater Service.) - C:\Program Files (x86)\Skype\Updater\Updater.exe
O23 - Service: (vToolbarUpdater18.4.0) . (...) - C:\Program Files (x86)\Common Files\AVG Secure Search\vToolbarUpdater\18.4.0\ToolbarUpdater.exe (.not file.) =>Toolbar.AVGSearch
O23 - Service: WtuSystemSupport (WtuSystemSupport) . (...) - C:\Program Files (x86)\AVG Web TuneUp\WtuSystemSupport.exe =>Toolbar.AVGSafeGuard
~ Services: 11 Scanned in 00mn 28s
---\\ Enumération Active Desktop & MHTML Editor (O24)
O24 - Default MHTML Editor: Last - .(...) - (.not file.)
~ Desktop Component: 4 Scanned in 00mn 00s
---\\ Enumère les données de BootExecute (BEX) (O34)
O34 - HKLM BootExecute: (autocheck autochk *) - File not found
~ BEX: 1 Scanned in 00mn 00s
---\\ Tâches planifiées en automatique (O39)
[MD5.64495D9B3C4B640230E9265C23A33F55] [APT] [Adobe Acrobat Update Task] (.Adobe Systems Incorporated.) -- C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe [1018056]
[MD5.B04A4810C6CC205F9DC72DC22E4AB236] [APT] [Adobe Flash Player Updater] (.Adobe Systems Incorporated.) -- C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe [268464]
[MD5.1F014EA12ECB13C909DA9395E9CD3D18] [APT] [CCleanerSkipUAC] (.Piriform Ltd.) -- C:\Program Files\CCleaner\CCleaner.exe [6278424]
[MD5.506708142BC63DABA64F2D3AD1DCD5BF] [APT] [GoogleUpdateTaskMachineCore] (.Google Inc..) -- C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [116648]
[MD5.506708142BC63DABA64F2D3AD1DCD5BF] [APT] [GoogleUpdateTaskMachineUA] (.Google Inc..) -- C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [116648]
[MD5.D41D8CD98F00B204E9800998ECF8427E] [APT] [MyDefrag v4.3.1 Daily] (...) -- C:\Program Files\MyDefrag v4.3.1\Scripts\AutomaticDaily.MyD" [5663]
[MD5.D41D8CD98F00B204E9800998ECF8427E] [APT] [MyDefrag v4.3.1 Monthly] (...) -- C:\Program Files\MyDefrag v4.3.1\Scripts\AutomaticMonthly.MyD" [5626]
[MD5.38272D7EAE1D5348AF235E157DAFE556] [APT] [{67D77F24-43DB-451A-AED0-80DD1D8CC230}] (.Lavasoft.) -- C:\Users\Claude\Downloads\WcInstaller.exe [303336]
O39 - APT: Adobe Flash Player Updater - (.Adobe Systems Incorporated.) -- C:\Windows\Tasks\Adobe Flash Player Updater.job [1002]
O39 - APT: Adobe Flash Player Updater - (.Adobe Systems Incorporated.) -- C:\Windows\System32\Tasks\Adobe Flash Player Updater [1002]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineCore.job [1066]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineCore [1066]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineUA.job [1070]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineUA [1070]
~ Scheduled Task: 12 Scanned in 00mn 05s
---\\ Composants installés (ActiveSetup Installed Components) (O40)
O40 - ASIC: Microsoft Windows Media Player [64Bits] - >{22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Microsoft Windows Media Player 12.0 [64Bits] - {22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Windows Media Player Extension.) -- C:\Windows\SysWOW64\wmpdxm.dll =>.Microsoft Corporation
O40 - ASIC: Themes Setup [64Bits] - {2C7339CF-2B09-4501-B3F3-F3508C9228ED} . (.Microsoft Corporation - API Windows Theme.) -- C:\Windows\System32\themeui.dll
O40 - ASIC: Microsoft Windows [64Bits] - {44BBA840-CC51-11CF-AAFA-00AA00B6015C} . (.Microsoft Corporation - Windows Mail.) -- C:\Program Files (x86)\Windows Mail\WinMail.exe =>.Microsoft Corporation
O40 - ASIC: Browsing Enhancements [64Bits] - {630b1da0-b465-11d1-9948-00c04f98bbc9} . (.Microsoft Corporation - Extension Shell dossier FTP Microsoft Internet Explorer..) -- C:\Windows\System32\msieftp.dll
O40 - ASIC: Microsoft Windows Media Player [64Bits] - {6BF52A52-394A-11d3-B153-00C04F79FAA6} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Disable SSL3 [64Bits] - {7D715857-A67C-4C2F-A929-038448584D63} . (.Microsoft Corporation - Utilitaire d'initialisation d'Internet Explorer par utilisateur.) -- C:\Windows\System32\ie4uinit.exe
O40 - ASIC: Windows Desktop Update [64Bits] - {89820200-ECBD-11cf-8B85-00AA005B4340} . (.Microsoft Corporation - DLL commune du shell Windows.) -- C:\Windows\System32\shell32.dll
O40 - ASIC: Web Platform Customizations [64Bits] - {89820200-ECBD-11cf-8B85-00AA005B4383} . (.Microsoft Corporation - Utilitaire d'initialisation d'Internet Explorer par utilisateur.) -- C:\Windows\System32\ie4uinit.exe
O40 - ASIC: (no name) [64Bits] - {89B4C1CD-B018-4511-B0A1-5476DBF70820} . (.Microsoft Corporation - Microsoft .NET IE SECURITY REGISTRATION.) -- C:\Windows\system32\mscories.dll
~ Active Setup: 10 Scanned in 00mn 00s
---\\ Pilotes lancés au démarrage du système (O41)
O41 - Driver: C:\Windows\System32\drivers\afd.sys (AFD) . (.Microsoft Corporation - Ancillary Function Driver for WinSock.) - C:\Windows\system32\drivers\afd.sys
O41 - Driver: (Avgdiska) . (.AVG Technologies CZ, s.r.o. - AVG File Vault Driver.) - C:\Windows\System32\DRIVERS\avgdiska.sys
O41 - Driver: (Avgfwfd) . (.AVG Technologies CZ, s.r.o. - AVG Filter Driver.) - C:\Windows\System32\DRIVERS\avgfwd6a.sys
O41 - Driver: (AVGIDSDriver) . (.AVG Technologies CZ, s.r.o. - AVG IDS Application Activity Monitor Driver.) - C:\Windows\System32\DRIVERS\avgidsdrivera.sys
O41 - Driver: (Avgldx64) . (.AVG Technologies CZ, s.r.o. - AVG AVI Loader Driver.) - C:\Windows\System32\DRIVERS\avgldx64.sys
O41 - Driver: (Avgtdia) . (.AVG Technologies CZ, s.r.o. - AVG Network connection watcher.) - C:\Windows\System32\DRIVERS\avgtdia.sys
O41 - Driver: (blbdrive) . (.Microsoft Corporation - BLB Drive Driver.) - C:\Windows\System32\DRIVERS\blbdrive.sys
O41 - Driver: (cdrom) . (.Microsoft Corporation - SCSI CD-ROM Driver.) - C:\Windows\System32\DRIVERS\cdrom.sys
O41 - Driver: C:\Windows\System32\cscsvc.dll (CSC) . (.Microsoft Corporation - Windows Client Side Caching Driver.) - C:\Windows\System32\drivers\csc.sys
O41 - Driver: C:\Windows\System32\drivers\dfsc.sys (DfsC) . (.Microsoft Corporation - DFS Namespace Client Driver.) - C:\Windows\System32\Drivers\dfsc.sys
O41 - Driver: C:\Windows\System32\drivers\discache.sys (discache) . (.Microsoft Corporation - System Indexer/Cache Driver.) - C:\Windows\System32\drivers\discache.sys
O41 - Driver: (mssmbios) . (.Microsoft Corporation - System Management BIOS Driver.) - C:\Windows\System32\DRIVERS\mssmbios.sys
O41 - Driver: (NetBIOS) . (.Microsoft Corporation - NetBIOS interface driver.) - C:\Windows\System32\DRIVERS\netbios.sys
O41 - Driver: C:\Windows\System32\drivers\netbt.sys (NetBT) . (.Microsoft Corporation - MBT Transport driver.) - C:\Windows\System32\DRIVERS\netbt.sys
O41 - Driver: C:\Windows\System32\drivers\nsiproxy.sys (nsiproxy) . (.Microsoft Corporation - NSI Proxy.) - C:\Windows\System32\drivers\nsiproxy.sys
O41 - Driver: C:\Windows\System32\drivers\pacer.sys (Psched) . (.Microsoft Corporation - Planificateur de paquets QoS.) - C:\Windows\System32\DRIVERS\pacer.sys
O41 - Driver: C:\Windows\System32\wkssvc.dll (rdbss) . (.Microsoft Corporation - Pilote du sous-système de mise en mémoire t.) - C:\Windows\System32\DRIVERS\rdbss.sys
O41 - Driver: C:\Windows\System32\DRIVERS\RDPCDD.sys (RDPCDD) . (.Microsoft Corporation - RDP Miniport.) - C:\Windows\System32\DRIVERS\RDPCDD.sys
O41 - Driver: C:\Windows\System32\drivers\RDPENCDD.sys (RDPENCDD) . (.Microsoft Corporation - RDP Encoder Miniport.) - C:\Windows\System32\drivers\rdpencdd.sys
O41 - Driver: C:\Windows\System32\drivers\RdpRefMp.sys (RDPREFMP) . (.Microsoft Corporation - RDP Reflector Driver Miniport.) - C:\Windows\System32\drivers\rdprefmp.sys
O41 - Driver: (Serial) . (.Microsoft Corporation - Pilote de périphérique série.) - C:\Windows\System32\DRIVERS\serial.sys
O41 - Driver: C:\Windows\System32\tcpipcfg.dll (tdx) . (.Microsoft Corporation - TDI Translation Driver.) - C:\Windows\System32\DRIVERS\tdx.sys
O41 - Driver: (TermDD) . (.Microsoft Corporation - Remote Desktop Server Driver.) - C:\Windows\System32\DRIVERS\termdd.sys
O41 - Driver: (VgaSave) . (.Microsoft Corporation - VGA/Super VGA Video Driver.) - C:\Windows\system32\drivers\vga.sys
O41 - Driver: C:\Windows\System32\rascfg.dll (Wanarpv6) . (.Microsoft Corporation - MS Remote Access and Routing ARP Driver.) - C:\Windows\System32\DRIVERS\wanarp.sys
O41 - Driver: (WfpLwf) . (.Microsoft Corporation - WFP NDIS 6.20 Lightweight Filter Driver.) - C:\Windows\System32\DRIVERS\wfplwf.sys
O41 - Driver: Environnement de prise en charge de Fournisseur de services non-IFS Windows Sockets 2.0 (ws2ifsl) . (.Microsoft Corporation - Couche IFS Winsock2.) - C:\Windows\system32\drivers\ws2ifsl.sys
~ Drivers: 81 Scanned in 00mn 00s
---\\ Logiciels installés (O42)
O42 - Logiciel: AVG 2015 - (.AVG Technologies.) [HKLM][64Bits] -- AVG
O42 - Logiciel: AVG 2015 - (.AVG Technologies.) [HKLM][64Bits] -- {3A1B060C-5D3F-4FFA-914E-6292A6F7464E}
O42 - Logiciel: AVG 2015 - (.AVG Technologies.) [HKLM][64Bits] -- {B38CFE4C-C9C4-460B-8353-F56DF2AC3877}
O42 - Logiciel: AVG Web TuneUp - (.AVG Technologies.) [HKLM][64Bits] -- AVG Web TuneUp =>Toolbar.AVGSafeGuard
O42 - Logiciel: Adobe Acrobat Reader DC - Français - (.Adobe Systems Incorporated.) [HKLM][64Bits] -- {AC76BA86-7AD7-1036-7B44-AC0F074E4100}
O42 - Logiciel: Adobe Flash Player 17 ActiveX - (.Adobe Systems Incorporated.) [HKLM][64Bits] -- Adobe Flash Player ActiveX
O42 - Logiciel: Adobe Flash Player 17 NPAPI - (.Adobe Systems Incorporated.) [HKLM][64Bits] -- Adobe Flash Player NPAPI
O42 - Logiciel: CCleaner - (.Piriform.) [HKLM][64Bits] -- CCleaner
O42 - Logiciel: CDBurnerXP - (.CDBurnerXP.) [HKLM][64Bits] -- {7E265513-8CDA-4631-B696-F40D983F3B07}_is1
O42 - Logiciel: CameraHelperMsi - (.Logitech.) [HKLM][64Bits] -- {15634701-BACE-4449-8B25-1567DA8C9FD3}
O42 - Logiciel: ConvertXtoDVD 4.2.0.0 - (...) [HKLM][64Bits] -- {DB6AB705-C9BD-40E3-8929-2EA57F36A4FF}_is1
O42 - Logiciel: D3DX10 - (.Microsoft.) [HKLM][64Bits] -- {E09C4DB7-630C-4F06-A631-8EA7239923AF}
O42 - Logiciel: Galerie de photos - (.Microsoft Corporation.) [HKLM][64Bits] -- {439B34FF-F74E-4807-B5E2-4B758551DA6B}
O42 - Logiciel: Google Chrome - (.Google Inc..) [HKLM][64Bits] -- Google Chrome
O42 - Logiciel: Google Toolbar for Internet Explorer - (.Google Inc..) [HKLM][64Bits] -- {18455581-E099-4BA8-BC6B-F34B2F06600C}
O42 - Logiciel: Google Toolbar for Internet Explorer - (.Google Inc..) [HKLM][64Bits] -- {2318C2B1-4965-11d4-9B18-009027A5CD4F}
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM][64Bits] -- {60EC980A-BDA2-4CB6-A427-B07A5498B4CA}
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM][64Bits] -- {A92DAB39-4E2C-4304-9AB6-BC44E68B55E2}
O42 - Logiciel: Intel(R) Chipset Device Software - (.Intel Corporation.) [HKLM][64Bits] -- {9A431D9C-9FC9-454E-AC8D-15DBAA6ED0F7}
O42 - Logiciel: Intel(R) Driver Update Utility 2.0 - (.Intel.) [HKLM][64Bits] -- {59DB38EB-F864-4E10-841D-38CFBCF864B0}
O42 - Logiciel: Intel(R) Processor Graphics - (.Intel Corporation.) [HKLM][64Bits] -- {F0E3AD40-2BBD-4360-9C76-B9AC9A5886EA}
O42 - Logiciel: Intel(R) USB 3.0 eXtensible Host Controller Driver - (.Intel Corporation.) [HKLM][64Bits] -- {240C3DDD-C5E9-4029-9DF7-95650D040CF2}
O42 - Logiciel: Intel® Driver Update Utility - (.Intel.) [HKLM][64Bits] -- {8409c4f7-2340-4933-a304-5d37db4fb48b}
O42 - Logiciel: Junk Mail filter update - (.Microsoft Corporation.) [HKLM][64Bits] -- {0BE9E708-5DC0-4963-9CFD-0AA519090E79}
O42 - Logiciel: LWS Facebook - (.Logitech.) [HKLM][64Bits] -- {FF167195-9EE4-46C0-8CD7-FBA3457E88AB}
O42 - Logiciel: LWS Gallery - (.Logitech.) [HKLM][64Bits] -- {6F76EC3C-34B1-436E-97FB-48C58D7BEDCD}
O42 - Logiciel: LWS Help_main - (.Logitech.) [HKLM][64Bits] -- {1651216E-E7AD-4250-92A1-FB8ED61391C9}
O42 - Logiciel: LWS Launcher - (.Logitech.) [HKLM][64Bits] -- {83C8FA3C-F4EA-46C4-8392-D3CE353738D6}
O42 - Logiciel: LWS Motion Detection - (.Logitech.) [HKLM][64Bits] -- {71E66D3F-A009-44AB-8784-75E2819BA4BA}
O42 - Logiciel: LWS Pictures And Video - (.Logitech.) [HKLM][64Bits] -- {08610298-29AE-445B-B37D-EFBE05802967}
O42 - Logiciel: LWS Twitter - (.Logitech.) [HKLM][64Bits] -- {174A3B31-4C43-43DD-866F-73C9DB887B48}
O42 - Logiciel: LWS WLM Plugin - (.Logitech.) [HKLM][64Bits] -- {9DAEA76B-E50F-4272-A595-0124E826553D}
O42 - Logiciel: LWS Webcam Software - (.Logitech.) [HKLM][64Bits] -- {8937D274-C281-42E4-8CDB-A0B2DF979189}
O42 - Logiciel: LWS YouTube Plugin - (.Logitech.) [HKLM][64Bits] -- {21DF0294-6B9D-4741-AB6F-B2ABFBD2387E}
O42 - Logiciel: LavasoftTcpService - (.Lavasoft.) [HKLM][64Bits] -- {90CF05DE-735F-42AB-A52A-F447FDFBE207}
O42 - Logiciel: Logiciel pour périphérique à chipset Intel® - (.Intel(R) Corporation.) [HKLM][64Bits] -- {5a6a5d15-d5af-417c-b08f-f7e5eb1f98af}
O42 - Logiciel: Logitech Webcam Software - (.Logitech Inc..) [HKLM][64Bits] -- {D40EB009-0499-459c-A8AF-C9C110766215} =>.Logitech Inc
O42 - Logiciel: MSVCRT - (.Microsoft.) [HKLM][64Bits] -- {8DD46C6A-0056-4FEC-B70A-28BB16A1F11F}
O42 - Logiciel: MSVCRT110 - (.Microsoft.) [HKLM][64Bits] -- {8E14DDC8-EA60-4E18-B3E3-1937104D5BDA}
O42 - Logiciel: MSVCRT110_amd64 - (.Microsoft.) [HKLM][64Bits] -- {E9FA781F-3E80-4399-825A-AD3E11C28C77}
O42 - Logiciel: MSVCRT_amd64 - (.Microsoft.) [HKLM][64Bits] -- {D0B44725-3666-492D-BEF6-587A14BD9BD9}
O42 - Logiciel: Ma-Config.com (64 bits) - (.Cybelsoft.) [HKLM][64Bits] -- {7713B2C6-A0E1-47EA-BD3B-B22F22F7C010}
O42 - Logiciel: Malwarebytes Anti-Malware version 2.1.6.1022 - (.Malwarebytes Corporation.) [HKLM][64Bits] -- Malwarebytes Anti-Malware_is1
O42 - Logiciel: Microsoft Silverlight - (.Microsoft Corporation.) [HKLM][64Bits] -- {89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}
O42 - Logiciel: MyDefrag v4.3.1 - (.J.C. Kessels.) [HKLM][64Bits] -- MyDefrag v4.3.1_is1
O42 - Logiciel: Realtek Ethernet Controller Driver - (.Realtek.) [HKLM][64Bits] -- {8833FFB6-5B0C-4764-81AA-06DFEED9A476}
O42 - Logiciel: Realtek High Definition Audio Driver - (.Realtek Semiconductor Corp..) [HKLM][64Bits] -- {F132AF7F-7BCA-4EDE-8A7C-958108FE7DBC}
O42 - Logiciel: Revo Uninstaller 1.95 - (.VS Revo Group.) [HKLM][64Bits] -- Revo Uninstaller
O42 - Logiciel: Skype Click to Call - (.Microsoft Corporation.) [HKLM][64Bits] -- {6D1221A9-17BF-4EC0-81F2-27D30EC30701}
O42 - Logiciel: Skype(TM) 7.4 - (.Skype Technologies S.A..) [HKLM][64Bits] -- {24991BA0-F0EE-44AD-9CC8-5EC50AECF6B7}
O42 - Logiciel: SpeedFan (remove only) - (...) [HKLM][64Bits] -- SpeedFan
O42 - Logiciel: Visual Studio 2012 x64 Redistributables - (.AVG Technologies.) [HKLM][64Bits] -- {8C775E70-A791-4DA8-BCC3-6AB7136F4484}
O42 - Logiciel: Visual Studio 2012 x86 Redistributables - (.AVG Technologies CZ, s.r.o..) [HKLM][64Bits] -- {98EFF19A-30AB-4E4B-B943-F06B1C63EBF8}
O42 - Logiciel: WinRAR 5.21 (64-bit) - (.win.rar GmbH.) [HKLM][64Bits] -- WinRAR archiver
O42 - Logiciel: erLT - (.Logitech, Inc..) [HKLM][64Bits] -- {3EE9BCAE-E9A9-45E5-9B1C-83A4D357E05C}
~ Logic: 37 Scanned in 00mn 00s
---\\ HKCU & HKLM Software Keys
[HKCU\Software\AVG Web TuneUp] =>Toolbar.AVGSafeGuard
[HKCU\Software\Adobe]
[HKCU\Software\AppDataLow]
[HKCU\Software\Avg Secure Update]
[HKCU\Software\Avg]
[HKCU\Software\Canneverbe Limited]
[HKCU\Software\Classes]
[HKCU\Software\Clients]
[HKCU\Software\Clubic]
[HKCU\Software\Digital River]
[HKCU\Software\Freemake]
[HKCU\Software\Google]
[HKCU\Software\IM Providers]
[HKCU\Software\Intel]
[HKCU\Software\Leadertech]
[HKCU\Software\LogiShrd]
[HKCU\Software\Logitech]
[HKCU\Software\Macromedia]
[HKCU\Software\MozillaPlugins]
[HKCU\Software\MyDefrag]
[HKCU\Software\Netscape]
[HKCU\Software\Piriform]
[HKCU\Software\Policies]
[HKCU\Software\Realtek]
[HKCU\Software\Skype]
[HKCU\Software\SpeedFan]
[HKCU\Software\Trolltech]
[HKCU\Software\VSO]
[HKCU\Software\VSRevoGroup]
[HKCU\Software\WinRAR SFX]
[HKCU\Software\WinRAR]
[HKCU\Software\Wow6432Node]
[HKCU\Software\ZebHelpProcess Helper]
[HKLM\Software\ATI Technologies]
[HKLM\Software\CBSTEST]
[HKLM\Software\Classes]
[HKLM\Software\Clients]
[HKLM\Software\DTS]
[HKLM\Software\Dolby]
[HKLM\Software\IM Providers]
[HKLM\Software\Intel]
[HKLM\Software\Khronos]
[HKLM\Software\Knowles]
[HKLM\Software\Logitech]
[HKLM\Software\Macromedia]
[HKLM\Software\MozillaPlugins]
[HKLM\Software\Nahimic]
[HKLM\Software\Nuance]
[HKLM\Software\ODBC]
[HKLM\Software\Piriform]
[HKLM\Software\Policies]
[HKLM\Software\RTLSetup]
[HKLM\Software\Realtek]
[HKLM\Software\RegisteredApplications]
[HKLM\Software\SRS Labs]
[HKLM\Software\SonicFocus]
[HKLM\Software\Sonic]
[HKLM\Software\SoundResearch]
[HKLM\Software\Waves Audio]
[HKLM\Software\WinRAR]
[HKLM\Software\Wow6432Node\AVG Tuneup]
[HKLM\Software\Wow6432Node\Adguard]
[HKLM\Software\Wow6432Node\Adobe]
[HKLM\Software\Wow6432Node\AdwCleaner]
[HKLM\Software\Wow6432Node\Avg]
[HKLM\Software\Wow6432Node\Canneverbe Limited]
[HKLM\Software\Wow6432Node\Classes]
[HKLM\Software\Wow6432Node\Clients]
[HKLM\Software\Wow6432Node\Freemake]
[HKLM\Software\Wow6432Node\Google]
[HKLM\Software\Wow6432Node\IM Providers]
[HKLM\Software\Wow6432Node\Intel]
[HKLM\Software\Wow6432Node\Khronos]
[HKLM\Software\Wow6432Node\Lavasoft]
[HKLM\Software\Wow6432Node\Logitech]
[HKLM\Software\Wow6432Node\Macromedia]
[HKLM\Software\Wow6432Node\Malwarebytes' Anti-Malware]
[HKLM\Software\Wow6432Node\MozillaPlugins]
[HKLM\Software\Wow6432Node\Nuance]
[HKLM\Software\Wow6432Node\ODBC]
[HKLM\Software\Wow6432Node\Policies]
[HKLM\Software\Wow6432Node\Realtek Semiconductor Corp.]
[HKLM\Software\Wow6432Node\Realtek]
[HKLM\Software\Wow6432Node\RegisteredApplications]
[HKLM\Software\Wow6432Node\SRS Labs]
[HKLM\Software\Wow6432Node\Skype]
[HKLM\Software\Wow6432Node\VSO]
[HKLM\Software\Wow6432Node\logishrd]
[HKLM\Software\Wow6432Node]
[HKLM\Software\Yamaha APO]
[HKLM\Software\cybelsoft]
~ Key Software: 188 Scanned in 00mn 00s
---\\ Contenu des dossiers Programs/ProgramFiles/ProgramData/AppData (O43)
O43 - CFD: 2015-05-05 - 01:10:38 - [] ----D C:\Program Files (x86)\Adguard
O43 - CFD: 2015-05-04 - 17:17:53 - [] ----D C:\Program Files (x86)\Adobe
O43 - CFD: 2015-05-04 - 17:02:58 - [] ----D C:\Program Files (x86)\AVG
O43 - CFD: 2015-05-04 - 17:09:46 - [] ----D C:\Program Files (x86)\AVG Web TuneUp =>Toolbar.AVGSafeGuard
O43 - CFD: 2015-05-05 - 11:59:41 - [] ----D C:\Program Files (x86)\CDBurnerXP
O43 - CFD: 2015-05-05 - 12:27:03 - [] ----D C:\Program Files (x86)\Common Files
O43 - CFD: 2015-05-04 - 20:58:12 - [] ----D C:\Program Files (x86)\Google
O43 - CFD: 2015-05-04 - 19:45:43 - [] --H-D C:\Program Files (x86)\InstallShield Installation Information
O43 - CFD: 2015-05-05 - 01:23:06 - [] ----D C:\Program Files (x86)\Intel
O43 - CFD: 2015-05-05 - 09:56:10 - [] ----D C:\Program Files (x86)\Intel Driver Update Utility
O43 - CFD: 2015-05-05 - 11:21:45 - [] ----D C:\Program Files (x86)\Internet Explorer
O43 - CFD: 2015-05-04 - 20:42:58 - [] ----D C:\Program Files (x86)\Lavasoft
O43 - CFD: 2015-05-05 - 09:11:11 - [] ----D C:\Program Files (x86)\Logitech
O43 - CFD: 2015-05-04 - 21:06:18 - [] ----D C:\Program Files (x86)\Malwarebytes Anti-Malware
O43 - CFD: 2015-05-04 - 17:50:59 - [] ----D C:\Program Files (x86)\Microsoft Silverlight
O43 - CFD: 2015-05-04 - 18:54:48 - [] ----D C:\Program Files (x86)\Microsoft SQL Server Compact Edition
O43 - CFD: 2015-05-04 - 18:34:29 - [] ----D C:\Program Files (x86)\Microsoft.NET
O43 - CFD: 2009-07-14 - 01:32:38 - [] ----D C:\Program Files (x86)\MSBuild
O43 - CFD: 2015-05-04 - 19:45:47 - [] ----D C:\Program Files (x86)\Realtek
O43 - CFD: 2009-07-14 - 01:32:38 - [] ----D C:\Program Files (x86)\Reference Assemblies
O43 - CFD: 2015-05-04 - 20:34:31 - [] R---D C:\Program Files (x86)\Skype
O43 - CFD: 2015-05-05 - 14:11:48 - [] ----D C:\Program Files (x86)\SpeedFan
O43 - CFD: 2015-05-04 - 20:07:25 - [0] --H-D C:\Program Files (x86)\Temp
O43 - CFD: 2009-07-14 - 00:57:06 - [0] --H-D C:\Program Files (x86)\Uninstall Information
O43 - CFD: 2015-05-05 - 12:45:16 - [] ----D C:\Program Files (x86)\VS Revo Group
O43 - CFD: 2015-05-05 - 13:09:59 - [] ----D C:\Program Files (x86)\VSO
O43 - CFD: 2015-05-05 - 00:34:31 - [] ----D C:\Program Files (x86)\Windows Defender
O43 - CFD: 2015-05-04 - 18:54:32 - [] ----D C:\Program Files (x86)\Windows Live
O43 - CFD: 2011-04-12 - 05:16:36 - [] ----D C:\Program Files (x86)\Windows Mail =>.Microsoft Corporation
O43 - CFD: 2015-05-05 - 00:35:06 - [] ----D C:\Program Files (x86)\Windows Media Player =>.Microsoft Corporation
O43 - CFD: 2009-07-14 - 01:32:38 - [] ----D C:\Program Files (x86)\Windows NT
O43 - CFD: 2011-04-12 - 05:16:36 - [] ----D C:\Program Files (x86)\Windows Photo Viewer
O43 - CFD: 2010-11-20 - 23:31:38 - [] ----D C:\Program Files (x86)\Windows Portable Devices
O43 - CFD: 2011-04-12 - 05:16:36 - [] ----D C:\Program Files (x86)\Windows Sidebar
O43 - CFD: 2015-05-05 - 14:46:42 - [] ----D C:\Program Files (x86)\ZHPDiag =>.Nicolas Coolman
O43 - CFD: 2015-05-04 - 17:17:54 - [] ----D C:\Program Files (x86)\Common Files\Adobe
O43 - CFD: 2015-05-04 - 18:59:42 - [] ----D C:\Program Files (x86)\Common Files\Intel
O43 - CFD: 2015-05-05 - 09:12:08 - [] ----D C:\Program Files (x86)\Common Files\logishrd
O43 - CFD: 2015-05-04 - 18:51:28 - [] ----D C:\Program Files (x86)\Common Files\microsoft shared
O43 - CFD: 2009-07-13 - 23:20:08 - [] ----D C:\Program Files (x86)\Common Files\Services
O43 - CFD: 2015-05-04 - 20:33:30 - [] ----D C:\Program Files (x86)\Common Files\Skype
O43 - CFD: 2009-07-13 - 23:20:08 - [] ----D C:\Program Files (x86)\Common Files\SpeechEngines
O43 - CFD: 2015-05-05 - 00:35:24 - [] ----D C:\Program Files (x86)\Common Files\System
O43 - CFD: 2015-05-04 - 18:23:50 - [] ----D C:\Program Files (x86)\Common Files\Windows Live
O43 - CFD: 2015-05-05 - 01:10:34 - [] ----D C:\ProgramData\Adguard
O43 - CFD: 2015-05-04 - 17:40:18 - [] ----D C:\ProgramData\Adobe
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Application Data
O43 - CFD: 2015-05-04 - 17:10:11 - [] ----D C:\ProgramData\AVG Web TuneUp =>Toolbar.AVGSafeGuard
O43 - CFD: 2015-05-04 - 17:03:46 - [] ----D C:\ProgramData\AVG2015
O43 - CFD: 2015-05-04 - 16:55:51 - [] -SH-D C:\ProgramData\Bureau
O43 - CFD: 2015-05-05 - 12:00:05 - [] ----D C:\ProgramData\Canneverbe Limited
O43 - CFD: 2015-05-04 - 17:00:10 - [] --H-D C:\ProgramData\Common Files
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Desktop
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Documents
O43 - CFD: 2015-05-04 - 16:55:51 - [] -SH-D C:\ProgramData\Favoris
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Favorites
O43 - CFD: 2015-05-05 - 12:55:04 - [0] ----D C:\ProgramData\Freemake
O43 - CFD: 2015-05-04 - 17:19:19 - [] ----D C:\ProgramData\Google
O43 - CFD: 2015-05-05 - 09:11:50 - [] ----D C:\ProgramData\LogiShrd
O43 - CFD: 2015-05-04 - 18:04:24 - [] ----D C:\ProgramData\ma-config.com
O43 - CFD: 2015-05-04 - 21:06:14 - [] ----D C:\ProgramData\Malwarebytes
O43 - CFD: 2015-05-04 - 16:55:52 - [] -SH-D C:\ProgramData\Menu Démarrer
O43 - CFD: 2015-05-05 - 13:52:11 - [] ----D C:\ProgramData\MFAData
O43 - CFD: 2015-05-05 - 07:59:31 - [] -S--D C:\ProgramData\Microsoft
O43 - CFD: 2015-05-04 - 16:55:52 - [] -SH-D C:\ProgramData\Modèles
O43 - CFD: 2015-05-05 - 11:07:46 - [] ----D C:\ProgramData\Package Cache
O43 - CFD: 2015-05-04 - 20:34:09 - [] ----D C:\ProgramData\Skype
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Start Menu
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Templates
O43 - CFD: 2015-05-05 - 08:27:05 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Accessories
O43 - CFD: 2015-05-04 - 10:53:03 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Administrative Tools
O43 - CFD: 2015-05-04 - 17:03:27 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVG
O43 - CFD: 2015-05-04 - 20:58:22 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\CCleaner
O43 - CFD: 2015-05-04 - 10:53:00 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Games
O43 - CFD: 2015-05-04 - 20:58:06 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Chrome
O43 - CFD: 2015-05-05 - 09:56:11 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Intel Driver Update Utility
O43 - CFD: 2015-05-05 - 12:52:10 - [0] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Lavasoft
O43 - CFD: 2015-05-05 - 09:09:46 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Logitech
O43 - CFD: 2015-05-04 - 18:04:24 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\ma-config.com
O43 - CFD: 2009-07-14 - 00:57:09 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Maintenance
O43 - CFD: 2015-05-04 - 21:06:19 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Malwarebytes Anti-Malware
O43 - CFD: 2015-05-04 - 17:51:05 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Silverlight
O43 - CFD: 2015-05-04 - 20:33:33 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Skype
O43 - CFD: 2009-07-14 - 00:54:24 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup
O43 - CFD: 2011-04-12 - 05:27:56 - [0] R-H-D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Tablet PC
O43 - CFD: 2015-05-05 - 13:10:22 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\VSO
O43 - CFD: 2015-05-04 - 19:32:19 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\WinRAR
O43 - CFD: 2015-05-05 - 14:46:42 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\ZHP =>.Nicolas Coolman
O43 - CFD: 2015-05-04 - 17:46:43 - [] ----D C:\Users\Claude\AppData\Roaming\Adobe
O43 - CFD: 2015-05-04 - 17:04:06 - [] ----D C:\Users\Claude\AppData\Roaming\AVG2015
O43 - CFD: 2015-05-05 - 11:59:42 - [] ----D C:\Users\Claude\AppData\Roaming\Canneverbe Limited
O43 - CFD: 2015-05-04 - 17:29:20 - [] ----D C:\Users\Claude\AppData\Roaming\Google
O43 - CFD: 2015-05-04 - 16:56:14 - [] ----D C:\Users\Claude\AppData\Roaming\Identities
O43 - CFD: 2015-05-05 - 09:11:12 - [] ----D C:\Users\Claude\AppData\Roaming\Leadertech
O43 - CFD: 2015-05-04 - 17:47:41 - [] ----D C:\Users\Claude\AppData\Roaming\Macromedia
O43 - CFD: 2011-04-12 - 05:27:56 - [0] ----D C:\Users\Claude\AppData\Roaming\Media Center Programs
O43 - CFD: 2015-05-05 - 09:11:11 - [] -S--D C:\Users\Claude\AppData\Roaming\Microsoft
O43 - CFD: 2015-05-05 - 01:09:48 - [] ----D C:\Users\Claude\AppData\Roaming\Performix LLC
O43 - CFD: 2015-05-04 - 21:13:31 - [] ----D C:\Users\Claude\AppData\Roaming\Skype
O43 - CFD: 2015-05-04 - 17:03:27 - [] ----D C:\Users\Claude\AppData\Roaming\TuneUp Software
O43 - CFD: 2015-05-05 - 13:11:37 - [] ----D C:\Users\Claude\AppData\Roaming\Vso
O43 - CFD: 2015-05-04 - 19:58:23 - [] ----D C:\Users\Claude\AppData\Roaming\Windows Live Writer
O43 - CFD: 2015-05-05 - 01:22:34 - [] ----D C:\Users\Claude\AppData\Roaming\WinRAR
O43 - CFD: 2015-05-05 - 14:48:08 - [] ----D C:\Users\Claude\AppData\Roaming\ZHP =>.Nicolas Coolman
O43 - CFD: 2015-05-05 - 08:42:06 - [] ----D C:\Users\Claude\AppData\Local\Adobe
O43 - CFD: 2015-05-04 - 16:56:01 - [] -SH-D C:\Users\Claude\AppData\Local\Application Data
O43 - CFD: 2015-05-04 - 17:10:23 - [] ----D C:\Users\Claude\AppData\Local\AVG Web TuneUp =>Toolbar.AVGSafeGuard
O43 - CFD: 2015-05-04 - 20:24:18 - [] ----D C:\Users\Claude\AppData\Local\Avg2015
O43 - CFD: 2015-05-05 - 11:45:33 - [] ----D C:\Users\Claude\AppData\Local\Diagnostics
O43 - CFD: 2015-05-05 - 00:53:52 - [] -SH-D C:\Users\Claude\AppData\Local\EmieBrowserModeList
O43 - CFD: 2015-05-05 - 00:53:52 - [] -SH-D C:\Users\Claude\AppData\Local\EmieSiteList
O43 - CFD: 2015-05-05 - 00:53:52 - [] -SH-D C:\Users\Claude\AppData\Local\EmieUserList
O43 - CFD: 2015-05-04 - 20:43:56 - [] ----D C:\Users\Claude\AppData\Local\FreemakeVideoConverter
O43 - CFD: 2015-05-05 - 01:21:10 - [] ----D C:\Users\Claude\AppData\Local\Google
O43 - CFD: 2015-05-04 - 16:56:01 - [] -SH-D C:\Users\Claude\AppData\Local\Historique
O43 - CFD: 2015-05-05 - 09:57:03 - [] ----D C:\Users\Claude\AppData\Local\Intel
O43 - CFD: 2015-05-05 - 09:14:39 - [] ----D C:\Users\Claude\AppData\Local\Logitech® Webcam Software
O43 - CFD: 2015-05-04 - 17:00:09 - [] ----D C:\Users\Claude\AppData\Local\MFAData
O43 - CFD: 2015-05-05 - 11:45:22 - [] ----D C:\Users\Claude\AppData\Local\Microsoft
O43 - CFD: 2015-05-04 - 20:40:23 - [] ----D C:\Users\Claude\AppData\Local\Programs
O43 - CFD: 2015-05-04 - 20:34:37 - [] ----D C:\Users\Claude\AppData\Local\Skype
O43 - CFD: 2015-05-05 - 14:46:44 - [] ----D C:\Users\Claude\AppData\Local\Temp
O43 - CFD: 2015-05-04 - 16:56:01 - [] -SH-D C:\Users\Claude\AppData\Local\Temporary Internet Files
O43 - CFD: 2015-05-05 - 13:38:43 - [] ----D C:\Users\Claude\AppData\Local\VirtualStore
O43 - CFD: 2015-05-04 - 19:00:04 - [] ----D C:\Users\Claude\AppData\Local\Windows Live
O43 - CFD: 2015-05-04 - 19:01:44 - [] ----D C:\Users\Claude\AppData\Local\Windows Live Writer
O43 - CFD: 2009-07-14 - 00:54:32 - [] R---D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories
O43 - CFD: 2015-05-05 - 00:52:30 - [] R---D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Administrative Tools
O43 - CFD: 2009-07-14 - 00:49:38 - [] R---D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Maintenance
O43 - CFD: 2015-05-05 - 12:45:28 - [] ----D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Revo Uninstaller
O43 - CFD: 2015-05-04 - 21:25:19 - [] ----D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\SpeedFan
O43 - CFD: 2015-05-05 - 09:11:12 - [] R---D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup
O43 - CFD: 2015-05-04 - 19:32:19 - [] ----D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\WinRAR
~ Program Folder: 133 Scanned in 00mn 00s
---\\ Derniers fichiers modifiés ou crées sous Windows et System32 (O44)
O44 - LFC:[MD5.D449C36379EBEFD3CCDAEC328002BB5B] - 2015-04-27 - 13:06:48 ---A- . (.Microsoft Corporation - Microsoft Windows Diagnostics Tracking.) -- C:\Windows\System32\UtcResources.dll [36864]
O44 - LFC:[MD5.AF278DB00C43E925E58C8CA2C0CF4C71] - 2015-04-27 - 14:16:33 ---A- . (.Microsoft Corporation - DLL du schéma d'audit de sécurité.) -- C:\Windows\System32\adtschema.dll [686080]
O44 - LFC:[MD5.19F08DF0A6599D0259D1B224CC5F9ED5] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-console-l1-1-0.dll [3072]
O44 - LFC:[MD5.FCA971E5C584A3828A020FF4B2BEFCCE] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-datetime-l1-1-0.dll [3072]
O44 - LFC:[MD5.1A7D6385E3F99544327E984830676EF4] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-debug-l1-1-0.dll [3072]
O44 - LFC:[MD5.B3A3B2782C1CA5EDFBD380E34AEFB797] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-delayload-l1-1-0.dll [3072]
O44 - LFC:[MD5.A5E6D69385BCA6A787434E2FE062986D] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-errorhandling-l1-1-0.dll [3072]
O44 - LFC:[MD5.643631684239D63818F30957E8667187] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-fibers-l1-1-0.dll [3072]
O44 - LFC:[MD5.B206F476A21445BDC7C6365070CC33BC] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-file-l1-1-0.dll [5120]
O44 - LFC:[MD5.5E7FDE8D591E1E184E39A04201403453] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-handle-l1-1-0.dll [3072]
O44 - LFC:[MD5.0B558439CCB936A97C78A0CAF9AAB856] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-heap-l1-1-0.dll [3584]
O44 - LFC:[MD5.824D1D40174B687108841C9AEE9CF6C8] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-interlocked-l1-1-0.dll [3072]
O44 - LFC:[MD5.2FAAFF164E3183477868C4743DD015E3] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-io-l1-1-0.dll [3072]
O44 - LFC:[MD5.306C1665A1FA72292827BC62C5068E28] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-libraryloader-l1-1-0.dll [3584]
O44 - LFC:[MD5.360FBA71F144CE416B2AE7D5553C87AD] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-localization-l1-1-0.dll [4096]
O44 - LFC:[MD5.975CA905CF10C14D1C2EB29026DD6E60] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-localregistry-l1-1-0.dll [4096]
O44 - LFC:[MD5.67B03204F468B24702787D9AD90089DB] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-memory-l1-1-0.dll [3584]
O44 - LFC:[MD5.1FCED4EA7CB62E69D4BBC476384D996D] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-misc-l1-1-0.dll [3584]
O44 - LFC:[MD5.E0FF0290115192214F5DC73C2DDACD76] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-namedpipe-l1-1-0.dll [3584]
O44 - LFC:[MD5.FD18F6B70748ED7F3004ECA7CB91CE82] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-processenvironment-l1-1-0.dll [3584]
O44 - LFC:[MD5.5FF2586D38C0B50C16976633D2064B4C] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-processthreads-l1-1-0.dll [4608]
O44 - LFC:[MD5.2ED9BDA64C82A1FE9614E5CABC98104A] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-profile-l1-1-0.dll [3072]
O44 - LFC:[MD5.E229C592341A73F3AB579F503582FEDD] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-rtlsupport-l1-1-0.dll [3584]
O44 - LFC:[MD5.8486D0DAC57FC6D20697C5C93B688EF1] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-string-l1-1-0.dll [3072]
O44 - LFC:[MD5.81AA6F9E338EB279DFA5082BCD4F6AC5] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-synch-l1-1-0.dll [4096]
O44 - LFC:[MD5.A788BD5D470BE3DB47D8C9EE382B3FEE] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-sysinfo-l1-1-0.dll [4096]
O44 - LFC:[MD5.B3238F9DFCB93035033A4EEE21153C1C] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-threadpool-l1-1-0.dll [4608]
O44 - LFC:[MD5.21A9F0F2D42258826A78CEA98EDC4641] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-util-l1-1-0.dll [3072]
O44 - LFC:[MD5.C7BDEFDC1B82292D9457CB8E5E4FDF5E] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-xstate-l1-1-0.dll [3072]
O44 - LFC:[MD5.306215737213CD3839250D3FE142C221] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-security-base-l1-1-0.dll [6144]
O44 - LFC:[MD5.90293AAC2AB0908BFF98ADB89CEBC931] - 2015-04-27 - 14:16:38 ---A- . (.Microsoft Corporation - ApiSet Schema DLL.) -- C:\Windows\System32\apisetschema.dll [6656]
O44 - LFC:[MD5.7A448B8CED7F7348C36159D5CC8E19ED] - 2015-04-27 - 14:18:25 ---A- . (.Microsoft Corporation - DLL des événements d'audit de la sécurité.) -- C:\Windows\System32\msaudite.dll [146432]
O44 - LFC:[MD5.90DC7B112F946B412C9CDC6F459F4053] - 2015-04-27 - 14:18:37 ---A- . (.Microsoft Corporation - Nom d'audit des objets système.) -- C:\Windows\System32\msobjs.dll [60416]
O44 - LFC:[MD5.4DD0098FFAB4664DB979537C48AE055F] - 2015-04-27 - 14:21:37 ---A- . (.Microsoft Corporation - Programme de stratégie d'audit.) -- C:\Windows\System32\auditpol.exe [64000]
O44 - LFC:[MD5.E55A72876BC5E244D0A8F7F07862A939] - 2015-04-27 - 14:22:08 ---A- . (.Microsoft Corporation - Hôte de la fenêtre de la console.) -- C:\Windows\System32\conhost.exe [338432]
O44 - LFC:[MD5.BB7BAF9532DBA5AB4009E981687D1EA6] - 2015-04-27 - 14:22:26 ---A- . (.Microsoft Corporation - Utilitaire de configuration des performance.) -- C:\Windows\System32\diskperf.exe [19456]
O44 - LFC:[MD5.9C5DBA74D0C641C2A4ABDC79969B7BEF] - 2015-04-27 - 14:22:34 ---A- . (.Microsoft Corporation - Utilitaire d'enregistrement des Performance.) -- C:\Windows\System32\logman.exe [104448]
O44 - LFC:[MD5.9262D6E2C239EDD6D87B080F2BCCEC9F] - 2015-04-27 - 14:22:35 ---A- . (.Microsoft Corporation - Local Security Authority Process.) -- C:\Windows\System32\lsass.exe [31232]
O44 - LFC:[MD5.79F036EB691ABBA84E8EB1715E5F2B17] - 2015-04-27 - 14:22:46 ---A- . (.Microsoft Corporation - Utilitaire de réenregistrement de Performan.) -- C:\Windows\System32\relog.exe [43008]
O44 - LFC:[MD5.52935C072F8D5A92508AA3A3CC9133C7] - 2015-04-27 - 14:22:47 ---A- . (.Microsoft Corporation - Restauration du système de Microsoft® Windo.) -- C:\Windows\System32\rstrui.exe [296960]
O44 - LFC:[MD5.DA5EF2CC0764BE7097BAFA9CAF903FE8] - 2015-04-27 - 14:22:53 ---A- . (.Microsoft Corporation - Gestionnaire de sessions Windows.) -- C:\Windows\System32\smss.exe [112640]
O44 - LFC:[MD5.FE60A67032A5C94F6ACE483C8FE84105] - 2015-04-27 - 14:22:57 ---A- . (.Microsoft Corporation - Moniteur de performance de la ligne de comm.) -- C:\Windows\System32\typeperf.exe [47104]
O44 - LFC:[MD5.EE27E1D639E3807229C15AF94320CF0A] - 2015-04-27 - 14:22:57 ---A- . (.Microsoft Corporation - Outil de rapport de suivi d'événements.) -- C:\Windows\System32\tracerpt.exe [404992]
O44 - LFC:[MD5.B01B21E15671ACD3F0AD131DC4CABFC7] - 2015-04-27 - 14:23:11 ---A- . (.Microsoft Corporation - API avancées Windows 32.) -- C:\Windows\System32\advapi32.dll [879104]
O44 - LFC:[MD5.50EBA6640805F6D5EF4A0DCEF2D180AB] - 2015-04-27 - 14:23:13 ---A- . (.Microsoft Corporation - Credential Delegation Security Package.) -- C:\Windows\System32\credssp.dll [22016]
O44 - LFC:[MD5.A3DCC3D8BB57E31EA07949313CC3A3CF] - 2015-04-27 - 14:23:13 ---A- . (.Microsoft Corporation - Processus d'exécution client-serveur.) -- C:\Windows\System32\csrsrv.dll [43520]
O44 - LFC:[MD5.FDF1E0FD74DED0034BA6FFB665E0641E] - 2015-04-27 - 14:23:19 ---A- . (.Microsoft Corporation - DLL du client API BASE Windows NT.) -- C:\Windows\System32\KernelBase.dll [424448]
O44 - LFC:[MD5.1C9F2F4A2C603739BD8CC8C64310AFD7] - 2015-04-27 - 14:23:19 ---A- . (.Microsoft Corporation - DLL du client API BASE Windows NT.) -- C:\Windows\System32\kernel32.dll [1162752]
O44 - LFC:[MD5.DA8B541825991F6699790E617FF0FF60] - 2015-04-27 - 14:23:19 ---A- . (.Microsoft Corporation - DLL serveur LSA.) -- C:\Windows\System32\lsasrv.dll [1461760]
O44 - LFC:[MD5.CCAB9BE9C9100C5F54A5A8F355730841] - 2015-04-27 - 14:23:19 ---A- . (.Microsoft Corporation - Package de sécurité Kerberos.) -- C:\Windows\System32\kerberos.dll [728064]
O44 - LFC:[MD5.CD3770C78AFFC223A3B9D38F27B7A309] - 2015-04-27 - 14:23:22 ---A- . (.Microsoft Corporation - Bibliothèque de chiffrement Windows.) -- C:\Windows\System32\ncrypt.dll [309760]
O44 - LFC:[MD5.408A8232E84515E4AA819E0C95E65257] - 2015-04-27 - 14:23:22 ---A- . (.Microsoft Corporation - Microsoft Authentication Package v1.0.) -- C:\Windows\System32\msv1_0.dll [314880]
O44 - LFC:[MD5.E1B0C7042BA7B8903D60DF3885F2DFE7] - 2015-04-27 - 14:23:22 ---A- . (.Microsoft Corporation - Émulation 16 bits sur NT64.) -- C:\Windows\System32\ntvdm64.dll [16384]
O44 - LFC:[MD5.52146DBFE253B83FAB1980AA704C7974] - 2015-04-27 - 14:23:26 ---A- . (.Microsoft Corporation - Host for SCM/SDDL/LSA Lookup APIs.) -- C:\Windows\System32\sechost.dll [113664]
O44 - LFC:[MD5.0D9BDBE780DD81757AC5AF87E8B1EBEC] - 2015-04-27 - 14:23:26 ---A- . (.Microsoft Corporation - Security Support Provider Interface.) -- C:\Windows\System32\secur32.dll [28160]
O44 - LFC:[MD5.639E3005261836E526263087F64FF888] - 2015-04-27 - 14:23:26 ---A- . (.Microsoft Corporation - TLS / SSL Security Provider.) -- C:\Windows\System32\schannel.dll [341504]
O44 - LFC:[MD5.0CD609B1143961F5C3BA691729A6A5DA] - 2015-04-27 - 14:23:27 ---A- . (.Microsoft Corporation - Bibliothèque principale de Restauration du.) -
desoler j'avais pas vue je l'ai renvoyer sur pjjoint dsl^^
-
Re,
Le rapport n'est pas complet et si sur pjjoint tu n'y arrive pas et essaye ici
https://up2sha.re/
Fait plus d'options Parcourir et Envoyer.-
~ Rapport de ZHPDiag v2015.5.5.46 - Nicolas Coolman (2015-05-05)
~ Lancé par Claude (2015-05-05 15:43:25)
~ Facebook : https://www.facebook.com/nicolascoolman1
~ Adresse du Forum https://nicolascoolman.eu
~ Traduit par Nicolas Coolman
~ Etat de la version : Version à jour.
~ Liste blanche : Désactivée par l'utilisateur
~ Elévation des Privilèges : OK
~ User Account Control (UAC): Activate by user
---\\ Navigateurs Internet
MSIE: Internet Explorer v11.0.9600.17728
GCIE: Google Chrome v42.0.2311.135 (Defaut)
---\\ Informations sur les produits Windows
~ Langage: Français
Windows Server License Manager Script : OK
~ Windows Operating System - Windows(R) 7, OEM_COA_NSLP channel
Windows ID Activation : OK
~ Windows Partial Key : MW72B
Windows License : OK
~ Windows Remaining Initializations Number : 3
Software Protection Service (Protection logicielle) : OK
Windows Automatic Updates : OK
Windows Vista (TM) Ultimate, 64-bit Service Pack 1 (Build 6000)
---\\ Logiciels de protection du système
AVG 2015 v15.0.5941
Malwarebytes Anti-Malware version 2.1.6.1022
---\\ Logiciels d'optimisation du système
CCleaner v5.05
---\\ Logiciels de partage PeerToPeer
---\\ Surveillance de Logiciels
Adobe Flash Player 17 NPAPI
Adobe Acrobat Reader DC - Français
---\\ Informations sur le système
~ Processor: Intel64 Family 6 Model 55 Stepping 3, GenuineIntel
~ Operating System: 64 Bits
Boot mode: Normal (Normal boot)
Total RAM: 3797 MB (46% free)
System Restore: Activé (Enable)
System drive C: has 430 GB (92%) free of 466 GB
---\\ Mode de connexion au système
~ Computer Name: CLAUDE-PC
~ User Name: Claude
~ All Users Names: HomeGroupUser$, Claude, Administrateur,
~ Unselected Option: None
Logged in as Administrator
---\\ Variables d'environnement
~ System Unit : C:\
~ %AppZHP% : C:\Users\Claude\AppData\Roaming\ZHP\
~ %AppData% : C:\Users\Claude\AppData\Roaming\
~ %Desktop% : C:\Users\Claude\Desktop\
~ %Favorites% : C:\Users\Claude\Favorites\
~ %LocalAppData% : C:\Users\Claude\AppData\Local\
~ %StartMenu% : C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\
~ %Windir% : C:\Windows\
~ %System% : C:\Windows\System32\
---\\ Enumération des unités disques
C: Hard drive, Flash drive, Thumb drive (Free 430 Go of 466 Go)
D: CD-ROM drive (Not Inserted)
---\\ Etat du Centre de Sécurité Windows
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiSpywareOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiVirusOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] FirewallOverride: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\Explorer] NoActiveDesktopChanges: Modified
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\system] EnableLUA: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\NOHIDDEN] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\SHOWALL] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Associations] Application: OK
[HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon] Shell: OK
[HKLM\SYSTEM\CurrentControlSet\Services\COMSysApp] Type: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install] LastSuccessTime : OK
~ Security Center: 41 Scanned in 00mn 00s
---\\ Recherche particulière de fichiers génériques
[MD5.332FEAB1435662FC6C672E25BEB37BE3] - (.Microsoft Corporation - Explorateur Windows.) (.2011-02-25 - 01:19:30.) -- C:\Windows\Explorer.exe [2871808]
[MD5.94355C28C1970635A31B3FE52EB7CEBA] - (.Microsoft Corporation - Application de démarrage de Windows.) (.2009-07-13 - 20:39:52.) -- C:\Windows\System32\Wininit.exe [129024]
[MD5.77B35D0FC22A2D2EAC8D07C3F9784DBF] - (.Microsoft Corporation - Extensions Internet pour Win32.) (.2015-03-12 - 21:45:57.) -- C:\Windows\System32\wininet.dll [2358784]
[MD5.8CEBD9D0A0A879CDE9F36F4383B7CAEA] - (.Microsoft Corporation - Application d'ouverture de session Windows.) (.2014-07-16 - 21:07:24.) -- C:\Windows\System32\Winlogon.exe [455168]
[MD5.067FA52BFB59A56110A12312EF9AF243] - (.Microsoft Corporation - Bibliothèque de licences.) (.2010-11-20 - 22:24:16.) -- C:\Windows\System32\sppcomapi.dll [232448]
[MD5.FA886682CFC5D36718D3E436AACF10B9] - (.Microsoft Corporation - Ancillary Function Driver for WinSock.) (.2014-05-30 - 01:45:52.) -- C:\Windows\system32\Drivers\AFD.sys [497152]
[MD5.02062C0B390B7729EDC9E69C680A6F3C] - (.Microsoft Corporation - ATAPI IDE Miniport Driver.) (.2009-07-13 - 20:52:21.) -- C:\Windows\system32\Drivers\atapi.sys [24128]
[MD5.B8BD2BB284668C84865658C77574381A] - (.Microsoft Corporation - CD-ROM File System Driver.) (.2009-07-13 - 18:19:47.) -- C:\Windows\system32\Drivers\Cdfs.sys [92160]
[MD5.F036CE71586E93D94DAB220D7BDF4416] - (.Microsoft Corporation - SCSI CD-ROM Driver.) (.2010-11-20 - 22:23:47.) -- C:\Windows\system32\Drivers\Cdrom.sys [147456]
[MD5.9BB2EF44EAA163B29C4A4587887A0FE4] - (.Microsoft Corporation - DFS Namespace Client Driver.) (.2010-11-20 - 22:24:32.) -- C:\Windows\system32\Drivers\DfsC.sys [102400]
[MD5.97BFED39B6B79EB12CDDBFEED51F56BB] - (.Microsoft Corporation - High Definition Audio Bus Driver.) (.2010-11-20 - 22:23:47.) -- C:\Windows\system32\Drivers\HDAudBus.sys [122368]
[MD5.FA55C73D4AFFA7EE23AC4BE53B4592D3] - (.Microsoft Corporation - Pilote de port i8042.) (.2009-07-13 - 18:19:57.) -- C:\Windows\system32\Drivers\i8042prt.sys [105472]
[MD5.AF9B39A7E7B6CAA203B3862582E9F2D0] - (.Microsoft Corporation - IP Network Address Translator.) (.2009-07-13 - 19:10:03.) -- C:\Windows\system32\Drivers\IpNat.sys [116224]
[MD5.A5D9106A73DC88564C825D317CAC68AC] - (.Microsoft Corporation - Windows NT SMB Minirdr.) (.2011-04-26 - 21:40:40.) -- C:\Windows\system32\Drivers\MRxSmb.sys [158208]
[MD5.09594D1089C523423B32A4229263F068] - (.Microsoft Corporation - MBT Transport driver.) (.2010-11-20 - 22:23:51.) -- C:\Windows\system32\Drivers\netBT.sys [261632]
[MD5.1A29A59A4C5BA6F8C85062A613B7E2B2] - (.Microsoft Corporation - Pilote du système de fichiers NT.) (.2014-01-23 - 21:37:55.) -- C:\Windows\system32\Drivers\ntfs.sys [1684928]
[MD5.0086431C29C35BE1DBC43F52CC273887] - (.Microsoft Corporation - Pilote de port parallèle.) (.2009-07-13 - 19:00:41.) -- C:\Windows\system32\Drivers\Parport.sys [97280]
[MD5.471815800AE33E6F1C32FB1B97C490CA] - (.Microsoft Corporation - RAS L2TP mini-port/call-manager driver.) (.2010-11-20 - 22:24:33.) -- C:\Windows\system32\Drivers\Rasl2tp.sys [129536]
[MD5.1B6163C503398B23FF8B939C67747683] - (.Microsoft Corporation - Microsoft RDP Device redirector.) (.2010-11-20 - 22:25:07.) -- C:\Windows\system32\Drivers\rdpdr.sys [165888]
[MD5.548260A7B8654E024DC30BF8A7C5BAA4] - (.Microsoft Corporation - SMB Transport driver.) (.2009-07-13 - 19:09:09.) -- C:\Windows\system32\Drivers\smb.sys [93184]
[MD5.70988118145F5F10EF24720B97F35F65] - (.Microsoft Corporation - TDI Translation Driver.) (.2014-11-10 - 20:46:26.) -- C:\Windows\system32\Drivers\tdx.sys [119296]
[MD5.0D08D2F3B3FF84E433346669B5E0F639] - (.Microsoft Corporation - Pilote de cliché instantané du volume.) (.2010-11-20 - 22:23:47.) -- C:\Windows\system32\Drivers\volsnap.sys [295808]
~ Generic Processes: Scanned in 00mn 03s
---\\ Etat des fichiers cachés (Caché/Total)
~ Mes images (My Pictures) : 1/4
~ Mes Favoris (My Favorites) : 0/62
~ Mon Bureau (My Desktop) : 1/127
~ Menu demarrer (Programs) : 1/36
~ Hidden Files: Scanned in 00mn 00s
---\\ Processus lancés
[MD5.7E212E742BF06BF678AE35E9C1B74B8F] - (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) -- C:\Program Files (x86)\Malwarebytes Anti-Malware\mbam.exe [6212920] [PID.2720]
[MD5.BEE793728636C7E729937D317B5D1F6D] - (.AVG Technologies CZ, s.r.o. - AVG User Interface.) -- C:\Program Files (x86)\AVG\AVG2015\avgui.exe [3745232] [PID.3944]
[MD5.2555A094409BD20DAB7A97A5A539F21C] - (.Intel Corporation - iusb3mon.) -- C:\Program Files (x86)\Intel\Intel(R) USB 3.0 eXtensible Host Controller Driver\Application\iusb3mon.exe [296216] [PID.3992]
[MD5.8FFDB89A0FB7C8ABC3A8825E38047341] - (.Logitech Inc. - Logitech Webcam Software.) -- C:\Program Files (x86)\Logitech\LWS\Webcam Software\LWS.exe [204136] [PID.4000]
[MD5.E4C53CE8409DCFF708C790A0AC76398D] - (...) -- C:\Program Files (x86)\Logitech\LWS\Webcam Software\CameraHelperShell.exe [264040] [PID.2980]
[MD5.0ED961A25AC5C8EB29219513B7A7DEA5] - (.Almico Software (almico.com) - Pas de description.) -- C:\Program Files (x86)\SpeedFan\speedfan.exe [4841120] [PID.6136]
[MD5.B3581F426DC500A51091CDD5BACF0454] - (.Microsoft Corporation - Internet Explorer.) -- C:\Program Files (x86)\Internet Explorer\IEXPLORE.exe [815288] [PID.6128]
[MD5.E8B7FD67DA14A7BE57A5CB80E3139E60] - (.Google Inc. - Google Toolbar Broker.) -- C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbarUser_32.exe [309704] [PID.4380]
[MD5.A299EA000386A57EBAA2699A95FB91E0] - (.Nicolas Coolman - ZHPDiag.) -- C:\Program Files (x86)\ZHPDiag\ZHPDiag.exe [8207360] [PID.4428]
[MD5.FFD80DC0CDA145C3376A5076360162C8] - (...) -- C:\Program Files (x86)\AVG Web TuneUp\WtuSystemSupport.exe [620056] [PID.1032] =>Toolbar.AVGSafeGuard
[MD5.929593D76589294BA3F74540298D1B3E] - (.Adobe Systems Incorporated - Adobe Acrobat Update Service.) -- C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [81088] [PID.1864]
[MD5.ABCDD4260B6AF7631322ED71D6379779] - (.AVG Technologies CZ, s.r.o. - AVG Firewall Service.) -- C:\Program Files (x86)\AVG\AVG2015\avgfws.exe [1517480] [PID.1916]
[MD5.ADDD8FF660E3758A4D3C6B47EE71356E] - (.AVG Technologies CZ, s.r.o. - AVG Identity Protection Service.) -- C:\Program Files (x86)\AVG\AVG2015\avgidsagent.exe [3438032] [PID.2108]
[MD5.95A260961EB2401BE0FAB69B7A8A049C] - (.AVG Technologies CZ, s.r.o. - AVG Watchdog Service.) -- C:\Program Files (x86)\AVG\AVG2015\avgwdsvc.exe [311792] [PID.2152]
[MD5.1F79342D9EB530A48742F651E570983A] - (.Microsoft Corporation - Updates Skype Click to Call.) -- C:\Program Files (x86)\Skype\Toolbars\AutoUpdate\SkypeC2CAutoUpdateSvc.exe [1390176] [PID.2180]
[MD5.E4938E0A376CF0B9D989EE5C0A146891] - (.Microsoft Corporation - Phone Number Recognition (PNR) module.) -- C:\Program Files (x86)\Skype\Toolbars\PNRSvc\SkypeC2CPNRSvc.exe [1767520] [PID.2304]
[MD5.516E29AD03BDF610CC36A95AE692FE42] - (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) -- C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamscheduler.exe [1871160] [PID.2560]
[MD5.2B983F067AEE3F9EB4DF5E97F45D21D1] - (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) -- C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamservice.exe [1080120] [PID.2984]
~ Processes Running: Scanned in 00mn 03s
---\\ Google Chrome, Démarrage,Recherche,Extensions (G0,G1,G2)
C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Preferences
---\\ Liste des dossiers d'extension Google Chrome
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\aapbdbdomjkkjkaonfhkkikfgjllcleb [__MSG_8969005060131950570__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\aohghmighlieiainnegkcijnfilokake [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\apdfllckaahabafndbhieahigkjlhalf [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\bgnkhhnnamicmpeenaelnjfhikgbkllg [__MSG_name__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\blpcfgokakmgnkcojhhkbfbldkacnbeo [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\coobgpohoikkiipiblmjeljniedjpjpf [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\felcaaldnbdncclmgdcncolpebgiejap [__MSG_appName__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\gighmmpiobklfepjocnamgkkbiglidom [AdBlock]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\gmlllbghnfkpflemihljekbapjopfjik [Bookmark Manager]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\habdflddkbkcmiglihdemgpijopehham [Currency Converter]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\lccekmodgklaepjeofjdjpbminllajkg [Chrome Hotword Shared Module]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\mlomiejdfkolichcflejclcbmpeaniij [Ghostery]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\nmmhkkegccagdldgiimedpiccmgmieda [__MSG_APP_NAME__]
G2 - EXT: C:\Users\Claude\AppData\Local\Google\Chrome\User Data\Default\Extensions\pjkljhegncpnkpknbcohdijeoejaedia [__MSG_appName__]
~ Google Lines Browser: 28 Scanned in 00mn 02s
---\\ Mozilla Firefox, Plugins,Demarrage,Recherche,Extensions (P2,M0,M1,M2,M3)
P2 - FPN: [HKLM] [@adobe.com/FlashPlayer] - (...) -- C:\Windows\system32\Macromed\Flash\NPSWF64_17_0_0_169.dll
P2 - FPN: [HKLM] [@Microsoft.com/NpCtrl,version=1.0] - (. Microsoft Corporation - 5.1.30514.0.) -- C:\Program Files\Microsoft Silverlight\5.1.30514.0\npctrl.dll
~ Firefox Browser: 2 Scanned in 00mn 00s
---\\ Internet Explorer, Démarrage,Recherche,URLSearchHook, Phishing (R0,R1,R3,R4)
R0 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = https://www.google.ca/?gws_rd=ssl
R0 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = https://www.microsoft.com/fr-fr/
R0 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Start Page = https://www.microsoft.com/fr-fr/
R1 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Extensions Off Page = about:noadd-ons
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Security Risk Page = about:securityrisk
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Search_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Search Page = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Default_Page_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Default_Search_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Extensions Off Page = about:noadd-ons
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Security Risk Page = about:securityrisk
R3 - URLSearchHook: Microsoft Url Search Hook [64Bits] - {CFBFAE00-17A6-11D0-99CB-00C04FD64497} . (.Microsoft Corporation - Navigateur Internet.) (11.00.9600.17631 (winblue_r7.150111-1500)) -- C:\Windows\SysWOW64\ieframe.dll
R4 - HKLM\SOFTWARE\Microsoft\Internet Explorer\PhishingFilter,EnabledV8 = 1
R4 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\PhishingFilter,EnabledV8 = 1
~ IE Browser: 17 Scanned in 00mn 00s
---\\ Internet Explorer, Proxy Management (R5)
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = no key
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyEnable = 0
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,MigrateProxy = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,EnableHttp1_1 = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,AutoConfigProxy = wininet.dll
~ Proxy management: Scanned in 00mn 00s
---\\ Analyse des lignes F0, F1, F2, F3 - IniFiles, Autoloading programs
F2 - REG:system.ini: USERINIT=C:\Windows\system32\userinit.exe,
F2 - REG:system.ini: Shell=C:\Windows\explorer.exe
F2 - REG:system.ini: VMApplet=C:\Windows\System32\SystemPropertiesPerformance.exe
~ Keys: Scanned in 00mn 00s
---\\ Hosts file redirection (O1)
~ Le fichier hôte est sain (The hosts file is clean) (21)
~ Hosts File: Scanned in 00mn 00s
---\\ Browser Helper Objects de navigateur (O2)
O2 - BHO: Programme d'aide de l'Assistant de connexion au compte Microsoft [64Bits] - {9030D464-4C02-4ABF-8ECC-5164760863C6} . (.Microsoft Corp. - Microsoft® Windows Live ID Login Helper.) -- C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: Google Toolbar Helper [64Bits] - {AA58ED58-01DD-4d91-8333-CF10577473F7} . (.Google Inc. - Google Toolbar.) -- C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O2 - BHO: SkypeIEPluginBHO [64Bits] - {AE805869-2E5C-4ED4-8F7B-F1F7851A4497} . (.Microsoft Corporation - Skype Click to Call IE Add-on.) -- C:\Program Files (x86)\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O2 - BHO: Google Toolbar Notifier BHO [64Bits] - {AF69DE43-7D58-4638-B6FA-CE66B5AD205D} . (.Google Inc. - GoogleToolbarNotifier.) -- C:\Program Files (x86)\Google\GoogleToolbarNotifier\5.10.11023.1534\swg.dll
~ BHO: 8 Scanned in 00mn 00s
---\\ Internet Explorer Toolbars (O3)
O3 - Toolbar: Google Toolbar - [HKLM]{2318C2B1-4965-11d4-9B18-009027A5CD4F} . (.Google Inc. - Google Toolbar.) -- C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{2318C2B1-4965-11D4-9B18-009027A5CD4F} Clé orpheline
~ Toolbar: Scanned in 00mn 00s
---\\ Applications lancées au démarrage du système (O4)
O4 - HKLM\..\Run: [RTHDVCPL] . (.Realtek Semiconductor - Gestionnaire audio HD Realtek.) -- C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe =>.Realtek Semiconductor Corp
O4 - HKCU\..\Run: [Web Companion] C:\Program Files (x86)\Lavasoft\Web Companion\Application\WebCompanion.exe (.not file.)
O4 - HKCU\..\Run: [CCleaner Monitoring] . (.Piriform Ltd - CCleaner.) -- C:\Program Files\CCleaner\CCleaner64.exe =>.Piriform Ltd
O4 - HKLM\..\Wow6432Node\Run: [AVG_UI] . (.AVG Technologies CZ, s.r.o. - AVG User Interface.) -- C:\Program Files (x86)\AVG\AVG2015\avgui.exe
O4 - HKLM\..\Wow6432Node\Run: [USB3MON] . (.Intel Corporation - iusb3mon.) -- C:\Program Files (x86)\Intel\Intel(R) USB 3.0 eXtensible Host Controller Driver\Application\iusb3mon.exe
O4 - HKLM\..\Wow6432Node\Run: [LWS] . (.Logitech Inc. - Logitech Webcam Software.) -- C:\Program Files (x86)\Logitech\LWS\Webcam Software\LWS.exe =>.Logitech Inc
O4 - HKUS\S-1-5-19\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files (x86)\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files (x86)\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-19\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-21-2664199691-3854510578-2085819547-1000\..\Run: [Web Companion] C:\Program Files (x86)\Lavasoft\Web Companion\Application\WebCompanion.exe (.not file.)
O4 - HKUS\S-1-5-21-2664199691-3854510578-2085819547-1000\..\Run: [CCleaner Monitoring] . (.Piriform Ltd - CCleaner.) -- C:\Program Files\CCleaner\CCleaner64.exe =>.Piriform Ltd
~ Application: Scanned in 00mn 00s
---\\ Invisibilité de l'icône d'options IE dans le panneau de Configuration (O5)
O5 - control.ini: [HKLM\..\Control Panel] inetcpl.cpl=no
~ IE Control Panel: 1 Scanned in 00mn 00s
---\\ Boutons situés sur la barre d'outils principale d'Internet Explorer (O9)
O9 - Extra button: Skype Click to Call settings [64Bits] - {898EA8C8-E7FF-479B-8935-AEC46303B9E5} . (...) -- c:\program files (x86)\skype\toolbars\internet explorer x64\icon.ico
~ IE Extra Buttons: Scanned in 00mn 00s
---\\ Winsock hijacker (Layered Service Provider) (O10)
O10 - WLSP:\000000000001\Winsock LSP File . (.Microsoft Corporation - Network Location Awareness 2.) -- C:\Windows\system32\NLAapi.dll
O10 - WLSP:\000000000002\Winsock LSP File . (.Microsoft Corporation - Fournisseur Shim d'affectation de noms de messagerie.) -- C:\Windows\system32\napinsp.dll
O10 - WLSP:\000000000003\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000004\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000005\Winsock LSP File . (.Microsoft Corporation - Fournisseur de service Sockets 2.0 de Microsoft Windows.) -- C:\Windows\system32\mswsock.dll =>.Microsoft Corporation
O10 - WLSP:\000000000006\Winsock LSP File . (.Microsoft Corporation - LDAP RnR Provider DLL.) -- C:\Windows\system32\winrnr.dll
O10 - WLSP:\000000000007\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
O10 - WLSP:\000000000008\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
~ Winsock: 8 Scanned in 00mn 00s
---\\ Modification Domaine/Adresses DNS (O17)
O17 - HKLM\System\CCS\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpNameServer = 192.168.2.1
O17 - HKLM\System\CCS\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpDomain = gateway.2wire.net
O17 - HKLM\System\CS1\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpNameServer = 192.168.2.1
O17 - HKLM\System\CS1\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpDomain = gateway.2wire.net
O17 - HKLM\System\CS2\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpNameServer = 192.168.2.1
O17 - HKLM\System\CS2\Services\Tcpip\..\{2B493A70-F63F-40CF-B534-7F6F4729B13B}: DhcpDomain = gateway.2wire.net
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = 192.168.2.1
~ Domain: Scanned in 00mn 00s
---\\ Protocole additionnel (O18)
O18 - Handler: wlpg [64Bits] - {E43EF6CD-A37A-4A9B-9E6F-83F89B8E6324} . (...) --
O18 - Filter: application/x-msdownload [64Bits] - {1E66F26B-79EE-11D2-8710-00C04F79ED0D} . (.Microsoft Corporation - Microsoft .NET Runtime Execution Engine.) -- C:\Windows\System32\mscoree.dll =>.Microsoft Corporation
~ Protocole Additionnel: Scanned in 00mn 00s
---\\ Clé de Registre autorun ShellServiceObjectDelayLoad (SSO/SSODL) (O21)
O21 - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} - CLSID or File not found.
~ SSODL: 1 Scanned in 00mn 00s
---\\ Liste des services NT non Microsoft et non désactivés (O23)
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) . (.Adobe Systems Incorporated - Adobe Acrobat Update Service.) - C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: Pare-feu AVG (avgfws) . (.AVG Technologies CZ, s.r.o. - AVG Firewall Service.) - C:\Program Files (x86)\AVG\AVG2015\avgfws.exe
O23 - Service: AVGIDSAgent (AVGIDSAgent) . (.AVG Technologies CZ, s.r.o. - AVG Identity Protection Service.) - C:\Program Files (x86)\AVG\AVG2015\avgidsagent.exe
O23 - Service: AVG WatchDog (avgwd) . (.AVG Technologies CZ, s.r.o. - AVG Watchdog Service.) - C:\Program Files (x86)\AVG\AVG2015\avgwdsvc.exe
O23 - Service: Service Google Update (gupdate) (gupdate) . (.Google Inc. - Programme d'installation de Google.) - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe =>.Google Inc
O23 - Service: Intel(R) HD Graphics Control Panel Service (igfxCUIService1.0.0.0) . (.Intel Corporation - igfxCUIService Module.) - C:\Windows\System32\igfxCUIService.exe
O23 - Service: Ma-Config Agent (MaConfigAgent) . (.CybelSoft - Service de détection matériel.) - C:\Program Files\ma-config.com\MaConfigAgent.exe
O23 - Service: (MBAMScheduler) . (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) - C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamscheduler.exe
O23 - Service: (MBAMService) . (.Malwarebytes Corporation - Malwarebytes Anti-Malware.) - C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamservice.exe
O23 - Service: Skype Updater (SkypeUpdate) . (.Skype Technologies - Skype Updater Service.) - C:\Program Files (x86)\Skype\Updater\Updater.exe
O23 - Service: (vToolbarUpdater18.4.0) . (...) - C:\Program Files (x86)\Common Files\AVG Secure Search\vToolbarUpdater\18.4.0\ToolbarUpdater.exe (.not file.) =>Toolbar.AVGSearch
O23 - Service: WtuSystemSupport (WtuSystemSupport) . (...) - C:\Program Files (x86)\AVG Web TuneUp\WtuSystemSupport.exe =>Toolbar.AVGSafeGuard
~ Services: 11 Scanned in 01mn 10s
---\\ Enumération Active Desktop & MHTML Editor (O24)
O24 - Default MHTML Editor: Last - .(...) - (.not file.)
~ Desktop Component: 4 Scanned in 00mn 00s
---\\ Enumère les données de BootExecute (BEX) (O34)
O34 - HKLM BootExecute: (autocheck autochk *) - File not found
~ BEX: 1 Scanned in 00mn 00s
---\\ Tâches planifiées en automatique (O39)
[MD5.64495D9B3C4B640230E9265C23A33F55] [APT] [Adobe Acrobat Update Task] (.Adobe Systems Incorporated.) -- C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe [1018056]
[MD5.B04A4810C6CC205F9DC72DC22E4AB236] [APT] [Adobe Flash Player Updater] (.Adobe Systems Incorporated.) -- C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe [268464]
[MD5.1F014EA12ECB13C909DA9395E9CD3D18] [APT] [CCleanerSkipUAC] (.Piriform Ltd.) -- C:\Program Files\CCleaner\CCleaner.exe [6278424]
[MD5.506708142BC63DABA64F2D3AD1DCD5BF] [APT] [GoogleUpdateTaskMachineCore] (.Google Inc..) -- C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [116648]
[MD5.506708142BC63DABA64F2D3AD1DCD5BF] [APT] [GoogleUpdateTaskMachineUA] (.Google Inc..) -- C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [116648]
[MD5.D41D8CD98F00B204E9800998ECF8427E] [APT] [MyDefrag v4.3.1 Daily] (...) -- C:\Program Files\MyDefrag v4.3.1\Scripts\AutomaticDaily.MyD" [5663]
[MD5.D41D8CD98F00B204E9800998ECF8427E] [APT] [MyDefrag v4.3.1 Monthly] (...) -- C:\Program Files\MyDefrag v4.3.1\Scripts\AutomaticMonthly.MyD" [5626]
[MD5.38272D7EAE1D5348AF235E157DAFE556] [APT] [{67D77F24-43DB-451A-AED0-80DD1D8CC230}] (.Lavasoft.) -- C:\Users\Claude\Downloads\WcInstaller.exe [303336]
[MD5.C155A13687144076286989EF078112C2] [APT] [{A8F46F6C-A112-43E7-9072-AFCBBB3102A0}] (.Nicolas Coolman.) -- C:\Program Files (x86)\ZHPDiag\ZHPhep.exe [1917440]
[MD5.C155A13687144076286989EF078112C2] [APT] [{FF272049-611C-4F51-B5A2-2D235174CF9B}] (.Nicolas Coolman.) -- C:\Program Files (x86)\ZHPDiag\ZHPFix\ZHPhep.exe [1917440]
O39 - APT: Adobe Flash Player Updater - (.Adobe Systems Incorporated.) -- C:\Windows\Tasks\Adobe Flash Player Updater.job [1002]
O39 - APT: Adobe Flash Player Updater - (.Adobe Systems Incorporated.) -- C:\Windows\System32\Tasks\Adobe Flash Player Updater [1002]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineCore.job [1066]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineCore [1066]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineUA.job [1070]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineUA [1070]
~ Scheduled Task: 14 Scanned in 00mn 12s
---\\ Composants installés (ActiveSetup Installed Components) (O40)
O40 - ASIC: Microsoft Windows Media Player [64Bits] - >{22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Microsoft Windows Media Player 12.0 [64Bits] - {22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Windows Media Player Extension.) -- C:\Windows\SysWOW64\wmpdxm.dll =>.Microsoft Corporation
O40 - ASIC: Themes Setup [64Bits] - {2C7339CF-2B09-4501-B3F3-F3508C9228ED} . (.Microsoft Corporation - API Windows Theme.) -- C:\Windows\System32\themeui.dll
O40 - ASIC: Microsoft Windows [64Bits] - {44BBA840-CC51-11CF-AAFA-00AA00B6015C} . (.Microsoft Corporation - Windows Mail.) -- C:\Program Files (x86)\Windows Mail\WinMail.exe =>.Microsoft Corporation
O40 - ASIC: Browsing Enhancements [64Bits] - {630b1da0-b465-11d1-9948-00c04f98bbc9} . (.Microsoft Corporation - Extension Shell dossier FTP Microsoft Internet Explorer..) -- C:\Windows\System32\msieftp.dll
O40 - ASIC: Microsoft Windows Media Player [64Bits] - {6BF52A52-394A-11d3-B153-00C04F79FAA6} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Disable SSL3 [64Bits] - {7D715857-A67C-4C2F-A929-038448584D63} . (.Microsoft Corporation - Utilitaire d'initialisation d'Internet Explorer par utilisateur.) -- C:\Windows\System32\ie4uinit.exe
O40 - ASIC: Windows Desktop Update [64Bits] - {89820200-ECBD-11cf-8B85-00AA005B4340} . (.Microsoft Corporation - DLL commune du shell Windows.) -- C:\Windows\System32\shell32.dll
O40 - ASIC: Web Platform Customizations [64Bits] - {89820200-ECBD-11cf-8B85-00AA005B4383} . (.Microsoft Corporation - Utilitaire d'initialisation d'Internet Explorer par utilisateur.) -- C:\Windows\System32\ie4uinit.exe
O40 - ASIC: (no name) [64Bits] - {89B4C1CD-B018-4511-B0A1-5476DBF70820} . (.Microsoft Corporation - Microsoft .NET IE SECURITY REGISTRATION.) -- C:\Windows\system32\mscories.dll
~ Active Setup: 10 Scanned in 00mn 00s
---\\ Pilotes lancés au démarrage du système (O41)
O41 - Driver: C:\Windows\System32\drivers\afd.sys (AFD) . (.Microsoft Corporation - Ancillary Function Driver for WinSock.) - C:\Windows\system32\drivers\afd.sys
O41 - Driver: (Avgdiska) . (.AVG Technologies CZ, s.r.o. - AVG File Vault Driver.) - C:\Windows\System32\DRIVERS\avgdiska.sys
O41 - Driver: (Avgfwfd) . (.AVG Technologies CZ, s.r.o. - AVG Filter Driver.) - C:\Windows\System32\DRIVERS\avgfwd6a.sys
O41 - Driver: (AVGIDSDriver) . (.AVG Technologies CZ, s.r.o. - AVG IDS Application Activity Monitor Driver.) - C:\Windows\System32\DRIVERS\avgidsdrivera.sys
O41 - Driver: (Avgldx64) . (.AVG Technologies CZ, s.r.o. - AVG AVI Loader Driver.) - C:\Windows\System32\DRIVERS\avgldx64.sys
O41 - Driver: (Avgtdia) . (.AVG Technologies CZ, s.r.o. - AVG Network connection watcher.) - C:\Windows\System32\DRIVERS\avgtdia.sys
O41 - Driver: (blbdrive) . (.Microsoft Corporation - BLB Drive Driver.) - C:\Windows\System32\DRIVERS\blbdrive.sys
O41 - Driver: (cdrom) . (.Microsoft Corporation - SCSI CD-ROM Driver.) - C:\Windows\System32\DRIVERS\cdrom.sys
O41 - Driver: C:\Windows\System32\cscsvc.dll (CSC) . (.Microsoft Corporation - Windows Client Side Caching Driver.) - C:\Windows\System32\drivers\csc.sys
O41 - Driver: C:\Windows\System32\drivers\dfsc.sys (DfsC) . (.Microsoft Corporation - DFS Namespace Client Driver.) - C:\Windows\System32\Drivers\dfsc.sys
O41 - Driver: C:\Windows\System32\drivers\discache.sys (discache) . (.Microsoft Corporation - System Indexer/Cache Driver.) - C:\Windows\System32\drivers\discache.sys
O41 - Driver: (mssmbios) . (.Microsoft Corporation - System Management BIOS Driver.) - C:\Windows\System32\DRIVERS\mssmbios.sys
O41 - Driver: (NetBIOS) . (.Microsoft Corporation - NetBIOS interface driver.) - C:\Windows\System32\DRIVERS\netbios.sys
O41 - Driver: C:\Windows\System32\drivers\netbt.sys (NetBT) . (.Microsoft Corporation - MBT Transport driver.) - C:\Windows\System32\DRIVERS\netbt.sys
O41 - Driver: C:\Windows\System32\drivers\nsiproxy.sys (nsiproxy) . (.Microsoft Corporation - NSI Proxy.) - C:\Windows\System32\drivers\nsiproxy.sys
O41 - Driver: C:\Windows\System32\drivers\pacer.sys (Psched) . (.Microsoft Corporation - Planificateur de paquets QoS.) - C:\Windows\System32\DRIVERS\pacer.sys
O41 - Driver: C:\Windows\System32\wkssvc.dll (rdbss) . (.Microsoft Corporation - Pilote du sous-système de mise en mémoire t.) - C:\Windows\System32\DRIVERS\rdbss.sys
O41 - Driver: C:\Windows\System32\DRIVERS\RDPCDD.sys (RDPCDD) . (.Microsoft Corporation - RDP Miniport.) - C:\Windows\System32\DRIVERS\RDPCDD.sys
O41 - Driver: C:\Windows\System32\drivers\RDPENCDD.sys (RDPENCDD) . (.Microsoft Corporation - RDP Encoder Miniport.) - C:\Windows\System32\drivers\rdpencdd.sys
O41 - Driver: C:\Windows\System32\drivers\RdpRefMp.sys (RDPREFMP) . (.Microsoft Corporation - RDP Reflector Driver Miniport.) - C:\Windows\System32\drivers\rdprefmp.sys
O41 - Driver: (Serial) . (.Microsoft Corporation - Pilote de périphérique série.) - C:\Windows\System32\DRIVERS\serial.sys
O41 - Driver: C:\Windows\System32\tcpipcfg.dll (tdx) . (.Microsoft Corporation - TDI Translation Driver.) - C:\Windows\System32\DRIVERS\tdx.sys
O41 - Driver: (TermDD) . (.Microsoft Corporation - Remote Desktop Server Driver.) - C:\Windows\System32\DRIVERS\termdd.sys
O41 - Driver: (VgaSave) . (.Microsoft Corporation - VGA/Super VGA Video Driver.) - C:\Windows\system32\drivers\vga.sys
O41 - Driver: C:\Windows\System32\rascfg.dll (Wanarpv6) . (.Microsoft Corporation - MS Remote Access and Routing ARP Driver.) - C:\Windows\System32\DRIVERS\wanarp.sys
O41 - Driver: (WfpLwf) . (.Microsoft Corporation - WFP NDIS 6.20 Lightweight Filter Driver.) - C:\Windows\System32\DRIVERS\wfplwf.sys
O41 - Driver: Environnement de prise en charge de Fournisseur de services non-IFS Windows Sockets 2.0 (ws2ifsl) . (.Microsoft Corporation - Couche IFS Winsock2.) - C:\Windows\system32\drivers\ws2ifsl.sys
~ Drivers: 81 Scanned in 00mn 01s
---\\ Logiciels installés (O42)
O42 - Logiciel: AVG 2015 - (.AVG Technologies.) [HKLM][64Bits] -- AVG
O42 - Logiciel: AVG 2015 - (.AVG Technologies.) [HKLM][64Bits] -- {3A1B060C-5D3F-4FFA-914E-6292A6F7464E}
O42 - Logiciel: AVG 2015 - (.AVG Technologies.) [HKLM][64Bits] -- {B38CFE4C-C9C4-460B-8353-F56DF2AC3877}
O42 - Logiciel: AVG Web TuneUp - (.AVG Technologies.) [HKLM][64Bits] -- AVG Web TuneUp =>Toolbar.AVGSafeGuard
O42 - Logiciel: Adobe Acrobat Reader DC - Français - (.Adobe Systems Incorporated.) [HKLM][64Bits] -- {AC76BA86-7AD7-1036-7B44-AC0F074E4100}
O42 - Logiciel: Adobe Flash Player 17 ActiveX - (.Adobe Systems Incorporated.) [HKLM][64Bits] -- Adobe Flash Player ActiveX
O42 - Logiciel: Adobe Flash Player 17 NPAPI - (.Adobe Systems Incorporated.) [HKLM][64Bits] -- Adobe Flash Player NPAPI
O42 - Logiciel: CCleaner - (.Piriform.) [HKLM][64Bits] -- CCleaner
O42 - Logiciel: CDBurnerXP - (.CDBurnerXP.) [HKLM][64Bits] -- {7E265513-8CDA-4631-B696-F40D983F3B07}_is1
O42 - Logiciel: CameraHelperMsi - (.Logitech.) [HKLM][64Bits] -- {15634701-BACE-4449-8B25-1567DA8C9FD3}
O42 - Logiciel: ConvertXtoDVD 4.2.0.0 - (...) [HKLM][64Bits] -- {DB6AB705-C9BD-40E3-8929-2EA57F36A4FF}_is1
O42 - Logiciel: D3DX10 - (.Microsoft.) [HKLM][64Bits] -- {E09C4DB7-630C-4F06-A631-8EA7239923AF}
O42 - Logiciel: Galerie de photos - (.Microsoft Corporation.) [HKLM][64Bits] -- {439B34FF-F74E-4807-B5E2-4B758551DA6B}
O42 - Logiciel: Google Chrome - (.Google Inc..) [HKLM][64Bits] -- Google Chrome
O42 - Logiciel: Google Toolbar for Internet Explorer - (.Google Inc..) [HKLM][64Bits] -- {18455581-E099-4BA8-BC6B-F34B2F06600C}
O42 - Logiciel: Google Toolbar for Internet Explorer - (.Google Inc..) [HKLM][64Bits] -- {2318C2B1-4965-11d4-9B18-009027A5CD4F}
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM][64Bits] -- {60EC980A-BDA2-4CB6-A427-B07A5498B4CA}
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM][64Bits] -- {A92DAB39-4E2C-4304-9AB6-BC44E68B55E2}
O42 - Logiciel: Intel(R) Chipset Device Software - (.Intel Corporation.) [HKLM][64Bits] -- {9A431D9C-9FC9-454E-AC8D-15DBAA6ED0F7}
O42 - Logiciel: Intel(R) Driver Update Utility 2.0 - (.Intel.) [HKLM][64Bits] -- {59DB38EB-F864-4E10-841D-38CFBCF864B0}
O42 - Logiciel: Intel(R) Processor Graphics - (.Intel Corporation.) [HKLM][64Bits] -- {F0E3AD40-2BBD-4360-9C76-B9AC9A5886EA}
O42 - Logiciel: Intel(R) USB 3.0 eXtensible Host Controller Driver - (.Intel Corporation.) [HKLM][64Bits] -- {240C3DDD-C5E9-4029-9DF7-95650D040CF2}
O42 - Logiciel: Intel® Driver Update Utility - (.Intel.) [HKLM][64Bits] -- {8409c4f7-2340-4933-a304-5d37db4fb48b}
O42 - Logiciel: Junk Mail filter update - (.Microsoft Corporation.) [HKLM][64Bits] -- {0BE9E708-5DC0-4963-9CFD-0AA519090E79}
O42 - Logiciel: LWS Facebook - (.Logitech.) [HKLM][64Bits] -- {FF167195-9EE4-46C0-8CD7-FBA3457E88AB}
O42 - Logiciel: LWS Gallery - (.Logitech.) [HKLM][64Bits] -- {6F76EC3C-34B1-436E-97FB-48C58D7BEDCD}
O42 - Logiciel: LWS Help_main - (.Logitech.) [HKLM][64Bits] -- {1651216E-E7AD-4250-92A1-FB8ED61391C9}
O42 - Logiciel: LWS Launcher - (.Logitech.) [HKLM][64Bits] -- {83C8FA3C-F4EA-46C4-8392-D3CE353738D6}
O42 - Logiciel: LWS Motion Detection - (.Logitech.) [HKLM][64Bits] -- {71E66D3F-A009-44AB-8784-75E2819BA4BA}
O42 - Logiciel: LWS Pictures And Video - (.Logitech.) [HKLM][64Bits] -- {08610298-29AE-445B-B37D-EFBE05802967}
O42 - Logiciel: LWS Twitter - (.Logitech.) [HKLM][64Bits] -- {174A3B31-4C43-43DD-866F-73C9DB887B48}
O42 - Logiciel: LWS WLM Plugin - (.Logitech.) [HKLM][64Bits] -- {9DAEA76B-E50F-4272-A595-0124E826553D}
O42 - Logiciel: LWS Webcam Software - (.Logitech.) [HKLM][64Bits] -- {8937D274-C281-42E4-8CDB-A0B2DF979189}
O42 - Logiciel: LWS YouTube Plugin - (.Logitech.) [HKLM][64Bits] -- {21DF0294-6B9D-4741-AB6F-B2ABFBD2387E}
O42 - Logiciel: LavasoftTcpService - (.Lavasoft.) [HKLM][64Bits] -- {90CF05DE-735F-42AB-A52A-F447FDFBE207}
O42 - Logiciel: Logiciel pour périphérique à chipset Intel® - (.Intel(R) Corporation.) [HKLM][64Bits] -- {5a6a5d15-d5af-417c-b08f-f7e5eb1f98af}
O42 - Logiciel: Logitech Webcam Software - (.Logitech Inc..) [HKLM][64Bits] -- {D40EB009-0499-459c-A8AF-C9C110766215} =>.Logitech Inc
O42 - Logiciel: MSVCRT - (.Microsoft.) [HKLM][64Bits] -- {8DD46C6A-0056-4FEC-B70A-28BB16A1F11F}
O42 - Logiciel: MSVCRT110 - (.Microsoft.) [HKLM][64Bits] -- {8E14DDC8-EA60-4E18-B3E3-1937104D5BDA}
O42 - Logiciel: MSVCRT110_amd64 - (.Microsoft.) [HKLM][64Bits] -- {E9FA781F-3E80-4399-825A-AD3E11C28C77}
O42 - Logiciel: MSVCRT_amd64 - (.Microsoft.) [HKLM][64Bits] -- {D0B44725-3666-492D-BEF6-587A14BD9BD9}
O42 - Logiciel: Ma-Config.com (64 bits) - (.Cybelsoft.) [HKLM][64Bits] -- {7713B2C6-A0E1-47EA-BD3B-B22F22F7C010}
O42 - Logiciel: Malwarebytes Anti-Malware version 2.1.6.1022 - (.Malwarebytes Corporation.) [HKLM][64Bits] -- Malwarebytes Anti-Malware_is1
O42 - Logiciel: Microsoft Silverlight - (.Microsoft Corporation.) [HKLM][64Bits] -- {89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}
O42 - Logiciel: MyDefrag v4.3.1 - (.J.C. Kessels.) [HKLM][64Bits] -- MyDefrag v4.3.1_is1
O42 - Logiciel: Realtek Ethernet Controller Driver - (.Realtek.) [HKLM][64Bits] -- {8833FFB6-5B0C-4764-81AA-06DFEED9A476}
O42 - Logiciel: Realtek High Definition Audio Driver - (.Realtek Semiconductor Corp..) [HKLM][64Bits] -- {F132AF7F-7BCA-4EDE-8A7C-958108FE7DBC}
O42 - Logiciel: Revo Uninstaller 1.95 - (.VS Revo Group.) [HKLM][64Bits] -- Revo Uninstaller
O42 - Logiciel: Skype Click to Call - (.Microsoft Corporation.) [HKLM][64Bits] -- {6D1221A9-17BF-4EC0-81F2-27D30EC30701}
O42 - Logiciel: Skype(TM) 7.4 - (.Skype Technologies S.A..) [HKLM][64Bits] -- {24991BA0-F0EE-44AD-9CC8-5EC50AECF6B7}
O42 - Logiciel: SpeedFan (remove only) - (...) [HKLM][64Bits] -- SpeedFan
O42 - Logiciel: Visual Studio 2012 x64 Redistributables - (.AVG Technologies.) [HKLM][64Bits] -- {8C775E70-A791-4DA8-BCC3-6AB7136F4484}
O42 - Logiciel: Visual Studio 2012 x86 Redistributables - (.AVG Technologies CZ, s.r.o..) [HKLM][64Bits] -- {98EFF19A-30AB-4E4B-B943-F06B1C63EBF8}
O42 - Logiciel: WinRAR 5.21 (64-bit) - (.win.rar GmbH.) [HKLM][64Bits] -- WinRAR archiver
O42 - Logiciel: erLT - (.Logitech, Inc..) [HKLM][64Bits] -- {3EE9BCAE-E9A9-45E5-9B1C-83A4D357E05C}
~ Logic: 37 Scanned in 00mn 00s
---\\ HKCU & HKLM Software Keys
[HKCU\Software\AVG Web TuneUp] =>Toolbar.AVGSafeGuard
[HKCU\Software\Adobe]
[HKCU\Software\AppDataLow]
[HKCU\Software\Avg Secure Update]
[HKCU\Software\Avg]
[HKCU\Software\Canneverbe Limited]
[HKCU\Software\Classes]
[HKCU\Software\Clients]
[HKCU\Software\Clubic]
[HKCU\Software\Digital River]
[HKCU\Software\Freemake]
[HKCU\Software\Google]
[HKCU\Software\IM Providers]
[HKCU\Software\Intel\Indeo\4.1]
[HKCU\Software\Intel]
[HKCU\Software\Leadertech]
[HKCU\Software\LogiShrd]
[HKCU\Software\Logitech]
[HKCU\Software\Macromedia]
[HKCU\Software\MozillaPlugins]
[HKCU\Software\MyDefrag]
[HKCU\Software\Netscape]
[HKCU\Software\Piriform]
[HKCU\Software\Policies]
[HKCU\Software\Realtek]
[HKCU\Software\Skype]
[HKCU\Software\SpeedFan]
[HKCU\Software\Trolltech]
[HKCU\Software\VSO]
[HKCU\Software\VSRevoGroup]
[HKCU\Software\WinRAR SFX]
[HKCU\Software\WinRAR]
[HKCU\Software\Wow6432Node]
[HKCU\Software\ZebHelpProcess Helper]
[HKLM\Software\ATI Technologies]
[HKLM\Software\CBSTEST]
[HKLM\Software\Classes]
[HKLM\Software\Clients]
[HKLM\Software\DTS]
[HKLM\Software\Dolby]
[HKLM\Software\IM Providers]
[HKLM\Software\Intel]
[HKLM\Software\Khronos]
[HKLM\Software\Knowles]
[HKLM\Software\Logitech]
[HKLM\Software\Macromedia]
[HKLM\Software\MozillaPlugins]
[HKLM\Software\Nahimic]
[HKLM\Software\Nuance]
[HKLM\Software\ODBC]
[HKLM\Software\Piriform]
[HKLM\Software\Policies]
[HKLM\Software\RTLSetup]
[HKLM\Software\Realtek]
[HKLM\Software\RegisteredApplications]
[HKLM\Software\SRS Labs]
[HKLM\Software\SonicFocus]
[HKLM\Software\Sonic]
[HKLM\Software\SoundResearch]
[HKLM\Software\Waves Audio]
[HKLM\Software\WinRAR]
[HKLM\Software\Wow6432Node\AVG Tuneup]
[HKLM\Software\Wow6432Node\Adguard]
[HKLM\Software\Wow6432Node\Adobe]
[HKLM\Software\Wow6432Node\AdwCleaner]
[HKLM\Software\Wow6432Node\Avg]
[HKLM\Software\Wow6432Node\Canneverbe Limited]
[HKLM\Software\Wow6432Node\Classes]
[HKLM\Software\Wow6432Node\Clients]
[HKLM\Software\Wow6432Node\Freemake]
[HKLM\Software\Wow6432Node\Google]
[HKLM\Software\Wow6432Node\IM Providers]
[HKLM\Software\Wow6432Node\Intel]
[HKLM\Software\Wow6432Node\Khronos]
[HKLM\Software\Wow6432Node\Lavasoft]
[HKLM\Software\Wow6432Node\Logitech]
[HKLM\Software\Wow6432Node\Macromedia]
[HKLM\Software\Wow6432Node\Malwarebytes' Anti-Malware]
[HKLM\Software\Wow6432Node\MozillaPlugins]
[HKLM\Software\Wow6432Node\Nuance]
[HKLM\Software\Wow6432Node\ODBC]
[HKLM\Software\Wow6432Node\Policies]
[HKLM\Software\Wow6432Node\Realtek Semiconductor Corp.]
[HKLM\Software\Wow6432Node\Realtek]
[HKLM\Software\Wow6432Node\RegisteredApplications]
[HKLM\Software\Wow6432Node\SRS Labs]
[HKLM\Software\Wow6432Node\Skype]
[HKLM\Software\Wow6432Node\VSO]
[HKLM\Software\Wow6432Node\logishrd]
[HKLM\Software\Wow6432Node]
[HKLM\Software\Yamaha APO]
[HKLM\Software\cybelsoft]
~ Key Software: 189 Scanned in 00mn 00s
---\\ Contenu des dossiers Programs/ProgramFiles/ProgramData/AppData (O43)
O43 - CFD: 2015-05-05 - 01:10:38 - [] ----D C:\Program Files (x86)\Adguard
O43 - CFD: 2015-05-04 - 17:17:53 - [] ----D C:\Program Files (x86)\Adobe
O43 - CFD: 2015-05-04 - 17:02:58 - [] ----D C:\Program Files (x86)\AVG
O43 - CFD: 2015-05-04 - 17:09:46 - [] ----D C:\Program Files (x86)\AVG Web TuneUp =>Toolbar.AVGSafeGuard
O43 - CFD: 2015-05-05 - 11:59:41 - [] ----D C:\Program Files (x86)\CDBurnerXP
O43 - CFD: 2015-05-05 - 12:27:03 - [] ----D C:\Program Files (x86)\Common Files
O43 - CFD: 2015-05-04 - 20:58:12 - [] ----D C:\Program Files (x86)\Google
O43 - CFD: 2015-05-04 - 19:45:43 - [] --H-D C:\Program Files (x86)\InstallShield Installation Information
O43 - CFD: 2015-05-05 - 01:23:06 - [] ----D C:\Program Files (x86)\Intel
O43 - CFD: 2015-05-05 - 09:56:10 - [] ----D C:\Program Files (x86)\Intel Driver Update Utility
O43 - CFD: 2015-05-05 - 11:21:45 - [] ----D C:\Program Files (x86)\Internet Explorer
O43 - CFD: 2015-05-04 - 20:42:58 - [] ----D C:\Program Files (x86)\Lavasoft
O43 - CFD: 2015-05-05 - 09:11:11 - [] ----D C:\Program Files (x86)\Logitech
O43 - CFD: 2015-05-04 - 21:06:18 - [] ----D C:\Program Files (x86)\Malwarebytes Anti-Malware
O43 - CFD: 2015-05-04 - 17:50:59 - [] ----D C:\Program Files (x86)\Microsoft Silverlight
O43 - CFD: 2015-05-04 - 18:54:48 - [] ----D C:\Program Files (x86)\Microsoft SQL Server Compact Edition
O43 - CFD: 2015-05-04 - 18:34:29 - [] ----D C:\Program Files (x86)\Microsoft.NET
O43 - CFD: 2009-07-14 - 01:32:38 - [] ----D C:\Program Files (x86)\MSBuild
O43 - CFD: 2015-05-04 - 19:45:47 - [] ----D C:\Program Files (x86)\Realtek
O43 - CFD: 2009-07-14 - 01:32:38 - [] ----D C:\Program Files (x86)\Reference Assemblies
O43 - CFD: 2015-05-04 - 20:34:31 - [] R---D C:\Program Files (x86)\Skype
O43 - CFD: 2015-05-05 - 14:11:48 - [] ----D C:\Program Files (x86)\SpeedFan
O43 - CFD: 2015-05-04 - 20:07:25 - [0] --H-D C:\Program Files (x86)\Temp
O43 - CFD: 2009-07-14 - 00:57:06 - [0] --H-D C:\Program Files (x86)\Uninstall Information
O43 - CFD: 2015-05-05 - 12:45:16 - [] ----D C:\Program Files (x86)\VS Revo Group
O43 - CFD: 2015-05-05 - 13:09:59 - [] ----D C:\Program Files (x86)\VSO
O43 - CFD: 2015-05-05 - 00:34:31 - [] ----D C:\Program Files (x86)\Windows Defender
O43 - CFD: 2015-05-04 - 18:54:32 - [] ----D C:\Program Files (x86)\Windows Live
O43 - CFD: 2011-04-12 - 05:16:36 - [] ----D C:\Program Files (x86)\Windows Mail =>.Microsoft Corporation
O43 - CFD: 2015-05-05 - 00:35:06 - [] ----D C:\Program Files (x86)\Windows Media Player =>.Microsoft Corporation
O43 - CFD: 2009-07-14 - 01:32:38 - [] ----D C:\Program Files (x86)\Windows NT
O43 - CFD: 2011-04-12 - 05:16:36 - [] ----D C:\Program Files (x86)\Windows Photo Viewer
O43 - CFD: 2010-11-20 - 23:31:38 - [] ----D C:\Program Files (x86)\Windows Portable Devices
O43 - CFD: 2011-04-12 - 05:16:36 - [] ----D C:\Program Files (x86)\Windows Sidebar
O43 - CFD: 2015-05-05 - 14:46:42 - [] ----D C:\Program Files (x86)\ZHPDiag =>.Nicolas Coolman
O43 - CFD: 2015-05-04 - 17:17:54 - [] ----D C:\Program Files (x86)\Common Files\Adobe
O43 - CFD: 2015-05-04 - 18:59:42 - [] ----D C:\Program Files (x86)\Common Files\Intel
O43 - CFD: 2015-05-05 - 09:12:08 - [] ----D C:\Program Files (x86)\Common Files\logishrd
O43 - CFD: 2015-05-04 - 18:51:28 - [] ----D C:\Program Files (x86)\Common Files\microsoft shared
O43 - CFD: 2009-07-13 - 23:20:08 - [] ----D C:\Program Files (x86)\Common Files\Services
O43 - CFD: 2015-05-04 - 20:33:30 - [] ----D C:\Program Files (x86)\Common Files\Skype
O43 - CFD: 2009-07-13 - 23:20:08 - [] ----D C:\Program Files (x86)\Common Files\SpeechEngines
O43 - CFD: 2015-05-05 - 00:35:24 - [] ----D C:\Program Files (x86)\Common Files\System
O43 - CFD: 2015-05-04 - 18:23:50 - [] ----D C:\Program Files (x86)\Common Files\Windows Live
O43 - CFD: 2015-05-05 - 01:10:34 - [] ----D C:\ProgramData\Adguard
O43 - CFD: 2015-05-04 - 17:40:18 - [] ----D C:\ProgramData\Adobe
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Application Data
O43 - CFD: 2015-05-04 - 17:10:11 - [] ----D C:\ProgramData\AVG Web TuneUp =>Toolbar.AVGSafeGuard
O43 - CFD: 2015-05-04 - 17:03:46 - [] ----D C:\ProgramData\AVG2015
O43 - CFD: 2015-05-04 - 16:55:51 - [] -SH-D C:\ProgramData\Bureau
O43 - CFD: 2015-05-05 - 12:00:05 - [] ----D C:\ProgramData\Canneverbe Limited
O43 - CFD: 2015-05-04 - 17:00:10 - [] --H-D C:\ProgramData\Common Files
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Desktop
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Documents
O43 - CFD: 2015-05-04 - 16:55:51 - [] -SH-D C:\ProgramData\Favoris
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Favorites
O43 - CFD: 2015-05-05 - 12:55:04 - [0] ----D C:\ProgramData\Freemake
O43 - CFD: 2015-05-04 - 17:19:19 - [] ----D C:\ProgramData\Google
O43 - CFD: 2015-05-05 - 09:11:50 - [] ----D C:\ProgramData\LogiShrd
O43 - CFD: 2015-05-04 - 18:04:24 - [] ----D C:\ProgramData\ma-config.com
O43 - CFD: 2015-05-04 - 21:06:14 - [] ----D C:\ProgramData\Malwarebytes
O43 - CFD: 2015-05-04 - 16:55:52 - [] -SH-D C:\ProgramData\Menu Démarrer
O43 - CFD: 2015-05-05 - 15:28:31 - [] ----D C:\ProgramData\MFAData
O43 - CFD: 2015-05-05 - 07:59:31 - [] -S--D C:\ProgramData\Microsoft
O43 - CFD: 2015-05-04 - 16:55:52 - [] -SH-D C:\ProgramData\Modèles
O43 - CFD: 2015-05-05 - 11:07:46 - [] ----D C:\ProgramData\Package Cache
O43 - CFD: 2015-05-04 - 20:34:09 - [] ----D C:\ProgramData\Skype
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Start Menu
O43 - CFD: 2009-07-14 - 01:08:56 - [] -SH-D C:\ProgramData\Templates
O43 - CFD: 2015-05-05 - 08:27:05 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Accessories
O43 - CFD: 2015-05-04 - 10:53:03 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Administrative Tools
O43 - CFD: 2015-05-04 - 17:03:27 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVG
O43 - CFD: 2015-05-04 - 20:58:22 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\CCleaner
O43 - CFD: 2015-05-04 - 10:53:00 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Games
O43 - CFD: 2015-05-04 - 20:58:06 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Chrome
O43 - CFD: 2015-05-05 - 09:56:11 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Intel Driver Update Utility
O43 - CFD: 2015-05-05 - 12:52:10 - [0] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Lavasoft
O43 - CFD: 2015-05-05 - 09:09:46 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Logitech
O43 - CFD: 2015-05-04 - 18:04:24 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\ma-config.com
O43 - CFD: 2009-07-14 - 00:57:09 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Maintenance
O43 - CFD: 2015-05-04 - 21:06:19 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Malwarebytes Anti-Malware
O43 - CFD: 2015-05-04 - 17:51:05 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Silverlight
O43 - CFD: 2015-05-04 - 20:33:33 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Skype
O43 - CFD: 2009-07-14 - 00:54:24 - [] R---D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup
O43 - CFD: 2011-04-12 - 05:27:56 - [0] R-H-D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Tablet PC
O43 - CFD: 2015-05-05 - 13:10:22 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\VSO
O43 - CFD: 2015-05-04 - 19:32:19 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\WinRAR
O43 - CFD: 2015-05-05 - 14:46:42 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\ZHP =>.Nicolas Coolman
O43 - CFD: 2015-05-04 - 17:46:43 - [] ----D C:\Users\Claude\AppData\Roaming\Adobe
O43 - CFD: 2015-05-04 - 17:04:06 - [] ----D C:\Users\Claude\AppData\Roaming\AVG2015
O43 - CFD: 2015-05-05 - 11:59:42 - [] ----D C:\Users\Claude\AppData\Roaming\Canneverbe Limited
O43 - CFD: 2015-05-04 - 17:29:20 - [] ----D C:\Users\Claude\AppData\Roaming\Google
O43 - CFD: 2015-05-04 - 16:56:14 - [] ----D C:\Users\Claude\AppData\Roaming\Identities
O43 - CFD: 2015-05-05 - 09:11:12 - [] ----D C:\Users\Claude\AppData\Roaming\Leadertech
O43 - CFD: 2015-05-04 - 17:47:41 - [] ----D C:\Users\Claude\AppData\Roaming\Macromedia
O43 - CFD: 2011-04-12 - 05:27:56 - [0] ----D C:\Users\Claude\AppData\Roaming\Media Center Programs
O43 - CFD: 2015-05-05 - 09:11:11 - [] -S--D C:\Users\Claude\AppData\Roaming\Microsoft
O43 - CFD: 2015-05-05 - 01:09:48 - [] ----D C:\Users\Claude\AppData\Roaming\Performix LLC
O43 - CFD: 2015-05-04 - 21:13:31 - [] ----D C:\Users\Claude\AppData\Roaming\Skype
O43 - CFD: 2015-05-04 - 17:03:27 - [] ----D C:\Users\Claude\AppData\Roaming\TuneUp Software
O43 - CFD: 2015-05-05 - 13:11:37 - [] ----D C:\Users\Claude\AppData\Roaming\Vso
O43 - CFD: 2015-05-04 - 19:58:23 - [] ----D C:\Users\Claude\AppData\Roaming\Windows Live Writer
O43 - CFD: 2015-05-05 - 01:22:34 - [] ----D C:\Users\Claude\AppData\Roaming\WinRAR
O43 - CFD: 2015-05-05 - 15:45:11 - [] ----D C:\Users\Claude\AppData\Roaming\ZHP =>.Nicolas Coolman
O43 - CFD: 2015-05-05 - 08:42:06 - [] ----D C:\Users\Claude\AppData\Local\Adobe
O43 - CFD: 2015-05-04 - 16:56:01 - [] -SH-D C:\Users\Claude\AppData\Local\Application Data
O43 - CFD: 2015-05-04 - 17:10:23 - [] ----D C:\Users\Claude\AppData\Local\AVG Web TuneUp =>Toolbar.AVGSafeGuard
O43 - CFD: 2015-05-04 - 20:24:18 - [] ----D C:\Users\Claude\AppData\Local\Avg2015
O43 - CFD: 2015-05-05 - 11:45:33 - [] ----D C:\Users\Claude\AppData\Local\Diagnostics
O43 - CFD: 2015-05-05 - 00:53:52 - [] -SH-D C:\Users\Claude\AppData\Local\EmieBrowserModeList
O43 - CFD: 2015-05-05 - 00:53:52 - [] -SH-D C:\Users\Claude\AppData\Local\EmieSiteList
O43 - CFD: 2015-05-05 - 00:53:52 - [] -SH-D C:\Users\Claude\AppData\Local\EmieUserList
O43 - CFD: 2015-05-04 - 20:43:56 - [] ----D C:\Users\Claude\AppData\Local\FreemakeVideoConverter
O43 - CFD: 2015-05-05 - 01:21:10 - [] ----D C:\Users\Claude\AppData\Local\Google
O43 - CFD: 2015-05-04 - 16:56:01 - [] -SH-D C:\Users\Claude\AppData\Local\Historique
O43 - CFD: 2015-05-05 - 09:57:03 - [] ----D C:\Users\Claude\AppData\Local\Intel
O43 - CFD: 2015-05-05 - 09:14:39 - [] ----D C:\Users\Claude\AppData\Local\Logitech® Webcam Software
O43 - CFD: 2015-05-04 - 17:00:09 - [] ----D C:\Users\Claude\AppData\Local\MFAData
O43 - CFD: 2015-05-05 - 11:45:22 - [] ----D C:\Users\Claude\AppData\Local\Microsoft
O43 - CFD: 2015-05-04 - 20:40:23 - [] ----D C:\Users\Claude\AppData\Local\Programs
O43 - CFD: 2015-05-04 - 20:34:37 - [] ----D C:\Users\Claude\AppData\Local\Skype
O43 - CFD: 2015-05-05 - 15:45:05 - [] ----D C:\Users\Claude\AppData\Local\Temp
O43 - CFD: 2015-05-04 - 16:56:01 - [] -SH-D C:\Users\Claude\AppData\Local\Temporary Internet Files
O43 - CFD: 2015-05-05 - 13:38:43 - [] ----D C:\Users\Claude\AppData\Local\VirtualStore
O43 - CFD: 2015-05-04 - 19:00:04 - [] ----D C:\Users\Claude\AppData\Local\Windows Live
O43 - CFD: 2015-05-04 - 19:01:44 - [] ----D C:\Users\Claude\AppData\Local\Windows Live Writer
O43 - CFD: 2009-07-14 - 00:54:32 - [] R---D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories
O43 - CFD: 2015-05-05 - 00:52:30 - [] R---D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Administrative Tools
O43 - CFD: 2009-07-14 - 00:49:38 - [] R---D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Maintenance
O43 - CFD: 2015-05-05 - 12:45:28 - [] ----D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Revo Uninstaller
O43 - CFD: 2015-05-04 - 21:25:19 - [] ----D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\SpeedFan
O43 - CFD: 2015-05-05 - 09:11:12 - [] R---D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup
O43 - CFD: 2015-05-04 - 19:32:19 - [] ----D C:\Users\Claude\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\WinRAR
~ Program Folder: 133 Scanned in 00mn 00s
---\\ Derniers fichiers modifiés ou crées sous Windows et System32 (O44)
O44 - LFC:[MD5.D449C36379EBEFD3CCDAEC328002BB5B] - 2015-04-27 - 13:06:48 ---A- . (.Microsoft Corporation - Microsoft Windows Diagnostics Tracking.) -- C:\Windows\System32\UtcResources.dll [36864]
O44 - LFC:[MD5.AF278DB00C43E925E58C8CA2C0CF4C71] - 2015-04-27 - 14:16:33 ---A- . (.Microsoft Corporation - DLL du schéma d'audit de sécurité.) -- C:\Windows\System32\adtschema.dll [686080]
O44 - LFC:[MD5.19F08DF0A6599D0259D1B224CC5F9ED5] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-console-l1-1-0.dll [3072]
O44 - LFC:[MD5.FCA971E5C584A3828A020FF4B2BEFCCE] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-datetime-l1-1-0.dll [3072]
O44 - LFC:[MD5.1A7D6385E3F99544327E984830676EF4] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-debug-l1-1-0.dll [3072]
O44 - LFC:[MD5.B3A3B2782C1CA5EDFBD380E34AEFB797] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-delayload-l1-1-0.dll [3072]
O44 - LFC:[MD5.A5E6D69385BCA6A787434E2FE062986D] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-errorhandling-l1-1-0.dll [3072]
O44 - LFC:[MD5.643631684239D63818F30957E8667187] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-fibers-l1-1-0.dll [3072]
O44 - LFC:[MD5.B206F476A21445BDC7C6365070CC33BC] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-file-l1-1-0.dll [5120]
O44 - LFC:[MD5.5E7FDE8D591E1E184E39A04201403453] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-handle-l1-1-0.dll [3072]
O44 - LFC:[MD5.0B558439CCB936A97C78A0CAF9AAB856] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-heap-l1-1-0.dll [3584]
O44 - LFC:[MD5.824D1D40174B687108841C9AEE9CF6C8] - 2015-04-27 - 14:16:36 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-interlocked-l1-1-0.dll [3072]
O44 - LFC:[MD5.2FAAFF164E3183477868C4743DD015E3] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-io-l1-1-0.dll [3072]
O44 - LFC:[MD5.306C1665A1FA72292827BC62C5068E28] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-libraryloader-l1-1-0.dll [3584]
O44 - LFC:[MD5.360FBA71F144CE416B2AE7D5553C87AD] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-localization-l1-1-0.dll [4096]
O44 - LFC:[MD5.975CA905CF10C14D1C2EB29026DD6E60] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-localregistry-l1-1-0.dll [4096]
O44 - LFC:[MD5.67B03204F468B24702787D9AD90089DB] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-memory-l1-1-0.dll [3584]
O44 - LFC:[MD5.1FCED4EA7CB62E69D4BBC476384D996D] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-misc-l1-1-0.dll [3584]
O44 - LFC:[MD5.E0FF0290115192214F5DC73C2DDACD76] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-namedpipe-l1-1-0.dll [3584]
O44 - LFC:[MD5.FD18F6B70748ED7F3004ECA7CB91CE82] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-processenvironment-l1-1-0.dll [3584]
O44 - LFC:[MD5.5FF2586D38C0B50C16976633D2064B4C] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-processthreads-l1-1-0.dll [4608]
O44 - LFC:[MD5.2ED9BDA64C82A1FE9614E5CABC98104A] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-profile-l1-1-0.dll [3072]
O44 - LFC:[MD5.E229C592341A73F3AB579F503582FEDD] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-rtlsupport-l1-1-0.dll [3584]
O44 - LFC:[MD5.8486D0DAC57FC6D20697C5C93B688EF1] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-string-l1-1-0.dll [3072]
O44 - LFC:[MD5.81AA6F9E338EB279DFA5082BCD4F6AC5] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-synch-l1-1-0.dll [4096]
O44 - LFC:[MD5.A788BD5D470BE3DB47D8C9EE382B3FEE] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-sysinfo-l1-1-0.dll [4096]
O44 - LFC:[MD5.B3238F9DFCB93035033A4EEE21153C1C] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-threadpool-l1-1-0.dll [4608]
O44 - LFC:[MD5.21A9F0F2D42258826A78CEA98EDC4641] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-util-l1-1-0.dll [3072]
O44 - LFC:[MD5.C7BDEFDC1B82292D9457CB8E5E4FDF5E] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-core-xstate-l1-1-0.dll [3072]
O44 - LFC:[MD5.306215737213CD3839250D3FE142C221] - 2015-04-27 - 14:16:37 --HA- . (.Microsoft Corporation - ApiSet Stub DLL.) -- C:\Windows\System32\api-ms-win-security-base-l1-1-0.dll [6144]
O44 - LFC:[MD5.90293AAC2AB0908BFF98ADB89CEBC931] - 2015-04-27 - 14:16:38 ---A- . (.Microsoft Corporation - ApiSet Schema DLL.) -- C:\Windows\System32\apisetschema.dll [6656]
O44 - LFC:[MD5.7A448B8CED7F7348C36159D5CC8E19ED] - 2015-04-27 - 14:18:25 ---A- . (.Microsoft Corporation - DLL des événements d'audit de la sécurité.) -- C:\Windows\System32\msaudite.dll [146432]
O44 - LFC:[MD5.90DC7B112F946B412C9CDC6F459F4053] - 2015-04-27 - 14:18:37 ---A- . (.Microsoft Corporation - Nom d'audit des objets système.) -- C:\Windows\System32\msobjs.dll [60416]
O44 - LFC:[MD5.4DD0098FFAB4664DB979537C48AE055F] - 2015-04-27 - 14:21:37 ---A- . (.Microsoft Corporation - Programme de stratégie d'audit.) -- C:\Windows\System32\auditpol.exe [64000]
O44 - LFC:[MD5.E55A72876BC5E244D0A8F7F07862A939] - 2015-04-27 - 14:22:08 ---A- . (.Microsoft Corporation - Hôte de la fenêtre de la console.) -- C:\Windows\System32\conhost.exe [338432]
O44 - LFC:[MD5.BB7BAF9532DBA5AB4009E981687D1EA6] - 2015-04-27 - 14:22:26 ---A- . (.Microsoft Corporation - Utilitaire de configuration des performance.) -- C:\Windows\System32\diskperf.exe [19456]
O44 - LFC:[MD5.9C5DBA74D0C641C2A4ABDC79969B7BEF] - 2015-04-27 - 14:22:34 ---A- . (.Microsoft Corporation - Utilitaire d'enregistrement des Performance.) -- C:\Windows\System32\logman.exe [104448]
O44 - LFC:[MD5.9262D6E2C239EDD6D87B080F2BCCEC9F] - 2015-04-27 - 14:22:35 ---A- . (.Microsoft Corporation - Local Security Authority Process.) -- C:\Windows\System32\lsass.exe [31232]
O44 - LFC:[MD5.79F036EB691ABBA84E8EB1715E5F2B17] - 2015-04-27 - 14:22:46 ---A- . (.Microsoft Corporation - Utilitaire de réenregistrement de Performan.) -- C:\Windows\System32\relog.exe [43008]
O44 - LFC:[MD5.52935C072F8D5A92508AA3A3CC9133C7] - 2015-04-27 - 14:22:47 ---A- . (.Microsoft Corporation - Restauration du système de Microsoft® Windo.) -- C:\Windows\System32\rstrui.exe [296960]
O44 - LFC:[MD5.DA5EF2CC0764BE7097BAFA9CAF903FE8] - 2015-04-27 - 14:22:53 ---A- . (.Microsoft Corporation - Gestionnaire de sessions Windows.) -- C:\Windows\System32\smss.exe [112640]
O44 - LFC:[MD5.FE60A67032A5C94F6ACE483C8FE84105] - 2015-04-27 - 14:22:57 ---A- . (.Microsoft Corporation - Moniteur de performance de la ligne de comm.) -- C:\Windows\System32\typeperf.exe [47104]
O44 - LFC:[MD5.EE27E1D639E3807229C15AF94320CF0A] - 2015-04-27 - 14:22:57 ---A- . (.Microsoft Corporation - Outil de rapport de suivi d'événements.) -- C:\Windows\System32\tracerpt.exe [404992]
O44 - LFC:[MD5.B01B21E15671ACD3F0AD131DC4CABFC7] - 2015-04-27 - 14:23:11 ---A- . (.Microsoft Corporation - API avancées Windows 32.) -- C:\Windows\System32\advapi32.dll [879104]
O44 - LFC:[MD5.50EBA6640805F6D5EF4A0DCEF2D180AB] - 2015-04-27 - 14:23:13 ---A- . (.Microsoft Corporation - Credential Delegation Security Package.) -- C:\Windows\System32\credssp.dll [22016]
O44 - LFC:[MD5.A3DCC3D8BB57E31EA07949313CC3A3CF] - 2015-04-27 - 14:23:13 ---A- . (.Microsoft Corporation - Processus d'exécution client-serveur.) -- C:\Windows\System32\csrsrv.dll [43520]
O44 - LFC:[MD5.FDF1E0FD74DED0034BA6FFB665E0641E] - 2015-04-27 - 14:23:19 ---A- . (.Microsoft Corporation - DLL du client API BASE Windows NT.) -- C:\Windows\System32\KernelBase.dll [424448]
O44 - LFC:[MD5.1C9F2F4A2C603739BD8CC8C64310AFD7] - 2015-04-27 - 14:23:19 ---A- . (.Microsoft Corporation - DLL du client API BASE Windows NT.) -- C:\Windows\System32\kernel32.dll [1162752]
O44 - LFC:[MD5.DA8B541825991F6699790E617FF0FF60] - 2015-04-27 - 14:23:19 ---A- . (.Microsoft Corporation - DLL serveur LSA.) -- C:\Windows\System32\lsasrv.dll [1461760]
O44 - LFC:[MD5.CCAB9BE9C9100C5F54A5A8F355730841] - 2015-04-27 - 14:23:19 ---A- . (.Microsoft Corporation - Package de sécurité Kerberos.) -- C:\Windows\System32\kerberos.dll [728064]
O44 - LFC:[MD5.CD3770C78AFFC223A3B9D38F27B7A309] - 2015-04-27 - 14:23:22 ---A- . (.Microsoft Corporation - Bibliothèque de chiffrement Windows.) -- C:\Windows\System32\ncrypt.dll [309760]
O44 - LFC:[MD5.408A8232E84515E4AA819E0C95E65257] - 2015-04-27 - 14:23:22 ---A- . (.Microsoft Corporation - Microsoft Authentication Package v1.0.) -- C:\Windows\System32\msv1_0.dll [314880]
O44 - LFC:[MD5.E1B0C7042BA7B8903D60DF3885F2DFE7] - 2015-04-27 - 14:23:22 ---A- . (.Microsoft Corporation - Émulation 16 bits sur NT64.) -- C:\Windows\System32\ntvdm64.dll [16384]
O44 - LFC:[MD5.52146DBFE253B83FAB1980AA704C7974] - 2015-04-27 - 14:23:26 ---A- . (.Microsoft Corporation - Host for SCM/SDDL/LSA Lookup APIs.) -- C:\Windows\System32\sechost.dll [113664]
O44 - LFC:[MD5.0D9BDBE780DD81757AC5AF87E8B1EBEC] - 2015-04-27 - 14:23:26 ---A
-
-
°°
Tu ne comprends pas ? -
Non il n'est pas complet.
Il faut aller par exemple sur ce site
https://up2sha.re/
Clique sur les images par exemple la maison
Sélectionne le rapport et clique sur envoyer.
Un lien se crée, poste dans ta prochaine réponse ce lien. -
Bonsoir,
Alors si tu as réussit poste le lien du rapport.
:)