Virus unideals
Résolu
Bonjour,
Depuis quelque temps il y a un virus sur mon ordi et je suis agressée par la pubilcité et mon ordi rame. j'ai tout essayé, je l'ai supprimé de mes extentions google chrome, j'ai téléchargé malwaresbytes, j'ai aussi essayé de le supprimer depuis programmes files mais rien n'y fait il revient systématiquement
Pouvez vous m'aidez à effacez ce virus de mon ordinateur s'il vous plait?
Merci, cordialement.
14 réponses
-
Bonjour,
voici le rapport :
All processes killed
========== OTL ==========
Error: No service named AVGIDSDriver was found to stop!
Service\Driver key AVGIDSDriver not found.
File C:\Windows\SysNative\drivers\avgidsdrivera.sys not found.
Error: Unable to stop service Avgldx64!
Service\Driver key Avgldx64 not found.
File C:\Windows\SysNative\drivers\avgldx64.sys not found.
Error: Unable to stop service Avgtdia!
Registry key HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Avgtdia deleted successfully.
C:\Windows\SysNative\drivers\avgtdia.sys moved successfully.
Error: Unable to stop service Avgrkx64!
Registry key HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Avgrkx64 deleted successfully.
C:\Windows\SysNative\drivers\avgrkx64.sys moved successfully.
Error: Unable to stop service Avgmfx64!
Registry key HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Avgmfx64 deleted successfully.
C:\Windows\SysNative\drivers\avgmfx64.sys moved successfully.
Service AVGIDSFilter stopped successfully!
Service AVGIDSFilter deleted successfully!
C:\Windows\SysNative\drivers\avgidsfiltera.sys moved successfully.
64bit-Registry key HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{31332EEF-CB9F-458F-AFEB-D30E9A66B6BA}\ deleted successfully.
64bit-Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{31332EEF-CB9F-458F-AFEB-D30E9A66B6BA}\ not found.
64bit-Registry value HKEY_LOCAL_MACHINE\Software\Microsoft\Internet Explorer\Toolbar\\10 deleted successfully.
Registry value HKEY_LOCAL_MACHINE\Software\Microsoft\Internet Explorer\Toolbar\\10 deleted successfully.
Registry value HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run\\ deleted successfully.
========== FILES ==========
File\Folder C:\Windows\SysNative\drivers\avgidsdrivera.sys not found.
File\Folder C:\Windows\SysNative\drivers\avgldx64.sys not found.
File\Folder C:\Windows\SysNative\drivers\avgtdia.sys not found.
File\Folder C:\Windows\SysNative\drivers\avgidsfiltera.sy not found.
File\Folder C:\Windows\SysNative\drivers\avgmfx64.sys not found.
File\Folder C:\Windows\SysNative\drivers\avgrkx64.sys not found.
C:\Users\PC\AppData\Roaming\appdataFr3.bin moved successfully.
C:\Users\PC\AppData\Roaming\AVG2012\cfgall folder moved successfully.
C:\Users\PC\AppData\Roaming\AVG2012 folder moved successfully.
Folder move failed. C:\program files (x86)\AVG\AVG2012 scheduled to be moved on reboot.
Folder move failed. C:\program files (x86)\AVG scheduled to be moved on reboot.
C:\Users\PC\AppData\Local\Temp\AdobeARM.log moved successfully.
C:\Users\PC\AppData\Local\Temp\adwcleaner.db moved successfully.
C:\Users\PC\AppData\Local\Temp\AdwCleaner.jpg moved successfully.
C:\Users\PC\AppData\Local\Temp\au-descriptor-1.8.0_40-b26.xml moved successfully.
C:\Users\PC\AppData\Local\Temp\chrome_installer.log moved successfully.
C:\Users\PC\AppData\Local\Temp\Cleaning.ico moved successfully.
C:\Users\PC\AppData\Local\Temp\EULA.txt moved successfully.
File move failed. C:\Users\PC\AppData\Local\Temp\FXSAPIDebugLogFile.txt scheduled to be moved on reboot.
C:\Users\PC\AppData\Local\Temp\JavaDeployReg.log moved successfully.
C:\Users\PC\AppData\Local\Temp\java_install_sp.log moved successfully.
C:\Users\PC\AppData\Local\Temp\jinstall.cfg moved successfully.
C:\Users\PC\AppData\Local\Temp\jusched.log moved successfully.
C:\Users\PC\AppData\Local\Temp\PCW39A8.tmp moved successfully.
C:\Users\PC\AppData\Local\Temp\PCW39A8.xml moved successfully.
C:\Users\PC\AppData\Local\Temp\PCW90FB.tmp moved successfully.
C:\Users\PC\AppData\Local\Temp\PCW90FB.xml moved successfully.
C:\Users\PC\AppData\Local\Temp\ptuD616.tmp moved successfully.
C:\Users\PC\AppData\Local\Temp\Quarantine.exe moved successfully.
C:\Users\PC\AppData\Local\Temp\Report.ico moved successfully.
C:\Users\PC\AppData\Local\Temp\Scan.ico moved successfully.
C:\Users\PC\AppData\Local\Temp\sqlite3.dll moved successfully.
C:\Users\PC\AppData\Local\Temp\Uninstall.ico moved successfully.
C:\Users\PC\AppData\Local\Temp\wls8FF2.tmp moved successfully.
C:\Users\PC\AppData\Local\Temp\wls914B.tmp moved successfully.
C:\Users\PC\AppData\Local\Temp\wmplog00.sqm moved successfully.
C:\Users\PC\AppData\Local\Temp\wmplog01.sqm moved successfully.
C:\Users\PC\AppData\Local\Temp\wmplog02.sqm moved successfully.
C:\Users\PC\AppData\Local\Temp\wmsetup.log moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileBGSocial.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileBroom.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileCheck.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileClose.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileCluff_EN.txt moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileCluff_FR.txt moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileDetected.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileExit-40.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileFB.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileForum.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileGP.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileInfo.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFilelogo-texte.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileNav_FF.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileNav_GG.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileNav_IE.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileNav_OP.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFilePayPal.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFilePercent.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileQuar.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileQuestion.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileRapport.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileSearch.png moved successfully.
C:\Users\PC\AppData\Local\Temp\ZHPCFileTransGui.jpg moved successfully.
C:\Users\PC\AppData\Local\Temp\__cclog.txt moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF000006BE7CBBEB06.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF01F479EC46FFB1E6.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF04E51E5EF177F1EA.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF054658B054183EA8.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF0CBF18E4222BD065.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF1275737AB28BA62E.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF165EB60E950F844A.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF1C7598850898A774.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF1C7BD4D1203BEEEE.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF21E4AC2E70046D27.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF226C43C37561F175.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF292DE54AD5DE0155.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF2B5E78B0D59EE459.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF2BB0318FA59A254B.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF2CB6F33ED892780D.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF2CE0C0A5381B53CC.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF2F8B5D8C7C371A9D.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF32A8F210CACDD351.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF360A0369BDEA9904.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF370F8583C3CF8771.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF3B291740935481A4.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF3FF242B4095E7295.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF445B8609B465FEF0.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF44CEE8DD1187A11A.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF48CB25363CA8B8EF.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF599C0157DF9A9D07.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF59F88D106FC4D625.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF5E6B6A800A9CAD1B.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF5F2B012C1D187F44.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF61EDB49C24FF7327.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF6547BC6F2A57A5FB.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF6787E8886BA3C34F.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF6859638B7DCE0B19.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF694B0069EA17EC5C.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF6A261A5F37C317A7.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF6C56608917D1DDD0.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF7132F0265D5B498F.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF72D696CCAA1F4E95.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF750B90C03E68AB77.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF779DA06FA0D211BE.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF7AD1DDF155236F99.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF7D5DB07162E80410.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF7F65D2CCB8DC2966.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF84331E37777EFFE4.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF8ADDEA09ACAA5A3B.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF8D88A34043421713.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF8EA3B61748E6A09E.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF94A1877CE90F3E71.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF95308475D74F3726.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF9542D877E9FB4AC4.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF97D2F3BFC1794021.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF9994C7CFE15BF34B.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF9E28D8D827BE8E92.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DF9F63F1FE85828348.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFA33913985DD40B90.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFA5DCC9531D53CACD.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFA66497656569C1D0.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFAC6AAD5BD2696C24.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFAF87197579FADC38.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFB433C50E8F98B304.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFB68C3C428D1C506B.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFB7C94A19D7C90973.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFC7A1EA5FB516FA59.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFC965763900531EDB.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFCF3B92E7AC4965D0.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFD327E27E2F96915B.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFDFF9CF35F555D9FD.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFE91E51DB3B5DDD4C.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFEBF477CBF47EA1A8.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFEC897B1438C1E102.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFF41D413451BEE275.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFFE16690B44C32A3B.TMP moved successfully.
C:\Users\PC\AppData\Local\Temp\~DFFE41DAFFE39BA9AB.TMP moved successfully.
========== REGISTRY ==========
Registry value HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\\{31CE1406-5C12-44C5-B6C5-0F55F2039DE3} not found.
Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{31CE1406-5C12-44C5-B6C5-0F55F2039DE3}\ not found.
Registry value HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\\{F2CD25EB-2FC9-4D58-812A-32BBFBF06186} not found.
Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{F2CD25EB-2FC9-4D58-812A-32BBFBF06186}\ not found.
Registry value HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Uninstall\\{31CE1406-5C12-44C5-B6C5-0F55F2039DE3} not found.
Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{31CE1406-5C12-44C5-B6C5-0F55F2039DE3}\ not found.
Registry value HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Uninstall\\{F2CD25EB-2FC9-4D58-812A-32BBFBF06186} not found.
Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{F2CD25EB-2FC9-4D58-812A-32BBFBF06186}\ not found.
========== SERVICES/DRIVERS ==========
Error: Unable to stop service Avgldx64!
Service\Driver key Avgldx64 not found.
Error: No service named AVGIDSDriver was found to stop!
Service\Driver key AVGIDSDriver not found.
Error: Unable to stop service Avgtdia!
Service\Driver key Avgtdia not found.
Error: Unable to stop service Avgrkx64!
Service\Driver key Avgrkx64 not found.
Error: Unable to stop service Avgmfx64!
Service\Driver key Avgmfx64 not found.
Error: No service named AVGIDSFilter was found to stop!
Service\Driver key AVGIDSFilter not found.
========== COMMANDS ==========
[EMPTYTEMP]
User: All Users
User: Default
->Temp folder emptied: 0 bytes
->Temporary Internet Files folder emptied: 33170 bytes
User: Default User
->Temp folder emptied: 0 bytes
->Temporary Internet Files folder emptied: 0 bytes
User: hedev
->Temp folder emptied: 43164427 bytes
User: PC
->Temp folder emptied: 44 bytes
->Temporary Internet Files folder emptied: 2586631 bytes
->Java cache emptied: 2569470 bytes
->FireFox cache emptied: 370461608 bytes
->Google Chrome cache emptied: 250642423 bytes
->Flash cache emptied: 3169596 bytes
User: Public
User: UpdatusUser
->Temp folder emptied: 0 bytes
->Temporary Internet Files folder emptied: 0 bytes
%systemdrive% .tmp files removed: 0 bytes
%systemroot% .tmp files removed: 0 bytes
%systemroot%\System32 .tmp files removed: 0 bytes
%systemroot%\System32 (64bit) .tmp files removed: 0 bytes
%systemroot%\System32\drivers .tmp files removed: 0 bytes
Windows Temp folder emptied: 12737257 bytes
%systemroot%\sysnative\config\systemprofile\AppData\Local\Microsoft\Windows\Temporary Internet Files folder emptied: 78246 bytes
RecycleBin emptied: 127958998 bytes
Total Files Cleaned = 776,00 mb
[EMPTYFLASH]
User: All Users
User: Default
User: Default User
User: hedev
User: PC
->Flash cache emptied: 0 bytes
User: Public
User: UpdatusUser
Total Flash Files Cleaned = 0,00 mb
OTL by OldTimer - Version 3.2.69.0 log created on 04172015_170205
Files\Folders moved on Reboot...
C:\program files (x86)\AVG\AVG2012 folder moved successfully.
C:\program files (x86)\AVG folder moved successfully.
C:\Users\PC\AppData\Local\Temp\FXSAPIDebugLogFile.txt moved successfully.
File move failed. C:\Windows\temp\_avast_\AvastLock.txt scheduled to be moved on reboot.
PendingFileRenameOperations files...
Registry entries deleted on Reboot...
Voilà tout est fait et le problème à l'air d'être résolu.
Un IMMENSE MERCI à toi ainsi qu'à Comment ça marche.net
Merci aussi pour tous tes précieux conseils
Je conseille vivement ce site :D -
Hello,
Relance OTL.
Sous Persfonnalisation (Custom Scan), copie-colle le contenu du cadre ci dessous (bien prendre :OTL en début).
Clic Correction (Fix), un rapport apparraitra, copie/colle le contenu ici:
:OTL
DRV:64bit: - [2012/12/10 04:28:34 | 000,127,328 | ---- | M] (AVG Technologies CZ, s.r.o. ) [Kernel | On_Demand | Stopped] -- C:\Windows\SysNative\drivers\avgidsdrivera.sys -- (AVGIDSDriver)
DRV:64bit: - [2012/11/08 04:49:24 | 000,307,040 | ---- | M] (AVG Technologies CZ, s.r.o.) [Kernel | System | Running] -- C:\Windows\SysNative\drivers\avgldx64.sys -- (Avgldx64)
DRV:64bit: - [2012/08/24 15:43:16 | 000,384,352 | ---- | M] (AVG Technologies CZ, s.r.o.) [Kernel | System | Running] -- C:\Windows\SysNative\drivers\avgtdia.sys -- (Avgtdia)
DRV:64bit: - [2012/01/31 04:46:48 | 000,036,944 | ---- | M] (AVG Technologies CZ, s.r.o.) [File_System | Boot | Running] -- C:\Windows\SysNative\drivers\avgrkx64.sys -- (Avgrkx64)
DRV:64bit: - [2011/12/23 13:32:14 | 000,047,696 | ---- | M] (AVG Technologies CZ, s.r.o.) [File_System | System | Running] -- C:\Windows\SysNative\drivers\avgmfx64.sys -- (Avgmfx64)
DRV:64bit: - [2011/12/23 13:32:04 | 000,029,776 | ---- | M] (AVG Technologies CZ, s.r.o. ) [Kernel | On_Demand | Stopped] -- C:\Windows\SysNative\drivers\avgidsfiltera.sys -- (AVGIDSFilter)
O2:64bit: - BHO: (no name) - {31332EEF-CB9F-458F-AFEB-D30E9A66B6BA} - No CLSID value found.
O3:64bit: - HKLM\..\Toolbar: (no name) - 10 - No CLSID value found.
O3 - HKLM\..\Toolbar: (no name) - 10 - No CLSID value found.
O4 - HKLM..\Run: []  File not found

:files
C:\Windows\SysNative\drivers\avgidsdrivera.sys
C:\Windows\SysNative\drivers\avgldx64.sys
C:\Windows\SysNative\drivers\avgtdia.sys
C:\Windows\SysNative\drivers\avgidsfiltera.sy
C:\Windows\SysNative\drivers\avgmfx64.sys
C:\Windows\SysNative\drivers\avgrkx64.sys
C:\Users\PC\AppData\Roaming\appdataFr3.bin
C:\Users\PC\AppData\Roaming\AVG2012
C:\program files (x86)\avg
%Temp%\*.*

:reg
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"{31CE1406-5C12-44C5-B6C5-0F55F2039DE3}"=-
"{F2CD25EB-2FC9-4D58-812A-32BBFBF06186}"=-
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Uninstall]
"{31CE1406-5C12-44C5-B6C5-0F55F2039DE3}"=-
"{F2CD25EB-2FC9-4D58-812A-32BBFBF06186}"=-

:services
Avgldx64
AVGIDSDriver
Avgtdia
Avgrkx64
Avgmfx64
AVGIDSFilter

:Commands
[emptytemp]
[emptyflash]
[reboot]
Redemarre le pc sous windows et poste le rapport dans ta prochaine réponse.
Le rapport est sauvegardé sous C:\_OTL\MovedFiles\date_heure.log
#########
Réinitialise tes navigateurs : http://www.sosvirus.net/comment-reinitialiser-son-navigateur-internet-t82282.html
##########
Pour supprimer les outils de désinfections utilisés :
Télécharges DelFix par Xplode sur ton Bureau.
Lance DelFix, exécuter en tant qu'administrateur sous Windows : 7/8 et Vista
Coche les cases suivantes :
Supprimer les outils de désinfection
Purger la restauration système

-
salut,
voici le lien manquant :
http://upload.sosvirus.net/download/loe6tlu1vo1u1cb0pxltczb7lm97fwghhv1t9gtr -
Hello,
Il me manque OTL.txt qui doit être sur ton bureau
-
Bonjour,
Malwarebytes m'indique qu'il n'y a aucune menace détéctée
voici le lien du rapport OTL :
http://upload.sosvirus.net/download/z896mmmyesr22e3y2qabfjemz1fbjyl0wo2mz2oc -
Ok,
# Télécharge MalwareBytes
# Procède à l'installation de celui çi (Décocher "Activer l'essai gratuit de Malwarebytes Anti-Malware Premium")
# Clic sur Mettre à jour (à droite, au centre)
# Clic sur Examen (en haut)
# Sélectionne Examen "Menaces"
# Clic sur Examiner maintenant

# A la fin du scan clic sur Tout mettre en quarantaine !
# Clic sur Copier dans le Presse-papiers
# Un rapport va s'ouvrir. Copie/Colle son contenue dans ta prochaine réponse.
#######
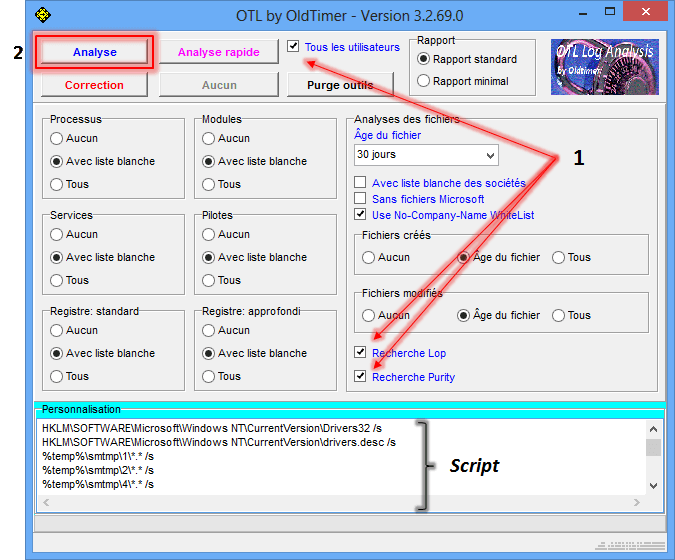
Télécharge OTL de Old_Timer et enregistre le sur le Bureau
Ferme toutes les autres fenêtres et double-clique sur OTL.exe
Sous Vista et Windows 7, il faut lancer le fichier par clic-droit-> Exécuter en tant qu'adminsitrateur.
Vérifie que les cases Tous les utilisateurs, Recherche Lop et Recherche Purity] soient cochées.
Dans le cadre Personnalisation, copie-colle l'intégralité de ce qui suit :
netsvcs
msconfig
safebootminimal
safebootnetwork
activex
drivers32
%ALLUSERSPROFILE%\Application Data\*.
%ALLUSERSPROFILE%\Application Data\*.exe /s
%APPDATA%\*.
%APPDATA%\*.exe /s
%temp%\*.exe /s
%SYSTEMDRIVE%\*.exe
%systemroot%\*. /mp /s
%systemroot%\system32\consrv.dll
%systemroot%\system32\*.dll /lockedfiles
%windir%\Tasks\*.job /lockedfiles
%systemroot%\system32\drivers\*.sys /lockedfiles
%systemroot%\System32\config\*.sav
/md5start
explorer.exe
winlogon.exe
services.exe
wininit.exe
/md5stop
HKEY_CLASSES_ROOT\CLSID\{F3130CDB-AA52-4C3A-AB32-85FFC23AF9C1}\InprocServer32 /s
HKEY_LOCAL_MACHINE\SYSTEM\SYSTEM\CurrentControlSet\Services\lanmanserver\parameters /s
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Session Manager\SubSystems /s
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Session Manager\AppCertDlls /s
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\ProfileList /s
HKEY_LOCAL_MACHINE\Software\Microsoft\Command Processor /s
HKEY_CURRENT_USER\Software\Microsoft\Command Processor /s
CREATERESTOREPOINT
nslookup https://www.google.fr/?gws_rd=ssl /c
hklm\software\clients\startmenuinternet|command /rs
hklm\software\clients\startmenuinternet|command /64 /rs
CREATERESTOREPOINT
SAVEMBR:0
Clique ensuite sur Analyse et patiente le temps du scan.

A la fin de l'analyse, les rapports OTL.txtet Extras.txt s'affichent.
Les rapports étant trop longs pour le forum, héberge-les sur SosUpload et indique les liens fournis dans ta réponse.
-> Tutoriel SosUpload : https://www.sosvirus.net/tutoriel-sosupload/
Les rapports sont sauvegardés sur le Bureau.
-
Je n'ai pas trouvé avg et java dans " desinstaller un programme" j'ai donc essayé de les supprimer dans programme files 86, ce qui semble avoir fonctionné pour java, mais pour avg il y a un message qui s'affiche me disant que le dossier est ouvert dans un autre programme
Voici les liens demandés
http://upload.sosvirus.net/download/y4a555dlmeezra4o8znsbp0a73od7ohij9zbjo2k
http://upload.sosvirus.net/download/rldmmeljhg5r3tm0bygtglwqi5tcfyi6xpjs4o1m
Par contre je ne peux plus répondre depuis mon ordinateur, lorsque je clique sur répondre il ne se passe rien -
Désinstalle AVG ou Avast pour ne garder qu'un seul antivirus, je te conseil de garder avast.
#########
Clic droit sur le fichier setup.exe (C:\Users\PC\Downloads\Setup.exe) situé dans ton dossier de téléchargements, choisis envoyer vers dossier compressé. Cela va créer un fichier setup.zip, transmet moi ce fichier via SosUpload
#######
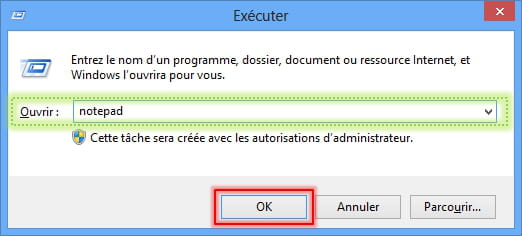
# Appuies simultanément sur les touches Windows et R
# Une fenêtre va s'ouvrir, tape ceci : notepad
# Clic sur OK
# Note : Le bloc note va s'ouvrir
# Copie les lignes suivantes :
start
Task: {095BF618-6597-4728-89B6-2FD0653C745D} - \MediaPlayerEnhance-enabler No Task File <==== ATTENTION
Task: {2B0E1D55-113F-467C-80CA-F33830024662} - \HQ-Video-Profession-1.3-chromeinstaller No Task File <==== ATTENTION
Task: {32434A51-659E-4521-99CC-F35D1AAEA6D9} - System32\Tasks\Microsoft\Windows\Setup\gwx\launchtrayprocess => C:\Windows\system32\GWX\GWX.exe [2015-03-25] (Microsoft Corporation)
Task: {3456DD7C-4641-4765-91E9-7838243B7DF5} - System32\Tasks\Microsoft\Windows\Setup\gwx\refreshgwxcontent => C:\Windows\system32\GWX\GWXConfigManager.exe [2015-03-25] (Microsoft Corporation)
Task: {3903A710-4B35-40BA-84DF-D053D8192E67} - \HQ-Video-Profession-1.3-enabler No Task File <==== ATTENTION
Task: {3DF1FB41-6DDD-4C2F-81D6-232C239EA15A} - \HQ-Video-Profession-1.3-firefoxinstaller No Task File <==== ATTENTION
Task: {479CB305-6624-42DC-9174-23F8A1DB17BB} - System32\Tasks\{75C70CE8-8754-4AA3-B49B-BF1B837D399D} => pcalua.exe -a C:\Users\PC\AppData\Roaming\awesomehp\UninstallManager.exe
Task: {4B9FBCA9-85E9-44DB-B6A2-BDE4AC2A482E} - System32\Tasks\Microsoft\Windows\Setup\gwx\refreshgwxconfig => C:\Windows\system32\GWX\GWXConfigManager.exe [2015-03-25] (Microsoft Corporation)
Task: {56B124F4-C567-4AEE-88CD-99FE58D9DCED} - \MediaPlayerEnhance-chromeinstaller No Task File <==== ATTENTION
Task: {5E41B49D-A492-42E4-A991-A6C8E0FDB873} - System32\Tasks\Microsoft\Windows\Setup\gwx\runappraiser => C:\Windows\system32\GWX\GWXConfigManager.exe [2015-03-25] (Microsoft Corporation)
Task: {6201F993-469B-43D2-B762-C05425D0763B} - System32\Tasks\AVG-Secure-Search-Update_JUNE2013_TB_rmv => C:\Windows\TEMP\{1F0D0DE6-B322-4C85-868C-2393371FA0B9}.exe
Task: {72804725-A985-4549-9D81-2D519F6EAD47} - \MediaPlayerEnhance-updater No Task File <==== ATTENTION
Task: {73F8BB1B-41D6-4163-BECC-84F4C18748DE} - \MediaPlayerEnhance-codedownloader No Task File <==== ATTENTION
Task: {78C13436-D82E-45BB-80F2-C117ABB90DA7} - \HQ-Video-Profession-1.3-codedownloader No Task File <==== ATTENTION
Task: {8F495CE1-BAEF-4792-8DEF-8479BC968E57} - \MediaPlayerEnhance-firefoxinstaller No Task File <==== ATTENTION
Task: {DD48383C-9B27-4B65-B85B-B4419092874F} - \HQ-Video-Profession-1.3-updater No Task File <==== ATTENTION
Task: C:\Windows\Tasks\AVG-Secure-Search-Update_JUNE2013_TB_rmv.job => C:\Windows\TEMP\{1F0D0DE6-B322-4C85-868C-2393371FA0B9}.exe <==== ATTENTION
C:\Windows\TEMP\{1F0D0DE6-B322-4C85-868C-2393371FA0B9}.exe
C:\Windows\system32\GWX
C:\Windows\SysWOW64\GWX
C:\Windows\System32\Tasks\Microsoft\Windows\Setup\gwx
C:\Users\PC\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\DD5C.lnk
C:\ProgramData\{aa1e29a0-5ae1-6d75-aa1e-e29a05aea681}
C:\Users\PC\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\John Wick.FRENCH.BRRiP.XviD.(Keanu Reeves).(2014) (1).lnk
C:\Users\PC\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\John Wick.FRENCH.BRRiP.XviD.(Keanu Reeves).(2014).lnk
Toolbar: HKLM - avast! WebRep - {318A227B-5E9F-45bd-8999-7F8F10CA4CF5} -  No File
Toolbar: HKU\S-1-5-21-3598576173-2487849744-3046334321-1000 -> No Name - {2318C2B1-4965-11D4-9B18-009027A5CD4F} -  No File
Hosts:
FF Extension: No Name - C:\Users\PC\AppData\Roaming\Mozilla\Firefox\Profiles\awab6h2p.default-1416474555389\extensions\searchengine@gmail.com [Not Found]
FF Extension: No Name - C:\Users\PC\AppData\Roaming\Mozilla\Firefox\Profiles\awab6h2p.default-1416474555389\extensions\istart_ffnt@gmail.com [Not Found]
FF Extension: No Name - C:\Program Files (x86)\Mozilla Firefox\browser\extensions\{972ce4c6-7e08-4474-a285-3208198ce6fd} [Not Found]
C:\Windows\System32\Tasks\{D5EA1182-13FE-4606-B275-2F1442E80819}
C:\Users\PC\Downloads\Firefox Setup Stub 36.0.4.exe
C:\Users\PC\Downloads\Setup.exe
C:\Program Files (x86)\LighterEdit
2015-03-12 21:10 - 2015-03-12 21:10 - 00000000 ____D () C:\ProgramData\blanhdahggohpancceebkkjlmpfoeneh
2015-03-12 21:09 - 2015-03-26 12:40 - 00000000 ____D () C:\ProgramData\{aa1e29a0-5ae1-6d75-aa1e-e29a05aea681}
2015-03-12 21:09 - 2015-03-12 21:09 - 00000000 ____D () C:\ProgramData\eoecpljfaomamgejeilfklcmolmgpdal
2015-03-12 21:08 - 2015-03-26 12:40 - 00000000 ____D () C:\ProgramData\{17ace501-c0db-e53b-17ac-ce501c0d9407}
2015-03-12 21:07 - 2015-03-26 12:40 - 00000000 ____D () C:\ProgramData\{c9fd2d1c-646a-3719-c9fd-d2d1c646b471}
end
# Retourne dans le bloc note puis colle les lignes copiées.
# Clic sur Fichier, puis Enregistrer sous ... , nomme le fixlist.txt et enregistre le sur ton bureau
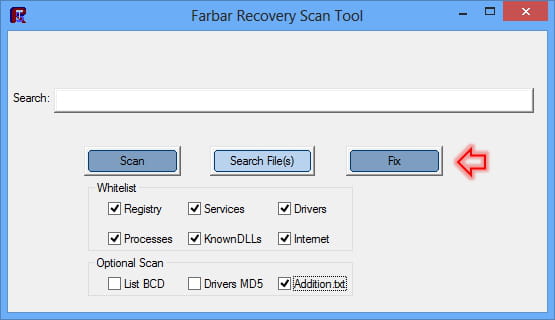
# Rends toi sur le bureau, Lance FRST, [u]exécuter en tant qu'administrateur/u sous Windows : 7/8 et Vista
# Clic sur Fix
# Note : Patiente le temps de la suppression
# Une fois le scan terminé rends toi sur le bureau, un rapport Fixlog.txt a été créé.
# Héberge les rapports Fixlog.txt sur SosUpload, puis copie/colle le lien généré dans ta prochaine réponse
Développeur : UsbFix ## Webmaster : SosVirus -
:)
voici les liens :
http://upload.sosvirus.net/download/5ap1cabtjv7g2eqrlzavhbopz4eh4hvp4revcw92
http://upload.sosvirus.net/download/tat39jriw2x3cayiqnpc6xifixpp0u5xfth8fogp -
Bon travail :)
Nous allons faire un diagnostique
# Télécharge FRST (de Farbar) sur ton bureau !
# Ferme toutes les applications en cours !
# Lance FRST, exécuter en tant qu'administrateur sous Windows : 7/8 et Vista
# Coche la case Addition.txt
# Coche la case Shortcut.txt
# Clique sur Scan
# Une fois le scan terminé rends toi sur le bureau, deux rapports FRST.txt et Addition.txt ont été créés.
# Héberge les rapports FRST.txt , Shortcut.txt et Addition.txt sur SosUpload, puis copie/colle les liens générés dans ta prochaine réponse
-> Tutoriel SosUpload : https://www.sosvirus.net/tutoriel-sosupload/
-
Merci
http://upload.sosvirus.net/download/66ujfsb6ncpl6dt8awu1s4quicj81vkzqpdf6kdw -
De rien ;)
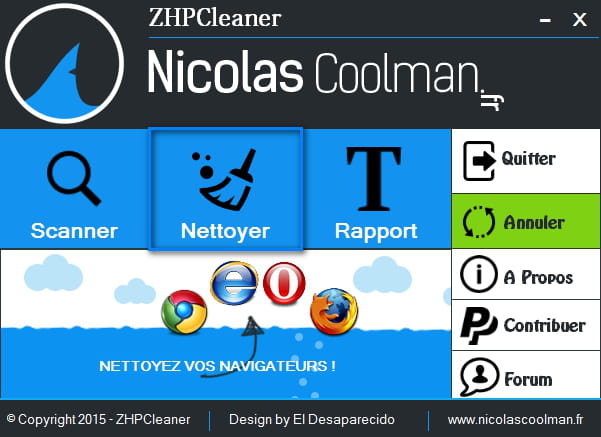
# Télécharge ZHPCleaner de Nicolas Coolman sur ton bureau.
(Désactive ton antivirus le temps du téléchargement et de l'utilisation.
Aide : http://www.sosvirus.net/tutoriel-desactiver-protection-residentiel-t586.html )
# Ferme ton navigateur
# Fais un double clique sur l'icône pour le lancer
-> Note: Clique droit sur l'icône puis Exécuter en tant qu'administrateur sous Windows Vista, Seven et Windows 8
# Accepte "les conditions d'utilisation"
# Clique sur Nettoyer
->Note: Durant le scan, si l'outil te demande "Avez-vous installé ce proxy ?" et que tu n'en as pas installé, clique sur "Non" ou "Voulez-vous remplacer la page d'accueil ?, clique sur "Non"

# Héberge le rapport rapport ZHPCleaner.txt présent sur ton bureau sur SosUpload puis transmet le lien généré dans ta prochaine réponse.
-> Tutoriel SosUpload : https://www.sosvirus.net/tutoriel-sosupload/
-
Merci de ta rapidité :) voici le lien :
http://upload.sosvirus.net/download/fw4cc6qqg78qo7awtv9qtj0lv426lhdsvf5766jx -
Hello ,
Tu as installé des adwares et des logiciels indésirables sur ton PC (Certainement à ton insu).
Pour comprendre, je t'invite à lire ce sujet : http://www.sosvirus.net/topic82172.html
# Télécharge AdwCleaner par Xplode sur ton bureau.
# Exécute AdwCleaner.exe.
# Fais clic droit dessus, exécuter en tant qu'administrateur sous Windows : 7/8 et Vista
# Choisi l'option Scanner
# Choisi l'option Nettoyer
# Accepte l'avertissement en cliquant sur OK

# Une fois le scan fini, un rapport s'ouvrira. Poste son contenu dans ta prochaine réponse.
Copie le contenu du rapport AdwCleaner sur Paste And Furious puis transmet le lien généré dans ta prochaine réponse.
-> Tuto Paste And Furious : http://www.sosvirus.net/tutoriel-paste-and-furious-t104985.html
# Le rapport est également sauvegardé sous C:\AdwCleaner[S1].txt