Fake McAfee Virus Popup
Solved/ClosedHello,
For some time now, I've been getting pop-ups from McAfee telling me that my PC is infected or that someone is downloading files onto my PC.
They appear in the bottom right corner.
Additionally, your help would allow me to clean up my PC :-)
Thank you
Pascal
9 answers
-
Moderator
Hello,
This is most likely about allowed notifications in a web browser.
You know, a pop-up on a web page that asks if you accept notifications...
In such a case, you can revoke or block them through the settings of the browser in question. -
Moderator
Hello.
Download FRST, once downloaded save it on the desktop then right-click on FRST and choose Run as administrator you will get this :

Click on Scan

Note, wait for the messages saying that the scan is finished to appear.

At the end of the scan you will have two text files on the desktop FRST and Addition.


Then send the FRST and ADDITION reports to PJJOINT see THIS TUTORIAL then provide the two links generated by PJJOINT in your reply.
bazfile
Moderator/Security Contributor.
a hello, a response, a thank you are always appreciated.-
-
-
Moderator@Pascal11300
Procedure to follow in the order indicated:
1- Open FRST as an administrator by right-clicking on FRST and choosing run as administrator
2 - Copy the entire script that is in the following box:Start:: CreateRestorePoint: CloseProcesses: Edge Notifications: Default -> hxxps://allowsuccess.org; hxxps://telecharger-youtube-mp3.com; hxxps://unnersosew.com FF Extension: (No name) - C:\Program Files (x86)\McAfee\SiteAdvisor\e10ssaffplg.xpi [not found] CHR Notifications: Default -> hxxps://lodder5.biz HKLM\...\Run: [] => [X] HKLM-x32\...\Run: [] => [X] HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\...\Run: [] => [X] HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\...\RunOnce: [Delete Cached Update Binary] => C:\WINDOWS\system32\cmd.exe /q /c del /q "C:\Users\cassi\AppData\Local\Microsoft\OneDrive\Update\OneDriveSetup.exe" (No file) HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\...\RunOnce: [Delete Cached Standalone Update Binary] => C:\WINDOWS\system32\cmd.exe /q /c del /q "C:\Users\cassi\AppData\Local\Microsoft\OneDrive\StandaloneUpdater\OneDriveSetup.exe" (No file) HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\...\RunOnce: [Uninstall 23.007.0109.0004] => C:\WINDOWS\system32\cmd.exe /q /c rmdir /s /q "C:\Users\cassi\AppData\Local\Microsoft\OneDrive\23.007.0109.0004" (No file) Task: {271F7124-9FBD-4043-A2B1-645450EF97CC} - \Lenovo\ImController\Lenovo iM Controller Scheduled Maintenance -> No file Task: {579B2F23-4D2D-4B6D-BE1E-E0344396D841} - System32\Tasks\CLMLSvc_P2G8 => C:\Program Files (x86)\Lenovo\Power2Go\CLMLSvc_P2G8.exe (No file) Task: {73BCA52E-21CD-4542-9BE1-2D8D165A96E4} - \Lenovo\ImController\Plugins\LenovoSystemUpdatePlugin_WeeklyTask -> No file Task: {B2F22D8D-EE3D-485B-8D25-87F8BCE55C74} - System32\Tasks\Lenovo\Vantage\Schedule\VantageTelemetryAddinTask => C:\Program Files (x86)\Lenovo\VantageService\3.6.15.0\ScheduleEventAction.exe VantageTelemetryAddinTask (No file) Task: {CE9845EB-3E0B-431D-B228-4E147E161557} - \Lenovo\ImController\Lenovo iM Controller Monitor -> No file S3 netprotection_network_filter2; System32\drivers\netprotection_network_filter2.sys [X] HKLM\SOFTWARE\Microsoft\Windows Defender: [DisableAntiSpyware] Restriction HKLM\SOFTWARE\Microsoft\Windows Defender: [DisableAntiVirus] Restriction HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate: Restriction GroupPolicy-Firefox: Restriction HKLM\SOFTWARE\Policies\Microsoft\Windows\CurrentVersion\Internet Settings\Zones\3: <==== ATTENTION (Restriction - Zones) ContextMenuHandlers1: [CLVDShellExt] -> {3E2A0A32-6E14-4BAD-AA87-BBB6A75EBFF2} => -> No file ContextMenuHandlers2: [CLVDShellExt] -> {3E2A0A32-6E14-4BAD-AA87-BBB6A75EBFF2} => -> No file ContextMenuHandlers5: [igfxcui] -> {3AB1675A-CCFF-11D2-8B20-00A0C93CB1F4} => -> No file SearchScopes: HKU\S-1-5-21-3532964059-4079266314-1441800742-1001 -> DefaultScope {B20908B5-5EAA-4A06-8293-1F85FAF6122E} URL = Handler: sacore - {5513F07E-936B-4E52-9B00-067394E91CC5} - No file End::3- Once the script is copied, click on Fix, FRST will automatically take the script that is in the clipboard.

Let the fix complete; once it is finished, you will be asked to restart your pc, do it as soon as prompted, see below.
Then, once your computer has restarted:
4- You will have a Fixlog file on your desktop, then send this report fixlog to PJJOINT and provide the link generated by PJJOINT in your reply.5- CHECK AND LET ME KNOW IF YOUR PROBLEM IS STILL PRESENT
-
-
Farbar Recovery Scan Tool (x64) Correction Results Version: 12-03-2023
Executed by cassi (14-03-2023 18:14:30) Run:1
Executed from C:\Users\cassi\Downloads\FRST-OlderVersion
Loaded Profiles: cassi
Boot Mode: Normal
==============================================fixlist content:
*****************
Start::
CreateRestorePoint:
CloseProcesses:
Edge Notifications: Default -> hxxps://allowsuccess.org; hxxps://telecharger-youtube-mp3.com; hxxps://unnersosew.com
FF Extension: (No name) - C:\Program Files (x86)\McAfee\SiteAdvisor\e10ssaffplg.xpi [not found]
CHR Notifications: Default -> hxxps://lodder5.biz
HKLM\...\Run: [] => [X]
HKLM-x32\...\Run: [] => [X]
HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\...\Run: [] => [X]
HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\...\RunOnce: [Delete Cached Update Binary] => C:\WINDOWS\system32\cmd.exe /q /c del /q "C:\Users\cassi\AppData\Local\Microsoft\OneDrive\Update\OneDriveSetup.exe" (File not found)
HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\...\RunOnce: [Delete Cached Standalone Update Binary] => C:\WINDOWS\system32\cmd.exe /q /c del /q "C:\Users\cassi\AppData\Local\Microsoft\OneDrive\StandaloneUpdater\OneDriveSetup.exe" (File not found)
HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\...\RunOnce: [Uninstall 23.007.0109.0004] => C:\WINDOWS\system32\cmd.exe /q /c rmdir /s /q "C:\Users\cassi\AppData\Local\Microsoft\OneDrive\23.007.0109.0004" (File not found)
Task: {271F7124-9FBD-4043-A2B1-645450EF97CC} - \Lenovo\ImController\Lenovo iM Controller Scheduled Maintenance -> File not found
Task: {579B2F23-4D2D-4B6D-BE1E-E0344396D841} - System32\Tasks\CLMLSvc_P2G8 => C:\Program Files (x86)\Lenovo\Power2Go\CLMLSvc_P2G8.exe (File not found)
Task: {73BCA52E-21CD-4542-9BE1-2D8D165A96E4} - \Lenovo\ImController\Plugins\LenovoSystemUpdatePlugin_WeeklyTask -> File not found
Task: {B2F22D8D-EE3D-485B-8D25-87F8BCE55C74} - System32\Tasks\Lenovo\Vantage\Schedule\VantageTelemetryAddinTask => C:\Program Files (x86)\Lenovo\VantageService\3.6.15.0\ScheduleEventAction.exe VantageTelemetryAddinTask (File not found)
Task: {CE9845EB-3E0B-431D-B228-4E147E161557} - \Lenovo\ImController\Lenovo iM Controller Monitor -> File not found
S3 netprotection_network_filter2; System32\drivers\netprotection_network_filter2.sys [X]
HKLM\SOFTWARE\Microsoft\Windows Defender: [DisableAntiSpyware] Restriction
HKLM\SOFTWARE\Microsoft\Windows Defender: [DisableAntiVirus] Restriction
HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate: Restriction
GroupPolicy-Firefox: Restriction
HKLM\SOFTWARE\Policies\Microsoft\Windows\CurrentVersion\Internet Settings\Zones\3: <==== ATTENTION (Restriction - Zones)
ContextMenuHandlers1: [CLVDShellExt] -> {3E2A0A32-6E14-4BAD-AA87-BBB6A75EBFF2} => -> File not found
ContextMenuHandlers2: [CLVDShellExt] -> {3E2A0A32-6E14-4BAD-AA87-BBB6A75EBFF2} => -> File not found
ContextMenuHandlers5: [igfxcui] -> {3AB1675A-CCFF-11D2-8B20-00A0C93CB1F4} => -> File not found
SearchScopes: HKU\S-1-5-21-3532964059-4079266314-1441800742-1001 -> DefaultScope {B20908B5-5EAA-4A06-8293-1F85FAF6122E} URL =
Handler: sacore - {5513F07E-936B-4E52-9B00-067394E91CC5} - File not found
End::
*****************The restore point was created successfully.
Processes closed successfully.
"Edge Notifications" => removed successfully
C:\Program Files (x86)\McAfee\SiteAdvisor\e10ssaffplg.xpi => path removed successfully
"Chrome Notifications" => removed successfully
"HKLM\Software\Microsoft\Windows\CurrentVersion\Run\\" => removed successfully
"HKLM\Software\WOW6432Node\Microsoft\Windows\CurrentVersion\Run\\" => removed successfully
"HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\Software\Microsoft\Windows\CurrentVersion\Run\\" => removed successfully
"HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\Software\Microsoft\Windows\CurrentVersion\RunOnce\\Delete Cached Update Binary" => removed successfully
"HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\Software\Microsoft\Windows\CurrentVersion\RunOnce\\Delete Cached Standalone Update Binary" => removed successfully
"HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\Software\Microsoft\Windows\CurrentVersion\RunOnce\\Uninstall 23.007.0109.0004" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Logon\{271F7124-9FBD-4043-A2B1-645450EF97CC}" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{271F7124-9FBD-4043-A2B1-645450EF97CC}" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Lenovo\ImController\Lenovo iM Controller Scheduled Maintenance" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Logon\{579B2F23-4D2D-4B6D-BE1E-E0344396D841}" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{579B2F23-4D2D-4B6D-BE1E-E0344396D841}" => removed successfully
C:\WINDOWS\System32\Tasks\CLMLSvc_P2G8 => moved successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\CLMLSvc_P2G8" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{73BCA52E-21CD-4542-9BE1-2D8D165A96E4}" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{73BCA52E-21CD-4542-9BE1-2D8D165A96E4}" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Lenovo\ImController\Plugins\LenovoSystemUpdatePlugin_WeeklyTask" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{B2F22D8D-EE3D-485B-8D25-87F8BCE55C74}" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{B2F22D8D-EE3D-485B-8D25-87F8BCE55C74}" => removed successfully
C:\WINDOWS\System32\Tasks\Lenovo\Vantage\Schedule\VantageTelemetryAddinTask => moved successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Lenovo\Vantage\Schedule\VantageTelemetryAddinTask" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{CE9845EB-3E0B-431D-B228-4E147E161557}" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{CE9845EB-3E0B-431D-B228-4E147E161557}" => removed successfully
"HKLM\Software\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Lenovo\ImController\Lenovo iM Controller Monitor" => removed successfully
HKLM\System\CurrentControlSet\Services\netprotection_network_filter2 => unable to delete. Access denied.
HKLM\SOFTWARE\Microsoft\Windows Defender\\"DisableAntiSpyware"="0" => value restored successfully
HKLM\SOFTWARE\Microsoft\Windows Defender\\"DisableAntiVirus"="0" => value restored successfully
HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate => removed successfully
C:\Program Files\Mozilla Firefox\distribution\policies.json => moved successfully
HKLM\SOFTWARE\Policies\Microsoft\Windows\CurrentVersion\Internet Settings\Zones\3 => removed successfully
HKLM\Software\Classes\*\ShellEx\ContextMenuHandlers\CLVDShellExt => removed successfully
HKLM\Software\Classes\Drive\ShellEx\ContextMenuHandlers\CLVDShellExt => removed successfully
HKLM\Software\Classes\Directory\Background\ShellEx\ContextMenuHandlers\igfxcui => removed successfully
"HKU\S-1-5-21-3532964059-4079266314-1441800742-1001\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\\DefaultScope" => removed successfully
HKLM\Software\Classes\PROTOCOLS\Handler\sacore => removed successfullyResults of scheduled file moving (Boot Mode: Normal) (Date&Time: 14-03-2023 18:45:01)
Results of planned key deletion after reboot:HKLM\System\CurrentControlSet\Services\netprotection_network_filter2 => unable to delete. Access denied.
==== End of Fixlog 18:45:01 ====
-
Please excuse me, but PJJOINT was not working....
-
Otherwise, everything seems to be back to normal, no more McAfee pop-ups!!!!
-
Moderator
The fixlog is OK.
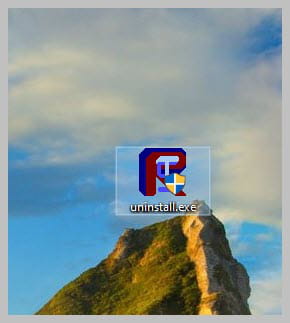
You can uninstall FRST, rename the FRST file you downloaded to uninstall, then once the file is renamed, open it; the uninstallation will happen automatically via a PC restart.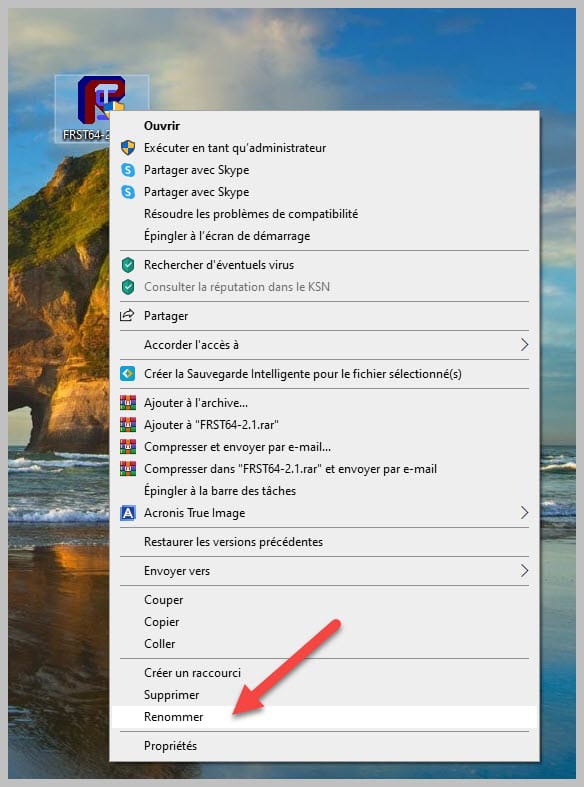
bazfile
Moderator/Security Contributor.
A hello, a reply, a thank you are always appreciated. -
Hello, I'm new to the forum. I found this post that deals with the same problem I'm encountering – pop-up windows that open in the notifications saying "payment error" and "Avast expired."
Since I have very little knowledge in computing, would it be possible to get some advice or help? -
Moderator
Hello,
Create your own topic,
Thank you
-
Moderator
Since you are new, to create your own post and ask your question click on:
https://forums.commentcamarche.net/forum/virus-securite-7/new
.
bazfile
Moderator/Security Contributor.
A hello, a response, and a thank you are always appreciated.