
Raccourcis clé uSB
RésoluAyant des virus sur tous mes supports amovibles (tous les dossiers s'affichent en raccourcis) j'ai suivi les conseils trouvés sur internet à savoir, telecharger roguekiller et le faire fonctionner, puis USBfix et le faire fonctionner. J'ai enregistré le rapport d'erreur de roguekiller. Je peux vous le joindre.
Quand j'ai actionné le USBfix, en revanche, au bout de 73% de moulinage et 31 fichiers infectés, il a pedalé dans la semoule... l'ordi s'est mis en veille. J'ai dû arrêter le logiciel au bout de 2h, arreter la session afin de pouvoir vous écrire ce message.
QU'en pensez vous ? QUe me conseillez vous de faire ?
54 réponses
Virus sur tous les supports amovibles et affichage des dossiers en raccourcis constituent la problématique, avec des essais de RogueKiller et USBFix qui peinent à supprimer les infections. Des solutions proposées incluent l’exécution de USBFix en mode sans échec avec suppression et le partage des rapports, l’utilisation de Shortcut_Module pour nettoyer les raccourcis, et la vérification des périphériques via des rapports. Pour progresser, certains conseillent de débrancher les autres périphériques, lancer USBFix en mode sans échec avec suppression, puis examiner les rapports pour repérer les éléments à nettoyer. En cas d’échec persistant, des messages d’erreur comme « allocation mémoire » apparaissent même en mode sans échec, d’où l’importance de lancer les outils un à un et de sauvegarder les données.
-
Contributeur sécuritéfais suppression
-
voici le rapport
http://upload.sosvirus.net/www/?a=d&i=Jxn3myba05
merci -
Contributeur sécuritéOui poste le
-
Bonjour !
A nouveau ce même virus : les dossiers sur clés usb se présentent sous forme de raccourcis.
Je suis en train de le désinfecter avec USB fix, j'ai le rapport d'erreur et vous demande de l'assistance pour mener à bien le nettoyage.
Merci ! -
il semblerait que tout va bien.
Merci ! -
Hello ,
Pour avast oui réinstalle le mais je te conseil quelque chose d'un peut plus performant vu que tes clés naviguent entre chez toi et le travail :
-> https://www.bitdefender.fr/solutions/
Plus de soucis sinon avec les clés ? Les rapport sont OK
-
Hello ,
Ok a demain :)
-
-
Bonjour !
Voici le rapport pour les deux dernieres clés USB.
Manifestement elles étaient infestées car un collegue s'en est servi sur son ordi et son antivirus les a vidées de leur contenu !
############################## | UsbFix V 7.169 | [Suppression]
Utilisateur: Administrateur (Administrateur) # UP1-LR3E2H7
Mis à jour le 31/03/2014 par El Desaparecido - Team SosVirus
Lancé à 09:51:08 | 19/04/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://depannageinformatique.org/acheter/reservation/?f=6
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: LENOVO (5017A78)
CPU: Intel(R) Core(TM) i5-2410M CPU @ 2.30GHz
RAM -> [Total : 3936 Mo| Free : 2840 Mo]
Bios: LENOVO
Boot: Normal boot
OS: Microsoft Windows 7 Professionnel (6.1.7601 64-Bit) Service Pack 1
WB: Windows Internet Explorer : 11.0.9600.17041
WB: Mozilla Firefox : 28.0
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AS: Windows Defender [Enabled | Updated]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 298 Go (68 Go libre(s) - 23%) [OSDisk] # NTFS
D:\ -> CD-ROM
E:\ -> Disque amovible # 7 Go (7 Go libre(s) - 94%) [KINGSTON] # FAT32
F:\ -> CD-ROM
G:\ -> Disque amovible # 7 Go (7 Go libre(s) - 100%) [] # FAT32
################## | Processus Actif |
C:\Windows\system32\csrss.exe (ID: 428 |ParentID: 420)
C:\Windows\system32\wininit.exe (ID: 492 |ParentID: 420)
C:\Windows\system32\csrss.exe (ID: 516 |ParentID: 500)
C:\Windows\system32\services.exe (ID: 556 |ParentID: 492)
C:\Windows\system32\lsass.exe (ID: 568 |ParentID: 492)
C:\Windows\system32\lsm.exe (ID: 580 |ParentID: 492)
C:\Windows\system32\svchost.exe (ID: 684 |ParentID: 556)
C:\Windows\system32\ibmpmsvc.exe (ID: 744 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 800 |ParentID: 556)
C:\Windows\System32\svchost.exe (ID: 860 |ParentID: 556)
C:\Windows\System32\svchost.exe (ID: 892 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 936 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 968 |ParentID: 556)
C:\Windows\system32\winlogon.exe (ID: 1004 |ParentID: 500)
C:\Program Files\Realtek\Audio\HDA\RtkAudioService64.exe (ID: 1076 |ParentID: 556)
C:\Program Files\Realtek\Audio\HDA\RAVBg64.exe (ID: 1100 |ParentID: 1076)
C:\Windows\system32\svchost.exe (ID: 1124 |ParentID: 556)
C:\Windows\System32\spoolsv.exe (ID: 1360 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 1400 |ParentID: 556)
C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe (ID: 1492 |ParentID: 556)
C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe (ID: 1512 |ParentID: 556)
C:\Program Files\Bonjour\mDNSResponder.exe (ID: 1556 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 1620 |ParentID: 556)
C:\Program Files (x86)\FusionInventory-Agent\perl\bin\perl.exe (ID: 1656 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 1772 |ParentID: 556)
C:\Windows\system32\taskhost.exe (ID: 1160 |ParentID: 556)
C:\Windows\system32\taskeng.exe (ID: 1528 |ParentID: 968)
C:\Windows\system32\Dwm.exe (ID: 1576 |ParentID: 892)
C:\Windows\Explorer.EXE (ID: 1768 |ParentID: 1420)
C:\Windows\system32\runonce.exe (ID: 2256 |ParentID: 1768)
C:\Windows\SysWOW64\runonce.exe (ID: 2276 |ParentID: 2256)
C:\Windows\system32\svchost.exe (ID: 2548 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 2584 |ParentID: 556)
C:\Windows\System32\rundll32.exe (ID: 2820 |ParentID: 684)
C:\Windows\System32\WUDFHost.exe (ID: 2876 |ParentID: 892)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 2060 |ParentID: 684)
################## | Recherche générique |
Supprimé! E:\jSugLyCC.vbs
Supprimé! G:\jSugLyCC.vbs
(!) Fichiers temporaires supprimés.
################## | Registre |
Supprimé! HKU\S-1-5-21-3331046427-1064584010-3109013383-500\Software\.\.\.\.\Mountpoints2\{36fc46cc-19c3-11e2-b328-cc52af824b4f}
################## | Regedit Run |
F2 - HKLM\..\Winlogon : [Shell] explorer.exe
F2 - [x64] HKLM\..\Winlogon : [Shell] explorer.exe
F2 - HKLM\..\Winlogon : [Userinit] userinit.exe,
F2 - [x64] HKLM\..\Winlogon : [Userinit] C:\Windows\system32\userinit.exe,
04 - HKCU\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKCU\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKCU\..\Run : [AdobeBridge]
04 - HKCU\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKCU\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKCU\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [Adobe Acrobat Speed Launcher] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrobat_sl.exe"
04 - HKLM\..\Run : [Acrobat Assistant 8.0] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrotray.exe"
04 - HKLM\..\Run : [AdobeCS4ServiceManager] "C:\Program Files (x86)\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" -launchedbylogin
04 - HKLM\..\Run : [APSDaemon] "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe"
04 - HKLM\..\Run : [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe"
04 - HKLM\..\Run : [HP Software Update] C:\Program Files (x86)\Hp\HP Software Update\HPWuSchd2.exe
04 - HKLM\..\Run : []
04 - [x64] HKLM\..\Run : [SynTPEnh] %ProgramFiles%\Synaptics\SynTP\SynTPEnh.exe
04 - [x64] HKLM\..\Run : [IgfxTray] C:\Windows\system32\igfxtray.exe
04 - [x64] HKLM\..\Run : [HotKeysCmds] C:\Windows\system32\hkcmd.exe
04 - [x64] HKLM\..\Run : [Persistence] C:\Windows\system32\igfxpers.exe
04 - [x64] HKLM\..\Run : [RTHDVCPL] C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe -s
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [AdobeBridge]
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Listing |
[12/03/2013 - 11:39:34 | SHD] - C:\$Recycle.Bin
[17/02/2014 - 17:59:26 | N | 0 Ko] - C:\AVScanner.ini
[31/01/2012 - 15:56:33 | D] - C:\certs
[04/04/2014 - 17:11:55 | N | 1 Ko | CA974E73AB3623A7C74124B45307B2D3] - C:\DelFix.txt
[14/07/2009 - 07:08:56 | SHD] - C:\Documents and Settings
[03/10/2013 - 15:24:36 | D] - C:\Drivers
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1028.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1031.txt
[07/11/2007 - 08:00:40 | N | 10 Ko | 99C22D4A31F4EAD4351B71D6F4E5F6A1] - C:\eula.1033.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1036.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1040.txt
[07/11/2007 - 08:00:40 | N | 0 Ko | 9B15A3A055CC6E67EA191A1B7885649A] - C:\eula.1041.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1042.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.2052.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.3082.txt
[18/10/2012 - 13:59:31 | D] - C:\GIRDAC
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\globdata.ini
[19/04/2014 - 09:49:48 | ASH | 3023220 Ko] - C:\hiberfil.sys
[07/11/2007 - 08:03:18 | N | 550 Ko | 520A6D1CBCC9CF642C625FE814C93C58] - C:\install.exe
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\install.ini
[31/01/2012 - 15:56:32 | N | 0 Ko] - C:\install.log
[07/11/2007 - 08:03:18 | N | 75 Ko | 4151A4D07640863783F837E588235837] - C:\install.res.1028.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 3B8A82E04238655EAEF97E074FB29911] - C:\install.res.1031.dll
[07/11/2007 - 08:03:18 | N | 89 Ko | 9EDEB8B1C5C0A4CD3A3016B85108127D] - C:\install.res.1033.dll
[07/11/2007 - 08:03:18 | N | 95 Ko | 5B6FF470CFA7087690E61F87E81EF78A] - C:\install.res.1036.dll
[07/11/2007 - 08:03:18 | N | 93 Ko | 6310AB8FC9E3DBEE80592FC453A34FEE] - C:\install.res.1040.dll
[07/11/2007 - 08:03:18 | N | 80 Ko | 13ED4517152203DE4BC52ACC0255D952] - C:\install.res.1041.dll
[07/11/2007 - 08:03:18 | N | 78 Ko | 0D4FB4095EA49C1EC89B9E8DB0B936A3] - C:\install.res.1042.dll
[07/11/2007 - 08:03:18 | N | 74 Ko | D7366B34E8AFB605C39EF56E2201FE85] - C:\install.res.2052.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 41BB37A347121F3E5E88D85100638B79] - C:\install.res.3082.dll
[31/01/2012 - 15:40:00 | D] - C:\Intel
[07/01/2014 - 20:35:06 | N | 0 Ko] - C:\lxct.log
[31/01/2012 - 15:45:17 | D] - C:\MININT
[02/10/2012 - 08:02:41 | RHD] - C:\MSOCache
[19/04/2014 - 09:49:52 | ASH | 6045696 Ko] - C:\pagefile.sys
[14/07/2009 - 05:20:08 | D] - C:\PerfLogs
[27/03/2014 - 18:28:07 | D] - C:\Program Files
[29/03/2014 - 18:39:51 | D] - C:\Program Files (x86)
[18/03/2014 - 11:34:26 | HD] - C:\ProgramData
[31/01/2012 - 15:44:07 | SHD] - C:\Recovery
[16/01/2014 - 02:42:40 | N | 594 Ko | ECFA4E7350DE3BB49AE671A9A3382A35] - C:\SecurityScanner.dll
[18/03/2014 - 14:41:20 | N | 219 Ko | 09F7E8F1D80416F7C17E8D76A65E93C9] - C:\Shortcut_Module_18_03_2014_13_41_20.txt
[18/04/2014 - 15:58:08 | SHD] - C:\System Volume Information
[19/04/2014 - 09:47:56 | D] - C:\UsbFix
[19/04/2014 - 09:57:11 | A | 10 Ko | 99CD7FAE9040BC3298D2AB135CD96F7C] - C:\UsbFix [Clean 10] UP1-LR3E2H7.txt
[15/04/2014 - 10:55:33 | N | 12 Ko | 3CC3307DEDD69021ABF7C2C8E0DB5049] - C:\UsbFix [Clean 2] UP1-LR3E2H7.txt
[15/04/2014 - 23:27:25 | N | 12 Ko | F35B8564A0A4DEE34A7F206657FB057D] - C:\UsbFix [Clean 4] UP1-LR3E2H7.txt
[15/04/2014 - 23:33:57 | N | 12 Ko | F916701323B46DAB5EF4DAD25262687D] - C:\UsbFix [Clean 6] UP1-LR3E2H7.txt
[15/04/2014 - 23:40:33 | N | 13 Ko | 30A405AB8D7F5B7938AAF9AB1CCC12D1] - C:\UsbFix [Clean 8] UP1-LR3E2H7.txt
[10/10/2013 - 09:33:33 | D] - C:\Users
[07/11/2007 - 08:00:40 | N | 6 Ko] - C:\vcredist.bmp
[07/11/2007 - 08:09:22 | N | 1409 Ko] - C:\VC_RED.cab
[07/11/2007 - 08:12:28 | N | 228 Ko] - C:\VC_RED.MSI
[04/04/2014 - 17:10:57 | D] - C:\Windows
[31/03/2014 - 16:33:08 | D] - C:\xampp
[28/01/2014 - 20:09:58 | N | 478565 Ko] - E:\Film PREDIT v30mn.wmv
[01/04/2014 - 17:12:18 | N | 3496 Ko] - E:\Diapo MEISSONNIER-8avril2014.odp
[11/04/2014 - 14:52:18 | N | 70 Ko] - E:\Com WCTR francophone - 14-03-14.odt
[31/10/2012 - 12:13:42 | SH | 4 Ko] - E:\._.Trashes
################## | Vaccin |
E:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
G:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
-
-
-
Et il ne me restera qu'une seule clé usb à vacciner... mais je ne la retrouverai que jeudi soir !
Voilà...c'est tout pour aujourd'hui !
Merci ! -
Et le troisieme disque dur externe qui se nomme aussi E:
---
############################## | UsbFix V 7.169 | [Suppression]
Utilisateur: Administrateur (Administrateur) # UP1-LR3E2H7
Mis à jour le 31/03/2014 par El Desaparecido - Team SosVirus
Lancé à 23:40:03 | 15/04/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://depannageinformatique.org/acheter/reservation/?f=6
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: LENOVO (5017A78)
CPU: Intel(R) Core(TM) i5-2410M CPU @ 2.30GHz
RAM -> [Total : 3936 Mo| Free : 2872 Mo]
Bios: LENOVO
Boot: Normal boot
OS: Microsoft Windows 7 Professionnel (6.1.7601 64-Bit) Service Pack 1
WB: Windows Internet Explorer : 11.0.9600.17041
WB: Mozilla Firefox : 28.0
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AS: Windows Defender [Enabled | Updated]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 298 Go (68 Go libre(s) - 23%) [OSDisk] # NTFS
D:\ -> CD-ROM
E:\ -> Disque fixe # 466 Go (107 Go libre(s) - 23%) [Iomega HDD] # NTFS
F:\ -> CD-ROM
################## | Processus Actif |
C:\Windows\system32\csrss.exe (ID: 428 |ParentID: 412)
C:\Windows\system32\wininit.exe (ID: 492 |ParentID: 412)
C:\Windows\system32\csrss.exe (ID: 516 |ParentID: 500)
C:\Windows\system32\services.exe (ID: 560 |ParentID: 492)
C:\Windows\system32\lsass.exe (ID: 568 |ParentID: 492)
C:\Windows\system32\lsm.exe (ID: 580 |ParentID: 492)
C:\Windows\system32\svchost.exe (ID: 684 |ParentID: 560)
C:\Windows\system32\ibmpmsvc.exe (ID: 744 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 800 |ParentID: 560)
C:\Windows\system32\winlogon.exe (ID: 836 |ParentID: 500)
C:\Windows\System32\svchost.exe (ID: 900 |ParentID: 560)
C:\Windows\System32\svchost.exe (ID: 948 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 988 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 1020 |ParentID: 560)
C:\Program Files\Realtek\Audio\HDA\RtkAudioService64.exe (ID: 1052 |ParentID: 560)
C:\Program Files\Realtek\Audio\HDA\RAVBg64.exe (ID: 1076 |ParentID: 1052)
C:\Windows\system32\svchost.exe (ID: 1100 |ParentID: 560)
C:\Windows\System32\spoolsv.exe (ID: 1376 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 1404 |ParentID: 560)
C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe (ID: 1508 |ParentID: 560)
C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe (ID: 1592 |ParentID: 560)
C:\Program Files\Bonjour\mDNSResponder.exe (ID: 1632 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 1680 |ParentID: 560)
C:\Program Files (x86)\FusionInventory-Agent\perl\bin\perl.exe (ID: 1716 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 1824 |ParentID: 560)
C:\Windows\system32\taskhost.exe (ID: 2088 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 2136 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 2256 |ParentID: 560)
C:\Windows\system32\taskeng.exe (ID: 2380 |ParentID: 1020)
C:\Windows\system32\Dwm.exe (ID: 2408 |ParentID: 948)
C:\Windows\Explorer.EXE (ID: 2436 |ParentID: 2392)
C:\Windows\system32\runonce.exe (ID: 2680 |ParentID: 2436)
C:\Windows\SysWOW64\runonce.exe (ID: 2692 |ParentID: 2680)
C:\Windows\System32\rundll32.exe (ID: 2744 |ParentID: 684)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 3040 |ParentID: 684)
################## | Recherche générique |
(!) Fichiers temporaires supprimés.
################## | Registre |
################## | Regedit Run |
F2 - HKLM\..\Winlogon : [Shell] explorer.exe
F2 - [x64] HKLM\..\Winlogon : [Shell] explorer.exe
F2 - HKLM\..\Winlogon : [Userinit] userinit.exe,
F2 - [x64] HKLM\..\Winlogon : [Userinit] C:\Windows\system32\userinit.exe,
04 - HKCU\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKCU\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKCU\..\Run : [AdobeBridge]
04 - HKCU\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKCU\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKCU\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [Adobe Acrobat Speed Launcher] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrobat_sl.exe"
04 - HKLM\..\Run : [Acrobat Assistant 8.0] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrotray.exe"
04 - HKLM\..\Run : [AdobeCS4ServiceManager] "C:\Program Files (x86)\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" -launchedbylogin
04 - HKLM\..\Run : [APSDaemon] "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe"
04 - HKLM\..\Run : [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe"
04 - HKLM\..\Run : [HP Software Update] C:\Program Files (x86)\Hp\HP Software Update\HPWuSchd2.exe
04 - HKLM\..\Run : []
04 - [x64] HKLM\..\Run : [SynTPEnh] %ProgramFiles%\Synaptics\SynTP\SynTPEnh.exe
04 - [x64] HKLM\..\Run : [IgfxTray] C:\Windows\system32\igfxtray.exe
04 - [x64] HKLM\..\Run : [HotKeysCmds] C:\Windows\system32\hkcmd.exe
04 - [x64] HKLM\..\Run : [Persistence] C:\Windows\system32\igfxpers.exe
04 - [x64] HKLM\..\Run : [RTHDVCPL] C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe -s
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [AdobeBridge]
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Listing |
[12/03/2013 - 11:39:34 | SHD] - C:\$Recycle.Bin
[17/02/2014 - 17:59:26 | N | 0 Ko] - C:\AVScanner.ini
[31/01/2012 - 15:56:33 | D] - C:\certs
[04/04/2014 - 17:11:55 | N | 1 Ko | CA974E73AB3623A7C74124B45307B2D3] - C:\DelFix.txt
[14/07/2009 - 07:08:56 | SHD] - C:\Documents and Settings
[03/10/2013 - 15:24:36 | D] - C:\Drivers
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1028.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1031.txt
[07/11/2007 - 08:00:40 | N | 10 Ko | 99C22D4A31F4EAD4351B71D6F4E5F6A1] - C:\eula.1033.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1036.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1040.txt
[07/11/2007 - 08:00:40 | N | 0 Ko | 9B15A3A055CC6E67EA191A1B7885649A] - C:\eula.1041.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1042.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.2052.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.3082.txt
[18/10/2012 - 13:59:31 | D] - C:\GIRDAC
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\globdata.ini
[15/04/2014 - 23:39:09 | ASH | 3023220 Ko] - C:\hiberfil.sys
[07/11/2007 - 08:03:18 | N | 550 Ko | 520A6D1CBCC9CF642C625FE814C93C58] - C:\install.exe
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\install.ini
[31/01/2012 - 15:56:32 | N | 0 Ko] - C:\install.log
[07/11/2007 - 08:03:18 | N | 75 Ko | 4151A4D07640863783F837E588235837] - C:\install.res.1028.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 3B8A82E04238655EAEF97E074FB29911] - C:\install.res.1031.dll
[07/11/2007 - 08:03:18 | N | 89 Ko | 9EDEB8B1C5C0A4CD3A3016B85108127D] - C:\install.res.1033.dll
[07/11/2007 - 08:03:18 | N | 95 Ko | 5B6FF470CFA7087690E61F87E81EF78A] - C:\install.res.1036.dll
[07/11/2007 - 08:03:18 | N | 93 Ko | 6310AB8FC9E3DBEE80592FC453A34FEE] - C:\install.res.1040.dll
[07/11/2007 - 08:03:18 | N | 80 Ko | 13ED4517152203DE4BC52ACC0255D952] - C:\install.res.1041.dll
[07/11/2007 - 08:03:18 | N | 78 Ko | 0D4FB4095EA49C1EC89B9E8DB0B936A3] - C:\install.res.1042.dll
[07/11/2007 - 08:03:18 | N | 74 Ko | D7366B34E8AFB605C39EF56E2201FE85] - C:\install.res.2052.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 41BB37A347121F3E5E88D85100638B79] - C:\install.res.3082.dll
[31/01/2012 - 15:40:00 | D] - C:\Intel
[07/01/2014 - 20:35:06 | N | 0 Ko] - C:\lxct.log
[31/01/2012 - 15:45:17 | D] - C:\MININT
[02/10/2012 - 08:02:41 | RHD] - C:\MSOCache
[15/04/2014 - 23:39:13 | ASH | 6045696 Ko] - C:\pagefile.sys
[14/07/2009 - 05:20:08 | D] - C:\PerfLogs
[27/03/2014 - 18:28:07 | D] - C:\Program Files
[29/03/2014 - 18:39:51 | D] - C:\Program Files (x86)
[18/03/2014 - 11:34:26 | HD] - C:\ProgramData
[31/01/2012 - 15:44:07 | SHD] - C:\Recovery
[16/01/2014 - 02:42:40 | N | 594 Ko | ECFA4E7350DE3BB49AE671A9A3382A35] - C:\SecurityScanner.dll
[18/03/2014 - 14:41:20 | N | 219 Ko | 09F7E8F1D80416F7C17E8D76A65E93C9] - C:\Shortcut_Module_18_03_2014_13_41_20.txt
[15/04/2014 - 09:51:32 | SHD] - C:\System Volume Information
[15/04/2014 - 23:38:22 | D] - C:\UsbFix
[15/04/2014 - 10:55:33 | N | 12 Ko | 3CC3307DEDD69021ABF7C2C8E0DB5049] - C:\UsbFix [Clean 2] UP1-LR3E2H7.txt
[15/04/2014 - 23:27:25 | N | 12 Ko | F35B8564A0A4DEE34A7F206657FB057D] - C:\UsbFix [Clean 4] UP1-LR3E2H7.txt
[15/04/2014 - 23:33:57 | N | 12 Ko | F916701323B46DAB5EF4DAD25262687D] - C:\UsbFix [Clean 6] UP1-LR3E2H7.txt
[15/04/2014 - 23:40:33 | A | 10 Ko | 65F9DEB2AFF35BA0628FBF62742EBB55] - C:\UsbFix [Clean 8] UP1-LR3E2H7.txt
[10/10/2013 - 09:33:33 | D] - C:\Users
[07/11/2007 - 08:00:40 | N | 6 Ko] - C:\vcredist.bmp
[07/11/2007 - 08:09:22 | N | 1409 Ko] - C:\VC_RED.cab
[07/11/2007 - 08:12:28 | N | 228 Ko] - C:\VC_RED.MSI
[04/04/2014 - 17:10:57 | D] - C:\Windows
[31/03/2014 - 16:33:08 | D] - C:\xampp
[09/10/2013 - 13:36:26 | SHD] - E:\$RECYCLE.BIN
[18/04/2011 - 22:36:15 | D] - E:\092511zik
[03/05/2013 - 13:07:00 | D] - E:\2013-05 Mes images MEILO
[13/03/2013 - 23:13:55 | N | 7441 Ko] - E:\CASNAV.pub
[07/07/2012 - 00:51:29 | D] - E:\Copie Lezarde
[14/06/2013 - 12:29:52 | D] - E:\Documentaires
[01/06/2005 - 14:36:46 | N | 419 Ko] - E:\DSCN3968.JPG
[02/06/2005 - 14:37:38 | N | 427 Ko] - E:\DSCN3971.JPG
[22/04/2012 - 22:37:45 | D] - E:\films serkan bea
[22/04/2012 - 22:23:39 | D] - E:\Final cut express
[04/05/2010 - 08:26:16 | N | 1312 Ko] - E:\girafe (3).JPG
[29/03/2013 - 12:07:57 | D] - E:\laurence2
[17/12/2012 - 23:54:48 | D] - E:\laurencelenovosauv2012_12_17
[07/11/2012 - 15:38:02 | D] - E:\MAG ALTER JEUNS
[07/11/2012 - 15:38:45 | D] - E:\meiloperso
[01/03/2011 - 19:47:59 | D] - E:\Mes vidéos
[07/10/2013 - 08:32:52 | D] - E:\Mise en page 2013-09-23
[09/10/2013 - 17:42:27 | D] - E:\Mise en page2013-10-08
[17/04/2011 - 22:46:47 | D] - E:\Nico
[25/09/2012 - 15:09:19 | D] - E:\plans maison
[05/02/2013 - 10:22:50 | D] - E:\PLUME
[15/04/2010 - 13:19:36 | N | 7989 Ko] - E:\pour zo.jpg
[11/11/2010 - 21:49:17 | D] - E:\RASED 2010
[15/02/2010 - 08:24:20 | SHD] - E:\RECYCLER
[31/08/2011 - 10:51:10 | D] - E:\sauvJO
[31/08/2011 - 10:50:03 | D] - E:\sauvLILLE
[24/01/2012 - 01:32:16 | D] - E:\sauvLO
[31/08/2011 - 10:53:31 | D] - E:\sauvMA MUSIQUE
[31/08/2011 - 10:55:03 | D] - E:\sauvMa musique meilo
[07/10/2013 - 14:06:15 | D] - E:\SEYYAR 2013-09-23
[06/02/2014 - 10:53:23 | D] - E:\SEYYAR IMPRIMEUR
[02/05/2013 - 14:23:30 | D] - E:\SEYYAR sauv 2009
[02/05/2013 - 14:31:42 | D] - E:\SEYYAR sauv 2012
[18/11/2012 - 11:52:44 | D] - E:\stage musique rome
[02/09/2011 - 09:28:16 | SHD] - E:\System Volume Information
[26/07/2010 - 00:26:22 | D] - E:\video posetmoset
################## | Vaccin |
E:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Disque G:
############################## | UsbFix V 7.169 | [Suppression]
Utilisateur: Administrateur (Administrateur) # UP1-LR3E2H7
Mis à jour le 31/03/2014 par El Desaparecido - Team SosVirus
Lancé à 23:33:33 | 15/04/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://depannageinformatique.org/acheter/reservation/?f=6
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: LENOVO (5017A78)
CPU: Intel(R) Core(TM) i5-2410M CPU @ 2.30GHz
RAM -> [Total : 3936 Mo| Free : 2819 Mo]
Bios: LENOVO
Boot: Normal boot
OS: Microsoft Windows 7 Professionnel (6.1.7601 64-Bit) Service Pack 1
WB: Windows Internet Explorer : 11.0.9600.17041
WB: Mozilla Firefox : 28.0
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AS: Windows Defender [Enabled | Updated]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 298 Go (68 Go libre(s) - 23%) [OSDisk] # NTFS
D:\ -> CD-ROM
F:\ -> CD-ROM
G:\ -> Disque fixe # 149 Go (28 Go libre(s) - 19%) [WD Passport] # FAT32
################## | Processus Actif |
C:\Windows\system32\csrss.exe (ID: 432 |ParentID: 424)
C:\Windows\system32\wininit.exe (ID: 496 |ParentID: 424)
C:\Windows\system32\csrss.exe (ID: 520 |ParentID: 504)
C:\Windows\system32\services.exe (ID: 560 |ParentID: 496)
C:\Windows\system32\lsass.exe (ID: 576 |ParentID: 496)
C:\Windows\system32\lsm.exe (ID: 584 |ParentID: 496)
C:\Windows\system32\svchost.exe (ID: 688 |ParentID: 560)
C:\Windows\system32\winlogon.exe (ID: 756 |ParentID: 504)
C:\Windows\system32\ibmpmsvc.exe (ID: 792 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 848 |ParentID: 560)
C:\Windows\System32\svchost.exe (ID: 912 |ParentID: 560)
C:\Windows\System32\svchost.exe (ID: 952 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 1012 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 292 |ParentID: 560)
C:\Program Files\Realtek\Audio\HDA\RtkAudioService64.exe (ID: 1040 |ParentID: 560)
C:\Program Files\Realtek\Audio\HDA\RAVBg64.exe (ID: 1068 |ParentID: 1040)
C:\Windows\system32\svchost.exe (ID: 1088 |ParentID: 560)
C:\Windows\System32\spoolsv.exe (ID: 1404 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 1432 |ParentID: 560)
C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe (ID: 1528 |ParentID: 560)
C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe (ID: 1580 |ParentID: 560)
C:\Program Files\Bonjour\mDNSResponder.exe (ID: 1628 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 1660 |ParentID: 560)
C:\Program Files (x86)\FusionInventory-Agent\perl\bin\perl.exe (ID: 1712 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 1804 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 1940 |ParentID: 560)
C:\Windows\system32\taskhost.exe (ID: 1760 |ParentID: 560)
C:\Windows\system32\svchost.exe (ID: 2132 |ParentID: 560)
C:\Windows\system32\taskeng.exe (ID: 2232 |ParentID: 292)
C:\Windows\system32\Dwm.exe (ID: 2280 |ParentID: 952)
C:\Windows\Explorer.EXE (ID: 2324 |ParentID: 2268)
C:\Windows\system32\runonce.exe (ID: 2572 |ParentID: 2324)
C:\Windows\SysWOW64\runonce.exe (ID: 2600 |ParentID: 2572)
C:\Windows\System32\rundll32.exe (ID: 2796 |ParentID: 688)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 2928 |ParentID: 688)
################## | Recherche générique |
(!) Fichiers temporaires supprimés.
################## | Registre |
################## | Regedit Run |
F2 - HKLM\..\Winlogon : [Shell] explorer.exe
F2 - [x64] HKLM\..\Winlogon : [Shell] explorer.exe
F2 - HKLM\..\Winlogon : [Userinit] userinit.exe,
F2 - [x64] HKLM\..\Winlogon : [Userinit] C:\Windows\system32\userinit.exe,
04 - HKCU\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKCU\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKCU\..\Run : [AdobeBridge]
04 - HKCU\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKCU\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKCU\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [Adobe Acrobat Speed Launcher] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrobat_sl.exe"
04 - HKLM\..\Run : [Acrobat Assistant 8.0] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrotray.exe"
04 - HKLM\..\Run : [AdobeCS4ServiceManager] "C:\Program Files (x86)\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" -launchedbylogin
04 - HKLM\..\Run : [APSDaemon] "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe"
04 - HKLM\..\Run : [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe"
04 - HKLM\..\Run : [HP Software Update] C:\Program Files (x86)\Hp\HP Software Update\HPWuSchd2.exe
04 - HKLM\..\Run : []
04 - [x64] HKLM\..\Run : [SynTPEnh] %ProgramFiles%\Synaptics\SynTP\SynTPEnh.exe
04 - [x64] HKLM\..\Run : [IgfxTray] C:\Windows\system32\igfxtray.exe
04 - [x64] HKLM\..\Run : [HotKeysCmds] C:\Windows\system32\hkcmd.exe
04 - [x64] HKLM\..\Run : [Persistence] C:\Windows\system32\igfxpers.exe
04 - [x64] HKLM\..\Run : [RTHDVCPL] C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe -s
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [AdobeBridge]
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Listing |
[12/03/2013 - 11:39:34 | SHD] - C:\$Recycle.Bin
[17/02/2014 - 17:59:26 | N | 0 Ko] - C:\AVScanner.ini
[31/01/2012 - 15:56:33 | D] - C:\certs
[04/04/2014 - 17:11:55 | N | 1 Ko | CA974E73AB3623A7C74124B45307B2D3] - C:\DelFix.txt
[14/07/2009 - 07:08:56 | SHD] - C:\Documents and Settings
[03/10/2013 - 15:24:36 | D] - C:\Drivers
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1028.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1031.txt
[07/11/2007 - 08:00:40 | N | 10 Ko | 99C22D4A31F4EAD4351B71D6F4E5F6A1] - C:\eula.1033.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1036.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1040.txt
[07/11/2007 - 08:00:40 | N | 0 Ko | 9B15A3A055CC6E67EA191A1B7885649A] - C:\eula.1041.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1042.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.2052.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.3082.txt
[18/10/2012 - 13:59:31 | D] - C:\GIRDAC
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\globdata.ini
[15/04/2014 - 23:32:33 | ASH | 3023220 Ko] - C:\hiberfil.sys
[07/11/2007 - 08:03:18 | N | 550 Ko | 520A6D1CBCC9CF642C625FE814C93C58] - C:\install.exe
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\install.ini
[31/01/2012 - 15:56:32 | N | 0 Ko] - C:\install.log
[07/11/2007 - 08:03:18 | N | 75 Ko | 4151A4D07640863783F837E588235837] - C:\install.res.1028.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 3B8A82E04238655EAEF97E074FB29911] - C:\install.res.1031.dll
[07/11/2007 - 08:03:18 | N | 89 Ko | 9EDEB8B1C5C0A4CD3A3016B85108127D] - C:\install.res.1033.dll
[07/11/2007 - 08:03:18 | N | 95 Ko | 5B6FF470CFA7087690E61F87E81EF78A] - C:\install.res.1036.dll
[07/11/2007 - 08:03:18 | N | 93 Ko | 6310AB8FC9E3DBEE80592FC453A34FEE] - C:\install.res.1040.dll
[07/11/2007 - 08:03:18 | N | 80 Ko | 13ED4517152203DE4BC52ACC0255D952] - C:\install.res.1041.dll
[07/11/2007 - 08:03:18 | N | 78 Ko | 0D4FB4095EA49C1EC89B9E8DB0B936A3] - C:\install.res.1042.dll
[07/11/2007 - 08:03:18 | N | 74 Ko | D7366B34E8AFB605C39EF56E2201FE85] - C:\install.res.2052.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 41BB37A347121F3E5E88D85100638B79] - C:\install.res.3082.dll
[31/01/2012 - 15:40:00 | D] - C:\Intel
[07/01/2014 - 20:35:06 | N | 0 Ko] - C:\lxct.log
[31/01/2012 - 15:45:17 | D] - C:\MININT
[02/10/2012 - 08:02:41 | RHD] - C:\MSOCache
[15/04/2014 - 23:32:38 | ASH | 6045696 Ko] - C:\pagefile.sys
[14/07/2009 - 05:20:08 | D] - C:\PerfLogs
[27/03/2014 - 18:28:07 | D] - C:\Program Files
[29/03/2014 - 18:39:51 | D] - C:\Program Files (x86)
[18/03/2014 - 11:34:26 | HD] - C:\ProgramData
[31/01/2012 - 15:44:07 | SHD] - C:\Recovery
[16/01/2014 - 02:42:40 | N | 594 Ko | ECFA4E7350DE3BB49AE671A9A3382A35] - C:\SecurityScanner.dll
[18/03/2014 - 14:41:20 | N | 219 Ko | 09F7E8F1D80416F7C17E8D76A65E93C9] - C:\Shortcut_Module_18_03_2014_13_41_20.txt
[15/04/2014 - 09:51:32 | SHD] - C:\System Volume Information
[15/04/2014 - 23:31:46 | D] - C:\UsbFix
[15/04/2014 - 10:55:33 | N | 12 Ko | 3CC3307DEDD69021ABF7C2C8E0DB5049] - C:\UsbFix [Clean 2] UP1-LR3E2H7.txt
[15/04/2014 - 23:27:25 | N | 12 Ko | F35B8564A0A4DEE34A7F206657FB057D] - C:\UsbFix [Clean 4] UP1-LR3E2H7.txt
[15/04/2014 - 23:33:57 | A | 10 Ko | 360A69543D0C3BEE1114C81463892855] - C:\UsbFix [Clean 6] UP1-LR3E2H7.txt
[10/10/2013 - 09:33:33 | D] - C:\Users
[07/11/2007 - 08:00:40 | N | 6 Ko] - C:\vcredist.bmp
[07/11/2007 - 08:09:22 | N | 1409 Ko] - C:\VC_RED.cab
[07/11/2007 - 08:12:28 | N | 228 Ko] - C:\VC_RED.MSI
[04/04/2014 - 17:10:57 | D] - C:\Windows
[31/03/2014 - 16:33:08 | D] - C:\xampp
[11/08/2009 - 13:28:24 | SHD] - G:\$RECYCLE.BIN
[05/03/2009 - 16:10:50 | AH | 15 Ko] - G:\.DS_Store
[24/03/2014 - 16:53:20 | D] - G:\2014-03 Mes images MEILO
[05/07/2008 - 16:13:10 | D] - G:\wd
[23/07/2009 - 15:21:48 | D] - G:\PM_récits
[11/09/2008 - 21:59:38 | D] - G:\Favoris
[07/10/2011 - 07:33:30 | D] - G:\2011-2012
[20/03/2008 - 14:07:26 | HD] - G:\.Trashes
[15/09/2011 - 15:31:24 | RSHD] - G:\RECYCLER
[02/08/2009 - 16:33:10 | N | 0 Ko] - G:\~$ript 30.doc
[19/03/2008 - 21:19:58 | SHD] - G:\System Volume Information
[19/03/2008 - 22:23:20 | D] - G:\Recycled
[11/07/2009 - 15:59:30 | ASH | 2801 Ko] - G:\Thumbs.db
[13/10/2011 - 21:54:42 | D] - G:\stage ORL
[20/04/2009 - 14:21:52 | D] - G:\films serkan bea
[10/05/2012 - 00:06:20 | D] - G:\2011-2012B
[03/09/2012 - 08:07:54 | D] - G:\meiloperso
[22/03/2009 - 20:17:58 | HD] - G:\.fseventsd
[05/01/2009 - 21:44:46 | N | 4 Ko] - G:\._Araba yolda 6.mov
[20/03/2008 - 14:07:26 | HD] - G:\.Spotlight-V100
[03/01/2009 - 01:39:26 | D] - G:\SAUVEGARDES LO 2007
[17/09/2012 - 11:27:20 | D] - G:\2012 SEYYAR
[30/01/2009 - 17:16:14 | HD] - G:\.TemporaryItems
[29/03/2012 - 13:40:32 | D] - G:\administratif
[22/04/2012 - 22:08:18 | D] - G:\sauvpartielleecole
[11/07/2009 - 15:55:18 | D] - G:\POSET MOSET
################## | Vaccin |
G:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Bonsoir
ALors non, je n'ai pas que le lecteur H:
voici les autres rapports, que je vais poster dans des messages différents et nommer par le nom du disque.
disque E:
############################## | UsbFix V 7.169 | [Suppression]
Utilisateur: Administrateur (Administrateur) # UP1-LR3E2H7
Mis à jour le 31/03/2014 par El Desaparecido - Team SosVirus
Lancé à 23:26:50 | 15/04/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://depannageinformatique.org/acheter/reservation/?f=6
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: LENOVO (5017A78)
CPU: Intel(R) Core(TM) i5-2410M CPU @ 2.30GHz
RAM -> [Total : 3936 Mo| Free : 2777 Mo]
Bios: LENOVO
Boot: Normal boot
OS: Microsoft Windows 7 Professionnel (6.1.7601 64-Bit) Service Pack 1
WB: Windows Internet Explorer : 11.0.9600.17041
WB: Mozilla Firefox : 28.0
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AS: Windows Defender [Enabled | Updated]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 298 Go (68 Go libre(s) - 23%) [OSDisk] # NTFS
D:\ -> CD-ROM
E:\ -> Disque fixe # 233 Go (105 Go libre(s) - 45%) [My Passport] # NTFS
F:\ -> CD-ROM
################## | Processus Actif |
C:\Windows\system32\csrss.exe (ID: 432 |ParentID: 420)
C:\Windows\system32\wininit.exe (ID: 492 |ParentID: 420)
C:\Windows\system32\csrss.exe (ID: 516 |ParentID: 500)
C:\Windows\system32\services.exe (ID: 556 |ParentID: 492)
C:\Windows\system32\lsass.exe (ID: 572 |ParentID: 492)
C:\Windows\system32\lsm.exe (ID: 580 |ParentID: 492)
C:\Windows\system32\svchost.exe (ID: 676 |ParentID: 556)
C:\Windows\system32\ibmpmsvc.exe (ID: 736 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 792 |ParentID: 556)
C:\Windows\system32\winlogon.exe (ID: 828 |ParentID: 500)
C:\Windows\System32\svchost.exe (ID: 896 |ParentID: 556)
C:\Windows\System32\svchost.exe (ID: 944 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 984 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 1016 |ParentID: 556)
C:\Program Files\Realtek\Audio\HDA\RtkAudioService64.exe (ID: 1040 |ParentID: 556)
C:\Program Files\Realtek\Audio\HDA\RAVBg64.exe (ID: 1072 |ParentID: 1040)
C:\Windows\system32\svchost.exe (ID: 1104 |ParentID: 556)
C:\Windows\System32\spoolsv.exe (ID: 1320 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 1372 |ParentID: 556)
C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe (ID: 1476 |ParentID: 556)
C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe (ID: 1508 |ParentID: 556)
C:\Program Files\Bonjour\mDNSResponder.exe (ID: 1540 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 1644 |ParentID: 556)
C:\Program Files (x86)\FusionInventory-Agent\perl\bin\perl.exe (ID: 1672 |ParentID: 556)
C:\Windows\system32\taskhost.exe (ID: 1268 |ParentID: 556)
C:\Windows\system32\taskeng.exe (ID: 968 |ParentID: 1016)
C:\Windows\system32\Dwm.exe (ID: 1772 |ParentID: 944)
C:\Windows\Explorer.EXE (ID: 2000 |ParentID: 1628)
C:\Windows\system32\runonce.exe (ID: 2276 |ParentID: 2000)
C:\Windows\SysWOW64\runonce.exe (ID: 2292 |ParentID: 2276)
C:\Windows\system32\svchost.exe (ID: 2404 |ParentID: 556)
C:\Windows\system32\svchost.exe (ID: 2440 |ParentID: 556)
C:\Windows\System32\rundll32.exe (ID: 2780 |ParentID: 676)
C:\Windows\system32\sppsvc.exe (ID: 1028 |ParentID: 556)
C:\Windows\System32\svchost.exe (ID: 2844 |ParentID: 556)
C:\Program Files\Windows Media Player\wmpnetwk.exe (ID: 2896 |ParentID: 556)
C:\Windows\system32\SearchIndexer.exe (ID: 444 |ParentID: 556)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 2136 |ParentID: 676)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 2724 |ParentID: 676)
\\?\C:\Windows\system32\wbem\WMIADAP.EXE (ID: 1524 |ParentID: 1016)
C:\Windows\system32\SearchProtocolHost.exe (ID: 1804 |ParentID: 444)
C:\Windows\system32\SearchFilterHost.exe (ID: 2792 |ParentID: 444)
################## | Recherche générique |
(!) Fichiers temporaires supprimés.
################## | Registre |
Supprimé! HKU\S-1-5-21-3331046427-1064584010-3109013383-500\Software\.\.\.\.\Mountpoints2\{36fc46cc-19c3-11e2-b328-cc52af824b4f}
################## | Regedit Run |
F2 - HKLM\..\Winlogon : [Shell] explorer.exe
F2 - [x64] HKLM\..\Winlogon : [Shell] explorer.exe
F2 - HKLM\..\Winlogon : [Userinit] userinit.exe,
F2 - [x64] HKLM\..\Winlogon : [Userinit] C:\Windows\system32\userinit.exe,
04 - HKCU\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKCU\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKCU\..\Run : [AdobeBridge]
04 - HKCU\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKCU\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKCU\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [Adobe Acrobat Speed Launcher] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrobat_sl.exe"
04 - HKLM\..\Run : [Acrobat Assistant 8.0] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrotray.exe"
04 - HKLM\..\Run : [AdobeCS4ServiceManager] "C:\Program Files (x86)\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" -launchedbylogin
04 - HKLM\..\Run : [APSDaemon] "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe"
04 - HKLM\..\Run : [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe"
04 - HKLM\..\Run : [HP Software Update] C:\Program Files (x86)\Hp\HP Software Update\HPWuSchd2.exe
04 - HKLM\..\Run : []
04 - [x64] HKLM\..\Run : [SynTPEnh] %ProgramFiles%\Synaptics\SynTP\SynTPEnh.exe
04 - [x64] HKLM\..\Run : [IgfxTray] C:\Windows\system32\igfxtray.exe
04 - [x64] HKLM\..\Run : [HotKeysCmds] C:\Windows\system32\hkcmd.exe
04 - [x64] HKLM\..\Run : [Persistence] C:\Windows\system32\igfxpers.exe
04 - [x64] HKLM\..\Run : [RTHDVCPL] C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe -s
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [AdobeBridge]
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Listing |
[12/03/2013 - 11:39:34 | SHD] - C:\$Recycle.Bin
[17/02/2014 - 17:59:26 | N | 0 Ko] - C:\AVScanner.ini
[31/01/2012 - 15:56:33 | D] - C:\certs
[04/04/2014 - 17:11:55 | N | 1 Ko | CA974E73AB3623A7C74124B45307B2D3] - C:\DelFix.txt
[14/07/2009 - 07:08:56 | SHD] - C:\Documents and Settings
[03/10/2013 - 15:24:36 | D] - C:\Drivers
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1028.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1031.txt
[07/11/2007 - 08:00:40 | N | 10 Ko | 99C22D4A31F4EAD4351B71D6F4E5F6A1] - C:\eula.1033.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1036.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1040.txt
[07/11/2007 - 08:00:40 | N | 0 Ko | 9B15A3A055CC6E67EA191A1B7885649A] - C:\eula.1041.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1042.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.2052.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.3082.txt
[18/10/2012 - 13:59:31 | D] - C:\GIRDAC
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\globdata.ini
[15/04/2014 - 23:21:04 | ASH | 3023220 Ko] - C:\hiberfil.sys
[07/11/2007 - 08:03:18 | N | 550 Ko | 520A6D1CBCC9CF642C625FE814C93C58] - C:\install.exe
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\install.ini
[31/01/2012 - 15:56:32 | N | 0 Ko] - C:\install.log
[07/11/2007 - 08:03:18 | N | 75 Ko | 4151A4D07640863783F837E588235837] - C:\install.res.1028.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 3B8A82E04238655EAEF97E074FB29911] - C:\install.res.1031.dll
[07/11/2007 - 08:03:18 | N | 89 Ko | 9EDEB8B1C5C0A4CD3A3016B85108127D] - C:\install.res.1033.dll
[07/11/2007 - 08:03:18 | N | 95 Ko | 5B6FF470CFA7087690E61F87E81EF78A] - C:\install.res.1036.dll
[07/11/2007 - 08:03:18 | N | 93 Ko | 6310AB8FC9E3DBEE80592FC453A34FEE] - C:\install.res.1040.dll
[07/11/2007 - 08:03:18 | N | 80 Ko | 13ED4517152203DE4BC52ACC0255D952] - C:\install.res.1041.dll
[07/11/2007 - 08:03:18 | N | 78 Ko | 0D4FB4095EA49C1EC89B9E8DB0B936A3] - C:\install.res.1042.dll
[07/11/2007 - 08:03:18 | N | 74 Ko | D7366B34E8AFB605C39EF56E2201FE85] - C:\install.res.2052.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 41BB37A347121F3E5E88D85100638B79] - C:\install.res.3082.dll
[31/01/2012 - 15:40:00 | D] - C:\Intel
[07/01/2014 - 20:35:06 | N | 0 Ko] - C:\lxct.log
[31/01/2012 - 15:45:17 | D] - C:\MININT
[02/10/2012 - 08:02:41 | RHD] - C:\MSOCache
[15/04/2014 - 23:21:09 | ASH | 6045696 Ko] - C:\pagefile.sys
[14/07/2009 - 05:20:08 | D] - C:\PerfLogs
[27/03/2014 - 18:28:07 | D] - C:\Program Files
[29/03/2014 - 18:39:51 | D] - C:\Program Files (x86)
[18/03/2014 - 11:34:26 | HD] - C:\ProgramData
[31/01/2012 - 15:44:07 | SHD] - C:\Recovery
[16/01/2014 - 02:42:40 | N | 594 Ko | ECFA4E7350DE3BB49AE671A9A3382A35] - C:\SecurityScanner.dll
[18/03/2014 - 14:41:20 | N | 219 Ko | 09F7E8F1D80416F7C17E8D76A65E93C9] - C:\Shortcut_Module_18_03_2014_13_41_20.txt
[15/04/2014 - 09:51:32 | SHD] - C:\System Volume Information
[15/04/2014 - 23:20:13 | D] - C:\UsbFix
[15/04/2014 - 10:55:33 | N | 12 Ko | 3CC3307DEDD69021ABF7C2C8E0DB5049] - C:\UsbFix [Clean 2] UP1-LR3E2H7.txt
[15/04/2014 - 23:27:25 | A | 11 Ko | 40490C27EBBC08E33682F4B7E3B29F2A] - C:\UsbFix [Clean 4] UP1-LR3E2H7.txt
[10/10/2013 - 09:33:33 | D] - C:\Users
[07/11/2007 - 08:00:40 | N | 6 Ko] - C:\vcredist.bmp
[07/11/2007 - 08:09:22 | N | 1409 Ko] - C:\VC_RED.cab
[07/11/2007 - 08:12:28 | N | 228 Ko] - C:\VC_RED.MSI
[04/04/2014 - 17:10:57 | D] - C:\Windows
[31/03/2014 - 16:33:08 | D] - C:\xampp
[21/03/2014 - 11:40:01 | SHD] - E:\$RECYCLE.BIN
[04/11/2009 - 18:21:30 | D] - E:\0911LOsauvegarde
[03/01/2009 - 17:03:50 | D] - E:\Mes jeux meilo
[29/11/2009 - 09:31:30 | D] - E:\Recycled
[02/11/2009 - 13:14:41 | SHD] - E:\RECYCLER
[29/11/2009 - 10:24:45 | D] - E:\sauvegarde Mes images meilo
[03/01/2009 - 17:07:46 | D] - E:\sauvegarde Ma musique
[29/11/2009 - 09:39:57 | D] - E:\sauvegarde Ma musique meilo
[03/01/2009 - 17:10:29 | D] - E:\sauvegardes video
[29/12/2009 - 23:34:09 | SHD] - E:\System Volume Information
################## | Vaccin |
E:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Je n'ai pas réussi à heberger le rapport sur sosupload qui ne prends manifestement plus que des images... dommage !
Oui, nous travaillons sur le site actuellement ;)
Tu n'as qu'un seul disque usb ?
Si c'est le cas, redémarre le PC et test le lecteur H mais tu ne devrais plus rencontrer de soucis.
Si tu as d'autres lecteur USB, déconnecte H et nettoie les autres de la même façon en communiquant le rapport stp :)
-
Bonjour
Je n'ai pas réussi à heberger le rapport sur sosupload qui ne prends manifestement plus que des images... dommage !
voici donc le rapport du scan d'uSB fix :
############################## | UsbFix V 7.169 | [Suppression]
Utilisateur: Administrateur (Administrateur) # UP1-LR3E2H7
Mis à jour le 31/03/2014 par El Desaparecido - Team SosVirus
Lancé à 10:48:26 | 15/04/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://depannageinformatique.org/acheter/reservation/?f=6
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: LENOVO (5017A78)
CPU: Intel(R) Core(TM) i5-2410M CPU @ 2.30GHz
RAM -> [Total : 3936 Mo| Free : 3029 Mo]
Bios: LENOVO
Boot: Normal boot
OS: Microsoft Windows 7 Professionnel (6.1.7601 64-Bit) Service Pack 1
WB: Windows Internet Explorer : 11.0.9600.17041
WB: Mozilla Firefox : 28.0
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AS: Windows Defender [Enabled | Updated]
FW: Windows FireWall [Enabled]
AS: Malwarebytes' Anti-Malware : 1.75.0001
C:\ (%systemdrive%) -> Disque fixe # 298 Go (68 Go libre(s) - 23%) [OSDisk] # NTFS
D:\ -> CD-ROM
E:\ -> Disque fixe # 466 Go (107 Go libre(s) - 23%) [Iomega HDD] # NTFS
F:\ -> CD-ROM
H:\ -> Disque amovible # 4 Go (4 Go libre(s) - 94%) [] # FAT32
################## | Processus Actif |
C:\Windows\system32\csrss.exe (ID: 436 |ParentID: 420)
C:\Windows\system32\wininit.exe (ID: 512 |ParentID: 420)
C:\Windows\system32\csrss.exe (ID: 536 |ParentID: 520)
C:\Windows\system32\services.exe (ID: 576 |ParentID: 512)
C:\Windows\system32\lsass.exe (ID: 588 |ParentID: 512)
C:\Windows\system32\lsm.exe (ID: 600 |ParentID: 512)
C:\Windows\system32\winlogon.exe (ID: 664 |ParentID: 520)
C:\Windows\system32\svchost.exe (ID: 760 |ParentID: 576)
C:\Windows\system32\ibmpmsvc.exe (ID: 824 |ParentID: 576)
C:\Windows\system32\svchost.exe (ID: 880 |ParentID: 576)
C:\Windows\System32\svchost.exe (ID: 964 |ParentID: 576)
C:\Windows\System32\svchost.exe (ID: 1004 |ParentID: 576)
C:\Windows\system32\svchost.exe (ID: 284 |ParentID: 576)
C:\Windows\system32\svchost.exe (ID: 456 |ParentID: 576)
C:\Program Files\Realtek\Audio\HDA\RtkAudioService64.exe (ID: 1088 |ParentID: 576)
C:\Program Files\Realtek\Audio\HDA\RAVBg64.exe (ID: 1112 |ParentID: 1088)
C:\Windows\system32\svchost.exe (ID: 1152 |ParentID: 576)
C:\Windows\System32\spoolsv.exe (ID: 1380 |ParentID: 576)
C:\Windows\system32\svchost.exe (ID: 1412 |ParentID: 576)
C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe (ID: 1496 |ParentID: 576)
C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe (ID: 1516 |ParentID: 576)
C:\Program Files\Bonjour\mDNSResponder.exe (ID: 1540 |ParentID: 576)
C:\Windows\system32\svchost.exe (ID: 1584 |ParentID: 576)
C:\Program Files (x86)\FusionInventory-Agent\perl\bin\perl.exe (ID: 1632 |ParentID: 576)
C:\Windows\system32\svchost.exe (ID: 1772 |ParentID: 576)
C:\Windows\system32\taskhost.exe (ID: 1268 |ParentID: 576)
C:\Windows\system32\Dwm.exe (ID: 1596 |ParentID: 1004)
C:\Windows\Explorer.EXE (ID: 1448 |ParentID: 1760)
C:\Windows\system32\taskeng.exe (ID: 2156 |ParentID: 456)
C:\Windows\system32\svchost.exe (ID: 2472 |ParentID: 576)
C:\Windows\system32\svchost.exe (ID: 2516 |ParentID: 576)
C:\Windows\system32\runonce.exe (ID: 2540 |ParentID: 1448)
C:\Windows\SysWOW64\runonce.exe (ID: 2608 |ParentID: 2540)
C:\Windows\System32\rundll32.exe (ID: 2700 |ParentID: 760)
C:\Windows\system32\taskeng.exe (ID: 2980 |ParentID: 456)
C:\Windows\system32\rundll32.exe (ID: 2084 |ParentID: 760)
C:\Windows\system32\DrvInst.exe (ID: 1020 |ParentID: 760)
C:\Windows\System32\WUDFHost.exe (ID: 2252 |ParentID: 1004)
C:\Windows\System32\dinotify.exe (ID: 2032 |ParentID: 2084)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 2152 |ParentID: 760)
C:\Windows\system32\rundll32.exe (ID: 2676 |ParentID: 760)
################## | Recherche générique |
Supprimé! H:\jSugLyCC.vbs
Supprimé! H:\presentation.lnk
Supprimé! H:\.lnk
Supprimé! H:\Publication1.lnk
Supprimé! H:\libellule-text.lnk
Supprimé! H:\P1000943.lnk
Supprimé! H:\P1000938.lnk
Supprimé! H:\P1000975.lnk
Supprimé! H:\plum2.lnk
Supprimé! H:\Libellule.lnk
Supprimé! H:\.Trashes.lnk
Supprimé! H:\.Spotlight-V100.lnk
Supprimé! H:\Autorun.inf.lnk
Supprimé! H:\sisi TECHNO.lnk
(!) Fichiers temporaires supprimés.
################## | Registre |
Supprimé! HKU\S-1-5-21-3331046427-1064584010-3109013383-500\Software\.\.\.\.\Mountpoints2\{36fc46cc-19c3-11e2-b328-cc52af824b4f}
################## | Regedit Run |
F2 - HKLM\..\Winlogon : [Shell] explorer.exe
F2 - [x64] HKLM\..\Winlogon : [Shell] explorer.exe
F2 - HKLM\..\Winlogon : [Userinit] userinit.exe,
F2 - [x64] HKLM\..\Winlogon : [Userinit] C:\Windows\system32\userinit.exe,
04 - HKCU\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKCU\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKCU\..\Run : [AdobeBridge]
04 - HKCU\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKCU\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKCU\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [Adobe Acrobat Speed Launcher] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrobat_sl.exe"
04 - HKLM\..\Run : [Acrobat Assistant 8.0] "C:\Program Files (x86)\Adobe\Acrobat 10.0\Acrobat\Acrotray.exe"
04 - HKLM\..\Run : [AdobeCS4ServiceManager] "C:\Program Files (x86)\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" -launchedbylogin
04 - HKLM\..\Run : [APSDaemon] "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe"
04 - HKLM\..\Run : [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe"
04 - HKLM\..\Run : [HP Software Update] C:\Program Files (x86)\Hp\HP Software Update\HPWuSchd2.exe
04 - HKLM\..\Run : []
04 - [x64] HKLM\..\Run : [SynTPEnh] %ProgramFiles%\Synaptics\SynTP\SynTPEnh.exe
04 - [x64] HKLM\..\Run : [IgfxTray] C:\Windows\system32\igfxtray.exe
04 - [x64] HKLM\..\Run : [HotKeysCmds] C:\Windows\system32\hkcmd.exe
04 - [x64] HKLM\..\Run : [Persistence] C:\Windows\system32\igfxpers.exe
04 - [x64] HKLM\..\Run : [RTHDVCPL] C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe -s
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [DAEMON Tools Lite] "C:\Program Files (x86)\DAEMON Tools Lite\DTLite.exe" -autorun
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Google Update] "C:\Users\Administrateur\AppData\Local\Google\Update\GoogleUpdate.exe" /c
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [AdobeBridge]
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [HP Photosmart Plus B210 series (NET)] "C:\Program Files\HP\HP Photosmart Plus B210 series\Bin\ScanToPCActivationApp.exe" -deviceID "CN16H3251605J9:NW" -scfn "HP Photosmart Plus B210 series (NET)" -AutoStart 1
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [YouSendIt.exe] C:\Program Files (x86)\YouSendIt\Express\YouSendIt.exe -ui none
04 - HKU\S-1-5-21-3331046427-1064584010-3109013383-500\..\Run : [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Listing |
[12/03/2013 - 11:39:34 | SHD] - C:\$Recycle.Bin
[17/02/2014 - 17:59:26 | N | 0 Ko] - C:\AVScanner.ini
[31/01/2012 - 15:56:33 | D] - C:\certs
[04/04/2014 - 17:11:55 | N | 1 Ko | CA974E73AB3623A7C74124B45307B2D3] - C:\DelFix.txt
[14/07/2009 - 07:08:56 | SHD] - C:\Documents and Settings
[03/10/2013 - 15:24:36 | D] - C:\Drivers
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1028.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1031.txt
[07/11/2007 - 08:00:40 | N | 10 Ko | 99C22D4A31F4EAD4351B71D6F4E5F6A1] - C:\eula.1033.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1036.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1040.txt
[07/11/2007 - 08:00:40 | N | 0 Ko | 9B15A3A055CC6E67EA191A1B7885649A] - C:\eula.1041.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.1042.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.2052.txt
[07/11/2007 - 08:00:40 | N | 17 Ko | 9147A93F43D8E58218EBCB15FDA888C9] - C:\eula.3082.txt
[18/10/2012 - 13:59:31 | D] - C:\GIRDAC
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\globdata.ini
[15/04/2014 - 10:47:08 | ASH | 3023220 Ko] - C:\hiberfil.sys
[07/11/2007 - 08:03:18 | N | 550 Ko | 520A6D1CBCC9CF642C625FE814C93C58] - C:\install.exe
[07/11/2007 - 08:00:40 | N | 1 Ko] - C:\install.ini
[31/01/2012 - 15:56:32 | N | 0 Ko] - C:\install.log
[07/11/2007 - 08:03:18 | N | 75 Ko | 4151A4D07640863783F837E588235837] - C:\install.res.1028.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 3B8A82E04238655EAEF97E074FB29911] - C:\install.res.1031.dll
[07/11/2007 - 08:03:18 | N | 89 Ko | 9EDEB8B1C5C0A4CD3A3016B85108127D] - C:\install.res.1033.dll
[07/11/2007 - 08:03:18 | N | 95 Ko | 5B6FF470CFA7087690E61F87E81EF78A] - C:\install.res.1036.dll
[07/11/2007 - 08:03:18 | N | 93 Ko | 6310AB8FC9E3DBEE80592FC453A34FEE] - C:\install.res.1040.dll
[07/11/2007 - 08:03:18 | N | 80 Ko | 13ED4517152203DE4BC52ACC0255D952] - C:\install.res.1041.dll
[07/11/2007 - 08:03:18 | N | 78 Ko | 0D4FB4095EA49C1EC89B9E8DB0B936A3] - C:\install.res.1042.dll
[07/11/2007 - 08:03:18 | N | 74 Ko | D7366B34E8AFB605C39EF56E2201FE85] - C:\install.res.2052.dll
[07/11/2007 - 08:03:18 | N | 94 Ko | 41BB37A347121F3E5E88D85100638B79] - C:\install.res.3082.dll
[31/01/2012 - 15:40:00 | D] - C:\Intel
[07/01/2014 - 20:35:06 | N | 0 Ko] - C:\lxct.log
[31/01/2012 - 15:45:17 | D] - C:\MININT
[02/10/2012 - 08:02:41 | RHD] - C:\MSOCache
[15/04/2014 - 10:47:11 | ASH | 6045696 Ko] - C:\pagefile.sys
[14/07/2009 - 05:20:08 | D] - C:\PerfLogs
[27/03/2014 - 18:28:07 | D] - C:\Program Files
[29/03/2014 - 18:39:51 | D] - C:\Program Files (x86)
[18/03/2014 - 11:34:26 | HD] - C:\ProgramData
[31/01/2012 - 15:44:07 | SHD] - C:\Recovery
[16/01/2014 - 02:42:40 | N | 594 Ko | ECFA4E7350DE3BB49AE671A9A3382A35] - C:\SecurityScanner.dll
[18/03/2014 - 14:41:20 | N | 219 Ko | 09F7E8F1D80416F7C17E8D76A65E93C9] - C:\Shortcut_Module_18_03_2014_13_41_20.txt
[15/04/2014 - 09:51:32 | SHD] - C:\System Volume Information
[15/04/2014 - 09:55:10 | D] - C:\UsbFix
[15/04/2014 - 10:55:32 | A | 11 Ko | 3FE492EF2B5985251CF67639491AE382] - C:\UsbFix [Clean 2] UP1-LR3E2H7.txt
[10/10/2013 - 09:33:33 | D] - C:\Users
[07/11/2007 - 08:00:40 | N | 6 Ko] - C:\vcredist.bmp
[07/11/2007 - 08:09:22 | N | 1409 Ko] - C:\VC_RED.cab
[07/11/2007 - 08:12:28 | N | 228 Ko] - C:\VC_RED.MSI
[04/04/2014 - 17:10:57 | D] - C:\Windows
[31/03/2014 - 16:33:08 | D] - C:\xampp
[29/11/2013 - 11:01:24 | N | 223007 Ko] - H:\presentation.pub
[05/03/2014 - 10:56:38 | SH | 4 Ko] - H:\._.Trashes
[05/03/2014 - 10:42:36 | N | 11 Ko | 8BA1269A0C1D0F8CCC76C6B2E5AD2783] - H:\Publication1.txt
[05/03/2014 - 10:38:16 | D] - H:\Libellule
[05/03/2014 - 10:56:38 | SHD] - H:\.Trashes
[05/03/2014 - 10:56:40 | SHD] - H:\.Spotlight-V100
[05/03/2014 - 12:14:14 | N | 4 Ko | A1118EA96ABE06694A27FFD666463965] - H:\libellule-text.txt
[27/11/2013 - 18:25:40 | N | 5393 Ko] - H:\P1000943.JPG
[27/11/2013 - 18:21:50 | N | 5268 Ko] - H:\P1000938.JPG
[04/12/2013 - 17:25:44 | N | 5003 Ko] - H:\P1000975.JPG
[12/11/2013 - 11:56:22 | N | 7308 Ko] - H:\plum2.jpg
[05/03/2014 - 12:26:24 | N | 16 Ko] - H:\libellule-text.rtf
[10/04/2014 - 16:05:54 | N | 46 Ko] - H:\sisi TECHNO.odt
################## | Vaccin |
E:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
H:\Autorun.inf -> Vaccin créé par UsbFix (El Desaparecido)
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Ok je vais faire ça.
Et j'en profite pour demander si c'est normal que dans la liste des disques durs apparait "lecteur BD-rom CS4 (F:)" depuis plusieurs mois sans qu'il s'agisse d'un disque dur externe ou d'une clé que j'ai installé. -
Bonjour meilo,
Ta version de UsbFix n'est pas à jours, si usbfix est toujours installé, désinstalle le .
# Télécharge UsbFix par El Desaparecido sur ton Bureau.
# Si ton antivirus affiche une alerte, ignore-la et désactive l'antivirus temporairement.
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Suppression.

# Note : L'ordinateur va redémarrer automatiquement, au redémarrage, clique sur le message transmis par UsbFix et laisse le programme travailler.
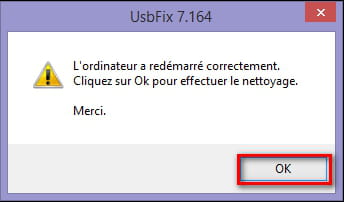
# Laisse travailler l'outil, ton bureau ne sera pas accessible durant la phase de nettoyage, c'est normal.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système ( C:\UsbFix [Clean ?] Nom de l'ordinateur.txt ).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# ->> Tutoriel (aide) en images sur le site de l'auteur.
-
merci !
-
alors là... je m'incline :-)
-
Contributeur sécuritéJ'ai prévenu le concepteur d'Usbfix :)
-
ok lilidurhone
mais le symptome de raccourcis sur les clés USB continue...
:-( -
Contributeur sécurité@HAWX
Comme promis je prends le relais
Meilo
il n'y a plus de raccourci mais un dossier
RECYCLER, un dossier caché $RECYCLE.BIN => pas touche c'est la corbeille
un dossier caché Autorun.inf => vaccin crée par usbfix
un dossier caché verrouillé system volume information => pas touche points de restauration!!
Sur la carte SD : restent les dossiers
FOUND.OOO
,le bloc note BOOTEX.LOG
AUTORUN.INF en caché
Laisse tout c'est normal


- 1
- 2
- 3
