
Démarrage PC très long
Je sollicite votre aide car le démarrage de mon PC est très long.
Je fais régulièrement des analyses avec Avira, Emisoft et Spybot et je n'ai pas de problèmes. Et j'utilise aussi régulièrement Ccleaner.
J'aurai besoin que l'on m'aide pour trouver d'autres astuces pour que mon PC démarre plus vite.
Vous remerciant d'avance.
Thomas
34 réponses
Démarrage lent d'un PC sous Windows 7 pousse à rechercher des astuces d'optimisation malgré des analyses régulières et l'usage de CCleaner, Avira, Emisoft et Spybot. La meilleure réponse propose de supprimer les outils de désinfection utilisés et de purger la restauration système afin de créer un nouveau point de restauration sain et stabiliser le démarrage. D'autres échanges évoquent des scans avec AdwCleaner et l'exécution répétée du script ZHPFix, puis l'optimisation du démarrage sous Windows via l'outil Démarrage de CCleaner et la vérification de l'impact. Pour éviter les ralentissements persistants, certaines solutions préconisent la désinstallation d'outils superflus et le suivi des rapports de nettoyage afin de prévenir l'influence des adwares et de corriger les paramètres système.
-
Bonjour,
Les ralentissements peuvent être matériels ... logiciels ...
Pour commencer il faut visualiser l'état d'utilisation du CPU & Mémoire, pour cela nous allons utiliser le Gestionnaire de tâches de Windows. Vous pouvez l'ouvrir ...
En appuyant simultanément sur les touches CTRL+ALT+ la touche Suppr et en cliquant sur Gestionnaire de tâches.
Faites moi une impression d'écran de :
vos Processus en cours.
et aussi celui de Performance.
A toute. -
Bonjour,
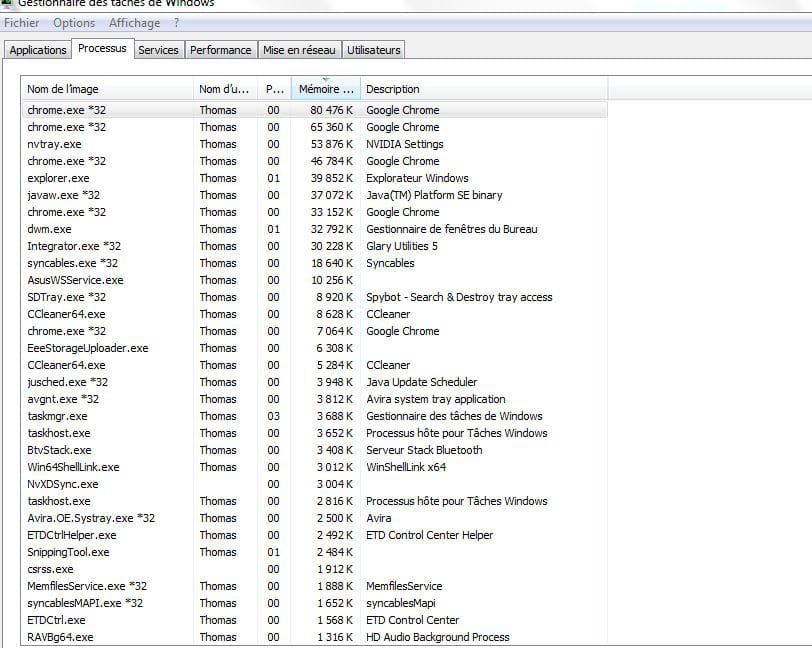
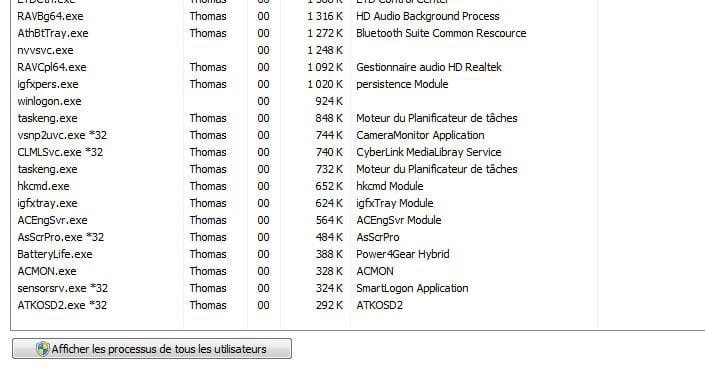
Voici l'impression écran
-
Re,
Apriori on peut Optimiser ton ordinateur pour qu'il démarre un peu plus vite.
Pour y voir plus clair peut-tu me faire un scan avec :
Télécharge et installe ZHPdiag : http://www.nicolascoolman.fr/download/zhpdiag/ ouvre ZHPdiag (icône en forme de parchemin) clique sur Configurer puis sur la loupe sans + ni -, l'analyse commence quand elle sera terminé tu auras sur ton bureau un fichier texte nommé ZHPdiag tu le postes sur http://www.cjoint.com/ puis tu mets le lien généré par cjoint dans ta réponse.
Tutoriel pour cjoint : https://www.commentcamarche.net/faq/29493-utiliser-cjoint-pour-heberger-des-fichiers
Merci -
Re,
Voici le lien
http://cjoint.com/?EArqx2s72ej -
Tu as installé des adwares et programmes parasites sur ton PC qui ouvrent des publicités et ralentissent l'ordinateur et les navigateurs WEB.
Voici la procédure à suivre pour les supprimer :
Désinstalle par programmes et fonctionnalité Spybot Search & Destroy 2 il est inutile et obsolète
Commence par ceci :
Suis le tutorial AdwCleaner http://forum.malekal.com/adwcleaner-t33839.html ( d'Xplode )
Lien de téléchargement --> https://toolslib.net/downloads/viewdownload/1-adwcleaner/
Télécharge le sur ton bureau ou dossier de téléchargement.
Lance AdwCleaner, clique sur [Scanner].
L'analyse peux durer plusieurs minutes, patiente.
Une fois le scan terminé, un rapport s'ouvrira. Copie/colle le contenu du rapport dans ta prochaine réponse par un copier/coller. -
Voici le rapport :
# AdwCleaner v4.108 - Rapport créé le 17/01/2015 à 16:44:13
# Mis à jour le 17/01/2015 par Xplode
# Database : 2015-01-13.2 [Live]
# Système d'exploitation : Windows 7 Home Premium Service Pack 1 (64 bits)
# Nom d'utilisateur : Thomas - THOMAS-PC
# Exécuté depuis : C:\Users\Thomas\Downloads\adwcleaner_4.108.exe
# Option : Nettoyer
***** [ Services ] *****
***** [ Fichiers / Dossiers ] *****
***** [ Tâches planifiées ] *****
***** [ Raccourcis ] *****
***** [ Registre ] *****
Clé Supprimée : HKCU\Software\Google\Chrome\Extensions\paoponfhfdfnjgddpnpjkambkcgdaaib
Clé Supprimée : HKCU\Software\Conduit
Clé Supprimée : [x64] HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\464AA55239C100F32AF2D438EDDC0F47
Clé Supprimée : [x64] HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\5652BA3D5FB98AE31B337BF0AF939856
Clé Supprimée : [x64] HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\86EB95E1AFCBABE3DB9ECCC669B99494
***** [ Navigateurs ] *****
-\\ Internet Explorer v11.0.9600.17496
-\\ Google Chrome v
*************************
AdwCleaner[R0].txt - [1375 octets] - [17/01/2015 16:40:41]
AdwCleaner[S0].txt - [1245 octets] - [17/01/2015 16:44:13]
########## EOF - C:\AdwCleaner\AdwCleaner[S0].txt - [1305 octets] ########## -
Peut-tu STP me refaire un scan de ZHPDiag.
Une fois le scan terminé, un rapport s'ouvrira.
Copie/colle le contenu du rapport dans ta prochaine réponse par un copier/coller.
++ -
~ Rapport de ZHPDiag v2015.1.15.6 - Nicolas Coolman (15/01/2015)
~ Lancé par Thomas (17/01/2015 16:58:38)
~ Facebook : https://www.facebook.com/nicolascoolman1
~ Adresse du Forum https://nicolascoolman.eu
~ Traduit par Nicolas Coolman
~ Etat de la version : Version à jour.
~ Liste blanche : Désactivée par l'utilisateur
~ Elévation des Privilèges : OK
~ User Account Control (UAC):
---\\ Navigateurs Internet
MSIE: Internet Explorer v11.0.9600.17501
GCIE: Google Chrome v39.0.2171.99 (Defaut)
---\\ Informations sur les produits Windows
~ Langage: Français
Windows 7 Home Premium, 64-bit Service Pack 1 (Build 7601)
Windows Server License Manager Script : OK
~ Windows Operating System - Windows(R) 7, OEM_SLP channel
System Locked Preinstallation (OEM_SLP) : OK
Windows ID Activation : OK
~ Windows Partial Key : 9YQTR
Windows License : OK
~ Windows Remaining Initializations Number : 3
Software Protection Service (Protection logicielle) : OK
Windows Automatic Updates : OK
Windows Activation Technologies : OK
---\\ Logiciels de protection du système
Avira Free Antivirus v14.0.7.468
Emsisoft Anti-Malware 5.1
Malwarebytes Anti-Malware version 2.0.2.1012
Windows Defender W7 (Activate)
---\\ Logiciels d'optimisation du système
CCleaner v5.00
---\\ Logiciels de partage PeerToPeer
µTorrent v3.2.0 =>P2P.µTorrent
---\\ Surveillance de Logiciels
Adobe Flash Player 16 NPAPI
Adobe Reader XI
---\\ Informations sur le système
~ Processor: Intel64 Family 6 Model 42 Stepping 7, GenuineIntel
~ Operating System: 64 Bits
Boot mode: Normal (Normal boot)
Total RAM: 4007 MB (51% free)
System Restore: Activé (Enable)
System drive C: has 50 GB (33%) free of 149 GB
---\\ Mode de connexion au système
~ Computer Name: THOMAS-PC
~ User Name: Thomas
~ All Users Names: UpdatusUser, Thomas, HomeGroupUser$, Administrateur,
~ Unselected Option: None
Logged in as Administrator
---\\ Variables d'environnement
~ System Unit : C:\
~ %AppZHP% : C:\Users\Thomas\AppData\Roaming\ZHP\
~ %AppData% : C:\Users\Thomas\AppData\Roaming\
~ %Desktop% : C:\Users\Thomas\Desktop\
~ %Favorites% : C:\Users\Thomas\Favorites\
~ %LocalAppData% : C:\Users\Thomas\AppData\Local\
~ %StartMenu% : C:\Users\Thomas\AppData\Roaming\Microsoft\Windows\Start Menu\
~ %Windir% : C:\Windows\
~ %System% : C:\Windows\System32\
---\\ Enumération des unités disques
C: Hard drive, Flash drive, Thumb drive (Free 50 Go of 149 Go)
D: Hard drive, Flash drive, Thumb drive (Free 362 Go of 426 Go)
E: CD-ROM drive (Not Inserted)
F: CD-ROM drive (Not Inserted)
G: CD-ROM drive (Not Inserted)
---\\ Etat du Centre de Sécurité Windows
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiSpywareOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] AntiVirusOverride: OK
[HKLM\SOFTWARE\Microsoft\Security Center\Svc] FirewallOverride: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\Explorer] NoActiveDesktopChanges: Modified
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\NOHIDDEN] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\SHOWALL] CheckedValue: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Associations] Application: OK
[HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon] Shell: OK
[HKLM\SYSTEM\CurrentControlSet\Services\COMSysApp] Type: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install] LastSuccessTime : OK
~ Security Center: 46 Scanned in 00mn 00s
---\\ Recherche particulière de fichiers génériques
[MD5.332FEAB1435662FC6C672E25BEB37BE3] - (.Microsoft Corporation - Explorateur Windows.) (.25/02/2011 - 07:19:30.) -- C:\Windows\Explorer.exe [2871808]
[MD5.94355C28C1970635A31B3FE52EB7CEBA] - (.Microsoft Corporation - Application de démarrage de Windows.) (.14/07/2009 - 02:39:52.) -- C:\Windows\System32\Wininit.exe [129024]
[MD5.4AF089160FE082E5EA5C4AA72782DCA2] - (.Microsoft Corporation - Extensions Internet pour Win32.) (.22/11/2014 - 02:28:21.) -- C:\Windows\System32\wininet.dll [2358272]
[MD5.8CEBD9D0A0A879CDE9F36F4383B7CAEA] - (.Microsoft Corporation - Application d'ouverture de session Windows.) (.17/07/2014 - 03:07:24.) -- C:\Windows\System32\Winlogon.exe [455168]
[MD5.067FA52BFB59A56110A12312EF9AF243] - (.Microsoft Corporation - Bibliothèque de licences.) (.20/11/2010 - 14:27:26.) -- C:\Windows\System32\sppcomapi.dll [232448]
[MD5.FA886682CFC5D36718D3E436AACF10B9] - (.Microsoft Corporation - Ancillary Function Driver for WinSock.) (.30/05/2014 - 07:45:52.) -- C:\Windows\system32\Drivers\AFD.sys [497152]
[MD5.02062C0B390B7729EDC9E69C680A6F3C] - (.Microsoft Corporation - ATAPI IDE Miniport Driver.) (.14/07/2009 - 02:52:21.) -- C:\Windows\system32\Drivers\atapi.sys [24128]
[MD5.B8BD2BB284668C84865658C77574381A] - (.Microsoft Corporation - CD-ROM File System Driver.) (.14/07/2009 - 00:19:47.) -- C:\Windows\system32\Drivers\Cdfs.sys [92160]
[MD5.F036CE71586E93D94DAB220D7BDF4416] - (.Microsoft Corporation - SCSI CD-ROM Driver.) (.20/11/2010 - 10:19:21.) -- C:\Windows\system32\Drivers\Cdrom.sys [147456]
[MD5.9BB2EF44EAA163B29C4A4587887A0FE4] - (.Microsoft Corporation - DFS Namespace Client Driver.) (.20/11/2010 - 10:26:32.) -- C:\Windows\system32\Drivers\DfsC.sys [102400]
[MD5.97BFED39B6B79EB12CDDBFEED51F56BB] - (.Microsoft Corporation - High Definition Audio Bus Driver.) (.20/11/2010 - 11:43:43.) -- C:\Windows\system32\Drivers\HDAudBus.sys [122368]
[MD5.FA55C73D4AFFA7EE23AC4BE53B4592D3] - (.Microsoft Corporation - Pilote de port i8042.) (.14/07/2009 - 00:19:57.) -- C:\Windows\system32\Drivers\i8042prt.sys [105472]
[MD5.AF9B39A7E7B6CAA203B3862582E9F2D0] - (.Microsoft Corporation - IP Network Address Translator.) (.14/07/2009 - 01:10:03.) -- C:\Windows\system32\Drivers\IpNat.sys [116224]
[MD5.A5D9106A73DC88564C825D317CAC68AC] - (.Microsoft Corporation - Windows NT SMB Minirdr.) (.27/04/2011 - 03:40:40.) -- C:\Windows\system32\Drivers\MRxSmb.sys [158208]
[MD5.09594D1089C523423B32A4229263F068] - (.Microsoft Corporation - MBT Transport driver.) (.20/11/2010 - 10:23:20.) -- C:\Windows\system32\Drivers\netBT.sys [261632]
[MD5.1A29A59A4C5BA6F8C85062A613B7E2B2] - (.Microsoft Corporation - Pilote du système de fichiers NT.) (.24/01/2014 - 03:37:55.) -- C:\Windows\system32\Drivers\ntfs.sys [1684928]
[MD5.0086431C29C35BE1DBC43F52CC273887] - (.Microsoft Corporation - Pilote de port parallèle.) (.14/07/2009 - 01:00:41.) -- C:\Windows\system32\Drivers\Parport.sys [97280]
[MD5.471815800AE33E6F1C32FB1B97C490CA] - (.Microsoft Corporation - RAS L2TP mini-port/call-manager driver.) (.20/11/2010 - 11:52:35.) -- C:\Windows\system32\Drivers\Rasl2tp.sys [129536]
[MD5.548260A7B8654E024DC30BF8A7C5BAA4] - (.Microsoft Corporation - SMB Transport driver.) (.14/07/2009 - 01:09:09.) -- C:\Windows\system32\Drivers\smb.sys [93184]
[MD5.70988118145F5F10EF24720B97F35F65] - (.Microsoft Corporation - TDI Translation Driver.) (.11/11/2014 - 02:46:26.) -- C:\Windows\system32\Drivers\tdx.sys [119296]
[MD5.0D08D2F3B3FF84E433346669B5E0F639] - (.Microsoft Corporation - Pilote de cliché instantané du volume.) (.20/11/2010 - 14:34:02.) -- C:\Windows\system32\Drivers\volsnap.sys [295808]
~ Generic Processes: Scanned in 00mn 02s
---\\ Etat des fichiers cachés (Caché/Total)
~ Mes images (My Pictures) : 1/3
~ Mes Favoris (My Favorites) : 1/23
~ Mes Documents (My Documents) : 1/269
~ Mon Bureau (My Desktop) : 8/14
~ Menu demarrer (Programs) : 1/38
~ Hidden Files: Scanned in 00mn 04s
---\\ Processus lancés
[MD5.37DEB76A2CF005841C4E45DE2B94D84F] - (.ASUS - AsScrPro.) -- C:\Windows\AsScrPro.exe [3058304] [PID.1436]
[MD5.57B4D34232852BFE4453BE571DF90D21] - (.CyberLink - CyberLink MediaLibray Service.) -- C:\Program Files (x86)\CyberLink\Power2Go\CLMLSvc.exe [103720] [PID.1912]
[MD5.868E3486E7EC522330344152A5535783] - (.ASUS - SmartLogon Application.) -- C:\Program Files (x86)\ASUS\SmartLogon\sensorsrv.exe [305720] [PID.2160]
[MD5.5BB1F77C8AF725A15EC9366498D275BB] - (.ASUS - ATKOSD2.) -- C:\Program Files (x86)\ASUS\ATK Package\ATKOSD2\ATKOSD2.exe [5732992] [PID.2176]
[MD5.D5C19842C2271327CA20511C30FFEED3] - (.Sonix Technology Co., Ltd. - CameraMonitor Application.) -- C:\Windows\vsnp2uvc.exe [909824] [PID.2496]
[MD5.A162B967A88BF374A81E01EF6E7A2655] - (.Avira Operations GmbH & Co. KG - Avira system tray application.) -- C:\Program Files (x86)\Avira\AntiVir Desktop\avgnt.exe [702768] [PID.2980]
[MD5.887CAA31048EB8ED09A0CBD0E6F46F09] - (.Oracle Corporation - Java Update Scheduler.) -- C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe [507776] [PID.3000]
[MD5.BA18CFAB98426BFA6D6EC7E5B1961ED0] - (.Avira Operations GmbH & Co. KG - Avira.) -- C:\Program Files (x86)\Avira\My Avira\Avira.OE.Systray.exe [126200] [PID.3008]
[MD5.89B52ECB4DF86F66100D218C16025EF1] - (.Glarysoft Ltd - Glary Utilities 5.) -- C:\Program Files (x86)\Glary Utilities 5\Integrator.exe [846624] [PID.3904]
[MD5.5F3587E344F2990B59C941FB405CAA0F] - (.Google Inc. - Google Chrome.) -- C:\Program Files (x86)\Google\Chrome\Application\chrome.exe [856904] [PID.2852]
[MD5.E0C58C3B1384100225BFAEE83E4221D4] - (.Emsi Software GmbH - Security Center.) -- C:\Program Files (x86)\Emsisoft Anti-Malware\a2start.exe [5543848] [PID.4460]
[MD5.711904AD15AC2DB5D90F7C5201FB8178] - (.Davy FREBOURG - Chronometre informatique.) -- C:\Program Files (x86)\Chronometre\Chronometre.exe [393216] [PID.1776]
[MD5.52F27003BA6A11C88BE9D9101127E2FA] - (.Microsoft Corporation - Microsoft Office Excel.) -- C:\Program Files (x86)\Microsoft Office\Office12\EXCEL.exe [18362032] [PID.3668]
[MD5.AFDF3BDDF90824B727A272A2715D34FB] - (.Nicolas Coolman - ZHPDiag.) -- C:\Program Files (x86)\ZHPDiag\ZHPDiag.exe [8154624] [PID.1992]
[MD5.18E5C2F937F9DEB8C282DF66A3761925] - (.ASUS - ASLDR Service.) -- C:\Program Files (x86)\ASUS\ATK Package\ATK Hotkey\ASLDRSrv.exe [84536] [PID.1240]
[MD5.DC893FAB5E18E383DC7147F37C8C0CA2] - (.ASUS - SmartLogon Application.) -- C:\Program Files (x86)\ASUS\SmartLogon\smartlogon.exe [428600] [PID.1356]
[MD5.7910158929571214A959D5A6D16DD9C0] - (.ASUS - GFNEXSrv.) -- C:\Program Files (x86)\ASUS\ATK Package\ATKGFNEX\GFNEXSrv.exe [96896] [PID.1384]
[MD5.C2700D35AA42311A32DF7EA09630B401] - (.Avira Operations GmbH & Co. KG - Antivirus Host Framework Service.) -- C:\Program Files (x86)\Avira\AntiVir Desktop\sched.exe [431920] [PID.1672]
[MD5.ADC420616C501B45D26C0FD3EF1E54E4] - (.ArcSoft Inc. - ArcSoft Connect Service.) -- C:\Program Files (x86)\Common Files\ArcSoft\Connection Service\Bin\ACService.exe [113152] [PID.1088]
[MD5.B1EA9681502EE57F87DB71D726288A5B] - (.Adobe Systems Incorporated - Adobe Acrobat Update Service.) -- C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [65192] [PID.1500]
[MD5.C2700D35AA42311A32DF7EA09630B401] - (.Avira Operations GmbH & Co. KG - Antivirus Host Framework Service.) -- C:\Program Files (x86)\Avira\AntiVir Desktop\avguard.exe [431920] [PID.1744]
[MD5.A6307F356D778E18A76E7783EF98C6AA] - (.Atheros - Atheros Coex Service Application.) -- C:\Program Files (x86)\Atheros\Ath_CoexAgent.exe [151552] [PID.1580]
[MD5.205E1B699FD3F2F9B036EEA2EC30C620] - (...) -- C:\Windows\SysWOW64\PnkBstrA.exe [76888] [PID.2440]
[MD5.6F77BBB8FC69D26132309EB4CE7A4E0E] - (.Avira Operations GmbH & Co. KG - Avira.OE.ServiceHost.) -- C:\Program Files (x86)\Avira\My Avira\Avira.OE.ServiceHost.exe [166192] [PID.2528]
[MD5.051A7A9C035BBAB779E2C96E65C32600] - (.Avira Operations GmbH & Co. KG - AntiVir WebGuard Service.) -- C:\Program Files (x86)\Avira\AntiVir Desktop\AVWEBGRD.exe [992560] [PID.3592]
[MD5.ECE5BAB5AA508C854E8E13B6091EA57C] - (.Emsi Software GmbH - Emsisoft Anti-Malware Service.) -- C:\Program Files (x86)\Emsisoft Anti-Malware\a2service.exe [2860800] [PID.5340]
~ Processes Running: Scanned in 00mn 02s
---\\ Google Chrome, Démarrage,Recherche,Extensions (G0,G1,G2)
C:\Users\Thomas\AppData\Local\Google\Chrome\User Data\Default\Preferences
---\\ Liste des dossiers d'extension Google Chrome
~ Google Lines Browser: 0 Scanned in 00mn 01s
---\\ Mozilla Firefox, Plugins,Demarrage,Recherche,Extensions (P2,M0,M1,M2,M3)
P2 - FPN: [HKLM] [@adobe.com/FlashPlayer] - (...) -- C:\Windows\system32\Macromed\Flash\NPSWF64_16_0_0_257.dll
P2 - FPN: [HKLM] [@Microsoft.com/NpCtrl,version=1.0] - (. Microsoft Corporation - 5.1.30514.0.) -- C:\Program Files\Microsoft Silverlight\5.1.30514.0\npctrl.dll
P2 - FPN: [HKCU] [@Skype Limited.com/Facebook Video Calling Plugin] - (...) -- C:\Users\Thomas\AppData\Local\Facebook\Video\Skype\npFacebookVideoCalling.dll (.not file.)
P2 - FPN: [HKCU] [@unity3d.com/UnityPlayer,version=1.0] - (.Unity Technologies ApS - Unity Player 4.3.4f1.) -- C:\Users\Thomas\AppData\LocalLow\Unity\WebPlayer\loader\npUnity3D32.dll
~ Firefox Browser: 4 Scanned in 00mn 00s
---\\ Internet Explorer, Démarrage,Recherche,URLSearchHook, Phishing (R0,R1,R3,R4)
R0 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = https://www.google.com/?gws_rd=ssl
R0 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = about:blank
R0 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Start Page = about:blank
R1 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = https://www.microsoft.com/fr-fr/
R1 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = https://www.msn.com/fr-fr/?cobrand=asus.msn.com&ocid=ASUDHP&pc=ASU2
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = about:blank
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = about:blank
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Extensions Off Page = about:noadd-ons
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Security Risk Page = about:securityrisk
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Search_URL = about:blank
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Search Page = about:blank
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Default_Page_URL = about:blank
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Default_Search_URL = about:blank
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Extensions Off Page = about:noadd-ons
R1 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Security Risk Page = about:securityrisk
R3 - URLSearchHook: Microsoft Url Search Hook [64Bits] - {CFBFAE00-17A6-11D0-99CB-00C04FD64497} . (.Microsoft Corporation - Navigateur Internet.) (11.00.9600.17496 (winblue_r5.141121-1500)) -- C:\Windows\SysWOW64\ieframe.dll
R4 - HKLM\SOFTWARE\Microsoft\Internet Explorer\PhishingFilter,EnabledV8 = 1
R4 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\PhishingFilter,EnabledV8 = 1
~ IE Browser: 18 Scanned in 00mn 00s
---\\ Internet Explorer, Proxy Management (R5)
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = <local>
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = no key
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyEnable = 0
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,MigrateProxy = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,EnableHttp1_1 = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,AutoConfigProxy = wininet.dll
~ Proxy management: Scanned in 00mn 00s
---\\ Analyse des lignes F0, F1, F2, F3 - IniFiles, Autoloading programs
F2 - REG:system.ini: USERINIT=C:\Windows\System32\Userinit.exe,
F2 - REG:system.ini: Shell=C:\Windows\explorer.exe
F2 - REG:system.ini: VMApplet=C:\Windows\System32\SystemPropertiesPerformance.exe
~ Keys: Scanned in 00mn 00s
---\\ Hosts file redirection (O1)
~ Le fichier hôte est sain (The hosts file is clean) (21)
~ Hosts File: Scanned in 00mn 00s
---\\ Browser Helper Objects de navigateur (O2)
O2 - BHO: AcroIEHelperStub [64Bits] - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} . (.Adobe Systems Incorporated - Adobe PDF Helper for Internet Explorer.) -- C:\Program Files (x86)\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
O2 - BHO: Java(tm) Plug-In SSV Helper [64Bits] - {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} . (.Oracle Corporation - Java(TM) Platform SE binary.) -- C:\Program Files (x86)\Java\jre1.8.0_25\bin\ssv.dll
O2 - BHO: IESpeakDoc [64Bits] - {8D10F6C4-0E01-4BD4-8601-11AC1FDF8126} . (.Atheros Commnucations - Bluetooth IE PlugIn.) -- C:\Program Files (x86)\Atheros\Bluetooth Suite\IEPlugIn.dll
O2 - BHO: Programme d'aide de l'Assistant de connexion Windows Live ID [64Bits] - {9030D464-4C02-4ABF-8ECC-5164760863C6} . (.Microsoft Corp. - Microsoft® Windows Live ID Login Helper.) -- C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: Windows Live Messenger Companion Helper [64Bits] - {9FDDE16B-836F-4806-AB1F-1455CBEFF289} . (.Microsoft Corporation - Windows Live Messenger Companion Core.) -- C:\Program Files (x86)\Windows Live\Companion\companioncore.dll
O2 - BHO: Java(tm) Plug-In 2 SSV Helper [64Bits] - {DBC80044-A445-435b-BC74-9C25C1C588A9} . (.Oracle Corporation - Java(TM) Platform SE binary.) -- C:\Program Files (x86)\Java\jre1.8.0_25\bin\jp2ssv.dll
~ BHO: 7 Scanned in 00mn 00s
---\\ Applications lancées au démarrage du système (O4)
O4 - HKLM\..\Run: [ASUS WebStorage] . (...) -- C:\Program Files (x86)\ASUS\ASUS WebStorage\SERVICE\AsusWSService.exe
O4 - HKLM\..\Run: [RtHDVBg] . (.Realtek Semiconductor - HD Audio Background Process.) -- C:\Program Files\Realtek\Audio\HDA\RAVBg64.exe
O4 - HKLM\..\Run: [AtherosBtStack] . (.Atheros Communications - Serveur Stack Bluetooth.) -- C:\Program Files (x86)\Atheros\Bluetooth Suite\BtvStack.exe
O4 - HKLM\..\Run: [AthBtTray] . (.Atheros Commnucations - Bluetooth Suite Common Rescource.) -- C:\Program Files (x86)\Atheros\Bluetooth Suite\AthBtTray.exe
O4 - HKLM\..\Run: [snp2uvc] . (.Sonix Technology Co., Ltd. - CameraMonitor Application.) -- C:\Windows\vsnp2uvc.exe
O4 - HKLM\..\Run: [IgfxTray] . (.Intel Corporation - igfxTray Module.) -- C:\Windows\system32\igfxtray.exe
O4 - HKLM\..\Run: [HotKeysCmds] . (.Intel Corporation - hkcmd Module.) -- C:\Windows\system32\hkcmd.exe
O4 - HKLM\..\Run: [Persistence] . (.Intel Corporation - persistence Module.) -- C:\Windows\system32\igfxpers.exe
O4 - HKCU\..\Run: [GUDelayStartup] . (.Glarysoft Ltd - Glary Utilities StartupManager.) -- C:\Program Files (x86)\Glary Utilities 5\StartupManager.exe
O4 - HKCU\..\Run: [CCleaner Monitoring] . (.Piriform Ltd - CCleaner.) -- C:\Program Files\CCleaner\CCleaner64.exe =>.Piriform Ltd
O4 - HKLM\..\Wow6432Node\Run: [avgnt] . (.Avira Operations GmbH & Co. KG - Avira system tray application.) -- C:\Program Files (x86)\Avira\AntiVir Desktop\avgnt.exe
O4 - HKLM\..\Wow6432Node\Run: [SunJavaUpdateSched] . (.Oracle Corporation - Java Update Scheduler.) -- C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe =>.Oracle Corporation
O4 - HKLM\..\Wow6432Node\Run: [Avira Systray] . (.Avira Operations GmbH & Co. KG - Avira.) -- C:\Program Files (x86)\Avira\My Avira\Avira.OE.Systray.exe
O4 - HKUS\S-1-5-19\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files (x86)\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] . (.Microsoft Corporation - Gadgets du Bureau Windows.) -- C:\Program Files (x86)\Windows Sidebar\Sidebar.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-19\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-20\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe =>.Microsoft Corporation
O4 - HKUS\S-1-5-21-3038434135-2178592342-654473034-1002\..\Run: [GUDelayStartup] . (.Glarysoft Ltd - Glary Utilities StartupManager.) -- C:\Program Files (x86)\Glary Utilities 5\StartupManager.exe
O4 - HKUS\S-1-5-21-3038434135-2178592342-654473034-1002\..\Run: [CCleaner Monitoring] . (.Piriform Ltd - CCleaner.) -- C:\Program Files\CCleaner\CCleaner64.exe =>.Piriform Ltd
~ Application: Scanned in 00mn 00s
---\\ Invisibilité de l'icône d'options IE dans le panneau de Configuration (O5)
O5 - control.ini: [HKLM\..\Control Panel] inetcpl.cpl=no
~ IE Control Panel: 1 Scanned in 00mn 00s
---\\ Boutons situés sur la barre d'outils principale d'Internet Explorer (O9)
O9 - Extra button: Send by Bluetooth to [64Bits] - {7815BE26-237D-41A8-A98F-F7BD75F71086} -- Clé orpheline
~ IE Extra Buttons: Scanned in 00mn 00s
---\\ Winsock hijacker (Layered Service Provider) (O10)
O10 - WLSP:\000000000001\Winsock LSP File . (.Microsoft Corporation - Network Location Awareness 2.) -- C:\Windows\system32\NLAapi.dll
O10 - WLSP:\000000000002\Winsock LSP File . (.Microsoft Corporation - Fournisseur Shim d'affectation de noms de messagerie.) -- C:\Windows\system32\napinsp.dll
O10 - WLSP:\000000000003\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000004\Winsock LSP File . (.Microsoft Corporation - Fournisseur d'espace de noms PNRP.) -- C:\Windows\system32\pnrpnsp.dll
O10 - WLSP:\000000000005\Winsock LSP File . (.Microsoft Corporation - Windows Sockets Helper DLL.) -- C:\Windows\system32\wshbth.dll
O10 - WLSP:\000000000006\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
O10 - WLSP:\000000000007\Winsock LSP File . (.Microsoft Corp. - Microsoft® Windows Live ID Namespace Provider.) -- C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WLIDNSP.dll =>.Microsoft Corporation
O10 - WLSP:\000000000008\Winsock LSP File . (.Microsoft Corporation - Fournisseur de service Sockets 2.0 de Microsoft Windows.) -- C:\Windows\system32\mswsock.dll =>.Microsoft Corporation
O10 - WLSP:\000000000009\Winsock LSP File . (.Microsoft Corporation - LDAP RnR Provider DLL.) -- C:\Windows\system32\winrnr.dll
~ Winsock: 9 Scanned in 00mn 00s
---\\ Modification Domaine/Adresses DNS (O17)
O17 - HKLM\System\CCS\Services\Tcpip\..\{5F712B5D-0E79-414A-8AEA-EDF890F8FD12}: DhcpNameServer = 192.168.1.1
O17 - HKLM\System\CCS\Services\Tcpip\..\{7433C9B4-3C0C-4D00-BFB1-07638D26EEB3}: DhcpNameServer = 192.168.1.1 192.168.1.1
O17 - HKLM\System\CS1\Services\Tcpip\..\{5F712B5D-0E79-414A-8AEA-EDF890F8FD12}: DhcpNameServer = 192.168.1.1
O17 - HKLM\System\CS1\Services\Tcpip\..\{7433C9B4-3C0C-4D00-BFB1-07638D26EEB3}: DhcpNameServer = 192.168.1.1 192.168.1.1
O17 - HKLM\System\CS2\Services\Tcpip\..\{5F712B5D-0E79-414A-8AEA-EDF890F8FD12}: DhcpNameServer = 192.168.1.1
O17 - HKLM\System\CS2\Services\Tcpip\..\{7433C9B4-3C0C-4D00-BFB1-07638D26EEB3}: DhcpNameServer = 192.168.1.1 192.168.1.1
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = 192.168.1.1 192.168.1.1
~ Domain: Scanned in 00mn 00s
---\\ Protocole additionnel (O18)
O18 - Handler: wlpg [64Bits] - {E43EF6CD-A37A-4A9B-9E6F-83F89B8E6324} . (...) --
O18 - Filter: text/xml [64Bits] - {807563E5-5146-11D5-A672-00B0D022E945} . (.Microsoft Corporation - Microsoft Office XML MIME Filter.) -- C:\Program Files\Common Files\Microsoft Shared\OFFICE12\MSOXMLMF.dll =>.Microsoft Corporation
~ Protocole Additionnel: Scanned in 00mn 00s
---\\ Valeur de Registre AppInit_DLLs et sous-clés Winlogon Notify (autorun) (O20)
O20 - Winlogon Notify: igfxcui . (.Intel Corporation - igfxdev Module.) -- C:\Windows\System32\igfxdev.dll
~ Winlogon: Scanned in 00mn 00s
---\\ Valeur de Registre AppInit_DLLs et sous-clés Winlogon Notify (autorun) (O20)
O20 - AppInit_DLLs: . (.NVIDIA Corporation - NVIDIA shim initialization dll, Version 310.) - C:\Windows\system32\nvinitx.dll
~ AppInit DLL: Scanned in 00mn 00s
---\\ Clé de Registre autorun ShellServiceObjectDelayLoad (SSO/SSODL) (O21)
O21 - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} - CLSID or File not found.
~ SSODL: 1 Scanned in 00mn 00s
---\\ Liste des services NT non Microsoft et non désactivés (O23)
O23 - Service: ArcSoft Connect Daemon (ACDaemon) . (.ArcSoft Inc. - ArcSoft Connect Service.) - C:\Program Files (x86)\Common Files\ArcSoft\Connection Service\Bin\ACService.exe
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) . (.Adobe Systems Incorporated - Adobe Acrobat Update Service.) - C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: AFBAgent (AFBAgent) . (.ASUSTeK Computer Inc. - ASUS FastBoot.) - C:\Windows\system32\FBAgent.exe
O23 - Service: Avira Planificateur (AntiVirSchedulerService) . (.Avira Operations GmbH & Co. KG - Antivirus Host Framework Service.) - C:\Program Files (x86)\Avira\AntiVir Desktop\sched.exe
O23 - Service: Avira Protection temps réel (AntiVirService) . (.Avira Operations GmbH & Co. KG - Antivirus Host Framework Service.) - C:\Program Files (x86)\Avira\AntiVir Desktop\avguard.exe
O23 - Service: Avira Protection Web (AntiVirWebService) . (.Avira Operations GmbH & Co. KG - AntiVir WebGuard Service.) - C:\Program Files (x86)\Avira\AntiVir Desktop\AVWEBGRD.exe
O23 - Service: ASLDR Service (ASLDRService) . (.ASUS - ASLDR Service.) - C:\Program Files (x86)\ASUS\ATK Package\ATK Hotkey\ASLDRSrv.exe
O23 - Service: Atheros Bt&Wlan Coex Agent (Atheros Bt&Wlan Coex Agent) . (.Atheros - Atheros Coex Service Application.) - C:\Program Files (x86)\Atheros\Ath_CoexAgent.exe
O23 - Service: AtherosSvc (AtherosSvc) . (.Atheros Commnucations - AdminService Application.) - C:\Program Files (x86)\Atheros\Bluetooth Suite\adminservice.exe
O23 - Service: ATKGFNEX Service (ATKGFNEXSrv) . (.ASUS - GFNEXSrv.) - C:\Program Files (x86)\ASUS\ATK Package\ATKGFNEX\GFNEXSrv.exe
O23 - Service: Avira Service Host (Avira.OE.ServiceHost) . (.Avira Operations GmbH & Co. KG - Avira.OE.ServiceHost.) - C:\Program Files (x86)\Avira\My Avira\Avira.OE.ServiceHost.exe
O23 - Service: Google Update Service (gupdate) (gupdate) . (.Google Inc. - Programme d'installation de Google.) - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe =>.Google Inc
O23 - Service: NVIDIA Display Driver Service (NVSvc) . (.NVIDIA Corporation - NVIDIA Driver Helper Service, Version 310.9.) - C:\Windows\System32\nvvsvc.exe
O23 - Service: NVIDIA Update Service Daemon (nvUpdatusService) . (.NVIDIA Corporation - NVIDIA Settings Update Manager.) - C:\Program Files (x86)\NVIDIA Corporation\NVIDIA Update Core\daemonu.exe
O23 - Service: Intel(R) Turbo Boost Technology Monitor (TurboBoost) . (.Intel(R) Corporation - Turbo Boost Monitor Service.) - C:\Program Files\Intel\TurboBoost\TurboBoost.exe
~ Services: 15 Scanned in 00mn 04s
---\\ Enumération Active Desktop & MHTML Editor (O24)
O24 - Default MHTML Editor: Last - .(...) - (.not file.)
~ Desktop Component: 4 Scanned in 00mn 00s
---\\ Enumère les données de BootExecute (BEX) (O34)
O34 - HKLM BootExecute: (autocheck autochk * ) - File not found
~ BEX: 1 Scanned in 00mn 00s
---\\ Tâches planifiées en automatique (O39)
[MD5.3ACABCA6A8DB71B7F19C8A7523AE1846] [APT] [ACMON] (.ASUS.) -- C:\Program Files (x86)\ASUS\Splendid\ACMON.exe [691328]
[MD5.CB1719E3EA00A0C114A8AD2655F43754] [APT] [Adobe Flash Player Updater] (.Adobe Systems Incorporated.) -- C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe [267440]
[MD5.180E79B16063F7DFD005DC021AC543C6] [APT] [ASUS P4G] (.ASUS.) -- C:\Program Files\P4G\BatteryLife.exe [977024]
[MD5.868E3486E7EC522330344152A5535783] [APT] [ASUS SmartLogon Console Sensor] (.ASUS.) -- C:\Program Files (x86)\ASUS\SmartLogon\sensorsrv.exe [305720]
[MD5.5BB1F77C8AF725A15EC9366498D275BB] [APT] [ATKOSD2] (.ASUS.) -- C:\Program Files (x86)\ASUS\ATK Package\ATKOSD2\ATKOSD2.exe [5732992]
[MD5.2E4EE47FBD9BB663A5220DBC38579986] [APT] [CCleanerSkipUAC] (.Piriform Ltd.) -- C:\Program Files\CCleaner\CCleaner.exe [5282584]
[MD5.C2168D98651841E2F6D7B08F3383A73C] [APT] [GlaryInitialize 5] (.Glarysoft Ltd.) -- C:\Program Files (x86)\Glary Utilities 5\Initialize.exe [104224]
[MD5.51508F0C2476177E50C31B0BBFBF1BDB] [APT] [GoogleUpdateTaskMachineCore] (.Google Inc..) -- C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [107912]
[MD5.51508F0C2476177E50C31B0BBFBF1BDB] [APT] [GoogleUpdateTaskMachineUA] (.Google Inc..) -- C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [107912]
[MD5.00000000000000000000000000000000] [APT] [{1FEF89C8-8D51-49E3-87D7-01E139E188A9}] (...) -- E:\SETUP.exe (.not file.) [0]
[MD5.C155A13687144076286989EF078112C2] [APT] [{5EFEA51E-D81C-46FD-BEF2-12068033AA47}] (.Nicolas Coolman.) -- C:\Program Files (x86)\ZHPDiag\ZHPFix\ZHPhep.exe [1917440]
[MD5.5F3587E344F2990B59C941FB405CAA0F] [APT] [{71FC60CF-659D-4154-91B9-E4AF373BD74A}] (.Google Inc..) -- c:\program files (x86)\google\chrome\application\chrome.exe [856904]
[MD5.00000000000000000000000000000000] [APT] [{9EC36DE6-F277-497F-A362-37F163AE8FB2}] (...) -- C:\Users\Thomas\Downloads\Autodesk_3ds_Max_2012_French_Win_32-64bit.exe (.not file.) [0]
[MD5.5F3587E344F2990B59C941FB405CAA0F] [APT] [{B07BEEDD-F69C-427C-A78A-59AF5787FB6E}] (.Google Inc..) -- c:\program files (x86)\google\chrome\application\chrome.exe [856904]
[MD5.00000000000000000000000000000000] [APT] [{DCF8928A-610B-4959-98BE-86556A2AF3DC}] (...) -- E:\DINSTALL.exe (.not file.) [0]
[MD5.00000000000000000000000000000000] [APT] [{F7D26770-8C53-4469-9C70-378A315EC1BA}] (...) -- G:\Ordinateur\Office 2007 pro\SETUP.exe (.not file.) [0]
O39 - APT: Adobe Flash Player Updater - (.Adobe Systems Incorporated.) -- C:\Windows\Tasks\Adobe Flash Player Updater.job [1002]
O39 - APT: Adobe Flash Player Updater - (.Adobe Systems Incorporated.) -- C:\Windows\System32\Tasks\Adobe Flash Player Updater [1002]
O39 - APT: GlaryInitialize 5 - (.Glarysoft Ltd.) -- C:\Windows\Tasks\GlaryInitialize 5.job [334]
O39 - APT: GlaryInitialize 5 - (.Glarysoft Ltd.) -- C:\Windows\System32\Tasks\GlaryInitialize 5 [334]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineCore.job [1066]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineCore [1066]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\Tasks\GoogleUpdateTaskMachineUA.job [1070]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\Windows\System32\Tasks\GoogleUpdateTaskMachineUA [1070]
~ Scheduled Task: 21 Scanned in 00mn 15s
---\\ Composants installés (ActiveSetup Installed Components) (O40)
O40 - ASIC: Microsoft Windows Media Player [64Bits] - >{22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Microsoft Windows Media Player 12.0 [64Bits] - {22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Windows Media Player Extension.) -- C:\Windows\SysWOW64\wmpdxm.dll =>.Microsoft Corporation
O40 - ASIC: Themes Setup [64Bits] - {2C7339CF-2B09-4501-B3F3-F3508C9228ED} . (.Microsoft Corporation - API Windows Theme.) -- C:\Windows\System32\themeui.dll
O40 - ASIC: Internet Explorer [64Bits] - {2D46B6DC-2207-486B-B523-A557E6D54B47} . (.Microsoft Corporation - Interpréteur de commandes Windows.) -- C:\Windows\system32\cmd.exe =>.Microsoft Corporation
O40 - ASIC: Microsoft Windows [64Bits] - {44BBA840-CC51-11CF-AAFA-00AA00B6015C} . (.Microsoft Corporation - Windows Mail.) -- C:\Program Files (x86)\Windows Mail\WinMail.exe =>.Microsoft Corporation
O40 - ASIC: Browsing Enhancements [64Bits] - {630b1da0-b465-11d1-9948-00c04f98bbc9} . (.Microsoft Corporation - Extension Shell dossier FTP Microsoft Internet Explorer..) -- C:\Windows\System32\msieftp.dll
O40 - ASIC: Microsoft Windows Media Player [64Bits] - {6BF52A52-394A-11d3-B153-00C04F79FAA6} . (.Microsoft Corporation - Ressources du Lecteur Windows Media.) -- C:\Windows\System32\wmploc.dll =>.Microsoft Corporation
O40 - ASIC: Windows Desktop Update [64Bits] - {89820200-ECBD-11cf-8B85-00AA005B4340} . (.Microsoft Corporation - DLL commune du shell Windows.) -- C:\Windows\System32\shell32.dll
O40 - ASIC: Web Platform Customizations [64Bits] - {89820200-ECBD-11cf-8B85-00AA005B4383} . (.Microsoft Corporation - Utilitaire d'initialisation d'Internet Explorer par utilisateur.) -- C:\Windows\System32\ie4uinit.exe
O40 - ASIC: (no name) [64Bits] - {89B4C1CD-B018-4511-B0A1-5476DBF70820} . (.Microsoft Corporation - Microsoft .NET IE SECURITY REGISTRATION.) -- C:\Windows\system32\mscories.dll
~ Active Setup: 10 Scanned in 00mn 01s
---\\ Pilotes lancés au démarrage du système (O41)
O41 - Driver: C:\Windows\System32\drivers\afd.sys (AFD) . (.Microsoft Corporation - Ancillary Function Driver for WinSock.) - C:\Windows\system32\drivers\afd.sys
O41 - Driver: (ATKWMIACPIIO) . (.ASUS - ATK WMIACPI Utility.) - C:\Program Files (x86)\ASUS\ATK Package\ATK WMIACPI\atkwmiacpi64.sys
O41 - Driver: (avipbb) . (.Avira Operations GmbH & Co. KG - Avira Driver for Security Enhancement.) - C:\Windows\System32\DRIVERS\avipbb.sys
O41 - Driver: (avkmgr) . (.Avira Operations GmbH & Co. KG - Avira Manager Driver.) - C:\Windows\System32\DRIVERS\avkmgr.sys
O41 - Driver: (blbdrive) . (.Microsoft Corporation - BLB Drive Driver.) - C:\Windows\System32\DRIVERS\blbdrive.sys
O41 - Driver: (cdrom) . (.Microsoft Corporation - SCSI CD-ROM Driver.) - C:\Windows\System32\DRIVERS\cdrom.sys
O41 - Driver: C:\Windows\System32\drivers\dfsc.sys (DfsC) . (.Microsoft Corporation - DFS Namespace Client Driver.) - C:\Windows\System32\Drivers\dfsc.sys
O41 - Driver: C:\Windows\System32\drivers\discache.sys (discache) . (.Microsoft Corporation - System Indexer/Cache Driver.) - C:\Windows\System32\drivers\discache.sys
O41 - Driver: (dtsoftbus01) . (.DT Soft Ltd - DAEMON Tools Virtual Bus Driver.) - C:\Windows\System32\DRIVERS\dtsoftbus01.sys
O41 - Driver: (GUBootStartup) . (.Glarysoft Ltd - The driver for the Startup Manager tool.) - C:\Windows\system32\drivers\GUBootStartup.sys
O41 - Driver: (mssmbios) . (.Microsoft Corporation - System Management BIOS Driver.) - C:\Windows\system32\drivers\mssmbios.sys
O41 - Driver: (NetBIOS) . (.Microsoft Corporation - NetBIOS interface driver.) - C:\Windows\System32\DRIVERS\netbios.sys
O41 - Driver: C:\Windows\System32\drivers\netbt.sys (NetBT) . (.Microsoft Corporation - MBT Transport driver.) - C:\Windows\System32\DRIVERS\netbt.sys
O41 - Driver: C:\Windows\System32\drivers\nsiproxy.sys (nsiproxy) . (.Microsoft Corporation - NSI Proxy.) - C:\Windows\System32\drivers\nsiproxy.sys
O41 - Driver: C:\Windows\System32\drivers\pacer.sys (Psched) . (.Microsoft Corporation - Planificateur de paquets QoS.) - C:\Windows\System32\DRIVERS\pacer.sys
O41 - Driver: C:\Windows\System32\wkssvc.dll (rdbss) . (.Microsoft Corporation - Pilote du sous-système de mise en mémoire t.) - C:\Windows\System32\DRIVERS\rdbss.sys
O41 - Driver: C:\Windows\System32\DRIVERS\RDPCDD.sys (RDPCDD) . (.Microsoft Corporation - RDP Miniport.) - C:\Windows\System32\DRIVERS\RDPCDD.sys
O41 - Driver: C:\Windows\System32\drivers\RDPENCDD.sys (RDPENCDD) . (.Microsoft Corporation - RDP Encoder Miniport.) - C:\Windows\System32\drivers\rdpencdd.sys
O41 - Driver: C:\Windows\System32\drivers\RdpRefMp.sys (RDPREFMP) . (.Microsoft Corporation - RDP Reflector Driver Miniport.) - C:\Windows\System32\drivers\rdprefmp.sys
O41 - Driver: C:\Windows\System32\tcpipcfg.dll (tdx) . (.Microsoft Corporation - TDI Translation Driver.) - C:\Windows\System32\DRIVERS\tdx.sys
O41 - Driver: (TermDD) . (.Microsoft Corporation - Remote Desktop Server Driver.) - C:\Windows\system32\drivers\termdd.sys
O41 - Driver: (VgaSave) . (.Microsoft Corporation - VGA/Super VGA Video Driver.) - C:\Windows\system32\drivers\vga.sys
O41 - Driver: (vwififlt) . (.Microsoft Corporation - Virtual WiFi Filter Driver.) - C:\Windows\System32\DRIVERS\vwififlt.sys
O41 - Driver: C:\Windows\System32\rascfg.dll (Wanarpv6) . (.Microsoft Corporation - MS Remote Access and Routing ARP Driver.) - C:\Windows\System32\DRIVERS\wanarp.sys
O41 - Driver: (WfpLwf) . (.Microsoft Corporation - WFP NDIS 6.20 Lightweight Filter Driver.) - C:\Windows\System32\DRIVERS\wfplwf.sys
~ Drivers: 75 Scanned in 00mn 01s
---\\ Logiciels installés (O42)
O42 - Logiciel: ASUS AI Recovery - (.ASUS.) [HKLM][64Bits] -- {38253529-D97D-4901-AE53-5CC9736D3A2E}
O42 - Logiciel: ASUS FancyStart - (.ASUSTeK Computer Inc..) [HKLM][64Bits] -- {2B81872B-A054-48DA-BE3B-FA5C164C303A}
O42 - Logiciel: ASUS K3 Series ScreenSaver - (.ASUS.) [HKLM][64Bits] -- ASUS K3 Series ScreenSaver
O42 - Logiciel: ASUS LifeFrame3 - (.ASUS.) [HKLM][64Bits] -- {1DBD1F12-ED93-49C0-A7CC-56CBDE488158}
O42 - Logiciel: ASUS Power4Gear Hybrid - (.ASUS.) [HKLM][64Bits] -- {9B6239BF-4E85-4590-8D72-51E30DB1A9AA}
O42 - Logiciel: ASUS SmartLogon - (.ASUS.) [HKLM][64Bits] -- {64452561-169F-4A36-A2FF-B5E118EC65F5}
O42 - Logiciel: ASUS Splendid Video Enhancement Technology - (.ASUS.) [HKLM][64Bits] -- {0969AF05-4FF6-4C00-9406-43599238DE0D}
O42 - Logiciel: ASUS Virtual Camera - (.asus.) [HKLM][64Bits] -- {EC8BD21F-0CA0-4BBF-97D9-4A52B30041A1}
O42 - Logiciel: ASUS WebStorage - (.eCareme Technologies, Inc..) [HKLM][64Bits] -- ASUS WebStorage
O42 - Logiciel: ATK Package - (.ASUS.) [HKLM][64Bits] -- {AB5C933E-5C7D-4D30-B314-9C83A49B94BE}
O42 - Logiciel: Adobe Flash Player 16 NPAPI - (.Adobe Systems Incorporated.) [HKLM][64Bits] -- Adobe Flash Player NPAPI
O42 - Logiciel: Adobe Reader XI - (.Adobe Systems Incorporated.) [HKLM][64Bits] -- {AC76BA86-7AD7-1033-7B44-AB0000000001}
O42 - Logiciel: ArcSoft WebCam Companion 3 - (.ArcSoft.) [HKLM][64Bits] -- {55FB8585-9F5F-482E-BDE3-57F338C1DE97}
O42 - Logiciel: AsusVibe2.0 - (.ASUSTEK.) [HKLM][64Bits] -- Asus Vibe2.0
O42 - Logiciel: Atheros WLAN and Bluetooth Client Installation Program - (.Atheros.) [HKLM][64Bits] -- {28006915-2739-4EBE-B5E8-49B25D32EB33}
O42 - Logiciel: Avira Free Antivirus v14.0.7.468 - (.Avira.) [HKLM][64Bits] -- Avira AntiVir Desktop
O42 - Logiciel: Avira v1.1.27.25527 - (.Avira Operations & Co. KG.) [HKLM][64Bits] -- {21388E37-9EC5-4549-95CA-95D9B2D327A4}
O42 - Logiciel: Avira v1.1.27.25527 - (.Avira Operations & Co. KG.) [HKLM][64Bits] -- {e7c7c227-b742-4878-9425-f09bbf9951db}
O42 - Logiciel: Battlefield 2(TM) - (...) [HKLM][64Bits] -- {04858915-9F49-4B2A-AED4-DC49A7DE6A7B}
O42 - Logiciel: Battlefield 3(TM) - (.Electronic Arts.) [HKLM][64Bits] -- {76285C16-411A-488A-BCE3-C83CB933D8CF}
O42 - Logiciel: Battlefield: Bad Company(TM) 2 - (.Electronic Arts.) [HKLM][64Bits] -- {3AC8457C-0385-4BEA-A959-E095F05D6D67}
O42 - Logiciel: CCleaner - (.Piriform.) [HKLM][64Bits] -- CCleaner
O42 - Logiciel: Chronometre - (...) [HKLM][64Bits] -- ST6UNST #1
O42 - Logiciel: Citrix XenApp Web Plugin - (.Citrix Systems, Inc..) [HKLM][64Bits] -- {EBFEEB3F-3E3B-4725-A4E0-376144CE4F76}
O42 - Logiciel: Complemento Messenger - (.Microsoft Corporation.) [HKLM][64Bits] -- {3A09ED0F-8DDF-47BB-B53D-841AB9D1D3A7}
O42 - Logiciel: Complément Messenger - (.Microsoft Corporation.) [HKLM][64Bits] -- {6E5324C1-84FC-4F76-9A3A-C65E07F80EE6}
O42 - Logiciel: Composite 2012 64-bit - (.Autodesk.) [HKLM][64Bits] -- {EA234BC3-39FE-4734-B72F-076086889F6D}
O42 - Logiciel: CyberLink LabelPrint - (.CyberLink Corp..) [HKLM][64Bits] -- InstallShield_{C59C179C-668D-49A9-B6EA-0121CCFC1243}
O42 - Logiciel: CyberLink LabelPrint - (.CyberLink Corp..) [HKLM][64Bits] -- {C59C179C-668D-49A9-B6EA-0121CCFC1243}
O42 - Logiciel: CyberLink Power2Go - (.CyberLink Corp..) [HKLM][64Bits] -- InstallShield_{40BF1E83-20EB-11D8-97C5-0009C5020658}
O42 - Logiciel: CyberLink Power2Go - (.CyberLink Corp..) [HKLM][64Bits] -- {40BF1E83-20EB-11D8-97C5-0009C5020658}
O42 - Logiciel: D3DX10 - (.Microsoft.) [HKLM][64Bits] -- {E09C4DB7-630C-4F06-A631-8EA7239923AF}
O42 - Logiciel: DAEMON Tools Lite - (.DT Soft Ltd.) [HKLM][64Bits] -- DAEMON Tools Lite =>.DT Soft Ltd
O42 - Logiciel: ESN Sonar - (.ESN Social Software AB.) [HKLM][64Bits] -- ESN Sonar-0.70.4
O42 - Logiciel: ETDWare PS/2-X64 8.0.5.0_WHQL - (.ELAN Microelectronic Corp..) [HKLM][64Bits] -- Elantech
O42 - Logiciel: Emsisoft Anti-Malware 5.1 - (.Emsi Software GmbH.) [HKLM][64Bits] -- Emsisoft Anti-Malware_is1
O42 - Logiciel: Facebook Video Calling 1.2.0.287 - (.Skype Limited.) [HKLM][64Bits] -- {B92C5909-1D37-4C51-8397-A28BB28E5DC3}
O42 - Logiciel: Fast Boot - (.ASUS.) [HKLM][64Bits] -- {13F4A7F3-EABC-4261-AF6B-1317777F0755}
O42 - Logiciel: Glary Utilities 5.16 - (.Glarysoft Ltd.) [HKLM][64Bits] -- Glary Utilities 5
O42 - Logiciel: Google Chrome - (.Google Inc..) [HKLM][64Bits] -- Google Chrome
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM][64Bits] -- {A92DAB39-4E2C-4304-9AB6-BC44E68B55E2}
O42 - Logiciel: Intel(R) Control Center - (.Intel Corporation.) [HKLM][64Bits] -- {F8A9085D-4C7A-41a9-8A77-C8998A96C421}
O42 - Logiciel: Intel(R) Processor Graphics - (.Intel Corporation.) [HKLM][64Bits] -- {F0E3AD40-2BBD-4360-9C76-B9AC9A5886EA}
O42 - Logiciel: Intel(R) Turbo Boost Technology Monitor - (.Intel.) [HKLM][64Bits] -- {39F4C6F9-618A-4E5B-8FB2-6BD661174E32}
O42 - Logiciel: Java 8 Update 25 - (.Oracle Corporation.) [HKLM][64Bits] -- {26A24AE4-039D-4CA4-87B4-2F83218025F0}
O42 - Logiciel: Junk Mail filter update - (.Microsoft Corporation.) [HKLM][64Bits] -- {1F6AB0E7-8CDD-4B93-8A23-AA9EB2FEFCE4}
O42 - Logiciel: MSVCRT - (.Microsoft.) [HKLM][64Bits] -- {8DD46C6A-0056-4FEC-B70A-28BB16A1F11F}
O42 - Logiciel: MSVCRT_amd64 - (.Microsoft.) [HKLM][64Bits] -- {D0B44725-3666-492D-BEF6-587A14BD9BD9}
O42 - Logiciel: MSXML 4.0 SP3 Parser (KB2721691) - (.Microsoft Corporation.) [HKLM][64Bits] -- {355B5AC0-CEEE-42C5-AD4D-7F3CFD806C36}
O42 - Logiciel: MSXML 4.0 SP3 Parser (KB2758694) - (.Microsoft Corporation.) [HKLM][64Bits] -- {1D95BA90-F4F8-47EC-A882-441C99D30C1E}
O42 - Logiciel: MSXML 4.0 SP3 Parser (KB973685) - (.Microsoft Corporation.) [HKLM][64Bits] -- {859DFA95-E4A6-48CD-B88E-A3E483E89B44}
O42 - Logiciel: Malwarebytes Anti-Malware version 2.0.2.1012 - (.Malwarebytes Corporation.) [HKLM][64Bits] -- Malwarebytes Anti-Malware_is1
O42 - Logiciel: Media Go - (.Sony.) [HKLM][64Bits] -- {0F895695-33CC-4203-9C47-25EF2AC9441C}
O42 - Logiciel: Mesh Runtime - (.Microsoft Corporation.) [HKLM][64Bits] -- {8C6D6116-B724-4810-8F2D-D047E6B7D68E}
O42 - Logiciel: Messenger Companion - (.Microsoft Corporation.) [HKLM][64Bits] -- {0481A2EA-DA1D-4D10-A7C3-F8237948F6B5}
O42 - Logiciel: Messenger Companion - (.Microsoft Corporation.) [HKLM][64Bits] -- {50816F92-1652-4A7C-B9BC-48F682742C4B}
O42 - Logiciel: Messenger Companion - (.Microsoft Corporation.) [HKLM][64Bits] -- {8142D25E-028A-4563-86ED-5755783C8029}
O42 - Logiciel: Messenger Companion - (.Microsoft Corporation.) [HKLM][64Bits] -- {939C80FA-96C9-44A6-B318-8E7D8BD8481B}
O42 - Logiciel: Messenger Companion - (.Microsoft Corporation.) [HKLM][64Bits] -- {96403552-88D1-429F-9C92-388B814B885E}
O42 - Logiciel: Messenger Companion - (.Microsoft Corporation.) [HKLM][64Bits] -- {C7DAD22D-29D4-438F-B986-03B9ED582EA4}
O42 - Logiciel: Messenger ???? - (.Microsoft Corporation.) [HKLM][64Bits] -- {CF088261-BC81-4FB9-9BA0-7B5B9602D01A}
O42 - Logiciel: Microsoft Silverlight - (.Microsoft Corporation.) [HKLM][64Bits] -- {89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}
O42 - Logiciel: Microsoft Text-to-Speech Engine 4.0 (English) - (...) [HKLM][64Bits] -- MSTTS
O42 - Logiciel: Mises à jour NVIDIA 1.11.3 - (.NVIDIA Corporation.) [HKLM][64Bits] -- {B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.Update
O42 - Logiciel: MonAlbumPhoto - (.MonAlbumPhoto.) [HKLM][64Bits] -- MonAlbumPhoto_is1
O42 - Logiciel: NVIDIA Logiciel système PhysX 9.12.1031 - (.NVIDIA Corporation.) [HKLM][64Bits] -- {B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.PhysX
O42 - Logiciel: NVIDIA PhysX - (.NVIDIA Corporation.) [HKLM][64Bits] -- {8B922CF8-8A6C-41CE-A858-F1755D7F5D29}
O42 - Logiciel: NVIDIA Pilote graphique 310.90 - (.NVIDIA Corporation.) [HKLM][64Bits] -- {B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.Driver
O42 - Logiciel: Origin - (.Electronic Arts, Inc..) [HKLM][64Bits] -- Origin
O42 - Logiciel: PunkBuster Services - (.Even Balance, Inc..) [HKLM][64Bits] -- PunkBusterSvc
O42 - Logiciel: QuickTime - (.Apple Inc..) [HKLM][64Bits] -- {57752979-A1C9-4C02-856B-FBB27AC4E02C}
O42 - Logiciel: Realtek Ethernet Controller Driver For Windows 7 - (.Realtek.) [HKLM][64Bits] -- {8833FFB6-5B0C-4764-81AA-06DFEED9A476}
O42 - Logiciel: Realtek High Definition Audio Driver - (.Realtek Semiconductor Corp..) [HKLM][64Bits] -- {F132AF7F-7BCA-4EDE-8A7C-958108FE7DBC}
O42 - Logiciel: Realtek USB 2.0 Reader Driver - (.Realtek Semiconductor Corp..) [HKLM][64Bits] -- {62BBB2F0-E220-4821-A564-730807D2C34D}
O42 - Logiciel: Skype(TM) 6.14 - (.Skype Technologies S.A..) [HKLM][64Bits] -- {7A3C7E05-EE37-47D6-99E1-2EB05A3DA3F7}
O42 - Logiciel: Sonic Focus - (.Virage Logic, Corp..) [HKLM][64Bits] -- {09BCB9CE-964B-4BDA-AE46-B5A0ABEF1D3F}
O42 - Logiciel: USB2.0 UVC VGA WebCam - (.Sonix.) [HKLM][64Bits] -- USB2.0 UVC VGA WebCam
O42 - Logiciel: Unity Web Player - (.Unity Technologies ApS.) [HKCU][64Bits] -- UnityWebPlayer
O42 - Logiciel: VLC media player 1.1.9 - (.VideoLAN.) [HKLM][64Bits] -- VLC media player =>.VideoLAN
O42 - Logiciel: Visual C++ 2008 x86 Runtime - (v9.0.30729) - (.Microsoft Corporation.) [HKLM][64Bits] -- {F333A33D-125C-32A2-8DCE-5C5D14231E27}
O42 - Logiciel: Visual C++ 2008 x86 Runtime - v9.0.30729.01 - (.Microsoft Corporation.) [HKLM][64Bits] -- {F333A33D-125C-32A2-8DCE-5C5D14231E27}.vc_x86runtime_30729_01
O42 - Logiciel: WinFlash - (.ASUS.) [HKLM][64Bits] -- {8F21291E-0444-4B1D-B9F9-4370A73E346D}
O42 - Logiciel: WinRAR 4.20 (32-bit) - (.win.rar GmbH.) [HKLM][64Bits] -- WinRAR archiver
O42 - Logiciel: Wireless Console 3 - (.ASUS.) [HKLM][64Bits] -- {20FDF948-C8ED-4543-A539-F7F4AEF5AFA2}
O42 - Logiciel: syncables desktop SE - (.syncables.) [HKLM][64Bits] -- {341697D8-9923-445E-B42A-529E5A99CB7A}
O42 - Logiciel: µTorrent - (.BitTorrent Inc..) [HKLM][64Bits] -- uTorrent =>P2P.BitTorrent
O42 - Logiciel: ????? Messenger - (.Microsoft Corporation.) [HKLM][64Bits] -- {AB5977C5-11AE-4003-BA7D-261C48F2BC35}
~ Logic: 40 Scanned in 00mn 00s
---\\ HKCU & HKLM Software Keys
[HKCU\Software\ASUS]
[HKCU\Software\ATK0100]
[HKCU\Software\AVS4YOU]
[HKCU\Software\Adobe]
[HKCU\Software\Alsoft]
[HKCU\Software\AppDataLow\Software\JavaSoft]
[HKCU\Software\AppDataLow\Software\Unity]
[HKCU\Software\AppDataLow]
[HKCU\Software\Apple Computer, Inc.]
[HKCU\Software\ArcSoft]
[HKCU\Software\Atheros]
[HKCU\Software\Autodesk]
[HKCU\Software\AviraSpeedup]
[HKCU\Software\Avira]
[HKCU\Software\BitTorrent] =>P2P.BitTorrent
[HKCU\Software\CDDB]
[HKCU\Software\Citrix]
[HKCU\Software\Classes]
[HKCU\Software\Clients]
[HKCU\Software\CyberLink]
[HKCU\Software\DT Soft]
[HKCU\Software\Datastead]
[HKCU\Software\EA Games]
[HKCU\Software\ECAREME]
[HKCU\Software\Elantech]
[HKCU\Software\Glarysoft]
[HKCU\Software\Google]
[HKCU\Software\HookNetwork]
[HKCU\Software\IM Providers]
[HKCU\Software\Intel]
[HKCU\Software\JavaSoft]
[HKCU\Software\Macromedia]
[HKCU\Software\Malwarebytes' Anti-Malware]
[HKCU\Software\Marseillesoft]
[HKCU\Software\Minuterie]
[HKCU\Software\MozillaPlugins]
[HKCU\Software\NVIDIA Corporation]
[HKCU\Software\Netscape]
[HKCU\Software\ODBC]
[HKCU\Software\Piriform]
[HKCU\Software\Policies]
[HKCU\Software\RealNetworks]
[HKCU\Software\Realtek]
[HKCU\Software\Safer Networking Limited]
[HKCU\Software\SecuROM]
[HKCU\Software\SkypeRS]
[HKCU\Software\Skype]
[HKCU\Software\Sony Corporation]
[HKCU\Software\Trolltech]
[HKCU\Software\Unity]
[HKCU\Software\VB and VBA Program Settings]
[HKCU\Software\Wargaming.net]
[HKCU\Software\WinRAR]
[HKCU\Software\Wow6432Node]
[HKCU\Software\syncables]
[HKLM\Software\AGEIA Technologies]
[HKLM\Software\ASUS]
[HKLM\Software\ATHEROS]
[HKLM\Software\ATI Technologies]
[HKLM\Software\ATK0100]
[HKLM\Software\Autodesk]
[HKLM\Software\Canon]
[HKLM\Software\Classes]
[HKLM\Software\Clients]
[HKLM\Software\CoreSecurity]
[HKLM\Software\DTS]
[HKLM\Software\ECAREME]
[HKLM\Software\Google]
[HKLM\Software\IM Providers]
[HKLM\Software\Intel]
[HKLM\Software\Khronos]
[HKLM\Software\Macromedia]
[HKLM\Software\Macrovision]
[HKLM\Software\MozillaPlugins]
[HKLM\Software\NVIDIA Corporation]
[HKLM\Software\ODBC]
[HKLM\Software\Piriform]
[HKLM\Software\Policies]
[HKLM\Software\RTLSetup]
[HKLM\Software\Realtek Semiconductor Corp.]
[HKLM\Software\Realtek]
[HKLM\Software\RegisteredApplications]
[HKLM\Software\SONIX]
[HKLM\Software\SRS Labs]
[HKLM\Software\Safer Networking Limited]
[HKLM\Software\Softland]
[HKLM\Software\SonicFocus]
[HKLM\Software\Sonic]
[HKLM\Software\Waves Audio]
[HKLM\Software\Wow6432Node\AGEIA Technologies]
[HKLM\Software\Wow6432Node\ASUS]
[HKLM\Software\Wow6432Node\AVS4YOU]
[HKLM\Software\Wow6432Node\Adobe]
[HKLM\Software\Wow6432Node\AdwCleaner]
[HKLM\Software\Wow6432Node\Apple Computer, Inc.]
[HKLM\Software\Wow6432Node\ArcSoft]
[HKLM\Software\Wow6432Node\Autodesk]
[HKLM\Software\Wow6432Node\Avira]
[HKLM\Software\Wow6432Node\Battlelog Web Plugins]
[HKLM\Software\Wow6432Node\Bunndle]
[HKLM\Software\Wow6432Node\Classes]
[HKLM\Software\Wow6432Node\Clients]
[HKLM\Software\Wow6432Node\CyberLink]
[HKLM\Software\Wow6432Node\DICE]
[HKLM\Software\Wow6432Node\DT Soft]
[HKLM\Software\Wow6432Node\EA Games]
[HKLM\Software\Wow6432Node\Electronic Arts]
[HKLM\Software\Wow6432Node\Emsi Software GmbH]
[HKLM\Software\Wow6432Node\Even Balance]
[HKLM\Software\Wow6432Node\GlarySoft]
[HKLM\Software\Wow6432Node\Google]
[HKLM\Software\Wow6432Node\HighCriteria]
[HKLM\Software\Wow6432Node\IM Providers]
[HKLM\Software\Wow6432Node\Intel]
[HKLM\Software\Wow6432Node\JavaSoft]
[HKLM\Software\Wow6432Node\JreMetrics]
[HKLM\Software\Wow6432Node\Kaydara]
[HKLM\Software\Wow6432Node\Khronos]
[HKLM\Software\Wow6432Node\Kodak]
[HKLM\Software\Wow6432Node\Lavasoft]
[HKLM\Software\Wow6432Node\Licenses]
[HKLM\Software\Wow6432Node\MAP-DN]
[HKLM\Software\Wow6432Node\Macromedia]
[HKLM\Software\Wow6432Node\Malwarebytes' Anti-Malware]
[HKLM\Software\Wow6432Node\MozillaPlugins]
[HKLM\Software\Wow6432Node\NVIDIA Corporation]
[HKLM\Software\Wow6432Node\ODBC]
[HKLM\Software\Wow6432Node\Oberon Media]
[HKLM\Software\Wow6432Node\Origin Games]
[HKLM\Software\Wow6432Node\Policies]
[HKLM\Software\Wow6432Node\RealNetworks]
[HKLM\Software\Wow6432Node\Realtek]
[HKLM\Software\Wow6432Node\RegisteredApplications]
[HKLM\Software\Wow6432Node\Safer Networking Limited]
[HKLM\Software\Wow6432Node\Skype]
[HKLM\Software\Wow6432Node\Sony Corporation]
[HKLM\Software\Wow6432Node\TQ566808]
[HKLM\Software\Wow6432Node\VideoLAN]
[HKLM\Software\Wow6432Node\Voice]
[HKLM\Software\Wow6432Node\Volatile]
[HKLM\Software\Wow6432Node\WinRAR]
[HKLM\Software\Wow6432Node\Wow6432Node]
[HKLM\Software\Wow6432Node\X-AVCSD]
[HKLM\Software\Wow6432Node\syncables]
[HKLM\Software\Wow6432Node]
~ Key Software: 276 Scanned in 00mn 00s
---\\ Contenu des dossiers Programs/ProgramFiles/ProgramData/AppData (O43)
O43 - CFD: 28/12/2012 - 09:28:24 - [] ----D C:\Program Files (x86)\Adobe
O43 - CFD: 13/04/2013 - 15:19:36 - [] ----D C:\Program Files (x86)\Alinea
O43 - CFD: 13/04/2013 - 15:28:02 - [] ----D C:\Program Files (x86)\Alinéa
O43 - CFD: 14/06/2012 - 16:25:07 - [] ----D C:\Program Files (x86)\ArcSoft
O43 - CFD: 25/07/2011 - 10:43:18 - [] ----D C:\Program Files (x86)\ASUS
O43 - CFD: 25/03/2011 - 04:36:35 - [] ----D C:\Program Files (x86)\Atheros
O43 - CFD: 14/12/2014 - 17:31:51 - [] ----D C:\Program Files (x86)\Avira
O43 - CFD: 27/12/2013 - 08:19:13 - [] ----D C:\Program Files (x86)\Battlelog Web Plugins
O43 - CFD: 30/07/2011 - 17:28:48 - [] ----D C:\Program Files (x86)\Chronometre
O43 - CFD: 17/01/2015 - 16:30:19 - [] ----D C:\Program Files (x86)\Common Files
O43 - CFD: 25/03/2011 - 03:32:31 - [] ----D C:\Program Files (x86)\CyberLink
O43 - CFD: 28/12/2012 - 10:06:45 - [] ----D C:\Program Files (x86)\DAEMON Tools Lite =>.DT Soft Ltd
O43 - CFD: 06/08/2011 - 11:08:38 - [] ----D C:\Program Files (x86)\EA GAMES
O43 - CFD: 07/08/2011 - 10:00:52 - [] ----D C:\Program Files (x86)\Electronic Arts
O43 - CFD: 15/07/2014 - 16:52:01 - [] ----D C:\Program Files (x86)\Emsisoft Anti-Malware
O43 - CFD: 29/12/2012 - 15:10:22 - [] ----D C:\Program Files (x86)\FileHippo.com
O43 - CFD: 17/01/2015 - 16:47:36 - [] ----D C:\Program Files (x86)\Glary Utilities 5
O43 - CFD: 25/07/2011 - 10:51:23 - [] ----D C:\Program Files (x86)\Google
O43 - CFD: 31/12/2013 - 12:37:31 - [] ----D C:\Program Files (x86)\Inspiration 8 IE
O43 - CFD: 14/07/2012 - 13:32:51 - [] --H-D C:\Program Files (x86)\InstallShield Installation Information
O43 - CFD: 06/01/2013 - 11:50:20 - [] ----D C:\Program Files (x86)\Intel
O43 - CFD: 12/12/2014 - 08:20:23 - [] ----D C:\Program Files (x86)\Internet Explorer
O43 - CFD: 08/12/2014 - 19:29:27 - [] ----D C:\Program Files (x86)\Java
O43 - CFD: 15/07/2014 - 16:34:23 - [] ----D C:\Program Files (x86)\Malwarebytes Anti-Malware
O43 - CFD: 20/03/2012 - 21:21:25 - [] ----D C:\Program Files (x86)\Microsoft Office
O43 - CFD: 24/07/2014 - 17:32:43 - [] ----D C:\Program Files (x86)\Microsoft Silverlight
O43 - CFD: 25/03/2011 - 03:48:29 - [] ----D C:\Program Files (x86)\Microsoft SQL Server Compact Edition
O43 - CFD: 06/08/2011 - 11:04:47 - [] ----D C:\Program Files (x86)\Microsoft Visual Studio
O43 - CFD: 06/08/2011 - 11:03:01 - [] ----D C:\Program Files (x86)\Microsoft Visual Studio 8
O43 - CFD: 08/08/2011 - 21:24:52 - [] ----D C:\Program Files (x86)\Microsoft Works
O43 - CFD: 06/08/2011 - 11:04:30 - [] ----D C:\Program Files (x86)\Microsoft.NET
O43 - CFD: 22/05/2014 - 18:06:11 - [] ----D C:\Program Files (x86)\MonAlbumPhoto
O43 - CFD: 06/08/2011 - 11:04:56 - [] ----D C:\Program Files (x86)\MSBuild
O43 - CFD: 25/03/2011 - 04:01:11 - [] ----D C:\Program Files (x86)\MSXML 4.0
O43 - CFD: 31/12/2013 - 12:37:31 - [] ----D C:\Program Files (x86)\MyDrive Connect
O43 - CFD: 06/01/2013 - 12:31:07 - [] ----D C:\Program Files (x86)\NVIDIA Corporation
O43 - CFD: 19/12/2014 - 10:01:24 - [] ----D C:\Program Files (x86)\Origin
O43 - CFD: 03/01/2013 - 19:08:26 - [] ----D C:\Program Files (x86)\Origin Games
O43 - CFD: 04/10/2011 - 18:00:10 - [] ----D C:\Program Files (x86)\QuickTime
O43 - CFD: 25/03/2011 - 04:40:07 - [] ----D C:\Program Files (x86)\Realtek
O43 - CFD: 14/07/2009 - 06:32:38 - [] ----D C:\Program Files (x86)\Reference Assemblies
O43 - CFD: 10/05/2014 - 14:39:31 - [] R---D C:\Program Files (x86)\Skype
O43 - CFD: 08/04/2012 - 14:30:06 - [] ----D C:\Program Files (x86)\Sony
O43 - CFD: 05/06/2012 - 18:11:20 - [] ----D C:\Program Files (x86)\Sony Media Go Install
O43 - CFD: 28/12/2012 - 09:47:09 - [] ----D C:\Program Files (x86)\Spybot - Search & Destroy
O43 - CFD: 17/01/2015 - 16:45:17 - [] ----D C:\Program Files (x86)\Spybot - Search & Destroy 2
O43 - CFD: 25/03/2011 - 03:56:17 - [] ----D C:\Program Files (x86)\syncables
O43 - CFD: 25/03/2011 - 04:29:59 - [0] --H-D C:\Program Files (x86)\Temp
O43 - CFD: 31/12/2013 - 12:37:31 - [] ----D C:\Program Files (x86)\TomTom HOME 2
O43 - CFD: 14/07/2009 - 05:57:06 - [0] --H-D C:\Program Files (x86)\Uninstall Information
O43 - CFD: 06/08/2011 - 11:55:08 - [] ----D C:\Program Files (x86)\Unlocker
O43 - CFD: 31/12/2013 - 12:37:31 - [] ----D C:\Program Files (x86)\uTorrent =>P2P.µTorrent
O43 - CFD: 14/08/2011 - 13:14:46 - [] ----D C:\Program Files (x86)\VideoLAN
O43 - CFD: 11/07/2013 - 08:13:37 - [] ----D C:\Program Files (x86)\Windows Defender
O43 - CFD: 25/07/2011 - 17:15:47 - [] ----D C:\Program Files (x86)\Windows Live
O43 - CFD: 20/03/2012 - 21:25:46 - [] ----D C:\Program Files (x86)\Windows Mail =>.Microsoft Corporation
O43 - CFD: 15/10/2014 - 16:56:01 - [] ----D C:\Program Files (x86)\Windows Media Player =>.Microsoft Corporation
O43 - CFD: 14/07/2009 - 06:32:38 - [] ----D C:\Program Files (x86)\Windows NT
O43 - CFD: 20/03/2012 - 21:25:46 - [] ----D C:\Program Files (x86)\Windows Photo Viewer
O43 - CFD: 20/03/2012 - 21:25:46 - [] ----D C:\Program Files (x86)\Windows Portable Devices
O43 - CFD: 20/03/2012 - 21:25:46 - [] ----D C:\Program Files (x86)\Windows Sidebar
O43 - CFD: 20/08/2013 - 07:51:24 - [] ----D C:\Program Files (x86)\WinRAR
O43 - CFD: 17/01/2015 - 16:06:29 - [] ----D C:\Program Files (x86)\ZHPDiag =>.Nicolas Coolman
O43 - CFD: 28/12/2012 - 09:28:27 - [] ----D C:\Program Files (x86)\Common Files\Adobe
O43 - CFD: 14/06/2012 - 16:25:09 - [] ----D C:\Program Files (x86)\Common Files\ArcSoft
O43 - CFD: 25/03/2011 - 04:33:26 - [] ----D C:\Program Files (x86)\Common Files\Atheros
O43 - CFD: 27/04/2012 - 16:06:12 - [] ----D C:\Program Files (x86)\Common Files\AVSMedia
O43 - CFD: 16/05/2014 - 12:19:55 - [] ----D C:\Program Files (x86)\Common Files\designer
O43 - CFD: 03/01/2013 - 19:56:11 - [] --H-D C:\Program Files (x86)\Common Files\EAInstaller
O43 - CFD: 25/03/2011 - 04:43:57 - [] ----D C:\Program Files (x86)\Common Files\InstallShield
O43 - CFD: 25/03/2011 - 04:21:50 - [] ----D C:\Program Files (x86)\Common Files\Intel
O43 - CFD: 08/12/2014 - 19:29:51 - [] ----D C:\Program Files (x86)\Common Files\Java
O43 - CFD: 05/04/2013 - 13:03:25 - [] ----D C:\Program Files (x86)\Common Files\microsoft shared
O43 - CFD: 25/03/2011 - 03:54:13 - [] ----D C:\Program Files (x86)\Common Files\Oberon Media
O43 - CFD: 28/08/2012 - 13:44:37 - [] ----D C:\Program Files (x86)\Common Files\Real
O43 - CFD: 14/07/2009 - 04:20:08 - [] ----D C:\Program Files (x86)\Common Files\Services
O43 - CFD: 10/05/2014 - 14:39:31 - [] ----D C:\Program Files (x86)\Common Files\Skype
O43 - CFD: 04/10/2011 - 18:01:02 - [] ----D C:\Program Files (x86)\Common Files\Sony Shared
O43 - CFD: 14/07/2009 - 04:20:08 - [] ----D C:\Program Files (x86)\Common Files\SpeechEngines
O43 - CFD: 14/07/2012 - 09:52:15 - [] ----D C:\Program Files (x86)\Common Files\System
O43 - CFD: 25/03/2011 - 03:35:42 - [] ----D C:\Program Files (x86)\Common Files\Windows Live
O43 - CFD: 25/07/2011 - 10:43:46 - [] --H-D C:\ProgramData\.Syncables
O43 - CFD: 25/07/2011 - 10:43:50 - [] --H-D C:\ProgramData\.syncID
O43 - CFD: 01/03/2013 - 19:10:11 - [] ----D C:\ProgramData\Adobe
O43 - CFD: 25/05/2014 - 18:37:59 - [] ----D C:\ProgramData\albumphoto
O43 - CFD: 04/10/2011 - 17:59:26 - [] ----D C:\ProgramData\Apple
O43 - CFD: 04/10/2011 - 17:59:49 - [] ----D C:\ProgramData\Apple Computer
O43 - CFD: 14/07/2009 - 06:08:56 - [] -SH-D C:\ProgramData\Application Data
O43 - CFD: 14/07/2012 - 13:32:51 - [] ----D C:\ProgramData\ArcSoft
O43 - CFD: 13/07/2011 - 15:24:15 - [] ----D C:\ProgramData\ASUS
O43 - CFD: 20/05/2014 - 18:04:34 - [] ----D C:\ProgramData\Atheros
O43 - CFD: 17/01/2015 - 16:29:25 - [] ----D C:\ProgramData\Autodesk
O43 - CFD: 20/08/2014 - 17:48:38 - [] ----D C:\ProgramData\Avira
O43 - CFD: 27/04/2012 - 15:34:42 - [] ----D C:\ProgramData\AVS4YOU
O43 - CFD: 04/12/2014 - 19:17:24 - [] ----D C:\ProgramData\boost_interprocess
O43 - CFD: 25/07/2011 - 09:17:55 - [] -SH-D C:\ProgramData\Bureau
O43 - CFD: 18/08/2013 - 08:53:38 - [] --H-D C:\ProgramData\CanonBJ
O43 - CFD: 06/08/2011 - 10:56:48 - [] ----D C:\ProgramData\CyberLink
O43 - CFD: 18/03/2014 - 20:54:07 - [] ----D C:\ProgramData\DAEMON Tools Lite =>.DT Soft Ltd
O43 - CFD: 14/07/2009 - 06:08:56 - [] -SH-D C:\ProgramData\Desktop
O43 - CFD: 14/07/2009 - 06:08:56 - [] -SH-D C:\ProgramData\Documents
O43 - CFD: 25/03/2011 - 03:33:36 - [] ----D C:\ProgramData\Downloaded Installations
O43 - CFD: 04/01/2013 - 06:40:51 - [] ----D C:\ProgramData\EA Core
O43 - CFD: 05/01/2013 - 09:59:21 - [] ----D C:\ProgramData\EA Logs
O43 - CFD: 04/01/2013 - 06:40:54 - [] ----D C:\ProgramData\Electronic Arts
O43 - CFD: 25/07/2011 - 09:17:55 - [] -SH-D C:\ProgramData\Favoris
O43 - CFD: 14/07/2009 - 06:08:56 - [] -SH-D C:\ProgramData\Favorites
O43 - CFD: 10/05/2014 - 15:00:15 - [] ----D C:\ProgramData\FLEXnet
O43 - CFD: 24/03/2013 - 17:00:27 - [] ----D C:\ProgramData\Inspiration 9 IE
O43 - CFD: 10/02/2013 - 17:40:23 - [] ----D C:\ProgramData\Ins -
Le rapport n'est pas passé en entier. Refait le STP en suivant cette Manip déjà décrite plus haut.
tu le postes sur http://www.cjoint.com/ puis tu mets le lien généré par cjoint dans ta réponse.
Tutoriel pour cjoint : https://www.commentcamarche.net/faq/29493-utiliser-cjoint-pour-heberger-des-fichiers
Merci. -
http://cjoint.com/?EArrJt42P9K
-
Est-ce que tu utilises les logiciels :
- uTorrent (Peer to peer).
- Glary utilities (réparation et optimisation) redondance tu as déjà Ccleaner je me trompe ?
- Emsisoft Anti-Malware.
Si tu n'en as pas l'utilité tu peux les désinstaller.
Ensuite je te fait le script ... -
Ok, j'ai supprimé uTorrent et Glary utilies que j'utilise peu
-
1/ Copie tout le texte présent en gras ci-dessous (Sélectionne-le, clique droit dessus et choisis "Copier").
--> Lance ZHPFix (avec les droits d'administrateur) depuis le raccourci situé sur ton Bureau.
--> Clique sur le bouton IMPORTER. Dans l'encadré principal, tu verras les lignes que tu as copié précédemment apparaître.
--> Clique sur GO et confirme pour lancer le nettoyage. Laisse l'outil travailler et ne touche à rien.
Une fois terminé, héberge le rapport sur http://www.cjoint.com/ puis copie-colle le lien dans ton prochain message.
2/ Ensuite tu me fais un scan avec malwarebytes.
J'attends le rapport ZHPFix et Malwarebyte.
Script ZHPFix
R0 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = about:blank
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = about:blank
OPT:O4 - HKLM\..\Run: [IgfxTray] . (.Intel Corporation - igfxTray Module.) -- C:\Windows\system32\igfxtray.exe
OPT:O4 - HKLM\..\Run: [Persistence] . (.Intel Corporation - persistence Module.) -- C:\Windows\system32\igfxpers.exe
OPT:O4 - HKUS\S-1-5-19\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe
OPT:O4 - HKUS\S-1-5-20\..\RunOnce: [mctadmin] . (.Microsoft Corporation - MCTAdmin.) -- C:\Windows\System32\mctadmin.exe
[MD5.00000000000000000000000000000000] [APT] [{1FEF89C8-8D51-49E3-87D7-01E139E188A9}] (...) -- E:\SETUP.exe (.not file.) [0]
[MD5.00000000000000000000000000000000] [APT] [{9EC36DE6-F277-497F-A362-37F163AE8FB2}] (...) -- C:\Users\Thomas\Downloads\Autodesk_3ds_Max_2012_French_Win_32-64bit.exe (.not file.) [0]
[MD5.00000000000000000000000000000000] [APT] [{DCF8928A-610B-4959-98BE-86556A2AF3DC}] (...) -- E:\DINSTALL.exe (.not file.) [0]
[MD5.00000000000000000000000000000000] [APT] [{F7D26770-8C53-4469-9C70-378A315EC1BA}] (...) -- G:\Ordinateur\Office 2007 pro\SETUP.exe (.not file.) [0]
O43 - CFD: 28/12/2012 - 09:47:09 - [] ----D C:\Program Files (x86)\Spybot - Search & Destroy
O43 - CFD: 17/01/2015 - 16:45:17 - [] ----D C:\Program Files (x86)\Spybot - Search & Destroy 2
O43 - CFD: 17/01/2015 - 16:33:09 - [] ----D C:\ProgramData\Spybot - Search & Destroy
O45 - LFCP:[MD5.9B2054F05A0ED4F9E98E50369C74E69D] - 17/01/2015 - 15:20:54 ---A- - C:\Windows\Prefetch\DISKCLEANER.EXE-7280868A.pf =>Rogue.DiskCleaner
O61 - LFC: 17/01/2015 - 17:24:02 ---A- . (.Safer-Networking Ltd..) -- C:\Users\Thomas\Downloads\spybot-2.4.exe [46525608]
ServiceDemand:gupdate
ServiceDemand:nvUpdatusService
ServiceDemand:AdobeARMservice
ServiceDemand:NVSvc
FirewallRaz
EmptyPrefetch
EmptyTemp
EmptyFlash
Emptyclsid
Sysrestore -
Aucun nettoyage se lance sur ZHPFix
-
Après toutes ces opérations effectuées ...
Comment se comporte ton Pc ? y a t'il du mieux ? -
Oui, il se lance déjà plus rapidement au démarrage ! C'est normal qu'un nettoyage se fasse du coup ? C'est qu'il n'y a rien à nettoyer ?
J'effectue un scan avec Malwarebytes là -
Oui il faut faire le Script ZHPFix avant de passer Malwarebytes.
-
Je n'ai aucun élément malveillant sur l'ordinateur
-
Le script enlève des résidus de malwares et optimise ton démarrage.
Des adwares ont déjà été enlevés avec le logiciel adwcleaner au début de l'après-midi. -
- 1
- 2
