
Virus PUP-FNK
Bonjour,
Depuis plusieurs jours j'ai McAfee qui n'arrive pas à supprimer le programme malveillant PUP-FNK, il le met en quarantaine mais n'arrive pas à le supprimer et il revient sans arrêt. Il ouvre plein de fenêtre publicitaire et ralenti la navigation. Si quelqu'un à une solution je suis preneur. Par avance merci
Depuis plusieurs jours j'ai McAfee qui n'arrive pas à supprimer le programme malveillant PUP-FNK, il le met en quarantaine mais n'arrive pas à le supprimer et il revient sans arrêt. Il ouvre plein de fenêtre publicitaire et ralenti la navigation. Si quelqu'un à une solution je suis preneur. Par avance merci
9 réponses
-
McAfee est certainement le pire antivirus qui existe. Tellement nul qu'ils sont obligés de les mettre en téléchargement "discret" couplé sur un autre programme pour qu'ils puissent arriver à avoir un peu de public. C'est pitoyable
Désinstalle le et met avast c'est beaucoup plus efficace -
Contributeur sécuritéIl ne faut pas changer d'antivirus pour l'instant...
Bonjour
Tu as dû installer des logiciels potentiellement indésirables
Pour éviter ce genre de problème :
- Ne télécharge aucun programme proposé dans des publicités ou sur des sites suspects. A noter que certains sites connus comme Softronic, Tuto4PC, etc modifient parfois les programmes proposés au téléchargement pour y ajouter des logiciels publicitaires ==> Préfère toujours le téléchargement directement sur le site de l'éditeur.
- Au cours de l'installation d'un programme gratuit, lis bien attentivement et décoche tous les programmes additionnels qui sont proposés, en particulier les barres d'outils.
Pour ton information lis ces dossier sur les Programmes Potentiellement Indésirables et Les Barres d'Outils ce n'est pas obligatoires
* Télécharge cet outil simple d'utilisation
https://toolslib.net/downloads/viewdownload/1-adwcleaner/
* Si problème avec le 1er lien prends le ici https://www.commentcamarche.net/telecharger/securite/2759-adwcleaner/
* Lance le (Sous vista/seven/8 clic droit dessus,et sur exécuter en tant qu'administrateur)si tu es sous xp double cliques dessus
* Cliques sur scanner
* Poste le rapport de recherche C:\Adwcleaner[R]
* Note le rapport de recherche est également sauvegardé sous C:\Adwcleaner[R1]
* Héberge le rapport sur cjoint
* Pour t'aider https://www.commentcamarche.net/faq/29493-utiliser-cjoint-pour-heberger-des-fichiers
-
-
AdwCleaner v3.310 - Rapport créé le 21/09/2014 à 19:01:58
# Mis à jour le 12/09/2014 par Xplode
# Système d'exploitation : Microsoft Windows XP Service Pack 3 (32 bits)
# Nom d'utilisateur : Antoine David - ANTOINE-DAVID
# Exécuté depuis : C:\Documents and Settings\Antoine David\Mes documents\Téléchargements\adwcleaner_3.310.exe
# Option : Scanner
***** [ Services ] *****
Service Présent : Update SmarterPower
Service Présent : Util SmarterPower
Service Présent : UpdaterSvcSmarterPower
Service Présent : {5eeb83d0-96ea-4249-942c-beead6847053}Gt
***** [ Fichiers / Dossiers ] *****
Dossier Présent : C:\Documents and Settings\All Users\Application Data\2308189059
Dossier Présent : C:\Documents and Settings\All Users\Uniblue
Dossier Présent : C:\Documents and Settings\All Users\Uniblue\DriverScanner
Dossier Présent : C:\Documents and Settings\Antoine David\Application Data\wse_astromenda
Dossier Présent : C:\Documents and Settings\Antoine David\Mes documents\Optimizer Pro
Dossier Présent : C:\Program Files\Optimizer Pro
Dossier Présent : C:\Program Files\SmarterPower
Fichier Présent : C:\Documents and Settings\Antoine David\Application Data\Mozilla\Firefox\Profiles\q2bhqz1j.default-1409559341937\searchplugins\astromenda.xml
Fichier Présent : C:\Documents and Settings\Antoine David\Application Data\Mozilla\Firefox\Profiles\q2bhqz1j.default-1409559341937\user.js
Fichier Présent : C:\WINDOWS\system32\drivers\{5eeb83d0-96ea-4249-942c-beead6847053}Gt.sys
***** [ Tâches planifiées ] *****
***** [ Raccourcis ] *****
***** [ Registre ] *****
Clé Présente : HKCU\Software\AppDataLow\{1146AC44-2F03-4431-B4FD-889BC837521F}
Clé Présente : HKCU\Software\AppDataLow\SmarterPower
Clé Présente : HKCU\Software\AppDataLow\SmarterPower
Clé Présente : HKCU\Software\InstallCore
Clé Présente : HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{2E00D31D-D171-423D-836D-1A4D7EA7F1A9}
Clé Présente : HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{1D4DB7D2-6EC9-47A3-BD87-1E41684E07BB}
Clé Présente : HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{bd7c9b62-a7d9-4405-be51-7fd633f08791}
Clé Présente : HKCU\Software\Optimizer Pro
Clé Présente : HKCU\Software\SmarterPower
Clé Présente : HKCU\Software\SmarterPower
Clé Présente : HKCU\Software\YahooPartnerToolbar
Clé Présente : HKLM\SOFTWARE\{1146AC44-2F03-4431-B4FD-889BC837521F}
Clé Présente : HKLM\SOFTWARE\{3A7D3E19-1B79-4E4E-BD96-5467DA2C4EF0}
Clé Présente : HKLM\SOFTWARE\{6791A2F3-FC80-475C-A002-C014AF797E9C}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{1AA60054-57D9-4F99-9A55-D0FBFBE7ECD3}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{4AA46D49-459F-4358-B4D1-169048547C23}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{5A4E3A41-FA55-4BDA-AED7-CEBE6E7BCB52}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{5A4E3A41-FA55-4BDA-AED7-CEBE6E7BCB52}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{bd7c9b62-a7d9-4405-be51-7fd633f08791}
Clé Présente : HKLM\SOFTWARE\Classes\driverscanner
Clé Présente : HKLM\SOFTWARE\Classes\Interface\{4E6354DE-9115-4AEE-BD21-C46C3E8A49DB}
Clé Présente : HKLM\SOFTWARE\Classes\Interface\{98D9C91C-10F5-4B34-BD72-AE981CAA6F54}
Clé Présente : HKLM\SOFTWARE\Classes\Interface\{FC073BDA-C115-4A1D-9DF9-9B5C461482E5}
Clé Présente : HKLM\SOFTWARE\Classes\protector_dll.protectorbho
Clé Présente : HKLM\SOFTWARE\Classes\protector_dll.protectorbho.1
Clé Présente : HKLM\SOFTWARE\Classes\TypeLib\{A2D733A7-73B0-4C6B-B0C7-06A432950B66}
Clé Présente : HKLM\SOFTWARE\Classes\TypeLib\{A2D733A7-73B0-4C6B-B0C7-06A432950B66}
Clé Présente : HKLM\SOFTWARE\Classes\TypeLib\{be7650b2-5936-4ee6-b4f2-ae385db13a90}
Clé Présente : HKLM\SOFTWARE\Google\Chrome\Extensions\bopakagnckmlgajfccecajhnimjiiedh
Clé Présente : HKLM\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\{2E00D31D-D171-423D-836D-1A4D7EA7F1A9}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\{ac225167-00fc-452d-94c5-bb93600e7d9a}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\{ac225167-00fc-452d-94c5-bb93600e7d9a}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\Optimizer Pro_is1
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\SmarterPower
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\SmarterPower
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{bd7c9b62-a7d9-4405-be51-7fd633f08791}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{ac225167-00fc-452d-94c5-bb93600e7d9a}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{ac225167-00fc-452d-94c5-bb93600e7d9a}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\SmarterPower
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\SmarterPower
Clé Présente : HKLM\SOFTWARE\SmarterPower
Clé Présente : HKLM\SOFTWARE\SmarterPower
Clé Présente : HKLM\SOFTWARE\Uniblue
Clé Présente : HKLM\SYSTEM\CurrentControlSet\Services\EventLog\Application\Update SmarterPower
Clé Présente : HKLM\SYSTEM\CurrentControlSet\Services\EventLog\Application\Util SmarterPower
Valeur Présente : HKLM\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile\AuthorizedApplications\List [C:\Program Files\SmarterPower\bin\SmarterPower.BRT.Helper.exe]
***** [ Navigateurs ] *****
-\\ Internet Explorer v8.0.6001.18702
-\\ Mozilla Firefox v32.0.1 (x86 fr)
[ Fichier : C:\Documents and Settings\Antoine David\Application Data\Mozilla\Firefox\Profiles\q2bhqz1j.default-1409559341937\prefs.js ]
*************************
AdwCleaner[R0].txt - [5757 octets] - [21/09/2014 19:01:58]
########## EOF - C:\AdwCleaner\AdwCleaner[R0].txt - [5817 octets] ##########
-
-
AdwCleaner v3.310 - Rapport créé le 21/09/2014 à 19:01:58
# Mis à jour le 12/09/2014 par Xplode
# Système d'exploitation : Microsoft Windows XP Service Pack 3 (32 bits)
# Nom d'utilisateur : Antoine David - ANTOINE-DAVID
# Exécuté depuis : C:\Documents and Settings\Antoine David\Mes documents\Téléchargements\adwcleaner_3.310.exe
# Option : Scanner
***** [ Services ] *****
Service Présent : Update SmarterPower
Service Présent : Util SmarterPower
Service Présent : UpdaterSvcSmarterPower
Service Présent : {5eeb83d0-96ea-4249-942c-beead6847053}Gt
***** [ Fichiers / Dossiers ] *****
Dossier Présent : C:\Documents and Settings\All Users\Application Data\2308189059
Dossier Présent : C:\Documents and Settings\All Users\Uniblue
Dossier Présent : C:\Documents and Settings\All Users\Uniblue\DriverScanner
Dossier Présent : C:\Documents and Settings\Antoine David\Application Data\wse_astromenda
Dossier Présent : C:\Documents and Settings\Antoine David\Mes documents\Optimizer Pro
Dossier Présent : C:\Program Files\Optimizer Pro
Dossier Présent : C:\Program Files\SmarterPower
Fichier Présent : C:\Documents and Settings\Antoine David\Application Data\Mozilla\Firefox\Profiles\q2bhqz1j.default-1409559341937\searchplugins\astromenda.xml
Fichier Présent : C:\Documents and Settings\Antoine David\Application Data\Mozilla\Firefox\Profiles\q2bhqz1j.default-1409559341937\user.js
Fichier Présent : C:\WINDOWS\system32\drivers\{5eeb83d0-96ea-4249-942c-beead6847053}Gt.sys
***** [ Tâches planifiées ] *****
***** [ Raccourcis ] *****
***** [ Registre ] *****
Clé Présente : HKCU\Software\AppDataLow\{1146AC44-2F03-4431-B4FD-889BC837521F}
Clé Présente : HKCU\Software\AppDataLow\SmarterPower
Clé Présente : HKCU\Software\AppDataLow\SmarterPower
Clé Présente : HKCU\Software\InstallCore
Clé Présente : HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{2E00D31D-D171-423D-836D-1A4D7EA7F1A9}
Clé Présente : HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{1D4DB7D2-6EC9-47A3-BD87-1E41684E07BB}
Clé Présente : HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{bd7c9b62-a7d9-4405-be51-7fd633f08791}
Clé Présente : HKCU\Software\Optimizer Pro
Clé Présente : HKCU\Software\SmarterPower
Clé Présente : HKCU\Software\SmarterPower
Clé Présente : HKCU\Software\YahooPartnerToolbar
Clé Présente : HKLM\SOFTWARE\{1146AC44-2F03-4431-B4FD-889BC837521F}
Clé Présente : HKLM\SOFTWARE\{3A7D3E19-1B79-4E4E-BD96-5467DA2C4EF0}
Clé Présente : HKLM\SOFTWARE\{6791A2F3-FC80-475C-A002-C014AF797E9C}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{1AA60054-57D9-4F99-9A55-D0FBFBE7ECD3}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{4AA46D49-459F-4358-B4D1-169048547C23}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{5A4E3A41-FA55-4BDA-AED7-CEBE6E7BCB52}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{5A4E3A41-FA55-4BDA-AED7-CEBE6E7BCB52}
Clé Présente : HKLM\SOFTWARE\Classes\CLSID\{bd7c9b62-a7d9-4405-be51-7fd633f08791}
Clé Présente : HKLM\SOFTWARE\Classes\driverscanner
Clé Présente : HKLM\SOFTWARE\Classes\Interface\{4E6354DE-9115-4AEE-BD21-C46C3E8A49DB}
Clé Présente : HKLM\SOFTWARE\Classes\Interface\{98D9C91C-10F5-4B34-BD72-AE981CAA6F54}
Clé Présente : HKLM\SOFTWARE\Classes\Interface\{FC073BDA-C115-4A1D-9DF9-9B5C461482E5}
Clé Présente : HKLM\SOFTWARE\Classes\protector_dll.protectorbho
Clé Présente : HKLM\SOFTWARE\Classes\protector_dll.protectorbho.1
Clé Présente : HKLM\SOFTWARE\Classes\TypeLib\{A2D733A7-73B0-4C6B-B0C7-06A432950B66}
Clé Présente : HKLM\SOFTWARE\Classes\TypeLib\{A2D733A7-73B0-4C6B-B0C7-06A432950B66}
Clé Présente : HKLM\SOFTWARE\Classes\TypeLib\{be7650b2-5936-4ee6-b4f2-ae385db13a90}
Clé Présente : HKLM\SOFTWARE\Google\Chrome\Extensions\bopakagnckmlgajfccecajhnimjiiedh
Clé Présente : HKLM\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\{2E00D31D-D171-423D-836D-1A4D7EA7F1A9}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\{ac225167-00fc-452d-94c5-bb93600e7d9a}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\{ac225167-00fc-452d-94c5-bb93600e7d9a}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\Optimizer Pro_is1
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\SmarterPower
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\SmarterPower
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{bd7c9b62-a7d9-4405-be51-7fd633f08791}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{ac225167-00fc-452d-94c5-bb93600e7d9a}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{ac225167-00fc-452d-94c5-bb93600e7d9a}
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\SmarterPower
Clé Présente : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\SmarterPower
Clé Présente : HKLM\SOFTWARE\SmarterPower
Clé Présente : HKLM\SOFTWARE\SmarterPower
Clé Présente : HKLM\SOFTWARE\Uniblue
Clé Présente : HKLM\SYSTEM\CurrentControlSet\Services\EventLog\Application\Update SmarterPower
Clé Présente : HKLM\SYSTEM\CurrentControlSet\Services\EventLog\Application\Util SmarterPower
Valeur Présente : HKLM\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile\AuthorizedApplications\List [C:\Program Files\SmarterPower\bin\SmarterPower.BRT.Helper.exe]
***** [ Navigateurs ] *****
-\\ Internet Explorer v8.0.6001.18702
-\\ Mozilla Firefox v32.0.1 (x86 fr)
[ Fichier : C:\Documents and Settings\Antoine David\Application Data\Mozilla\Firefox\Profiles\q2bhqz1j.default-1409559341937\prefs.js ]
*************************
AdwCleaner[R0].txt - [5757 octets] - [21/09/2014 19:01:58]
########## EOF - C:\AdwCleaner\AdwCleaner[R0].txt - [5817 octets] ########## -
Contributeur sécuritéfais nettoyer
-
Contributeur sécuritéPeux tu établir un diagnostic avec zhpdiag
https://www.commentcamarche.net/telecharger/utilitaires/24803-zhpdiag/-
Bonjour, voici le rapport:
~ Rapport de ZHPDiag v2014.9.28.138 - Nicolas Coolman (28/09/2014)
~ Lancé par Antoine David (29/09/2014 09:47:15)
~ Adresse du Site Web https://nicolascoolman.eu
~ Adresse du Forum https://nicolascoolman.eu
~ Traduit par Nicolas Coolman
~ Etat de la version : Version à jour.
~ Liste blanche : Désactivée par l'utilisateur
~ Elévation des Privilèges : OK
~ User Account Control (UAC): Not Found
---\\ Navigateurs Internet
MSIE: Internet Explorer v8.0.6001.18702
MFIE: Mozilla Firefox 32.0.3 (Defaut)
---\\ Informations sur les produits Windows
~ Langage: Français
Microsoft Windows XP, 32-bit Service Pack 3 (Build 2600)
Windows Automatic Updates : OK
Windows Genuine Advantage : OK
---\\ Logiciels de protection du système
McAfee Security Scan Plus v3.8.150.1
---\\ Logiciels d'optimisation du système
CCleaner v4.17
---\\ Logiciels de partage PeerToPeer
Vuze v5.4.0.0 =>P2P.Azureus
---\\ Surveillance de Logiciels
Adobe Flash Player 15 Plugin
Adobe Reader XI
Java 7 Update 25
---\\ Informations sur le système
~ Processor: x86 Family 6 Model 15 Stepping 6, GenuineIntel
~ Operating System: 32 Bits
Boot mode: Normal (Normal boot)
Total RAM: 1021 MB (22% free)
System Restore: Activé (Enable)
System drive C: has 45 GB (46%) free of 98 GB
---\\ Mode de connexion au système
~ Computer Name: ANTOINE-DAVID
~ User Name: Antoine David
~ All Users Names: SUPPORT_388945a0, HelpAssistant, ASPNET, Antoine David, Administrateur,
~ Unselected Option: None
Logged in as Administrator
---\\ Variables d'environnement
~ System Unit : C:\
~ %AppZHP% : C:\Documents and Settings\Antoine David\Application Data\ZHP\
~ %AppData% : C:\Documents and Settings\Antoine David\Application Data\
~ %Desktop% : C:\Documents and Settings\Antoine David\Bureau\
~ %Favorites% : C:\Documents and Settings\Antoine David\Favoris\
~ %LocalAppData% : C:\Documents and Settings\Antoine David\Local Settings\Application Data\
~ %StartMenu% : C:\Documents and Settings\Antoine David\Menu Démarrer\
~ %Windir% : C:\WINDOWS\
~ %System% : C:\WINDOWS\system32\
---\\ Enumération des unités disques
C: Hard drive, Flash drive, Thumb drive (Free 45 Go of 98 Go)
D: CD-ROM drive (Not Inserted)
E: Hard drive, Flash drive, Thumb drive (Free 105 Go of 135 Go)
O: CD-ROM drive (Not Inserted)
---\\ Etat du Centre de Sécurité Windows
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Associations] Application: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Associations] Intl: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Associations] XMLLookup: OK
[HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon] Shell: OK
[HKCU\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows] Load: OK
[HKLM\SYSTEM\CurrentControlSet\Services\COMSysApp] Type: OK
[HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install] LastSuccessTime : OK
~ Security Center: 42 Scanned in 00mn 00s
---\\ Recherche particulière de fichiers génériques
[MD5.F2317622D29F9FF0F88AEECD5F60F0DD] - (.Microsoft Corporation - Explorateur Windows.) (.14/04/2008 - 03:34:03.) -- C:\WINDOWS\Explorer.exe [1037824]
[MD5.E1948B1F45A176FB4A0251446A5AE86D] - (.Microsoft Corporation - Internet Extensions for Win32.) (.06/03/2014 - 18:58:52.) -- C:\WINDOWS\system32\wininet.dll [920064]
[MD5.DD73D6B9F6B4CB630CF35B438B540174] - (.Microsoft Corporation - Application d'ouverture de session Windows NT.) (.14/04/2008 - 03:34:28.) -- C:\WINDOWS\system32\Winlogon.exe [512000]
[MD5.1E44BC1E83D8FD2305F8D452DB109CF9] - (.Microsoft Corporation - Ancillary Function Driver for WinSock.) (.17/08/2011 - 14:49:54.) -- C:\WINDOWS\system32\Drivers\AFD.sys [138496]
[MD5.9F3A2F5AA6875C72BF062C712CFA2674] - (.Microsoft Corporation - IDE/ATAPI Port Driver.) (.13/04/2008 - 19:40:30.) -- C:\WINDOWS\system32\Drivers\atapi.sys [96512]
[MD5.C885B02847F5D2FD45A24E219ED93B32] - (.Microsoft Corporation - CD-ROM File System Driver.) (.13/04/2008 - 20:14:21.) -- C:\WINDOWS\system32\Drivers\Cdfs.sys [63744]
[MD5.1F4260CC5B42272D71F79E570A27A4FE] - (.Microsoft Corporation - SCSI CD-ROM Driver.) (.13/04/2008 - 19:40:46.) -- C:\WINDOWS\system32\Drivers\Cdrom.sys [62976]
[MD5.31F923EB2170FC172C81ABDA0045D18C] - (.Microsoft Corporation - Pilote de cryptographie FIPS.) (.14/04/2008 - 02:57:38.) -- C:\WINDOWS\system32\Drivers\Fips.sys [44672]
[MD5.573C7D0A32852B48F3058CFD8026F511] - (.Windows (R) Server 2003 DDK provider - High Definition Audio Bus Driver v1.0a.) (.13/04/2008 - 17:36:05.) -- C:\WINDOWS\system32\Drivers\HDAudBus.sys [144384]
[MD5.A09BDC4ED10E3B2E0EC27BB94AF32516] - (.Microsoft Corporation - Pilote de port i8042.) (.14/04/2008 - 03:00:52.) -- C:\WINDOWS\system32\Drivers\i8042prt.sys [54144]
[MD5.083A052659F5310DD8B6A6CB05EDCF8E] - (.Microsoft Corporation - IMAPI Kernel Driver.) (.13/04/2008 - 19:40:58.) -- C:\WINDOWS\system32\Drivers\Imapi.sys [42112]
[MD5.CC748EA12C6EFFDE940EE98098BF96BB] - (.Microsoft Corporation - IP Network Address Translator.) (.13/04/2008 - 19:57:15.) -- C:\WINDOWS\system32\Drivers\IpNat.sys [152832]
[MD5.23C74D75E36E7158768DD63D92789A91] - (.Microsoft Corporation - IPSec Driver.) (.13/04/2008 - 20:19:42.) -- C:\WINDOWS\system32\Drivers\IPSec.sys [75264]
[MD5.7D304A5EB4344EBEEAB53A2FE3FFB9F0] - (.Microsoft Corporation - Windows NT SMB Minirdr.) (.15/07/2011 - 14:29:31.) -- C:\WINDOWS\system32\Drivers\MRxSmb.sys [456320]
[MD5.74B2B2F5BEA5E9A3DC021D685551BD3D] - (.Microsoft Corporation - MBT Transport driver.) (.13/04/2008 - 20:21:00.) -- C:\WINDOWS\system32\Drivers\netBT.sys [162816]
[MD5.78A08DD6A8D65E697C18E1DB01C5CDCA] - (.Microsoft Corporation - NT File System Driver.) (.13/04/2008 - 20:15:53.) -- C:\WINDOWS\system32\Drivers\ntfs.sys [574976]
[MD5.8FD0BDBEA875D06CCF6C945CA9ABAF75] - (.Microsoft Corporation - Pilote de port parallèle.) (.14/04/2008 - 03:09:40.) -- C:\WINDOWS\system32\Drivers\Parport.sys [80384]
[MD5.11B4A627BC9614B885C4969BFA5FF8A6] - (.Microsoft Corporation - RAS L2TP mini-port/call-manager driver.) (.13/04/2008 - 20:19:43.) -- C:\WINDOWS\system32\Drivers\Rasl2tp.sys [51328]
[MD5.15CABD0F7C00C47C70124907916AF3F1] - (.Microsoft Corporation - Microsoft RDP Device redirector.) (.13/04/2008 - 19:32:51.) -- C:\WINDOWS\system32\Drivers\rdpdr.sys [196224]
[MD5.D8EB2A7904DB6C916EB5361878DDCBAE] - (.Microsoft Corporation - Pilote de filtre audio Livre rouge.) (.14/04/2008 - 02:57:34.) -- C:\WINDOWS\system32\Drivers\redbook.sys [58752]
[MD5.46DE1126684369BACE4849E4FC8C43CA] - (.Microsoft Corporation - Pilote de cliché instantané du volume.) (.14/04/2008 - 02:56:04.) -- C:\WINDOWS\system32\Drivers\volsnap.sys [53376]
~ Generic Processes: Scanned in 00mn 02s
---\\ Etat des fichiers cachés (Caché/Total)
~ Mes images (My Pictures) : 2/33
~ Mes musiques (My Musics) : 1/591
~ Mes Videos (My Videos) : 2/8
~ Mes Favoris (My Favorites) : 1/38
~ Mes Documents (My Documents) : 1/1431
~ Mon Bureau (My Desktop) : 0/128
~ Menu demarrer (Programs) : 1/38
~ Hidden Files: Scanned in 00mn 04s
---\\ Processus lancés
[MD5.C23082B890F21267037CA6111C385FF3] - (.ATI Technologies Inc. - ATI External Event Utility EXE Module.) -- C:\WINDOWS\system32\Ati2evxx.exe [409600] [PID.1652]
[MD5.9DBA73C2F1E76EC4CB837E67C5743596] - (.Sun Microsystems, Inc. - Java(TM) Quick Starter Service.) -- C:\Program Files\Java\jre6\bin\jqs.exe [153376] [PID.1204]
[MD5.5007E21208DA68F60EBF43352BDFE6D0] - (.McAfee, Inc. - McAfee Service Host.) -- C:\Program Files\Fichiers communs\Mcafee\Platform\McSvcHost\McSvHost.exe [281560] [PID.1340]
[MD5.9ECA2FA155897ED17E42AFC70F0CE01D] - (.McAfee, Inc. - McAfee Process Validation Service.) -- C:\WINDOWS\system32\mfevtps.exe [179600] [PID.2020]
[MD5.2D091A99624FB9E7EEF0A86D872EC0C3] - (.HP - PML Driver.) -- C:\WINDOWS\system32\HPZipm12.exe [73728] [PID.232]
[MD5.16B115E3706F493BE99FCA5D75EE54CF] - (.McAfee, Inc. - McAfee Access Protection.) -- C:\Program Files\McAfee\MSC\McAPexe.exe [145568] [PID.1052]
[MD5.2E0B0A051FFAA86E358465BB0880D453] - (.Microsoft Corporation - Windows Update.) -- C:\WINDOWS\system32\wuauclt.exe [53784] [PID.1144]
[MD5.283AA915917B621940B1434578A58E97] - (.McAfee, Inc. - McAfee On-Access Scanner service.) -- C:\Program Files\Fichiers communs\McAfee\AMCore\mcshield.exe [655936] [PID.1184]
[MD5.8020C7C06B9DDC3372A9A84844C03136] - (.McAfee, Inc. - McAfee Core Firewall Service.) -- C:\Program Files\Fichiers communs\McAfee\SystemCore\mfefire.exe [169800] [PID.1248]
[MD5.E18770ED0BA0BA5BBAE0ABBE456F3482] - (.SigmaTel, Inc. - Sigmatel Audio system tray application.) -- C:\WINDOWS\stsystra.exe [282624] [PID.2540]
[MD5.30E1F03DCC8825988528D9058312EDE2] - (.Apple Computer, Inc. - QuickTime Task.) -- C:\Program Files\QuickTime\qttask.exe [282624] [PID.2548]
[MD5.D658AB1B55127D18DCFBCAC8CAAEA522] - (.Hewlett-Packard - hpwuSchd Application.) -- C:\Program Files\HP\HP Software Update\HPWuSchd2.exe [49208] [PID.2568]
[MD5.81800928E0F713DF31F3393CC26F4013] - (.Pas de propriétaire - DivX Update.) -- C:\Program Files\DivX\DivX Update\DivXUpdate.exe [1263952] [PID.2692]
[MD5.D63797E8E7781EE1500A810CB6194FA6] - (.Oracle Corporation - Java(TM) Update Scheduler.) -- C:\Program Files\Fichiers communs\Java\Java Update\jusched.exe [253816] [PID.2788]
[MD5.C519CEC624CF9BCBA3059F32266C8FFF] - (.Hewlett-Packard Co. - HP Digital Imaging Monitor.) -- C:\Program Files\HP\Digital Imaging\bin\hpqtra08.exe [258048] [PID.3136]
[MD5.3D558E2572EDF52FAD098AF2534B4E20] - (.McAfee, Inc. - McAfee Security Scanner Scheduler.) -- C:\Program Files\McAfee Security Scan\3.8.150\SSScheduler.exe [279456] [PID.3408]
[MD5.74557BFD04530E512DBB9C151C4DA110] - (.McAfee, Inc. - McAfee.) -- C:\Program Files\Fichiers communs\McAfee\Platform\mcuicnt.exe [499384] [PID.3820]
[MD5.6B2B9B46D7DA5C67397412DEA6CF9A14] - (.Hewlett-Packard Co. - Pas de description.) -- C:\Program Files\HP\Digital Imaging\bin\hpqgalry.exe [425984] [PID.3896]
[MD5.93AD0B78C7357A05F50E594EC7C22300] - (...) -- ystem32\rundll32.exe [0] [PID.3292]
[MD5.FB104D17018B4CA9F0C1A9BED02D15FC] - (.Mozilla Corporation - Firefox.) -- C:\Program Files\Mozilla Firefox\firefox.exe [275568] [PID.3800]
[MD5.738F76CB3783EFE9575DA1B0055A28DA] - (.McAfee, Inc. - SiteAdvisor.) -- C:\Program Files\McAfee\SiteAdvisor\saUI.exe [740360] [PID.1912]
[MD5.31E05F7EC7B334AC0EADAE5663F8F316] - (.Nicolas Coolman - ZHPDiag.) -- C:\Program Files\ZHPDiag\ZHPDiag.exe [8109056] [PID.2928]
~ Processes Running: Scanned in 00mn 01s
---\\ Mozilla Firefox, Plugins,Demarrage,Recherche,Extensions (P2,M0,M1,M2,M3)
C:\Documents and Settings\Antoine David\Application Data\Mozilla\Firefox\Profiles\q2bhqz1j.default-1409559341937\prefs.js
M2 - MFEP: RegExtension {e4f94d1e-2f53-401e-8885-681602c0ddd8} . (...) -- C:\Documents and Settings\All Users\Application Data\McAfee Security Scan\Extensions\{e4f94d1e-2f53-401e-8885-681602c0ddd8}.xpi
M0 - MFSP: prefs.js [Antoine David - q2bhqz1j.default-1409559341937] https://www.google.fr/?gws_rd=ssl
P2 - FPN:Firefox Plugin Navigator . (.DivX, Inc - npdivxplayerplugin.) -- C:\Program Files\Mozilla Firefox\Plugins\npDivxPlayerPlugin.dll
P2 - FPN:Firefox Plugin Navigator . (.Adobe Systems Inc. - Adobe PDF Plug-In For Firefox and Netscape 11.0.8.) -- C:\Program Files\Mozilla Firefox\Plugins\nppdf32.dll
P2 - FPN:Firefox Plugin Navigator . (.Apple Computer, Inc. - The QuickTime Plugin allows you to view a wide variety of multimedia c.) -- C:\Program Files\Mozilla Firefox\Plugins\npqtplugin.dll
P2 - FPN:Firefox Plugin Navigator . (.Apple Computer, Inc. - The QuickTime Plugin allows you to view a wide variety of multimedia c.) -- C:\Program Files\Mozilla Firefox\Plugins\npqtplugin2.dll
P2 - FPN:Firefox Plugin Navigator . (.Apple Computer, Inc. - The QuickTime Plugin allows you to view a wide variety of multimedia c.) -- C:\Program Files\Mozilla Firefox\Plugins\npqtplugin3.dll
P2 - FPN:Firefox Plugin Navigator . (.Apple Computer, Inc. - The QuickTime Plugin allows you to view a wide variety of multimedia c.) -- C:\Program Files\Mozilla Firefox\Plugins\npqtplugin4.dll
P2 - FPN:Firefox Plugin Navigator . (.Apple Computer, Inc. - The QuickTime Plugin allows you to view a wide variety of multimedia c.) -- C:\Program Files\Mozilla Firefox\Plugins\npqtplugin5.dll
P2 - FPN:Firefox Plugin Navigator . (.Apple Computer, Inc. - The QuickTime Plugin allows you to view a wide variety of multimedia c.) -- C:\Program Files\Mozilla Firefox\Plugins\npqtplugin6.dll
P2 - FPN:Firefox Plugin Navigator . (.Apple Computer, Inc. - The QuickTime Plugin allows you to view a wide variety of multimedia c.) -- C:\Program Files\Mozilla Firefox\Plugins\npqtplugin7.dll
P2 - FPN: [HKLM] [@adobe.com/FlashPlayer] - (...) -- C:\WINDOWS\system32\Macromed\Flash\NPSWF32_15_0_0_152.dll
P2 - FPN: [HKLM] [@divx.com/DivX Browser Plugin,version=1.0.0] - (.DivX,Inc. - DivX Web Player version 1.5.0.52.) -- C:\Program Files\DivX\DivX Web Player\npdivx32.dll
P2 - FPN: [HKLM] [@divx.com/DivX Player Plugin,version=1.0.0] - (...) -- C:\Program Files\DivX\DivX Player\npDivxPlayerPlugin.dll (.not file.)
P2 - FPN: [HKLM] [@divx.com/DivX Plus Web Player Plug-In,version=1.0.0] - (.DivX, LLC - DivX Plus Web Player version 2.3.0.87.) -- C:\Program Files\DivX\DivX Plus Web Player\npdivx32.dll
P2 - FPN: [HKLM] [@divx.com/DivX VOD Helper,version=1.0.0] - (.DivX, LLC. - DivX VOD Helper Plug-in.) -- C:\Program Files\DivX\DivX OVS Helper\npovshelper.dll
P2 - FPN: [HKLM] [@java.com/JavaPlugin] - (.Sun Microsystems, Inc. - Next Generation Java Plug-in 1.6.0_26 for Mozilla browsers.) -- C:\Program Files\Java\jre6\bin\new_plugin\npjp2.dll
P2 - FPN: [HKLM] [@mcafee.com/MSC,version=10] - (...) -- C:\Program Files\McAfee\MSC\npMcSnFFPl.dll
P2 - FPN: [HKLM] [@mcafee.com/MVT] - (.McAfee, Inc. - McAfee Virtual Technician plugin.) -- C:\Program Files\McAfee\Supportability\MVT\NPMVTPlugin.dll
P2 - FPN: [HKLM] [@microsoft.com/WPF,version=3.5] - (.Microsoft Corporation - Windows Presentation Foundation (WPF) plug-in for Mozilla browsers.) -- C:\WINDOWS\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\NPWPF.dll
P2 - FPN: [HKLM] [@tools.google.com/Google Update;version=3] - (.Google Inc. - Google Update.) -- C:\Program Files\Google\Update\1.3.24.15\npGoogleUpdate3.dll
P2 - FPN: [HKLM] [@tools.google.com/Google Update;version=9] - (.Google Inc. - Google Update.) -- C:\Program Files\Google\Update\1.3.24.15\npGoogleUpdate3.dll
P2 - FPN: [HKLM] [Adobe Reader] - (.Adobe Systems Inc. - Adobe PDF Plug-In For Firefox and Netscape 11.0.8.) -- C:\Program Files\Adobe\Reader 11.0\Reader\AIR\nppdf32.dll
P2 - FPN: [HKCU] [@adobe.com/FlashPlayer] - (...) -- C:\WINDOWS\system32\Macromed\Flash\NPSWF32.dll (.not file.)
~ Firefox Browser: 24 Scanned in 00mn 02s
---\\ Internet Explorer, Démarrage,Recherche,URLSearchHook, Phishing (R0,R1,R3,R4)
R0 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = about:blank
R0 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = about:blank
R1 - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Extensions Off Page = about:noadd-ons
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Security Risk Page = about:securityrisk
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Search_URL = https://www.microsoft.com/fr-fr/
R1 - HKLM\SOFTWARE\Microsoft\Internet Explorer\AboutURLs,Tabs = res://ieframe.dll/tabswelcome.htm
R3 - URLSearchHook: Microsoft Url Search Hook - {CFBFAE00-17A6-11D0-99CB-00C04FD64497} . (...) (No version) -- (.not file.)
R4 - HKCU\SOFTWARE\Microsoft\Internet Explorer\PhishingFilter,Enabled = 2
~ IE Browser: 11 Scanned in 00mn 00s
---\\ Internet Explorer, Proxy Management (R5)
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = no key
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyEnable = 0
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,MigrateProxy = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,EnableHttp1_1 = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyHttp1.1 = 1
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,AutoConfigProxy = wininet.dll
~ Proxy management: Scanned in 00mn 00s
---\\ Analyse des lignes F0, F1, F2, F3 - IniFiles, Autoloading programs
F2 - REG:system.ini: USERINIT=C:\WINDOWS\system32\userinit.exe,
F2 - REG:system.ini: Shell=C:\WINDOWS\explorer.exe
F2 - REG:system.ini: VMApplet=rundll32 shell32,Control_RunDLL "sysdm.cpl"
~ Keys: Scanned in 00mn 00s
---\\ Hosts file redirection (O1)
~ Le fichier hôte est sain (The hosts file is clean) (20)
~ Hosts File: Scanned in 00mn 00s
---\\ Browser Helper Objects de navigateur (O2)
O2 - BHO: MSS+ Identifier - {0E8A89AD-95D7-40EB-8D9D-083EF7066A01} . (.McAfee, Inc. - Quick Browser Identifier for MSS+ Tool.) -- C:\Program Files\McAfee Security Scan\3.8.150\McAfeeMSS_IE.dll
O2 - BHO: McAfee Phishing Filter - {27B4851A-3207-45A2-B947-BE8AFE6163AB} . (...) -- c:\progra~1\mcafee\msk\mskapbho.dll (.not file.)
O2 - BHO: Increase performance and video formats for your HTML5 <video> - {326E768D-4182-46FD-9C16-1449A49795F4} . (.DivX, LLC - DivX Plus Web Player HTML5 <video> version.) -- C:\Program Files\DivX\DivX Plus Web Player\ie\DivXHTML5\DivXHTML5.dll
O2 - BHO: (no name) - {5C255C8A-E604-49b4-9D64-90988571CECB} Clé orpheline
O2 - BHO: Java(tm) Plug-In SSV Helper - {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} . (.Sun Microsystems, Inc. - Java(TM) Platform SE binary.) -- C:\Program Files\Java\jre6\bin\ssv.dll
O2 - BHO: Programme d'aide de l'Assistant de connexion Windows Live - {9030D464-4C02-4ABF-8ECC-5164760863C6} . (.Microsoft Corporation - WindowsLiveLogin.dll.) -- C:\Program Files\Fichiers communs\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: Google Toolbar Helper - {AA58ED58-01DD-4d91-8333-CF10577473F7} . (.Google Inc. - Google Toolbar.) -- C:\Program Files\Google\Google Toolbar\GoogleToolbar_32.dll
O2 - BHO: Google Toolbar Notifier BHO - {AF69DE43-7D58-4638-B6FA-CE66B5AD205D} . (.Google Inc. - GoogleToolbarNotifier.) -- C:\Program Files\Google\GoogleToolbarNotifier\5.7.9012.1008\swg.dll
O2 - BHO: McAfee SiteAdvisor BHO - {B164E929-A1B6-4A06-B104-2CD0E90A88FF} . (.McAfee, Inc. - SiteAdvisor.) -- C:\Program Files\McAfee\SiteAdvisor\McIEPlg.dll
O2 - BHO: Free Download Manager - {CC59E0F9-7E43-44FA-9FAA-8377850BF205} . (.FreeDownloadManager.ORG - Pas de description.) -- C:\Program Files\Free Download Manager\iefdm2.dll
O2 - BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} . (.Sun Microsystems, Inc. - Java(TM) Platform SE binary.) -- C:\Program Files\Java\jre6\bin\jp2ssv.dll
O2 - BHO: JQSIEStartDetectorImpl - {E7E6F031-17CE-4C07-BC86-EABFE594F69C} . (.Sun Microsystems, Inc. - Java(TM) Quick Starter binary.) -- C:\Program Files\Java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
~ BHO: 24 Scanned in 00mn 00s
---\\ Internet Explorer Toolbars (O3)
O3 - Toolbar: Google Toolbar - [HKLM]{2318C2B1-4965-11d4-9B18-009027A5CD4F} . (.Google Inc. - Google Toolbar.) -- C:\Program Files\Google\Google Toolbar\GoogleToolbar_32.dll
O3 - Toolbar: McAfee SiteAdvisor Toolbar - [HKLM]{0EBBBE48-BAD4-4B4C-8E5A-516ABECAE064} . (.McAfee, Inc. - SiteAdvisor.) -- C:\Program Files\McAfee\SiteAdvisor\McIEPlg.dll
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{2318C2B1-4965-11D4-9B18-009027A5CD4F} Clé orpheline
~ Toolbar: Scanned in 00mn 00s
---\\ Autres liens utilisateurs (O4)
O4 - GS\Program [AllUsers]: Vuze.lnk . (.Azureus Software, Inc - Vuze Launcher.) -- C:\Program Files\Vuze\Azureus.exe =>P2P.Azureus
~ Global Startup: 1 Scanned in 00mn 01s
---\\ Applications lancées au démarrage du système (O4)
O4 - HKLM\..\Run: [UIUCU] . (.Conexant Systems, Inc. - Conexant Universal Device Install/Uninstall.) -- C:\Documents and Settings\Antoine David\Local Settings\Temp\UIUCU.exe
O4 - HKLM\..\Run: [SigmatelSysTrayApp] . (.SigmaTel, Inc. - Sigmatel Audio system tray application.) -- C:\WINDOWS\stsystra.exe
O4 - HKLM\..\Run: [QuickTime Task] . (.Apple Computer, Inc. - QuickTime Task.) -- C:\Program Files\QuickTime\qttask.exe
O4 - HKLM\..\Run: [NeroFilterCheck] . (.Ahead Software Gmbh - NeroCheck.) -- C:\WINDOWS\system32\NeroCheck.exe
O4 - HKLM\..\Run: [HP Software Update] . (.Hewlett-Packard - hpwuSchd Application.) -- C:\Program Files\HP\HP Software Update\HPWuSchd2.exe =>.Hewlett-Packard Co
O4 - HKLM\..\Run: [DivXMediaServer] . (.DivX, LLC - DivX DLNA Media Server.) -- C:\Program Files\DivX\DivX Media Server\DivXMediaServer.exe
O4 - HKLM\..\Run: [DivXUpdate] . (.Pas de propriétaire - DivX Update.) -- C:\Program Files\DivX\DivX Update\DivXUpdate.exe
O4 - HKLM\..\Run: [Adobe ARM] . (.Adobe Systems Incorporated - Adobe Reader and Acrobat Manager.) -- C:\Program Files\Fichiers communs\Adobe\ARM\1.0\AdobeARM.exe =>.Adobe Systems Incorporated
O4 - HKLM\..\Run: [SunJavaUpdateSched] . (.Oracle Corporation - Java(TM) Update Scheduler.) -- C:\Program Files\Fichiers communs\Java\Java Update\jusched.exe =>.Oracle Corporation
O4 - HKLM\..\Run: [mcpltui_exe] . (.McAfee, Inc. - McAfee Security Center.) -- C:\Program Files\McAfee.com\Agent\mcagent.exe
O4 - HKCU\..\Run: [ctfmon.exe] . (.Microsoft Corporation - CTF Loader.) -- C:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [swg] . (.Google Inc. - GoogleToolbarNotifier.) -- C:\Program Files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe
O4 - HKUS\S-1-5-21-842925246-616249376-839522115-1003\..\Run: [ctfmon.exe] . (.Microsoft Corporation - CTF Loader.) -- C:\WINDOWS\system32\ctfmon.exe
O4 - HKUS\S-1-5-21-842925246-616249376-839522115-1003\..\Run: [swg] . (.Google Inc. - GoogleToolbarNotifier.) -- C:\Program Files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe
~ Application: Scanned in 00mn 00s
---\\ Boutons situés sur la barre d'outils principale d'Internet Explorer (O9)
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} . (...) -- C:\Program Files\Microsoft Office\Office12\REFBARH.ICO
O9 - Extra button: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} -- Clé orpheline
O9 - Extra button: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} . (.Microsoft Corporation - Windows Messenger.) -- C:\Program Files\Messenger\msmsgs.exe
~ IE Extra Buttons: Scanned in 00mn 00s
---\\ Winsock hijacker (Layered Service Provider) (O10)
O10 - WLSP:\000000000001\Winsock LSP File . (.Microsoft Corporation - Fournisseur de service Sockets 2.0 de Microsoft Windows.) -- C:\WINDOWS\system32\mswsock.dll =>.Microsoft Corporation
O10 - WLSP:\000000000002\Winsock LSP File . (.Microsoft Corporation - LDAP RnR Provider DLL.) -- C:\WINDOWS\system32\winrnr.dll
O10 - WLSP:\000000000003\Winsock LSP File . (.Microsoft Corporation - Fournisseur de service Sockets 2.0 de Microsoft Windows.) -- C:\WINDOWS\system32\mswsock.dll =>.Microsoft Corporation
~ Winsock: 3 Scanned in 00mn 00s
---\\ Objets ActiveX (Downloaded Program Files)(O16)
O16 - DPF: {6414512B-B978-451D-A0D8-FCFDF33E833C} ((no name)) - http://www.update.microsoft.com/windowsupdate/v6/V5Controls/en/x86/client/wuweb_site.cab?1206798237167
O16 - DPF: {917623D1-D8E5-11D2-BE8B-00104B06BDE3} ((no name)) - http://www.airport-nuernberg.de/_/tools/AxisCamControl.cab
O16 - DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} ((no name)) - http://fpdownload2.macromedia.com/get/shockwave/cabs/flash/swflash.cab
~ Objets ActiveX: Scanned in 00mn 00s
---\\ Modification Domaine/Adresses DNS (O17)
O17 - HKLM\System\CCS\Services\Tcpip\..\{A554670B-84A7-43F4-942F-6B03FE9F0B1E}: DhcpNameServer = 192.168.1.1 192.168.1.1
O17 - HKLM\System\CS1\Services\Tcpip\..\{A554670B-84A7-43F4-942F-6B03FE9F0B1E}: DhcpNameServer = 192.168.1.1 192.168.1.1
O17 - HKLM\System\CS3\Services\Tcpip\..\{A554670B-84A7-43F4-942F-6B03FE9F0B1E}: DhcpNameServer = 192.168.1.1 192.168.1.1
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = 192.168.1.1 192.168.1.1
~ Domain: Scanned in 00mn 00s
---\\ Protocole additionnel (O18)
O18 - Handler: wia - {13F3EA8B-91D7-4F0A-AD76-D2853AC8BECE} . (.Microsoft Corporation - WIA Scripting Layer.) -- C:\WINDOWS\system32\wiascr.dll
O18 - Filter: text/xml - {807563E5-5146-11D5-A672-00B0D022E945} . (.Microsoft Corporation - Microsoft Office XML MIME Filter.) -- C:\Program Files\Fichiers communs\Microsoft Shared\OFFICE12\MSOXMLMF.dll =>.Microsoft Corporation
~ Protocole Additionnel: Scanned in 00mn 00s
---\\ Valeur de Registre AppInit_DLLs et sous-clés Winlogon Notify (autorun) (O20)
O20 - Winlogon Notify: crypt32chain . (.Microsoft Corporation - Crypto API32.) -- C:\WINDOWS\system32\crypt32.dll
O20 - Winlogon Notify: cryptnet . (.Microsoft Corporation - Crypto Network Related API.) -- C:\WINDOWS\system32\cryptnet.dll
O20 - Winlogon Notify: cscdll . (.Microsoft Corporation - Agent réseau hors connexion.) -- C:\WINDOWS\system32\cscdll.dll
O20 - Winlogon Notify: dimsntfy . (.Microsoft Corporation - DIMS Notification Handler.) -- C:\WINDOWS\system32\dimsntfy.dll
O20 - Winlogon Notify: ScCertProp . (.Microsoft Corporation - DLL commune de réception des notifications.) -- C:\WINDOWS\system32\wlnotify.dll
O20 - Winlogon Notify: Schedule . (.Microsoft Corporation - DLL commune de réception des notifications.) -- C:\WINDOWS\system32\wlnotify.dll
O20 - Winlogon Notify: sclgntfy . (.Microsoft Corporation - DLL secondaire de notification de service d.) -- C:\WINDOWS\system32\sclgntfy.dll
O20 - Winlogon Notify: SensLogn . (.Microsoft Corporation - DLL commune de réception des notifications.) -- C:\WINDOWS\system32\WlNotify.dll
O20 - Winlogon Notify: termsrv . (.Microsoft Corporation - DLL commune de réception des notifications.) -- C:\WINDOWS\system32\wlnotify.dll
O20 - Winlogon Notify: WgaLogon . (.Microsoft Corporation - Notifications Windows Genuine Advantage.) -- C:\WINDOWS\system32\WgaLogon.dll
O20 - Winlogon Notify: wlballoon . (.Microsoft Corporation - DLL commune de réception des notifications.) -- C:\WINDOWS\system32\wlnotify.dll
~ Winlogon: Scanned in 00mn 00s
---\\ Clé de Registre autorun ShellServiceObjectDelayLoad (SSO/SSODL) (O21)
O21 - SSODL: PostBootReminder - {7849596a-48ea-486e-8937-a2a3009f31a9} . (.Microsoft Corporation - DLL commune du shell Windows.) -- C:\WINDOWS\system32\SHELL32.dll
O21 - SSODL: CDBurn - {fbeb8a05-beee-4442-804e-409d6c4515e9} . (.Microsoft Corporation - DLL commune du shell Windows.) -- C:\WINDOWS\system32\SHELL32.dll
O21 - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} . (.Microsoft Corporation - Web Site Monitor.) -- C:\WINDOWS\system32\webcheck.dll
O21 - SSODL: SysTray - {35CEC8A3-2BE6-11D2-8773-92E220524153} . (.Microsoft Corporation - Objet du service d'environnement Systray.) -- C:\WINDOWS\system32\stobject.dll
O21 - SSODL: WPDShServiceObj - {AAA288BA-9A4C-45B0-95D7-94D524869DB5} . (.Microsoft Corporation - Windows Portable Device Shell Service Objec.) -- C:\WINDOWS\system32\WPDShServiceObj.dll
~ SSODL: 5 Scanned in 00mn 00s
---\\ Liste des services NT non Microsoft et non désactivés (O23)
O23 - Service: (Ati HotKey Poller) . (.ATI Technologies Inc. - ATI External Event Utility EXE Module.) - C:\WINDOWS\system32\Ati2evxx.exe
O23 - Service: ATI Smart (ATI Smart) . (.Pas de propriétaire - ATI Smart.) - C:\WINDOWS\system32\ati2sgag.exe
O23 - Service: Service Google Update (gupdate) (gupdate) . (.Google Inc. - Programme d'installation de Google.) - C:\Program Files\Google\Update\GoogleUpdate.exe =>.Google Inc
O23 - Service: McAfee Home Network (HomeNetSvc) . (.McAfee, Inc. - McAfee Service Host.) - C:\Program Files\Fichiers communs\Mcafee\Platform\McSvcHost\McSvHost.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) . (.Sun Microsystems, Inc. - Java(TM) Quick Starter Service.) - C:\Program Files\Java\jre6\bin\jqs.exe
O23 - Service: McAfee SiteAdvisor Service (McAfee SiteAdvisor Service) . (.McAfee, Inc. - McAfee Service Host.) - C:\Program Files\Fichiers communs\Mcafee\Platform\McSvcHost\McSvHost.exe
O23 - Service: McAfee AP Service (McAPExe) . (.McAfee, Inc. - McAfee Access Protection.) - C:\Program Files\McAfee\MSC\McAPexe.exe
O23 - Service: McAfee Personal Firewall Service (McMPFSvc) . (.McAfee, Inc. - McAfee Service Host.) - C:\Program Files\Fichiers communs\Mcafee\Platform\McSvcHost\McSvHost.exe
O23 - Service: McAfee VirusScan Announcer (McNaiAnn) . (.McAfee, Inc. - McAfee Service Host.) - C:\Program Files\Fichiers communs\McAfee\Platform\McSvcHost\McSvHost.exe
O23 - Service: McAfee Platform Services (mcpltsvc) . (.McAfee, Inc. - McAfee Service Host.) - C:\Program Files\Fichiers communs\McAfee\Platform\McSvcHost\McSvHost.exe
O23 - Service: McAfee Proxy Service (McProxy) . (.McAfee, Inc. - McAfee Service Host.) - C:\Program Files\Fichiers communs\McAfee\Platform\McSvcHost\McSvHost.exe
O23 - Service: McAfee Anti-Malware Core (mfecore) . (.McAfee, Inc. - McAfee On-Access Scanner service.) - C:\Program Files\Fichiers communs\McAfee\AMCore\mcshield.exe
O23 - Service: McAfee Firewall Core Service (mfefire) . (.McAfee, Inc. - McAfee Core Firewall Service.) - C:\Program Files\Fichiers communs\McAfee\SystemCore\mfefire.exe
O23 - Service: McAfee Validation Trust Protection Service (mfevtp) . (.McAfee, Inc. - McAfee Process Validation Service.) - C:\WINDOWS\system32\mfevtps.exe
O23 - Service: McAfee Anti-Spam Service (MSK80Service) . (.McAfee, Inc. - McAfee Service Host.) - C:\Program Files\Fichiers communs\Mcafee\Platform\McSvcHost\McSvHost.exe
O23 - Service: Pml Driver HPZ12 (Pml Driver HPZ12) . (.HP - PML Driver.) - C:\WINDOWS\system32\HPZipm12.exe
O23 - Service: Skype Updater (SkypeUpdate) . (.Skype Technologies - Skype Updater Service.) - C:\Program Files\Skype\Updater\Updater.exe
~ Services: 17 Scanned in 00mn 06s
---\\ Enumération Active Desktop & MHTML Editor (O24)
O24 - Default MHTML Editor: Last - .(...) - (.not file.)
O24 - Desktop General: BackupWallPaper - .(...) - C:\WINDOWS\web\wallpaper\Colline verdoyante.bmp
O24 - Desktop General: WallPaper - .(...) - C:\WINDOWS\web\wallpaper\Colline verdoyante.bmp
~ Desktop Component: 4 Scanned in 00mn 00s
---\\ Enumère les données de BootExecute (BEX) (O34)
O34 - HKLM BootExecute: (autocheck autochk *) - File not found
~ BEX: 1 Scanned in 00mn 00s
---\\ Tâches planifiées en automatique (O39)
[MD5.4ECFCAAE5CB380F58934F0DCF5F64E7F] [APT] [Adobe Flash Player Updater] (.Adobe Systems Incorporated.) -- C:\WINDOWS\system32\Macromed\Flash\FlashPlayerUpdateService.exe [267440]
[MD5.ACCF8BABEBB0EADE39B372D0DA330879] [APT] [AppleSoftwareUpdate] (.Apple Computer, Inc..) -- C:\Program Files\Apple Software Update\SoftwareUpdate.exe [681568]
[MD5.8F0DE4FEF8201E306F9938B0905AC96A] [APT] [GoogleUpdateTaskMachineCore] (.Google Inc..) -- C:\Program Files\Google\Update\GoogleUpdate.exe [135664]
[MD5.8F0DE4FEF8201E306F9938B0905AC96A] [APT] [GoogleUpdateTaskMachineUA] (.Google Inc..) -- C:\Program Files\Google\Update\GoogleUpdate.exe [135664]
O39 - APT: Adobe Flash Player Updater - (.Adobe Systems Incorporated.) -- C:\WINDOWS\Tasks\Adobe Flash Player Updater.job [1002]
O39 - APT: AppleSoftwareUpdate - (.Apple Computer, Inc..) -- C:\WINDOWS\Tasks\AppleSoftwareUpdate.job [284]
O39 - APT: GoogleUpdateTaskMachineCore - (.Google Inc..) -- C:\WINDOWS\Tasks\GoogleUpdateTaskMachineCore.job [1066]
O39 - APT: GoogleUpdateTaskMachineUA - (.Google Inc..) -- C:\WINDOWS\Tasks\GoogleUpdateTaskMachineUA.job [1070]
O39 - APT: - (..) -- C:\WINDOWS\Tasks\Notification de fin de service de Microsoft Windows XP - à la connexion.job [238]
O39 - APT: - (..) -- C:\WINDOWS\Tasks\Notification de fin de service de Microsoft Windows XP -mensuellement.job [232]
O39 - APT: - (..) -- C:\WINDOWS\Tasks\User_Feed_Synchronization-{C862192C-7F85-4D87-A44B-0E331419D44E}.job [448]
~ Scheduled Task: 12 Scanned in 00mn 00s
---\\ Composants installés (ActiveSetup Installed Components) (O40)
O40 - ASIC: Mise à jour de la version d'Internet Explorer - <{12d0ed0d-0ee0-4f90-8827-78cefb8f4988} . (.Microsoft Corporation - IE Per User Active Setup Uninstall Utility.) -- C:\WINDOWS\system32\ieudinit.exe
O40 - ASIC: Microsoft Windows Media Player - >{22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Utilitaire d'installation du Lecteur Windows Media de Microsoft.) -- C:\WINDOWS\inf\unregmp2.exe =>.Microsoft Corporation
O40 - ASIC: Internet Explorer - >{26923b43-4d38-484f-9b9e-de460746276c} . (.Microsoft Corporation - Utilitaire d'initialisation d'Internet Explorer par utilisateur.) -- C:\WINDOWS\system32\ie4uinit.exe.mui
O40 - ASIC: Browser Customizations - >{60B49E34-C7CC-11D0-8953-00A0C90347FF} . (.Microsoft Corporation - IEAK branding.) -- C:\WINDOWS\system32\iedkcs32.dll
O40 - ASIC: Outlook Express - >{881dd1c5-3dcf-431b-b061-f3f88e8be88a} . (.Microsoft Corporation - Windows NT User Data Migration Tool.) -- C:\WINDOWS\system32\shmgrate.exe =>.Microsoft Corporation
O40 - ASIC: Java (Sun) - {08B0E5C0-4FCB-11CF-AAA5-00401C608500} . (.Sun Microsystems, Inc. - Java(TM) Platform SE binary.) -- C:\Program Files\Java\jre6\bin\regutils.dll
O40 - ASIC: Microsoft NetShow Player - {2179C5D3-EBFF-11CF-B6FD-00AA00B4E220} . (.Microsoft Corporation - Windows Media Player Extension.) -- C:\WINDOWS\system32\wmpdxm.dll =>.Microsoft Corporation
O40 - ASIC: Microsoft Windows Media Player 6.4 - {22d6f312-b0f6-11d0-94ab-0080c74c7e95} . (.Microsoft Corporation - Windows Media Player Extension.) -- C:\WINDOWS\system32\wmpdxm.dll =>.Microsoft Corporation
O40 - ASIC: Themes Setup - {2C7339CF-2B09-4501-B3F3-F3508C9228ED} . (.Microsoft Corporation - API Windows Theme.) -- C:\WINDOWS\system32\themeui.dll
O40 - ASIC: Microsoft Outlook Express 6 - {44BBA840-CC51-11CF-AAFA-00AA00B6015C} . (.Microsoft Corporation - Bibliothèque d'installation Outlook Express.) -- C:\Program Files\Outlook Express\setup50.exe =>.Microsoft Corporation
O40 - ASIC: NetMeeting 3.01 - {44BBA842-CC51-11CF-AAFA-00AA00B6015B} . (...) -- C:\WINDOWS\INF\msnetmtg.inf
O40 - ASIC: Windows Messenger 4.7 - {5945c046-1e7d-11d1-bc44-00c04fd912be} . (...) -- C:\WINDOWS\INF\msmsgs.inf
O40 - ASIC: Browsing Enhancements - {630b1da0-b465-11d1-9948-00c04f98bbc9} . (.Microsoft Corporation - Extension Shell dossier FTP Microsoft Internet Explorer..) -- C:\WINDOWS\system32\msieftp.dll
O40 - ASIC: Microsoft Windows Media Player - {6BF52A52-394A-11d3-B153-00C04F79FAA6} . (...) -- C:\WINDOWS\INF\wmp11.inf =>.Microsoft Corporation
O40 - ASIC: Carnet d'adresses 6 - {7790769C-0471-11d2-AF11-00C04FA35D02} . (.Microsoft Corporation - Bibliothèque d'installation Outlook Express.) -- C:\Program Files\Outlook Express\setup50.exe =>.Microsoft Corporation
O40 - ASIC: Mise à jour du Bureau Windows - {89820200-ECBD-11cf-8B85-00AA005B4340} . (.Microsoft Corporation - DLL commune du shell Windows.) -- C:\WINDOWS\system32\shell32.dll
O40 - ASIC: Internet Explorer - {89820200-ECBD-11cf-8B85-00AA005B4383} . (.Microsoft Corporation - Utilitaire d'initialisation d'Internet Explorer par utilisateur.) -- C:\WINDOWS\system32\ie4uinit.exe.mui
O40 - ASIC: (no name) - {89B4C1CD-B018-4511-B0A1-5476DBF70820} . (.Microsoft Corporation - Microsoft .NET IE SECURITY REGISTRATION.) -- C:\WINDOWS\system32\mscories.dll
O40 - ASIC: Adobe Flash Player - {D27CDB6E-AE6D-11cf-96B8-444553540000} . (.Adobe Systems, Inc. - Adobe Flash Player 15.0 r0.) -- C:\WINDOWS\system32\Macromed\Flash\Flash32_15_0_0_167.ocx
O40 - ASIC: Installed Component - S-1-5-21-842925246-616249376-839522115-1003 - <{12d0ed0d-0ee0-4f90-8827-78cefb8f4988} -- Not Hexadécimal CLSID
O40 - ASIC: Installed Component - S-1-5-21-842925246-616249376-839522115-1003 - >{60B49E34-C7CC-11D0-8953-00A0C90347FF}MICROS -- Not Hexadécimal CLSID
~ Active Setup: 21 Scanned in 00mn 01s
---\\ Pilotes lancés au démarrage du système (O41)
O41 - Driver: (AFD) . (.Microsoft Corporation - Ancillary Function Driver for WinSock.) - C:\WINDOWS\system32\drivers\afd.sys
O41 - Driver: (Cdrom) . (.Microsoft Corporation - SCSI CD-ROM Driver.) - C:\WINDOWS\system32\DRIVERS\cdrom.sys
O41 - Driver: (Imapi) . (.Microsoft Corporation - IMAPI Kernel Driver.) - C:\WINDOWS\system32\DRIVERS\imapi.sys
O41 - Driver: (intelppm) . (.Microsoft Corporation - Pilote de périphérique processeur.) - C:\WINDOWS\system32\DRIVERS\intelppm.sys
O41 - Driver: (IPSec) . (.Microsoft Corporation - IPSec Driver.) - C:\WINDOWS\system32\DRIVERS\ipsec.sys
O41 - Driver: (Kbdclass) . (.Microsoft Corporation - Pilote de la classe Clavier.) - C:\WINDOWS\system32\DRIVERS\kbdclass.sys
O41 - Driver: (kbdhid) . (.Microsoft Corporation - Pilote de filtre souris HID.) - C:\WINDOWS\system32\DRIVERS\kbdhid.sys
O41 - Driver: McAfee Inc. mfetdi2k (mfetdi2k) . (.McAfee, Inc. - Anti-Virus Mini-Firewall Driver.) - C:\WINDOWS\system32\drivers\mfetdi2k.sys
O41 - Driver: (Mouclass) . (.Microsoft Corporation - Pilote de la classe Souris.) - C:\WINDOWS\system32\DRIVERS\mouclass.sys
O41 - Driver: (MRxSmb) . (.Microsoft Corporation - Windows NT SMB Minirdr.) - C:\WINDOWS\system32\DRIVERS\mrxsmb.sys
O41 - Driver: (NetBIOS) . (.Microsoft Corporation - NetBIOS interface driver.) - C:\WINDOWS\system32\DRIVERS\netbios.sys
O41 - Driver: (NetBT) . (.Microsoft Corporation - MBT Transport driver.) - C:\WINDOWS\system32\DRIVERS\netbt.sys
O41 - Driver: (OMCI) . (. - .) - C:\WINDOWS\sysTEM32\DRIVERS\OMCI.sys (.not file.)
O41 - Driver: (RasAcd) . (.Microsoft Corporation - RAS Automatic Connection Driver.) - C:\WINDOWS\system32\DRIVERS\rasacd.sys
O41 - Driver: (Rdbss) . (.Microsoft Corporation - Redirected Drive Buffering SubSystem Driver.) - C:\WINDOWS\system32\DRIVERS\rdbss.sys
O41 - Driver: (RDPCDD) . (.Microsoft Corporation - RDP Miniport.) - C:\WINDOWS\system32\DRIVERS\RDPCDD.sys
O41 - Driver: (redbook) . (.Microsoft Corporation - Pilote de filtre audio Livre rouge.) - C:\WINDOWS\system32\DRIVERS\redbook.sys
O41 - Driver: (Tcpip) . (.Microsoft Corporation - TCP/IP Protocol Driver.) - C:\WINDOWS\system32\DRIVERS\tcpip.sys
O41 - Driver: (TermDD) . (.Microsoft Corporation - Terminal Server Driver.) - C:\WINDOWS\system32\DRIVERS\termdd.sys
O41 - Driver: Carte vidéo VGA. (VgaSave) . (.Microsoft Corporation - VGA/Super VGA Video Driver.) - C:\WINDOWS\system32\drivers\vga.sys
~ Drivers: 60 Scanned in 00mn 01s
---\\ Logiciels installés (O42)
O42 - Logiciel: ATI - Utilitaire de désinstallation du logiciel - (...) [HKLM] -- All ATI Software
O42 - Logiciel: ATI Display Driver - (...) [HKLM] -- ATI Display Driver
O42 - Logiciel: Adobe AIR - (.Adobe Systems Incorporated.) [HKLM] -- Adobe AIR
O42 - Logiciel: Adobe AIR - (.Adobe Systems Incorporated.) [HKLM] -- {7BBAEC47-1CC0-4CB8-ADB4-531B78DBD1DD}
O42 - Logiciel: Adobe Flash Player 15 ActiveX - (.Adobe Systems Incorporated.) [HKLM] -- Adobe Flash Player ActiveX
O42 - Logiciel: Adobe Flash Player 15 Plugin - (.Adobe Systems Incorporated.) [HKLM] -- Adobe Flash Player Plugin
O42 - Logiciel: Adobe Reader XI (11.0.08) - Français - (.Adobe Systems Incorporated.) [HKLM] -- {AC76BA86-7AD7-1036-7B44-AB0000000001}
O42 - Logiciel: Apple Software Update - (.Apple Computer, Inc..) [HKLM] -- {A260B422-70E1-41E2-957D-F76FA21266D5} =>.Apple Inc
O42 - Logiciel: Archiveur WinRAR - (...) [HKLM] -- WinRAR archiver
O42 - Logiciel: Bayam 3-7 - (.Bayard Presse.) [HKLM] -- bayardKids.08AE7BFC096D057FBA48C7E4F898C35F7FA11BBA.1
O42 - Logiciel: Bayam 3-7 - (.Bayard Presse.) [HKLM] -- {4B5FD0DF-6577-CD51-C502-A940408622E1}
O42 - Logiciel: Blood Ties - (...) [HKLM] -- {472A443D-1CE3-4E52-92E3-E391A67C6B64}
O42 - Logiciel: CCleaner - (.Piriform.) [HKLM] -- CCleaner
O42 - Logiciel: Choice Guard - (.Microsoft Corporation.) [HKLM] -- {8FFC5648-FAF8-43A3-BC8F-42BA1E275C4E}
O42 - Logiciel: Configuration DivX - (.DivX, LLC.) [HKLM] -- DivX Setup
O42 - Logiciel: ConvertXtoDVD 3.3.0.96 - (...) [HKLM] -- {76C24F39-B161-498F-BD8B-C64789812D13}_is1
O42 - Logiciel: Creative WebCam Pro Driver - (...) [HKLM] -- Creative WebCam Pro
O42 - Logiciel: Dell Resource CD - (.Dell Inc..) [HKLM] -- {FCD9CD52-7222-4672-94A0-A722BA702FD0}
O42 - Logiciel: DivX Converter - (.DivX, Inc..) [HKLM] -- {B13A7C41581B411290FBC0395694E2A9}
O42 - Logiciel: DivX Plus DirectShow Filters - (.DivX, Inc..) [HKLM] -- DivX Plus DirectShow Filters
O42 - Logiciel: DivX Web Player - (.DivX,Inc..) [HKLM] -- {B7050CBDB2504B34BC2A9CA0A692CC29}
O42 - Logiciel: Free Download Manager 3.9.2 - (.FreeDownloadManager.ORG.) [HKLM] -- Free Download Manager_is1
O42 - Logiciel: Google Toolbar for Internet Explorer - (.Google Inc..) [HKLM] -- {18455581-E099-4BA8-BC6B-F34B2F06600C}
O42 - Logiciel: Google Toolbar for Internet Explorer - (.Google Inc..) [HKLM] -- {2318C2B1-4965-11d4-9B18-009027A5CD4F}
O42 - Logiciel: Google Update Helper - (.Google Inc..) [HKLM] -- {A92DAB39-4E2C-4304-9AB6-BC44E68B55E2}
O42 - Logiciel: Governor of Poker - (.Adnan_Boy 2008.) [HKLM] -- Governor of Poker1.0
O42 - Logiciel: HP Extended Capabilities 4.7 - (.HP.) [HKLM] -- HPExtendedCapabilities
O42 - Logiciel: HP Image Zone 4.7 - (.HP.) [HKLM] -- HP Photo & Imaging
O42 - Logiciel: HP PSC & OfficeJet 4.7 - (.HP.) [HKLM] -- {342C7C88-D335-4bc2-8CF1-281857629CE2}
O42 - Logiciel: HP Product Assistant - (.Hewlett-Packard.) [HKLM] -- {36FDBE6E-6684-462B-AE98-9A39A1B200CC}
O42 - Logiciel: HP Update - (.Hewlett-Packard.) [HKLM] -- {B0069CFA-5BB9-4C03-B1C6-89CE290E5AFE}
O42 - Logiciel: High Definition Audio Driver Package - KB835221 - (.Microsoft Corporation.) [HKLM] -- KB835221WXP
O42 - Logiciel: Hotfix for Windows Media Format 11 SDK (KB929399) - (.Microsoft Corporation.) [HKLM] -- KB929399
O42 - Logiciel: Hotfix for Windows XP (KB954550-v5) - (.Microsoft Corporation.) [HKLM] -- KB954550-v5
O42 - Logiciel: Hotfix for Windows XP (KB976002-v5) - (.Microsoft Corporation.) [HKLM] -- KB976002-v5
O42 - Logiciel: Intel(R) PRO Network Connections Drivers - (...) [HKLM] -- PROSet
O42 - Logiciel: Iomega Product Registration - (.Iomega Corporation.) [HKLM] -- {90FF23FE-0E1B-40DF-A22E-B4C0372E5936}
O42 - Logiciel: Java 7 Update 25 - (.Oracle.) [HKLM] -- {26A24AE4-039D-4CA4-87B4-2F83217025FF}
O42 - Logiciel: Java(TM) 6 Update 26 - (.Sun Microsystems, Inc..) [HKLM] -- {26A24AE4-039D-4CA4-87B4-2F83216011FF}
O42 - Logiciel: Java(TM) 6 Update 7 - (.Sun Microsystems, Inc..) [HKLM] -- {3248F0A8-6813-11D6-A77B-00B0D0160070}
O42 - Logiciel: Le Mystère de la Mary Celeste - (...) [HKLM] -- {396BD340-D9D6-4361-AA94-0E4F1FFBA4F3}
O42 - Logiciel: Lecteur Windows Media 11 - (...) [HKLM] -- Windows Media Player =>.Microsoft Corporation
O42 - Logiciel: MSN - (...) [HKLM] -- MSNINST
O42 - Logiciel: MSVCRT - (.Microsoft.) [HKLM] -- {22B775E7-6C42-4FC5-8E10-9A5E3257BD94}
O42 - Logiciel: MSXML 4.0 SP2 (KB936181) - (.Microsoft Corporation.) [HKLM] -- {C04E32E0-0416-434D-AFB9-6969D703A9EF}
O42 - Logiciel: MSXML 4.0 SP2 (KB954430) - (.Microsoft Corporation.) [HKLM] -- {86493ADD-824D-4B8E-BD72-8C5DCDC52A71}
O42 - Logiciel: MSXML 4.0 SP2 (KB973688) - (.Microsoft Corporation.) [HKLM] -- {F662A8E6-F4DC-41A2-901E-8C11F044BDEC}
O42 - Logiciel: McAfee Security Scan Plus - (.McAfee, Inc..) [HKLM] -- McAfee Security Scan
O42 - Logiciel: McAfee SecurityCenter - (.McAfee, Inc..) [HKLM] -- MSC
O42 - Logiciel: McAfee Virtual Technician - (.McAfee, Inc..) [HKLM] -- McAfee Virtual Technician
O42 - Logiciel: Microsoft Compression Client Pack 1.0 for Windows XP - (.Microsoft Corporation.) [HKLM] -- MSCompPackV1
O42 - Logiciel: Microsoft Internationalized Domain Names Mitigation APIs - (.Microsoft Corporation.) [HKLM] -- IDNMitigationAPIs
O42 - Logiciel: Microsoft National Language Support Downlevel APIs - (.Microsoft Corporation.) [HKLM] -- NLSDownlevelMapping
O42 - Logiciel: Microsoft User-Mode Driver Framework Feature Pack 1.0 - (.Microsoft Corporation.) [HKLM] -- Wudf01000
O42 - Logiciel: Mozilla Firefox 32.0.3 (x86 fr) - (.Mozilla.) [HKLM] -- Mozilla Firefox 32.0.3 (x86 fr)
O42 - Logiciel: Mozilla Maintenance Service - (.Mozilla.) [HKLM] -- MozillaMaintenanceService
O42 - Logiciel: Myst V End Of Ages - (...) [HKLM] -- 1947ed9c549f680a9ed3f1fdbb9337a4
O42 - Logiciel: NVIDIA Drivers - (...) [HKLM] -- NVIDIA Drivers
O42 - Logiciel: Nero Suite - (...) [HKLM] -- NeroMultiInstaller!UninstallKey
O42 - Logiciel: Nostradamus - (.Microids.) [HKLM] -- Nostradamus
O42 - Logiciel: OpenOffice.org Installer 1.0 - (.Sun Microsystems.) [HKLM] -- {3A2AF807-9F9F-43C9-A24A-17B617238B74}
O42 - Logiciel: Playlist tool - (.IOMEGA .) [HKLM] -- {2C4A5877-21D1-4A15-9D20-24BA54A24093}
O42 - Logiciel: QuickTime - (.Apple Computer, Inc..) [HKLM] -- {5E863175-E85D-44A6-8968-82507D34AE7F}
O42 - Logiciel: REALTEK Wireless LAN Driver and Utility - (...) [HKLM] -- {9C049499-055C-4a0c-A916-1D8CA1FF45EB}
O42 - Logiciel: Security Update for CAPICOM (KB931906) - (.Microsoft Corporation.) [HKLM] -- KB931906
O42 - Logiciel: Security Update for CAPICOM (KB931906) - (.Microsoft Corporation.) [HKLM] -- {0EFDF2F9-836D-4EB7-A32D-038BD3F1FB2A}
O42 - Logiciel: Segoe UI - (.Microsoft Corp.) [HKLM] -- {A1F66FC9-11EE-4F2F-98C9-16F8D1E69FB7}
O42 - Logiciel: SigmaTel Audio - (.SigmaTel.) [HKLM] -- {A462213D-EED4-42C2-9A60-7BDD4D4B0B17}
O42 - Logiciel: Skype(TM) 6.11 - (.Skype Technologies S.A..) [HKLM] -- {4E76FF7E-AEBA-4C87-B788-CD47E5425B9D}
O42 - Logiciel: The Last Express - (...) [HKLM] -- The Last Express
O42 - Logiciel: VC80CRTRedist - 8.0.50727.6195 - (.DivX, Inc.) [HKLM] -- {933B4015-4618-4716-A828-5289FC03165F}
O42 - Logiciel: VLC media player 1.1.0 - (.VideoLAN.) [HKLM] -- VLC media player =>.VideoLAN
O42 - Logiciel: Vuze - (.Azureus Software, Inc..) [HKLM] -- 8461-7759-5462-8226 =>P2P.Azureus
O42 - Logiciel: Windows Genuine Advantage Notifications (KB905474) - (.Microsoft Corporation.) [HKLM] -- WgaNotify
O42 - Logiciel: Windows Genuine Advantage Validation Tool (KB892130) - (.Microsoft Corporation.) [HKLM] -- KB892130
O42 - Logiciel: Windows Internet Explorer 7 - (.Microsoft Corporation.) [HKLM] -- ie7
O42 - Logiciel: Windows Internet Explorer 8 - (.Microsoft Corporation.) [HKLM] -- ie8
O42 - Logiciel: Windows Media Format 11 runtime - (...) [HKLM] -- Windows Media Format Runtime
O42 - Logiciel: Windows Media Format 11 runtime - (.Microsoft Corporation.) [HKLM] -- WMFDist11
O42 - Logiciel: Windows Media Player 11 - (.Microsoft Corporation.) [HKLM] -- wmp11 =>.Microsoft Corporation
O42 - Logiciel: Windows XP Service Pack 3 - (.Microsoft Corporation.) [HKLM] -- Windows XP Service
O42 - Logiciel: XML Paper Specification Shared Components Language Pack 1.0 - (.Microsoft Corporation.) [HKLM] -- XPSEPSCLP
O42 - Logiciel: XML Paper Specification Shared Components Pack 1.0 - (.Microsoft Corporation.) [HKLM] -- XpsEPSC
O42 - Logiciel: Zattoo4 4.0.5 - (.Zattoo Inc..) [HKLM] -- Zattoo4
O42 - Logiciel: Zork Grand Inquisitor - (...) [HKLM] -- ZGIUninstallKey
O42 - Logiciel: Zork Nemesis - (...) [HKLM] -- Zork NemesisDeinstKey
~ Logic: 87 Scanned in 00mn 00s
---\\ HKCU & HKLM Software Keys
[HKCU\Software\Adobe]
[HKCU\Software\Ahead]
[HKCU\Software\AppDataLow\FDA]
[HKCU\Software\AppDataLow]
[HKCU\Software\Avanquest]
[HKCU\Software\Azureus] =>P2P.Azureus
[HKCU\Software\Broderbund Software]
[HKCU\Software\Classes]
[HKCU\Software\Clients]
[HKCU\Software\DAEMON Tools Applications]
[HKCU\Software\DT Soft]
[HKCU\Software\Dell Computer Corporation]
[HKCU\Software\Digital River]
[HKCU\Software\DivXNetworks]
[HKCU\Software\DivX]
[HKCU\Software\FreeDownloadManager.ORG]
[HKCU\Software\GOG]
[HKCU\Software\Google]
[HKCU\Software\Hewlett-Packard]
[HKCU\Software\IM Providers]
[HKCU\Software\Intel]
[HKCU\Software\Iris]
[HKCU\Software\JavaSoft]
[HKCU\Software\LeaderTech]
[HKCU\Software\Local AppWizard-Generated Applications]
[HKCU\Software\Macromedia]
[HKCU\Software\Magnet]
[HKCU\Software\MainConcept]
[HKCU\Software\McAfee]
[HKCU\Software\Microids]
[HKCU\Software\MozillaPlugins]
[HKCU\Software\Mozilla]
[HKCU\Software\Nero]
[HKCU\Software\Netscape]
[HKCU\Software\ODBC]
[HKCU\Software\ORL]
[HKCU\Software\Piriform]
[HKCU\Software\Policies]
[HKCU\Software\SecuROM]
[HKCU\Software\Skype]
[HKCU\Software\Sun Microsystems]
[HKCU\Software\TeleCharger]
[HKCU\Software\Trolltech]
[HKCU\Software\VSO]
[HKCU\Software\VicMan Software]
[HKCU\Software\WinRAR SFX]
[HKCU\Software\WinRAR]
[HKCU\Software\Zattoo Inc.]
[HKCU\Software\Zattoo]
[HKCU\Software\argosy]
[HKCU\Software\ej-technologies]
[HKLM\Software\1 Jeu par jour]
[HKLM\Software\ATI Technologies Inc.]
[HKLM\Software\ATI Technologies]
[HKLM\Software\ATI]
[HKLM\Software\Aardwork]
[HKLM\Software\Activision]
[HKLM\Software\Adobe]
[HKLM\Software\AdwCleaner]
[HKLM\Software\Ahead]
[HKLM\Software\America Online]
[HKLM\Software\Apple Computer, Inc.]
[HKLM\Software\Axis Communications]
[HKLM\Software\Azureus] =>P2P.Azureus
[HKLM\Software\Broderbund Software]
[HKLM\Software\BrowserChoice]
[HKLM\Software\C07ft5Y]
[HKLM\Software\Classes]
[HKLM\Software\Clients]
[HKLM\Software\Creative Tech]
[HKLM\Software\DIOC]
[HKLM\Software\DT Soft]
[HKLM\Software\Dell Computer Corporation]
[HKLM\Software\Dell]
[HKLM\Software\DivXNetworks]
[HKLM\Software\DivX]
[HKLM\Software\FreeDownloadManager.ORG]
[HKLM\Software\Gemplus]
[HKLM\Software\Google]
[HKLM\Software\HP]
[HKLM\Software\Hewlett-Packard]
[HKLM\Software\ICE]
[HKLM\Software\IM Providers]
[HKLM\Software\InstallShield]
[HKLM\Software\InstalledOptions]
[HKLM\Software\Intel]
[HKLM\Software\Iomega Corp]
[HKLM\Software\JavaSoft]
[HKLM\Software\JreMetrics]
[HKLM\Software\LEAD Technologies, Inc.]
[HKLM\Software\MDC]
[HKLM\Software\Macromedia]
[HKLM\Software\McAfee.com]
[HKLM\Software\McAfee]
[HKLM\Software\Micro Application]
[HKLM\Software\MozillaPlugins]
[HKLM\Software\Mozilla]
[HKLM\Software\Nero]
[HKLM\Software\ODBC]
[HKLM\Software\OmniVision]
[HKLM\Software\Piriform]
[HKLM\Software\Policies]
[HKLM\Software\Program Groups]
[HKLM\Software\REALTEK Semiconductor Corp.]
[HKLM\Software\Realtek]
[HKLM\Software\RegisteredApplications]
[HKLM\Software\RtWLan]
[HKLM\Software\Schlumberger]
[HKLM\Software\Secure]
[HKLM\Software\Set8188SU]
[HKLM\Software\Set8191SU]
[HKLM\Software\Set8192GU]
[HKLM\Software\Set8192SU]
[HKLM\Software\Set8712]
[HKLM\Software\SigmaTel]
[HKLM\Software\SiteAdvisor]
[HKLM\Software\Skype]
[HKLM\Software\SmarterPower] =>PUP.SmarterPower
[HKLM\Software\Sun Microsystems]
[HKLM\Software\UIU]
[HKLM\Software\VSO]
[HKLM\Software\VicMan Software]
[HKLM\Software\VideoLAN]
[HKLM\Software\Windows 3.1 Migration Status]
[HKLM\Software\Windows]
[HKLM\Software\ej-technologies]
[HKLM\Software\lameme]
[HKLM\Software\magnet]
[HKLM\Software\mcafeeupdater]
[HKLM\Software\mozilla.org]
~ Key Software: 303 Scanned in 00mn 00s
---\\ Contenu des dossiers Programs/ProgramFiles/ProgramData/AppData (O43)
O43 - CFD: 02/06/2013 - 17:07:48 - [] ----D C:\Program Files\1 Jeu par jour
O43 - CFD: 20/06/2010 - 15:04:48 - [] ----D C:\Program Files\Activision
O43 - CFD: 28/09/2014 - 10:05:59 - [] ----D C:\Program Files\Adobe
O43 - CFD: 30/03/2008 - 20:25:52 - [] ----D C:\Program Files\Ahead
O43 - CFD: 30/03/2008 - 19:49:29 - [] ----D C:\Program Files\Apple Software Update =>.Apple Inc
O43 - CFD: 29/03/2008 - 15:23:03 - [] ----D C:\Program Files\ATI Technologies
O43 - CFD: 01/09/2014 - 11:29:17 - [] ----D C:\Program Files\Azureus =>P2P.Azureus
O43 - CFD: 28/09/2014 - 10:11:14 - [] ----D C:\Program Files\Bayam 3-7
O43 - CFD: 09/09/2014 - 13:19:46 - [] ----D C:\Program Files\CCleaner
O43 - CFD: 29/03/2008 - 14:11:03 - [0] ----D C:\Program Files\ComPlus Applications
O43 - CFD: 18/01/2009 - 16:40:19 - [] ----D C:\Program Files\DAEMON Tools Lite =>.DT Soft Ltd
O43 - CFD: 29/03/2008 - 15:27:30 - [] ----D C:\Program Files\Dell
O43 - CFD: 28/04/2013 - 18:34:46 - [] ----D C:\Program Files\DivX
O43 - CFD: 28/09/2014 - 10:05:23 - [] ----D C:\Program Files\Fichiers communs
O43 - CFD: 19/05/2013 - 14:59:07 - [] ----D C:\Program Files\Free Download Manager
O43 - CFD: 28/09/2008 - 16:03:42 - [] ----D C:\Program Files\GameShadow
O43 - CFD: 11/06/2010 - 19:33:40 - [] ----D C:\Program Files\Google
O43 - CFD: 02/12/2008 - 20:44:57 - [] ----D C:\Program Files\Governor of Poker
O43 - CFD: 29/09/2013 - 16:27:43 - [0] ----D C:\Program Files\GUM139.tmp
O43 - CFD: 11/01/2009 - 15:27:56 - [] ----D C:\Program Files\Hewlett-Packard
O43 - CFD: 01/07/2010 - 14:42:31 - [] ----D C:\Program Files\HP
O43 - CFD: 02/06/2013 - 17:07:47 - [] --H-D C:\Program Files\InstallShield Installation Information
O43 - CFD: 29/03/2008 - 15:38:11 - [] ----D C:\Program Files\Intel
O43 - CFD: 31/08/2014 - 17:54:25 - [] ----D C:\Program Files\Internet Explorer
O43 - CFD: 23/04/2009 - 20:37:59 - [] ----D C:\Program Files\Iomega
O43 - CFD: 31/08/2014 - 16:32:21 - [] ----D C:\Program Files\Java
O43 - CFD: 21/09/2014 - 20:10:05 - [] ----D C:\Program Files\McAfee
O43 - CFD: 31/08/2014 - 16:26:38 - [] ----D C:\Program Files\McAfee Security Scan
O43 - CFD: 14/09/2014 - 17:49:11 - [] ----D C:\Program Files\McAfee.com
O43 - CFD: 20/09/2008 - 00:25:03 - [] ----D C:\Program Files\Messenger
O43 - CFD: 01/09/2013 - 16:33:20 - [] ----D C:\Program Files\Microids
O43 - CFD: 28/01/2009 - 14:53:50 - [] ----D C:\Program Files\Microsoft
O43 - CFD: 13/04/2008 - 04:00:32 - [] ----D C:\Program Files\Microsoft CAPICOM 2.1.0.2
O43 - CFD: 26/12/2008 - 11:19:37 - [] ----D C:\Program Files\microsoft frontpage
O43 - CFD: 08/08/2011 - 23:11:42 - [] ----D C:\Program Files\Microsoft Office
O43 - CFD: 30/03/2008 - 00:50:25 - [] ----D C:\Program Files\Microsoft Visual Studio
O43 - CFD: 01/06/2010 - 21:10:59 - [] ----D C:\Program Files\Microsoft Works
O43 - CFD: 12/08/2010 - 15:48:16 - [] ----D C:\Program Files\Movie Maker
O43 - CFD: 28/09/2014 - 14:54:03 - [] ----D C:\Program Files\Mozilla Firefox
O43 - CFD: 28/09/2014 - 14:54:03 - [] ----D C:\Program Files\Mozilla Maintenance Service
O43 - CFD: 01/09/2014 - 13:08:03 - [] ----D C:\Program Files\MSBuild
O43 - CFD: 06/11/2008 - 14:53:17 - [] ----D C:\Program Files\MSN
O43 - CFD: 29/03/2008 - 14:10:53 - [] ----D C:\Program Files\MSN Gaming Zone
O43 - CFD: 01/04/2008 - 15:31:59 - [0] ----D C:\Program Files\MSXML 4.0
O43 - CFD: 20/09/2008 - 00:19:17 - [] ----D C:\Program Files\NetMeeting
O43 - CFD: 29/03/2008 - 14:11:00 - [] ----D C:\Program Files\Online Services
O43 - CFD: 21/12/2010 - 04:00:43 - [] ----D C:\Program Files\Outlook Express =>.Microsoft Corporation
O43 - CFD: 30/03/2008 - 19:50:03 - [] ----D C:\Program Files\QuickTime
O43 - CFD: 20/10/2013 - 16:14:21 - [] ----D C:\Program Files\REALTEK
O43 - CFD: 01/09/2014 - 13:07:50 - [] ----D C:\Program Files\Reference Assemblies
O43 - CFD: 29/03/2008 - 14:12:50 - [] ----D C:\Program Files\Services en ligne
O43 - CFD: 29/03/2008 - 15:18:45 - [] ----D C:\Program Files\SigmaTel
O43 - CFD: 01/09/2014 - 09:57:45 - [] R---D C:\Program Files\Skype
O43 - CFD: 24/09/2008 - 15:21:06 - [] ----D C:\Program Files\Sun
O43 - CFD: 31/01/2009 - 16:05:45 - [] ----D C:\Program Files\The Last Express
O43 - CFD: 28/09/2008 - 12:42:52 - [] ----D C:\Program Files\Ubisoft
O43 - CFD: 29/03/2008 - 15:15:36 - [0] --H-D C:\Program Files\Uninstall Information
O43 - CFD: 28/06/2010 - 11:07:48 - [] ----D C:\Program Files\VideoLAN
O43 - CFD: 30/03/2008 - 19:34:20 - [] ----D C:\Program Files\VSO
O43 - CFD: 14/09/2014 - 18:26:47 - [] ----D C:\Program Files\Vuze =>P2P.Azureus
O43 - CFD: 28/01/2009 - 14:53:46 - [] ----D C:\Program Files\Windows Live
O43 - CFD: 28/01/2009 - 14:53:36 - [] ----D C:\Program Files\Windows Live SkyDrive
O43 - CFD: 29/03/2008 - 16:39:48 - [] ----D C:\Program Files\Windows Media Connect 2
O43 - CFD: 20/09/2008 - 00:19:15 - [] ----D C:\Program Files\Windows Media Player =>.Microsoft Corporation
O43 - CFD: 20/09/2008 - 00:19:15 - [] ----D C:\Program Files\Windows NT
O43 - CFD: 29/03/2008 - 14:12:51 - [0] --H-D C:\Program Files\WindowsUpdate
O43 - CFD: 30/03/2008 - 19:47:13 - [] ----D C:\Program Files\WinRAR
O43 - CFD: 29/03/2008 - 14:14:01 - [] ----D C:\Program Files\xerox
O43 - CFD: 28/06/2010 - 11:58:53 - [] ----D C:\Program Files\Zattoo4
O43 - CFD: 29/09/2014 - 09:45:06 - [] ----D C:\Program Files\ZHPDiag =>.Nicolas Coolman
O43 - CFD: 09/06/2013 - 12:10:45 - [] ----D C:\Program Files\Fichiers communs\Adobe
O43 - CFD: 28/09/2014 - 10:05:25 - [] ----D C:\Program Files\Fichiers communs\Adobe AIR
O43 - CFD: 30/03/2008 - 20:22:22 - [] ----D C:\Program Files\Fichiers communs\Ahead
O43 - CFD: 31/08/2014 - 17:56:57 - [] ----D C:\Program Files\Fichiers communs\DESIGNER
O43 - CFD: 28/04/2013 - 18:34:45 - [] ----D C:\Program Files\Fichiers communs\DivX Shared
O43 - CFD: 31/03/2008 - 16:07:36 - [] ----D C:\Program Files\Fichiers communs\Hewlett-Packard
O43 - CFD: 31/03/2008 - 16:09:28 - [] ----D C:\Program Files\Fichiers communs\HP
O43 - CFD: 29/03/2008 - 15:22:35 - [] ----D C:\Program Files\Fichiers communs\InstallShield
O43 - CFD: 09/06/2013 - 12:02:47 - [] ----D C:\Program Files\Fichiers communs\Java
O43 - CFD: 14/09/2014 - 17:50:11 - [] ----D C:\Program Files\Fichiers communs\McAfee
O43 - CFD: 08/09/2014 - 23:16:58 - [] ----D C:\Program Files\Fichiers communs\Microsoft Shared
O43 - CFD: 29/03/2008 - 14:11:53 - [] ----D C:\Program Files\Fichiers communs\MSSoap
O43 - CFD: 30/03/2008 - 20:24:02 - [] ----D C:\Program Files\Fichiers communs\Nero
O43 - CFD: 29/03/2008 - 14:59:28 - [] ----D C:\Program Files\Fichiers communs\ODBC
O43 - CFD: 29/03/2008 - 14:11:59 - [] ----D C:\Program Files\Fichiers communs\Services
O43 - CFD: 01/09/2014 - 09:57:45 - [] ----D C:\Program Files\Fichiers communs\Skype
O43 - CFD: 29/03/2008 - 14:59:25 - [] ----D C:\Program Files\Fichiers communs\SpeechEngines
O43 - CFD: 24/07/2012 - 17:52:07 - [] ----D C:\Program Files\Fichiers communs\System
O43 - CFD: 28/01/2009 - 14:30:12 - [] ----D C:\Program Files\Fichiers communs\Windows Live
O43 - CFD: 28/09/2014 - 10:06:14 - [] ----D C:\Documents and Settings\All Users\Application Data\Adobe
O43 - CFD: 30/03/2008 - 20:22:28 - [] ----D C:\Documents and Settings\All Users\Application Data\Ahead
O43 - CFD: 30/03/2008 - 19:49:28 - [] ----D C:\Documents and Settings\All Users\Application Data\Apple Computer
O43 - CFD: 30/03/2008 - 23:43:35 - [] ----D C:\Documents and Settings\All Users\Application Data\Azureus =>P2P.Azureus
O43 - CFD: 18/01/2009 - 16:40:23 - [0] ----D C:\Documents and Settings\All Users\Application Data\DAEMON Tools Lite =>.DT Soft Ltd
O43 - CFD: 28/04/2013 - 18:34:45 - [] ----D C:\Documents and Settings\All Users\Application Data\DivX
O43 - CFD: 09/06/2013 - 11:53:28 - [] ----D C:\Documents and Settings\All Users\Application Data\Free Download Manager
O43 - CFD: 30/03/2008 - 20:41:04 - [] ----D C:\Documents and Settings\All Users\Application Data\FreeDownloadManager.ORG
O43 - CFD: 11/06/2010 - 19:31:39 - [] ----D C:\Documents and Settings\All Users\Application Data\Google
O43 - CFD: 31/03/2008 - 16:10:15 - [] ----D C:\Documents and Settings\All Users\Application Data\HP
O43 - CFD: 11/01/2009 - 15:25:33 - [] ----D C:\Documents and Settings\All Users\Application Data\HP Product Assistant
O43 - CFD: 16/09/2014 - 13:56:41 - [] ----D C:\Documents and Settings\All Users\Application Data\McAfee
O43 - CFD: 31/08/2014 - 16:27:09 - [] ----D C:\Documents and Settings\All Users\Application Data\McAfee Security Scan
O43 - CFD: 28/04/2013 - 16:00:28 - [] ----D C:\Documents -
-
-
Contributeur sécurité# Télécharge UsbFix par El Desaparecido sur ton Bureau.
# Si ton antivirus affiche une alerte, ignore-la et désactive l'antivirus temporairement.
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Options, dans le menu BBCode choisis CCM.
# Valide en cliquant sur Appliquer.
# UsbFix se relancera pour prendre en compte tes réglages.
# Clique maintenant sur Nettoyage.
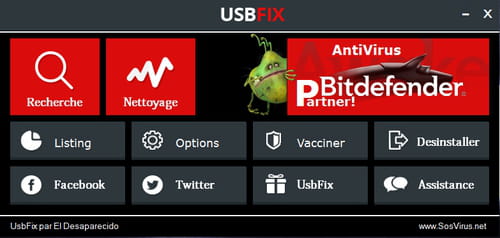
# Laisse travailler l'outil, ton bureau ne sera pas accessible durant la phase de nettoyage, c'est normal.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système.
(C:\Usbfix\Log\UsbFix [Clean ...txt).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# ->> Tutoriel (aide) en images sur le site de l'auteur.
-
Contributeur sécuritéOui
-
Voici le rapport:
https://www.cjoint.com/?3JbjGL8eGho
En revanche après une autre analyse de McAfee il me fait apparaître les programmes indésirables suivant:
- BrowseFox.a
-BrowseFox
- PUP-FNK
- Adware-browseFox
-PUP-FPS
-
-
Contributeur sécuritéSi tu as un programme browserfox tu le désinstalle
-
Contributeur sécuritéRefais zhpdiag mis à jour


