
Ma clé transforme tous en raccourci
Résolu
bonjour cher frère,
sil vous plait aidé moi j'ai des soucis avec la machine elle transforme tous les programmes et les dossiers retrouver dans la clés usb en raccourci
sil vous plait aidé moi j'ai des soucis avec la machine elle transforme tous les programmes et les dossiers retrouver dans la clés usb en raccourci
11 réponses
-
a tu bien mis les dossier originel dés fois et ça met arrivé tu pense avoir ms met en faite tu a fais que un raccourci et c'est normal fait plutôt un copier/coller que un glisser.
J'espère t'avoir aider. -
Contributeur sécuritéHello
Tu as une infection USB!
###########| Canned Recherche
# Télécharge UsbFix par El Desaparecido sur ton Bureau.
# Si ton antivirus affiche une alerte, ignore-la et désactive l'antivirus temporairement.
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Recherche.

# Laisse travailler l'outil.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système ( C:\UsbFix [Scan ?] Nom de l'ordinateur.txt ).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# Tutoriel (aide) en images
-
############################## | UsbFix V 7.165 | [Recherche]
Utilisateur: pierre (Administrateur) # PIERRE-PC
Mis à jour le16/02/2014 par El Desaparecido - Team SosVirus
Lancé à 19:41:43 | 17/02/2014
Site Web : http://www.usbfix.net/
Changelog : http://www.usbfix.net/maj/
Support : http://www.sosvirus.net/
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : http://www.usbfix.net/contact/
PC: Packard Bell (EG50_HC_HR)
CPU: Intel(R) Celeron(R) CPU B820 @ 1.70GHz
RAM -> [Total : 3932 Mo| Free : 1490 Mo]
Bios: Packard Bell
Boot: Normal boot
OS: Microsoft Windows 7 Édition Familiale Premium (6.1.7601 64-Bit) Service Pack 1
WB: Windows Internet Explorer : 11.0.9600.16518
WB: Google Chrome : 32.0.1700.107
WB: Mozilla Firefox : 27.0.1
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
AV: Pack Sécurité [Enabled | Updated]
AS: Pack Sécurité [Enabled | Updated]
AS: Windows Defender [(!) Disabled | Updated]
FW: Windows FireWall [(!) Disabled]
C:\ (%systemdrive%) -> Disque fixe # 684 Go (426 Go libre(s) - 62%) [Packard Bell] # NTFS
D:\ -> CD-ROM
E:\ -> Disque amovible # 29 Go (23 Go libre(s) - 79%) [KINGSTON] # FAT32
################## | Processus Actif |
C:\Windows\system32\csrss.exe (ID: 444 |ParentID: 432)
C:\Windows\system32\wininit.exe (ID: 500 |ParentID: 432)
C:\Windows\system32\csrss.exe (ID: 532 |ParentID: 508)
C:\Windows\system32\winlogon.exe (ID: 572 |ParentID: 508)
C:\Windows\system32\services.exe (ID: 608 |ParentID: 500)
C:\Windows\system32\lsass.exe (ID: 624 |ParentID: 500)
C:\Windows\system32\lsm.exe (ID: 632 |ParentID: 500)
C:\Windows\system32\svchost.exe (ID: 744 |ParentID: 608)
C:\Windows\system32\svchost.exe (ID: 820 |ParentID: 608)
C:\Windows\System32\svchost.exe (ID: 896 |ParentID: 608)
C:\Windows\System32\svchost.exe (ID: 964 |ParentID: 608)
C:\Windows\system32\svchost.exe (ID: 1004 |ParentID: 608)
C:\Windows\system32\svchost.exe (ID: 316 |ParentID: 608)
C:\Windows\system32\svchost.exe (ID: 476 |ParentID: 608)
C:\Program Files\Broadcom\Broadcom 802.11 Network Adapter\WLTRYSVC.EXE (ID: 1080 |ParentID: 608)
C:\Windows\system32\WLANExt.exe (ID: 1096 |ParentID: 964)
C:\Program Files\Broadcom\Broadcom 802.11 Network Adapter\bcmwltry.exe (ID: 1112 |ParentID: 1080)
C:\Windows\system32\conhost.exe (ID: 1120 |ParentID: 444)
C:\Windows\System32\spoolsv.exe (ID: 1296 |ParentID: 608)
C:\Windows\system32\svchost.exe (ID: 1328 |ParentID: 608)
C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe (ID: 1400 |ParentID: 608)
C:\Program Files (x86)\Launch Manager\dsiwmis.exe (ID: 1484 |ParentID: 608)
C:\Program Files\Packard Bell\Packard Bell Power Management\ePowerSvc.exe (ID: 1608 |ParentID: 608)
C:\Program Files (x86)\Launch Manager\LMutilps32.exe (ID: 1620 |ParentID: 1484)
C:\Windows\system32\svchost.exe (ID: 1676 |ParentID: 608)
C:\ProgramData\Freemake\FreemakeUtilsService\FreemakeUtilsService.exe (ID: 1704 |ParentID: 608)
C:\Windows\system32\taskhost.exe (ID: 1800 |ParentID: 608)
C:\Windows\system32\Dwm.exe (ID: 1872 |ParentID: 964)
C:\Windows\Explorer.EXE (ID: 2020 |ParentID: 1264)
C:\Windows\System32\igfxtray.exe (ID: 1540 |ParentID: 2020)
C:\Windows\System32\hkcmd.exe (ID: 1480 |ParentID: 2020)
C:\Windows\System32\igfxpers.exe (ID: 1744 |ParentID: 2020)
C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe (ID: 1756 |ParentID: 2020)
C:\Program Files\Elantech\ETDCtrl.exe (ID: 2068 |ParentID: 2020)
C:\Program Files\Broadcom\Broadcom 802.11 Network Adapter\WLTRAY.EXE (ID: 2092 |ParentID: 2020)
C:\Program Files\Packard Bell\Packard Bell Power Management\ePowerTray.exe (ID: 2216 |ParentID: 2020)
C:\Program Files (x86)\Skype\Phone\Skype.exe (ID: 2272 |ParentID: 2020)
C:\Program Files (x86)\SFR\Pack_Securite\fshoster32.exe (ID: 2480 |ParentID: 608)
C:\Program Files (x86)\SFR\Pack_Securite\apps\CCF_Reputation\fsorsp.exe (ID: 2632 |ParentID: 608)
C:\Program Files (x86)\Packard Bell\Registration\GREGsvc.exe (ID: 2652 |ParentID: 608)
C:\Program Files (x86)\SFR\Pack_Securite\apps\ComputerSecurity\Anti-Virus\FSGK32.EXE (ID: 2660 |ParentID: 2480)
C:\Program Files\Intel\iCLS Client\HeciServer.exe (ID: 2704 |ParentID: 608)
C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\DAL\jhi_service.exe (ID: 2732 |ParentID: 608)
C:\Program Files\Packard Bell\Packard Bell Updater\UpdaterService.exe (ID: 2772 |ParentID: 608)
C:\Program Files (x86)\PDF Architect\HelperService.exe (ID: 2864 |ParentID: 608)
C:\Program Files (x86)\PDF Architect\ConversionService.exe (ID: 2908 |ParentID: 608)
C:\Windows\system32\svchost.exe (ID: 3000 |ParentID: 608)
C:\Program Files (x86)\SFR\Pack_Securite\apps\ComputerSecurity\Common\FSMA32.EXE (ID: 2140 |ParentID: 608)
C:\Program Files\Elantech\ETDCtrlHelper.exe (ID: 3228 |ParentID: 2068)
C:\Windows\system32\svchost.exe (ID: 3252 |ParentID: 608)
C:\Program Files (x86)\SFR\Pack_Securite\apps\ComputerSecurity\Anti-Virus\fssm32.exe (ID: 3344 |ParentID: 2660)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 3544 |ParentID: 744)
C:\Windows\system32\SearchIndexer.exe (ID: 3612 |ParentID: 608)
C:\Windows\system32\igfxext.exe (ID: 3796 |ParentID: 744)
C:\Windows\system32\igfxsrvc.exe (ID: 3824 |ParentID: 744)
C:\Windows\system32\wbem\unsecapp.exe (ID: 3876 |ParentID: 744)
C:\Windows\system32\wbem\wmiprvse.exe (ID: 3952 |ParentID: 744)
C:\Program Files\Packard Bell\Packard Bell Power Management\ePowerEvent.exe (ID: 4016 |ParentID: 1608)
C:\Program Files (x86)\SFR\Pack_Securite\apps\ComputerSecurity\Common\FSHDLL64.EXE (ID: 4040 |ParentID: 2140)
C:\Program Files\Windows Media Player\wmpnetwk.exe (ID: 3396 |ParentID: 608)
C:\Program Files\McAfee Security Scan\3.8.141\SSScheduler.exe (ID: 4180 |ParentID: 2020)
C:\Users\pierre\AppData\Roaming\Dropbox\bin\Dropbox.exe (ID: 4204 |ParentID: 2020)
C:\Program Files (x86)\Launch Manager\LManager.exe (ID: 4412 |ParentID: 4160)
C:\Program Files (x86)\SFR\Pack_Securite\fshoster32.exe (ID: 4424 |ParentID: 4160)
C:\Program Files (x86)\SFR\Pack_Securite\apps\ComputerSecurity\Common\FSM32.EXE (ID: 4432 |ParentID: 4160)
C:\Program Files (x86)\Launch Manager\MMDx64Fx.exe (ID: 4500 |ParentID: 4412)
C:\Program Files (x86)\Launch Manager\LMworker.exe (ID: 4592 |ParentID: 1484)
C:\Windows\system32\taskeng.exe (ID: 4868 |ParentID: 316)
C:\Program Files (x86)\CyberLink\MediaEspresso\DeviceDetector\DeviceDetector.exe (ID: 4980 |ParentID: 4868)
C:\Windows\System32\svchost.exe (ID: 5084 |ParentID: 608)
C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\LMS\LMS.exe (ID: 2404 |ParentID: 608)
C:\Program Files (x86)\Nero\Update\NASvc.exe (ID: 4276 |ParentID: 608)
C:\Program Files (x86)\Symantec\Norton Online Backup\NOBuAgent.exe (ID: 1532 |ParentID: 608)
C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\UNS\UNS.exe (ID: 1140 |ParentID: 608)
C:\Program Files (x86)\Microsoft\BingBar\7.3.124.0\SeaPort.exe (ID: 4528 |ParentID: 608)
C:\Program Files (x86)\Mozilla Firefox\firefox.exe (ID: 3684 |ParentID: 2020)
C:\Program Files (x86)\Mozilla Firefox\plugin-container.exe (ID: 3848 |ParentID: 3684)
C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerPlugin_12_0_0_44.exe (ID: 3540 |ParentID: 3848)
C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerPlugin_12_0_0_44.exe (ID: 2572 |ParentID: 3540)
C:\Windows\system32\taskeng.exe (ID: 6040 |ParentID: 316)
C:\Windows\system32\taskeng.exe (ID: 5248 |ParentID: 316)
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe (ID: 1588 |ParentID: 2020)
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe (ID: 2880 |ParentID: 1588)
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe (ID: 704 |ParentID: 1588)
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe (ID: 5116 |ParentID: 1588)
C:\Windows\System32\WUDFHost.exe (ID: 1768 |ParentID: 964)
################## | Regedit Run |
04 - HKCU\..\Run : [Skype] "C:\Program Files (x86)\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKCU\..\Run : [Facebook Update] "C:\Users\pierre\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKCU\..\Run : [tmxnftcqgr] wscript.exe //B "C:\Users\pierre\AppData\Local\Temp\tmxnftcqgr..vbs"
04 - HKLM\..\Run : [LManager] C:\Program Files (x86)\Launch Manager\LManager.exe
04 - HKLM\..\Run : []
04 - HKLM\..\Run : [F-Secure Hoster (44996)] "C:\Program Files (x86)\SFR\Pack_Securite\fshoster32.exe" -app -hosterid:1
04 - HKLM\..\Run : [F-Secure Manager] "C:\Program Files (x86)\SFR\Pack_Securite\apps\ComputerSecurity\Common\FSM32.EXE" /splash
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\RunOnce : []
04 - HKLM64\..\Run : [IgfxTray] C:\Windows\system32\igfxtray.exe
04 - HKLM64\..\Run : [HotKeysCmds] C:\Windows\system32\hkcmd.exe
04 - HKLM64\..\Run : [Persistence] C:\Windows\system32\igfxpers.exe
04 - HKLM64\..\Run : [RTHDVCPL] C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe -s
04 - HKLM64\..\Run : [ETDCtrl] %ProgramFiles%\Elantech\ETDCtrl.exe
04 - HKLM64\..\Run : [Broadcom Wireless Manager UI] C:\Program Files\Broadcom\Broadcom 802.11 Network Adapter\WLTRAY.exe
04 - HKLM64\..\Run : [Power Management] C:\Program Files\Packard Bell\Packard Bell Power Management\ePowerTray.exe
04 - HKU\S-1-5-19\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-20\..\Run : [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun
04 - HKU\S-1-5-21-4080395528-3243526330-3576341410-1001\..\Run : [Skype] "C:\Program Files (x86)\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKU\S-1-5-21-4080395528-3243526330-3576341410-1001\..\Run : [Facebook Update] "C:\Users\pierre\AppData\Local\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKU\S-1-5-21-4080395528-3243526330-3576341410-1001\..\Run : [tmxnftcqgr] wscript.exe //B "C:\Users\pierre\AppData\Local\Temp\tmxnftcqgr..vbs"
04 - HKU\S-1-5-19\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
04 - HKU\S-1-5-20\..\RunOnce : [mctadmin] C:\Windows\System32\mctadmin.exe
################## | Recherche générique |
Présent! C:\Users\Public\sdelevURL.tmp
################## | Registre |
################## | E.O.F | http://www.usbfix.net/ - http://www.sosvirus.net | -
voici le rapport que USBFIX viens de m'envoyer après un nouveau scanne
############################## | UsbFix 7.036 | [Suppression]
Utilisateur: Administrateur (Administrateur) # KEUMENI [ ]
Mis à jour le 20/12/10 par El Desaparecido / C_XX
Lancé à 20:41:47 | 18/02/2014
Site Web: http://www.teamxscript.org
Contact: eldesaparecido@teamxscript.org
CPU: Intel(R) Pentium(R) D CPU 2.80GHz
CPU 2: Intel(R) Pentium(R) D CPU 2.80GHz
Microsoft Windows XP Professionnel (5.1.2600 32-Bit) # Service Pack 3
Internet Explorer 8.0.6001.18702
Pare-feu Windows: Désactivé /!\
Antivirus: avast! Antivirus 5.0.150996957 [(!) Disabled | Updated]
RAM -> 3574 Mo
C:\ (%systemdrive%) -> Disque fixe # 34 Go (5 Go libre(s) - 14%) [] # NTFS
D:\ -> Disque fixe # 40 Go (21 Go libre(s) - 52%) [Nouveau nom] # NTFS
E:\ -> CD-ROM
F:\ -> Disque amovible # 4 Go (586 Mo libre(s) - 16%) [] # FAT32
################## | Éléments infectieux |
Supprimé! C:\Recycler\S-1-5-21-1202660629-1343024091-1606980848-500
Supprimé! D:\Recycler\S-1-5-21-1202660629-1343024091-1606980848-500
################## | Registre |
################## | Mountpoints2 |
################## | Listing |
[11/09/2013 - 11:19:20 | D ] C:\$AVG
[05/10/2013 - 21:26:51 | N | 3072] C:\ads_err.adi
[05/10/2013 - 21:26:51 | N | 4559] C:\ads_err.adm
[05/10/2013 - 21:48:14 | N | 13785] C:\ads_err.adt
[14/05/2013 - 17:58:59 | N | 0] C:\AUTOEXEC.BAT
[18/02/2014 - 20:37:29 | RASHD ] C:\Autorun.inf
[18/12/2013 - 21:29:27 | N | 212] C:\boot.ini
[14/04/2008 - 13:00:00 | N | 4952] C:\Bootfont.bin
[23/09/2008 - 05:01:14 | | 1364] C:\changelog_MassStorage.txt
[17/02/2014 - 11:47:18 | D ] C:\Config.Msi
[14/05/2013 - 17:58:59 | N | 0] C:\CONFIG.SYS
[11/09/2013 - 10:37:20 | D ] C:\Documents and Settings
[11/09/2013 - 12:06:05 | N | 9] C:\END
[16/09/2013 - 08:49:16 | D ] C:\HP_LaserJet_Professional_CM1410_Series
[14/05/2013 - 17:58:59 | N | 0] C:\IO.SYS
[14/05/2013 - 17:58:59 | N | 0] C:\MSDOS.SYS
[14/09/2013 - 08:29:39 | RHD ] C:\MSOCache
[14/04/2008 - 13:00:00 | N | 47564] C:\NTDETECT.COM
[14/04/2008 - 13:00:00 | N | 252240] C:\ntldr
[03/01/2014 - 20:04:23 | D ] C:\ONE TOUCH Upgrade S 2.8.0
[18/02/2014 - 17:48:15 | ASH | 792723456] C:\pagefile.sys
[12/02/2014 - 11:50:32 | N | 13030] C:\PDOXUSRS.NET
[20/11/2013 - 14:32:06 | N | 233308] C:\process.txt
[17/02/2014 - 18:26:46 | D ] C:\Program Files
[18/02/2014 - 20:42:12 | SHD ] C:\RECYCLER
[18/02/2014 - 20:22:49 | N | 483] C:\STAT.DAT
[14/05/2013 - 19:37:54 | SHD ] C:\System Volume Information
[18/02/2014 - 20:42:12 | D ] C:\UsbFix
[17/02/2014 - 18:20:03 | N | 19142] C:\UsbFix [Clean 2] KEUMENI.txt
[17/02/2014 - 19:18:33 | N | 15804] C:\UsbFix [Clean 4] KEUMENI.txt
[17/02/2014 - 17:24:17 | N | 14340] C:\UsbFix [Scan 1] KEUMENI.txt
[17/02/2014 - 19:30:40 | N | 12969] C:\UsbFix [Scan 2] KEUMENI.txt
[18/02/2014 - 09:28:51 | N | 13153] C:\UsbFix [Scan 3] KEUMENI.txt
[18/02/2014 - 20:42:15 | A | 1051] C:\UsbFix.txt
[18/02/2014 - 20:19:37 | N | 347693822] C:\UsbFix_Upload_Me_KEUMENI.zip
[23/11/2013 - 14:42:05 | D ] C:\Users
[18/02/2014 - 09:58:20 | D ] C:\WINDOWS
[11/09/2013 - 12:43:32 | D ] D:\$AVG
[16/09/2013 - 08:09:33 | D ] D:\5c32dca40a47497382265e8601
[18/02/2014 - 20:37:31 | RASHD ] D:\Autorun.inf
[14/11/2013 - 09:06:55 | N | 1343488] D:\BD IMPRESSION.mdb
[03/10/2013 - 07:55:52 | D ] D:\dossiers
[16/09/2013 - 21:22:08 | D ] D:\f484d51d99b5efaaf1b600fa46
[11/09/2013 - 13:20:07 | D ] D:\FIND_MOZ_EXT
[20/11/2013 - 15:14:50 | D ] D:\nkk
[18/02/2014 - 20:42:12 | SHD ] D:\RECYCLER
[05/12/2013 - 13:41:19 | D ] D:\samsung
[11/09/2013 - 13:20:10 | D ] D:\searchplugins
[28/12/2013 - 14:57:26 | D ] D:\setup imprimante hp
[14/05/2013 - 18:26:08 | SHD ] D:\System Volume Information
[14/11/2013 - 14:48:31 | N | 678945792] D:\ubuntu-13.10-desktop-i386.iso
[09/12/2012 - 18:35:04 | D ] F:\PRIVATE
[09/12/2012 - 19:56:44 | D ] F:\DCIM
[09/12/2012 - 19:56:44 | D ] F:\MP_ROOT
[25/12/2012 - 17:48:28 | N | 512] F:\NIKON001.DSC
[26/01/2014 - 10:28:36 | N | 81920] F:\PRINTFDUMP.LOG
[18/02/2014 - 20:37:34 | RASHD ] F:\Autorun.inf
################## | Vaccin |
C:\Autorun.inf -> Dossier créé par UsbFix (El Desaparecido & C_XX)
D:\Autorun.inf -> Dossier créé par UsbFix (El Desaparecido & C_XX)
F:\Autorun.inf -> Dossier créé par UsbFix (El Desaparecido & C_XX)
################## | Upload |
Veuillez envoyer le fichier: C:\UsbFix_Upload_Me_KEUMENI.zip
http://www.teamxscript.org/Upload.php
Merci de votre contribution.
################## | E.O.F | -
-
-
non se n'est pas un probleme d'envoi de document quand un clients arrive avec sa clé usb pour faire des impressions dès que je la branche a mon UC tous ses documentts de transforment en raccourci
-
Contributeur sécurité@Pierre
Ouvres ton propre sujet
-
bjr a tous
voilà le rapport donné par usbfix
############################## | UsbFix V 7.165 | [Recherche]
Utilisateur: Administrateur (Administrateur) # KEUMENI
Mis à jour le16/02/2014 par El Desaparecido - Team SosVirus
Lancé à 09:20:42 | 18/02/2014
Site Web : https://www.usbfix.net/
Changelog : https://www.usb-antivirus.com/fr/maj/
Support : https://www.sosvirus.net/
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : https://www.usb-antivirus.com/fr/contact/
PC: Dell Inc. (0HH807)
CPU: Intel(R) Pentium(R) D CPU 2.80GHz
RAM -> [Total : 3574 Mo| Free : 2569 Mo]
Bios: Dell Inc.
Boot: Normal boot
OS: Microsoft Windows XP Professionnel (5.1.2600 32-Bit) Service Pack 3
WB: Windows Internet Explorer : 8.0.6001.18702
WB: Mozilla Firefox : 27.0.1
SC: Security Center [(!) Disabled]
WU: Windows Update [Enabled]
FW: Windows FireWall [Enabled]
C:\ (%systemdrive%) -> Disque fixe # 34 Go (5 Go libre(s) - 15%) [] # NTFS
D:\ -> Disque fixe # 40 Go (21 Go libre(s) - 52%) [Nouveau nom] # NTFS
E:\ -> CD-ROM
F:\ -> Disque amovible # 4 Go (585 Mo libre(s) - 16%) [] # FAT32
################## | Processus Actif |
C:\WINDOWS\System32\smss.exe (ID: 864 |ParentID: 4)
C:\WINDOWS\system32\winlogon.exe (ID: 1064 |ParentID: 864)
C:\WINDOWS\system32\services.exe (ID: 1208 |ParentID: 1064)
C:\WINDOWS\system32\lsass.exe (ID: 1236 |ParentID: 1064)
C:\WINDOWS\system32\svchost.exe (ID: 1500 |ParentID: 1208)
C:\WINDOWS\System32\svchost.exe (ID: 1792 |ParentID: 1208)
C:\WINDOWS\system32\svchost.exe (ID: 1844 |ParentID: 1208)
C:\Program Files\AVG\AVG9\avgchsvx.exe (ID: 1876 |ParentID: 1064)
C:\Program Files\AVG\AVG9\avgrsx.exe (ID: 1900 |ParentID: 1064)
C:\Program Files\AVG\AVG9\avgcsrvx.exe (ID: 404 |ParentID: 1900)
C:\Program Files\AVAST Software\Avast\AvastSvc.exe (ID: 1136 |ParentID: 1208)
C:\WINDOWS\Explorer.EXE (ID: 1712 |ParentID: 1540)
C:\WINDOWS\System32\svchost.exe (ID: 1972 |ParentID: 1208)
C:\WINDOWS\system32\spoolsv.exe (ID: 260 |ParentID: 1208)
C:\Program Files\Fichiers communs\Acronis\Schedule2\schedul2.exe (ID: 1416 |ParentID: 1208)
C:\Program Files\Fichiers communs\Apple\Mobile Device Support\AppleMobileDeviceService.exe (ID: 1240 |ParentID: 1208)
C:\Program Files\AVG\AVG9\avgwdsvc.exe (ID: 456 |ParentID: 1208)
C:\Program Files\Bonjour\mDNSResponder.exe (ID: 1152 |ParentID: 1208)
C:\Program Files\Analog Devices\Core\smax4pnp.exe (ID: 1440 |ParentID: 1712)
C:\Program Files\HP\HPLaserJetService\HPLaserJetService.exe (ID: 452 |ParentID: 1208)
C:\WINDOWS\system32\igfxtray.exe (ID: 1124 |ParentID: 1712)
C:\WINDOWS\system32\hkcmd.exe (ID: 776 |ParentID: 1712)
C:\WINDOWS\system32\igfxpers.exe (ID: 2072 |ParentID: 1712)
C:\Program Files\USB Disk Security\USBGuard.exe (ID: 2108 |ParentID: 1712)
C:\WINDOWS\system32\igfxsrvc.exe (ID: 2232 |ParentID: 1500)
C:\Program Files\Acronis\TrueImage\TrueImageMonitor.exe (ID: 2248 |ParentID: 1712)
C:\Program Files\Fichiers communs\Acronis\Schedule2\schedhlp.exe (ID: 2288 |ParentID: 1712)
C:\PROGRA~1\AVG\AVG9\avgtray.exe (ID: 2376 |ParentID: 1712)
C:\Program Files\HP\HP UT LEDM\bin\hppusg.exe (ID: 2472 |ParentID: 1712)
C:\Program Files\Fichiers communs\Research In Motion\USB Drivers\RIMBBLaunchAgent.exe (ID: 2508 |ParentID: 1712)
C:\WINDOWS\system32\HPSIsvc.exe (ID: 2804 |ParentID: 1208)
C:\PROGRA~1\VIDEOD~2\bar\1.bin\4zsrchmn.exe (ID: 3316 |ParentID: 1712)
C:\Program Files\HTC\HTC Sync Manager\HSMServiceEntry.exe (ID: 3428 |ParentID: 1208)
C:\PROGRA~1\VIDEOD~2\bar\1.bin\4zbrmon.exe (ID: 3436 |ParentID: 1712)
C:\Program Files\AVG\AVG9\avgnsx.exe (ID: 3552 |ParentID: 456)
C:\Documents and Settings\All Users\Application Data\ZGame Anti-Phishing Domain\zgame_antiphishing.exe (ID: 3580 |ParentID: 1712)
C:\Program Files\Yahoo!\Search Protection\SearchProtection.exe (ID: 3712 |ParentID: 1712)
C:\WINDOWS\System32\svchost.exe (ID: 3792 |ParentID: 1208)
C:\Program Files\Samsung\Kies\KiesTrayAgent.exe (ID: 4076 |ParentID: 1712)
C:\Program Files\HTC\Internet Pass-Through\PassThruSvr.exe (ID: 1312 |ParentID: 1208)
C:\Program Files\iTunes\iTunesHelper.exe (ID: 888 |ParentID: 1712)
C:\Program Files\AVAST Software\Avast\avastUI.exe (ID: 1628 |ParentID: 1712)
C:\WINDOWS\system32\wscript.exe (ID: 2120 |ParentID: 1712)
C:\WINDOWS\System32\svchost.exe (ID: 2180 |ParentID: 1208)
C:\Program Files\SuperCopier2\SuperCopier2.exe (ID: 2188 |ParentID: 1712)
C:\Program Files\Picasa2\PicasaMediaDetector.exe (ID: 2400 |ParentID: 1712)
C:\Documents and Settings\Administrateur\Local Settings\Application Data\Facebook\Update\FacebookUpdate.exe (ID: 2572 |ParentID: 1712)
C:\WINDOWS\system32\svchost.exe (ID: 2632 |ParentID: 1208)
C:\WINDOWS\system32\Rundll32.exe (ID: 2732 |ParentID: 1712)
C:\Program Files\Samsung\Kies\Kies.exe (ID: 2796 |ParentID: 1712)
C:\Program Files\Samsung\Kies\External\FirmwareUpdate\KiesPDLR.exe (ID: 2900 |ParentID: 1712)
C:\Program Files\Skype\Phone\Skype.exe (ID: 3052 |ParentID: 1712)
C:\Program Files\Yahoo!\SoftwareUpdate\YahooAUService.exe (ID: 3048 |ParentID: 1208)
C:\Program Files\HTC\HTC Sync Manager\HTC Sync\adb.exe (ID: 3336 |ParentID: 2744)
C:\Program Files\AVG\AVG9\avgemc.exe (ID: 3920 |ParentID: 1208)
C:\PROGRA~1\SearchProtect\Main\bin\CltMngSvc.exe (ID: 2176 |ParentID: 1208)
C:\Program Files\Microsoft Office\Office14\ONENOTEM.EXE (ID: 3676 |ParentID: 1712)
C:\PROGRA~1\SearchProtect\SearchProtect\bin\cltmng.exe (ID: 1688 |ParentID: 2176)
C:\PROGRA~1\SearchProtect\UI\bin\cltmngui.exe (ID: 2504 |ParentID: 2176)
C:\Program Files\AVG\AVG9\avgcsrvx.exe (ID: 2956 |ParentID: 3552)
C:\Program Files\AVG\AVG9\avgcsrvx.exe (ID: 936 |ParentID: 3920)
C:\Program Files\Fichiers communs\Research In Motion\USB Drivers\BbDevMgr.exe (ID: 4652 |ParentID: 1208)
C:\Program Files\iPod\bin\iPodService.exe (ID: 4792 |ParentID: 1208)
C:\Program Files\CCP Server\ccpsrv.exe (ID: 5772 |ParentID: 1712)
C:\Program Files\AVAST Software\Avast\setup\avast.setup (ID: 1000 |ParentID: 1136)
################## | Regedit Run |
04 - HKCU\..\Run : [SuperCopier2.exe] C:\Program Files\SuperCopier2\SuperCopier2.exe
04 - HKCU\..\Run : [Picasa Media Detector] C:\Program Files\Picasa2\PicasaMediaDetector.exe
04 - HKCU\..\Run : [Google Update] "C:\Documents and Settings\Administrateur\Local Settings\Application Data\Google\Update\GoogleUpdate.exe" /c
04 - HKCU\..\Run : [Facebook Update] "C:\Documents and Settings\Administrateur\Local Settings\Application Data\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKCU\..\Run : [Search Protection] C:\Program Files\Yahoo!\Search Protection\SearchProtection.exe
04 - HKCU\..\Run : [TBHostSupport] "C:\WINDOWS\system32\Rundll32.exe" "C:\Documents and Settings\Administrateur\Local Settings\Application Data\TBHostSupport\TBHostSupport_0.dll",DLLRunTBHostSupportPlugin
04 - HKCU\..\Run : [KiesPreload] C:\Program Files\Samsung\Kies\Kies.exe /preload
04 - HKCU\..\Run : [KiesAirMessage] C:\Program Files\Samsung\Kies\KiesAirMessage.exe -startup
04 - HKCU\..\Run : [] C:\Program Files\Samsung\Kies\External\FirmwareUpdate\KiesPDLR.exe Run
04 - HKCU\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKCU\..\Run : [123] wscript.exe //B "C:\DOCUME~1\ADMINI~1\LOCALS~1\Temp\123.vbe"
04 - HKLM\..\Run : [SoundMAXPnP] C:\Program Files\Analog Devices\Core\smax4pnp.exe
04 - HKLM\..\Run : [IgfxTray] C:\WINDOWS\system32\igfxtray.exe
04 - HKLM\..\Run : [HotKeysCmds] C:\WINDOWS\system32\hkcmd.exe
04 - HKLM\..\Run : [Persistence] C:\WINDOWS\system32\igfxpers.exe
04 - HKLM\..\Run : [USB Security] C:\Program Files\USB Disk Security\USBGuard.exe
04 - HKLM\..\Run : [Acronis True Image Monitor] C:\Program Files\Acronis\TrueImage\TrueImageMonitor.exe
04 - HKLM\..\Run : [Acronis Scheduler2 Service] C:\Program Files\Fichiers communs\Acronis\Schedule2\schedhlp.exe
04 - HKLM\..\Run : [AVG9_TRAY] C:\PROGRA~1\AVG\AVG9\avgtray.exe
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files\Fichiers communs\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : []
04 - HKLM\..\Run : [HPUsageTrackingLEDM] "C:\Program Files\HP\HP UT LEDM\bin\hppusg.exe" "C:\Program Files\HP\HP UT LEDM\"
04 - HKLM\..\Run : [RIMBBLaunchAgent.exe] C:\Program Files\Fichiers communs\Research In Motion\USB Drivers\RIMBBLaunchAgent.exe
04 - HKLM\..\Run : [VideoDownloadConverter Search Scope Monitor] "C:\PROGRA~1\VIDEOD~2\bar\1.bin\4zsrchmn.exe" /m=2 /w /h
04 - HKLM\..\Run : [VideoDownloadConverter_4z Browser Plugin Loader] C:\PROGRA~1\VIDEOD~2\bar\1.bin\4zbrmon.exe
04 - HKLM\..\Run : [ZGame Anti-Phishing Domain] "C:\Documents and Settings\All Users\Application Data\ZGame Anti-Phishing Domain\zgame_antiphishing.exe"
04 - HKLM\..\Run : [YSearchProtection] "C:\Program Files\Yahoo!\Search Protection\SearchProtection.exe"
04 - HKLM\..\Run : [mobilegeni daemon] C:\Program Files\Mobogenie\DaemonProcess.exe
04 - HKLM\..\Run : [APSDaemon] "C:\Program Files\Fichiers communs\Apple\Apple Application Support\APSDaemon.exe"
04 - HKLM\..\Run : [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
04 - HKLM\..\Run : [KiesTrayAgent] C:\Program Files\Samsung\Kies\KiesTrayAgent.exe
04 - HKLM\..\Run : [iTunesHelper] "C:\Program Files\iTunes\iTunesHelper.exe"
04 - HKLM\..\Run : [avast] "C:\Program Files\AVAST Software\Avast\avastUI.exe" /nogui
04 - HKLM\..\Run : [123] wscript.exe //B "C:\DOCUME~1\ADMINI~1\LOCALS~1\Temp\123.vbe"
04 - HKLM\Software\Microsoft\Windows NT\CurrentVersion\Terminal Server\Install\..\Run : []
04 - HKLM\Software\Microsoft\Windows NT\CurrentVersion\Terminal Server\Install\..\RunOnce : []
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [SuperCopier2.exe] C:\Program Files\SuperCopier2\SuperCopier2.exe
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [Picasa Media Detector] C:\Program Files\Picasa2\PicasaMediaDetector.exe
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [Google Update] "C:\Documents and Settings\Administrateur\Local Settings\Application Data\Google\Update\GoogleUpdate.exe" /c
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [Facebook Update] "C:\Documents and Settings\Administrateur\Local Settings\Application Data\Facebook\Update\FacebookUpdate.exe" /c /nocrashserver
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [Search Protection] C:\Program Files\Yahoo!\Search Protection\SearchProtection.exe
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [TBHostSupport] "C:\WINDOWS\system32\Rundll32.exe" "C:\Documents and Settings\Administrateur\Local Settings\Application Data\TBHostSupport\TBHostSupport_0.dll",DLLRunTBHostSupportPlugin
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [KiesPreload] C:\Program Files\Samsung\Kies\Kies.exe /preload
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [KiesAirMessage] C:\Program Files\Samsung\Kies\KiesAirMessage.exe -startup
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [] C:\Program Files\Samsung\Kies\External\FirmwareUpdate\KiesPDLR.exe Run
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKU\S-1-5-21-1202660629-1343024091-1606980848-500\..\Run : [123] wscript.exe //B "C:\DOCUME~1\ADMINI~1\LOCALS~1\Temp\123.vbe"
04 - HKU\S-1-5-19\..\RunOnce : [JkDefrag] rundll32 advpack.dll,LaunchINFSection JKDEFRAG.INF,RunOnce,1,N
04 - HKU\S-1-5-19\..\RunOnce : [SweetRegistry] rundll32 advpack.dll,LaunchINFSection SweetReg.inf,PerUserStub
04 - HKU\S-1-5-20\..\RunOnce : [JkDefrag] rundll32 advpack.dll,LaunchINFSection JKDEFRAG.INF,RunOnce,1,N
04 - HKU\S-1-5-20\..\RunOnce : [SweetRegistry] rundll32 advpack.dll,LaunchINFSection SweetReg.inf,PerUserStub
04 - HKU\S-1-5-18\..\RunOnce : [JkDefrag] rundll32 advpack.dll,LaunchINFSection JKDEFRAG.INF,RunOnce,1,N
04 - HKU\S-1-5-18\..\RunOnce : [SweetRegistry] rundll32 advpack.dll,LaunchINFSection SweetReg.inf,PerUserStub
04 - HKU\S-1-5-18\..\RunOnce : [SpUninstallDeleteDir] rmdir /s /q "C:\WINDOWS\system32\config\systemprofile\Application Data\SearchProtect"
04 - HKU\S-1-5-18\..\RunOnce : [Del2918468] cmd.exe /Q /D /c del "C:\WINDOWS\TEMP\0.del"
################## | Recherche générique |
Présent! C:\Documents and Settings\Administrateur\Menu Démarrer\Programmes\Démarrage\123.vbe
Présent! C:\DOCUME~1\ADMINI~1\LOCALS~1\Temp\123.vbe
Présent! F:\123.vbe
Présent! F:\NIKON001.lnk
Présent! F:\PRINTFDUMP.lnk
Présent! F:\PRIVATE.lnk
Présent! F:\DCIM.lnk
Présent! F:\MP_ROOT.lnk
Présent! F:\Autorun.inf.lnk
Présent! C:\RECYCLER\S-1-5-21-1202660629-1343024091-1606980848-500
Présent! D:\RECYCLER\S-1-5-21-1202660629-1343024091-1606980848-500
Présent! C:\Documents and Settings\Administrateur\Local Settings\Temp\123.vbe
################## | Registre |
Présent! HKU\S-1-5-21-1202660629-1343024091-1606980848-500\Software\Microsoft\Windows\CurrentVersion\Run|123
Présent! HKLM\Software\Microsoft\Windows\CurrentVersion\Run|123
Présent! HKCU\Software\Microsoft\Windows\CurrentVersion\Run|123
################## | E.O.F | https://www.usbfix.net/ - https://www.sosvirus.net/ | -
Contributeur sécuritéKadjiKN
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Suppression.

# Note : L'ordinateur va redémarrer automatiquement, au redémarrage, clique sur le message transmis par UsbFix et laisse le programme travailler.
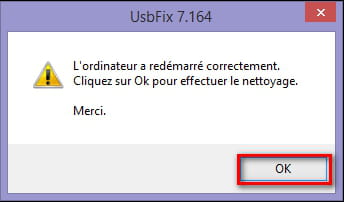
# Laisse travailler l'outil, ton bureau ne sera pas accessible durant la phase de nettoyage, c'est normal.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système ( C:\UsbFix [Clean ?] Nom de l'ordinateur.txt ).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# ->> Tutoriel (aide) en images sur le site de l'auteur.
-
Contributeur sécuritéKadjiKN
Réponds à la suite!
Toujours des raccourcis?
-
Contributeur sécuritéFais l'option Listing
-
merci beaucoup pour mes clé USB que j'ai branché hier on réussi j'aimerai terminer avec la dernière voici le rapport de USBFIX
############################## | UsbFix 7.036 | [Suppression]
Utilisateur: Administrateur (Administrateur) # KEUMENI [ ]
Mis à jour le 20/12/10 par El Desaparecido / C_XX
Lancé à 12:19:43 | 19/02/2014
Site Web: http://www.teamxscript.org
Contact: eldesaparecido@teamxscript.org
CPU: Intel(R) Pentium(R) D CPU 2.80GHz
CPU 2: Intel(R) Pentium(R) D CPU 2.80GHz
Microsoft Windows XP Professionnel (5.1.2600 32-Bit) # Service Pack 3
Internet Explorer 8.0.6001.18702
Pare-feu Windows: Désactivé /!\
Antivirus: avast! Antivirus 5.0.150996957 [Enabled | Updated]
RAM -> 3574 Mo
C:\ (%systemdrive%) -> Disque fixe # 34 Go (5 Go libre(s) - 14%) [] # NTFS
D:\ -> Disque fixe # 40 Go (21 Go libre(s) - 52%) [Nouveau nom] # NTFS
E:\ -> CD-ROM
F:\ -> Disque amovible # 4 Go (3 Go libre(s) - 90%) [] # FAT32
################## | Éléments infectieux |
Supprimé! F:\GT-E2550.lnk
Supprimé! F:\@ftp.lnk
Supprimé! F:\Received.lnk
Supprimé! F:\private.lnk
Supprimé! F:\DCIM.lnk
Supprimé! F:\Photos.lnk
Supprimé! F:\Images.lnk
Supprimé! F:\Videos.lnk
Supprimé! F:\Music.lnk
Supprimé! F:\Sounds.lnk
Supprimé! F:\Other files.lnk
Supprimé! C:\Recycler\S-1-5-21-1202660629-1343024091-1606980848-500
Supprimé! D:\Recycler\S-1-5-21-1202660629-1343024091-1606980848-500
################## | Registre |
################## | Mountpoints2 |
################## | Listing |
[11/09/2013 - 11:19:20 | D ] C:\$AVG
[05/10/2013 - 21:26:51 | N | 3072] C:\ads_err.adi
[05/10/2013 - 21:26:51 | N | 4559] C:\ads_err.adm
[05/10/2013 - 21:48:14 | N | 13785] C:\ads_err.adt
[14/05/2013 - 17:58:59 | N | 0] C:\AUTOEXEC.BAT
[18/02/2014 - 20:42:20 | RASHD ] C:\Autorun.inf
[18/12/2013 - 21:29:27 | N | 212] C:\boot.ini
[14/04/2008 - 13:00:00 | N | 4952] C:\Bootfont.bin
[23/09/2008 - 05:01:14 | | 1364] C:\changelog_MassStorage.txt
[17/02/2014 - 11:47:18 | D ] C:\Config.Msi
[14/05/2013 - 17:58:59 | N | 0] C:\CONFIG.SYS
[11/09/2013 - 10:37:20 | D ] C:\Documents and Settings
[11/09/2013 - 12:06:05 | N | 9] C:\END
[16/09/2013 - 08:49:16 | D ] C:\HP_LaserJet_Professional_CM1410_Series
[14/05/2013 - 17:58:59 | N | 0] C:\IO.SYS
[14/05/2013 - 17:58:59 | N | 0] C:\MSDOS.SYS
[14/09/2013 - 08:29:39 | RHD ] C:\MSOCache
[14/04/2008 - 13:00:00 | N | 47564] C:\NTDETECT.COM
[14/04/2008 - 13:00:00 | N | 252240] C:\ntldr
[03/01/2014 - 20:04:23 | D ] C:\ONE TOUCH Upgrade S 2.8.0
[19/02/2014 - 09:00:53 | ASH | 792723456] C:\pagefile.sys
[12/02/2014 - 11:50:32 | N | 13030] C:\PDOXUSRS.NET
[20/11/2013 - 14:32:06 | N | 233308] C:\process.txt
[17/02/2014 - 18:26:46 | D ] C:\Program Files
[19/02/2014 - 12:34:24 | SHD ] C:\RECYCLER
[19/02/2014 - 09:05:01 | N | 579] C:\STAT.DAT
[14/05/2013 - 19:37:54 | SHD ] C:\System Volume Information
[19/02/2014 - 12:34:25 | D ] C:\UsbFix
[17/02/2014 - 18:20:03 | N | 19142] C:\UsbFix [Clean 2] KEUMENI.txt
[17/02/2014 - 19:18:33 | N | 15804] C:\UsbFix [Clean 4] KEUMENI.txt
[17/02/2014 - 17:24:17 | N | 14340] C:\UsbFix [Scan 1] KEUMENI.txt
[17/02/2014 - 19:30:40 | N | 12969] C:\UsbFix [Scan 2] KEUMENI.txt
[18/02/2014 - 09:28:51 | N | 13153] C:\UsbFix [Scan 3] KEUMENI.txt
[19/02/2014 - 12:34:25 | A | 1324] C:\UsbFix.txt
[18/02/2014 - 20:43:26 | N | 347695644] C:\UsbFix_Upload_Me_KEUMENI.zip
[23/11/2013 - 14:42:05 | D ] C:\Users
[18/02/2014 - 09:58:20 | D ] C:\WINDOWS
[11/09/2013 - 12:43:32 | D ] D:\$AVG
[16/09/2013 - 08:09:33 | D ] D:\5c32dca40a47497382265e8601
[18/02/2014 - 20:42:20 | RASHD ] D:\Autorun.inf
[14/11/2013 - 09:06:55 | N | 1343488] D:\BD IMPRESSION.mdb
[03/10/2013 - 07:55:52 | D ] D:\dossiers
[16/09/2013 - 21:22:08 | D ] D:\f484d51d99b5efaaf1b600fa46
[11/09/2013 - 13:20:07 | D ] D:\FIND_MOZ_EXT
[20/11/2013 - 15:14:50 | D ] D:\nkk
[19/02/2014 - 12:34:24 | SHD ] D:\RECYCLER
[05/12/2013 - 13:41:19 | D ] D:\samsung
[11/09/2013 - 13:20:10 | D ] D:\searchplugins
[28/12/2013 - 14:57:26 | D ] D:\setup imprimante hp
[14/05/2013 - 18:26:08 | SHD ] D:\System Volume Information
[14/11/2013 - 14:48:31 | N | 678945792] D:\ubuntu-13.10-desktop-i386.iso
[01/06/2012 - 10:00:00 | D ] F:\@ftp
[01/06/2012 - 10:00:02 | D ] F:\Received
[01/01/2000 - 09:21:24 | D ] F:\private
[01/01/2000 - 09:21:48 | D ] F:\DCIM
[01/01/2013 - 00:01:00 | D ] F:\Photos
[06/07/2013 - 08:43:00 | N | 0] F:\GT-E2550.samsung
[06/07/2013 - 08:43:00 | D ] F:\Images
[06/07/2013 - 08:43:00 | D ] F:\Videos
[06/07/2013 - 08:43:00 | D ] F:\Music
[06/07/2013 - 08:43:00 | D ] F:\Sounds
[06/07/2013 - 08:43:00 | D ] F:\Other files
[26/10/2013 - 19:31:58 | N | 165608] F:\123.vbe
################## | Vaccin |
C:\Autorun.inf -> Dossier créé par UsbFix (El Desaparecido & C_XX)
D:\Autorun.inf -> Dossier créé par UsbFix (El Desaparecido & C_XX)
F:\Autorun.inf -> Dossier créé par UsbFix (El Desaparecido & C_XX)
################## | Upload |
Veuillez envoyer le fichier: C:\UsbFix_Upload_Me_KEUMENI.zip
http://www.teamxscript.org/Upload.php
Merci de votre contribution.
################## | E.O.F | -
Contributeur sécuritéToujours des raccourcis ?
-
Contributeur sécuritéTu devrais continuer...


