
Pc infecte
Voila, je crois que je suis infecte par des virus. j'utilise ie, mozzilla et opera sur mon ordi et quand je surf plusieurs fenetres s'ouvre sans que je demande rien. sur ie j'ai mysearchdial toolbar que je n'arrive pas a suprimer. mozzilla me demande la mise a jour java que je n'arrive pas a installer. quelqu'un peut m'aider svp? j'utilise windows xp sur un hp550 et j'ai avast comme antivirus.
21 réponses
Des symptômes d'infection informatique sont décrits: des fenêtres qui s'ouvrent sans demande et l'apparition de MySearchDial dans Internet Explorer, sur Windows XP avec Avast et plusieurs navigateurs tels que Mozilla et Opera. Plusieurs réponses évoquent un adware lié à MySearchDial et préconisent l'utilisation d'outils comme AdwCleaner pour supprimer les fichiers, entrées de registre et extensions indésirables afin de récupérer le contrôle du navigateur. Des échanges recommandent aussi de vérifier l'absence de programmes installés non désirés et de nettoyer les profils Firefox et les préférences, puis de réinitialiser la page d'accueil et les moteurs de recherche. Certaines contributions partagent des rapports détaillés via un lien et soulignent que le nettoyage peut nécessiter plusieurs passages et une vérification des tâches planifiées.
-
Salut,
j'ai eu le même problème que toi en ce qui concerne MySearchDial.
Ouvre firefox, puis clique sur "outils" en haut, puis sur "option".
Ensuite, clique sur l'onglet principal "Général", puis dans -Démarrage-, sélectionne "Afficher ma page d'accueil. Puis tu met l'URL Google.com dans la case du dessous.
-
Contributeur sécuritéAvant de faire la manip de securitest j'aimerais que tu passes ceci
http://www.sosvirus.net/infected-scanner-t47622.html
-
-
-
@lilidurhoneje n'arrive plus à me connecter à Internet. on me dit que la connexion à été refusé par le serveur proxy. je vousécris depuis mon smartphone. comment faire pour rétablir la connexion?
-
Salut lilidurhone
Merci pour ton aide, j'ai reetablie ma connexion Internet.
Voici le rapport de adwcleaner
# AdwCleaner v3.019 - Report created 20/02/2014 at 11:51:38
# Updated 17/02/2014 by Xplode
# Operating System : Microsoft Windows XP Service Pack 2 (32 bits)
# Username : user - USER-5D65D1BA2F
# Running from : C:\Documents and Settings\user\Desktop\adwcleaner.exe
# Option : Clean
***** [ Services ] *****
***** [ Files / Folders ] *****
Folder Deleted : C:\Documents and Settings\All Users\Application Data\NCH Software
Folder Deleted : C:\Program Files\Mobogenie
Folder Deleted : C:\Program Files\Mysearchdial
Folder Deleted : C:\Program Files\NCH Software
Folder Deleted : C:\Program Files\optimizer pro
Folder Deleted : C:\Program Files\Re-markit
Folder Deleted : C:\Program Files\HQ-Video-Profession-1.3
Folder Deleted : C:\Documents and Settings\user\Local Settings\Application Data\BrowserSafeguard
Folder Deleted : C:\Documents and Settings\user\Local Settings\Application Data\genienext
Folder Deleted : C:\Documents and Settings\user\Local Settings\Application Data\Mobogenie
Folder Deleted : C:\Documents and Settings\user\Application Data\DigitalSites
Folder Deleted : C:\Documents and Settings\user\Application Data\Mysearchdial
Folder Deleted : C:\Documents and Settings\user\Application Data\newnext.me
Folder Deleted : C:\Documents and Settings\user\Application Data\pdfforge
Folder Deleted : C:\Documents and Settings\user\My Documents\Mobogenie
Folder Deleted : C:\Documents and Settings\user\Application Data\Mozilla\Firefox\Profiles\9w3o3ej5.default\Extensions\13c471d9-6cbb-4c08-9dd1-8dc16c66bb1f@cf5065af-ca24-464a-a637-af7582a82514.com
File Deleted : C:\Documents and Settings\user\Application Data\Mozilla\Firefox\Profiles\9w3o3ej5.default\searchplugins\Mysearchdial.xml
File Deleted : C:\Documents and Settings\Administrator\Application Data\Mozilla\Firefox\Profiles\5doq1yf5.default\searchplugins\Mysearchdial.xml
File Deleted : C:\Documents and Settings\user\Application Data\Mozilla\Firefox\Profiles\9w3o3ej5.default\user.js
File Deleted : C:\WINDOWS\Tasks\Re-markit Update.job
File Deleted : C:\WINDOWS\Tasks\HQ-Video-Profession-1.3-chromeinstaller.job
File Deleted : C:\WINDOWS\Tasks\HQ-Video-Profession-1.3-codedownloader.job
File Deleted : C:\WINDOWS\Tasks\HQ-Video-Profession-1.3-enabler.job
File Deleted : C:\WINDOWS\Tasks\HQ-Video-Profession-1.3-firefoxinstaller.job
File Deleted : C:\WINDOWS\Tasks\HQ-Video-Profession-1.3-updater.job
***** [ Shortcuts ] *****
***** [ Registry ] *****
Value Deleted : HKCU\Software\Microsoft\Windows\CurrentVersion\Run [NextLive]
Key Deleted : HKLM\SOFTWARE\Classes\AppID\escort.DLL
Key Deleted : HKLM\SOFTWARE\Classes\AppID\escortApp.DLL
Key Deleted : HKLM\SOFTWARE\Classes\AppID\escortEng.DLL
Key Deleted : HKLM\SOFTWARE\Classes\AppID\escorTlbr.DLL
Key Deleted : HKLM\SOFTWARE\Classes\AppID\esrv.EXE
Key Deleted : HKLM\SOFTWARE\Classes\esrv.mysearchdialesrvc
Key Deleted : HKLM\SOFTWARE\Classes\esrv.mysearchdialesrvc.1
Key Deleted : HKLM\SOFTWARE\Classes\mysearchdial.mysearchdialappCore
Key Deleted : HKLM\SOFTWARE\Classes\mysearchdial.mysearchdialappCore.1
Key Deleted : HKLM\SOFTWARE\Classes\mysearchdial.mysearchdialdskBnd
Key Deleted : HKLM\SOFTWARE\Classes\mysearchdial.mysearchdialdskBnd.1
Key Deleted : HKLM\SOFTWARE\Classes\mysearchdial.mysearchdialHlpr
Key Deleted : HKLM\SOFTWARE\Classes\mysearchdial.mysearchdialHlpr.1
Key Deleted : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Paths\MobogenieAdd
Key Deleted : HKLM\SOFTWARE\Classes\CrossriderApp0051578.BHO
Key Deleted : HKLM\SOFTWARE\Classes\CrossriderApp0051578.BHO.1
Key Deleted : HKLM\SOFTWARE\Classes\CrossriderApp0051578.Sandbox
Key Deleted : HKLM\SOFTWARE\Classes\CrossriderApp0051578.Sandbox.1
Key Deleted : HKLM\SOFTWARE\Classes\AppID\{09C554C3-109B-483C-A06B-F14172F1A947}
Key Deleted : HKLM\SOFTWARE\Classes\AppID\{4E1E9D45-8BF9-4139-915C-9F83CC3D5921}
Key Deleted : HKLM\SOFTWARE\Classes\AppID\{B12E99ED-69BD-437C-86BE-C862B9E5444D}
Key Deleted : HKLM\SOFTWARE\Classes\AppID\{C292AD0A-C11F-479B-B8DB-743E72D283B0}
Key Deleted : HKLM\SOFTWARE\Classes\AppID\{CA5CAA63-B27C-4963-9BEC-CB16A36D56F8}
Key Deleted : HKLM\SOFTWARE\Classes\AppID\{D7EE8177-D51E-4F89-92B6-83EA2EC40800}
Key Deleted : HKLM\SOFTWARE\Classes\CLSID\{1AA60054-57D9-4F99-9A55-D0FBFBE7ECD3}
Key Deleted : HKLM\SOFTWARE\Classes\CLSID\{3004627E-F8E9-4E8B-909D-316753CBA923}
Key Deleted : HKLM\SOFTWARE\Classes\CLSID\{4ED063C9-4A0B-4B44-A9DC-23AFF424A0D3}
Key Deleted : HKLM\SOFTWARE\Classes\CLSID\{C358B3D0-B911-41E3-A276-E7D43A6BA56D}
Key Deleted : HKLM\SOFTWARE\Classes\CLSID\{D40753C7-8A59-4C1F-BE88-C300F4624D5B}
Key Deleted : HKLM\SOFTWARE\Classes\CLSID\{EF5625A3-37AB-4BDB-9875-2A3D91CD0DFD}
Key Deleted : HKLM\SOFTWARE\Classes\CLSID\{11111111-1111-1111-1111-110511151178}
Key Deleted : HKLM\SOFTWARE\Classes\CLSID\{22222222-2222-2222-2222-220522152278}
Key Deleted : HKLM\SOFTWARE\Classes\Interface\{55555555-5555-5555-5555-550555155578}
Key Deleted : HKLM\SOFTWARE\Classes\Interface\{66666666-6666-6666-6666-660566156678}
Key Deleted : HKLM\SOFTWARE\Classes\TypeLib\{4E1E9D45-8BF9-4139-915C-9F83CC3D5921}
Key Deleted : HKLM\SOFTWARE\Classes\TypeLib\{C292AD0A-C11F-479B-B8DB-743E72D283B0}
Key Deleted : HKLM\SOFTWARE\Classes\TypeLib\{D7EE8177-D51E-4F89-92B6-83EA2EC40800}
Key Deleted : HKLM\SOFTWARE\Classes\TypeLib\{44444444-4444-4444-4444-440544154478}
Key Deleted : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{EF5625A3-37AB-4BDB-9875-2A3D91CD0DFD}
Key Deleted : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{11111111-1111-1111-1111-110511151178}
Key Deleted : HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{3004627E-F8E9-4E8B-909D-316753CBA923}
Key Deleted : HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{EF5625A3-37AB-4BDB-9875-2A3D91CD0DFD}
Key Deleted : HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{11111111-1111-1111-1111-110511151178}
Key Deleted : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Ext\PreApproved\{11111111-1111-1111-1111-110511151178}
Key Deleted : HKLM\SOFTWARE\Microsoft\Internet Explorer\Low Rights\ElevationPolicy\{219046AE-358F-4CF1-B1FD-2B4DE83642A8}
Key Deleted : HKLM\SOFTWARE\Microsoft\Internet Explorer\Low Rights\ElevationPolicy\{0eb1e20d-5e04-43b9-a619-8258eb791cf4}
Key Deleted : HKLM\SOFTWARE\Microsoft\Internet Explorer\Low Rights\ElevationPolicy\{6dc2f884-1b81-421c-bfb5-bfb912176116}
Key Deleted : HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{77AA745B-F4F8-45DA-9B14-61D2D95054C8}
Key Deleted : HKLM\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\{77AA745B-F4F8-45DA-9B14-61D2D95054C8}
Value Deleted : HKLM\SOFTWARE\Microsoft\Internet Explorer\Toolbar [{3004627E-F8E9-4E8B-909D-316753CBA923}]
Key Deleted : HKCU\Software\Conduit
Key Deleted : HKCU\Software\Crossrider
Key Deleted : HKCU\Software\dsiteproducts
Key Deleted : HKCU\Software\DynConIE
Key Deleted : HKCU\Software\InstallCore
Key Deleted : HKCU\Software\installedbrowserextensions
Key Deleted : HKCU\Software\mysearchdial
Key Deleted : HKCU\Software\NCH Software
Key Deleted : HKCU\Software\HQ-Video-Profession-1.3
Key Deleted : HKCU\Software\AppDataLow\{1146AC44-2F03-4431-B4FD-889BC837521F}
Key Deleted : HKLM\Software\{3A7D3E19-1B79-4E4E-BD96-5467DA2C4EF0}
Key Deleted : HKLM\Software\{6791A2F3-FC80-475C-A002-C014AF797E9C}
Key Deleted : HKLM\Software\Conduit
Key Deleted : HKLM\Software\InstallCore
Key Deleted : HKLM\Software\mysearchdial
Key Deleted : HKLM\Software\NCH Software
Key Deleted : HKLM\Software\Speedchecker Limited
Key Deleted : HKLM\Software\Vittalia
Key Deleted : HKLM\Software\HQ-Video-Profession-1.3
Key Deleted : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\HQ-Video-Profession-1.3
Key Deleted : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\MyPC Backup
Key Deleted : HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\App Management\ARPCache\HQ-Video-Profession-1.3
***** [ Browsers ] *****
-\\ Internet Explorer v7.0.6000.20583
Setting Restored : HKLM\SOFTWARE\Microsoft\Internet Explorer\Main [Start Page]
Setting Restored : HKLM\SOFTWARE\Microsoft\Internet Explorer\AboutURls [Tabs]
-\\ Mozilla Firefox v27.0.1 (fr)
[ File : C:\Documents and Settings\user\Application Data\Mozilla\Firefox\Profiles\9w3o3ej5.default\prefs.js ]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.InstallationThankYouPage", true);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.InstallationTime", 1392812449);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.active", true);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.addressbar", "NA");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.addressbarenhanced", "");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.asyncdb.was_copied", "true");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.asyncdb_dbWasSet", true);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.asyncdb_dbWasSet_FF25_FIX", true);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.asyncinternaldb.was_copied", "true");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.asyncinternaldb_dbWasSet", true);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.asyncinternaldb_dbWasSet_FF25_FIX", true);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.backgroundver", 1);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.certdomaininstaller", "");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.changeprevious", false);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.cookie.InstallationTime.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard Time)");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.cookie.InstallationTime.value", "%221392812449%22");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.cookie.InstallerParams.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard Time)");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.cookie.InstallerParams.value", "%7B%22source_id%22%3A%22001075%22%2C%22sub_id%22%3A%220%22%2C%22uz[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.cookie.iframe-exists.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard Time)");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.cookie.iframe-exists.value", "true");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.cookie.jw_token.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard Time)");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.cookie.jw_token.value", "%2244beda8e-2a9c-0f16-8e88-6f580937e594%22");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.description", "HQ Videos is an add-on for your Internet browser that enhances your online experien[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.domain", "");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.enablesearch", false);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.homepage", "");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.iframe", false);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.InstallerIdentifiers.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard [...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.InstallerIdentifiers.value", "%7B%22installer_bic%22%3A%2221FB77914C99413EB8470632C9083[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.InstallerParams.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard Time)[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.InstallerParams.value", "%7B%22source_id%22%3A%22001075%22%2C%22sub_id%22%3A%220%22%2C%[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.InstallerParamsCache.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard [...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.InstallerParamsCache.value", "%7B%22source_id%22%3A%22001075%22%2C%22sub_id%22%3A%220%2[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.InstallerUserIdentifiersCache.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance [...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.InstallerUserIdentifiersCache.value", "%7B%22installer_bic%22%3A%2221FB77914C99413EB847[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_appVer.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard Time[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_appVer.value", "9");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_lastVersion.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_lastVersion.value", "1");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_meta.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard Time)"[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_meta.value", "%7B%7D");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_nextCheck.expiration", "Thu Feb 20 2014 13:54:16 GMT+0100 (Romance Standard T[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_nextCheck.value", "true");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_queue.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard Time)[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_queue.value", "%7B%7D");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_remote_resources.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Sta[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.Resources_remote_resources.value", "%7B%22remoteId%22%3A0%7D");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.__defualt_browser__.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard T[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.__defualt_browser__.value", "%22ff%22");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.installer.expiration", "Fri Feb 01 2030 00:00:00 GMT+0100 (Romance Standard Time)");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.installer.value", "%7B%22InstallerIdentifiers%22%3A%7B%22installer_bic%22%3A%2221FB7791[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.monetization_plugin_last_executable_request.expiration", "Thu Feb 20 2014 22:44:48 GMT+[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.internaldb.monetization_plugin_last_executable_request.value", "%22hxxp%3A//spybotupdates.com/file[...]
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.lastDailyReport", "1392879255183");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.lastUpdate", "1392879256063");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.manifesturl", "");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.name", "HQ-Video-Profession-1.3");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.newtab", "");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.opensearch", "");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.pluginsurl", "hxxps://w9u6a2p6.ssl.hwcdn.net/plugin/apps/51578/plugins/093/ff/plugins.json");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.pluginsversion", 5);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.publisher", "HQ-Video");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.searchstatus", 0);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.setnewtab", false);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.thankyou", "");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.updateinterval", 360);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.51578.ver", 9);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.FilesValidatorDueTime", "1392879313201");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.apps", "51578");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.bic", "1444a17e1227d30ea8a409e681585528");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.cid", 51578);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.firstrun", false);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.hadappinstalled", true);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.installationdate", 1392812483);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.modetype", "production");
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.reportInstall", true);
Line Deleted : user_pref("extensions.a13c471d96cbb4c089dd18dc16c66bb1fcf5065afca24464aa637af7582a82514com51578.statsDailyCounter", 3);
Line Deleted : user_pref("extensions.crossrider.bic", "1444a17e1227d30ea8a409e681585528");
[ File : C:\Documents and Settings\Administrator\Application Data\Mozilla\Firefox\Profiles\5doq1yf5.default\prefs.js ]
Line Deleted : user_pref("browser.startup.homepage", "hxxp://start.mysearchdial.com/?f=1&a=tele0101&cd=2XzuyEtN2Y1L1QzutDtDtBtCtDtDyBtCyDtD0C0D0CyBtB0EtN0D0Tzu0SyByEyDtN1L2XzutBtFtBtFtCyDtFtCyDzytBtN1L1CzutDzytDtCtG[...]
*************************
AdwCleaner[R0].txt - [4540 octets] - [13/09/2013 15:18:36]
AdwCleaner[R1].txt - [22549 octets] - [20/02/2014 11:47:42]
AdwCleaner[S0].txt - [4627 octets] - [13/09/2013 15:19:35]
AdwCleaner[S1].txt - [22251 octets] - [20/02/2014 11:51:38]
########## EOF - C:\AdwCleaner\AdwCleaner[S1].txt - [22312 octets] ########## -
-
-
Salut,
Si tu arrives encore à accéder à Internet, télécharge le logiciel CCleaner, ainsi que MBAM Malware Byte's Anti Malwares, tu peux aussi télécharger ADW cleaner,
Après avoir téléchargé et installé tout ça, en vérifiant que tu DÉCOCHES TOUTES LES CASES ou il te demande d'installer un toolbar ou autre. CE QUE TU NE FAISAIS PAS AUPARAVANT.
Tu pourras lancer les analyses. Et après moult redémarrage et heures d'attente, ton PC devrait être plus ou moins clean. Vérifier dans le Panneau de config/ ajouter supprimer des programmes ; si tu n'as pas installé des logiciels genre delta toolbar ou optimizer pro ou des débilités du genre :)
En espérant t'avoir aidé,
Salutations,
RODEPUMPS (IT)-
File Deleted : C:\Documents and Settings\user\Application Data\Mozilla\Firefox\Profiles\9w3o3ej5.default\searchplugins\Mysearchdial.xml
File Deleted : C:\Documents and Settings\Administrator\Application Data\Mozilla\Firefox\Profiles\5doq1yf5.default\searchplugins\Mysearchdial.xml
et voila tu as bien supprimer mycherdial
pense juste à faire nettoyage des fichier temporaires avec ccleaner
-
-
est ce que ton avast reagit? si oui c'est un virus.si non c'est que c'est programme que tu as installe donc verifie tes fichier installes.
-
Contributeur sécuritéHello
il faut décocher les proxy dans ton navigateur
-
Contributeur sécurité
-
Salut lilidurhone
Je n'arrive pas a telecharger le logiciel. Voici le message d'erreur que je recois;
'Erreur d'encodage de contenu
La page que vous essayez de voir ne peut être affichée car elle utilise un type de compression invalide ou non pris en charge.
Veuillez contacter les propriétaires du site pour les informer de ce problème.'
Que faire?-
Essaye ce lien : https://www.sosvirus.net/telecharger/infected-scanner/
-
-
Bonjour lilidurhone;
J'ai fais le teste et il est négatif; il me dit que pas de virus. -
Contributeur sécuritéSuper
Patientes un peu
-
Contributeur sécurité* Télécharge ZHPDiag (de Nicolas Coolman)
https://www.zebulon.fr/telechargements/securite/systeme/zhpdiag.html ou https://www.commentcamarche.net/telecharger/utilitaires/24803-zhpdiag/
* Au cas où le premier lien ne marcherai pas, clique sur celui de dessous
ftp://zebulon.fr/ZHPDiag2.exe
* Laisse toi guider lors de l'installation, il se lancera automatiquement à la fin.
* Surtout, n'oublie pas d'installer son icône sur le bureau l'icône est en forme de parchemin
https://www.cjoint.com/13sp/CIvuQfap3YY_zhpdiag.png
* A l'ouverture du logiciel il te sera proposé deux options "rechercher" et "configurer"
* Cliques sur configurer
* Tournevis puis tous
* Clique sur l'icône représentant une loupe + (« Lancer le diagnostic »)
* Enregistre le rapport sur ton Bureau à l'aide de l'icône représentant une disquette
* Pour héberger le rapport, rends toi sur cjoint.com
* Clique sur choisissez un fichier va chercher le rapport dans ton PC.
* Le rapport est hébergé:
- Pour XP : C:\Documents and Settings\username\Local Settings\Application Data\ZHP
- Depuis Vista : C:\Users\username\AppData\Roaming\ZHP
* Une fois le rapport trouvé, sélectionne le, et clique sur Ouvrir
* Choisis le type de diffusion(je te conseille privée 4 jours il sera détruit)
* Puis cliques sur créer le lien cjoint
* Une fois que tu auras obtenu le lien copies colle dans ta prochaine réponse
* Pour t'aider https://www.commentcamarche.net/faq/29493-utiliser-cjoint-pour-heberger-des-fichiers
-
Bonsoir lilidurhone,
J'ai suivie tes indications et voici le lien du rapport:
https://www.cjoint.com/?3BvvLkqk97d
En attendant ta reponse,
cdt -
Contributeur sécurité###########| Canned Recherche
# Télécharge UsbFix par El Desaparecido sur ton Bureau.
# Si ton antivirus affiche une alerte, ignore-la et désactive l'antivirus temporairement.
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Recherche.

# Laisse travailler l'outil.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système ( C:\UsbFix [Scan ?] Nom de l'ordinateur.txt ).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# Tutoriel (aide) en images
-
Bonjour Lilidurhone,
Merrci pour ton aide. J'ai suivi tes conseils et voici le rapport:
############################## | UsbFix V 7.165 | [Research]
User: user (Administrator) # USER-5D65D1BA2F
Updated 20/02/2014 by El Desaparecido - Team SosVirus
Started at 12:11:02 | 23/02/2014
Website : http://www.en.usbfix.net/
Changelog : http://www.en.usbfix.net/changelog/
Support : https://www.sosvirus.net/
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : http://www.en.usbfix.net/contact/
PC: Hewlett-Packard (3618)
CPU: Intel(R) Core(TM)2 Duo CPU T5470 @ 1.60GHz
CPU: Intel(R) Core(TM)2 Duo CPU T5470 @ 1.60GHz
RAM -> [Total : 2039 Mo| Free : 1291 Mo]
Bios: Hewlett-Packard
Boot: Normal boot
OS: Microsoft Windows XP Professional (5.1.2600 32-Bit) Service Pack 2
WB: Windows Internet Explorer : 7.0.5730.11
WB: Mozilla Firefox : 27.0.1
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
FW: Windows FireWall [Enabled]
C:\ (%systemdrive%) -> Fixed drive # 30 Gb (12 Mb free - 40%) [System] # NTFS
D:\ -> Fixed drive # 203 Gb (134 Mb free - 66%) [Discul] # NTFS
E:\ -> CD-ROM
F:\ -> Removable drive # 982 Mb (896 Mb free - 91%) [CANON_DC] # FAT
G:\ -> Removable drive # 242 Mb (37 Mb free - 15%) [] # FAT32
H:\ -> Removable drive # 15 Gb (14 Mb free - 92%) [CLÉ USB] # FAT32
I:\ -> Fixed drive # 233 Gb (97 Mb free - 42%) [DISQUE EXTE] # FAT32
J:\ -> Removable drive # 984 Mb (414 Mb free - 42%) [FLASH DISK] # FAT
K:\ -> Removable drive # 7 Gb (7 Mb free - 98%) [] # FAT32
################## | Active Processes |
C:\WINDOWS\System32\smss.exe (ID: 584 |ParentID: 4)
C:\WINDOWS\system32\winlogon.exe (ID: 656 |ParentID: 584)
C:\WINDOWS\system32\services.exe (ID: 700 |ParentID: 656)
C:\WINDOWS\system32\lsass.exe (ID: 712 |ParentID: 656)
C:\WINDOWS\system32\svchost.exe (ID: 884 |ParentID: 700)
C:\WINDOWS\System32\svchost.exe (ID: 992 |ParentID: 700)
C:\Program Files\WIDCOMM\Bluetooth Software\bin\btwdins.exe (ID: 1016 |ParentID: 700)
C:\WINDOWS\system32\svchost.exe (ID: 1040 |ParentID: 700)
C:\WINDOWS\system32\spoolsv.exe (ID: 1616 |ParentID: 700)
C:\WINDOWS\system32\ctfmon.exe (ID: 1748 |ParentID: 1724)
C:\Program Files\Avira\AntiVir Desktop\sched.exe (ID: 1764 |ParentID: 700)
C:\Program Files\Analog Devices\Core\smax4pnp.exe (ID: 1944 |ParentID: 1732)
C:\Program Files\Hewlett-Packard\HP Quick Launch Buttons\QlbCtrl.exe (ID: 1952 |ParentID: 1732)
C:\Program Files\Synaptics\SynTP\SynTPEnh.exe (ID: 1968 |ParentID: 1732)
C:\WINDOWS\system32\igfxtray.exe (ID: 1980 |ParentID: 1732)
C:\WINDOWS\system32\hkcmd.exe (ID: 172 |ParentID: 1732)
C:\WINDOWS\system32\igfxpers.exe (ID: 152 |ParentID: 1732)
C:\WINDOWS\system32\igfxsrvc.exe (ID: 224 |ParentID: 884)
C:\WINDOWS\vVX1000.exe (ID: 236 |ParentID: 1732)
C:\Program Files\Avira\AntiVir Desktop\avgnt.exe (ID: 268 |ParentID: 1732)
C:\Program Files\Common Files\Java\Java Update\jusched.exe (ID: 340 |ParentID: 1732)
C:\program files\real\realplayer\update\realsched.exe (ID: 352 |ParentID: 1732)
C:\Program Files\Common Files\Ahead\lib\NMBgMonitor.exe (ID: 396 |ParentID: 1732)
C:\Program Files\Skype\Phone\Skype.exe (ID: 448 |ParentID: 1732)
C:\Program Files\WIDCOMM\Bluetooth Software\BTTray.exe (ID: 504 |ParentID: 1732)
C:\PROGRA~1\WIDCOMM\BLUETO~1\BTSTAC~1.EXE (ID: 1376 |ParentID: 884)
C:\WINDOWS\system32\agrsmsvc.exe (ID: 1524 |ParentID: 700)
C:\Program Files\Avira\AntiVir Desktop\avguard.exe (ID: 816 |ParentID: 700)
C:\Program Files\Java\jre7\bin\jqs.exe (ID: 2028 |ParentID: 700)
C:\Documents and Settings\All Users\Application Data\MovieMode\MovieModeService.exe (ID: 2068 |ParentID: 700)
C:\Program Files\RealNetworks\RealDownloader\rndlresolversvc.exe (ID: 2316 |ParentID: 700)
C:\Program Files\Avira\AntiVir Desktop\avshadow.exe (ID: 2384 |ParentID: 816)
C:\WINDOWS\system32\svchost.exe (ID: 2488 |ParentID: 700)
C:\Documents and Settings\All Users\Application Data\MovieMode\MovieMode.exe (ID: 2620 |ParentID: 2068)
C:\Program Files\Hewlett-Packard\Shared\hpqwmiex.exe (ID: 2888 |ParentID: 700)
C:\Program Files\Hewlett-Packard\HP Quick Launch Buttons\Com4QLBEx.exe (ID: 4036 |ParentID: 700)
C:\WINDOWS\System32\svchost.exe (ID: 1556 |ParentID: 700)
C:\Program Files\Mozilla Firefox\firefox.exe (ID: 944 |ParentID: 1732)
C:\Program Files\Mozilla Firefox\plugin-container.exe (ID: 3856 |ParentID: 944)
C:\WINDOWS\explorer.exe (ID: 768 |ParentID: 656)
################## | Regedit Run |
04 - HKCU\..\Run : [BgMonitor_{79662E04-7C6C-4d9f-84C7-88D8A56B10AA}] "C:\Program Files\Common Files\Ahead\lib\NMBgMonitor.exe"
04 - HKCU\..\Run : [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
04 - HKCU\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKCU\..\Run : [SURVIVAL] wscript.exe //B "C:\DOCUME~1\user\LOCALS~1\Temp\SURVIVAL.vbe"
04 - HKLM\..\Run : [SoundMAXPnP] C:\Program Files\Analog Devices\Core\smax4pnp.exe
04 - HKLM\..\Run : [QlbCtrl.exe] C:\Program Files\Hewlett-Packard\HP Quick Launch Buttons\QlbCtrl.exe /Start
04 - HKLM\..\Run : [SynTPEnh] C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
04 - HKLM\..\Run : [IgfxTray] C:\WINDOWS\system32\igfxtray.exe
04 - HKLM\..\Run : [HotKeysCmds] C:\WINDOWS\system32\hkcmd.exe
04 - HKLM\..\Run : [Persistence] C:\WINDOWS\system32\igfxpers.exe
04 - HKLM\..\Run : [VX1000] C:\WINDOWS\vVX1000.exe
04 - HKLM\..\Run : [avgnt] "C:\Program Files\Avira\AntiVir Desktop\avgnt.exe" /min
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [TkBellExe] "C:\program files\real\realplayer\update\realsched.exe" -osboot
04 - HKLM\..\Run : [SURVIVAL] wscript.exe //B "C:\DOCUME~1\user\LOCALS~1\Temp\SURVIVAL.vbe"
04 - HKLM\..\RunOnce : []
04 - HKLM\Software\Microsoft\Windows NT\CurrentVersion\Terminal Server\Install\..\Run : []
04 - HKLM\Software\Microsoft\Windows NT\CurrentVersion\Terminal Server\Install\..\RunOnce : []
04 - HKU\S-1-5-21-1085031214-2000478354-682003330-1003\..\Run : [BgMonitor_{79662E04-7C6C-4d9f-84C7-88D8A56B10AA}] "C:\Program Files\Common Files\Ahead\lib\NMBgMonitor.exe"
04 - HKU\S-1-5-21-1085031214-2000478354-682003330-1003\..\Run : [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
04 - HKU\S-1-5-21-1085031214-2000478354-682003330-1003\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKU\S-1-5-21-1085031214-2000478354-682003330-1003\..\Run : [SURVIVAL] wscript.exe //B "C:\DOCUME~1\user\LOCALS~1\Temp\SURVIVAL.vbe"
04 - HKU\S-1-5-18\..\Run : [CTFMON.EXE] C:\WINDOWS\system32\ctfmon.exe
################## | Generic Research |
Found ! C:\WINDOWS\system32\user.exe
Found ! G:\SURVIVAL.vbe
Found ! K:\SURVIVAL.vbe
Found ! F:\DCIM.lnk
Found ! G:\mr_x_2014_02_01.lnk
Found ! G:\12097-01.lnk
Found ! G:\12097-25.lnk
Found ! H:\CV security.lnk
Found ! H:\Calendrier 2013-2015 ABM 1 et2.lnk
Found ! H:\1532844786.lnk
Found ! H:\winamp_cache_0001.lnk
Found ! H:\pmp_usb.lnk
Found ! K:\CV Elena CHIPER.lnk
Found ! K:\fevrier.lnk
Found ! K:\Quand j'étais à l'école.lnk
Found ! K:\Hist.lnk
Found ! K:\33230DIX11-I.lnk
Found ! K:\33230DIX11-O.lnk
Found ! K:\Lettres de motivation (Elena).lnk
Found ! K:\ENIK-NARIK.lnk
Found ! K:\Attachments_2011_10_25.lnk
Found ! K:\Lettre de motiv Elena (16-4-2013).lnk
Found ! K:\BTS CV Elena CHIPER.lnk
Found ! K:\Voix Elena 2012.lnk
Found ! K:\Devis ABM CHIPER.lnk
Found ! K:\traduceri Babara.lnk
Found ! K:\La fête Martisor en Moldavie.lnk
Found ! K:\Fizica 1.lnk
Found ! K:\Fizica 2.lnk
Found ! K:\Chapitre 1 - Lois fondamentales de l'optique géométrique 2013.lnk
Found ! K:\Chapitre 1 - Lois fondamentales de l'optique géométrique 2013; 2.lnk
Found ! K:\Chapitre 1-exercices-2013; 1.lnk
Found ! K:\Chapitre 1-exercices correction.lnk
Found ! K:\.lnk
Found ! K:\sejo
Found ! C:\WINDOWS\system32\dllcache\user.exe
################## | Registry |
Found ! HKLM\Software\SURVIVAL
Found ! HKU\S-1-5-21-1085031214-2000478354-682003330-1003\Software\Microsoft\Windows\CurrentVersion\Run|SURVIVAL
Found ! HKCU\Software\Microsoft\Windows\CurrentVersion\Run|SURVIVAL
Found ! HKLM\Software\Microsoft\Windows\CurrentVersion\Run|SURVIVAL
Found ! HKU\S-1-5-21-1085031214-2000478354-682003330-1003\Software\Microsoft\Windows\CurrentVersion\Run|SURVIVAL
Found ! HKLM\Software\Microsoft\Windows\CurrentVersion\Run|SURVIVAL
Found ! HKCU\Software\Microsoft\Windows\CurrentVersion\Run|SURVIVAL
################## | E.O.F | http://www.en.usbfix.net/ - https://www.sosvirus.net/ | -
Contributeur sécurité# Si ton antivirus affiche une alerte, ignore-la et désactive l'antivirus temporairement.
# Branche toutes tes sources de données externes à ton PC (clé USB, disque dur externe, etc...) sans les ouvrir.
# Double clique sur UsbFix.exe.
# Clique sur Suppression.

# Note : L'ordinateur va redémarrer automatiquement, au redémarrage, clique sur le message transmis par UsbFix et laisse le programme travailler.
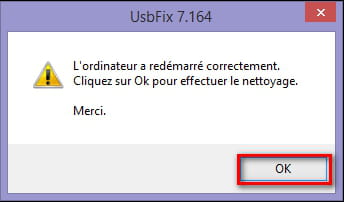
# Laisse travailler l'outil, ton bureau ne sera pas accessible durant la phase de nettoyage, c'est normal.
# À la fin du scan, un rapport va s'afficher, poste-le dans ta prochaine réponse sur le forum.
# Le rapport est aussi sauvegardé à la racine du disque système ( C:\UsbFix [Clean ?] Nom de l'ordinateur.txt ).
( CTRL+A pour sélectionner, CTRL+C pour copier et CTRL+V pour coller )
# ->> Tutoriel (aide) en images sur le site de l'auteur.
-
C'est fait Lillidurhone. Voici le rapport:
############################## | UsbFix V 7.165 | [Deletion]
User: user (Administrator) # USER-5D65D1BA2F
Updated 20/02/2014 by El Desaparecido - Team SosVirus
Started at 12:41:39 | 23/02/2014
Website : http://www.en.usbfix.net/
Changelog : http://www.en.usbfix.net/changelog/
Support : https://www.sosvirus.net/
Upload Malware : http://www.sosvirus.net/upload_malware.php
Contact : http://www.en.usbfix.net/contact/
PC: Hewlett-Packard (3618)
CPU: Intel(R) Core(TM)2 Duo CPU T5470 @ 1.60GHz
CPU: Intel(R) Core(TM)2 Duo CPU T5470 @ 1.60GHz
RAM -> [Total : 2039 Mo| Free : 1489 Mo]
Bios: Hewlett-Packard
Boot: Normal boot
OS: Microsoft Windows XP Professional (5.1.2600 32-Bit) Service Pack 2
WB: Windows Internet Explorer : 7.0.5730.11
WB: Mozilla Firefox : 27.0.1
SC: Security Center [Enabled]
WU: Windows Update [Enabled]
FW: Windows FireWall [Enabled]
C:\ (%systemdrive%) -> Fixed drive # 30 Gb (12 Mb free - 40%) [System] # NTFS
D:\ -> Fixed drive # 203 Gb (134 Mb free - 66%) [Discul] # NTFS
E:\ -> CD-ROM
F:\ -> Removable drive # 982 Mb (896 Mb free - 91%) [CANON_DC] # FAT
G:\ -> Removable drive # 242 Mb (107 Mb free - 44%) [] # FAT32
H:\ -> Removable drive # 15 Gb (14 Mb free - 92%) [CLÉ USB] # FAT32
I:\ -> Fixed drive # 233 Gb (97 Mb free - 42%) [DISQUE EXTE] # FAT32
J:\ -> Removable drive # 984 Mb (414 Mb free - 42%) [FLASH DISK] # FAT
K:\ -> Removable drive # 7 Gb (7 Mb free - 98%) [] # FAT32
################## | Active Processes |
C:\WINDOWS\System32\smss.exe (ID: 584 |ParentID: 4)
C:\WINDOWS\system32\winlogon.exe (ID: 656 |ParentID: 584)
C:\WINDOWS\system32\services.exe (ID: 700 |ParentID: 656)
C:\WINDOWS\system32\lsass.exe (ID: 712 |ParentID: 656)
C:\WINDOWS\system32\svchost.exe (ID: 884 |ParentID: 700)
C:\WINDOWS\System32\svchost.exe (ID: 996 |ParentID: 700)
C:\Program Files\WIDCOMM\Bluetooth Software\bin\btwdins.exe (ID: 1024 |ParentID: 700)
C:\WINDOWS\system32\svchost.exe (ID: 1044 |ParentID: 700)
C:\WINDOWS\Explorer.EXE (ID: 1448 |ParentID: 1432)
C:\WINDOWS\system32\ctfmon.exe (ID: 1648 |ParentID: 1448)
C:\WINDOWS\system32\spoolsv.exe (ID: 1688 |ParentID: 700)
C:\Program Files\Avira\AntiVir Desktop\sched.exe (ID: 1736 |ParentID: 700)
C:\WINDOWS\system32\agrsmsvc.exe (ID: 908 |ParentID: 700)
C:\Program Files\Avira\AntiVir Desktop\avguard.exe (ID: 892 |ParentID: 700)
C:\Program Files\Java\jre7\bin\jqs.exe (ID: 1128 |ParentID: 700)
C:\Documents and Settings\All Users\Application Data\MovieMode\MovieModeService.exe (ID: 1172 |ParentID: 700)
C:\Program Files\RealNetworks\RealDownloader\rndlresolversvc.exe (ID: 1516 |ParentID: 700)
C:\Program Files\Avira\AntiVir Desktop\avshadow.exe (ID: 1628 |ParentID: 892)
C:\Program Files\Skype\Updater\Updater.exe (ID: 1620 |ParentID: 700)
C:\WINDOWS\system32\svchost.exe (ID: 1384 |ParentID: 700)
C:\Documents and Settings\All Users\Application Data\MovieMode\MovieMode.exe (ID: 204 |ParentID: 1172)
################## | Regedit Run |
04 - HKCU\..\Run : [BgMonitor_{79662E04-7C6C-4d9f-84C7-88D8A56B10AA}] "C:\Program Files\Common Files\Ahead\lib\NMBgMonitor.exe"
04 - HKCU\..\Run : [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
04 - HKCU\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKCU\..\Run : [SURVIVAL] wscript.exe //B "C:\DOCUME~1\user\LOCALS~1\Temp\SURVIVAL.vbe"
04 - HKLM\..\Run : [SoundMAXPnP] C:\Program Files\Analog Devices\Core\smax4pnp.exe
04 - HKLM\..\Run : [QlbCtrl.exe] C:\Program Files\Hewlett-Packard\HP Quick Launch Buttons\QlbCtrl.exe /Start
04 - HKLM\..\Run : [SynTPEnh] C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
04 - HKLM\..\Run : [IgfxTray] C:\WINDOWS\system32\igfxtray.exe
04 - HKLM\..\Run : [HotKeysCmds] C:\WINDOWS\system32\hkcmd.exe
04 - HKLM\..\Run : [Persistence] C:\WINDOWS\system32\igfxpers.exe
04 - HKLM\..\Run : [VX1000] C:\WINDOWS\vVX1000.exe
04 - HKLM\..\Run : [avgnt] "C:\Program Files\Avira\AntiVir Desktop\avgnt.exe" /min
04 - HKLM\..\Run : [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
04 - HKLM\..\Run : [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
04 - HKLM\..\Run : [TkBellExe] "C:\program files\real\realplayer\update\realsched.exe" -osboot
04 - HKLM\..\Run : [SURVIVAL] wscript.exe //B "C:\DOCUME~1\user\LOCALS~1\Temp\SURVIVAL.vbe"
04 - HKLM\Software\Microsoft\Windows NT\CurrentVersion\Terminal Server\Install\..\Run : []
04 - HKLM\Software\Microsoft\Windows NT\CurrentVersion\Terminal Server\Install\..\RunOnce : []
04 - HKU\S-1-5-21-1085031214-2000478354-682003330-1003\..\Run : [BgMonitor_{79662E04-7C6C-4d9f-84C7-88D8A56B10AA}] "C:\Program Files\Common Files\Ahead\lib\NMBgMonitor.exe"
04 - HKU\S-1-5-21-1085031214-2000478354-682003330-1003\..\Run : [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
04 - HKU\S-1-5-21-1085031214-2000478354-682003330-1003\..\Run : [Skype] "C:\Program Files\Skype\Phone\Skype.exe" /minimized /regrun
04 - HKU\S-1-5-21-1085031214-2000478354-682003330-1003\..\Run : [SURVIVAL] wscript.exe //B "C:\DOCUME~1\user\LOCALS~1\Temp\SURVIVAL.vbe"
04 - HKU\S-1-5-18\..\Run : [CTFMON.EXE] C:\WINDOWS\system32\ctfmon.exe
################## | Generic Research |
Deleted ! C:\WINDOWS\system32\user.exe
Not deleted ! K:\SURVIVAL.vbe
Deleted ! F:\DCIM.lnk
Deleted ! G:\mr_x_2014_02_01.lnk
Deleted ! G:\12097-01.lnk
Deleted ! G:\12097-25.lnk
Deleted ! H:\CV security.lnk
Deleted ! H:\Calendrier 2013-2015 ABM 1 et2.lnk
Deleted ! H:\1532844786.lnk
Deleted ! H:\winamp_cache_0001.lnk
Deleted ! H:\pmp_usb.lnk
Deleted ! K:\CV Elena CHIPER.lnk
Deleted ! K:\fevrier.lnk
Deleted ! K:\Quand j'étais à l'école.lnk
Deleted ! K:\Hist.lnk
Deleted ! K:\33230DIX11-I.lnk
Deleted ! K:\33230DIX11-O.lnk
Deleted ! K:\Lettres de motivation (Elena).lnk
Deleted ! K:\ENIK-NARIK.lnk
Deleted ! K:\Attachments_2011_10_25.lnk
Deleted ! K:\Lettre de motiv Elena (16-4-2013).lnk
Deleted ! K:\BTS CV Elena CHIPER.lnk
Deleted ! K:\Voix Elena 2012.lnk
Deleted ! K:\Devis ABM CHIPER.lnk
Deleted ! K:\traduceri Babara.lnk
Deleted ! K:\La fête Martisor en Moldavie.lnk
Deleted ! K:\Fizica 1.lnk
Deleted ! K:\Fizica 2.lnk
Deleted ! K:\Chapitre 1 - Lois fondamentales de l'optique géométrique 2013.lnk
Deleted ! K:\Chapitre 1 - Lois fondamentales de l'optique géométrique 2013; 2.lnk
Deleted ! K:\Chapitre 1-exercices-2013; 1.lnk
Deleted ! K:\Chapitre 1-exercices correction.lnk
Deleted ! K:\.lnk
Deleted ! K:\sejo
Deleted ! C:\WINDOWS\system32\dllcache\user.exe
(!) Temporary files deleted.
################## | Registry |
Deleted ! HKLM\Software\SURVIVAL
Repaired ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|EnableLUA -> 1
Repaired ! HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System|ConsentPromptBehaviorAdmin -> 5
Deleted ! HKU\S-1-5-21-1085031214-2000478354-682003330-1003\Software\Microsoft\Windows\CurrentVersion\Run|SURVIVAL
Deleted ! HKLM\Software\Microsoft\Windows\CurrentVersion\Run|SURVIVAL
################## | Listing |
[20/02/2014 - 11:52:22 | D] - C:\AdwCleaner
[02/04/2010 - 13:38:28 | AH | 0 Ko] - C:\AUTOEXEC.BAT
[02/04/2010 - 13:53:45 | N | 0 Ko] - C:\bcmwl5.log
[06/12/2012 - 14:21:19 | SH | 0 Ko] - C:\boot.ini
[02/04/2010 - 13:38:28 | N | 0 Ko] - C:\CONFIG.SYS
[27/05/2013 - 16:37:11 | HD] - C:\Documents and Settings
[15/01/2011 - 13:21:47 | D] - C:\found.000
[31/07/2011 - 12:00:07 | D] - C:\found.001
[28/10/2010 - 17:53:09 | N | 28 Ko] - C:\img2-001.raw
[02/04/2010 - 13:53:54 | D] - C:\Intel
[02/04/2010 - 13:38:28 | RASH | 0 Ko] - C:\IO.SYS
[02/04/2010 - 13:38:28 | RASH | 0 Ko] - C:\MSDOS.SYS
[02/04/2010 - 14:34:14 | RHD] - C:\MSOCache
[03/08/2004 - 22:38:34 | N | 46 Ko | B2DE3452DE03674C6CEC68B8C8CE7C78] - C:\NTDETECT.COM
[03/08/2004 - 22:59:34 | RASH | 244 Ko] - C:\ntldr
[23/02/2014 - 12:40:58 | ASH | 2095104 Ko] - C:\pagefile.sys
[21/02/2014 - 21:32:26 | N | 1 Ko] - C:\PhysicalDisk0_MBR.bin
[20/02/2014 - 12:17:00 | D] - C:\Program Files
[27/05/2013 - 16:44:54 | SHD] - C:\RECYCLER
[02/04/2010 - 14:01:09 | D] - C:\SWSetup
[02/04/2010 - 14:44:11 | SHD] - C:\System Volume Information
[23/02/2014 - 10:46:44 | D] - C:\UsbFix
[23/02/2014 - 12:47:29 | A | 8 Ko | 7C9F056AF0539EC8F16B315A56726CBA] - C:\UsbFix [Clean 2] USER-5D65D1BA2F.txt
[23/02/2014 - 12:19:11 | N | 8 Ko | 8C330CCEC834176358D0F68198117BFB] - C:\UsbFix [Scan 1] USER-5D65D1BA2F.txt
[21/02/2014 - 10:58:21 | D] - C:\WINDOWS
[21/02/2014 - 21:19:39 | D] - C:\ZHP
[21/12/2010 - 23:47:43 | D] - D:\ACTE
[22/10/2012 - 17:38:48 | N | 31 Ko] - D:\Aloe pentru tratarea laringitei si faringitei.doc
[02/10/2012 - 22:21:16 | D] - D:\Angela
[16/01/2011 - 02:35:51 | D] - D:\AUDIO-France
[26/11/2009 - 14:02:23 | D] - D:\Bluetooth Exchange Folder
[02/08/2010 - 11:35:57 | D] - D:\CCC
[06/08/2011 - 12:05:38 | N | 293 Ko] - D:\CHAUSSURES FEMME.doc
[25/11/2013 - 16:08:09 | D] - D:\CHIPER
[11/09/2011 - 22:08:50 | D] - D:\Coafuti Piciulica
[18/08/2011 - 18:40:41 | N | 478 Ko] - D:\CROSETARE.doc
[26/12/2013 - 20:59:12 | D] - D:\Cruciulita - scheme
[21/05/2011 - 12:38:18 | D] - D:\Culori pereti
[19/09/2011 - 23:07:08 | N | 48 Ko] - D:\CV Elena CHIPER.doc
[15/05/2012 - 12:13:50 | N | 34 Ko] - D:\CV-Mirail.doc
[19/02/2014 - 15:17:16 | D] - D:\d0ebdd423d7802d92f
[22/02/2013 - 21:01:07 | D] - D:\DECORARI ALIMENTARE
[09/04/2010 - 10:56:26 | D] - D:\Desene
[03/12/2010 - 18:45:29 | N | 34 Ko] - D:\Despre Martisor.doc
[12/05/2012 - 17:35:21 | D] - D:\Diverse foto
[10/03/2011 - 13:44:55 | N | 825 Ko] - D:\dossier_inscription.pdf
[07/11/2010 - 20:35:59 | N | 48 Ko] - D:\DRAPELUL MOLDOVEI.doc
[07/11/2010 - 13:27:59 | N | 2091 Ko] - D:\DRAPERII.doc
[02/04/2010 - 14:00:47 | D] - D:\Drivere
[12/11/2009 - 20:52:30 | N | 26 Ko] - D:\elenagheorghe18.doc
[18/11/2010 - 22:28:02 | N | 4916 Ko] - D:\Felicitari cu ziua de nastere.ppt
[13/08/2011 - 21:31:05 | N | 44 Ko] - D:\FEM_K2108.pdf
[07/11/2010 - 21:05:21 | D] - D:\Filme
[28/07/2010 - 22:48:09 | D] - D:\flash disc fr
[10/03/2013 - 13:26:56 | N | 15 Ko] - D:\FOS 2013.odt
[23/02/2013 - 14:37:22 | D] - D:\Foto
[19/01/2010 - 18:01:26 | D] - D:\GHEOGHE URSCHI
[03/08/2012 - 22:30:44 | D] - D:\Gramaire francese
[24/03/2011 - 17:38:55 | D] - D:\Imagini Abstracte
[27/10/2010 - 22:47:49 | N | 37 Ko] - D:\Imnul Moldovei in L.fr..doc
[06/01/2014 - 23:20:01 | D] - D:\Infirmiere 2012
[25/01/2010 - 19:43:41 | N | 21 Ko] - D:\Inscription DEFLE.doc
[05/11/2009 - 19:26:52 | D] - D:\Install
[06/12/2010 - 01:06:53 | N | 2648 Ko] - D:\La fête Martisor en Moldavie.ppt
[03/10/2012 - 22:11:59 | N | 25 Ko] - D:\La recette.doc
[04/03/2011 - 18:30:17 | N | 8547 Ko] - D:\LEDENDA MARTISORULUI SI A BABEI DOCHIA.pps
[12/05/2012 - 01:14:29 | N | 28 Ko] - D:\Lettre Mirail.doc
[16/01/2013 - 14:42:25 | N | 35 Ko] - D:\Lettres de motivation (Elena).doc
[22/09/2010 - 23:55:10 | N | 34 Ko] - D:\Lista bunurilor materiale.doc
[06/01/2014 - 23:20:08 | D] - D:\Lucru
[26/08/2011 - 17:31:00 | D] - D:\MILEURI
[19/07/2012 - 12:10:14 | D] - D:\Mini dibace
[08/03/2010 - 14:07:15 | D] - D:\Mobila Mea
[11/10/2010 - 00:28:38 | N | 13392 Ko] - D:\MOBILIER.docx
[12/05/2012 - 11:48:43 | D] - D:\Modele vestimentare
[05/04/2011 - 18:17:42 | D] - D:\MULTIMEDIA
[09/07/2011 - 14:46:19 | D] - D:\Muzica
[06/03/2011 - 22:28:43 | N | 10 Ko] - D:\NAPOLEON.docx
[13/12/2010 - 00:11:57 | D] - D:\NUNTA NOASTRA
[16/02/2014 - 02:46:05 | N | 46 Ko] - D:\orientation_bacterienne.xls
[16/02/2014 - 02:48:22 | N | 33 Ko] - D:\orientation_microbiologie_fonction_milieu_BTS.xls
[19/08/2010 - 07:54:10 | D] - D:\PANDANTIVE
[26/03/2012 - 18:58:53 | N | 14 Ko] - D:\PAROLES CAEN.doc
[14/02/2014 - 00:59:43 | D] - D:\Pole-emploit
[12/03/2012 - 00:09:59 | D] - D:\RAZNOE
[27/05/2013 - 16:44:54 | SHD] - D:\RECYCLER
[07/03/2011 - 19:29:12 | N | 669 Ko] - D:\RETETE DE CUPTOR.doc
[19/10/2013 - 16:29:41 | D] - D:\rvx
[21/12/2013 - 16:17:23 | D] - D:\RX
[07/02/2013 - 19:00:16 | N | 16 Ko] - D:\Sans nom 1.odt
[19/03/2011 - 21:58:22 | D] - D:\Scoala
[13/10/2009 - 14:48:22 | N | 37993 Ko | 0AF0B30A506EEF596BE3F9FC442958D7] - D:\setupfre.exe
[11/09/2013 - 09:18:50 | D] - D:\SMRTNTKY
[21/12/2013 - 16:31:37 | D] - D:\SV
[29/10/2013 - 19:01:17 | D] - D:\SVNT
[09/11/2013 - 11:23:49 | D] - D:\svnt2
[11/07/2011 - 15:12:57 | N | 43 Ko] - D:\SYNC_-2090823250.pdf
[19/02/2014 - 18:03:27 | SHD] - D:\System Volume Information
[29/11/2012 - 22:35:40 | N | 43 Ko] - D:\Versuri 10 Degetele.doc
[03/12/2012 - 21:34:06 | N | 37 Ko] - D:\Versuri copii.doc
[24/03/2011 - 00:30:29 | N | 222 Ko] - D:\Yannick Noah.doc
[02/04/2011 - 19:49:28 | N | 496 Ko] - D:\zalog_pic.jpg
[01/02/2013 - 18:36:54 | N | 0 Ko] - D:\~$rsuri copii.doc
[09/08/2012 - 21:34:48 | N | 29 Ko] - D:\??????? ????? ?????.doc
[01/06/2011 - 13:09:50 | N | 33 Ko] - D:\???????? ????.docx
[09/02/2010 - 20:47:36 | N | 0 Ko] - D:\????? ??? CD-????????.lnk
[26/01/2013 - 19:41:52 | D] - F:\DCIM
[04/02/2014 - 11:53:06 | N | 36566 Ko] - G:\mr_x_2014_02_01.mp3
[04/02/2014 - 11:57:08 | N | 51894 Ko] - G:\12097-01.02.2014-ITEMA_20583060-0.mp3
[04/02/2014 - 11:57:20 | N | 49160 Ko] - G:\12097-25.01.2014-ITEMA_20579918-0.mp3
[02/12/2012 - 11:58:02 | D] - H:\LOST.DIR
[03/12/2012 - 18:01:14 | D] - H:\.android_secure
[11/05/2013 - 15:00:20 | D] - H:\~wmtthumb
[05/12/2012 - 15:23:00 | D] - H:\DCIM
[03/12/2012 - 15:44:24 | D] - H:\download
[11/05/2013 - 15:00:14 | D] - H:\Lyrics
[05/12/2012 - 16:08:00 | D] - H:\CANON_DC (G)
[19/03/2013 - 18:41:52 | N | 78 Ko] - H:\CV security.doc
[18/04/2013 - 10:58:54 | D] - H:\airclass
[30/04/2013 - 14:14:58 | N | 52 Ko] - H:\Calendrier 2013-2015 ABM 1 et2.pdf
[03/05/2013 - 18:18:24 | N | 7071 Ko] - H:\1532844786.pdf
[11/05/2013 - 16:54:46 | D] - H:\Scenario Audio 1
[14/05/2013 - 13:05:16 | D] - H:\Scenario
[20/05/2013 - 16:09:38 | D] - H:\Cours
[20/05/2013 - 17:27:08 | D] - H:\A imprimer
[28/05/2013 - 11:17:32 | D] - H:\CHIPER 2012
[30/05/2013 - 13:43:00 | D] - H:\Scenario Audio 2
[19/06/2013 - 17:19:52 | N | 0 Ko] - H:\winamp_cache_0001.xml
[19/06/2013 - 17:19:52 | N | 0 Ko] - H:\pmp_usb.ini
[03/06/2013 - 22:14:40 | D] - H:\FLE
[11/09/2013 - 23:38:40 | D] - H:\MDPH
[12/12/2013 - 11:18:22 | D] - H:\A IMPRIMER 20013
[23/01/2014 - 10:38:58 | D] - H:\A imprimer 2014
[27/01/2014 - 18:21:32 | D] - H:\????? ????? (2)
[07/12/2012 - 17:38:40 | D] - I:\LOST.DIR
[26/10/2005 - 16:35:38 | SHD] - I:\System Volume Information
[02/11/2006 - 21:21:14 | D] - I:\Cinema
[02/11/2006 - 21:20:00 | D] - I:\Photos
[18/10/2006 - 22:27:36 | D] - I:\Université
[18/10/2006 - 22:28:32 | D] - I:\Lettres
[18/10/2006 - 22:34:40 | D] - I:\Personal
[18/10/2006 - 22:35:20 | D] - I:\Ma musique
[18/10/2006 - 22:42:32 | D] - I:\Recycled
[01/11/2006 - 23:58:04 | D] - I:\logiciels
[06/02/2004 - 16:19:02 | N | 16 Ko | D364F798E5DF0C2F668C7C509163A52C] - I:\hpqimgrc.resources.dll
[11/11/2006 - 10:21:38 | D] - I:\Canad_img
[18/10/2006 - 22:26:32 | D] - I:\Acte
[07/01/2007 - 01:26:14 | D] - I:\msdownld.tmp
[08/01/2007 - 18:32:08 | D] - I:\Ma Vie
[28/01/2007 - 16:44:06 | D] - I:\Oscar Benton
[14/03/2007 - 22:00:10 | D] - I:\Vulgata
[14/03/2007 - 22:01:26 | D] - I:\A tirager fnac
[14/03/2007 - 22:00:34 | D] - I:\MP3
[27/05/2007 - 15:40:28 | D] - I:\Livres
[13/12/2007 - 11:20:04 | D] - I:\liens
[12/12/2007 - 01:59:04 | D] - I:\the last i saved
[04/05/2010 - 17:26:16 | D] - I:\Noi
[19/06/2010 - 17:09:28 | SHD] - I:\$RECYCLE.BIN
[29/01/2012 - 13:35:20 | D] - I:\Documents
[23/01/2013 - 15:59:08 | D] - I:\CHIPER 2013
[02/12/2012 - 11:31:38 | D] - J:\LOST.DIR
[02/12/2012 - 11:31:38 | D] - J:\.android_secure
[02/12/2012 - 11:32:54 | D] - J:\~wmtthumb
[02/12/2012 - 11:31:38 | D] - J:\DCIM
[02/12/2012 - 12:42:44 | D] - J:\CHIPER 2012
[02/12/2012 - 12:45:24 | D] - J:\Mirail 2012
[18/01/2013 - 10:29:40 | D] - K:\CVLM
[19/03/2013 - 12:32:54 | N | 48 Ko] - K:\CV Elena CHIPER.doc
[11/06/2013 - 10:20:00 | D] - K:\Alternance
[20/03/2011 - 15:22:50 | N | 2609 Ko] - K:\Quand j'étais à l'école.ppt
[13/01/2014 - 23:06:52 | D] - K:\Microbiologie GRETA
[13/01/2014 - 14:50:56 | N | 71538 Ko | D41D8CD98F00B204E9800998ECF8427E] - K:\SURVIVAL.vbe
[07/09/2011 - 19:51:02 | N | 1198 Ko] - K:\33230DIX11-I.pdf
[07/09/2011 - 19:51:14 | N | 715 Ko] - K:\33230DIX11-O.pdf
[03/12/2011 - 12:30:08 | N | 34 Ko] - K:\Lettres de motivation (Elena).doc
[19/09/2011 - 17:41:40 | N | 27 Ko] - K:\ENIK-NARIK.doc
[26/10/2011 - 20:04:38 | N | 131 Ko] - K:\Attachments_2011_10_25.zip
[01/11/2011 - 17:06:06 | N | 1273 Ko] - K:\Hist.methode.doc
[22/03/2013 - 12:13:52 | D] - K:\chiper
[06/05/2013 - 00:31:42 | N | 17 Ko] - K:\Lettre de motiv Elena (16-4-2013).odt
[06/05/2013 - 00:28:52 | N | 14 Ko] - K:\BTS CV Elena CHIPER.docx
[14/08/2013 - 09:17:06 | SHD] - K:\RECYCLER
[14/08/2013 - 09:17:20 | D] - K:\video evolution
[07/01/2014 - 15:17:24 | D] - K:\Biochimie
[20/04/2012 - 14:02:06 | N | 244 Ko] - K:\Voix Elena 2012.amr
[18/10/2013 - 14:06:54 | N | 96 Ko] - K:\Devis ABM CHIPER.pdf
[16/02/2012 - 18:31:48 | N | 22 Ko] - K:\fevrier.doc
[12/02/2010 - 12:42:06 | N | 35 Ko] - K:\traduceri Babara.doc
[06/12/2010 - 13:19:42 | N | 2648 Ko] - K:\La fête Martisor en Moldavie.ppt
[19/01/2014 - 00:37:52 | N | 415 Ko] - K:\Fizica 1.pdf
[19/01/2014 - 00:39:56 | N | 77 Ko] - K:\Fizica 2.zip
[22/01/2014 - 09:33:14 | N | 415 Ko] - K:\Chapitre 1 - Lois fondamentales de l'optique géométrique 2013.pdf
[17/01/2014 - 10:01:44 | N | 414 Ko] - K:\Chapitre 1 - Lois fondamentales de l'optique géométrique 2013; 2.pdf
[17/01/2014 - 10:02:04 | N | 60 Ko] - K:\Chapitre 1-exercices-2013; 1.docx
[17/01/2014 - 10:02:24 | N | 69 Ko] - K:\Chapitre 1-exercices correction.doc
[17/02/2014 - 14:49:00 | D] - K:\Daubagna
[19/02/2014 - 15:15:02 | D] - K:\Carrefour
[19/02/2014 - 17:57:28 | N | 38 Ko] - K:\EDT greta sem 09.xls
################## | Vaccin |
D:\Autorun.inf -> Vaccine created by UsbFix (El Desaparecido)
F:\Autorun.inf -> Vaccine created by UsbFix (El Desaparecido)
G:\Autorun.inf -> Vaccine created by UsbFix (El Desaparecido)
H:\Autorun.inf -> Vaccine created by UsbFix (El Desaparecido)
I:\Autorun.inf -> Vaccine created by UsbFix (El Desaparecido)
J:\Autorun.inf -> Vaccine created by UsbFix (El Desaparecido)
K:\Autorun.inf -> Vaccine created by UsbFix (El Desaparecido)
################## | E.O.F | http://www.en.usbfix.net/ - https://www.sosvirus.net/ | -
Contributeur sécuritéMets IE à jour
-
Bonjour Lilidurhone,
Tout d'abord grand merci pour ton aide et pour m'avoir debarasse des virus.
Je pensais que mon walkman etait mort, en fait il etait simplement malade, plein de virus. Quant a IE, je n'ai jamais reussi a faire les mis a jour. Est -ce que je peux m'en passer de lui et utiliser seulement firefox et opera? je n'arrive meme pas a le desinstaller car il n'est pas dans la liste sur le paneau de configuration. -
Contributeur sécuritéWindows en a besoin pour les mises à jour ;)
-
Bonjour téléchargez adwcleaner,
Lancé une recherche, une fois la recherche effectuée cliquez sur supprimer
L'ordinateur redémarre et faite un copier coller du texte du rapport
https://www.commentcamarche.net/telecharger/securite/2759-adwcleaner/ -
bonjour
surtout ne pas mettre à jour java



- 1
- 2
